crowdsec
 crowdsecurity/crowdsec
Open-source IDS/IPS and WAF engine that analyzes logs and HTTP requests to detect and block malicious IPs, leveraging a crowdsourced community…
anti-botdefensive-toolsids-ips-evasion+6
15.1k
crowdsecurity/crowdsecOpen-source IDS/IPS and WAF engine that analyzes logs and HTTP requests to detect and block malicious IPs, leveraging a crowdsourced community…
 stamparm/maltrail
Real-time malicious traffic detection system using public blacklists, static malware trails, and heuristic analysis to identify threats across DNS,…
 owasp-modsecurity/modsecurity
ModSecurity is an open source, cross platform web application firewall (WAF) engine for Apache, IIS and Nginx. It has a robust event-based…
 beelzebub-labs/beelzebub
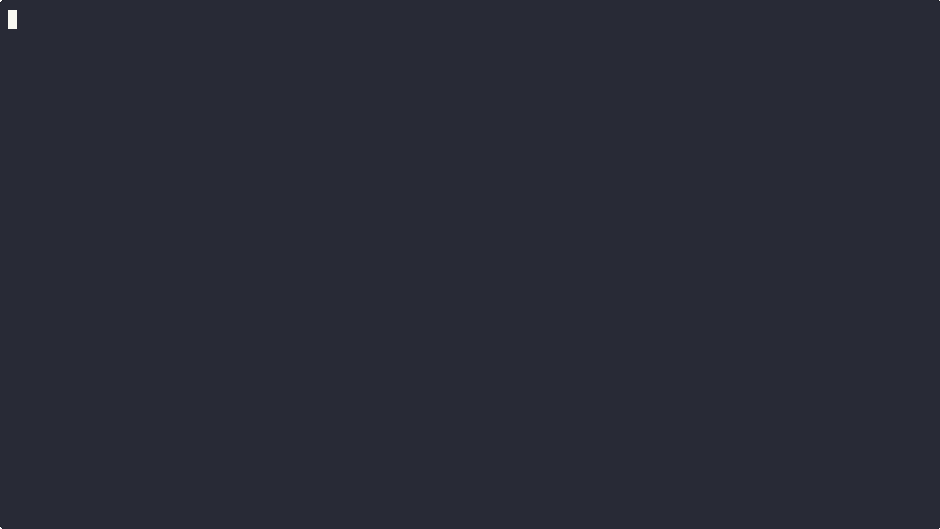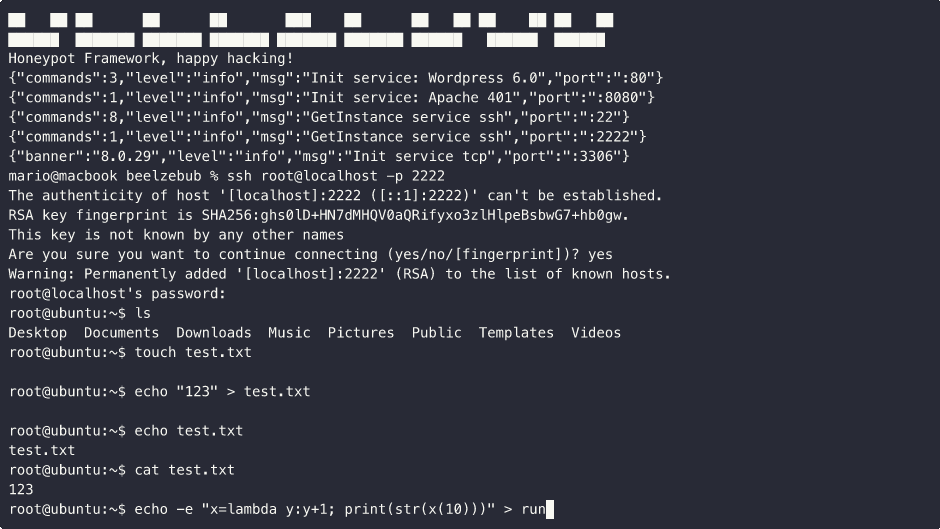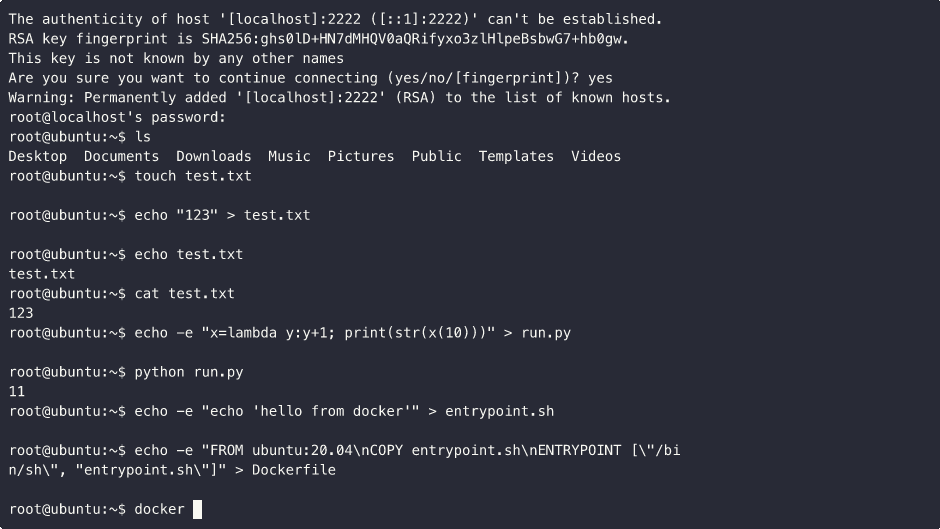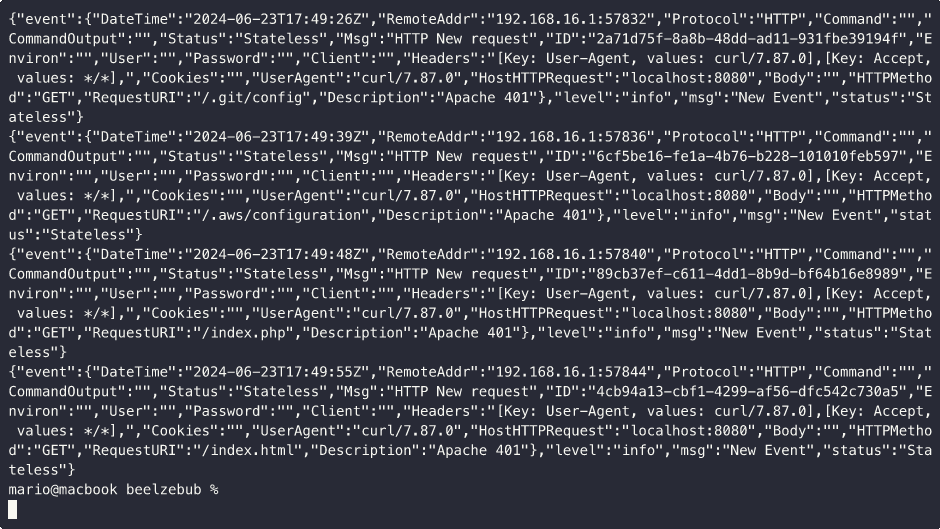
A secure low code deception runtime framework, leveraging AI for System Virtualization.
 oisf/libhtp
Security-aware HTTP protocol parser library used by IDS/IPS engines to inspect and normalize HTTP traffic for threat detection.
 chpratik/nginx_2026_cve_bundle_cti_report
Covered CVEs: CVE-2026-28755, CVE-2026-42926, CVE-2026-9256, CVE-2026-42055, CVE-2026-42533
 offseckit/cve-2026-24207
CVE-2026-24207 — NVIDIA Triton SageMaker auth bypass to unauth RCE. Detection script, bypass demo, RCE-chain PoC, and IDS rules.
 jconeby/elastic-peak-dashboards
PEAK Baseline Threat Hunt dashboards for Security Onion 3.0 — covering DNS, HTTP, TLS, SMB, Kerberos, SSH, RDP, DCE/RPC, LDAP, Modbus, DNP3,…
 corelight/cve-2021-44228
Zeek package for detecting Log4j CVE-2021-44228 exploit attempts via HTTP header payloads, LDAP Java class downloads, and second-stage Java class…
 michaelsanford/log4shell-honeypot
Dockerized honeypot for CVE-2021-44228.
 nosie12/fire-wall-server
Python-based simulated firewall to detect and block Spring4Shell (CVE-2022-22965) exploit attempts. This project filters HTTP requests by identifying…
 0x4d31/galah
Galah: An LLM-powered web honeypot.
 elshaheedy/cve-2025-29927-sigma-rule
Sigma rule for detecting CVE-2025-29927 exploitation via suspicious x-middleware-subrequest HTTP headers in Next.js applications, with detection…
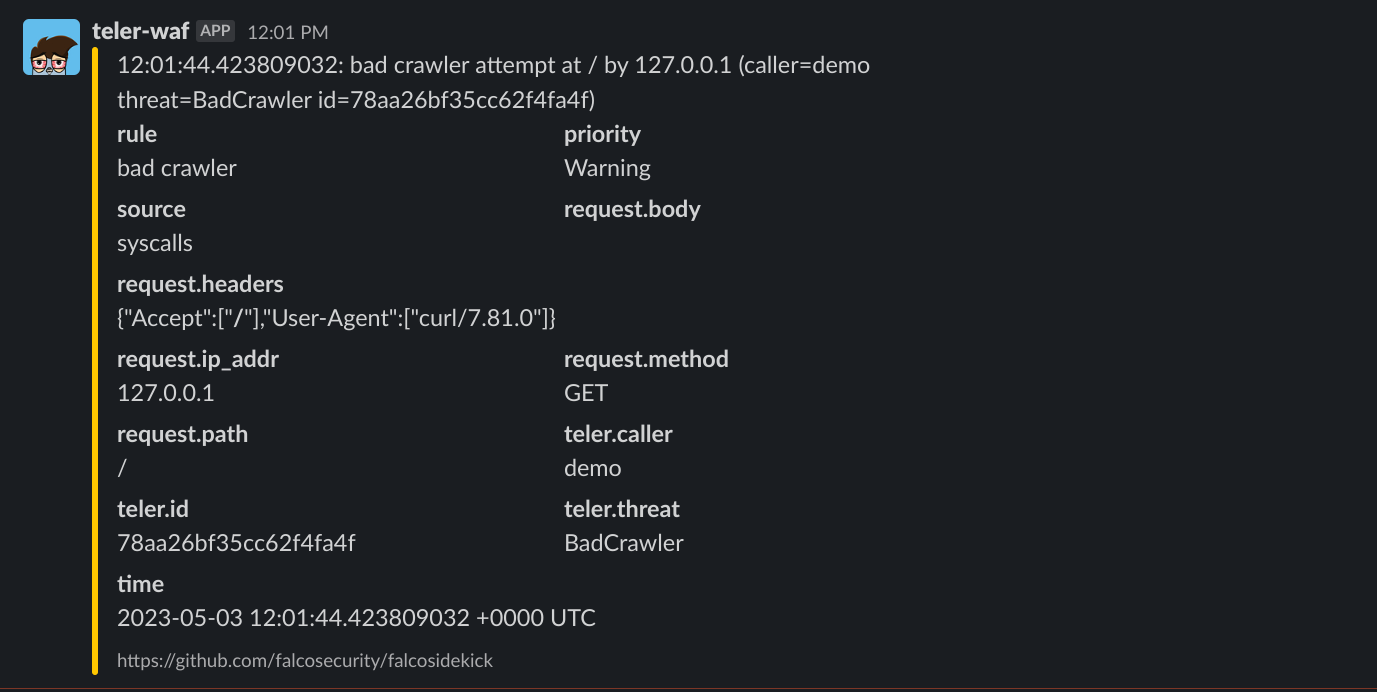 teler-sh/teler-waf
teler-waf is a Go HTTP middleware that protects local web services from OWASP Top 10 threats, known vulnerabilities, malicious actors, botnets,…
 corelight/cve-2021-31166
Detection rules (Suricata + Zeek) for CVE-2021-31166 HTTP Protocol Stack vulnerability, providing network-level alerts on exploit attempts against…
 corelight/cve-2022-21907
Zeek package to detect CVE-2022-21907 HTTP exploit attempts by analyzing packet captures for malformed requests and triggering alerts.