

wazuh
 wazuh/wazuh
Open-source XDR and SIEM platform for threat detection, log analysis, file integrity monitoring, vulnerability assessment, and compliance management…
anomaly-detectionanti-botcloud-security+12
17.4k20h 55m ago
wazuh/wazuhOpen-source XDR and SIEM platform for threat detection, log analysis, file integrity monitoring, vulnerability assessment, and compliance management…
 sana-404/cve-2026-8838-mitigation-and-detection
Detection and mitigation scripts for CVE-2026-8838, providing vulnerability scanning, configuration auditing, and incident response guidance to…
 t0tooro/cve-2025-24054-lab
Blue-team lab: detecting & mitigating CVE-2025-24054 (Windows NTLM hash disclosure) with Sysmon, Wazuh SIEM, and Group Policy
 deckhouse/d8-copy-fail-mitigation
Kubernetes-native CVE-2026-31431 mitigation with automated kernel module blocking, runtime Falco detection rules, and bashible-based node…
 garethmsheldon/cve-2026-22557-unifi-detection
Detection content for CVE-2026-22557 — UniFi Network Application unauthenticated path traversal (CVSS 10.0). Includes YARA, Sigma, KQL, Splunk SPL,…
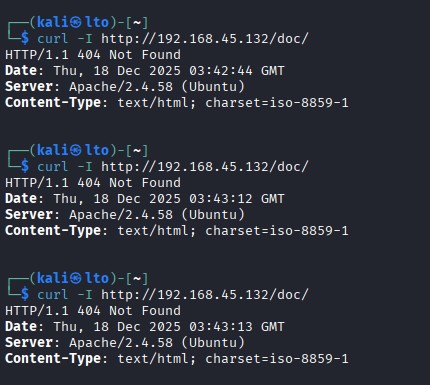 lto7777777/cve-1999-0678
CVE-1999-0678- /doc directory browsable
 adarkst/honeypot_smart_infrastructure
This Repository Includes Kubernetes manifest files for configuration of Honeypot system and Falco IDS in K8s environment. There are also Demo…
 zecure/shadowd
The Shadow Daemon web application firewall server
 mckinnonit/zabbix-template-cve-2020-1472
Zabbix Template to monitor for Windows Event Viewer event's related to Netlogon Elevation of Privilege Vulnerability - CVE-2020-1472. Monitors event…