
DANGDUT
 xsanflip/dangdut
Passive wireless intrusion detection system for ESP32-S3 and Flipper Zero that detects Wi-Fi deauthentication and disassociation attacks in real…
defensive-toolsembedded-systems-securityhardware-hacking+6
3
xsanflip/dangdutPassive wireless intrusion detection system for ESP32-S3 and Flipper Zero that detects Wi-Fi deauthentication and disassociation attacks in real…
 xeeshanajmal/qai2026-fgsm-transfer
Code and results for the QAI 2026 paper on FGSM attack transferability from simulation to IBM quantum hardware.
 wagga40/logstotal
Self-hosted multi-engine Sigma detection for event logs
 dragon-lady/netward-standalone
User-space bot and DDoS deflection for small HTTP services
 phpatch/weblogchecker
Free access-log compromise analyzer: webshell interactions, exploitation patterns and brute-force bursts in your Apache/nginx logs - severity,…
 d3lightfu1/quietphase
Pwsh tool for AD Group Enumeration Auditing
 supermhel/fengarde
Open-source, self-hosted security pipeline for IT, AI and OT. Logs in. Evidence out.: OCSF normalization, 46 detection rules…
 check-risk-waf/check-risk-waf
Reverse-proxy web application firewall with WAF, anti-bot and anti-DDoS protection at L3/L4/L7, custom rules, rate limiting, geo/IP filtering and…
 buybitart/get-the-hacker
Hunt WiFi threats silently. Catch the hackers.
 maureille/agentic-pcap
Benchmark code and interactive results for autonomous network-attack detection by tool-using LLM agents investigating raw PCAPs.
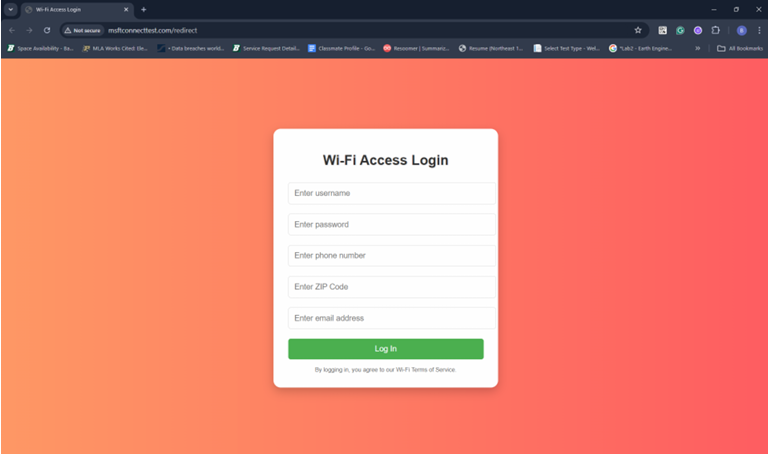
 yashubitra/evil_twin_attack
Rogue access point attack and defense on Kali Linux: deauth with aireplay-ng, an airbase-ng evil twin with a captive portal, plus real-time…
 yashubitra/mobile-intrusion-detection-system
Unsupervised deep autoencoder that flags anomalous mobile traffic: 25,000+ HTTP/HTTPS flows intercepted from a live iOS device with mitmproxy,…
 dshield-isc/dshield
Installs and configures a DShield honeypot sensor on Raspberry Pi or Ubuntu, running Cowrie SSH and HTTP honeypots and forwarding firewall logs to…
 0xajstrike/opcuatrap
High-interaction OPC UA honeypot for ICS/SCADA — multi-profile (oil & gas, water, power grid), live process simulation, per-session threat scoring,…
 corelight/emudhra-weak-keys
A Zeek package that detects when compromised eMudhra intermediate certificates are used in TLS 1.2 and below.
 corelight/php2shell-detect
Zeek and Suricata Detections for "php2shell" CVE-2026-109618 and CVE-2026-109619
 aide/aide
File integrity monitoring tool that detects unauthorized changes to monitored files and directories using attribute checks, multiple hash algorithms,…
 gitlab-security-oss/tldr
Sigma-based detection rules, log queries, atomic tests, and response procedures for monitoring and threat hunting in GitLab environments.