

LogsTotal
 wagga40/logstotal
Self-hosted multi-engine Sigma detection for event logs
defensive-toolsdigital-forensicsincident-response+5
wagga40/logstotalSelf-hosted multi-engine Sigma detection for event logs
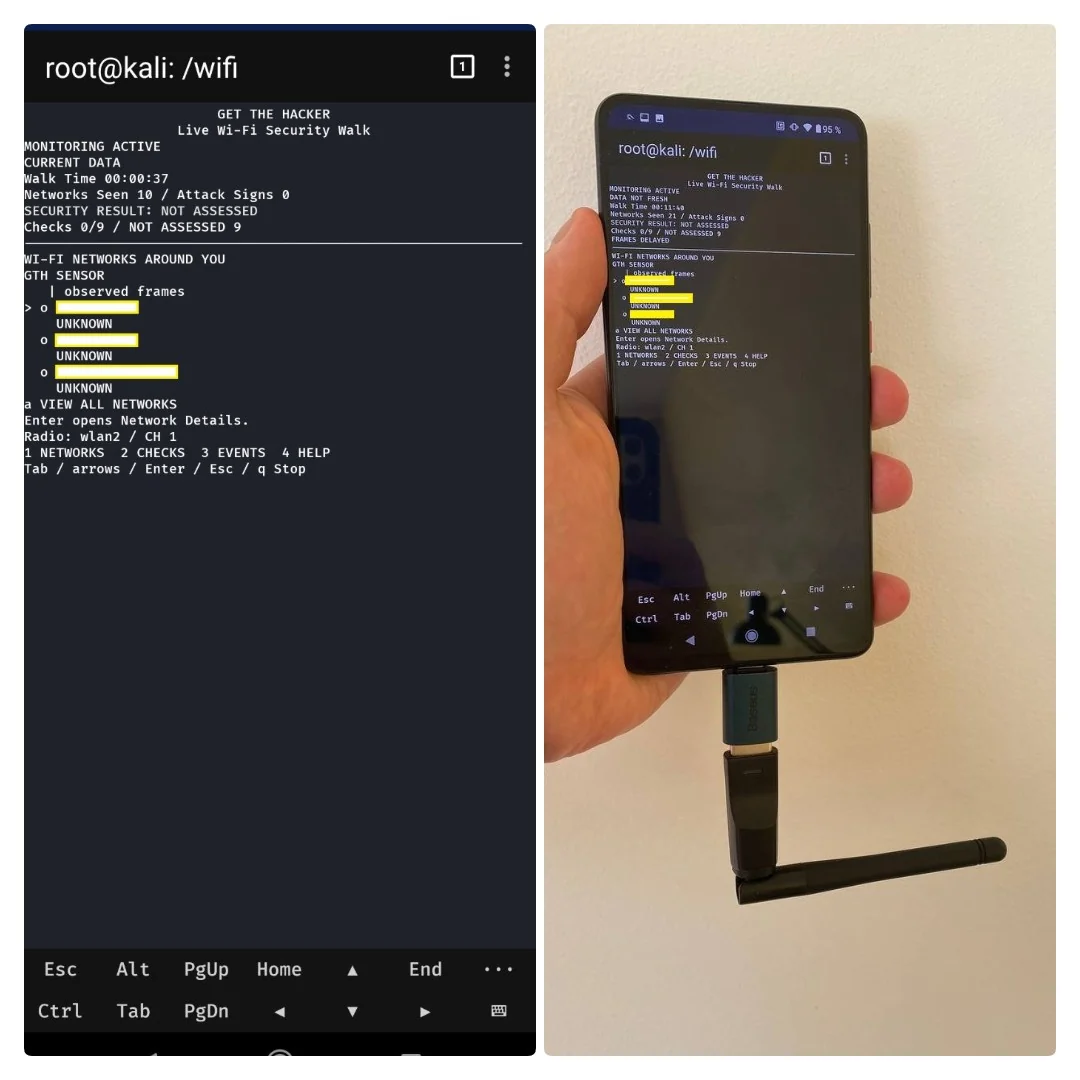 buybitart/get-the-hacker
Hunt WiFi threats silently. Catch the hackers.
 trustedsec/artillery
Open-source blue team tool that protects Linux and Windows systems using multiple host and network defense and detection methods.
 sonitbahl/sshintel
Self-contained SSH honeypot for capturing attacker interactions and turning them into structured security intelligence.
 gmh5225/crowarmor
Linux kernel security driver using LSM to harden the system, monitor and restore syscall table integrity, and protect CPU control registers against…
 thinkst/opencanary
Low-resource honeypot that emulates common network services to detect post-breach attacker activity, with extensible protocol modules and…
 thrandomv/cve-2026-31431-detection
Defensive detection package for CVE-2026-31431 (Linux kernel AF_ALG LPE). Sigma, Falco, auditd, KQL, and EQL rules mapped to MITRE ATT&CK…
 mr-r3b00t/cve-2021-44228
PowerShell-based backdoor detection tool for VMware Horizon connection servers, targeting CVE-2021-44228. Includes canary with optional submission…
 liamromanis101/cve-2026-31431-copy-fail---vulnerability-detection-script
Detection script for CVE-2026-31431 (Copy Fail) that checks kernel version, patch presence, kernel configs, AF_ALG socket availability, setuid…
 kadir/copy-fail-cve-2026-31431-ioc
Detection, mitigation, and IOC toolkit for Copy Fail CVE-2026-31431 Linux kernel page-cache privilege escalation
 hslatman/awesome-industrial-control-system-security
A curated list of resources related to Industrial Control System (ICS) security.
 falcosecurity/falco
Real-time cloud-native runtime security agent for Linux that monitors syscalls and container/Kubernetes metadata to detect anomalous behavior and…
 vedantk6403/koobe-guard
Linux kernel module using Kprobes to detect and neutralize CVE-2024-1086 heap double-free exploits via temporal gap tracking and active register…
 thinkst/canarytokens-docker
Docker configuration to quickly setup your own Canarytokens.
 olafhartong/sysmon-modular
A repository of sysmon configuration modules
 rfxn/linux-malware-detect
Multi-engine Linux malware scanner with five detection stages (MD5, HEX pattern, YARA, ClamAV, statistical), real-time inotify monitoring,…
 mthcht/purpleteam
Purpleteam scripts simulation & Detection - trigger events for SOC detections
 1-bit-wonder/kestrel
Single-host runtime-security dashboard on eBPF — Go agent + SvelteKit. Live process tree, network map, and rule-based alerts for plain Linux hosts.