

maltrail
 stamparm/maltrail
Real-time malicious traffic detection system using public blacklists, static malware trails, and heuristic analysis to identify threats across DNS,…
anomaly-detectionanti-botdefensive-tools+11
8.6k
stamparm/maltrailReal-time malicious traffic detection system using public blacklists, static malware trails, and heuristic analysis to identify threats across DNS,…
 corelight/cve-2021-41773
Zeek package detecting Apache HTTP Server path traversal/RCE exploits (CVE-2021-41773, CVE-2021-42013) with payload capture and server header…
 crowdsecurity/crowdsec
Open-source IDS/IPS and WAF engine that analyzes logs and HTTP requests to detect and block malicious IPs, leveraging a crowdsourced community…
 owasp-modsecurity/modsecurity
ModSecurity is an open source, cross platform web application firewall (WAF) engine for Apache, IIS and Nginx. It has a robust event-based…
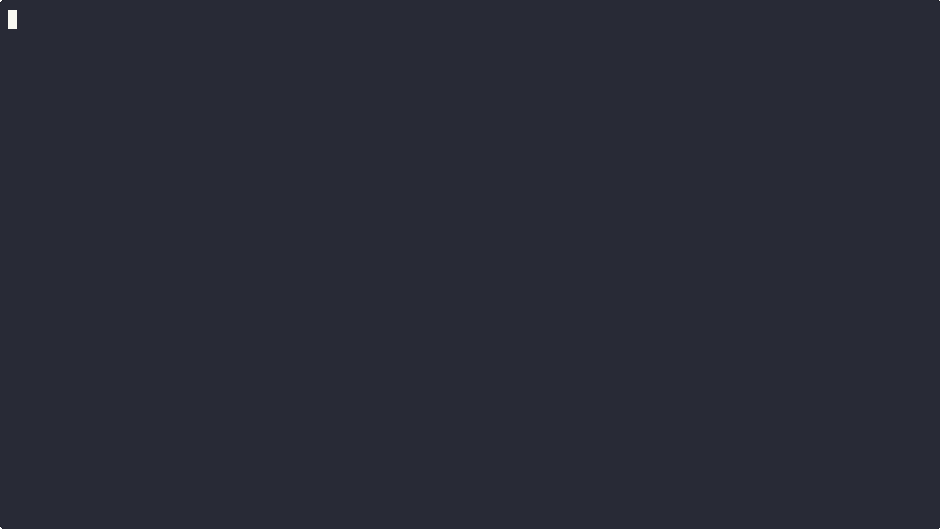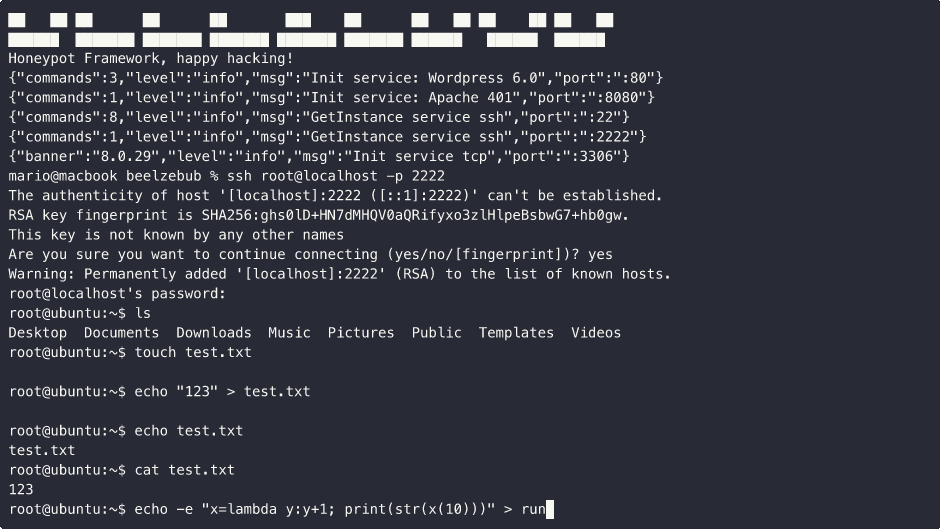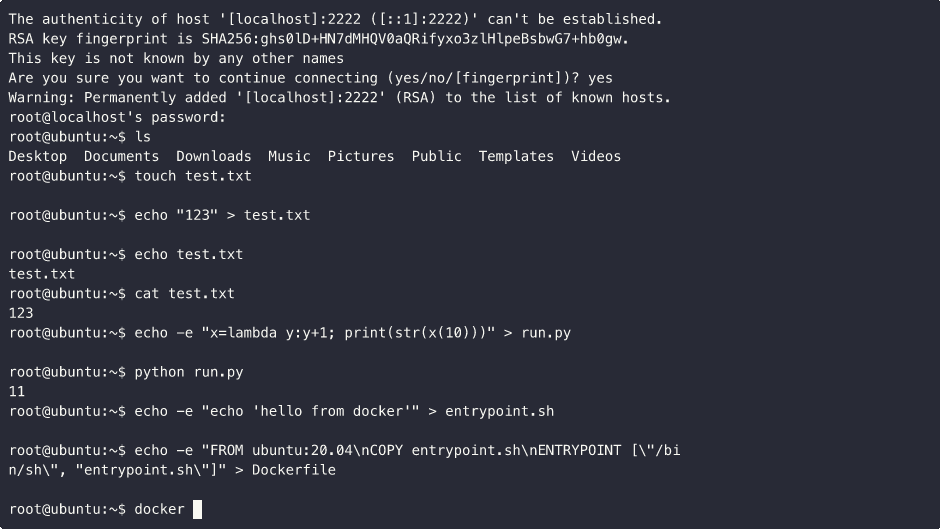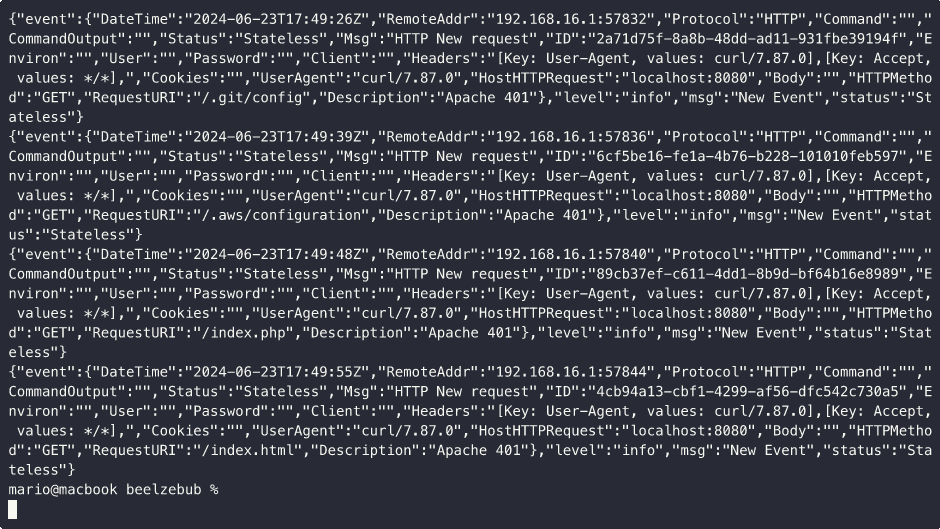 beelzebub-labs/beelzebub
A secure low code deception runtime framework, leveraging AI for System Virtualization.
 corelight/http-stalling-detector
Detect HTTP stalling attacks like slowloris with Bro
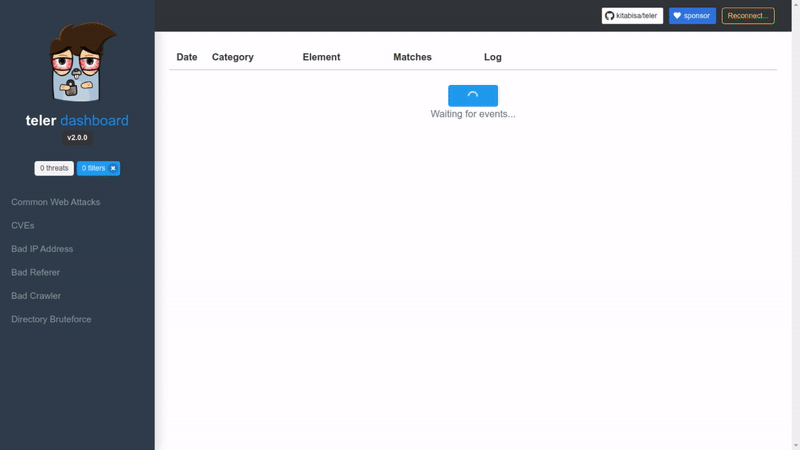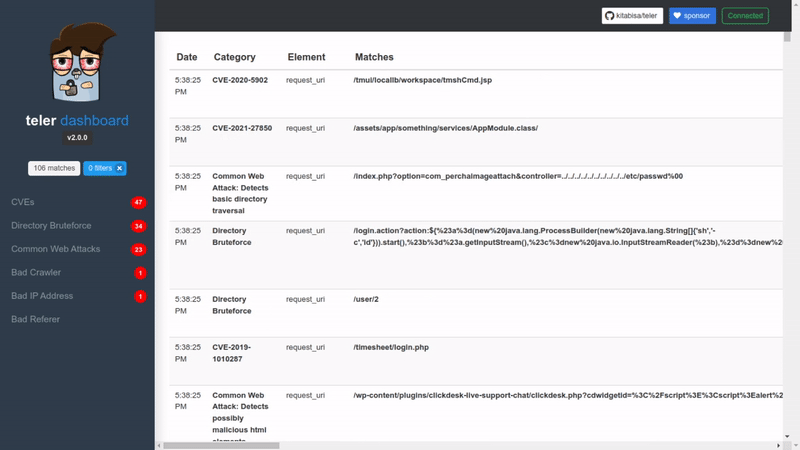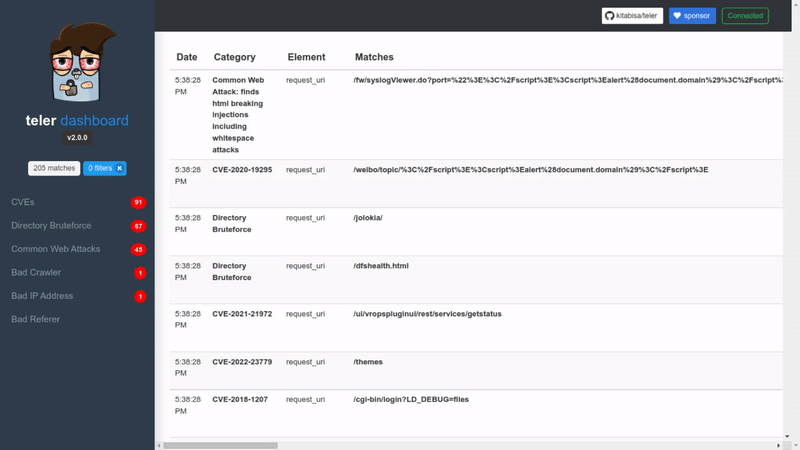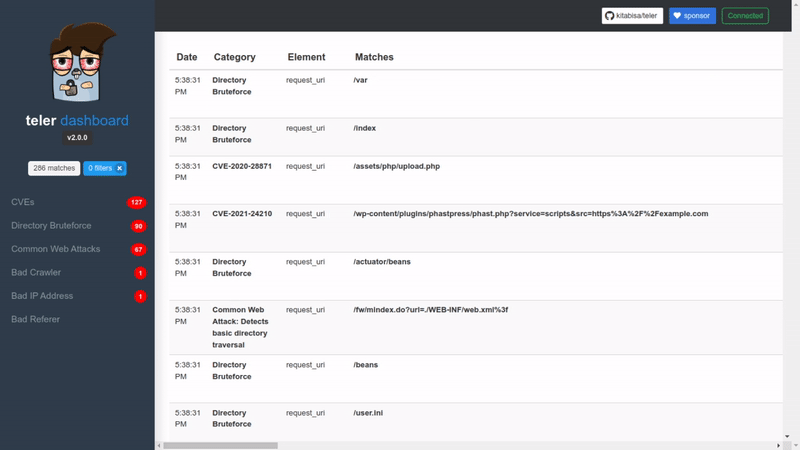 teler-sh/teler
Real-time HTTP Intrusion Detection
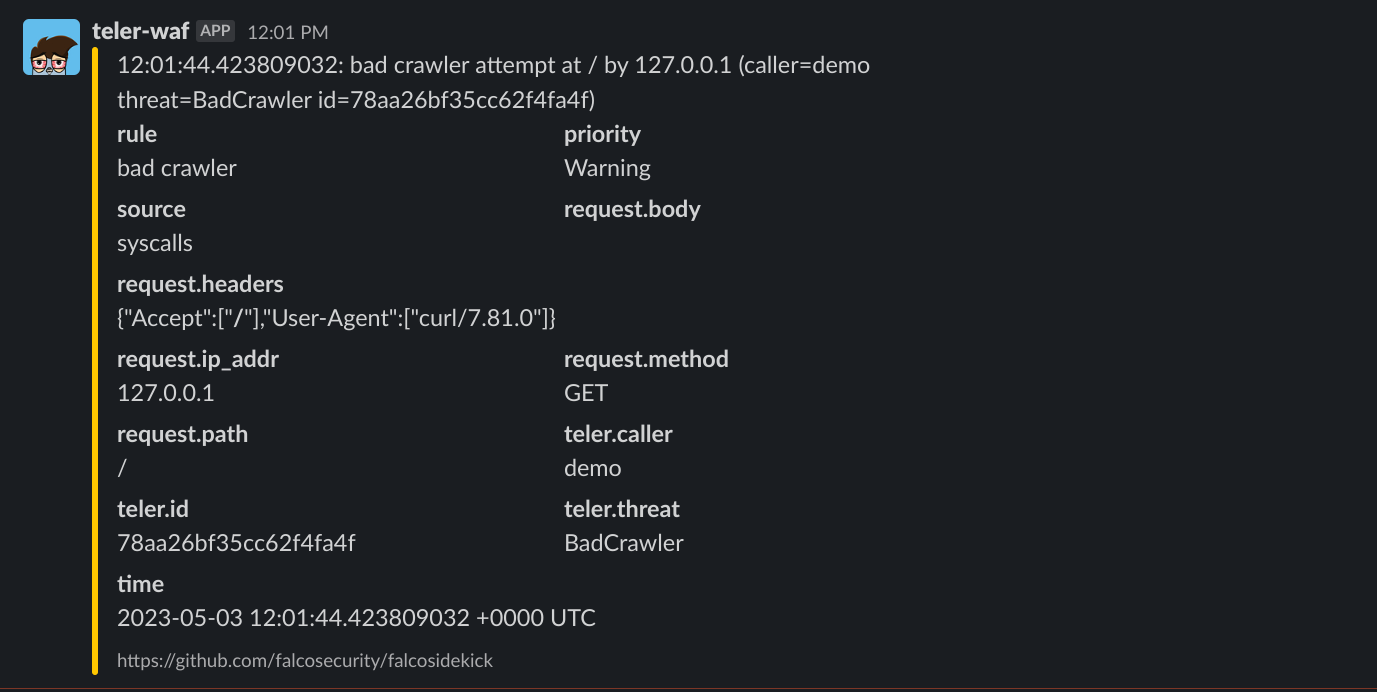 teler-sh/teler-waf
teler-waf is a Go HTTP middleware that protects local web services from OWASP Top 10 threats, known vulnerabilities, malicious actors, botnets,…
 michaelsanford/log4shell-honeypot
Dockerized honeypot for CVE-2021-44228.
 jconeby/elastic-peak-dashboards
PEAK Baseline Threat Hunt dashboards for Security Onion 3.0 — covering DNS, HTTP, TLS, SMB, Kerberos, SSH, RDP, DCE/RPC, LDAP, Modbus, DNP3,…
 lopqto/cve-2021-41773_honeypot
Lightweight honeypot for Apache HTTP Server path traversal vulnerability CVE-2021-41773, designed to capture and log exploitation attempts.
 offseckit/cve-2026-24207
CVE-2026-24207 — NVIDIA Triton SageMaker auth bypass to unauth RCE. Detection script, bypass demo, RCE-chain PoC, and IDS rules.
 nosie12/fire-wall-server
Python-based simulated firewall to detect and block Spring4Shell (CVE-2022-22965) exploit attempts. This project filters HTTP requests by identifying…
 elshaheedy/cve-2025-29927-sigma-rule
Sigma rule for detecting CVE-2025-29927 exploitation via suspicious x-middleware-subrequest HTTP headers in Next.js applications, with detection…
 0x4d31/galah
Galah: An LLM-powered web honeypot.
 corelight/cve-2021-31166
Detection rules (Suricata + Zeek) for CVE-2021-31166 HTTP Protocol Stack vulnerability, providing network-level alerts on exploit attempts against…
 corelight/cve-2022-21907
Zeek package to detect CVE-2022-21907 HTTP exploit attempts by analyzing packet captures for malformed requests and triggering alerts.