OSCP Notes and Custom Dashboard

OSCP notes vault + exam cockpit dashboard: merged technique notes, variable-filled command decks, machines, creds, and runbook for exam day. MIT.

OSCP notes vault + exam cockpit dashboard: merged technique notes, variable-filled command decks, machines, creds, and runbook for exam day. MIT.

Custom Bash and Python scripts used to automate various penetration testing tasks including recon, scanning, enumeration, and malicious payload…

A collection of custom security tools for quick needs.

High-speed API and web content discovery tool that bruteforces routes using compiled Swagger datasets, supporting depth scanning, custom wordlists,…

Search Google/Bing/Ecosia/DuckDuckGo/Yandex/Yahoo for a search term (dork) with a default set of websites, bug bounty programs or custom collection.

Advanced search in search engines, enables analysis provided to exploit GET / POST capturing emails & urls, with an internal custom validation…

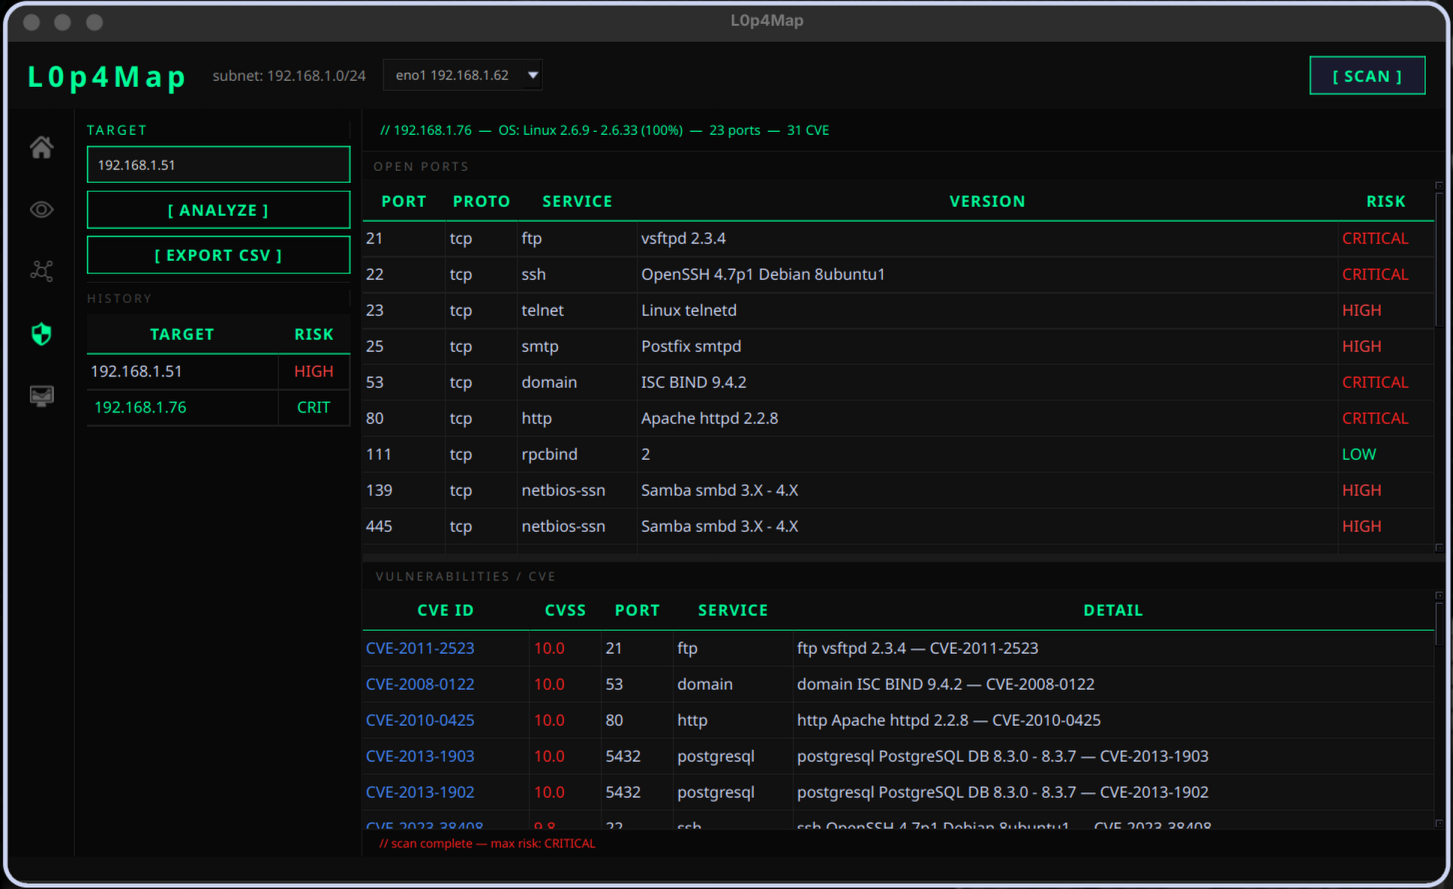
Professional network monitoring & visualization tool. L0P4Map combines high-speed ARP discovery with full nmap integration and a real-time…

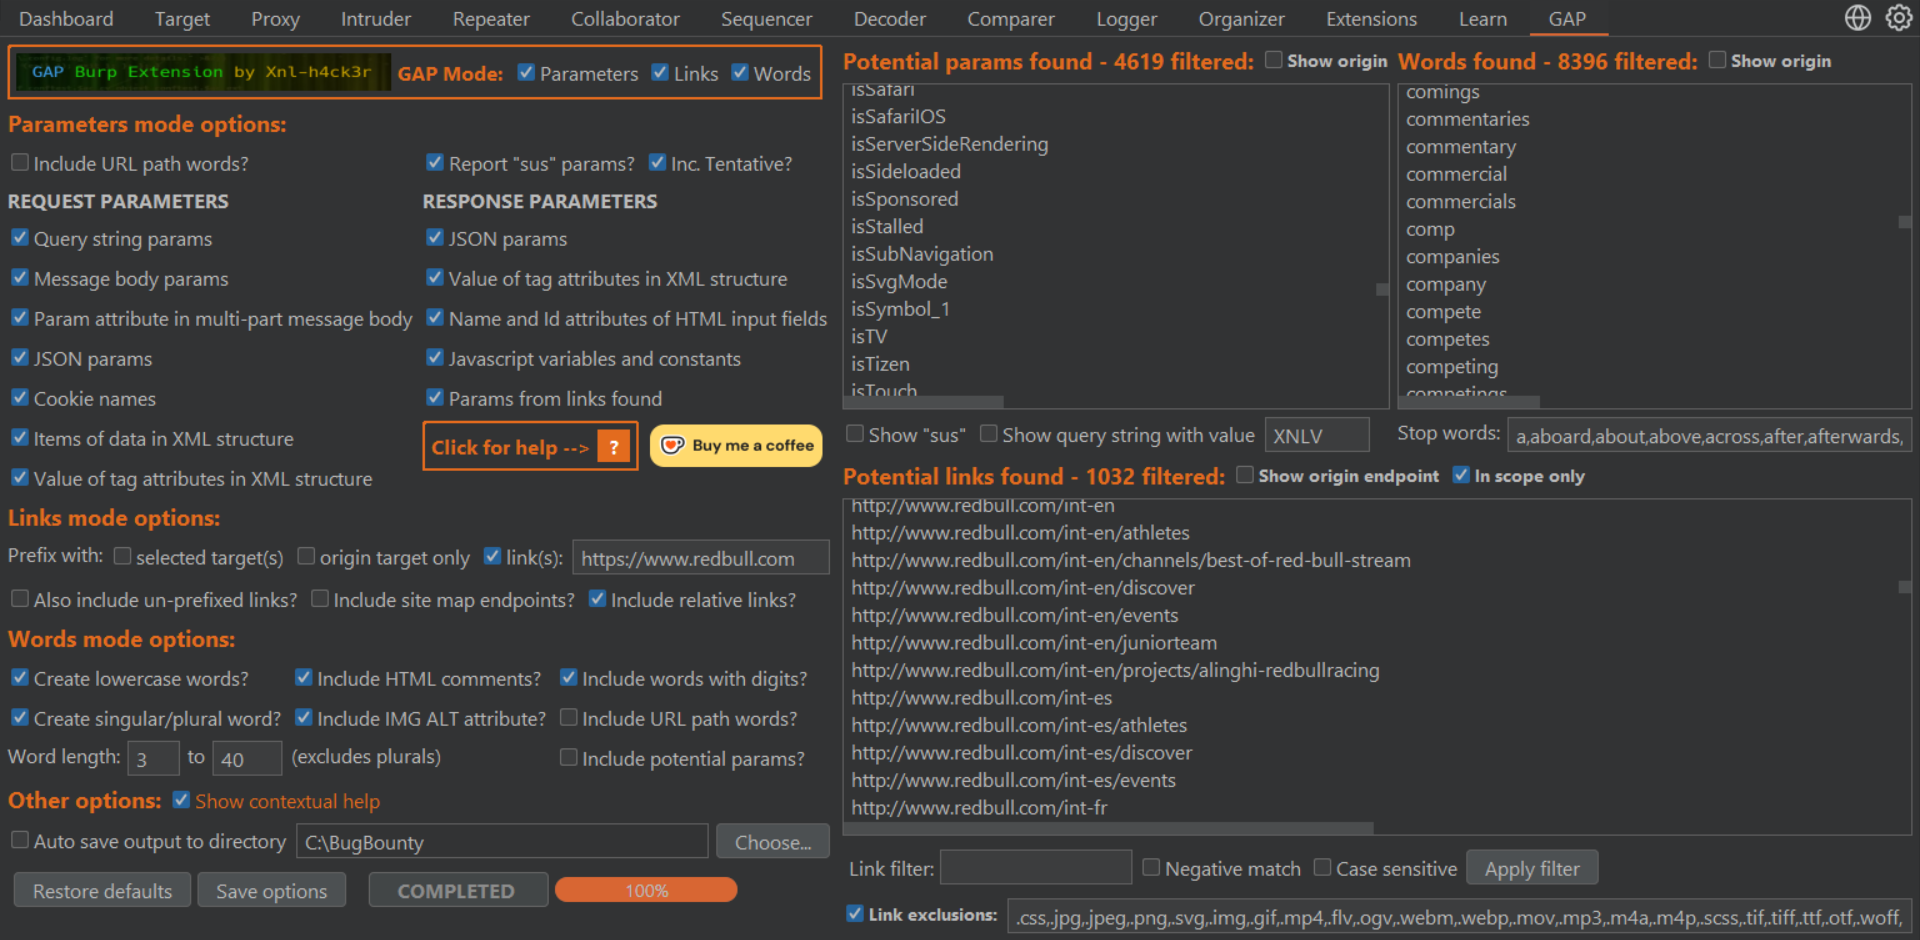
Burp Extension to find potential endpoints, parameters, and generate a custom target wordlist

A standalone python script which utilizes python's built-in modules to enumerate SUID binaries, separate default binaries from custom binaries,…

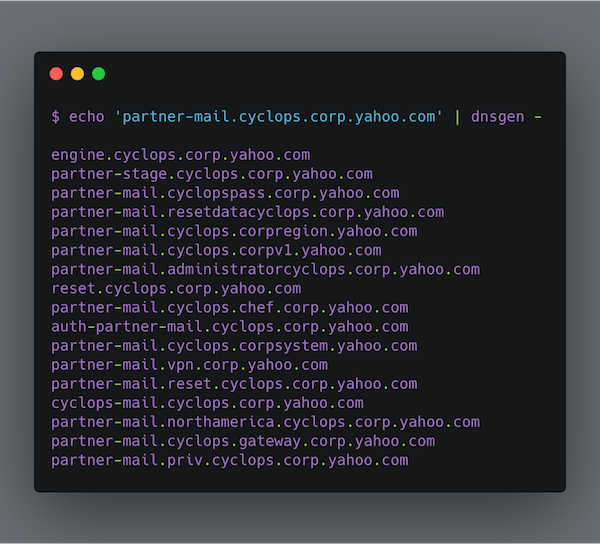
Generates domain name permutations for subdomain enumeration and recon, supporting custom wordlists, cloud patterns, and fast mode for security…

Suite of tools for BloodHound that enables domain password auditing, privilege path analysis, edge manipulation, and custom Cypher queries to…

Concurrent CLI tool for discovering secrets, API keys, and links in JavaScript files during web reconnaissance, with custom regex pattern support and…

Concurrent web directory and file brute-forcing tool that performs HEAD requests against a target URL using a wordlist, with support for custom…

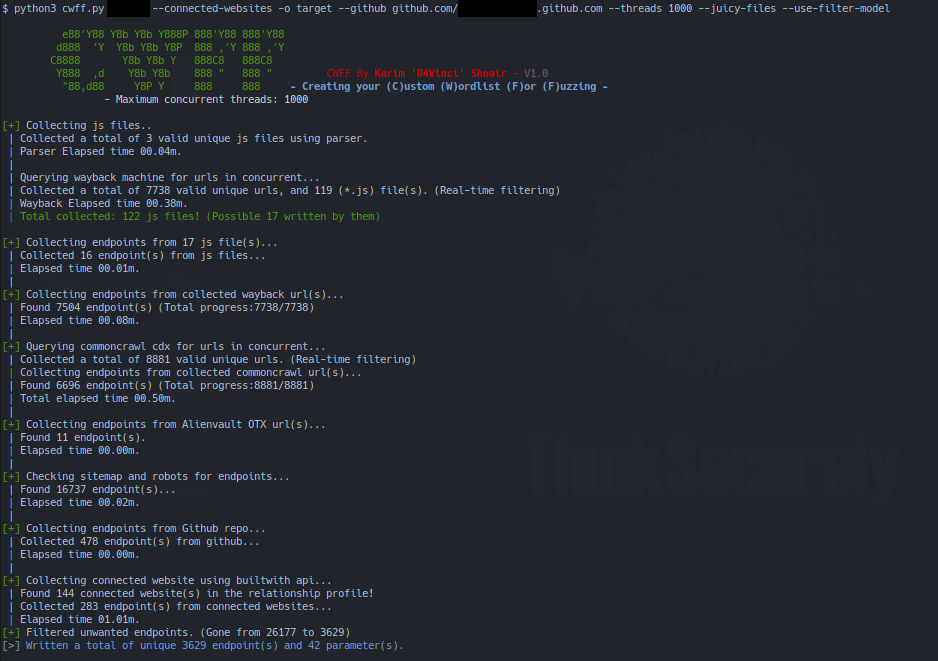
Create your Custom Wordlist For Fuzzing

Brute-force tool for discovering hidden GET and POST parameters in web applications, supporting custom wordlists and concurrent requests.

BucketLoot is an automated S3-compatible bucket inspector that can help users extract assets, flag secret exposures and even search for custom…

Correlates NTLM hashes, BloodHound data, and cracked passwords for Active Directory penetration testing. Imports NTDS.dit, syncs to Neo4j, analyzes…

This tool is design to find admin panel of any website by using custom wordlist or default wordlist easily and allow you to find admin panel trough a…