

SwaggerSpy
 undeadsec/swaggerspy
Automated OSINT tool that scans SwaggerHub API documentation to discover exposed secrets, credentials, and sensitive information using regex-based…
api-securityinformation-gatheringosint+1
321
undeadsec/swaggerspyAutomated OSINT tool that scans SwaggerHub API documentation to discover exposed secrets, credentials, and sensitive information using regex-based…
 jiangsir404/poc-s
POC-T强化版本 POC-S , 用于红蓝对抗中快速验证Web应用漏洞, 对功能进行强化以及脚本进行分类添加,自带dnslog等, 平台补充来自vulhub靶机及其他开源项目的高可用POC
 bountystrike/bountystrike-sh
Poor (rich?) man's bug bounty pipeline https://dubell.io
 noptrix/lulzbuster
A multithreaded, very fast and smart HTTP(S) directory and file bruteforcer written in C on top of libcurl
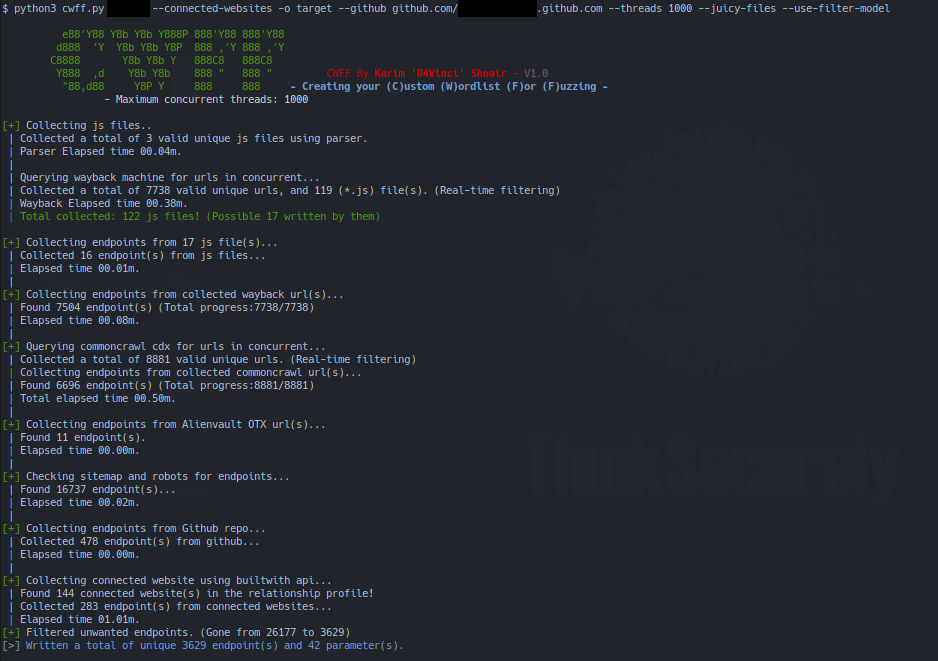 d4vinci/cwff
Create your Custom Wordlist For Fuzzing
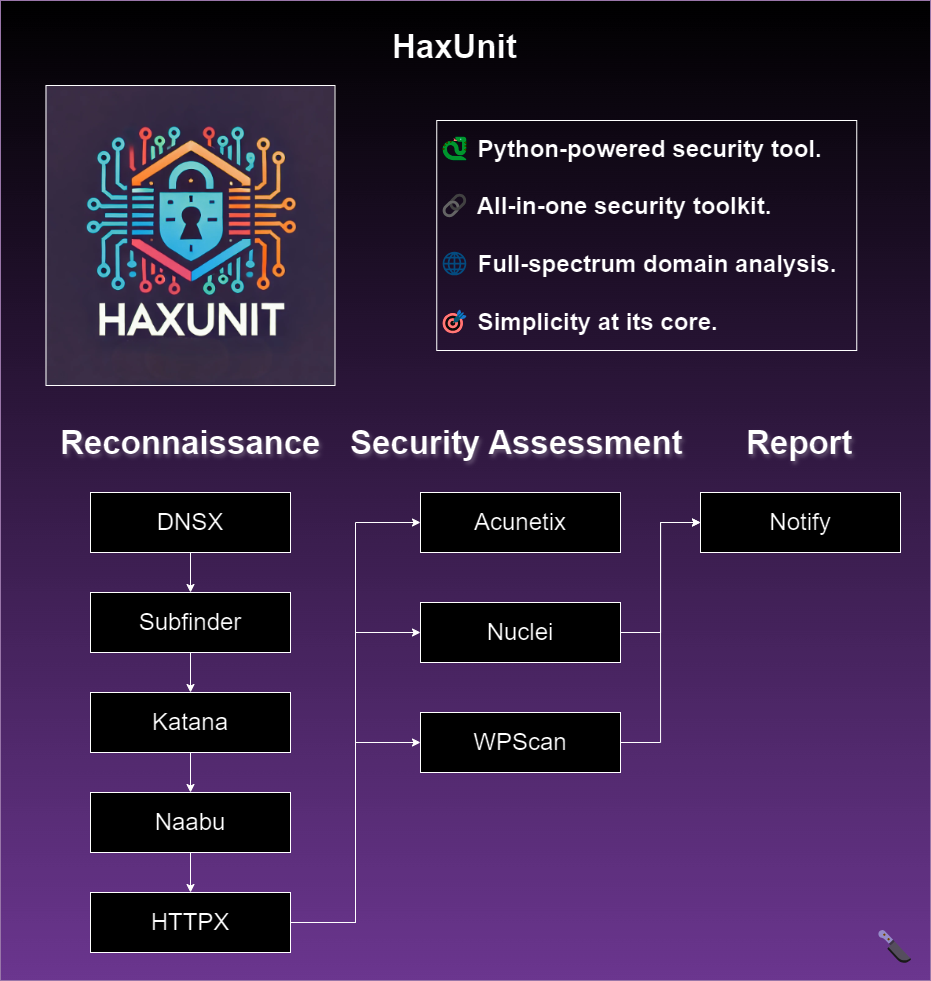 bandit-haxunit/haxunit
Automated web domain reconnaissance and security assessment tool integrating subdomain enumeration, port scanning, vulnerability scanning, and…
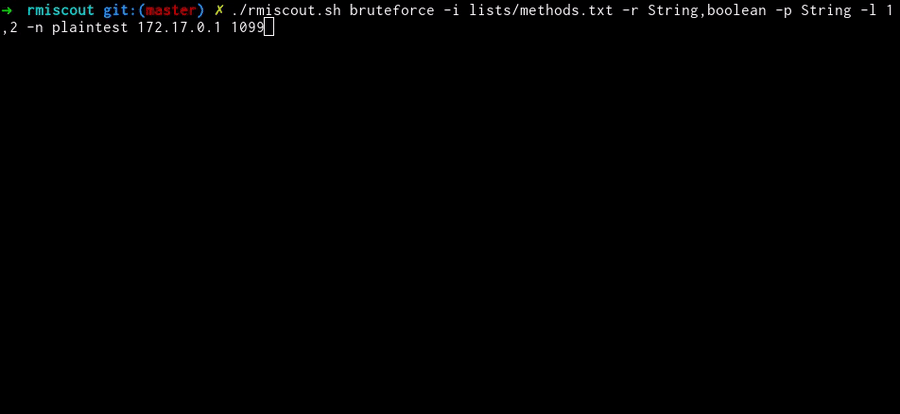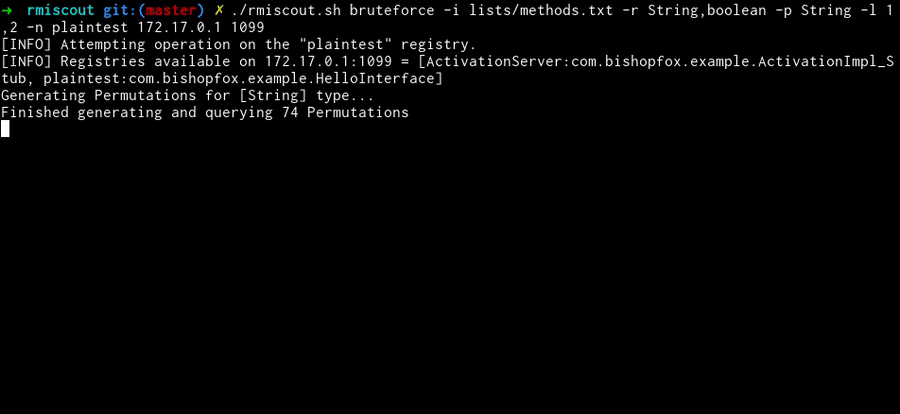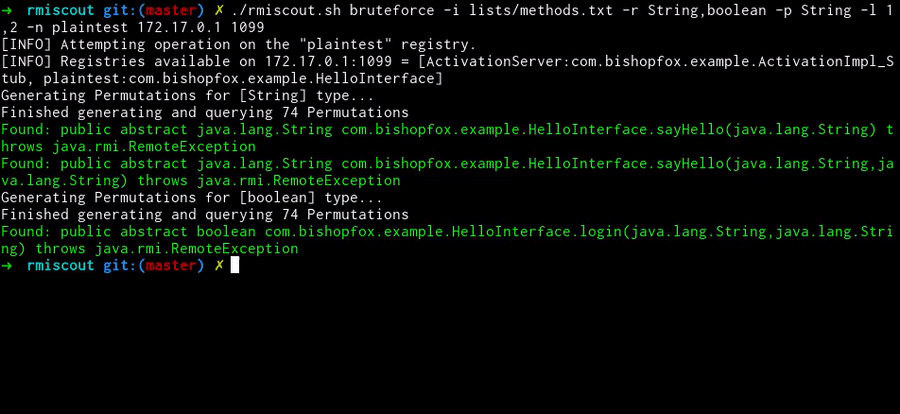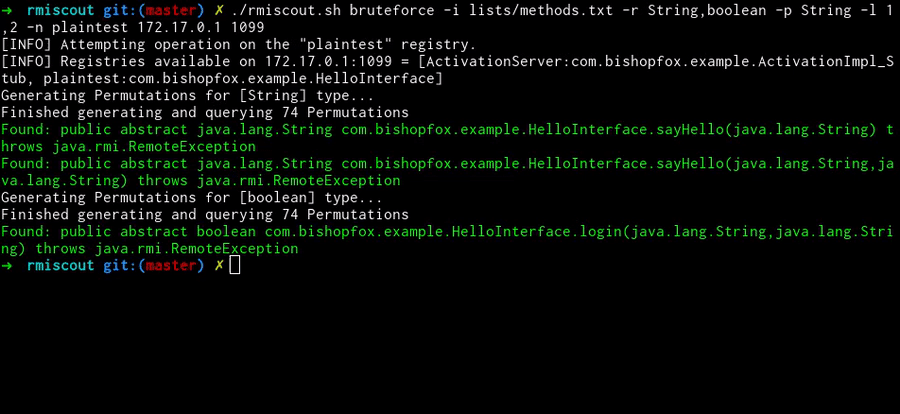 bishopfox/rmiscout
RMIScout uses wordlist and bruteforce strategies to enumerate Java RMI functions and exploit RMI parameter unmarshalling vulnerabilities
 th0h0/autossrf
Smart context-based SSRF vulnerability scanner.
 bo0om/parampampam
Brute-force tool for discovering hidden GET and POST parameters in web applications, supporting custom wordlists and concurrent requests.
 pwnwriter/kanha
🦚 A web-app pentesting suite written in rust .
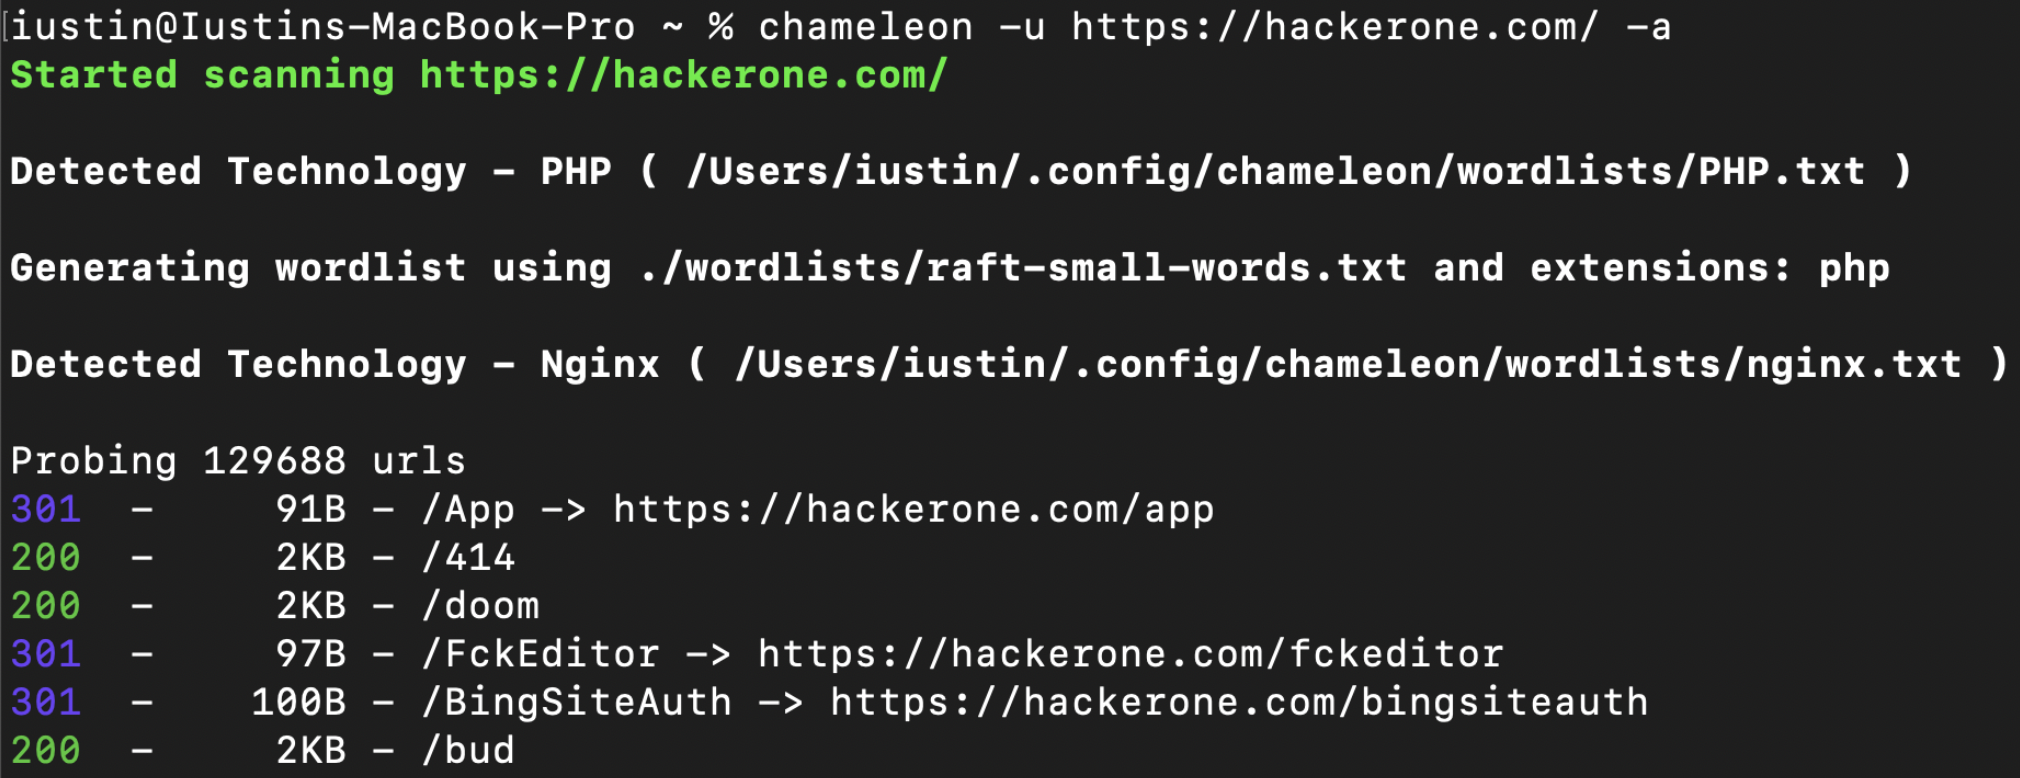 iustin24/chameleon
Technology-aware web content discovery scanner: detects Wappalyzer fingerprints, adapts wordlists/extensions, and performs fast directory bruteforce…
 nccgroup/blesuite
BLESuite is a Python package that provides an easier way to test Bluetooth Low Energy (BLE) device
 net-hunter121/api-wordlist
Curated wordlists of API function names, verbs, and nouns for fuzzing web application endpoints with Burp Suite Intruder.
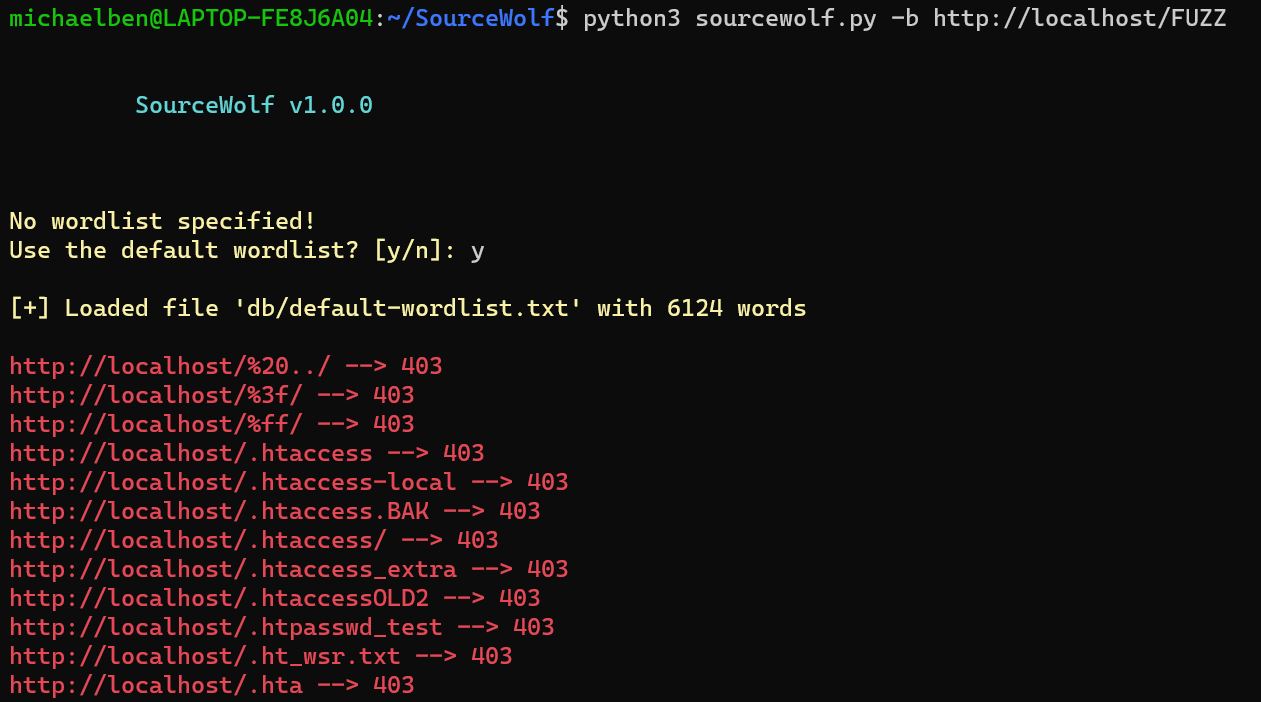 ksharinarayanan/sourcewolf
Amazingly fast response crawler to find juicy stuff in the source code! 😎🔥
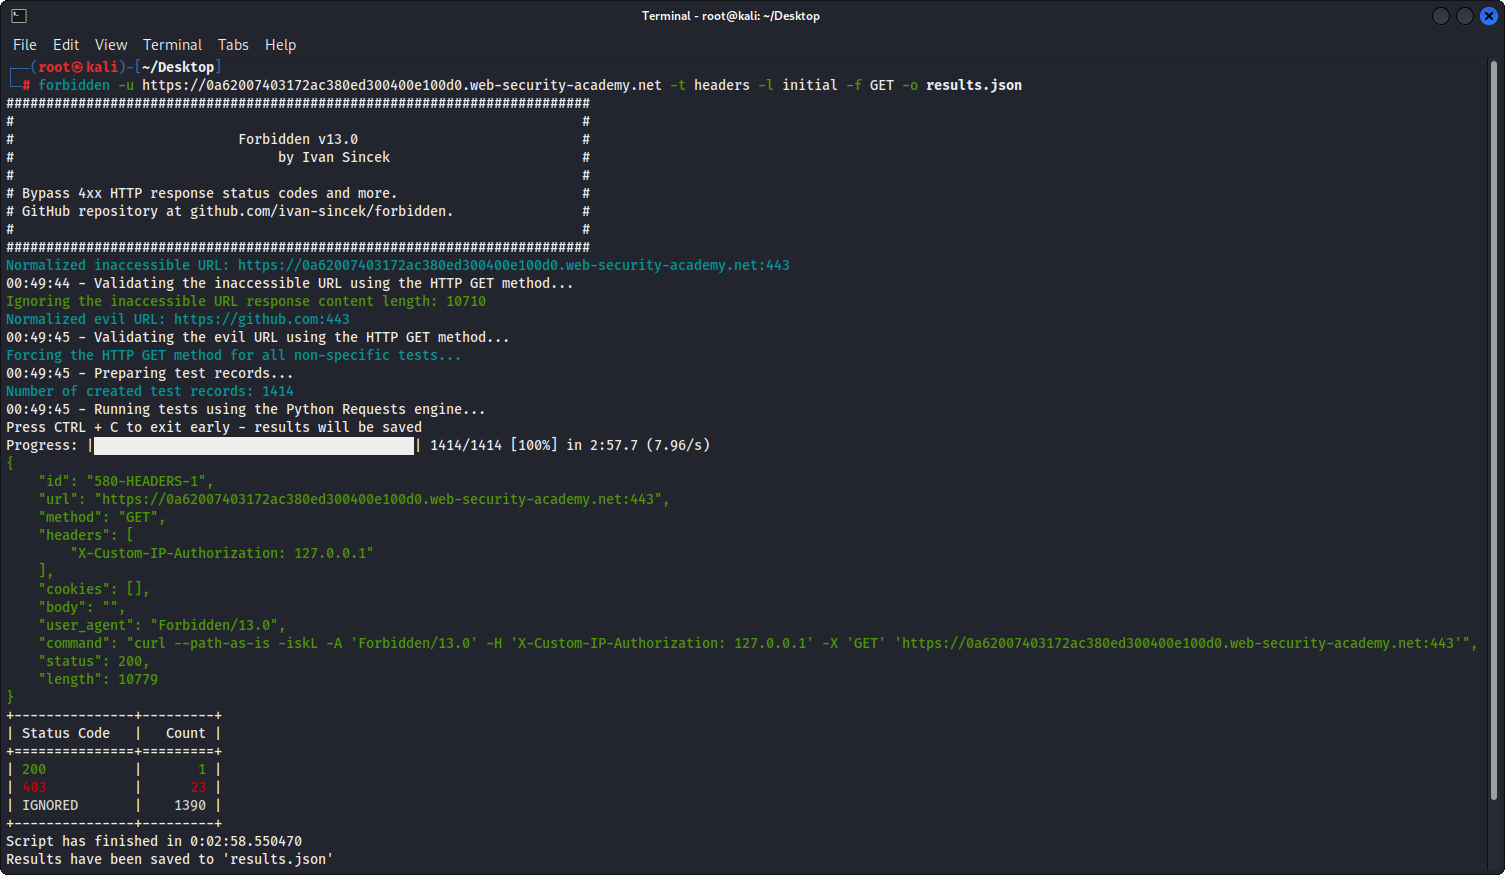 ivan-sincek/forbidden
Bypass 4xx HTTP response status codes and more. The tool is based on Python Requests, PycURL, and HTTP Client.
 thumpbo/cve-2025-30208-exp
CVE-2025-30208-EXP
 dirsoooo/recon
Recon is a script to perform a full recon on a target with the main tools to search for vulnerabilities. Created based on @ofjaaah and @Jhaddix…
 akabe1/oauthscan
Burp Suite Extension useful to verify OAUTHv2 and OpenID security