Admin-Panel_Finder
Burp Suite extension that finds exposed admin panels and login pages of web applications and infrastructure. 1,000+ payloads, OWASP WSTG-CONF-05.

Burp Suite extension that finds exposed admin panels and login pages of web applications and infrastructure. 1,000+ payloads, OWASP WSTG-CONF-05.

Penetration tests guide based on OWASP including test cases, resources and examples.

A OWASP Based Checklist With 80+ Test Cases

Vendor-neutral cloud security testing guide with structured phases for enumeration, privilege escalation, lateral movement, and post-exploitation…

OWASP Web Security Testing Guide RAG system with ChromaDB, MCP for Claude Code

Finds internet-exposed resources in an AWS account

Proof-of-concept exploit for CVE-2026-26012, demonstrating an authenticated organization collection permissions bypass and cipher enumeration in…

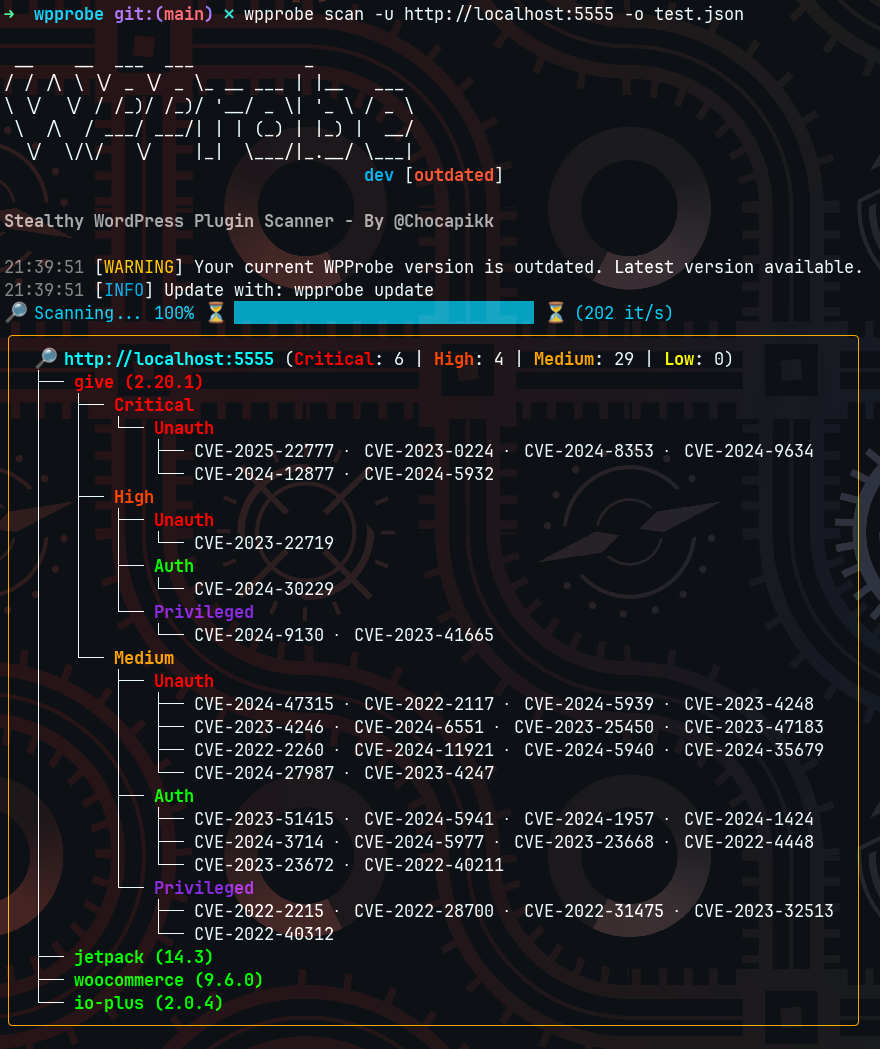
A fast WordPress plugin enumeration tool

A Security Tool for Enumerating WebSockets

A multi threaded Python script designed to brute force directories and files names on webservers.

Insecure TeamCity CI environment for hands-on penetration testing training: reconnaissance, credential theft, privilege escalation, and lateral…

Custom Bash and Python scripts used to automate various penetration testing tasks including recon, scanning, enumeration, and malicious payload…

Opensource, cross-platform and portable toolkit for automating routine processes when carrying out various works for testing!

MAPS cloud scanner and response parser for Microsoft Defender research.

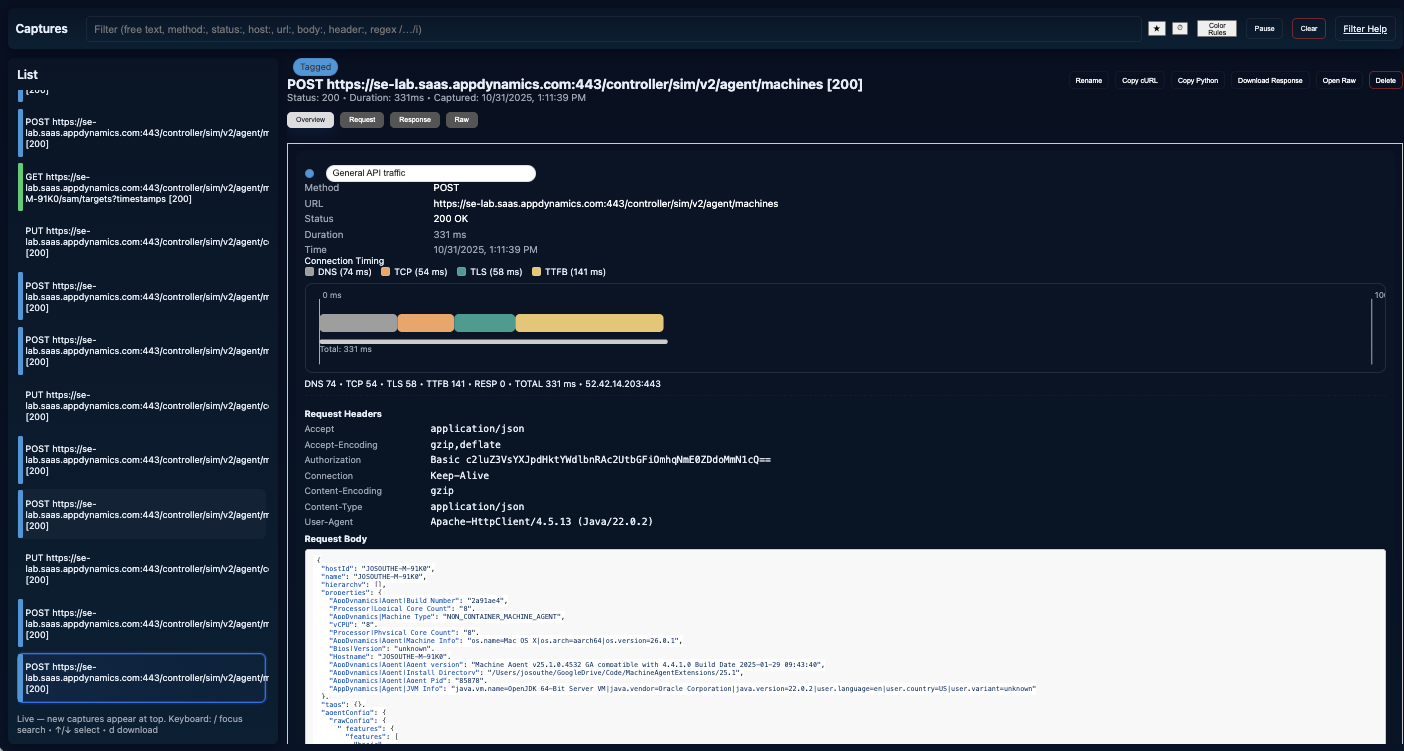
HTTP Proxy Analysis for reverse engineering protocol communication

find sensitive data leaking from ServiceNow instances.

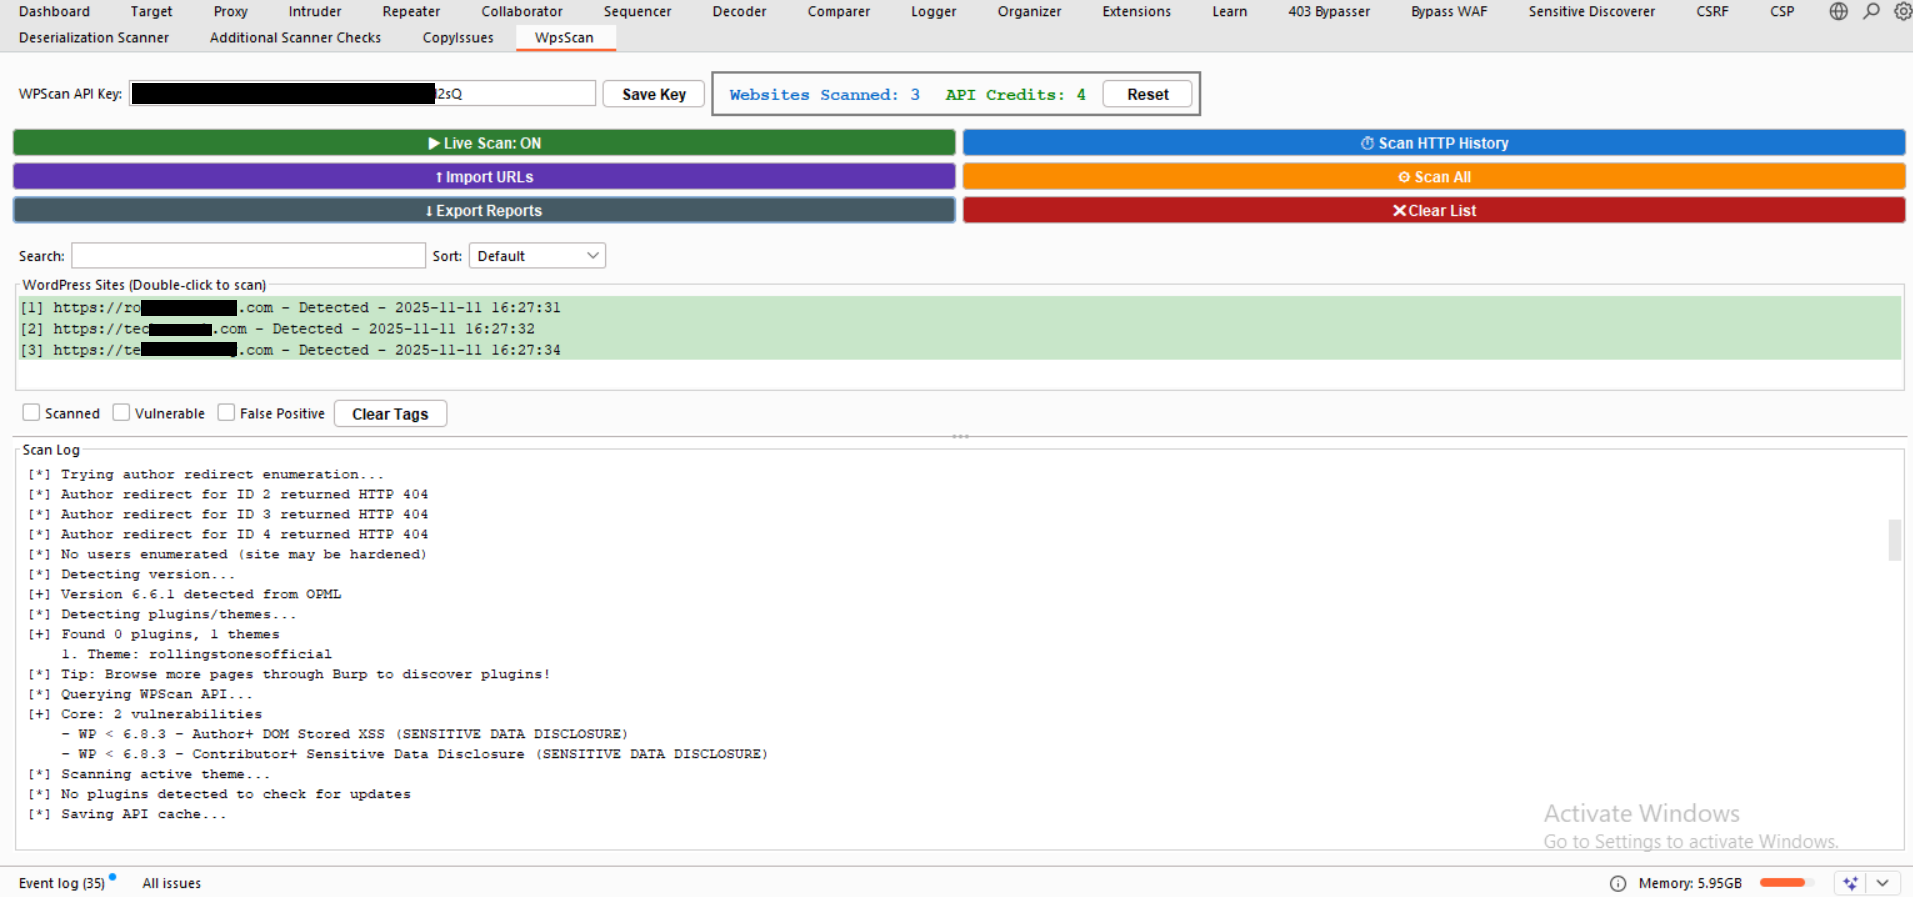
Burp extension for wordpress security scanning

Asynchronous WordPress security scanner with WAF bypass via headless browser. Enumerates plugins, themes, users, and multisite installations with…