Data-Shield_IPv4_Blocklist

Curated IPv4 blocklist of malicious addresses, refreshed every 6 hours for firewall and WAF ingestion, with split lists and CTI-ready formats for…

Curated IPv4 blocklist of malicious addresses, refreshed every 6 hours for firewall and WAF ingestion, with split lists and CTI-ready formats for…

Rust-based XSS scanner with context-aware payload selection, WAF detection and bypass, crawling, blind XSS callbacks, and static DOM sink analysis.

Automated WAF assessment tool that detects firewall vendors, tests 19 attack categories with advanced evasion payloads, and provides color-coded…

Open-source web security testing platform: proxy, scanner and fuzzer in one CLI. By Pennacle Security.

evilwaf is a penetration testing tool designed to detect and bypass common Web Application Firewalls (WAFs).

Stop getting 403 Forbidden. A specialized httpx-like toolkit for WAF evasion.

OWASP Web Recon & Directory Discovery Platform

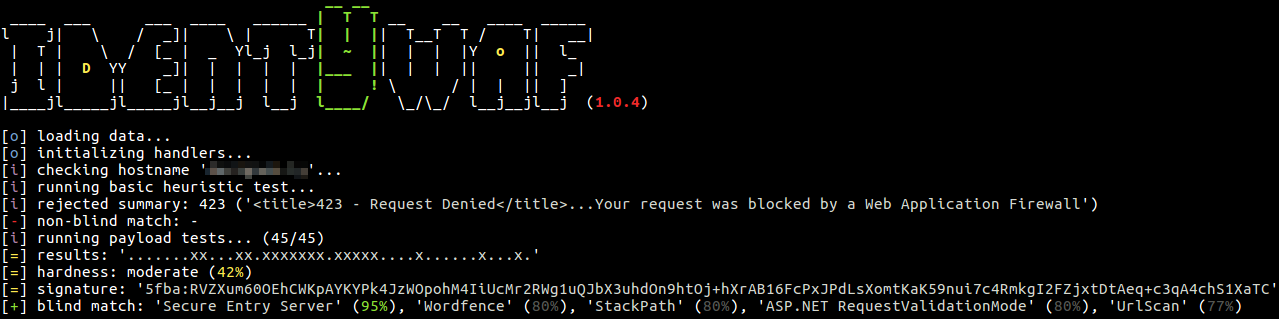
Blind WAF identification tool

🛡️ High-performance WAF & CDN detection tool. Identify protection layers (Cloudflare, Akamai, AWS, Fastly, and more), run effectiveness and…

Terminal UI for browsing and replaying AWS WAF v2 logs from CloudWatch, S3, and the sampling API, with YAML filtering, auth detection, and…

Automated reconnaissance framework with 17+ modules for subdomain enumeration, directory brute-forcing, JS/link mining, WAF fingerprinting, and…

Lightweight web-attack monitor. One Go binary + SQLite. Not OSSEC, not a WAF.

Automated Web Application Firewall fingerprinting tool that identifies and detects over 200 WAF products by analyzing HTTP responses to normal and…

Asynchronous WordPress security scanner with WAF bypass via headless browser. Enumerates plugins, themes, users, and multisite installations with…

Tests your WAF with +160 payloads

Go tool that passively discovers the real origin IP behind a WAF/CDN using multiple OSINT sources, then verifies candidates via HTML similarity, SSL…

Advanced security testing tool for CVE-2025-55182 vulnerability assessment in Next.js applications. Features interactive shell, batch scanning, WAF…

Remote detection tool for OWASP Core Rule Set version and paranoia level on ModSecurity WAFs, aiding security posture assessment.