Big-Ass-Data-Broker-Opt-Out-List

Curated, community-maintained directory of data broker opt-out instructions to help individuals remove personal information from people-search sites…

Curated, community-maintained directory of data broker opt-out instructions to help individuals remove personal information from people-search sites…

Fast passive subdomain enumeration tool.

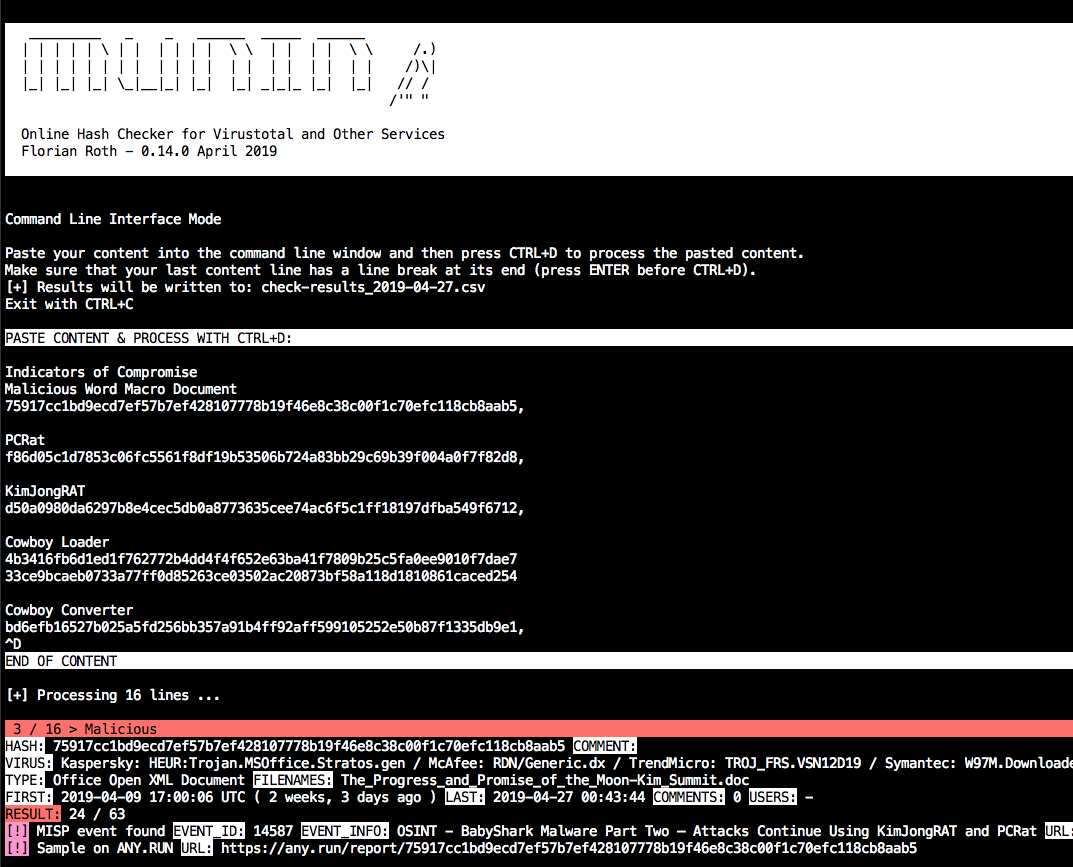
Online hash checker for Virustotal and other services

Fast, accurate subdomain takeover scanner with zero false positives. Detects vulnerable subdomains, collects metadata (IP, CNAME, title, status…

Search and download public exploits from the Vulners database — online, or fully offline from a local SQLite FTS5 index.

WooCommerce Designer Pro <= 1.9.28 - Unauthenticated Arbitrary File Read

CVE-2026-5513: Bookly <= 27.2 Stored XSS via Cookie (Unauthenticated)

IPGhost is a strong tool for ethical hackers. This tool automatically changes your IP address , making it hard for anyone to track your online…

Just a silly recon tool that uses data from SSL Certificates to find potential host names

Proof of concept demonstrating unauthenticated access to user resumes via directory listing in CodeAstro Online Job Portal, with reproduction steps…

Privacy-first behavioral intelligence framework for multi-platform analysis and sociodynamic research.

Crawlector is a threat hunting framework designed for scanning websites for malicious objects.

Passive subdomain discovery tool that aggregates results from multiple online sources via CLI, supporting stdin/stdout, JSONL output, and API key…

RestroPress – Online Food Ordering System 3.0.0 - 3.1.9.2 - Unauthenticated Information Exposure to Authentication Bypass via Forged JWT

Exploit blind SQL Injection in (Online Learning Management System)

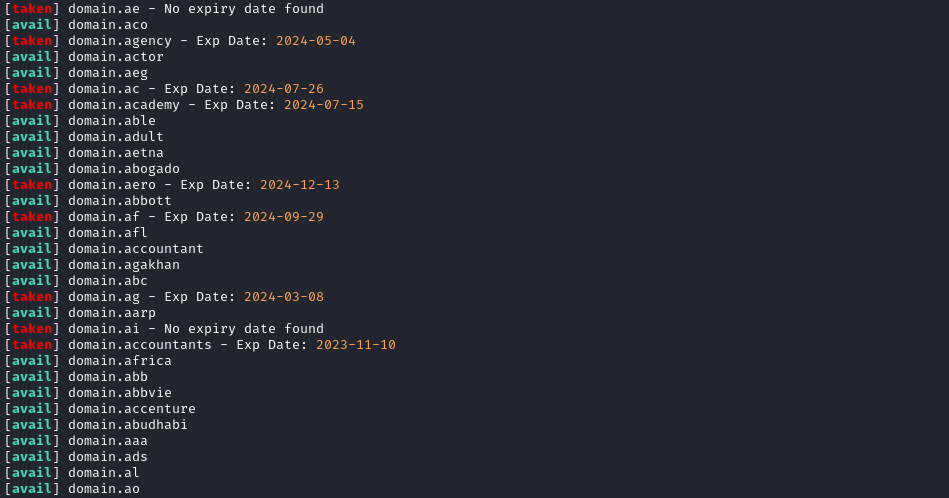
Bash-based domain availability checker that scans WHOIS records across multiple TLDs to find unregistered domains for red teaming and phishing…

SQL Injection in Online Shopping System Advanced (CVE-2025-51970)

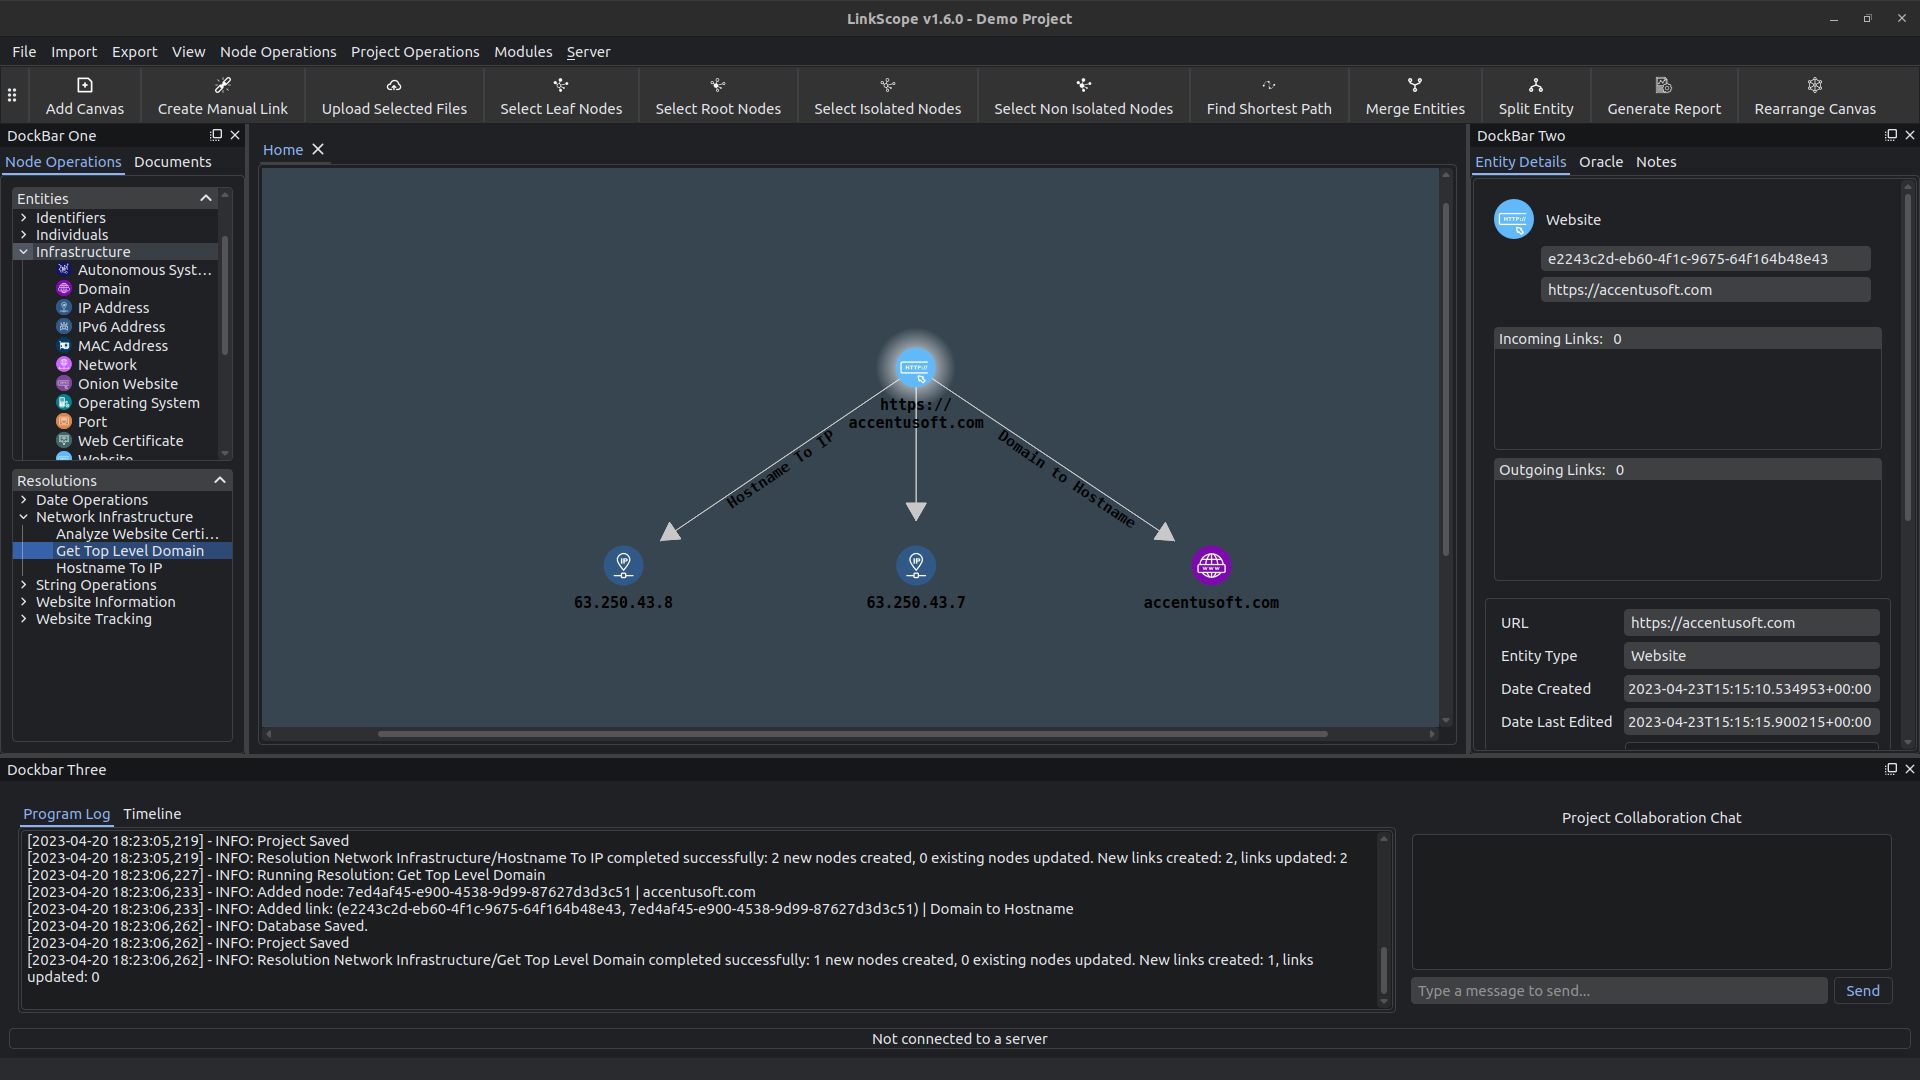
Repository for the LinkScope Client software.