
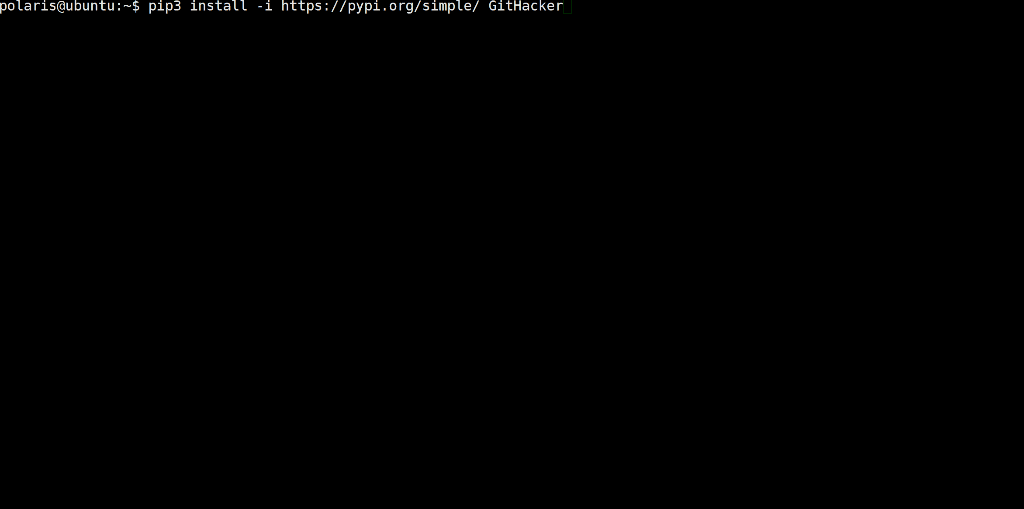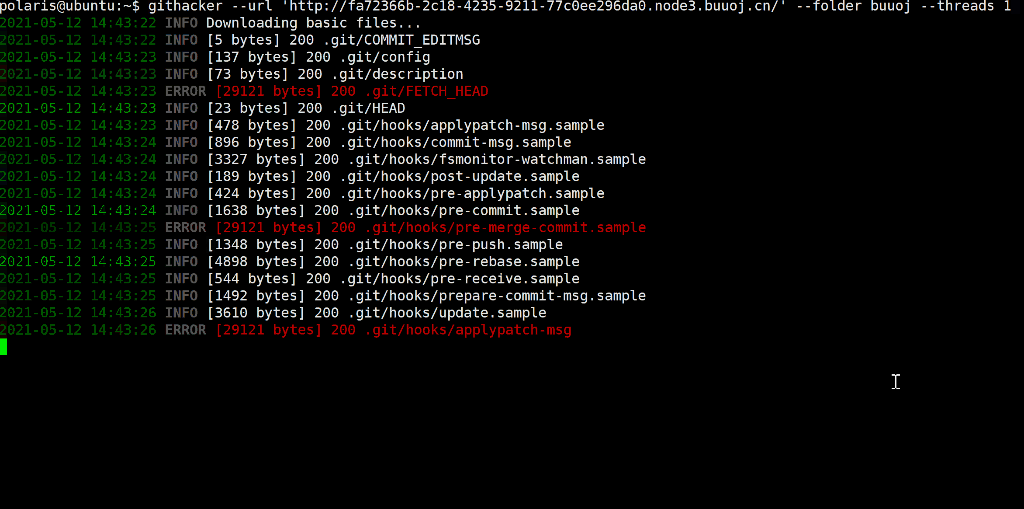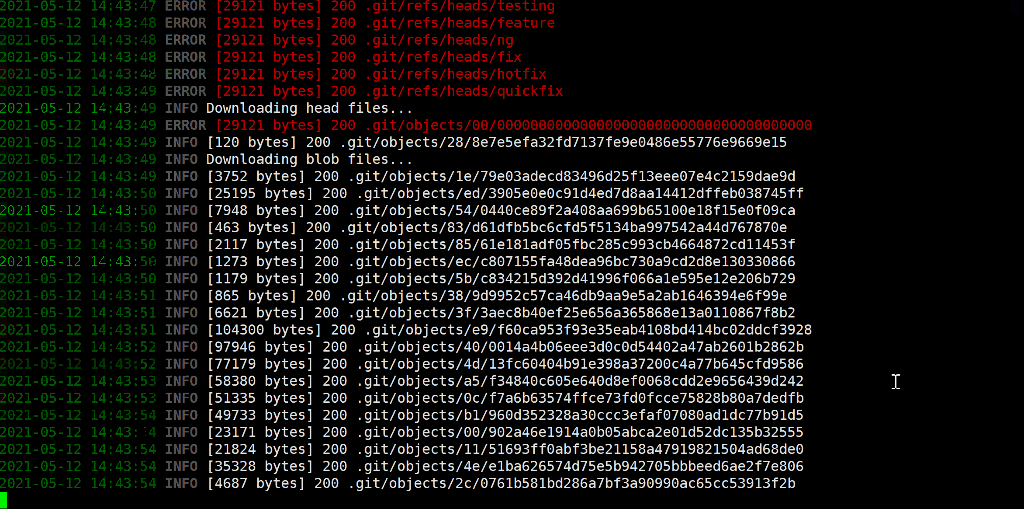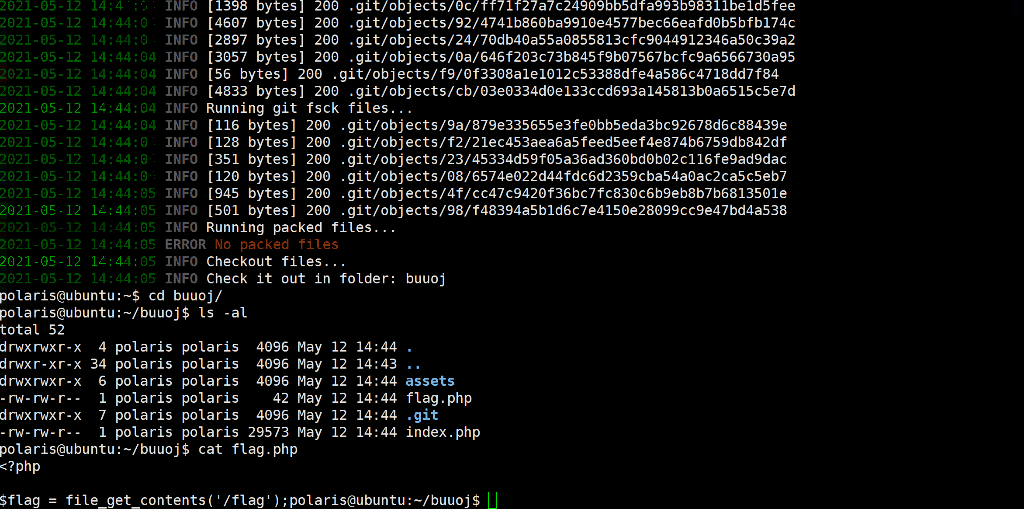
GitHacker
 wangyihang/githacker
🕷️ A `.git` folder exploiting tool that is able to restore the entire Git repository, including stash, common branches and common tags.
information-gatheringpenetration-testingreconnaissance+2
1.7k
wangyihang/githacker🕷️ A `.git` folder exploiting tool that is able to restore the entire Git repository, including stash, common branches and common tags.
 soxoj/gitcolombo
🧬 Extract and analyze contributors info from git repos
 arthaud/git-dumper
A tool to dump a git repository from a website
 rndhouse/vcamper
PoC: identify silent security patches before CVE
 expel-io/expel-intel
This is the home of the Expel Intel Team. Here, we will share IOCs and other information that is either not suitable for fitting into other mediums…
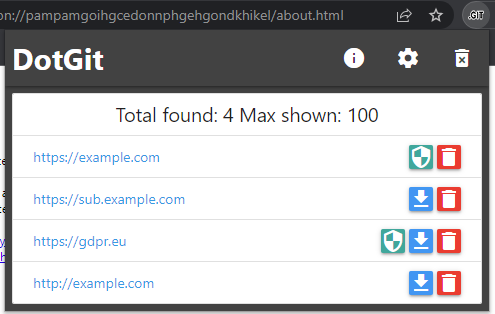 davtur19/dotgit
An extension for checking if .git is exposed in visited websites
 ebryx/gitdump
A pentesting tool that dumps the source code from .git even when the directory traversal is disabled
 0xdak/cve-2026-44881_exploit
Single-script exploit for CVE-2026-44881 that chains .git credential leakage, Portainer Git-symlink injection, arbitrary host file read, and SSH…
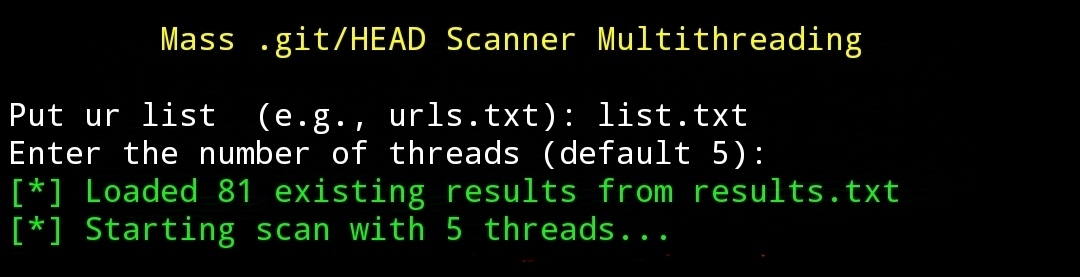 jenderal92/git-scan
This tool is designed to scan and identify whether a website has an exposed ".git" directory, which may contain sensitive information such as source…
 jenderal92/git-dump
This script is a tool to recursively download the contents of the '.git' directory from a website. Using Python and libraries like 'requests' and…
 teycir/diffcatcher
A Rust CLI tool that recursively discovers Git repositories, captures state changes, generates diffs, extracts code elements with full snippets, and…
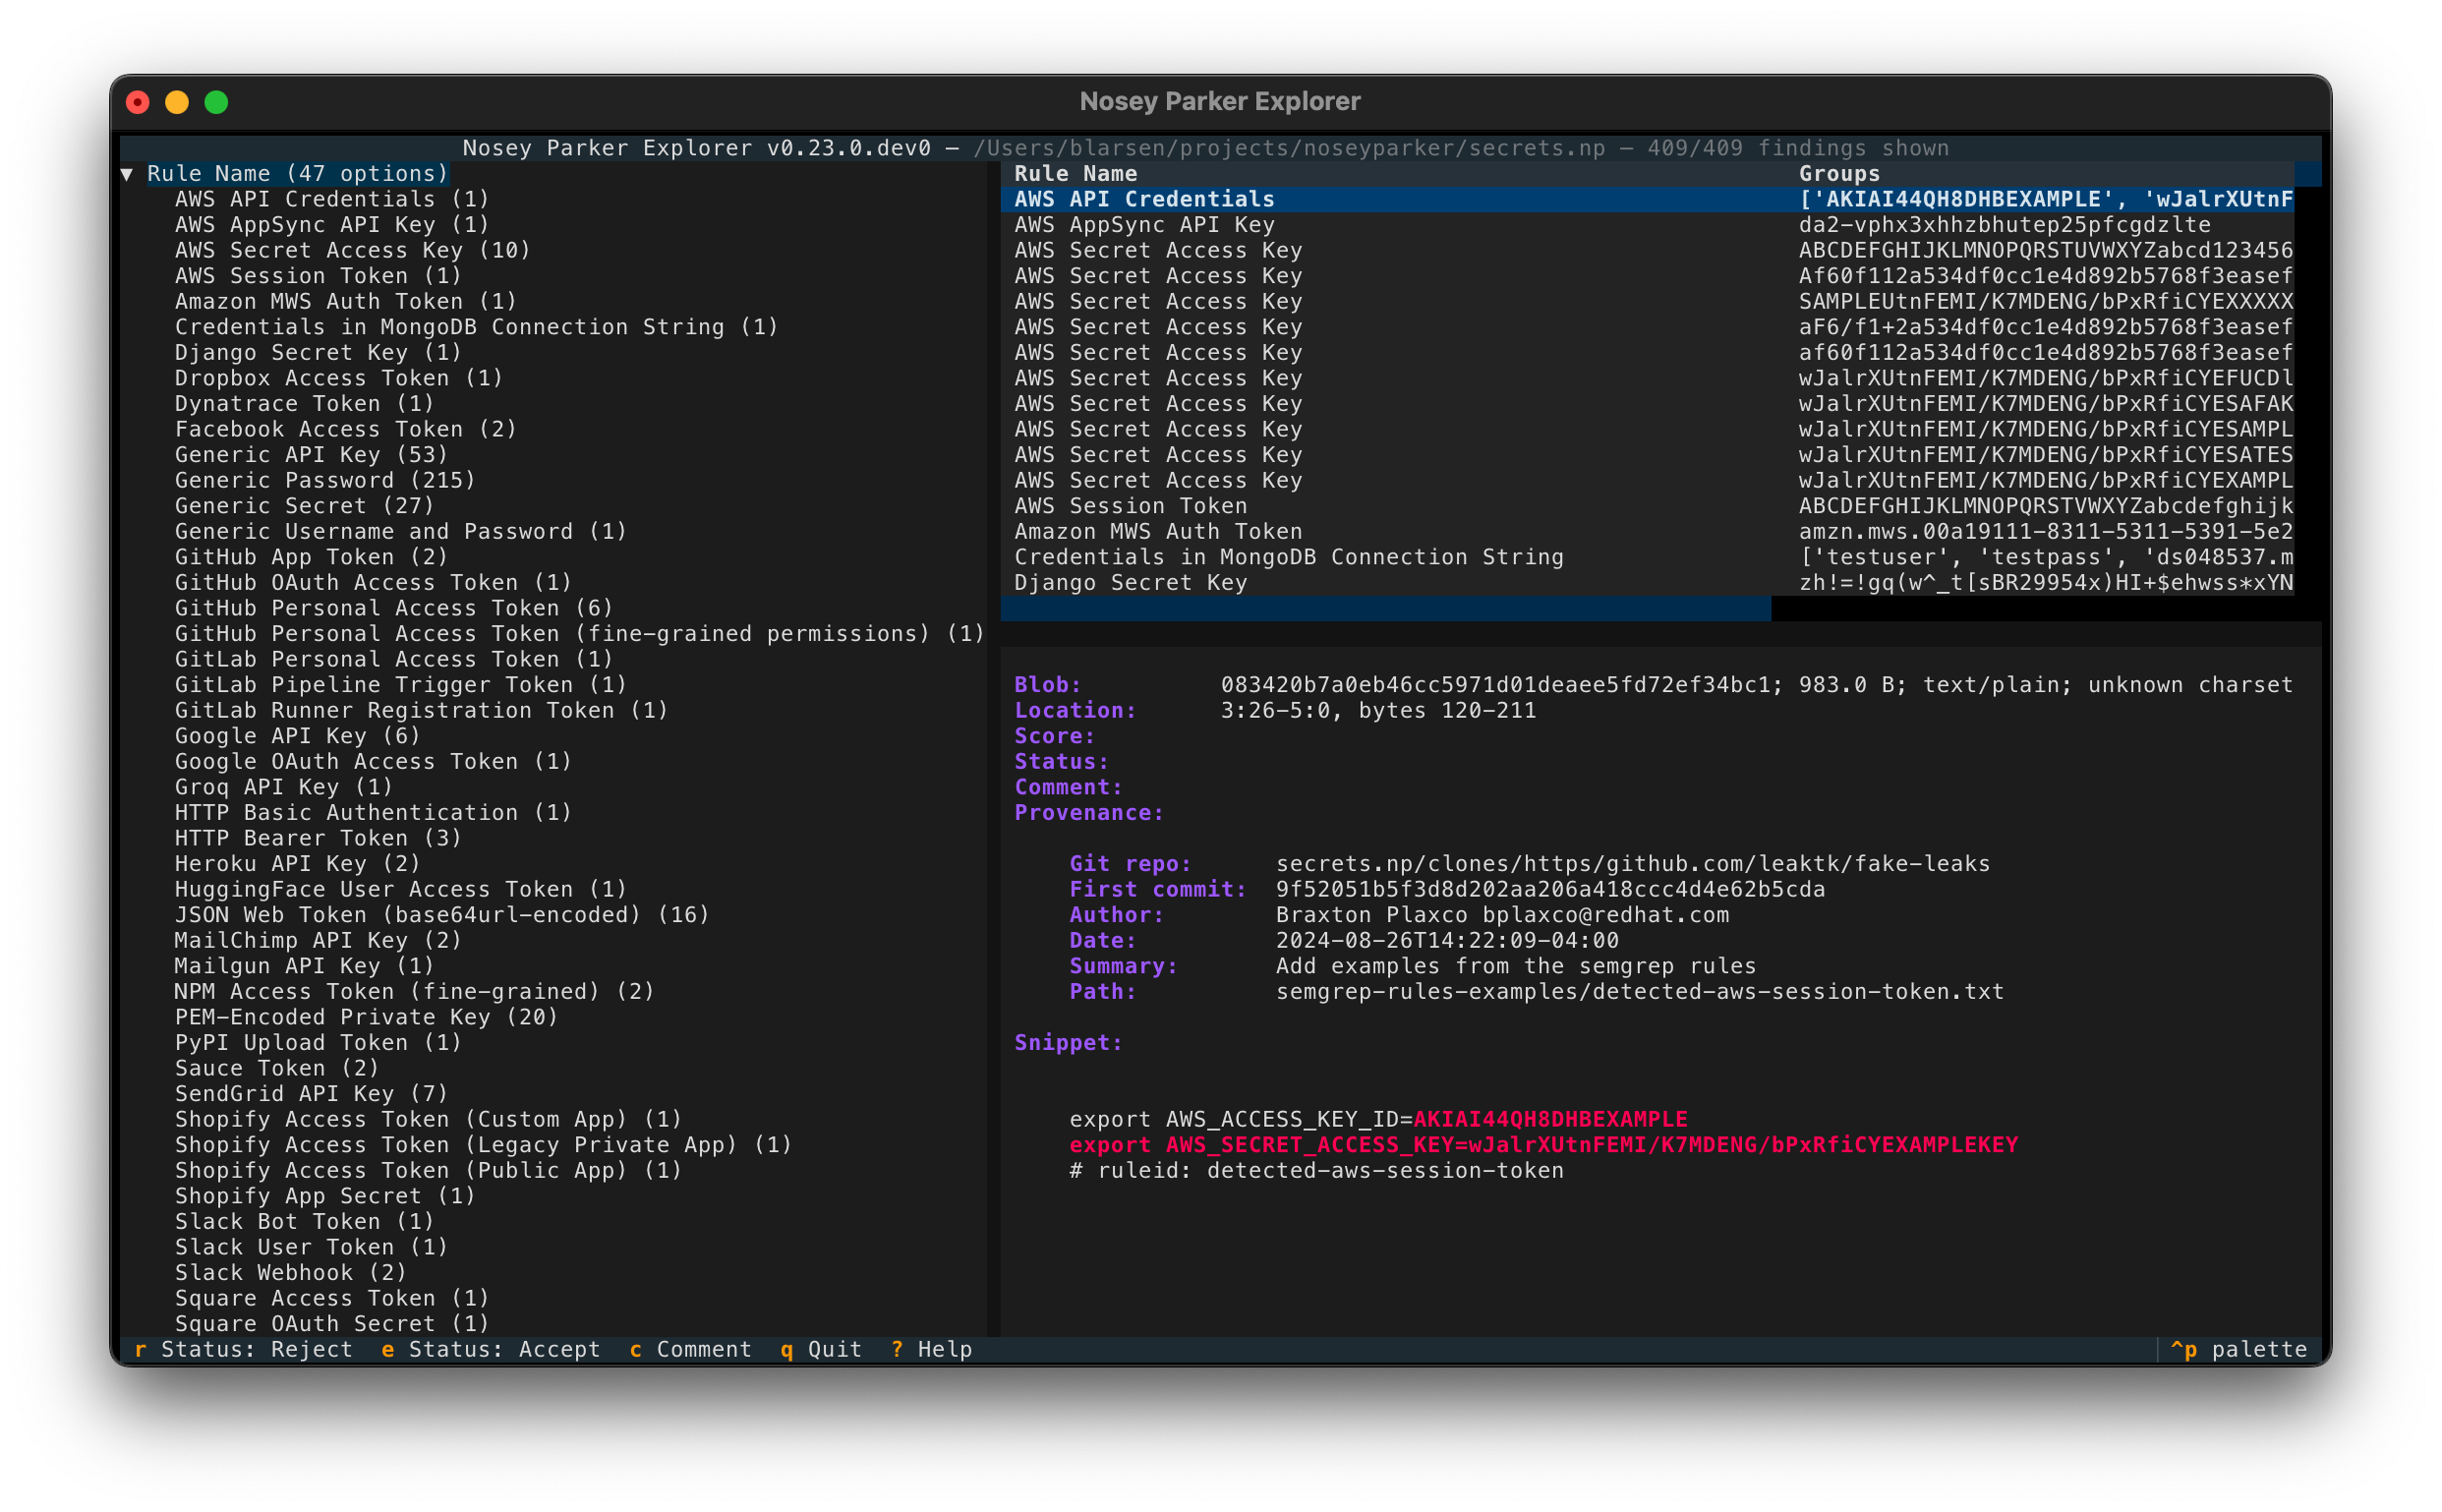 praetorian-inc/noseyparker
Nosey Parker is a command-line tool that finds secrets and sensitive information in textual data and Git history.
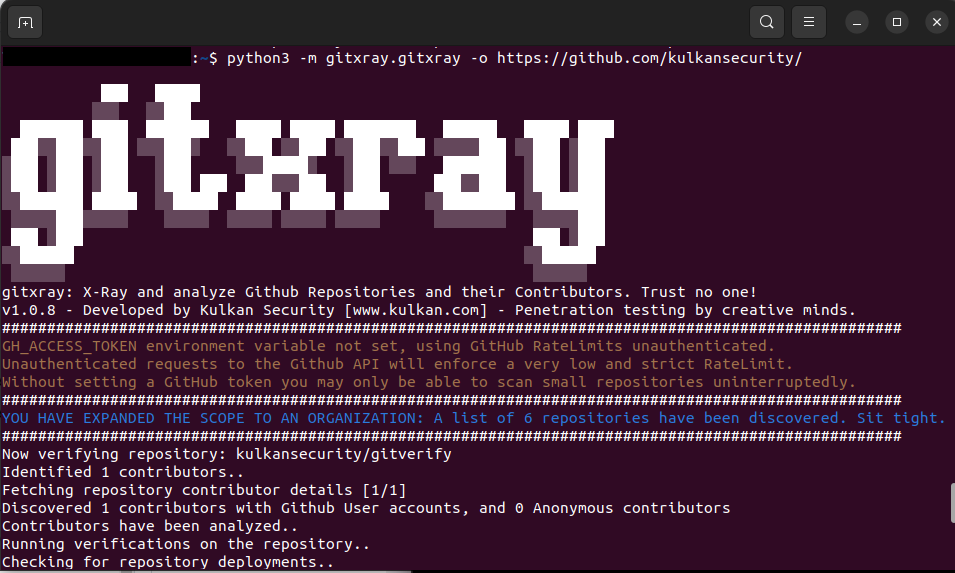 kulkansecurity/gitxray
A multifaceted security tool which leverages Public GitHub REST APIs for OSINT, Forensics, Pentesting and more.
 dirkjanm/ldapdomaindump
Active Directory information dumper via LDAP
 dream434/cve-2017-5487
Exploit for CVE-2017-5487 to enumerate WordPress user accounts via the REST API, extracting sensitive information from vulnerable 4.7 installations.
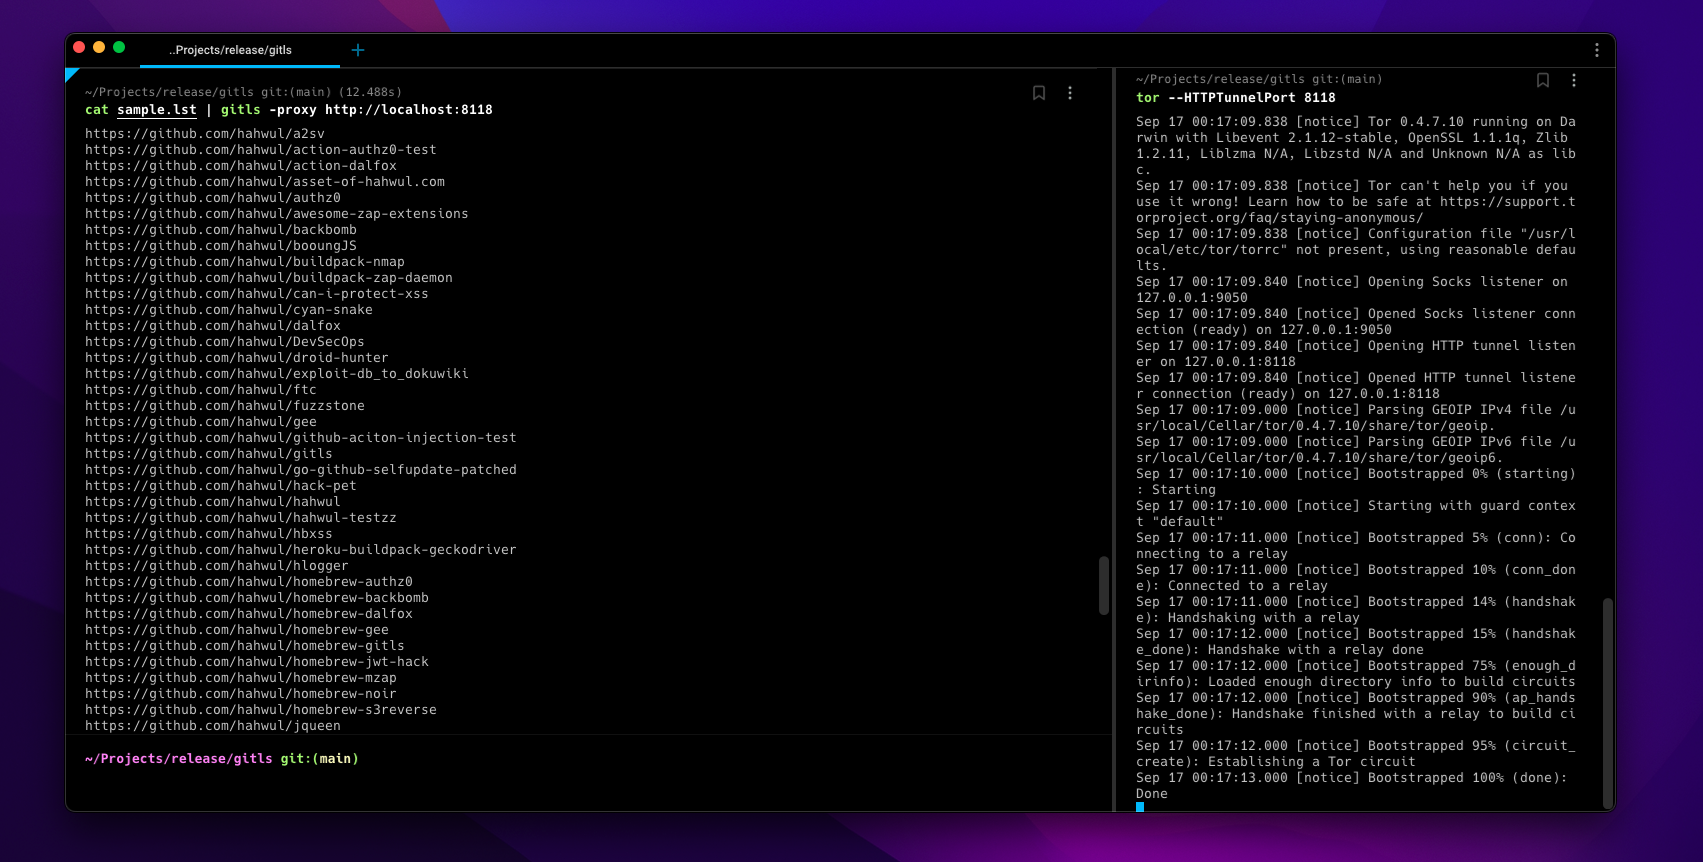 hahwul/gitls
🖇 Enumerate git repository URL from list of URL / User / Org. Friendly to pipeline
 dogucyber/wordpress-exploit-cve-2024-1071
Unauthenticated SQL injection exploit for WordPress versions 2.1.3 to 2.8.2, targeting the Ultimate Member plugin to extract sensitive database…
 johndoeanonita/cve-2023-23752
CVE-2023-23752 Data Extractor