NWH-Stealer-Analysis-Fileless-Bun-Runtime-Execution-Clipboard-Image-Theft-Cloud-C2-AWS-R2-

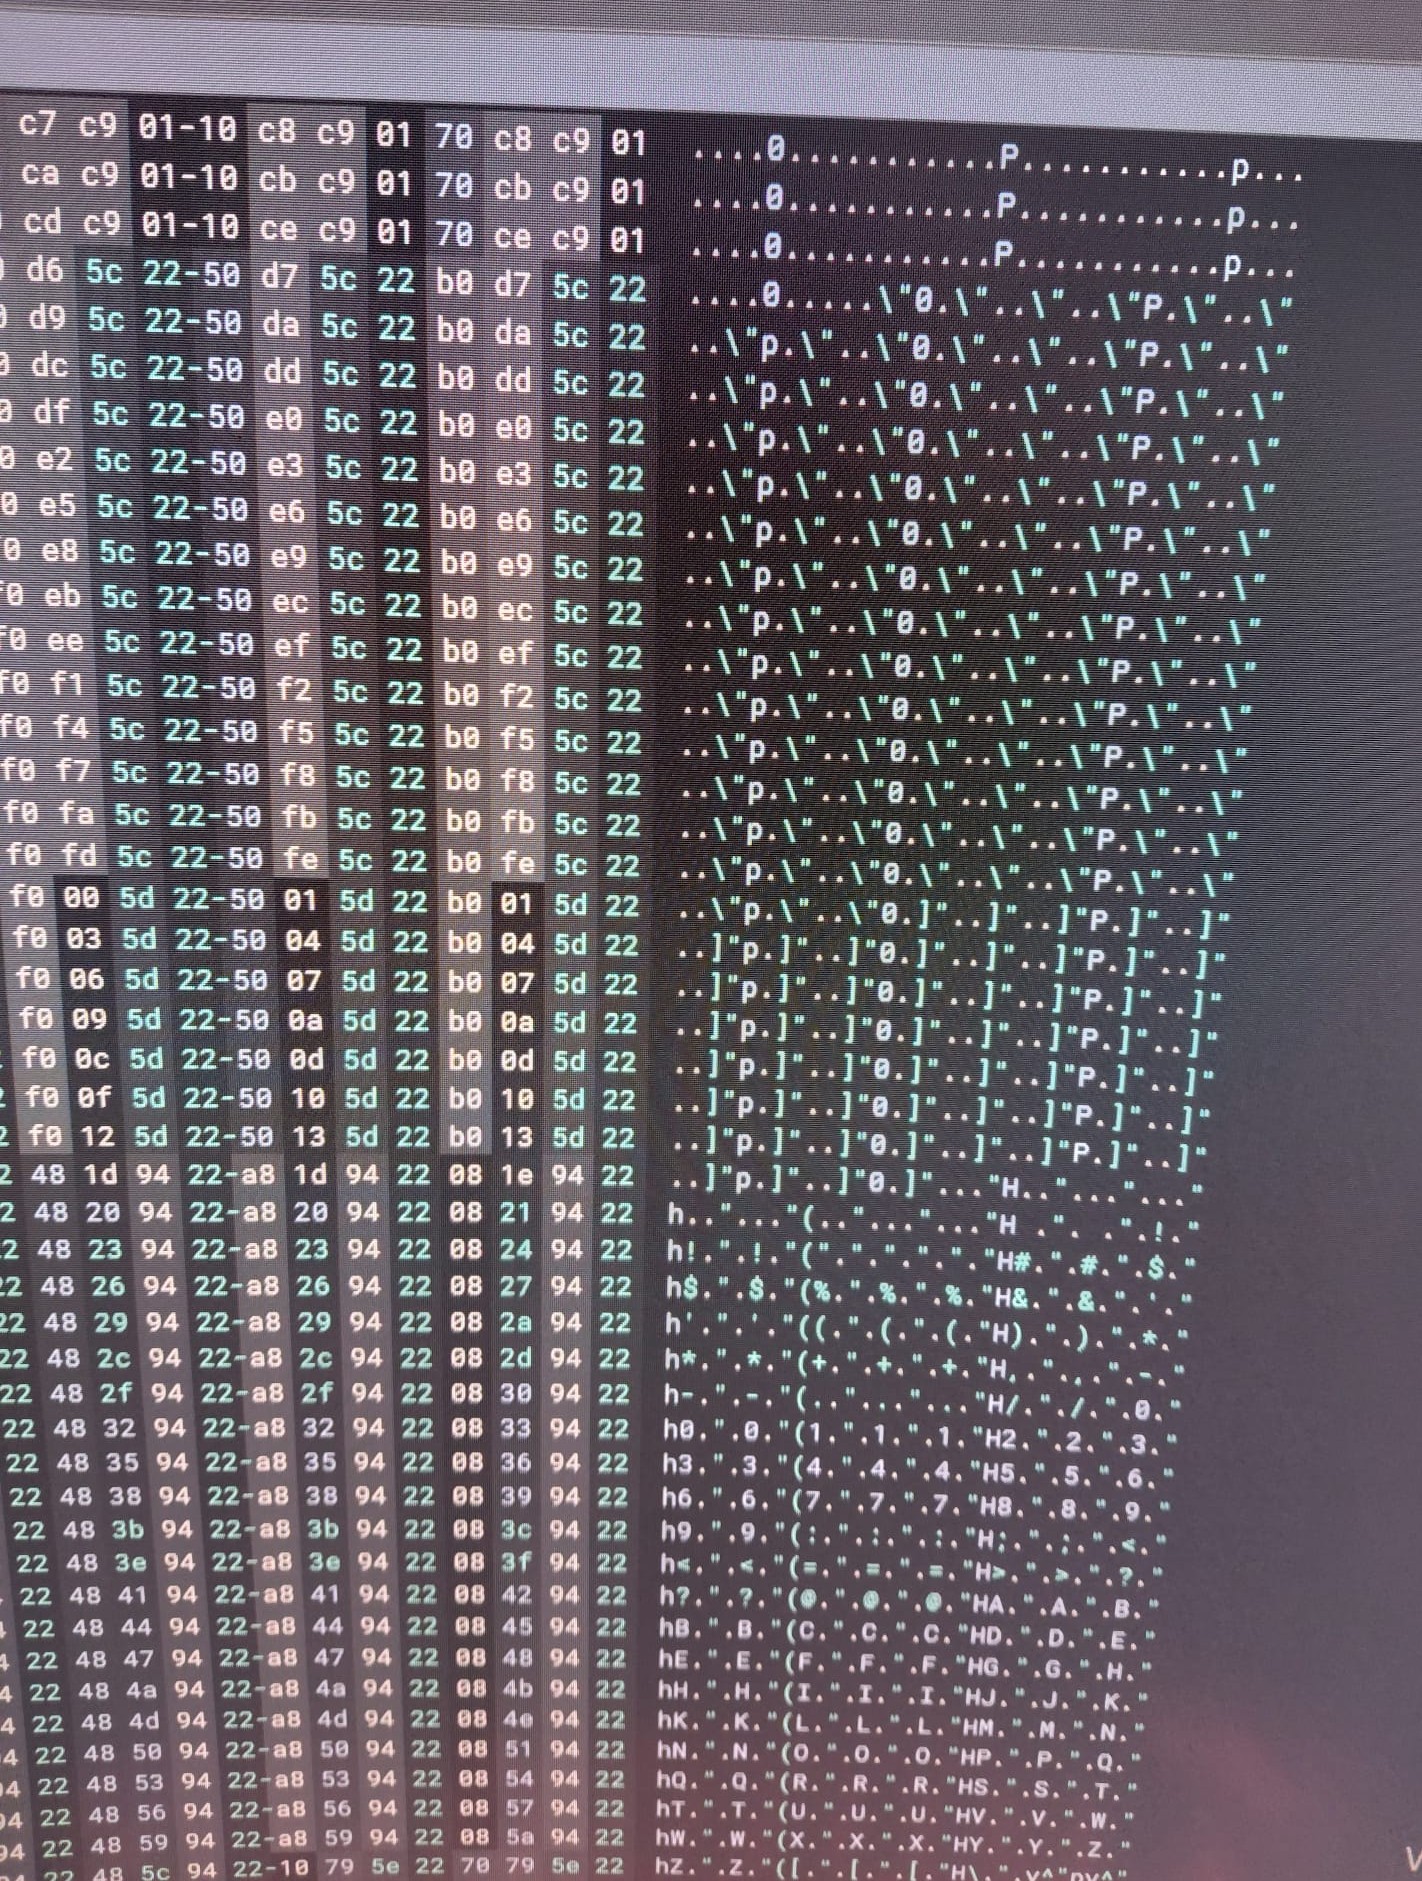
Static analysis and payload extraction of NWH Stealer. Features deep dive into fileless execution via Bun JavaScript Runtime, in-memory clipboard…

Static analysis and payload extraction of NWH Stealer. Features deep dive into fileless execution via Bun JavaScript Runtime, in-memory clipboard…

Rust-based XSS scanner with context-aware payload selection, WAF detection and bypass, crawling, blind XSS callbacks, and static DOM sink analysis.

Custom Bash and Python scripts used to automate various penetration testing tasks including recon, scanning, enumeration, and malicious payload…

Rust CLI for MQTT penetration testing: subscribe/publish, broker fingerprinting, ACL probing, topic enumeration, credential brute-force, and Last…

A lightweight Blind XSS (Cross-Site Scripting) collector and payload server built with Flask

Reverse engineering analysis of Formbook, an info-stealer that uses .NET assembly manipulation and XOR decryption. Full payload extracted via x32dbg,…

Reverse engineering analysis of StealC Stealer, an info-stealer that uses RuntimeBroker.exe hollowing, C2 infrastructure, and payload extraction.…

Self-hosted SSRF redirect, payload, callback, and DNS workbench

Practical study notes and walkthroughs for PortSwigger Academy labs, covering web vulnerabilities, payloads, enumeration, and BSCP exam strategies.

Validates pre-authentication reflected XSS in WordPress, fingerprints vulnerable versions, checks payload reflection and JSONP, and generates…

"Reverse engineering analysis of Salat Stealer, a Go-based info-stealer that uses a Telegram proxy decoy, C2 communication, and encrypted memory…

wp2shell - WordPress RCE & PoC (CVE-2026-63030 + CVE-2026-60137)

JavaScript beacons and C2 to be used for XSS payload or post exploitation implants on webapp servers or desktop software to monitor users and…

Blind XSS detection and exploitation platform with persistent sessions, reverse proxy, and automated information gathering for penetration testers…

Tool designed to scan a list of websites for a known vulnerability in the PHPUnit framework, specifically the CVE-2017-9841 vulnerability.

Exploit CVE-2020-13886 - LFI Intelbras TIP 200 / 200 LITE /

Simple Python PoC to check Citrix NetScaler ADC/Gateway for CVE-2025-12101 reflected XSS on /cgi/logout using a crafted SAMLResponse + RelayState…

ALL IN ONE Hacking Tool For Hackers, Penetration Tester and Cybersecurity. New Version Beginner to Advanced Tool. This Tool is made for educational…