

waf-fu
 confused-binary/waf-fu
Terminal UI for browsing and replaying AWS WAF v2 logs from CloudWatch, S3, and the sampling API, with YAML filtering, auth detection, and…
cloud-securitydefensive-toolsincident-response+6
2
confused-binary/waf-fuTerminal UI for browsing and replaying AWS WAF v2 logs from CloudWatch, S3, and the sampling API, with YAML filtering, auth detection, and…
 thakur2309/pagasus-pro
Python ADB-based Android device management and security audit toolkit with an interactive menu for root detection, permission dumps, debuggable app…
 mbanyamer/llama-stack-0.4.0rc3-local-cve-2026-25211
Local proof-of-concept scanner that detects plaintext database passwords in llama-stack initialization logs, using regex pattern matching to identify…
 1amunvalid/cve-2025-10951
Proof-of-concept checker for CVE-2025-10951, an unauthenticated path traversal in ml-logger, validating arbitrary file read via /glob and /stream…
 randomrobbiebf/cve-2024-12849
Error Log Viewer By WP Guru <= 1.0.1.3 - Missing Authorization to Unauthenticated Arbitrary File Read
 nccgroup/impossibletravelloganalysis
Basic log analysis tool to detect impossible travel via IP address geographic information
 corelight/zeek-endpoint-enrichment
Zeek log enrichment tool that adds host information and known entity references to enhance network security monitoring and incident response.
 mushorg/buttinsky
Botnet monitoring is a crucial part in threat analysis and often neglected due to the lack of proper open source tools. Our tool will provide an open…
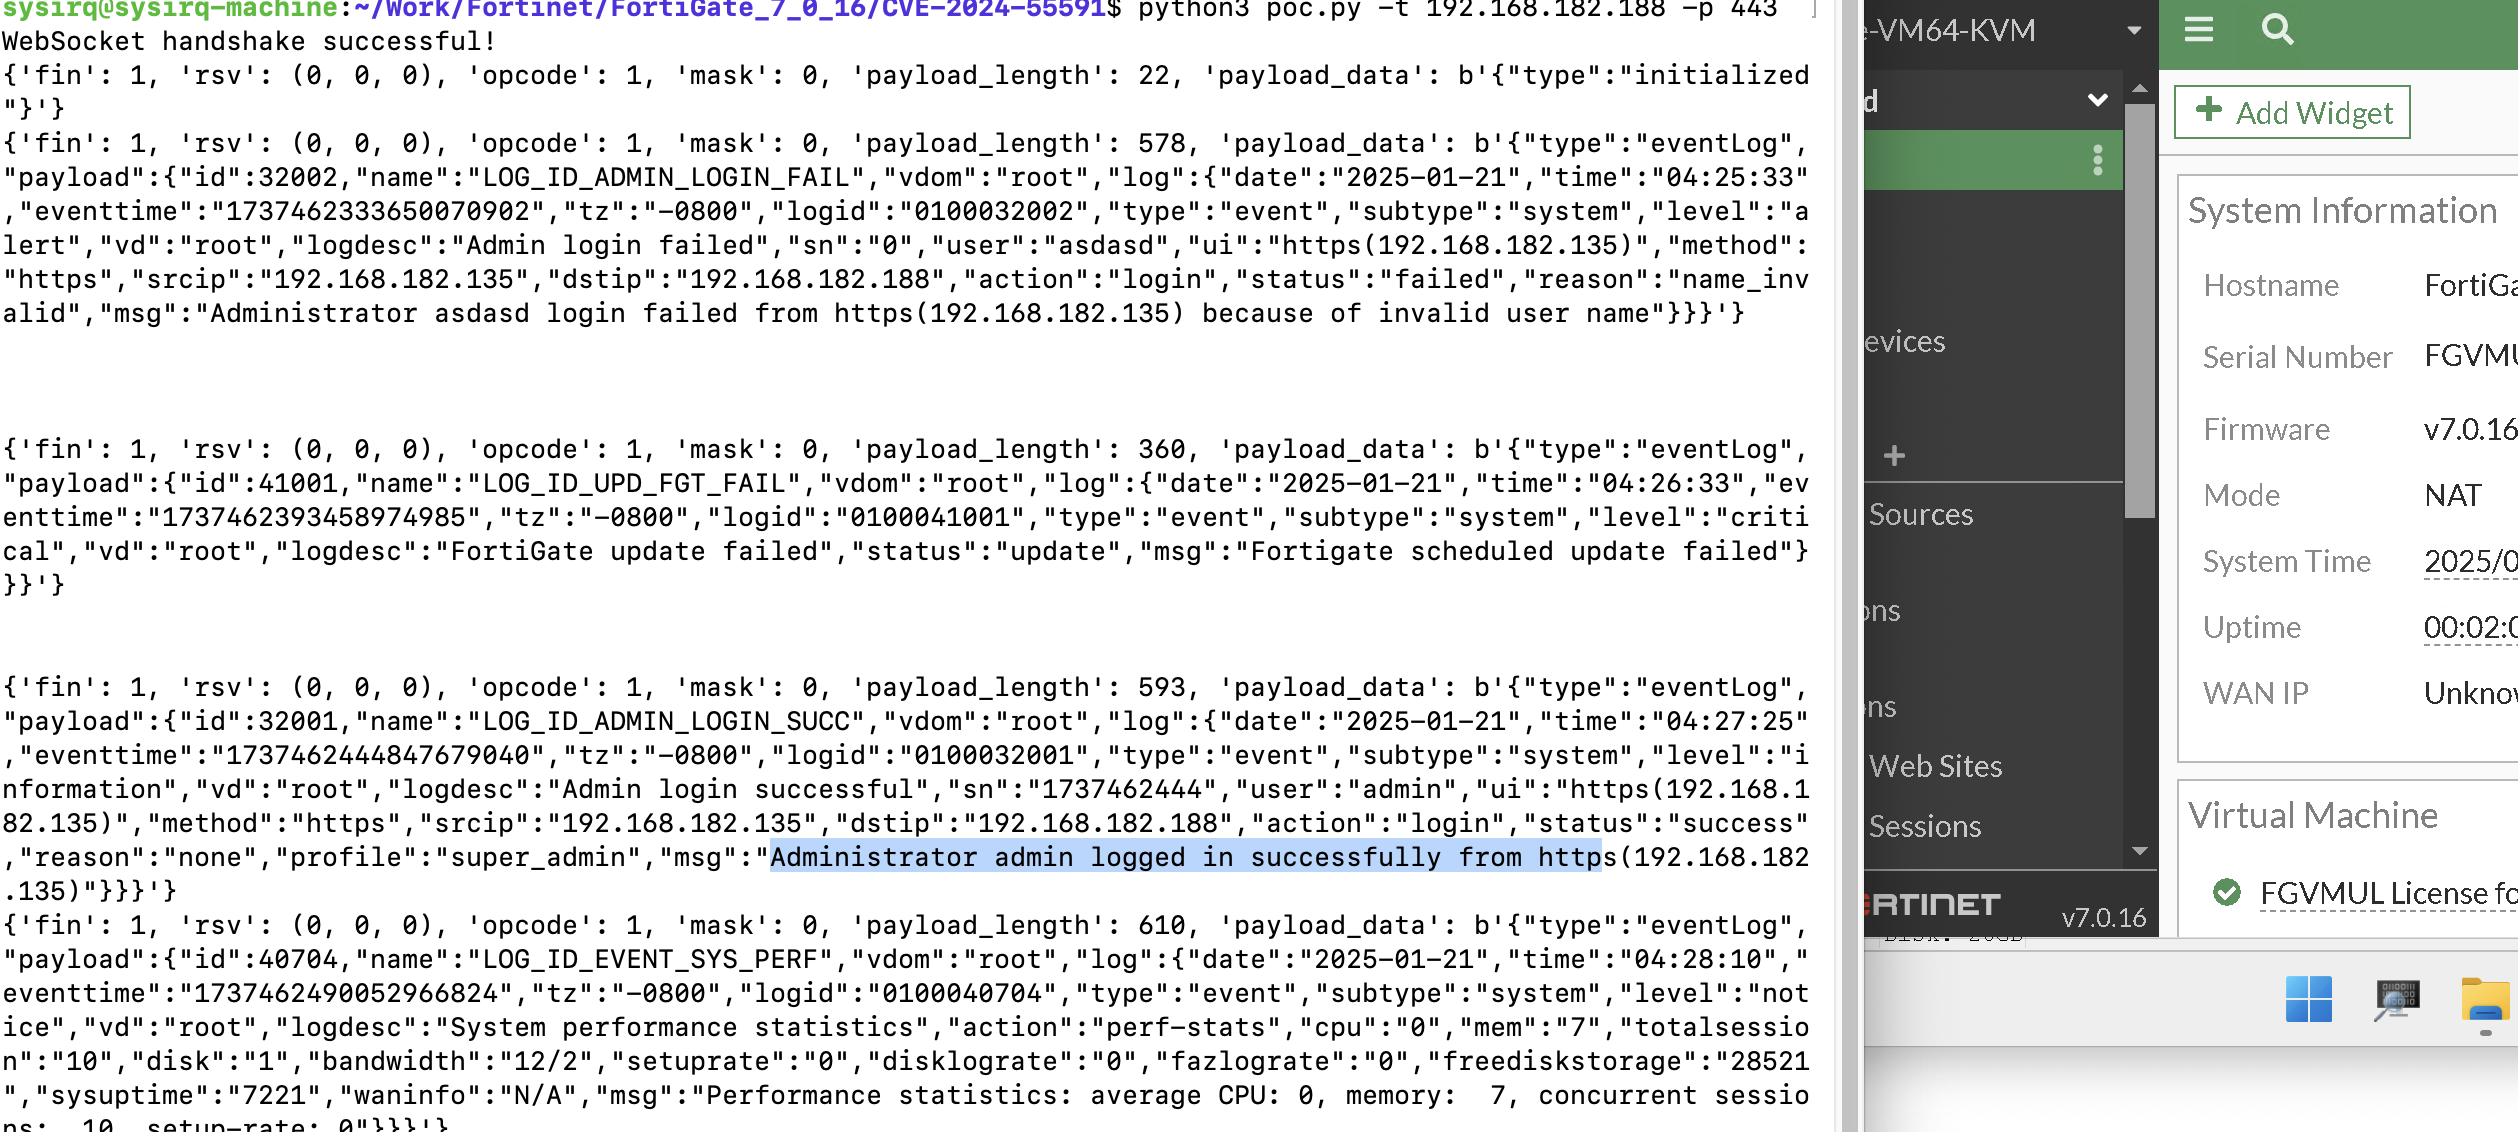 sysirq/fortios-auth-bypass-poc-cve-2024-55591
Proof-of-concept exploit for FortiOS authentication bypass (CVE-2024-55591) that allows unauthenticated access to system logs via WebSocket on…
 mkultra6969/anysniff
AnySniff is a tool for monitoring TCP connections of processes like AnyDesk on Windows. It uses the CVE-2024-52940 vulnerability to track open…
 skraft9/cve-2025-44823
Authenticated API Key Exposure in Nagios Log Server 2024R1.3.1
 nxploited/cve-2023-47668
Python exploit for CVE-2023-47668 that extracts sensitive log information from vulnerable Restrict Content WordPress plugin versions <= 3.2.7.
 randomrobbiebf/cve-2023-47529
Cloud Templates & Patterns collection <= 1.2.2 - Sensitive Information Exposure via Log File
 shamo0/cve-2021-44228
log4shell (CVE-2021-44228) scanning tool
 mdanzaruddin/cve-2021-33558.
Exploit code for CVE-2021-33558 targeting Boa/0.94.13 misconfigurations that expose sensitive information via backup, preview, log, and config files.
 gazettel/cve-2020-17519
Python-based directory traversal exploit for CVE-2020-17519 (Apache Flink) with multi-threading, proxy support, and configurable depth for retrieving…
 jra89/cve-2019-19653
Chevereto information disclosure <= 3.13.5 Core
 jet-pentest/cve-2020-29666
Proof-of-concept for CVE-2020-29666: directory listing vulnerability in Lan ATMService M3 ATM Monitoring System 6.1.0 that exposes log files…