NWH-Stealer-Analysis-Fileless-Bun-Runtime-Execution-Clipboard-Image-Theft-Cloud-C2-AWS-R2-

Static analysis and payload extraction of NWH Stealer. Features deep dive into fileless execution via Bun JavaScript Runtime, in-memory clipboard…

Static analysis and payload extraction of NWH Stealer. Features deep dive into fileless execution via Bun JavaScript Runtime, in-memory clipboard…

ALL IN ONE Hacking Tool For Hackers, Penetration Tester and Cybersecurity. New Version Beginner to Advanced Tool. This Tool is made for educational…

Rust-based XSS scanner with context-aware payload selection, WAF detection and bypass, crawling, blind XSS callbacks, and static DOM sink analysis.

Rust CLI for MQTT penetration testing: subscribe/publish, broker fingerprinting, ACL probing, topic enumeration, credential brute-force, and Last…

Reverse engineering analysis of Formbook, an info-stealer that uses .NET assembly manipulation and XOR decryption. Full payload extracted via x32dbg,…

A lightweight Blind XSS (Cross-Site Scripting) collector and payload server built with Flask

Self-hosted SSRF redirect, payload, callback, and DNS workbench

Reverse engineering analysis of StealC Stealer, an info-stealer that uses RuntimeBroker.exe hollowing, C2 infrastructure, and payload extraction.…

Practical study notes and walkthroughs for PortSwigger Academy labs, covering web vulnerabilities, payloads, enumeration, and BSCP exam strategies.

Validates pre-authentication reflected XSS in WordPress, fingerprints vulnerable versions, checks payload reflection and JSONP, and generates…

Hooked browser communication over MQTT

"Reverse engineering analysis of Salat Stealer, a Go-based info-stealer that uses a Telegram proxy decoy, C2 communication, and encrypted memory…

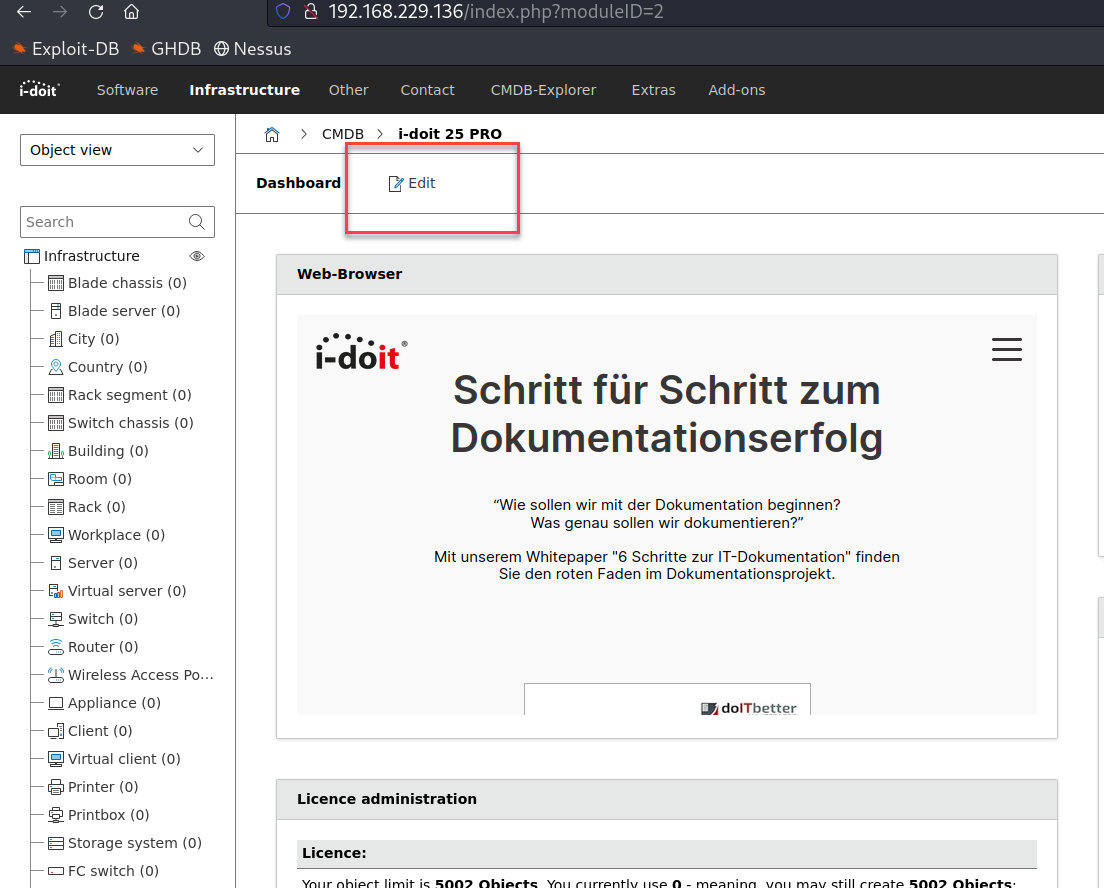
Proof-of-concept for a stored XSS vulnerability in i-doit Pro 25 and below, demonstrating payload injection via multiple parameters and components…

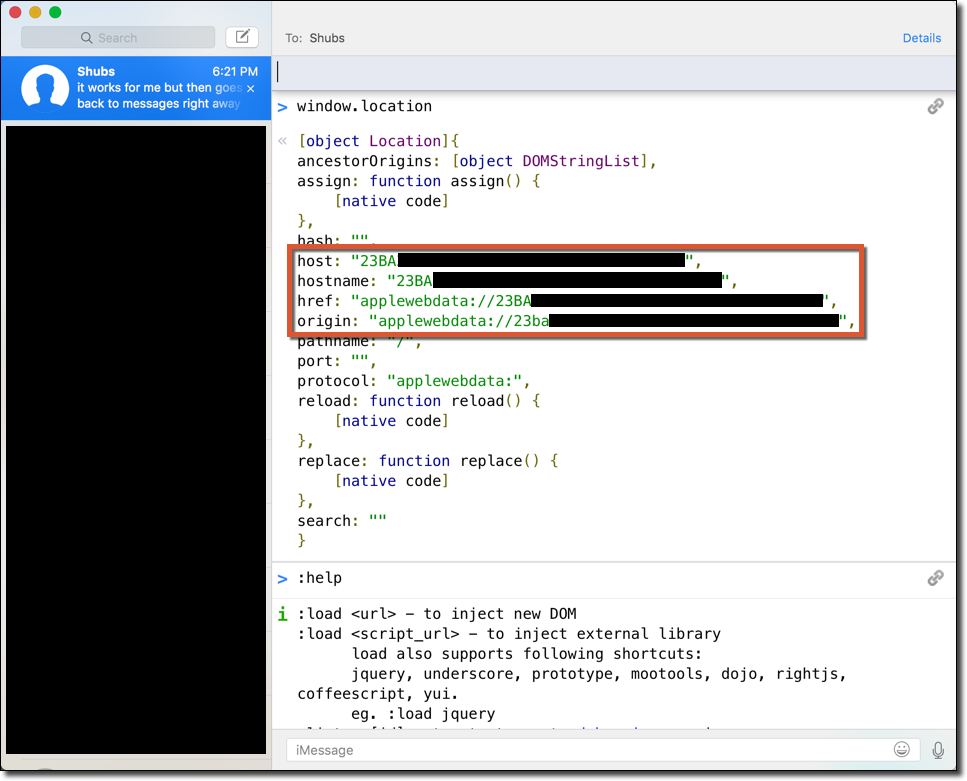
Extraction of iMessage Data via XSS

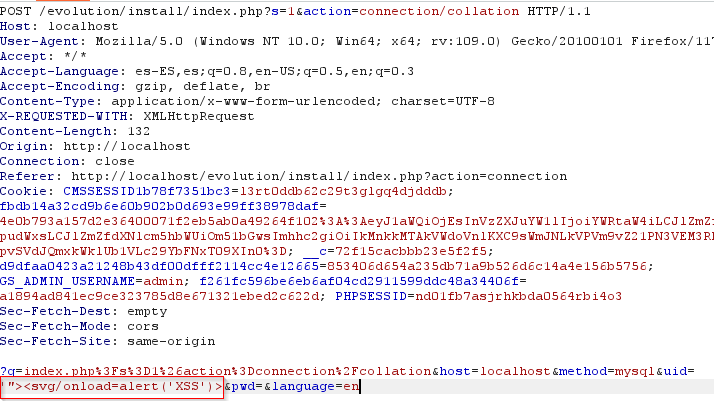
Evolution CMS 3.2.3 is affected by a Cross-Site Scripting (XSS) vulnerability that allows attackers to execute arbitrary code via a crafted payload…

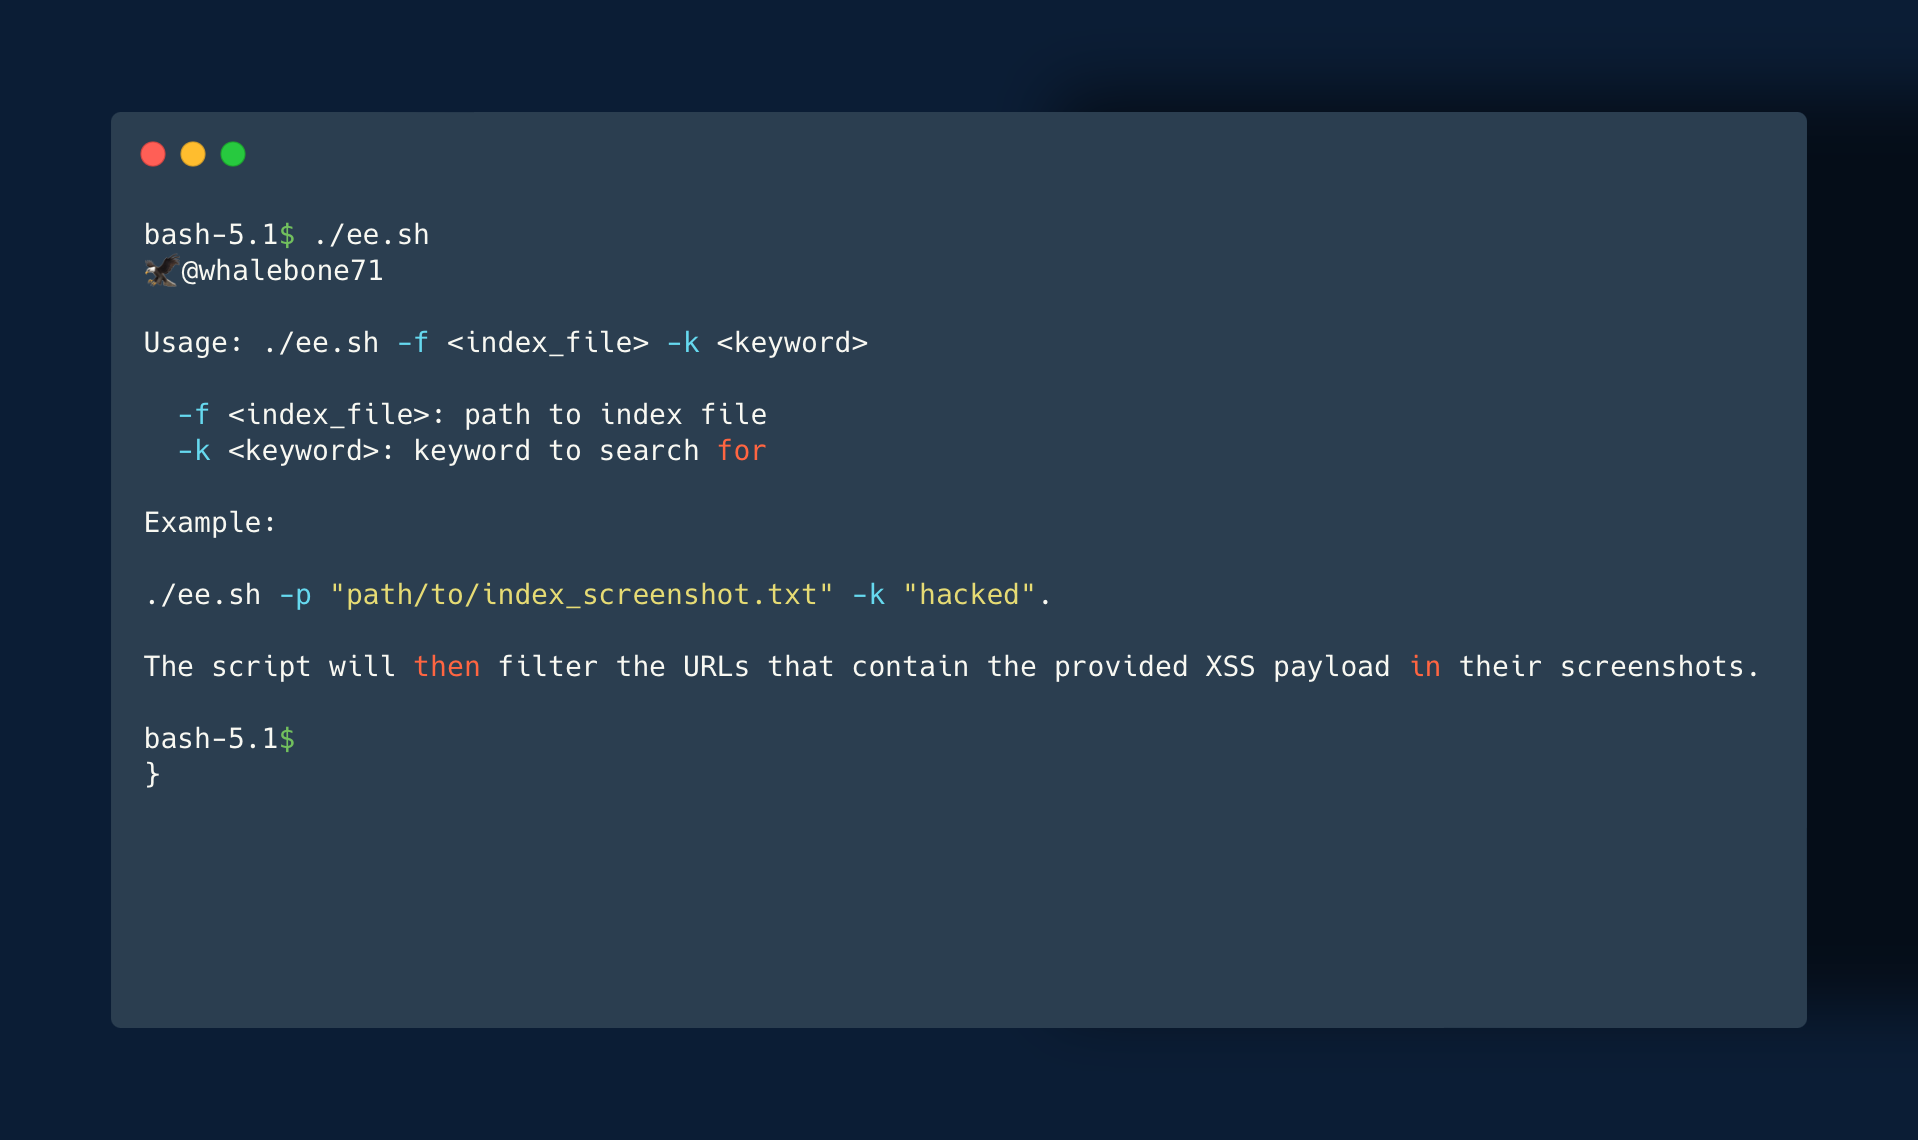
To filter the actual vulnerable URLs from the screenshots, you can use the ee.sh script. Simply run ./ee.sh -f "path/to/index_screenshot.txt" -k…

wp2shell - WordPress RCE & PoC (CVE-2026-63030 + CVE-2026-60137)

A script that checks for vulnerable Log4j (CVE-2021-44228) systems using injection of the payload in common HTTP headers.