
CVE-2022-41401
 ixsly/cve-2022-41401
Proof-of-concept exploit for CVE-2022-41401, a server-side request forgery (SSRF) vulnerability in OpenRefine <= v3.5.2, enabling unauthorized…
exploitationinformation-gatheringpenetration-testing+2
1
ixsly/cve-2022-41401Proof-of-concept exploit for CVE-2022-41401, a server-side request forgery (SSRF) vulnerability in OpenRefine <= v3.5.2, enabling unauthorized…
 infostealers-stats/data-breach
A continuously updated resource that catalogs confirmed data breaches from across the globe. Each entry includes the breach name, usually aligned…
 hyd3sec/azur3alph4
PowerShell module for post-breach Azure red teaming, automating token extraction, resource enumeration, and lateral movement within managed identity…
 fuzzdb-project/fuzzdb
Dictionary of attack patterns and primitives for black-box application fault injection and resource discovery.
 ajayantoisdev/wasonar
WhatsApp Intelligence & Resource Exhaustion Tool. Features real-time device tracking, silent RTT probing, and protocol stress testing for security…
 bittentech/bug-bounty-beginner-roadmap
This is a resource factory for anyone looking forward to starting bug hunting and would require guidance as a beginner.
 biitts/cve-2026-72001-pangolin-cross-org-auth-bypass
PoC for CVE-2026-72001 — Pangolin < 1.22.0 cross-organization resource authentication bypass via the share-link access-token endpoint (CWE-639, CVSS…
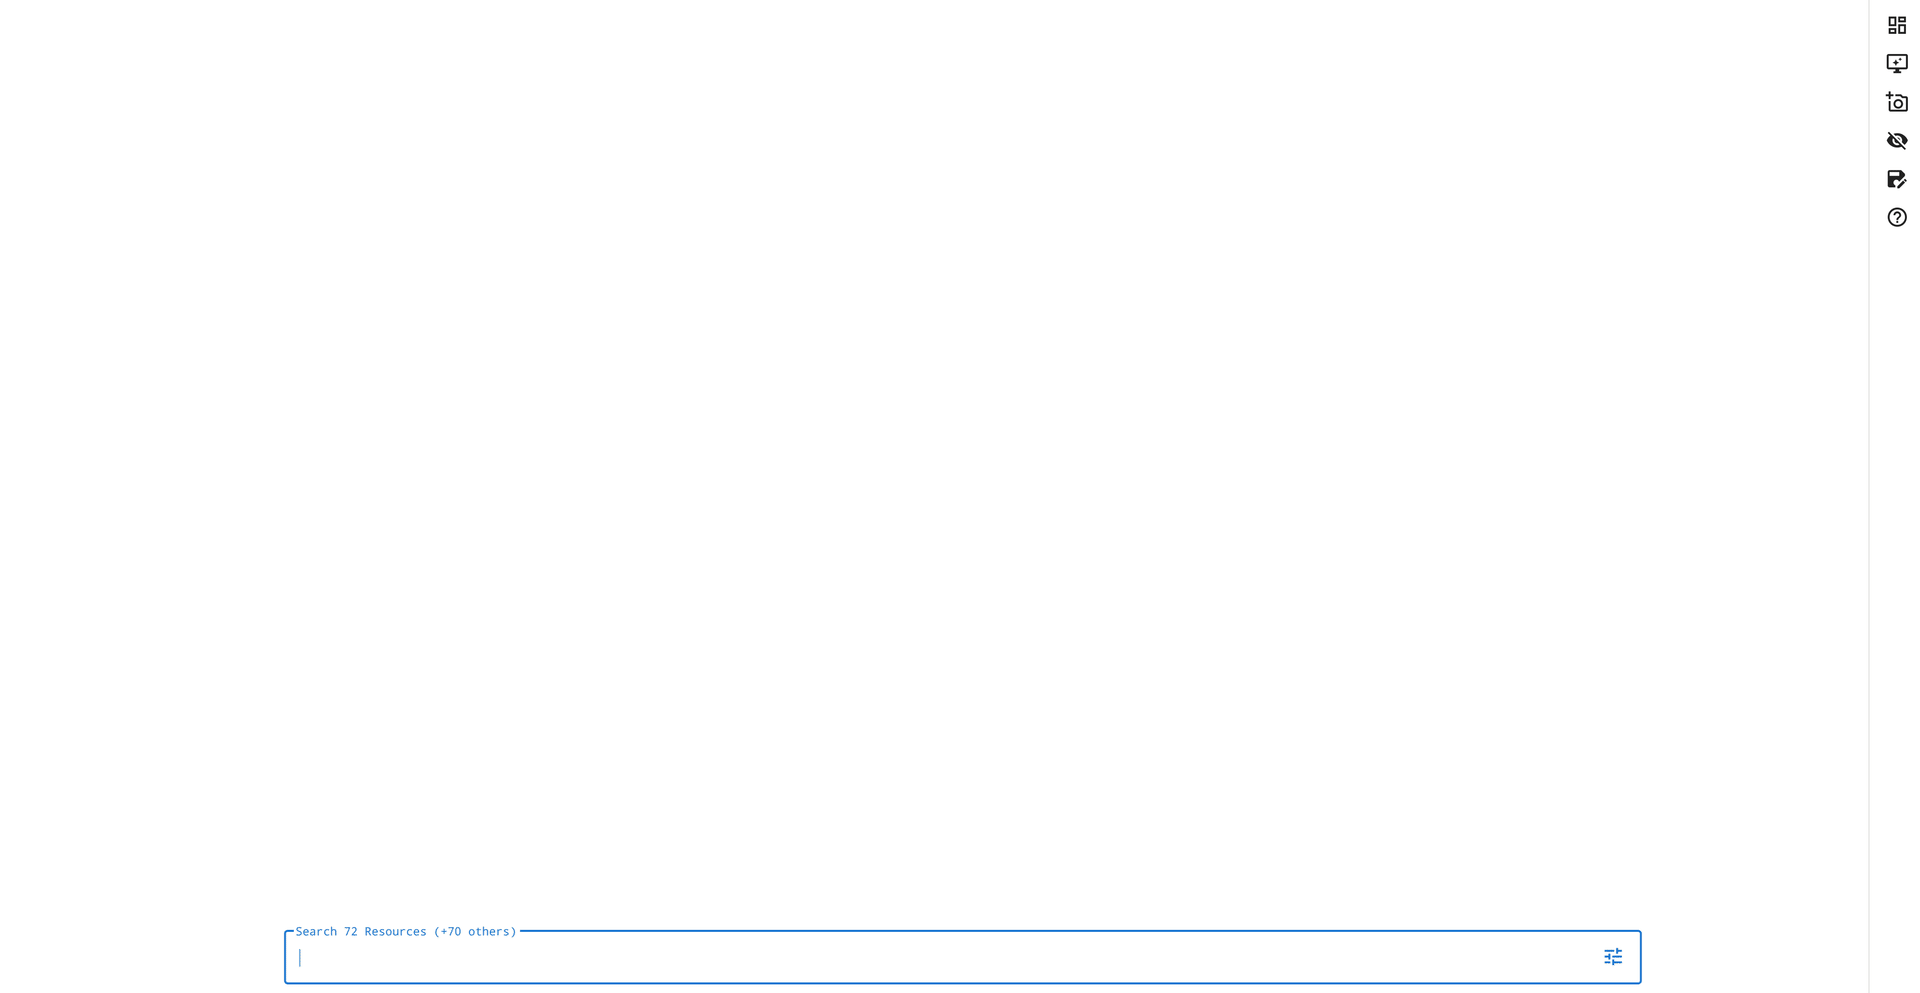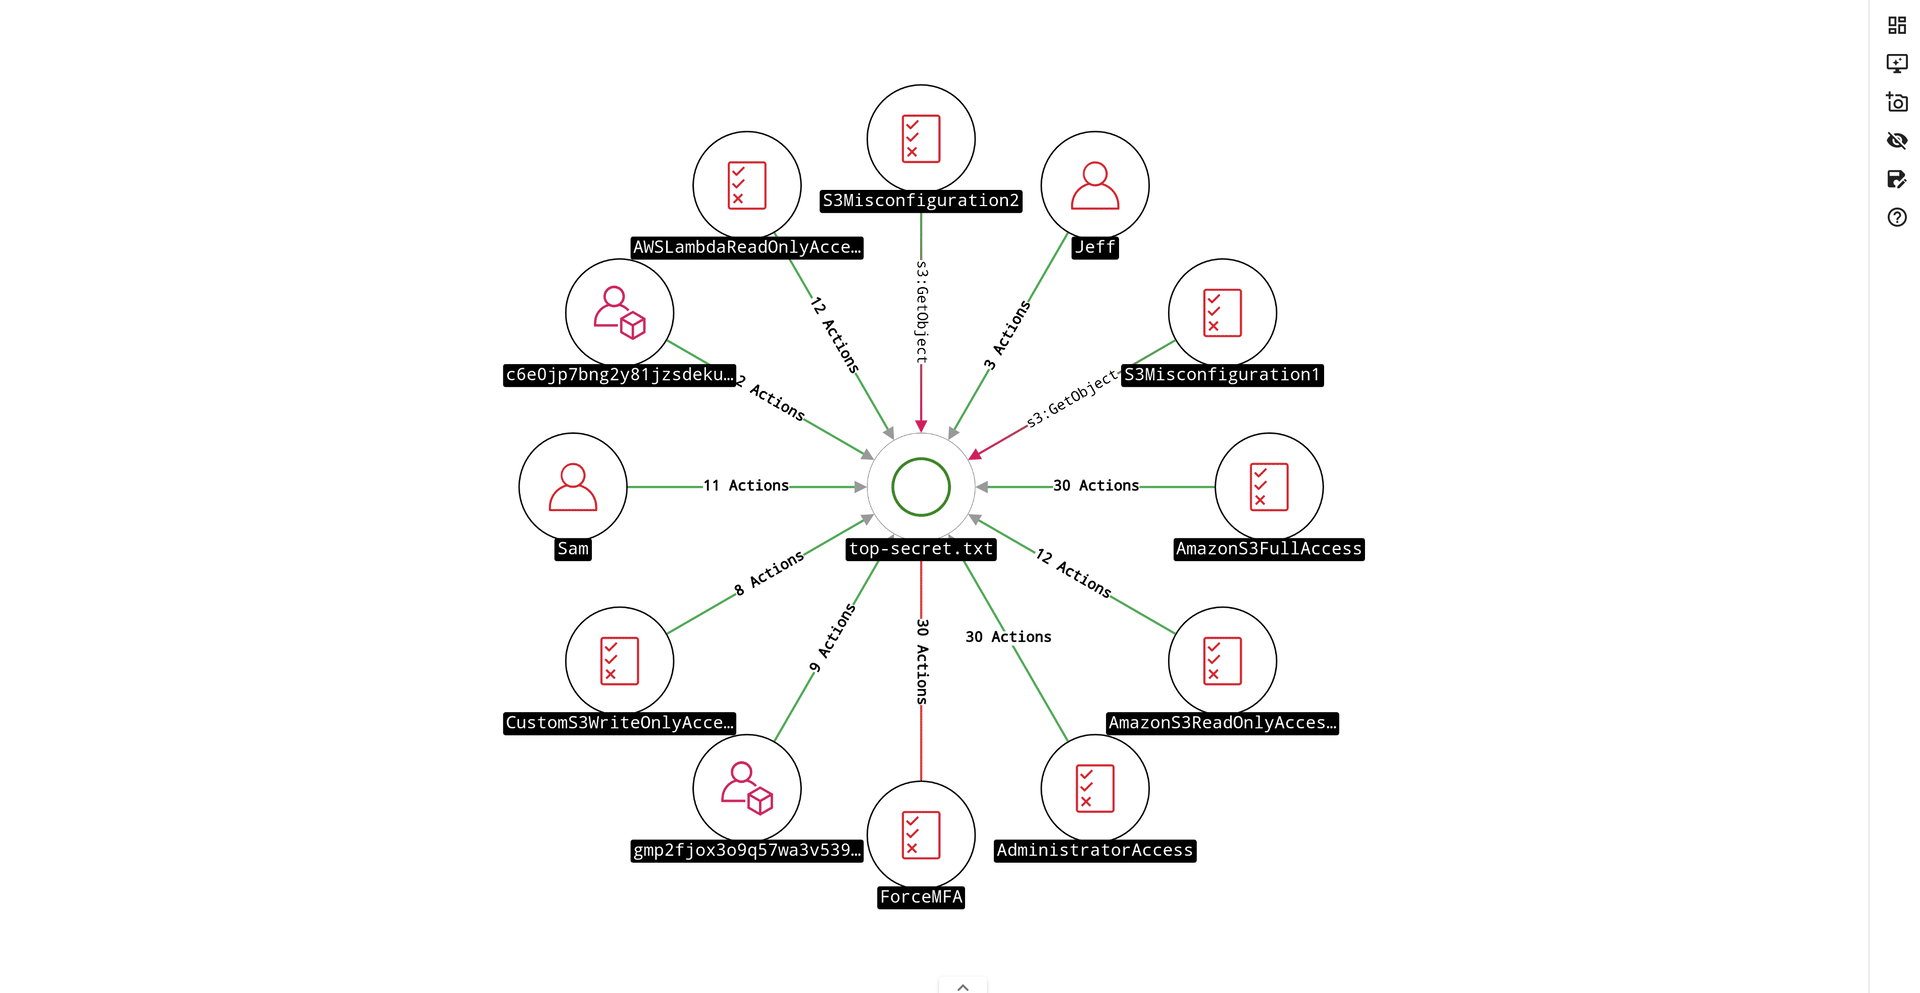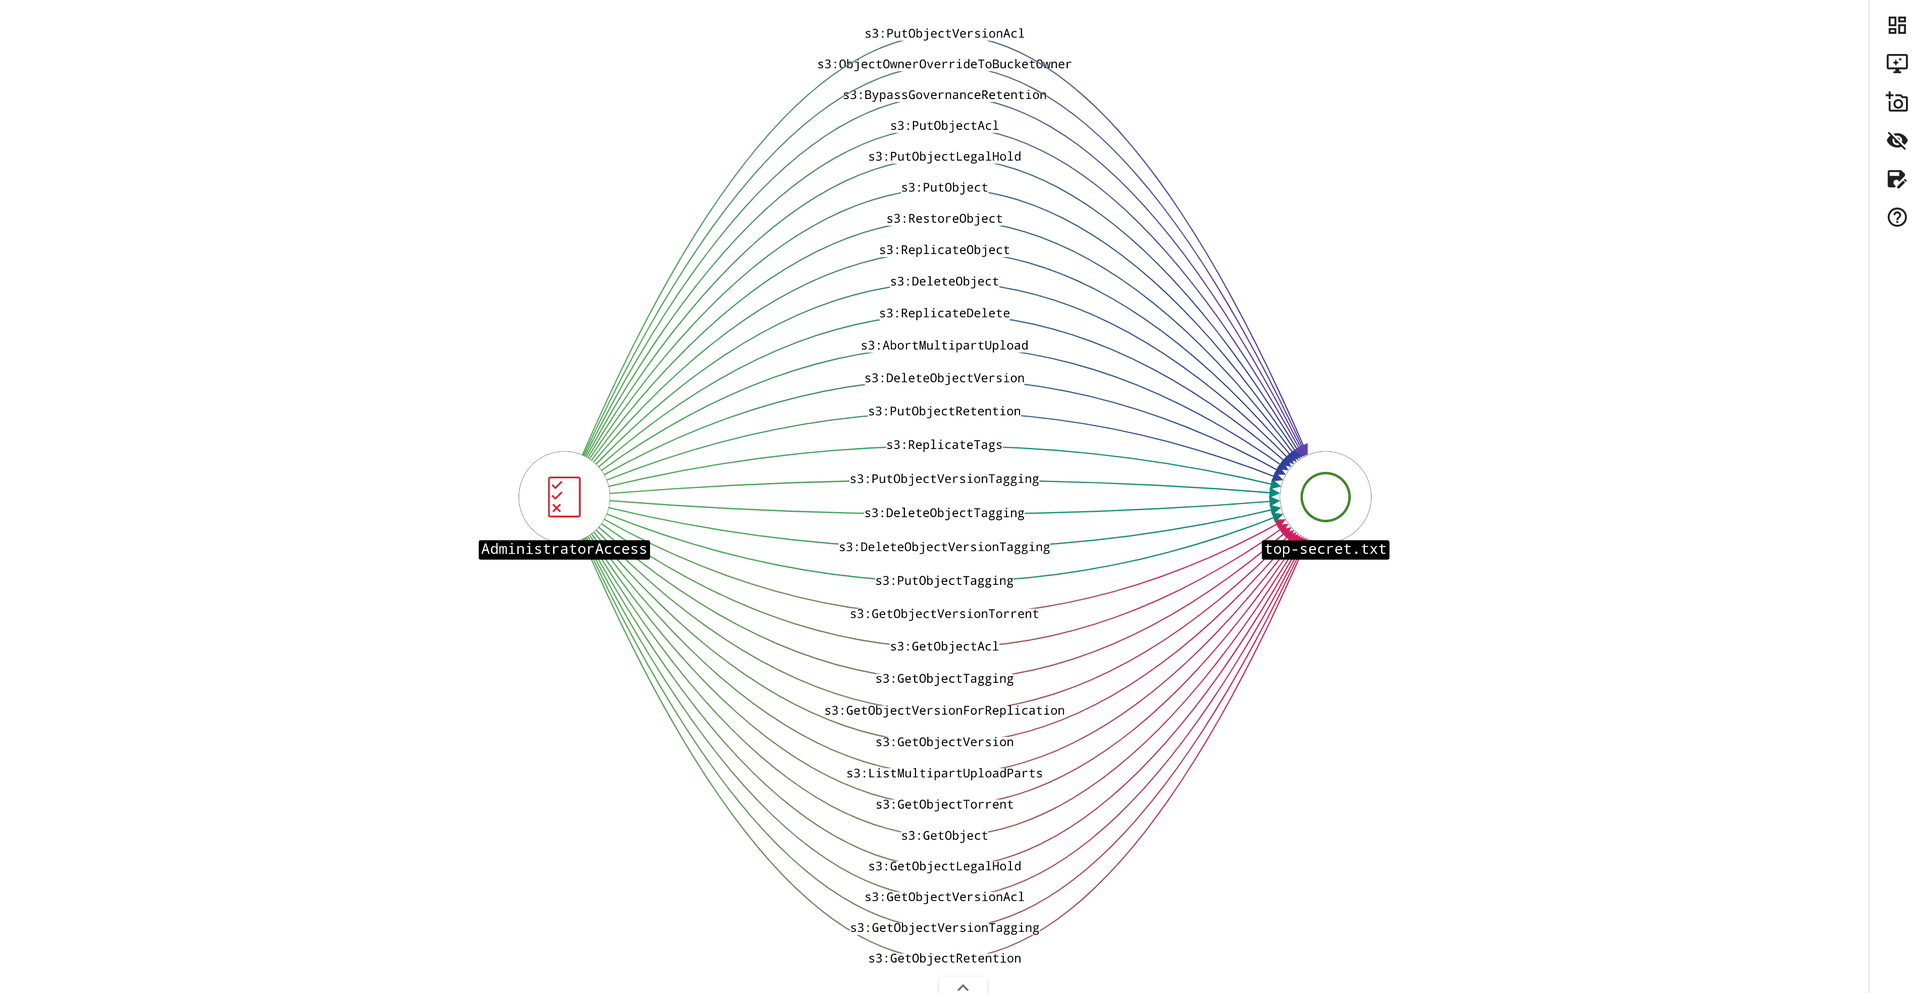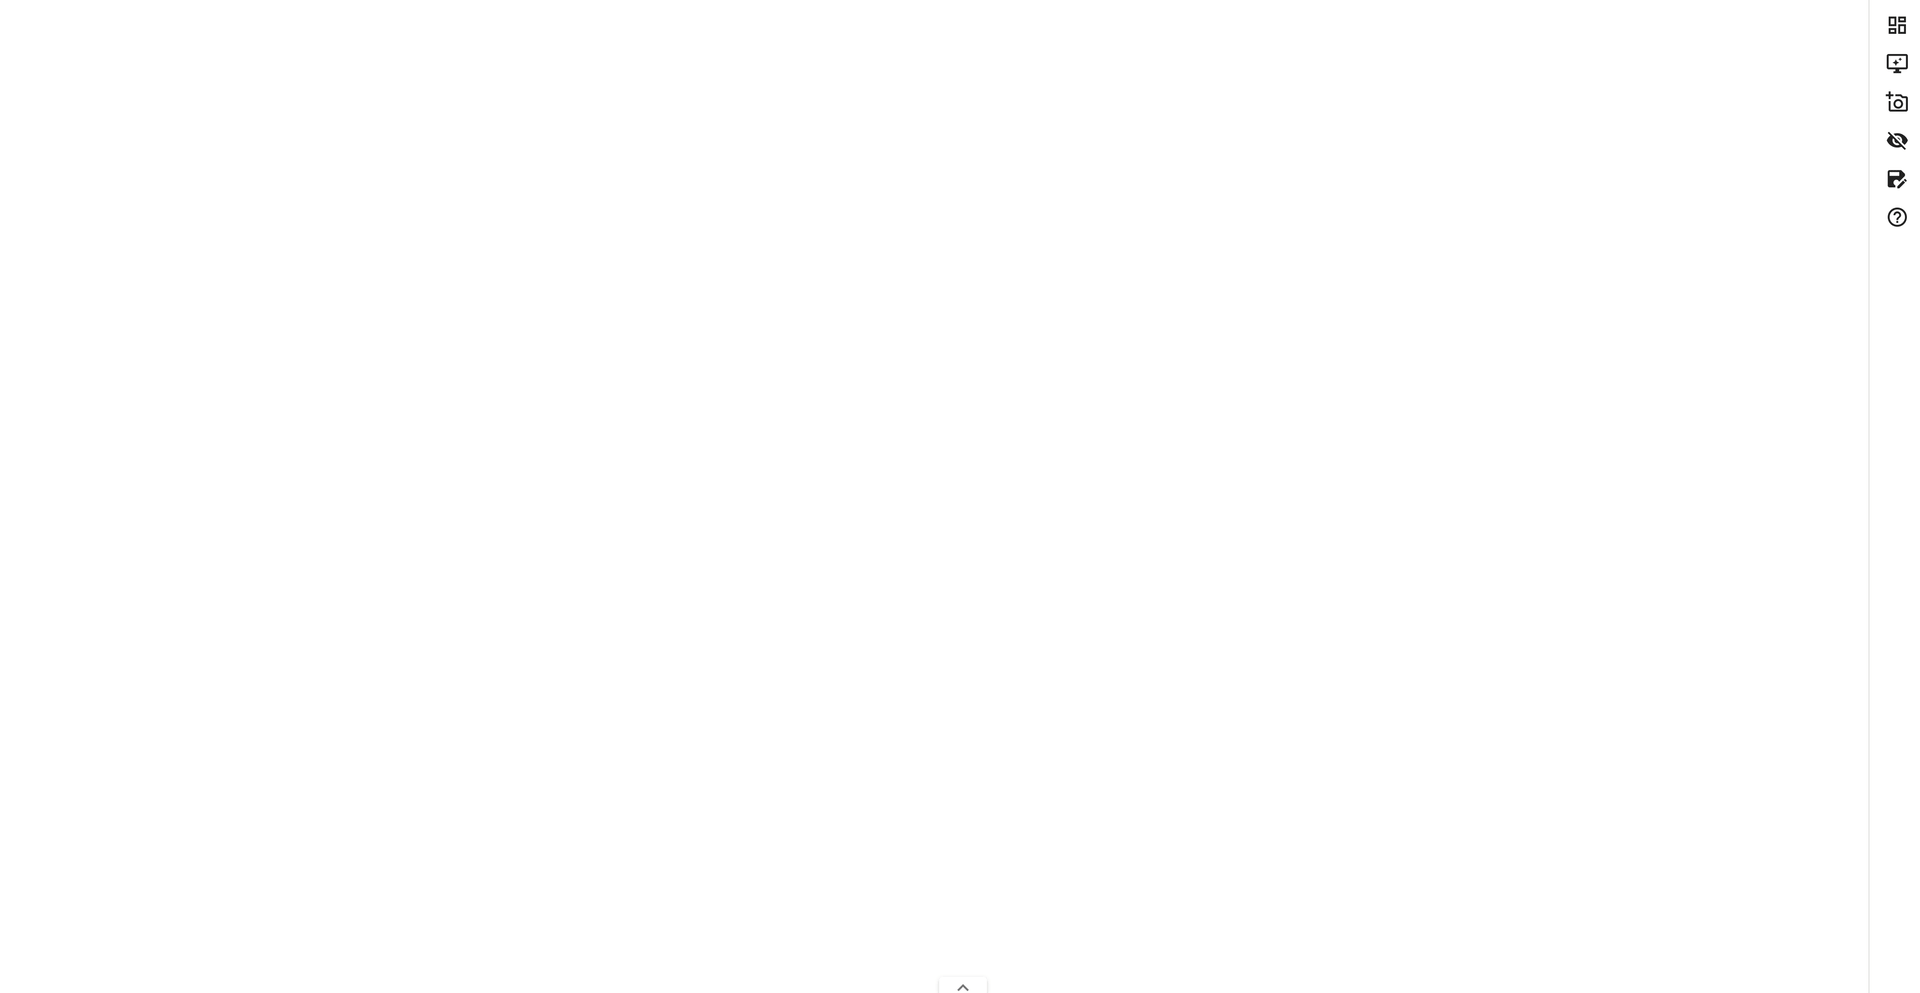 reverseclabs/awspx
A graph-based tool for visualizing effective access and resource relationships in AWS environments.
 awesom3alex/osint-menace
Passive OSINT triage console for email, username, domain, IP, and crypto wallet reconnaissance. Features case management, curated resource links, and…
 r00ts3c/ddos-rootsec
Explore RootSec's DDOS Archive, featuring top-tier scanners, powerful botnets (Mirai & QBot) and other variants, high-impact exploits, advanced…
 bishopfox/cirro-azcli-ext
Azure CLI extension for Cirro collection
 google/gcp_scanner
GCP resource scanner that evaluates access levels of compromised credentials by enumerating cloud services, projects, and IAM permissions across…
 nu11secur1ty/hackers-and-crackers
Educational resource explaining the ethical and technical differences between hackers and crackers, covering vulnerability analysis, system security,…
 stolichnayer/cve-2025-22828
Apache CloudStack vulnerability allows unauthorized access to annotations on certain resources.
 nu11secur1ty/xssight
Educational resource on Cross-site Scripting (XSS) attack techniques, covering non-persistent, persistent, and DOM-based vectors with practical…
 r00tpgp/http-pulse_ssl_vpn.nse
Nmap NSE script to detect Pulse Secure SSL VPN file disclosure CVE-2019-11510
 c411e/cve-2023-47564
CVE-2023-47564
 smarttfoxx/cve-2025-65321
Language Sloth Sloth Bot 1.0 is vulnerable to Directory Traversal in the gif() and png() functions. The functions build file paths using unsanitized…