

maltrail
 stamparm/maltrail
Real-time malicious traffic detection system using public blacklists, static malware trails, and heuristic analysis to identify threats across DNS,…
anomaly-detectionanti-botdefensive-tools+11
8.6k
stamparm/maltrailReal-time malicious traffic detection system using public blacklists, static malware trails, and heuristic analysis to identify threats across DNS,…
 projectdiscovery/httpx
Fast, multi-probe HTTP toolkit for reconnaissance and information gathering. Probes TLS, CSP, headers, tech stack, and CDN. Supports matchers,…
 findomain/findomain
The fastest and complete solution for domain recognition. Supports screenshoting, port scan, HTTP check, data import from other tools, subdomain…
 lgandx/responder
Responder is a LLMNR, NBT-NS and MDNS poisoner, with built-in HTTP/SMB/MSSQL/FTP/LDAP rogue authentication server supporting NTLMv1/NTLMv2/LMv2,…
 osyanina/westone-cve-2020-14883-scanner
A vulnerability scanner that detects CVE-2020-14883 vulnerabilities.
 gpiechnik2/nmap-cve-2022-21907
Repository containing nse script for vulnerability CVE-2022-21907. It is a component (IIS) vulnerability on Windows. It allows remote code execution.…
 yunemse48/403bypasser
Automates HTTP 403 access control bypass techniques using header manipulation, path obfuscation, and HTTP method conversion for web application…
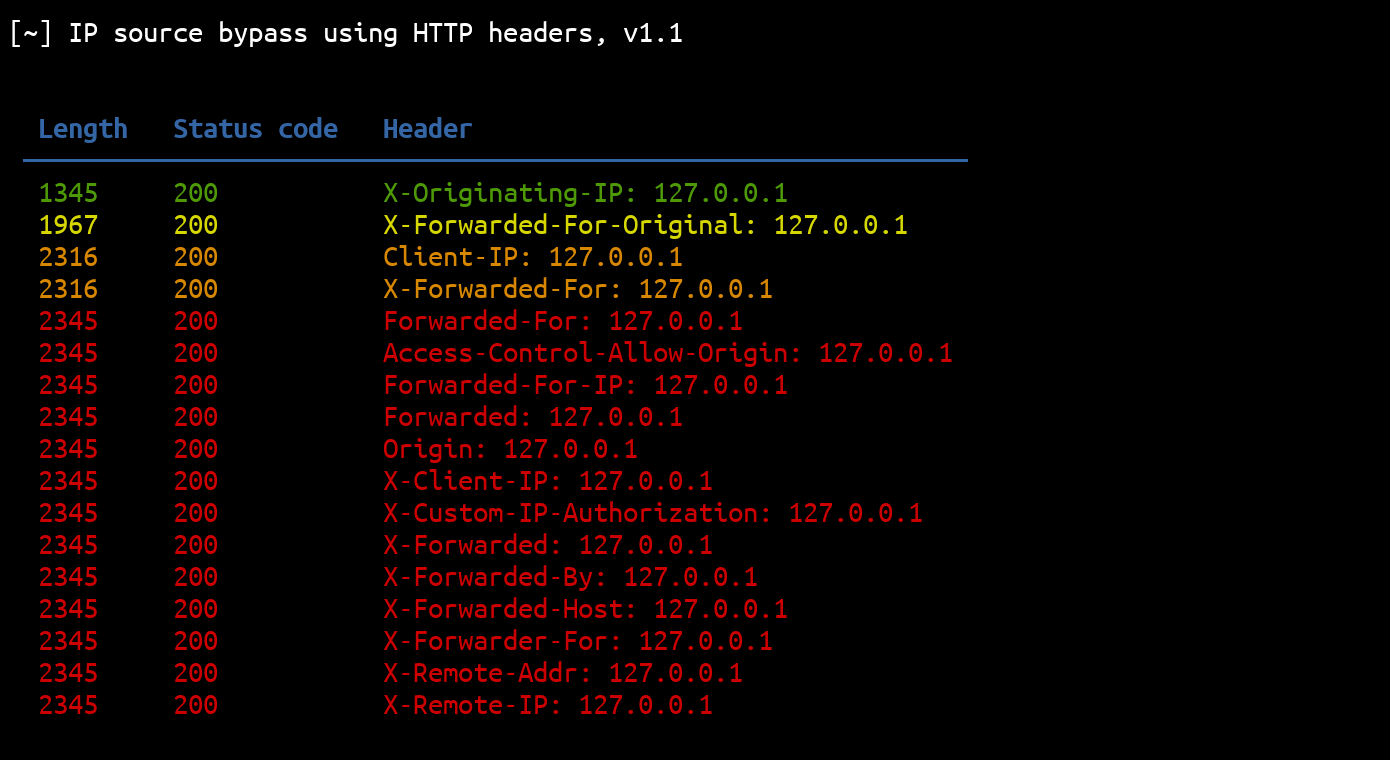 p0dalirius/ipsourcebypass
This Python script can be used to bypass IP source restrictions using HTTP headers.
 thoropass-public/area51
The exploit server for out-of-band findings. Point a target at a domain you own. Every HTTP request and every email it sends back lands in a…
 wattocyber/vegadns
Rust-based DNS enumeration and subdomain discovery tool for reconnaissance and penetration testing security assessments.
 lgandx/pcredz
This tool extracts Credit card numbers, NTLM(DCE-RPC, HTTP, SQL, LDAP, etc), Kerberos (AS-REQ Pre-Auth etype 23), HTTP Basic, SNMP, POP, SMTP, FTP,…
 henshin/filebuster
An extremely fast and flexible web fuzzer
 morph3/crawpy
Asynchronous HTTP content discovery tool with auto-calibration, recursive scanning, and report generation for enumerating hidden web directories and…
 tarlogicsecurity/arecibo
Endpoint for Out-of-Band Exfiltration (DNS & HTTP)
 smiegles/mass3
Multi-threaded DNS-based enumeration tool for discovering AWS S3 buckets using pre-compiled wordlists and custom DNS resolvers, with optional Docker…
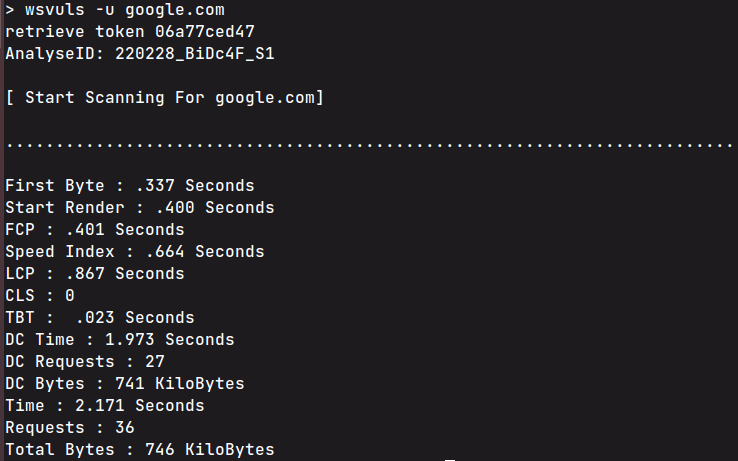 anouarbensaad/wsvuls
CLI website vulnerability scanner that detects outdated server software, insecure HTTP headers, and extracts Cloudflare IP/port data with performance…

 xmohamed0/cve-2021-41773
Shell-based exploit for CVE-2021-41773 targeting Apache HTTP Server path traversal vulnerability, enabling unauthenticated remote file disclosure and…