

BurpMetaFinder
 josue87/burpmetafinder
Burp Suite extension for extracting metadata from files
forensicsinformation-gatheringosint+1
josue87/burpmetafinderBurp Suite extension for extracting metadata from files
 hisxo/jspector
A simple Burp Suite extension to crawl JavaScript (JS) files in passive mode and display the results directly on the issues
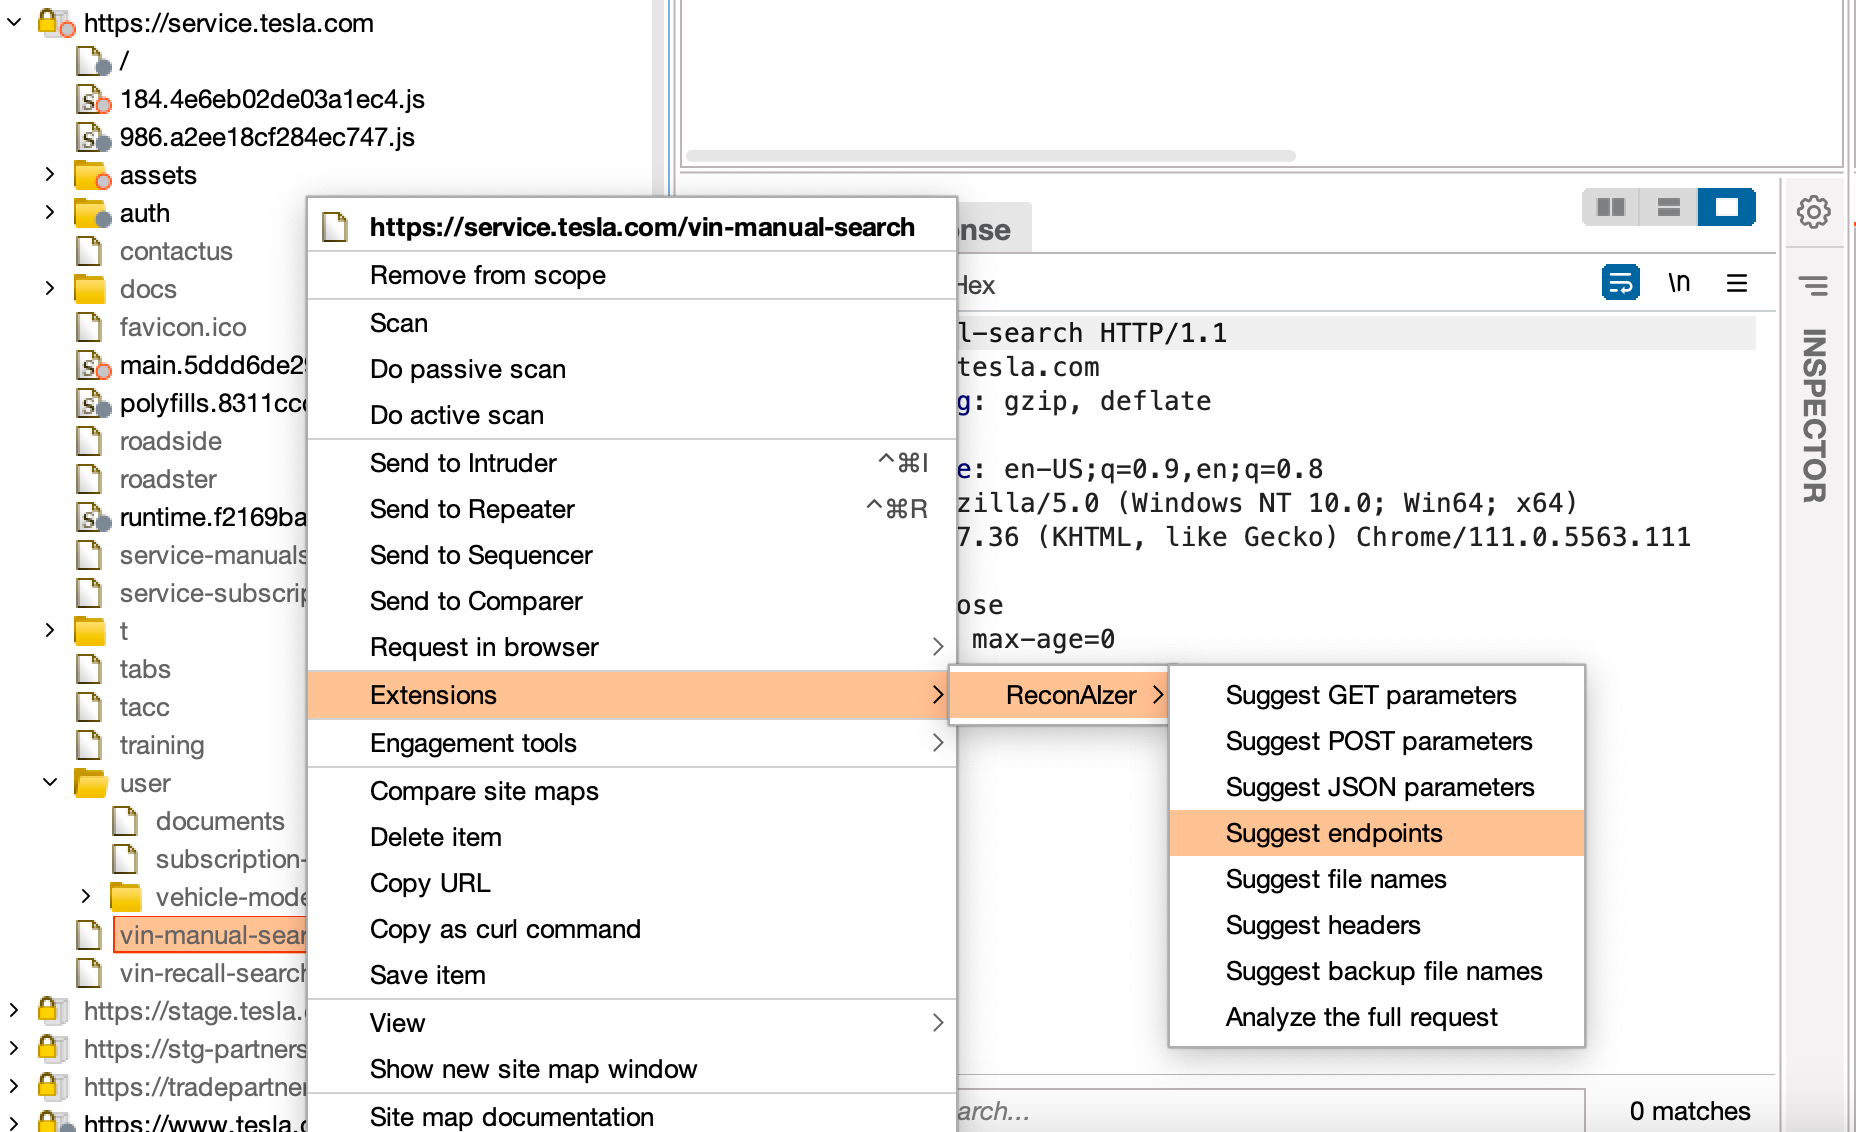 hisxo/reconaizer
A Burp Suite extension to add OpenAI (GPT) on Burp and help you with your Bug Bounty recon to discover endpoints, params, URLs, subdomains and more!
 moeinfatehi/admin-panel_finder
Burp Suite extension that finds exposed admin panels and login pages of web applications and infrastructure. 1,000+ payloads, OWASP WSTG-CONF-05.
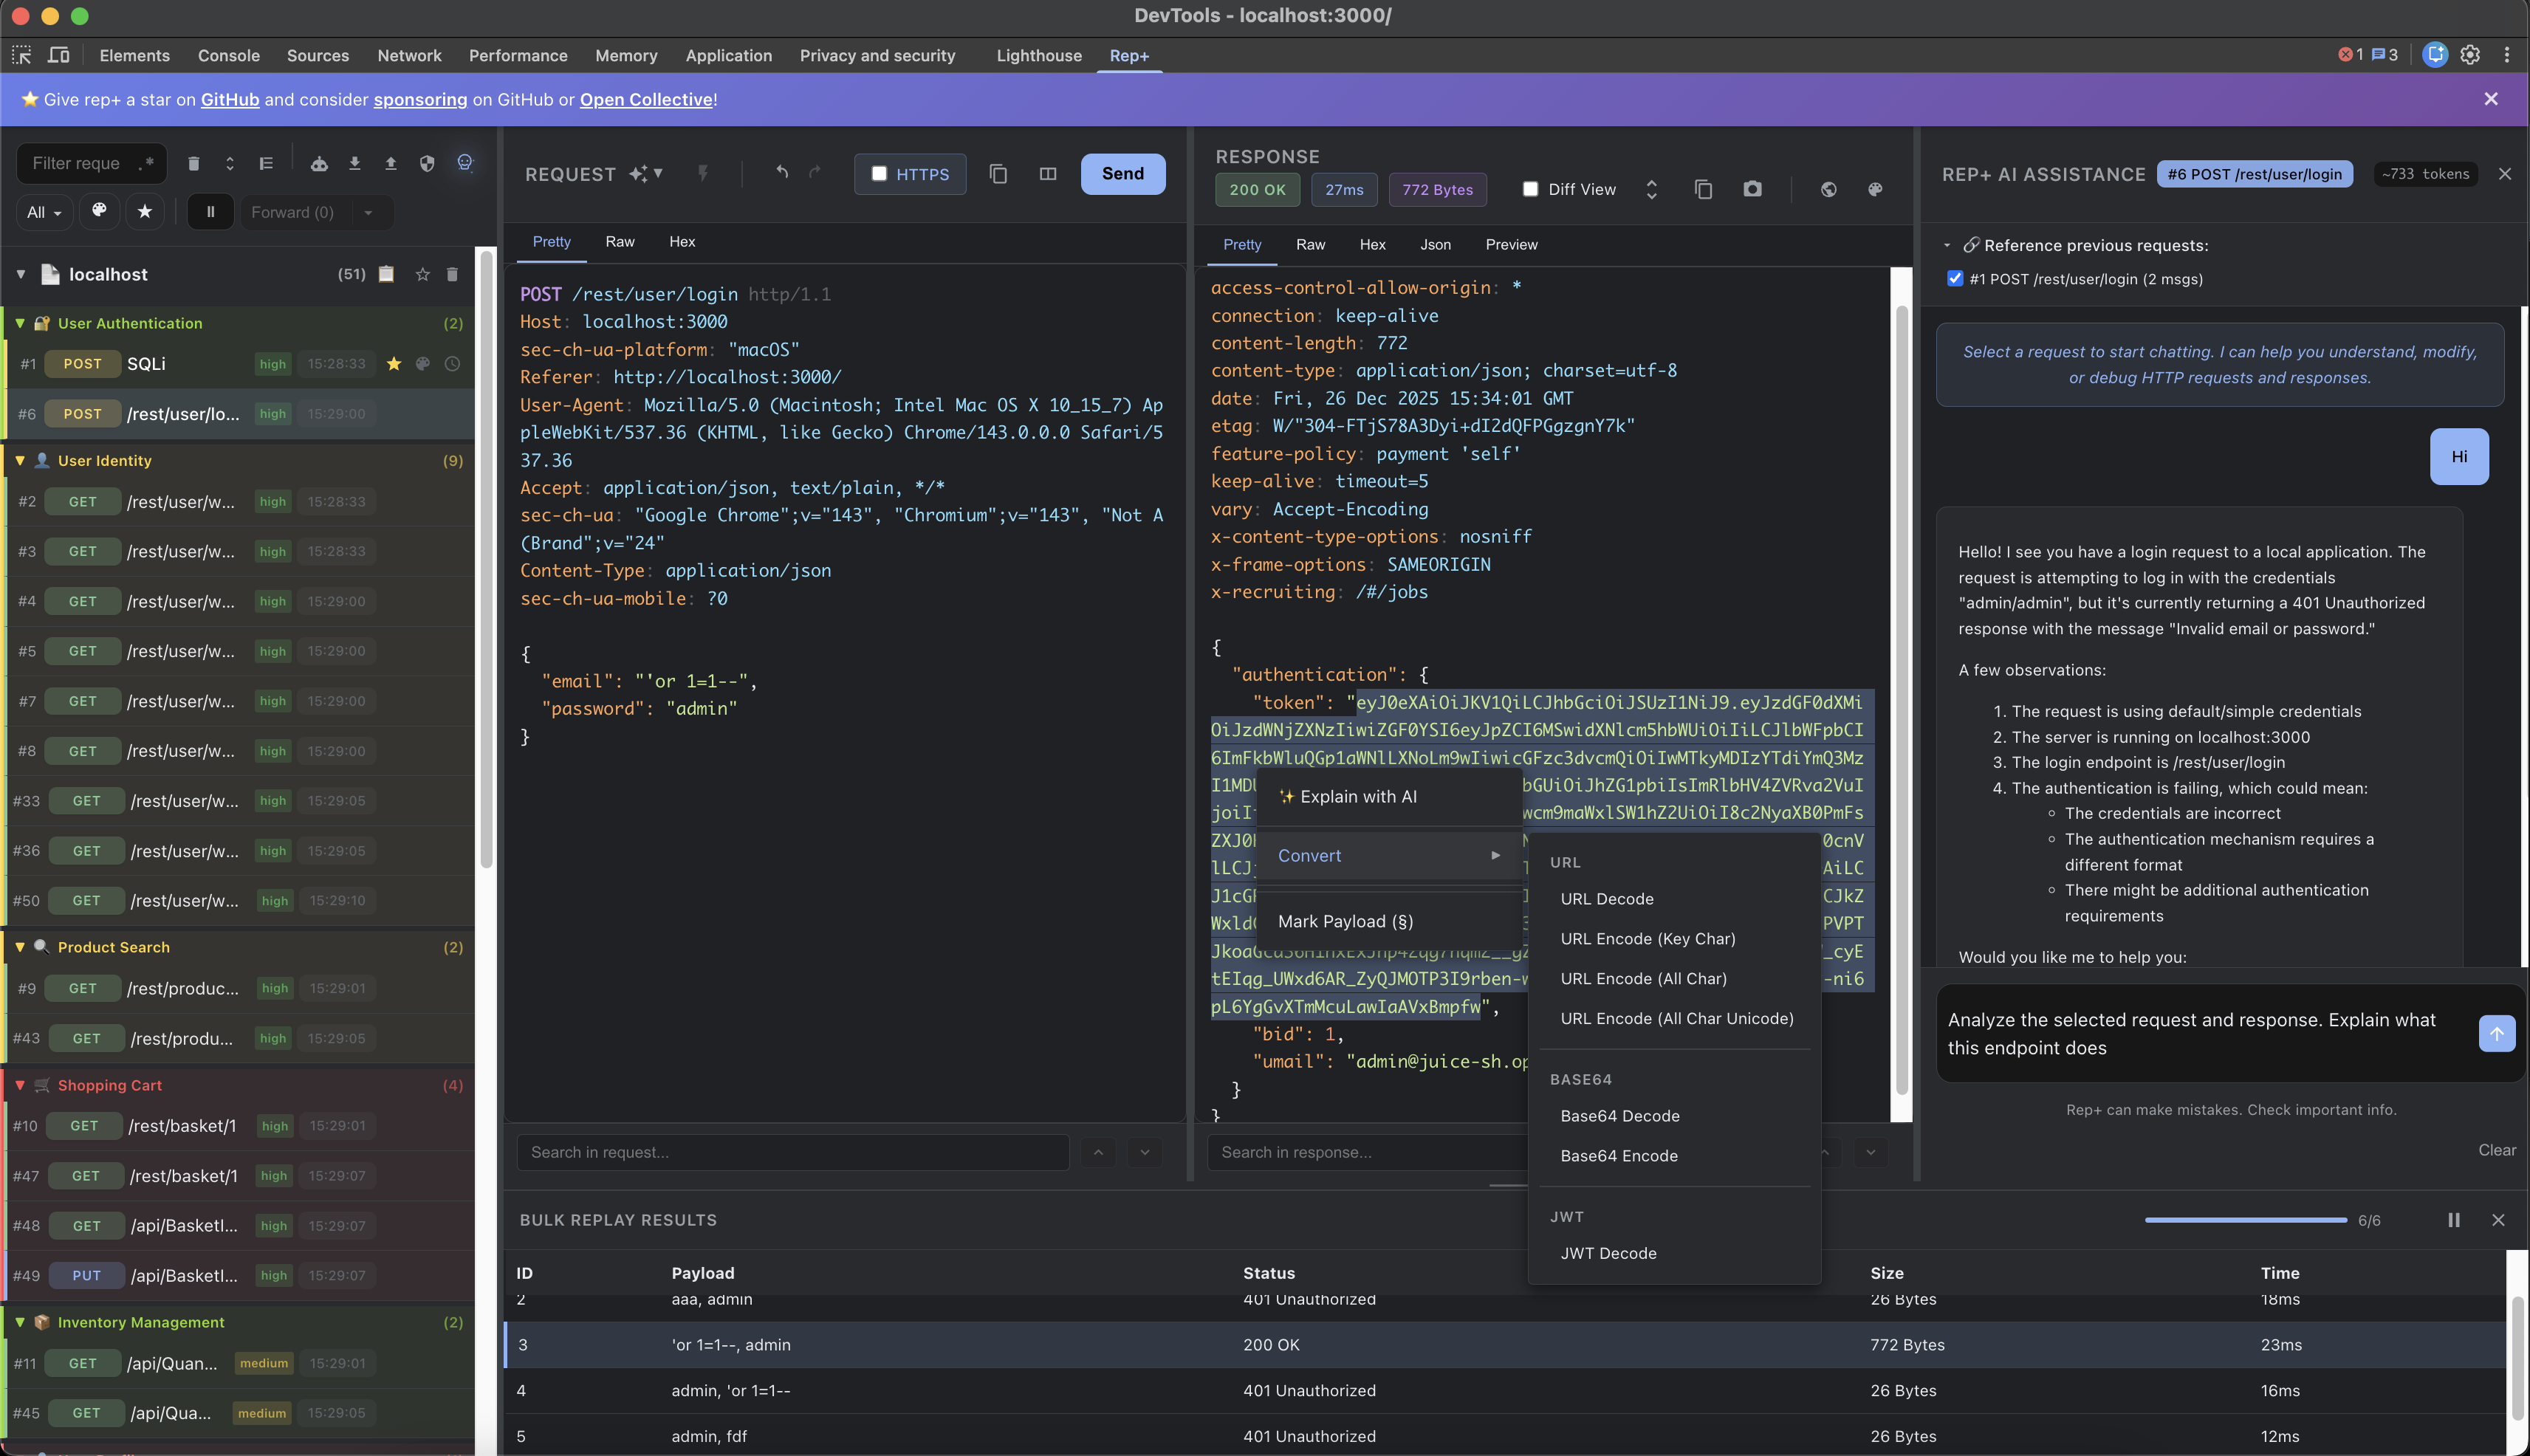 repplus/rep-chrome
rep+ — Burp-style HTTP Repeater for Chrome DevTools with built‑in AI to explain requests and suggest attacks
 jenish-sojitra/jsanalyzer
Burp Suite extension for JavaScript static analysis: extracts API endpoints, URLs, secrets, and emails with noise filtering for web security testing.
 hoodoer/js-tap
JavaScript beacons and C2 to be used for XSS payload or post exploitation implants on webapp servers or desktop software to monitor users and…
 akabe1/oauthscan
Burp Suite Extension useful to verify OAUTHv2 and OpenID security
 0x999-x/jsluicepp
jsluice++ is a Burp Suite extension designed for passive and active scanning of JavaScript traffic using the CLI tool jsluice
 portswigger/oauth-scan
Burp Suite Extension useful to verify OAUTHv2 and OpenID security
 overspace-labs/hae
Modular Burp Suite extension for fine-grained highlighting and extraction of sensitive data from HTTP and WebSocket traffic, enabling efficient…
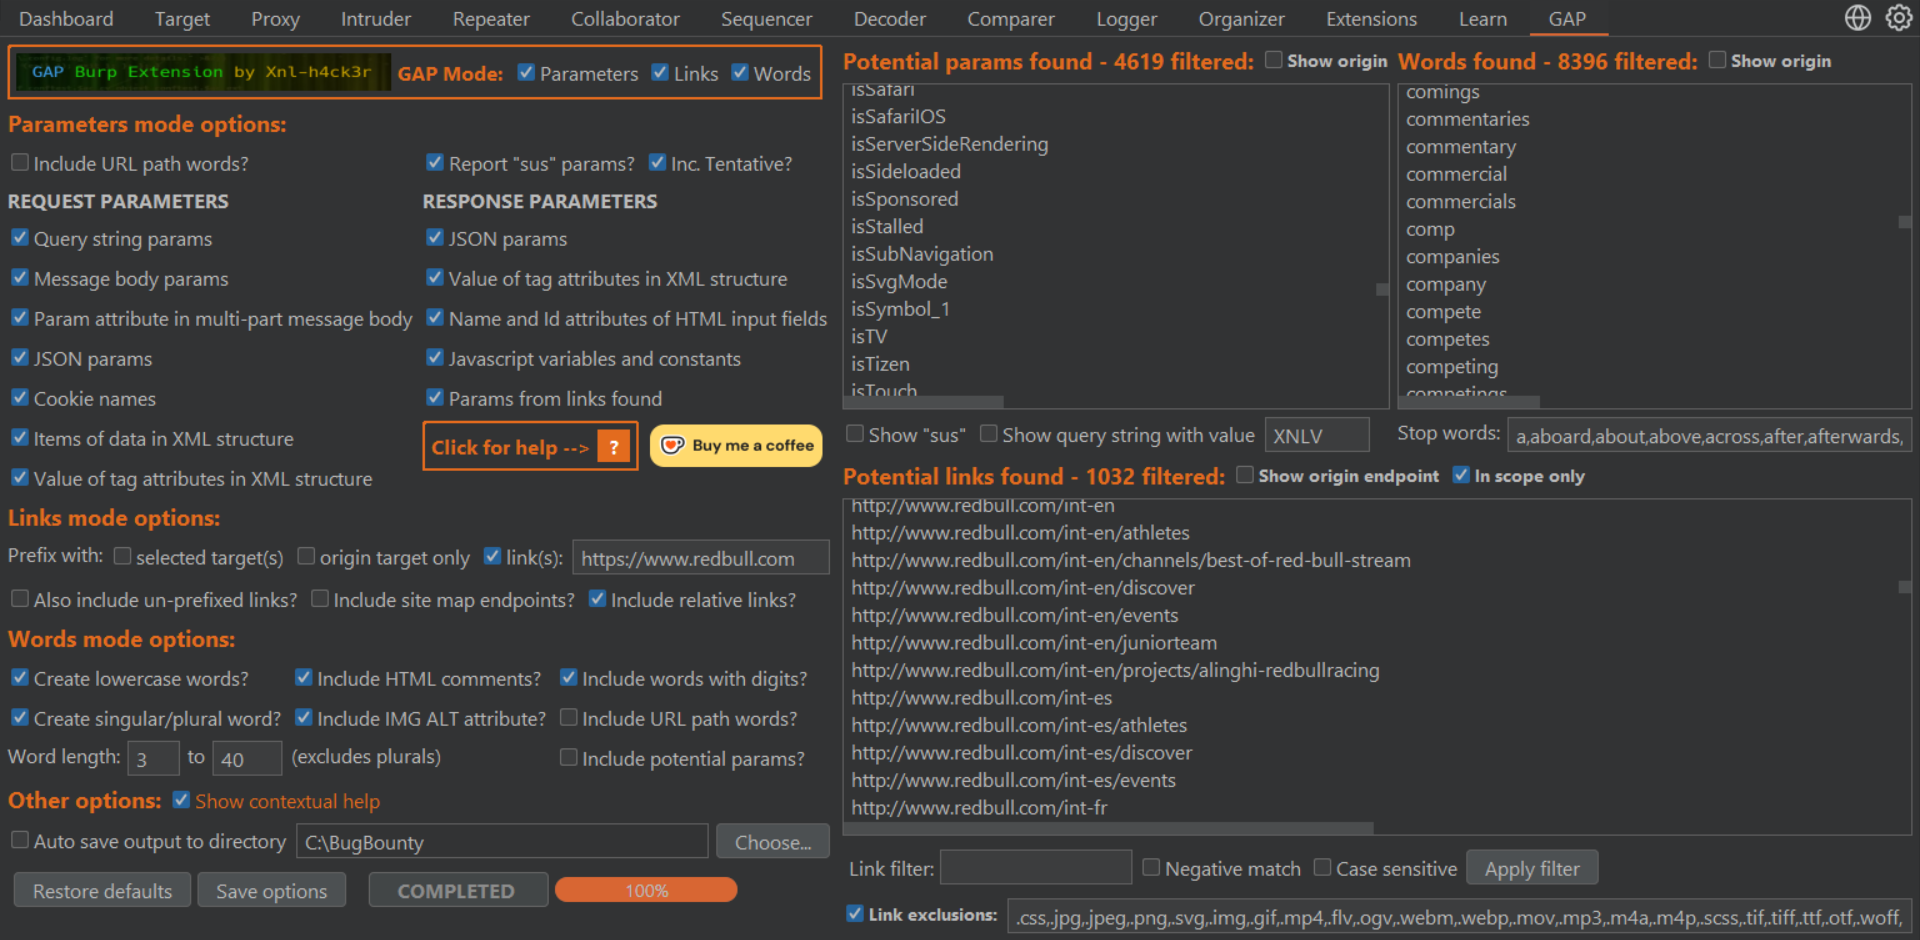 xnl-h4ck3r/gap-burp-extension
Burp Extension to find potential endpoints, parameters, and generate a custom target wordlist
 4ier/neo
Turn any web app into an API. Chrome extension captures browser traffic, auto-generates schemas, lets AI replay APIs directly. No official API needed.
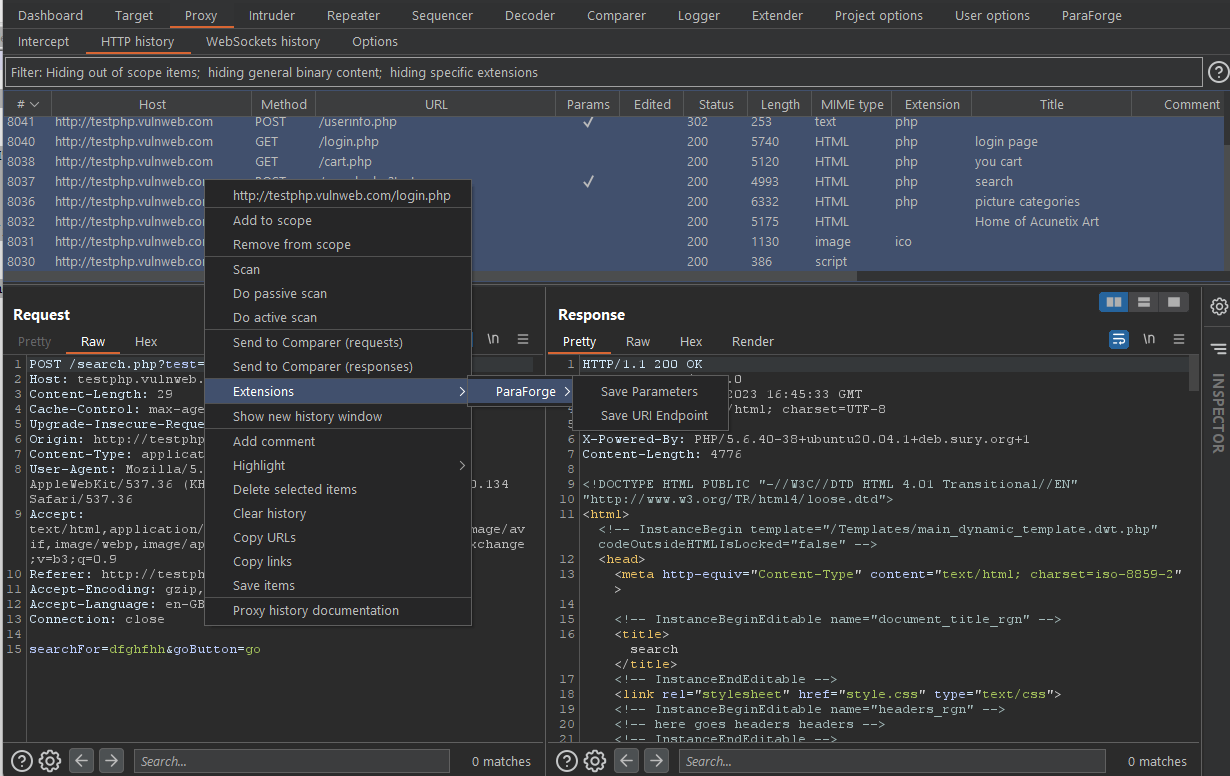 anof-cyber/paraforge
A BurpSuite extension to create a custom word-list of endpoint and parameters for enumeration and fuzzing
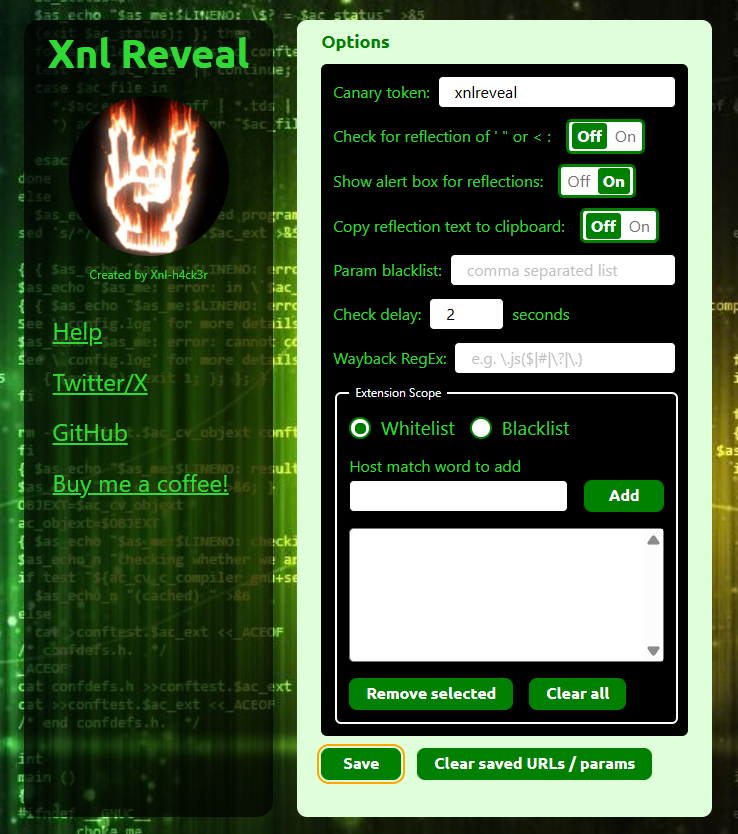 xnl-h4ck3r/xnlreveal
A Chrome/Firefox browser extension to show alerts for reflected query params, show Wayback archive links for the current path, show hidden elements…
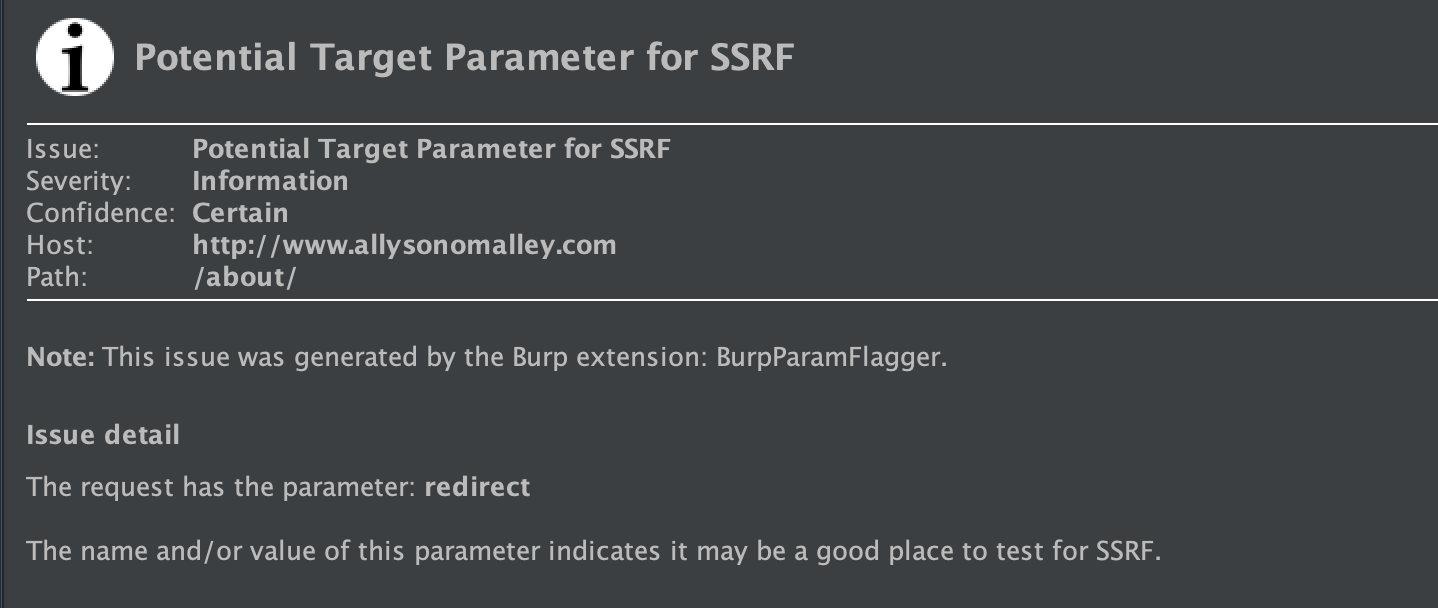 allyomalley/burpparamflagger
A Burp extension adding a passive scan check to flag parameters whose name or value may indicate a possible insertion point for SSRF or LFI.
 synacktiv/extloader
A chromium extension exploitation toolkit
 toanln-cov/cve-2026-66491
The Joomla extension PhocaCommander is vulnerable to Path Traversal in the getSource function - CVSS 8.2