

Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
76 results
scan preview

scan

GitHubatomdrift-project/scan

0-day malware detection for binaries, source & scripts (that doesn't suck)

binary-analysiscode-analysisdefensive-tools+9
22412h 49m ago
ShellSCope preview

ShellSCope

GitHubd0rb/shellscope

Defensive exposure auditor for Plex2Shell and php2shell — find your own before they find you.
configuration-auditingdefensive-toolsdevsecops+7
11 days ago
five-nights-at-follina-s preview

five-nights-at-follina-s

GitHubjeffreybxu/five-nights-at-follina-s

A Fullstack Academy Cybersecurity project examining the full cycle of the Follina (CVE-2022-30190) vulnerability, from exploit to detection and…
defensive-toolseducationexploitation+4
24 years ago
SOC274-Palo-Alto-Networks-PAN-OS-Command-Injection-Vulnerability-Exploitation-CVE-2024-3400 preview

SOC274-Palo-Alto-Networks-PAN-OS-Command-Injection-Vulnerability-Exploitation-CVE-2024-3400

GitHubhashdr1ft/soc274-palo-alto-networks-pan-os-command-injection-vulnerability-exploitation-cve-2024-3400

SOC lab exercise for analyzing and responding to Palo Alto Networks PAN-OS command injection vulnerability (CVE-2024-3400) with step-by-step incident…
command-and-controleducationincident-response+3
11 year ago
Arbitrary-File-Read-CVE-2024-24919 preview

Arbitrary-File-Read-CVE-2024-24919

GitHubluismateo1/arbitrary-file-read-cve-2024-24919

Walkthrough of detecting, investigating, and responding to a CVE-2024-24919 path traversal attack, including log analysis, threat intel checks, and…
educationexploitationincident-response+3
1 year ago
plex2shell_pcap preview

plex2shell_pcap

GitHubboredhackerblog/plex2shell_pcap

Packet capture artifacts of plex2shell exploitation against Plex, including lab and in-the-wild traffic, for building and validating detection…
exploitationincident-responsenetwork-forensics+3
114 days ago
-SOC342---CVE-2025-53770-SharePoint-ToolShell-Auth-Bypass-and-RCE preview

-SOC342---CVE-2025-53770-SharePoint-ToolShell-Auth-Bypass-and-RCE

GitHubbossnick98/-soc342---cve-2025-53770-sharepoint-toolshell-auth-bypass-and-rce

An activity to train analysis skills and reporting
educationexploitationforensics+5
1 year ago
log4j preview

log4j

GitHubwortell/log4j

Repo containing all info, scripts, etc. related to CVE-2021-44228
curated-resourceseducationexploitation+6
94 years ago
CVE-2026-48908 preview

CVE-2026-48908

GitHub0xblackash/cve-2026-48908

CVE-2026-48908
exploitationincident-responsepenetration-testing+3
24 months ago
CVE-2020-14882-weblogicRCE preview

CVE-2020-14882-weblogicRCE

GitHubcorelight/cve-2020-14882-weblogicrce

Detection of RCE in Oracle's WebLogic Server CVE-2020-14882 / CVE-2020-14750
exploitationincident-responseintrusion-detection+3
75 years ago
cve-2021-44228-qingteng-online-patch preview

cve-2021-44228-qingteng-online-patch

GitHubqingtengyun/cve-2021-44228-qingteng-online-patch

Hot-patch CVE-2021-44228 by exploiting the vulnerability itself.
command-and-controlexploitationincident-response+3
254 years ago
Log4Shell-PoC preview

Log4Shell-PoC

GitHubjosemariamicoli/log4shell-poc

**Log4Shell PoC is a high-fidelity exploitation environment designed to replicate the CVE-2021-44228 vulnerability.** It provides a containerized…
command-and-controleducationexploitation+6
9 months ago
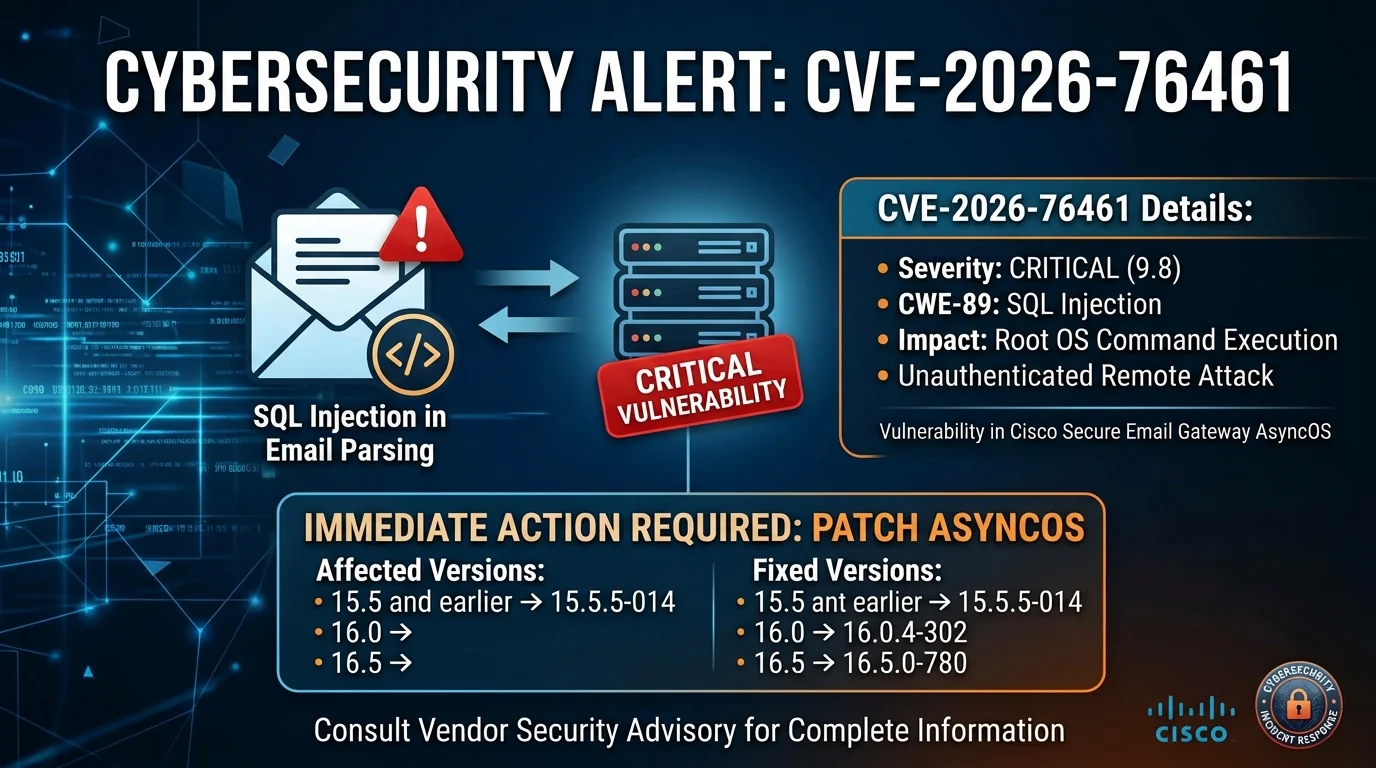
CVE-2026-76461 preview

CVE-2026-76461

GitHub0xblackash/cve-2026-76461

Research repository for CVE-2026-76461, a critical SQL injection in Cisco Secure Email Gateway leading to root RCE, with detection rules, mitigation…

educationemail-securityexploitation+7
21 month ago
GPEWebDefender preview

GPEWebDefender

GitHubgopasteverything/gpewebdefender

Lightweight web-attack monitor. One Go binary + SQLite. Not OSSEC, not a WAF.
defensive-toolsincident-responseinformation-gathering+8
52 months ago
CVE-2026-48908-joomla-sp-page-builder-detection preview

CVE-2026-48908-joomla-sp-page-builder-detection

GitHubg0thamrabb1t/cve-2026-48908-joomla-sp-page-builder-detection

Validates CVE-2026-48908 in Joomla SP Page Builder with unauthorized icon upload leading to PHP code execution. Includes auditd/PCAP evidence, event…
educationexploitationforensics+6
3 months ago
CVE-2022-30190 preview

CVE-2022-30190

GitHubernestak/cve-2022-30190

Official guidance and workarounds for CVE-2022-30190, a remote code execution vulnerability in the Microsoft Support Diagnostic Tool (MSDT)…
defensive-toolseducationexploitation+3
4 years ago
veilgate preview

veilgate

GitHubc0oki3s/veilgate

Asymmetric defense against adversarial AI agents. VeilGate evaluates each incoming request, redirects suspected agents into a per-IP-consistent…
ai-securityanomaly-detectionanti-bot+6
154 months ago
CVE-2025-49706-SharePoint-Spoofing-Vulnerability-Under-Active-Exploitation preview

CVE-2025-49706-SharePoint-Spoofing-Vulnerability-Under-Active-Exploitation

GitHubadityabhatt3010/cve-2025-49706-sharepoint-spoofing-vulnerability-under-active-exploitation

A deep dive into CVE-2025-49706 — the SharePoint spoofing flaw now exploited in the wild for stealthy web shell deployment and privilege escalation.

educationexploitationincident-response+6
181 year ago
Previous12345Next