CVE-2022-26134-Exploit-Detection

This repository contains Yara rule and the method that a security investigator may want to use for CVE-2022-26134 threat hunting on their Linux…

This repository contains Yara rule and the method that a security investigator may want to use for CVE-2022-26134 threat hunting on their Linux…

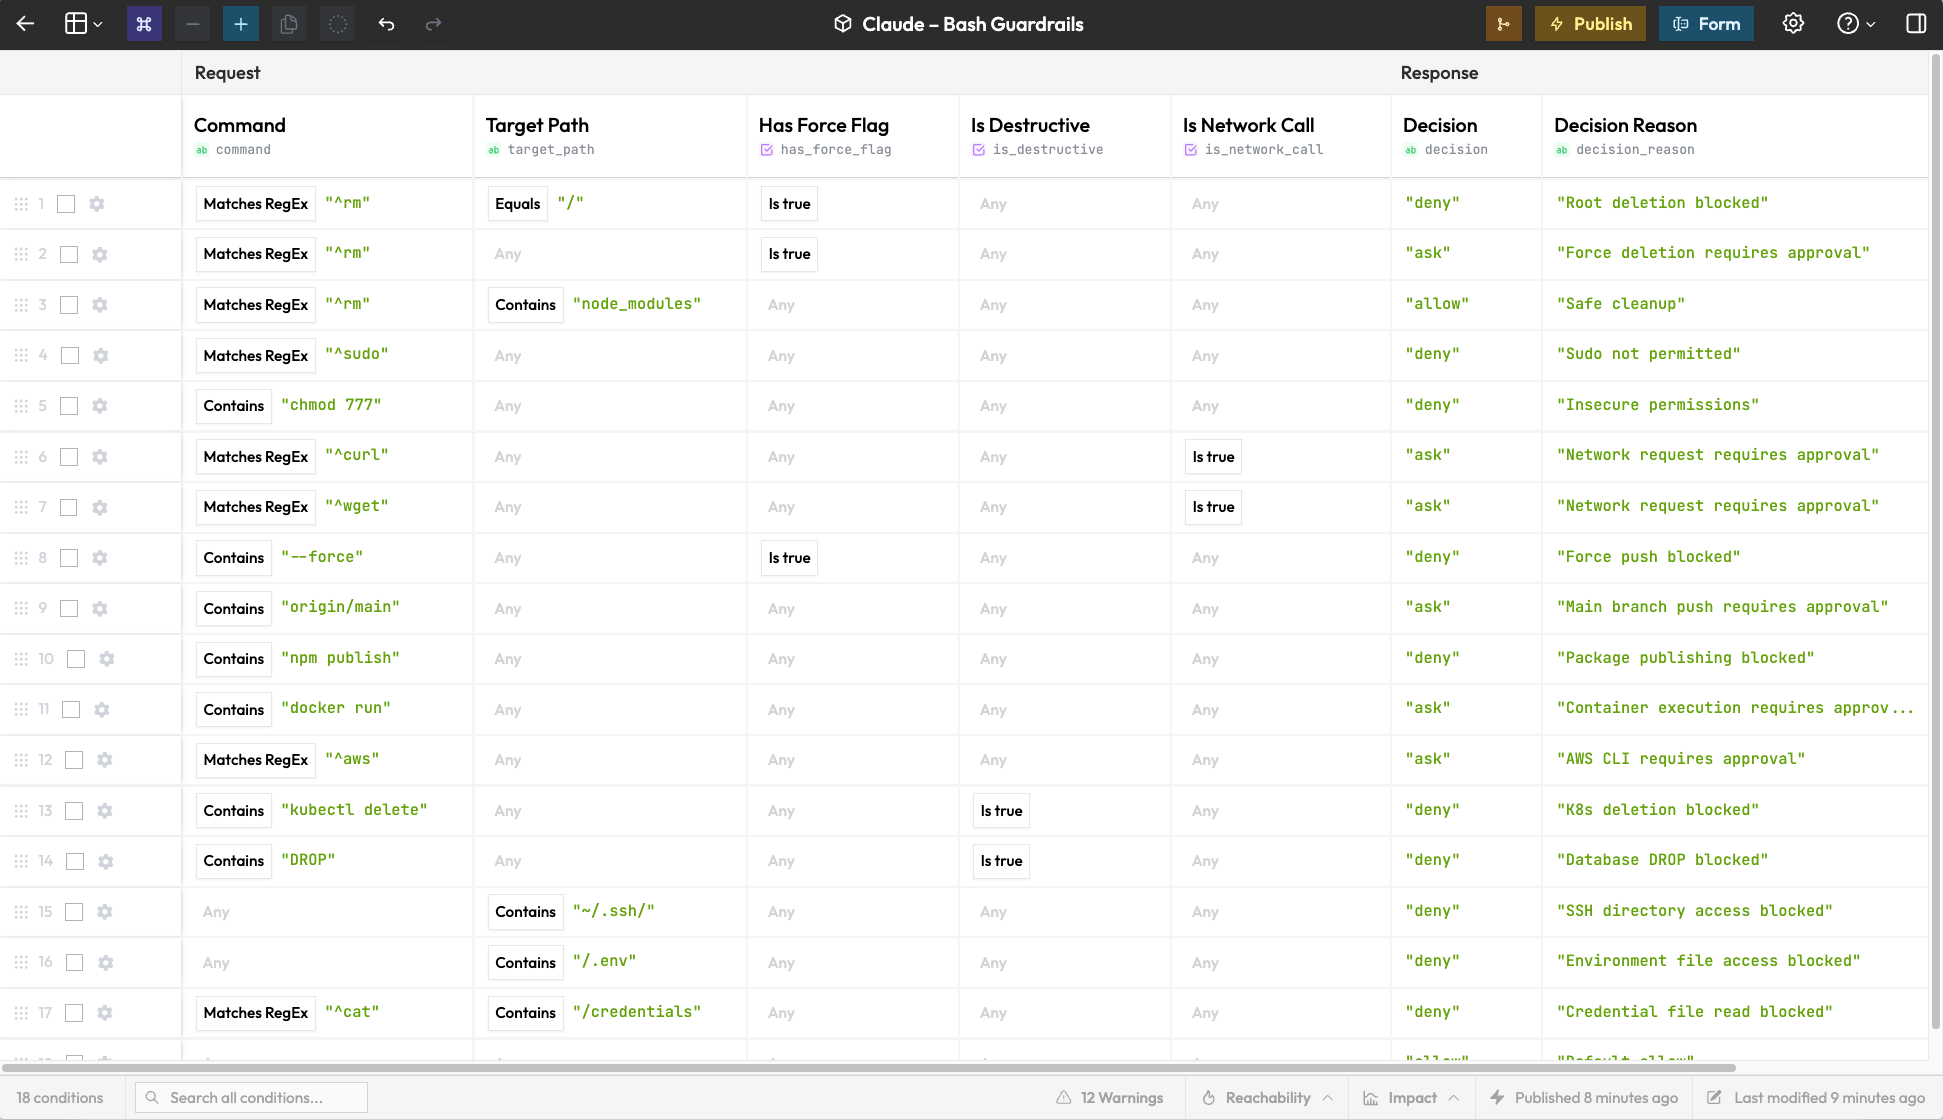
Real-time guardrails for Claude Code tool calls.

Anti-Virus for K8s. Protect your Applications running on Kubernetes from malicious attacks with pre-registered source code, runtime processes…

A Simple Ransomware Vaccine

Welcome to the NCC Group Threat Intelligence Alert repo, here you will find the alerts which we have raised to our customers regarding intelligence…

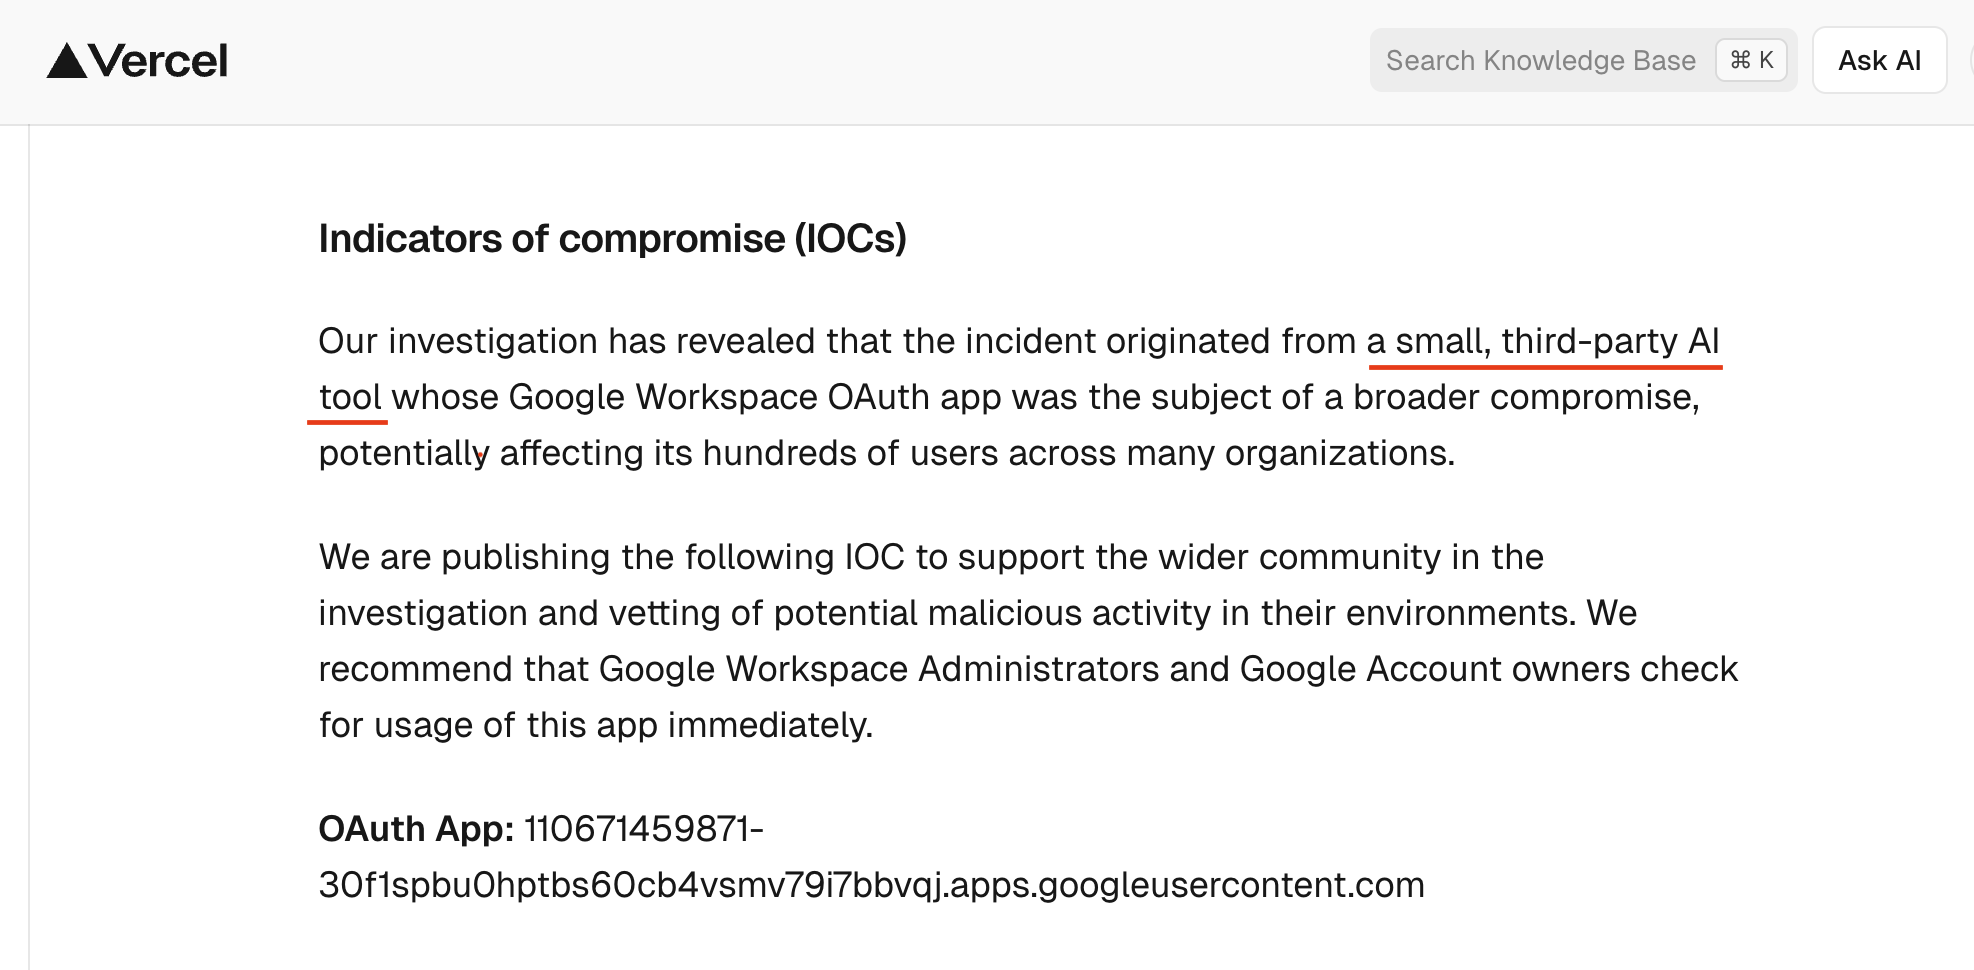
This is an incident response playbook we created for the Vercel April 2026 compromise

This repository contains all gathered resources we used during our Incident Reponse on CVE-2021-44228 and CVE-2021-45046 aka Log4Shell.

Data we are receiving from our honeypots about CVE-2021-44228

A resource containing all the tools each ransomware gangs uses

Useful resources for SOC Analyst and SOC Analyst candidates.

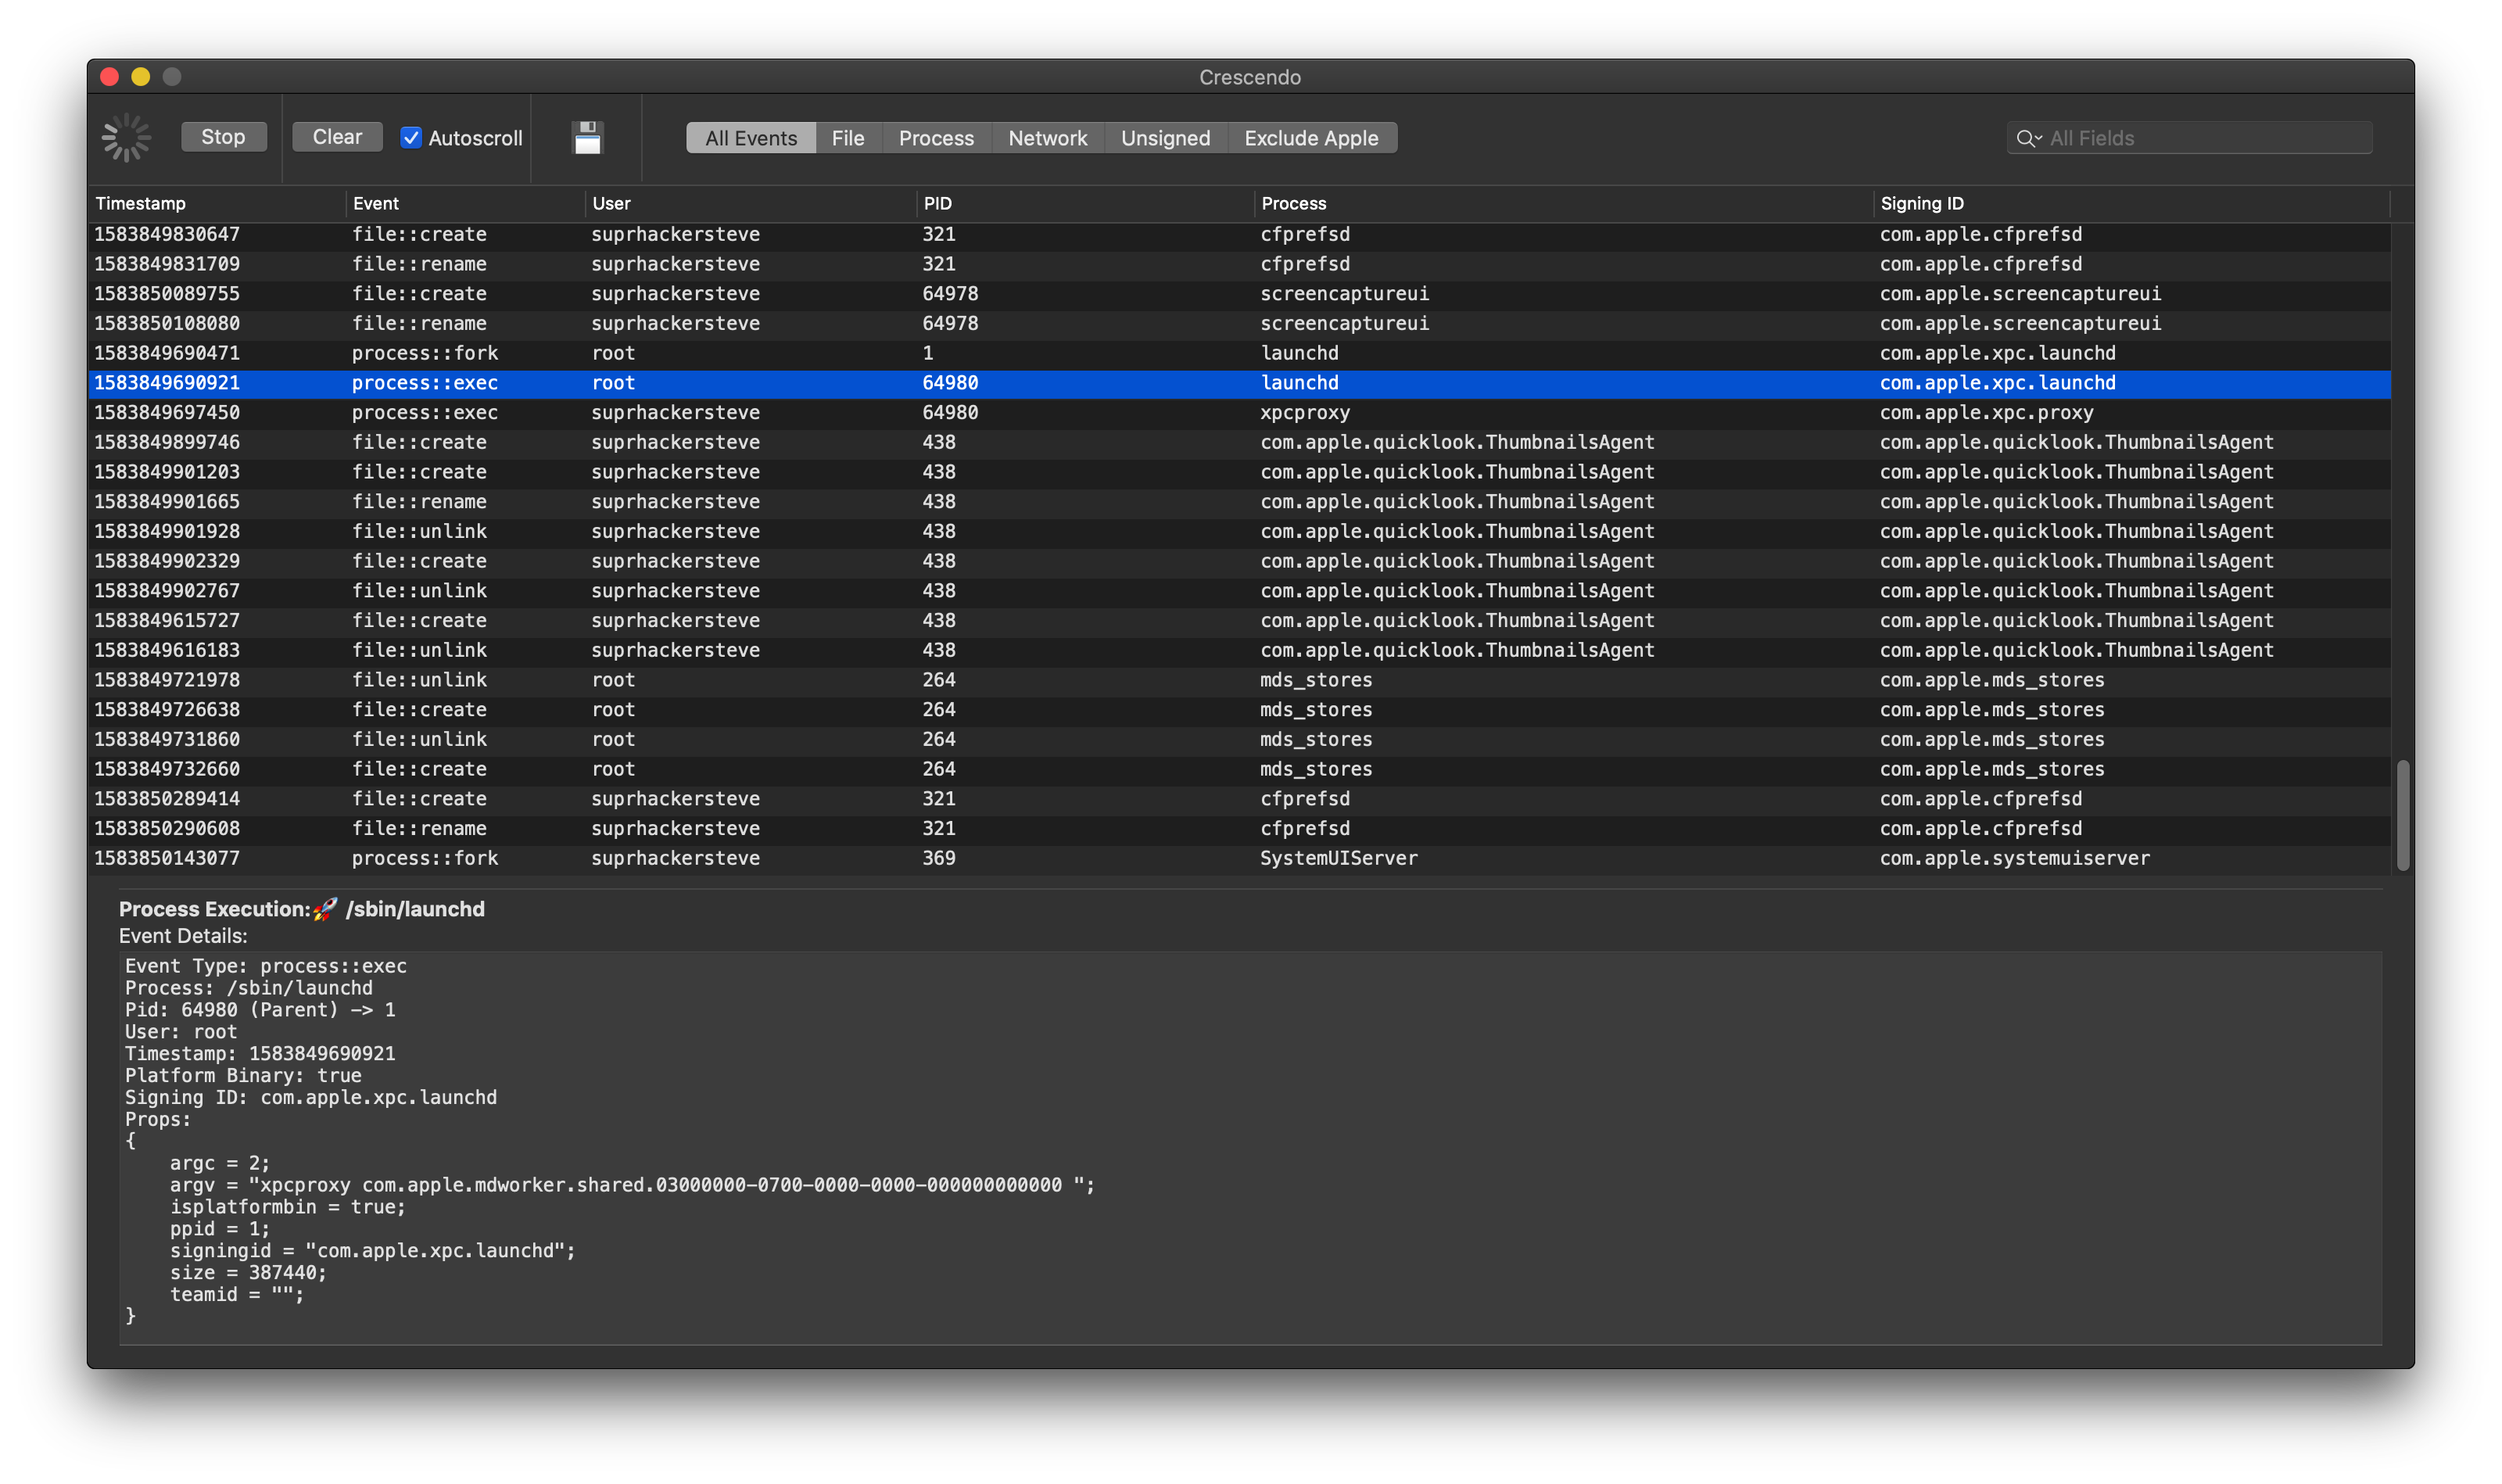
Crescendo is a swift based, real time event viewer for macOS. It utilizes Apple's Endpoint Security Framework.

Live Windows forensic acquisition tool that collects system artefacts (registry, memory, disk, files) into CSV/JSON for early compromise detection…

Collection of YARA rules for hunting malware, malicious Office documents, and exploit artifacts, with references to samples and research write-ups.


Technical dossier on the DPRK-linked PolinRider supply-chain attack, documenting obfuscated JS payload injection, git history manipulation, C2…

ETW-based Windows process creation logger that enriches events with file hashes, signatures, and parent process details, outputting to Windows…

Curated collection of detection rules and IOCs extracted from DFIR engagements and malware analyses to support threat hunting, incident response, and…

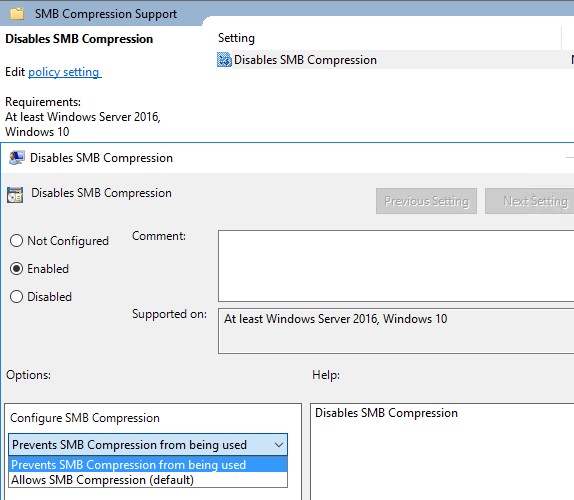
CVE-2020-0796 Flaw Mitigation - Active Directory Administrative Templates