
Skip to content
KitploitKITPLOIT
ToolsBlog
Submit
ToolsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
19 results
CVE-2025-31702 preview

CVE-2025-31702

GitHubitres-labs/cve-2025-31702

Repository with tools, exploits, and material associated with the analysis and discovery process of CVE-2025-31702 and other related security issues.
digital-forensicsexploitationincident-response+3
10
9 months ago
ThreatSentry-AI preview

ThreatSentry-AI

GitHubeclipsemanic/threatsentry-ai

ThreatSentry AI is an intelligent threat hunting dashboard that leverages machine learning to proactively identify and prioritize risks in your…
defensive-toolsincident-responseinformation-gathering+6
17 months ago
Microsoft-Extractor-Suite preview

Microsoft-Extractor-Suite

GitHubinvictus-ir/microsoft-extractor-suite

A PowerShell module for acquisition of data from Microsoft 365 and Azure for Incident Response and Cyber Security purposes.
cloud-securitydigital-forensicsincident-response+3
8482 months ago
DetectWindowsCopyOnWriteForAPI preview

DetectWindowsCopyOnWriteForAPI

GitHubnccgroup/detectwindowscopyonwriteforapi

Enumerate various traits from Windows processes as an aid to threat hunting

anomaly-detectiondefensive-toolsforensics+3
1984 years ago
IntelligentProcessLifecycle preview

IntelligentProcessLifecycle

GitHubd3sre/intelligentprocesslifecycle

The Intelligent Process Lifecycle of Active Cyber Defenders

configuration-auditingcurated-resourceseducation+6
343 years ago
Log4jPatch preview
Archived

Log4jPatch

GitHubsimonis/log4jpatch

Deploys an agent to fix CVE-2021-44228 (Log4j RCE vulnerability) in a running JVM process

exploitationincident-responsevulnerability-analysis
1084 years ago
CVE-2025-61155 preview

CVE-2025-61155

GitHubsf0rzin/cve-2025-61155

CVE-2025-61155 — arbitrary process termination in GameDriverX64.sys (Tower of Fantasy anti-cheat). Original IDA Pro teardown, PoC, YARA, IOCs,…

binary-analysiseducationexploitation+7
32 months ago
MemProcFS-Analyzer preview

MemProcFS-Analyzer

GitHublethal-forensics/memprocfs-analyzer

Automates Windows memory forensics and DFIR workflows with MemProcFS: YARA/ClamAV scanning, process anomaly detection, and artifact/log extraction.
anomaly-detectiondigital-forensicsincident-response+5
73617 days ago
Douglas-042 preview

Douglas-042

GitHubemrekybs/douglas-042

Triages a suspect Windows machine in minutes. Collects processes, services, autoruns, event logs and forensic artifacts, flags attacker activity, and…

forensicsincident-responseinformation-gathering+1
4524 days ago
CVE-2022-29072 preview

CVE-2022-29072

GitHubsentinelblue/cve-2022-29072

** DISPUTED ** 7-Zip through 21.07 on Windows allows privilege escalation and command execution when a file with the .7z extension is dragged to the…

exploitationincident-responselog-analysis+3
84 years ago
Vidar-Stealer-Reverse-Engineering preview

Vidar-Stealer-Reverse-Engineering

GitHubkaandemir993/vidar-stealer-reverse-engineering

"In-depth reverse engineering analysis of Vidar Stealer 2.0 covering Task Scheduler tampering (1999 timestamps), Explorer.exe process hollowing, and…
binary-analysiseducationforensics+7
22 months ago
clawdstrike preview

clawdstrike

GitHubbackbay-labs/clawdstrike

Policy engine and EDR for AI agent fleets and developer workstations. Monitors tool calls, file access, network flows, and process execution with…
ai-securitycloud-securitycontainer-security+5
28823 days ago
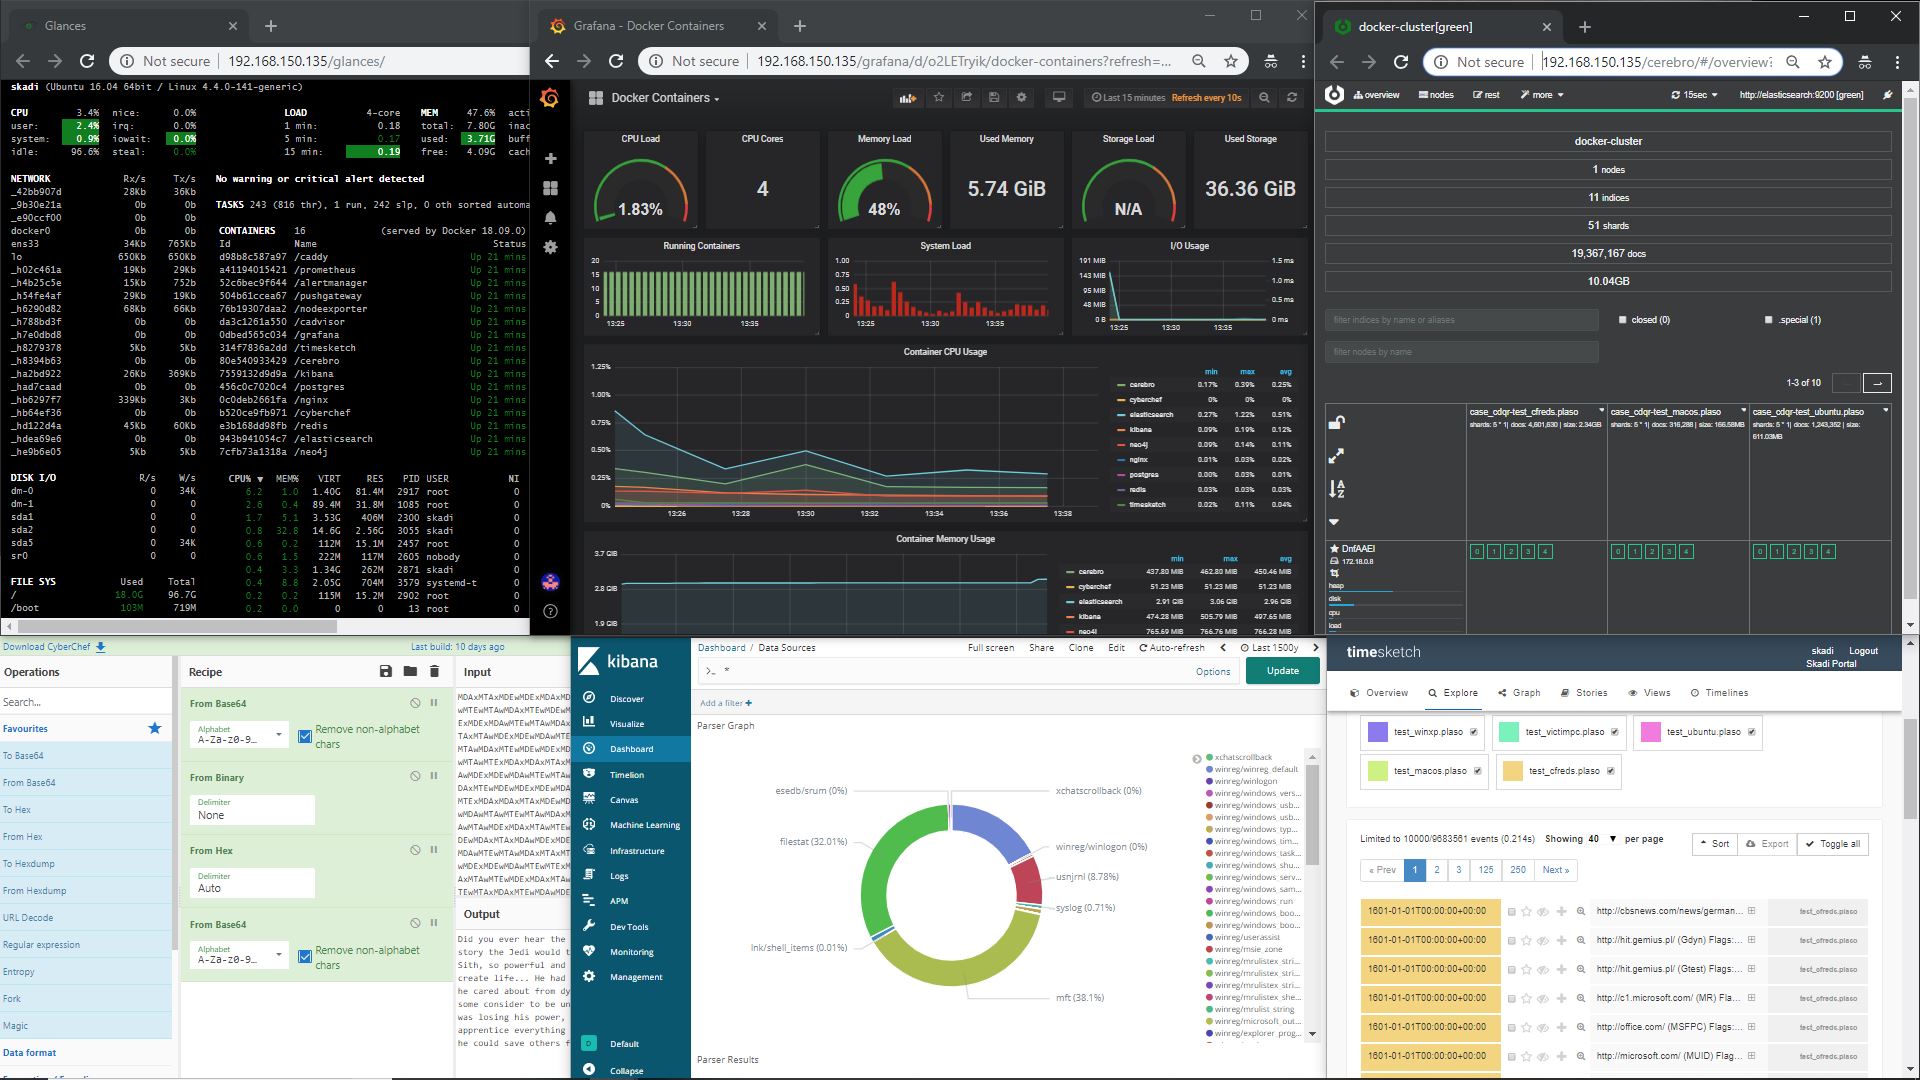
Skadi preview

Skadi

GitHuborlikoski/skadi

Collect, Process, and Hunt with host based data from MacOS, Windows, and Linux

curated-resourcesdigital-forensicsdisk-forensics+9
5193 years ago
patriot preview

patriot

GitHubjoe-desimone/patriot

In-memory stealth detection tool that identifies process hollowing, module stomping, unbacked executable regions, and anomalous CONTEXT structures…

anomaly-detectionbinary-analysisdefensive-tools+3
1644 years ago
autoresponder preview

autoresponder

GitHublawiet47/autoresponder

Automates incident response tasks via Carbon Black Response API: file/registry deletion, process killing, sensor isolation, binary collection, and…

forensicsincident-response
565 years ago
AgentSmith-HIDS preview
Archived

AgentSmith-HIDS

GitHubebwi11/agentsmith-hids

By Kprobe technology Open Source Host-based Intrusion Detection System(HIDS), from E_Bwill.

container-securitydns-analysisincident-response+4
6025 years ago
uac preview

uac

GitHubtclahr/uac

Portable, dependency-free incident response tool that automates forensic artifact collection from Unix-like systems, including memory acquisition,…

digital-forensicsforensicsincident-response+3
1.5k8 days ago
CVE-2021-1675_CarbonBlack_HuntingQuery preview

CVE-2021-1675_CarbonBlack_HuntingQuery

GitHubmrezqi/cve-2021-1675_carbonblack_huntingquery

CarbonBlack hunting queries to detect PrintNightmare (CVE-2021-1675) exploitation via file, module load, and process events, based on Sigma rules.

defensive-toolsincident-responseioc-management+3
5 years ago
Previous12Next