
Azure-Sentinel
 azure/azure-sentinel
Cloud-native SIEM for intelligent security analytics for your entire enterprise.
cloud-securitycurated-resourcesdefensive-tools+5
6.1k
azure/azure-sentinelCloud-native SIEM for intelligent security analytics for your entire enterprise.
 thinkst/canarytokens
Canarytokens helps track activity and actions on your network
 sleuthkit/autopsy
Autopsy® is a digital forensics platform and graphical interface to The Sleuth Kit® and other digital forensics tools. It can be used by law…
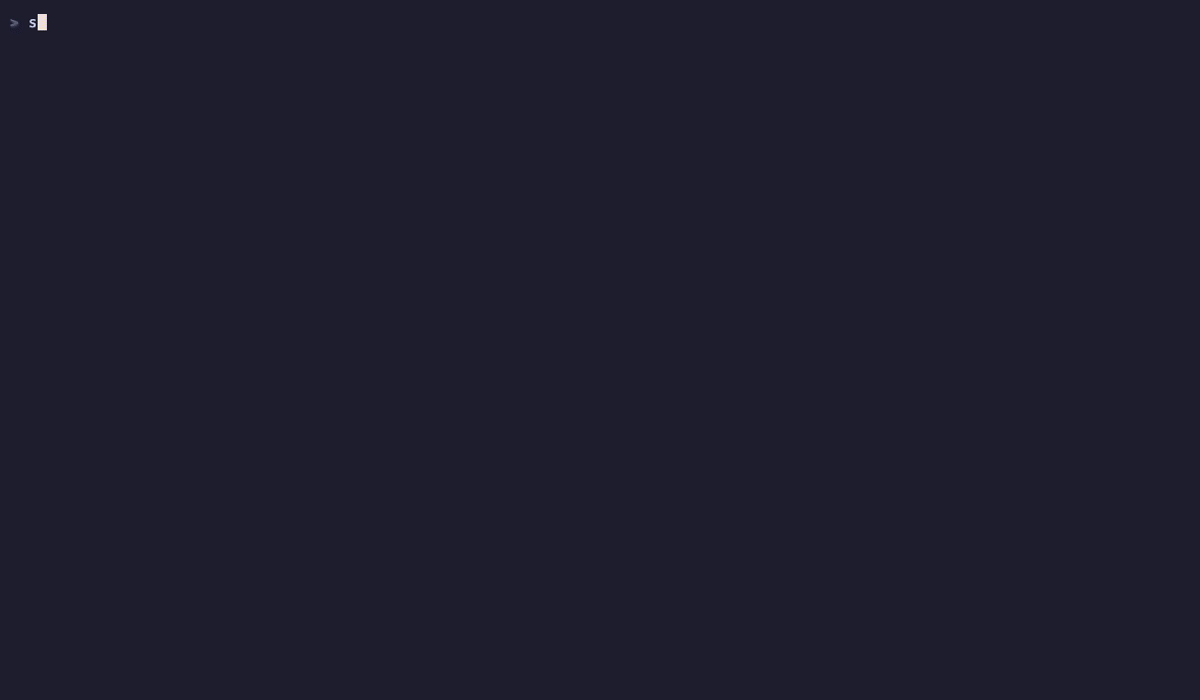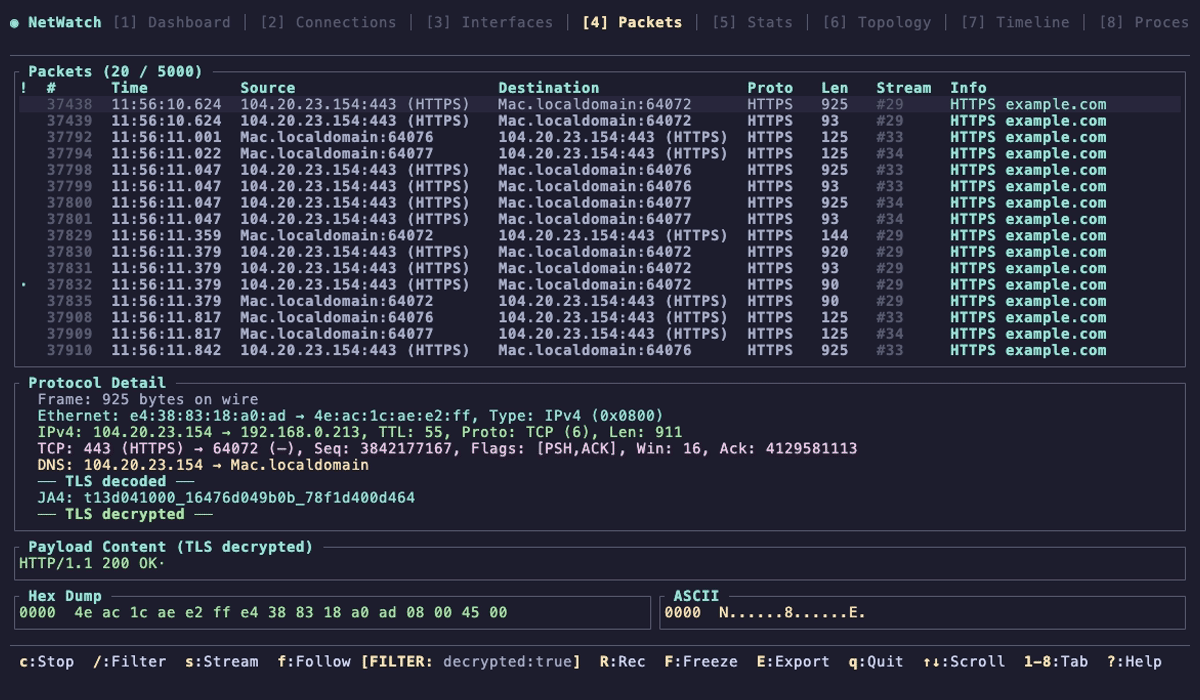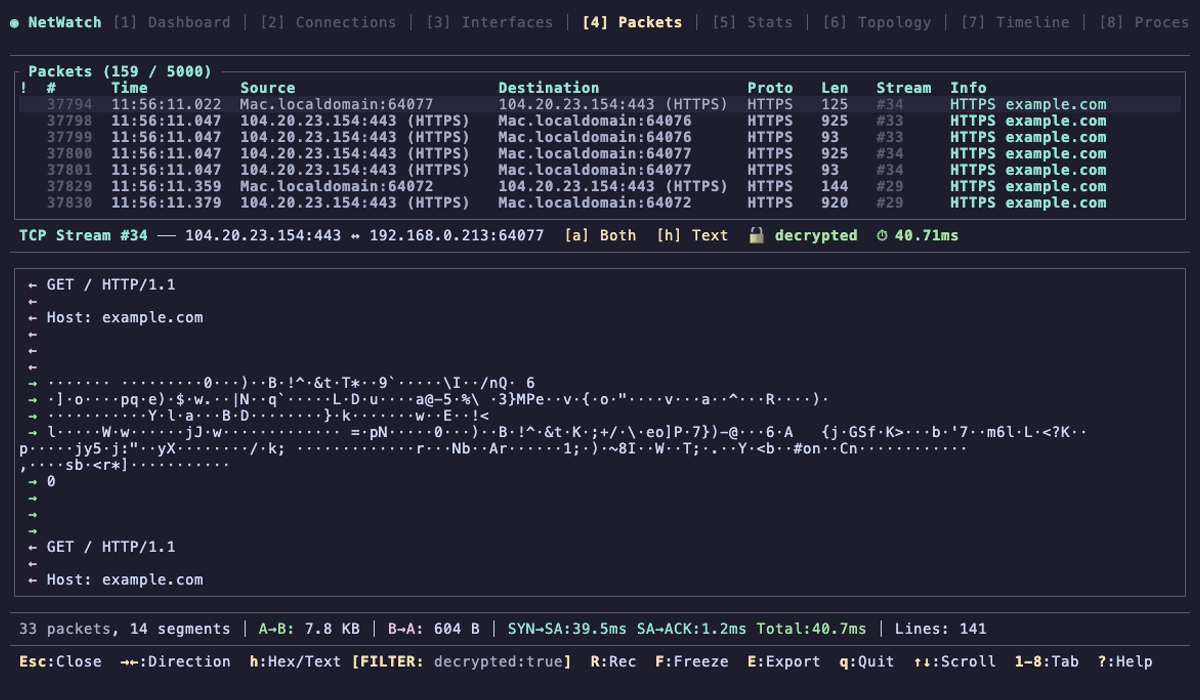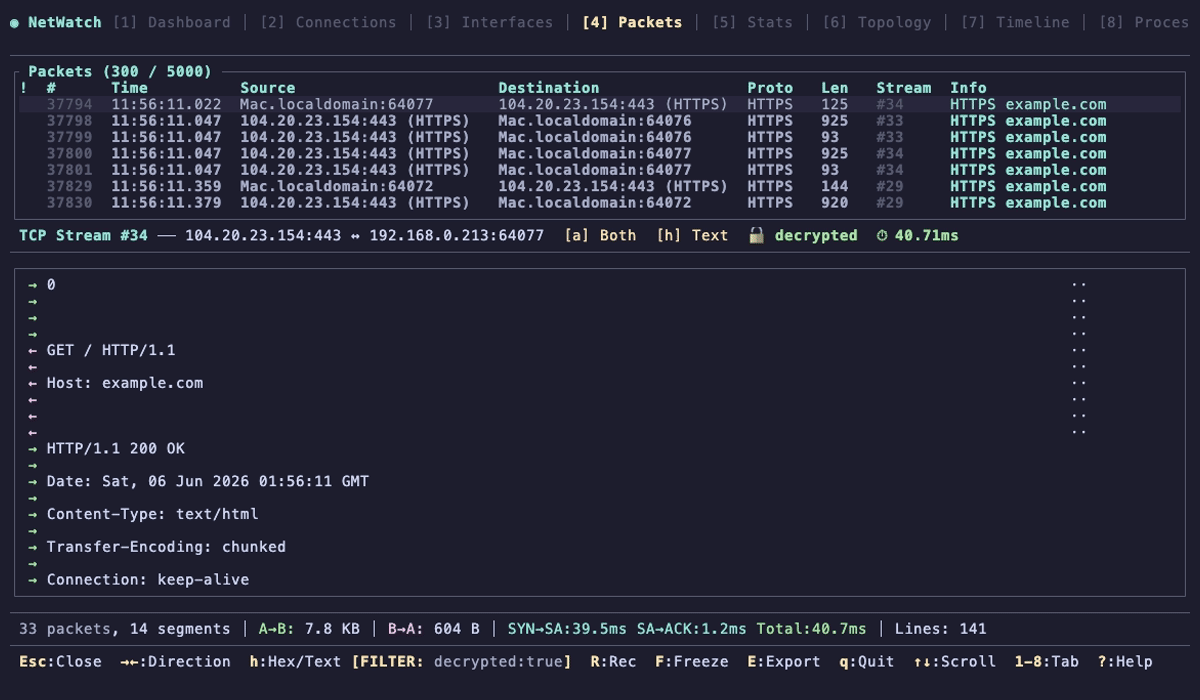 matthart1983/netwatch
Real-time network diagnostics in your terminal. One command, zero config, instant visibility.
 threathuntingproject/threathunting
An informational repo about hunting for adversaries in your IT environment.
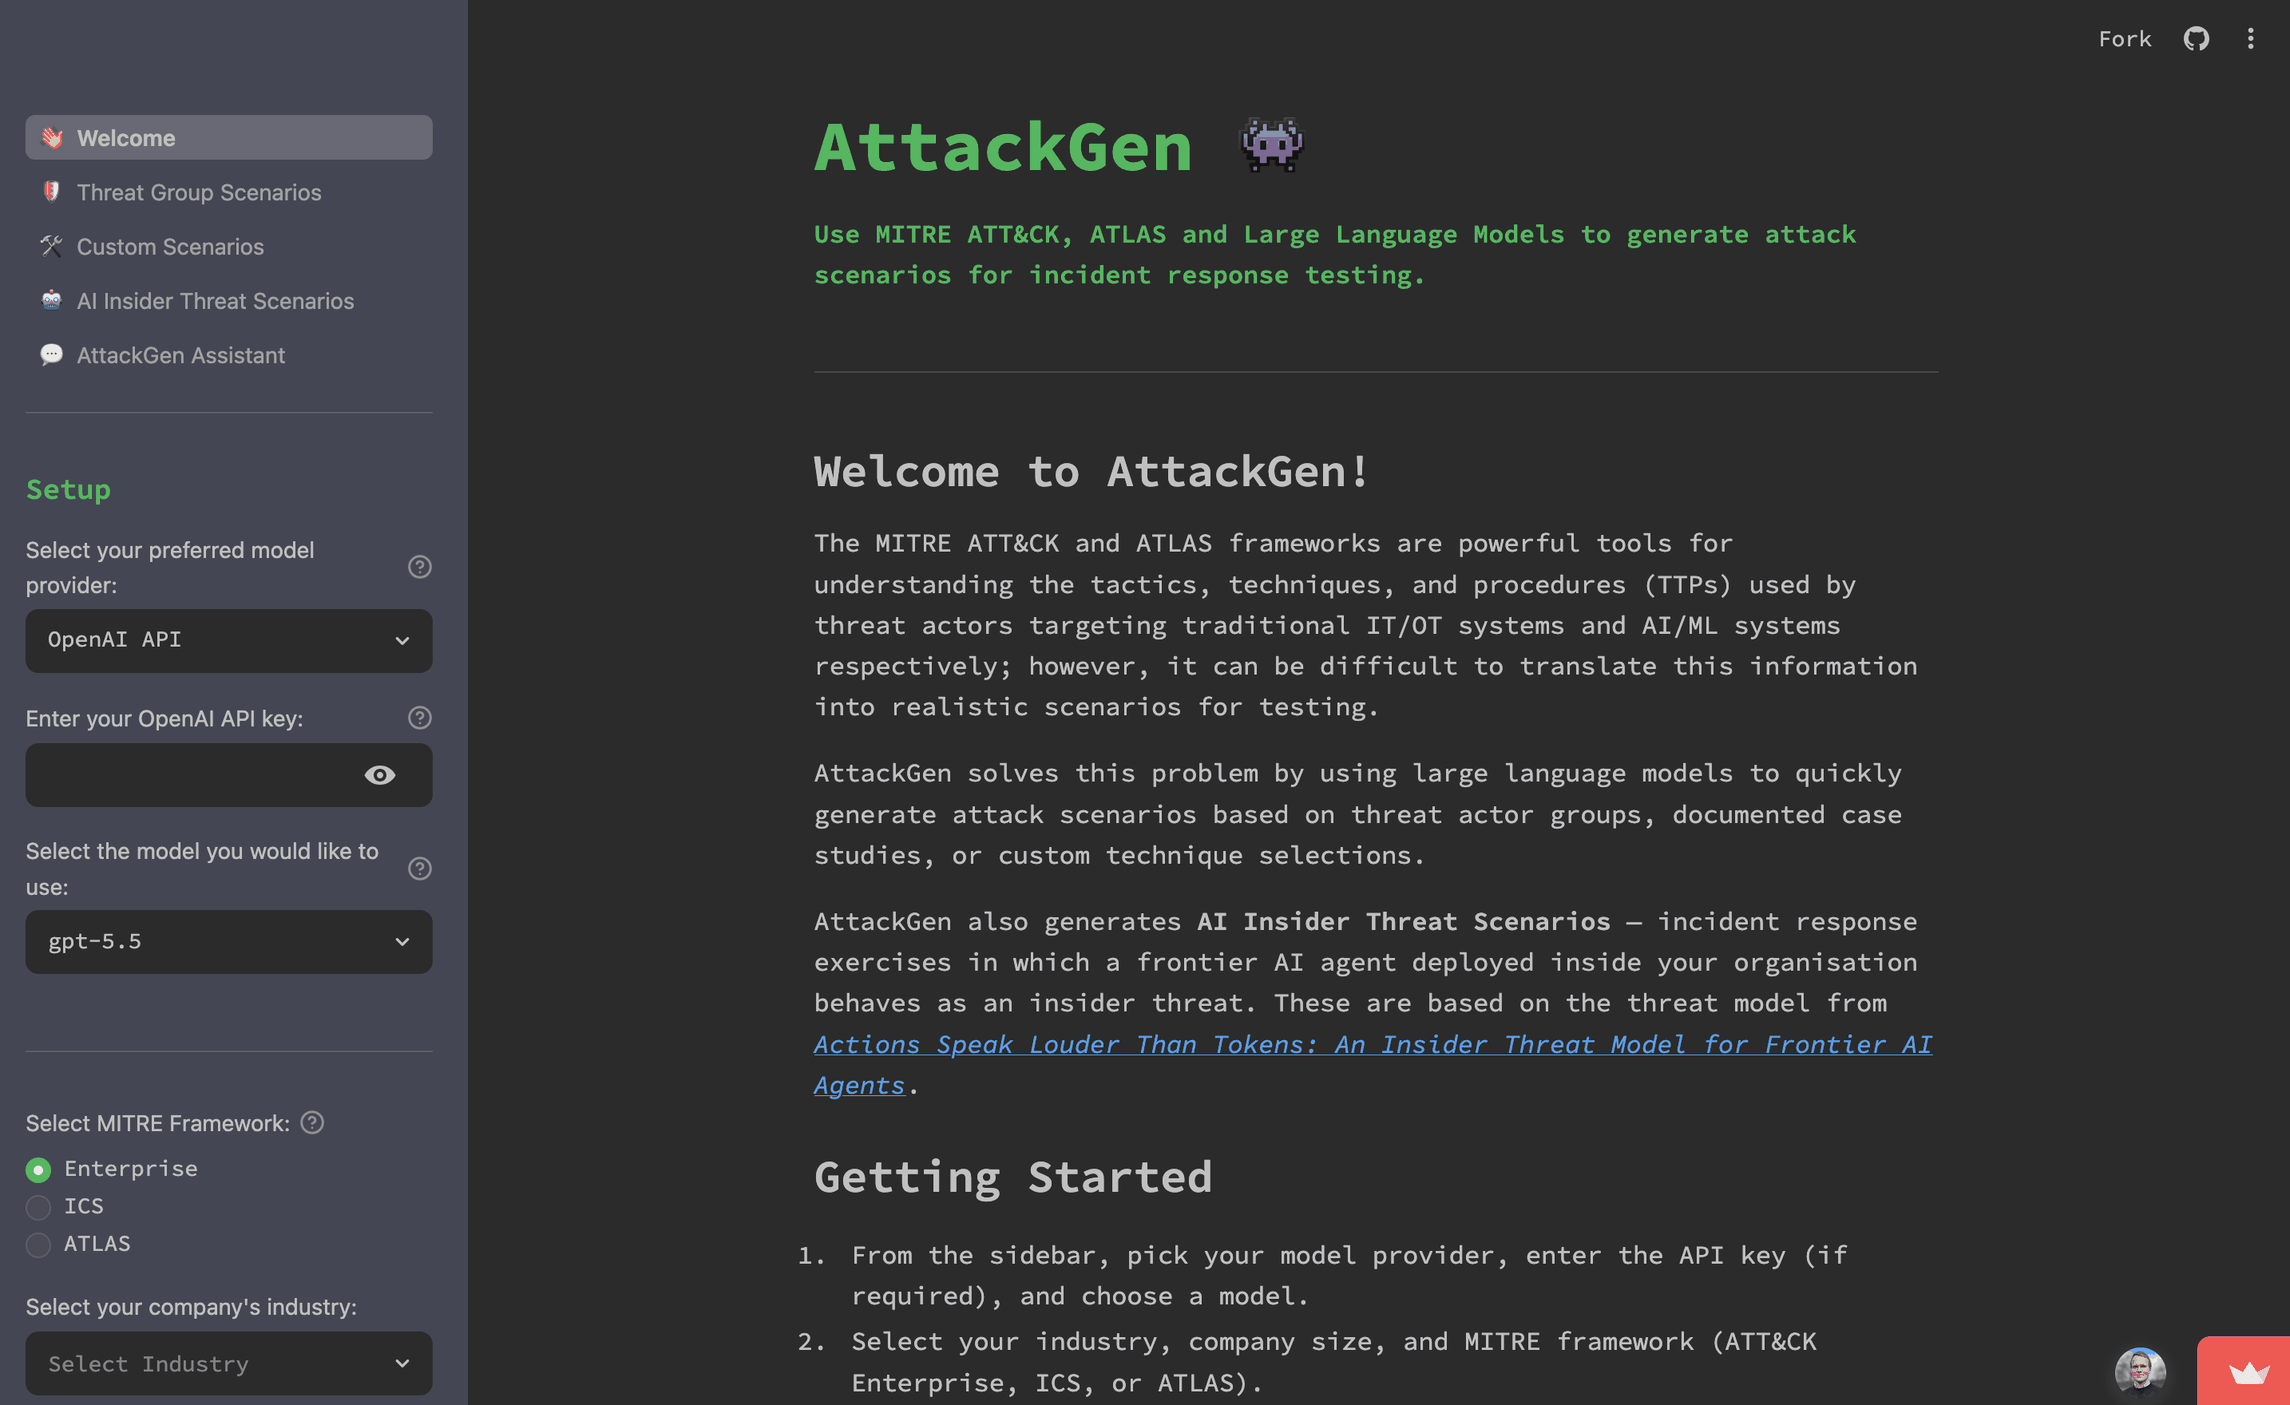 mrwadams/attackgen
AttackGen is a cybersecurity incident response testing tool that leverages the power of large language models and the comprehensive MITRE ATT&CK…
 securitytemplates/sectemplates
Open source templates you can use to bootstrap your security programs
 kubeshop/botkube
An app that helps you monitor your Kubernetes cluster, debug critical deployments & gives recommendations for standard practices
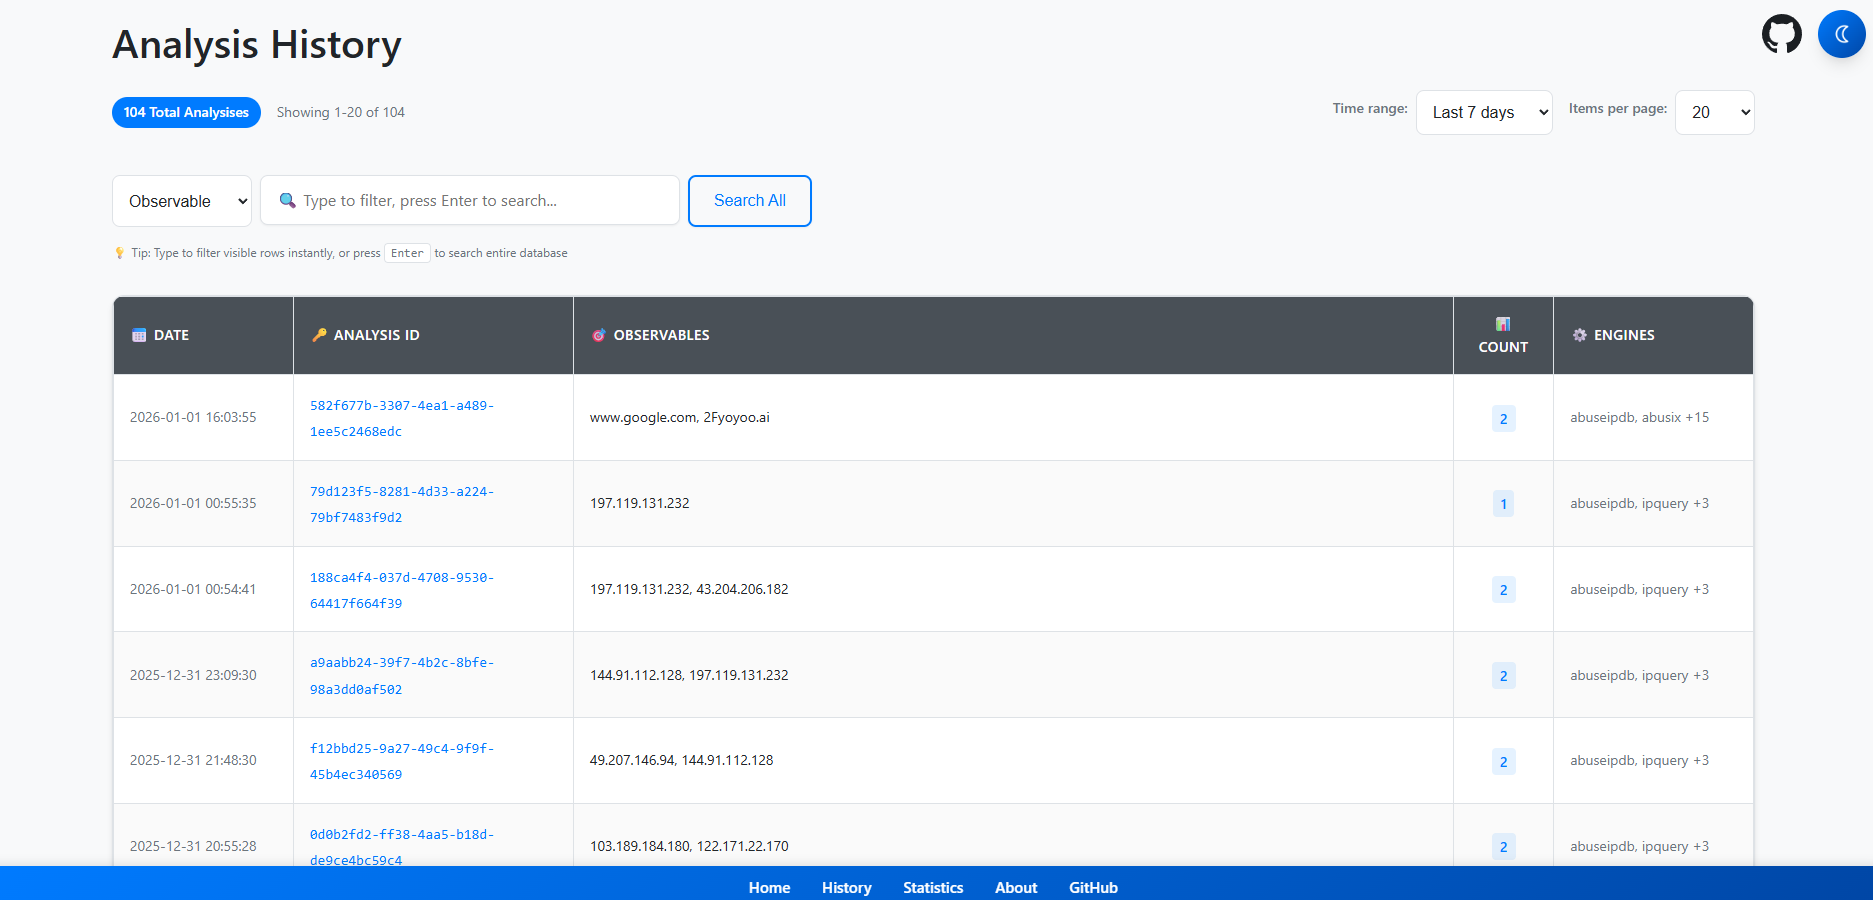 stanfrbd/cyberbro
A simple application that extracts your IoCs from garbage input and checks their reputation using multiple CTI services.
 adversis/tailsnitch
A security auditor for Tailscale configurations. Scans your tailnet for misconfigurations, overly permissive access controls, and security best…
 olafhartong/threathunting
A Splunk app mapped to MITRE ATT&CK to guide your threat hunts
 thinkst/canarytokens-docker
Docker configuration to quickly setup your own Canarytokens.
 wslyvh/paperweight
Paperweight scans your inbox to map your digital footprint, then helps you take back control and delete your data. Local-first and open source.
 back2root/log4shell-rex
PCRE RegEx matching Log4Shell CVE-2021-44228 IOC in your logs
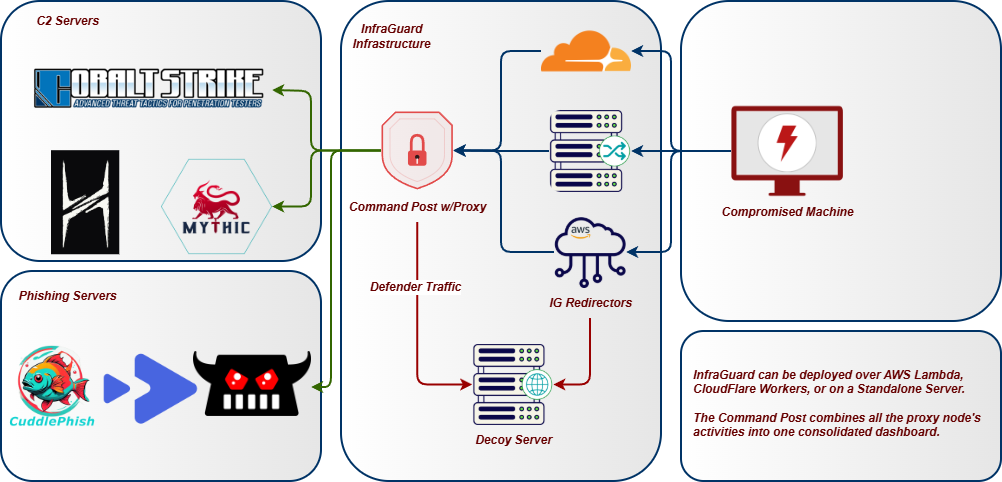 whispergate/infraguard
InfraGuard is a Command & Control Redirection Proxy and Manager which protects your Red Team Infrastructure against threat attribution
 cynative/cynative
Read-only AI agent that queries your cloud, code, and runtime infrastructure to surface misconfigurations, leaked secrets, and privilege escalation…
 srlabs/certiception
An ADCS honeypot to catch attackers in your internal network.