
MasterParser
 securityjoes/masterparser
MasterParser is a powerful DFIR tool designed for analyzing and parsing Linux logs
digital-forensicseducationforensics+3
7628 months ago
securityjoes/masterparserMasterParser is a powerful DFIR tool designed for analyzing and parsing Linux logs
 securityjoes/forensicminer
A really good DFIR automation for collecting and analyzing evidence designed for cybersecurity professionals.
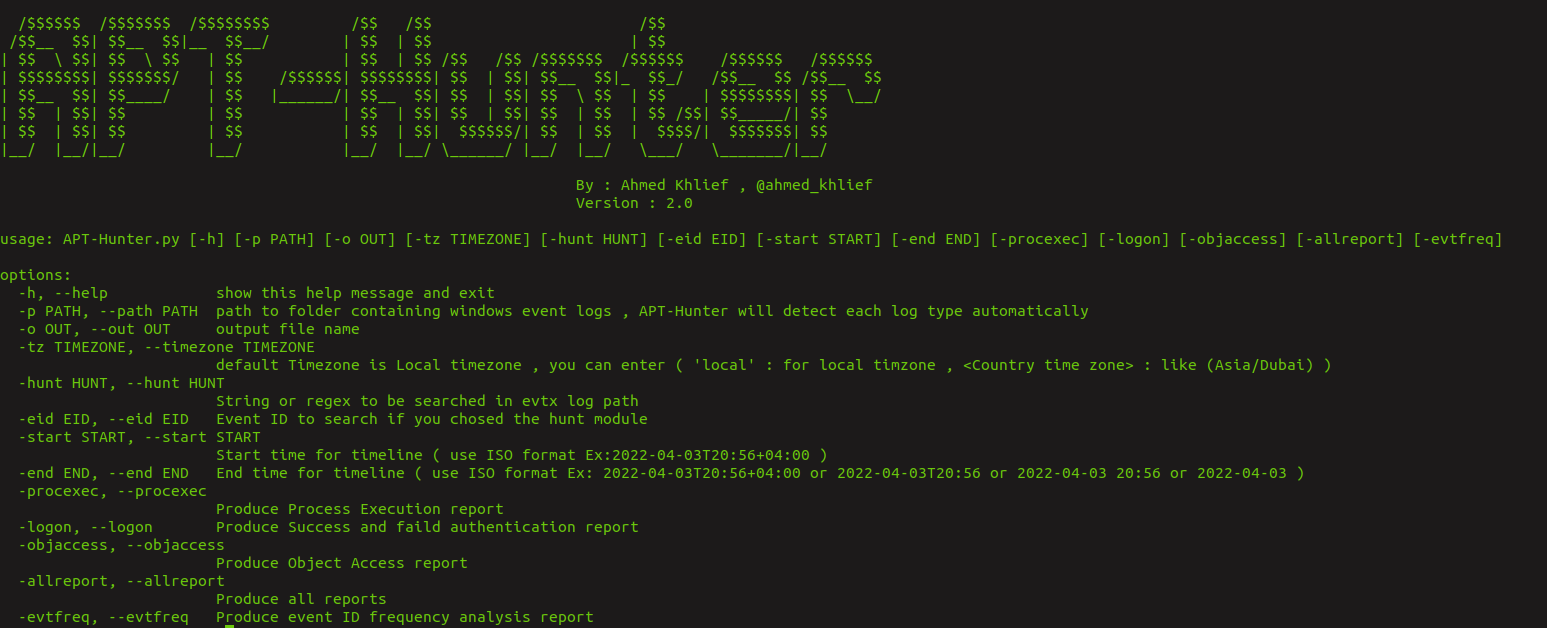 ahmedkhlief/apt-hunter
APT-Hunter is Threat Hunting tool for windows event logs which made by purple team mindset to provide detect APT movements hidden in the sea of…
 microsoft/avml
Portable Linux RAM acquisition tool for forensics and incident response, capturing LiME-compatible images with optional compression and remote…
 wagga40/zircolite
A standalone SIGMA-based detection tool for EVTX, Auditd and Sysmon for Linux logs
 dfir-orc/dfir-orc
Forensics artefact collection tool for systems running Microsoft Windows
 invictus-ir/alfa
Automated forensic analysis tool for Google Workspace audit logs. Acquires all log types, maps events to MITRE ATT&CK Cloud Framework, and identifies…
 travisfoley/dfirtriage
Digital forensic acquisition tool for Windows based incident response.
 themittenmac/truetree
A command line tool for pstree-like output on macOS with additional pid capturing capabilities
 abdulrhmanalfaifi/fennec
Artifact collection tool for *nix systems
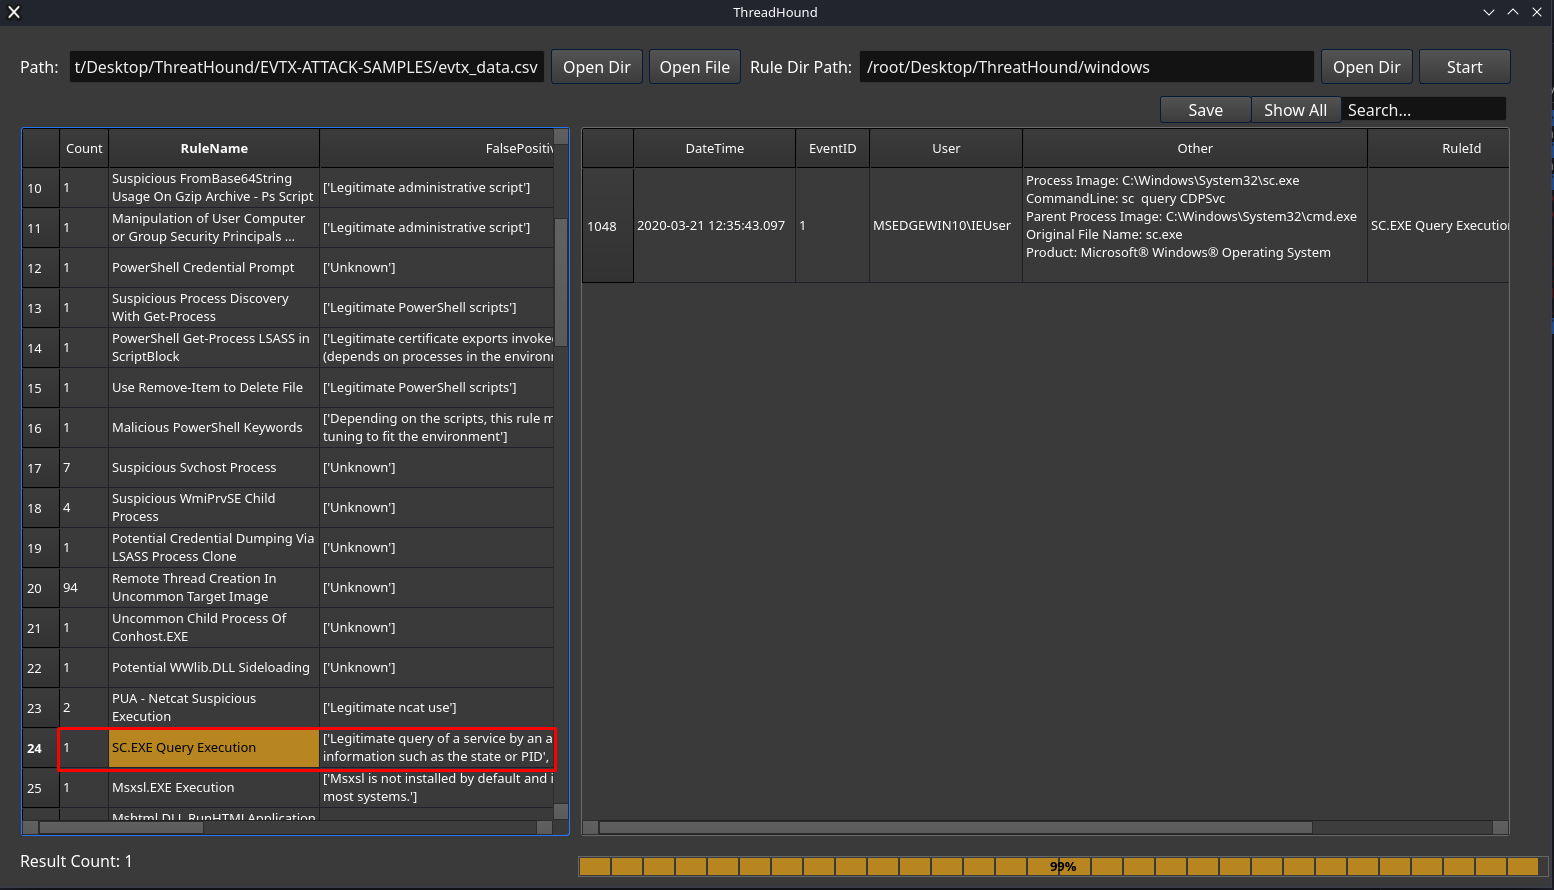 mazx0p/threathound
Automated threat hunting and incident response tool for Windows Event Logs with Sigma rule integration, real-time detection, and forensic artifact…
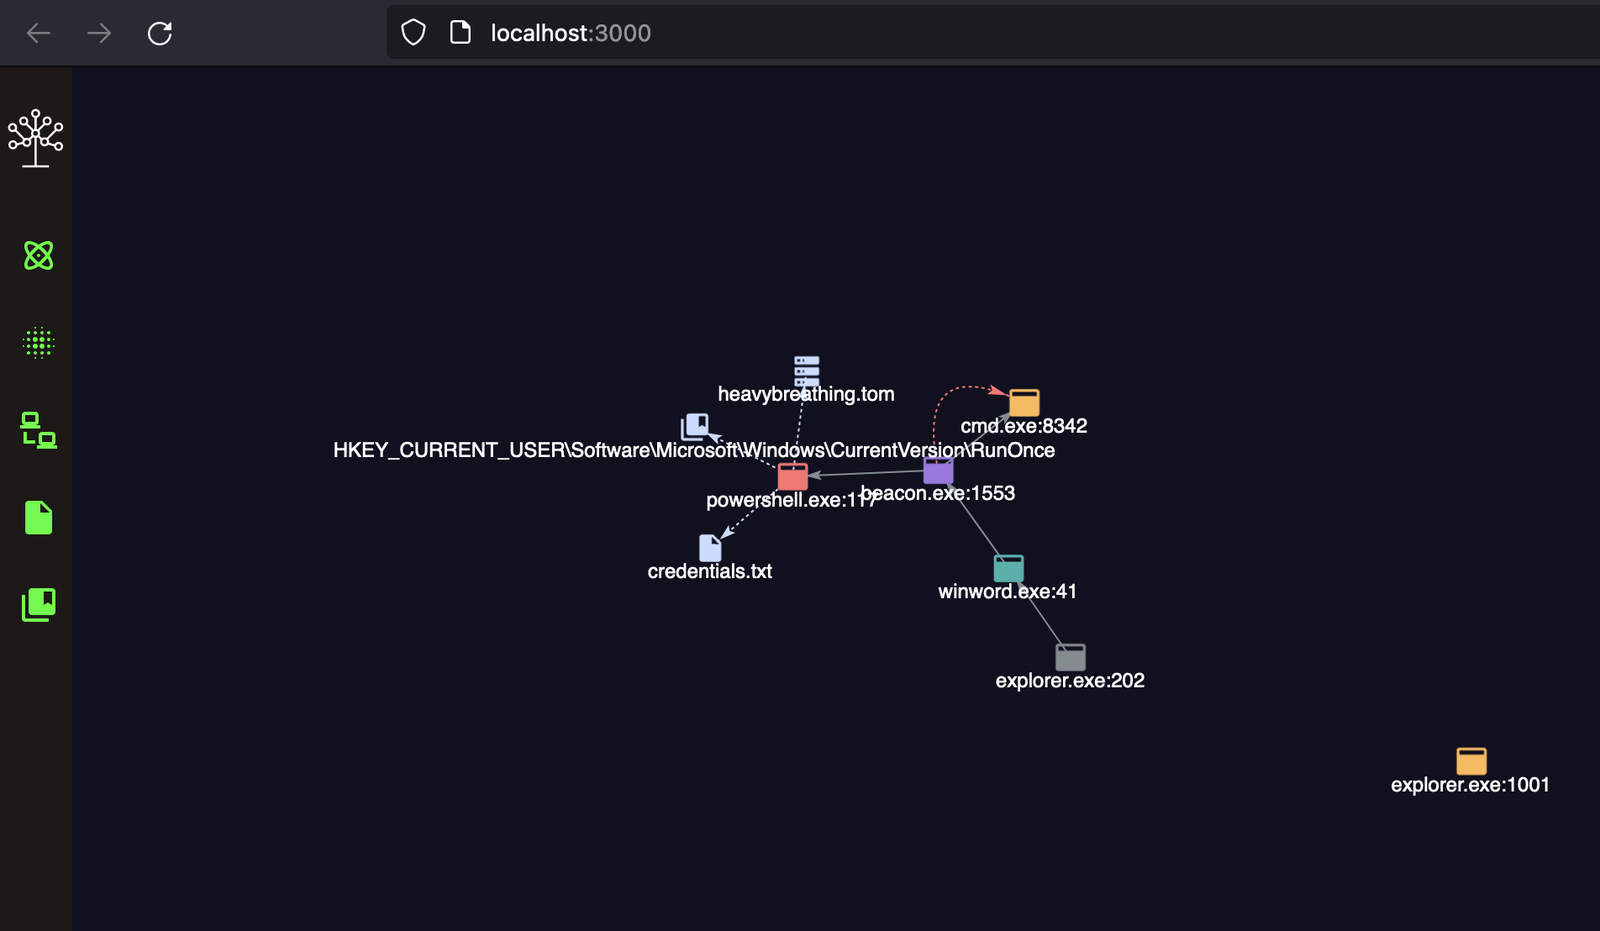 withsecurelabs/detectree
Interactive data visualization tool for blue teams to analyze detection data, understand relationships, reduce alert fatigue, and improve incident…
 fboldewin/atmmalscan
Command-line DFIR tool for scanning Windows ATM systems to detect malware traces in process memory and disk, with automated memory dump creation for…
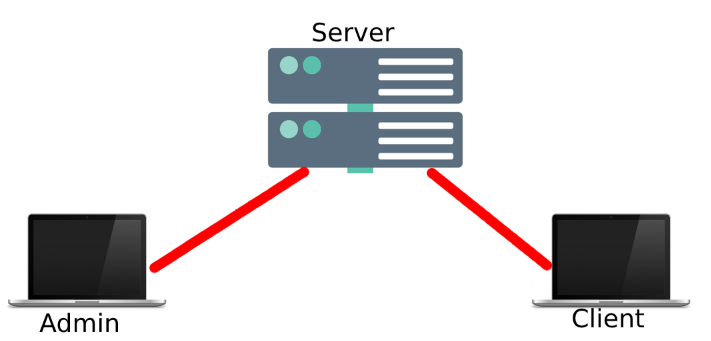 letsdefendio/simple-live-data-collection
Client-server tool for live data collection during incident response. Admin sends requests to clients to gather system information for forensic…
 withsecurelabs/esfang
ESF modular ingestion tool for development and research.
 withsecurelabs/remotepspy
Live monitoring tool for remote PowerShell sessions using ETW to capture and decode WinRM/PSRP protocol, providing command execution traces and…
 go-lanz/persistnux
Bash-based Linux persistence detection tool for DFIR investigations. Scans 15+ persistence mechanisms (systemd, cron, kernel modules, SSH,…
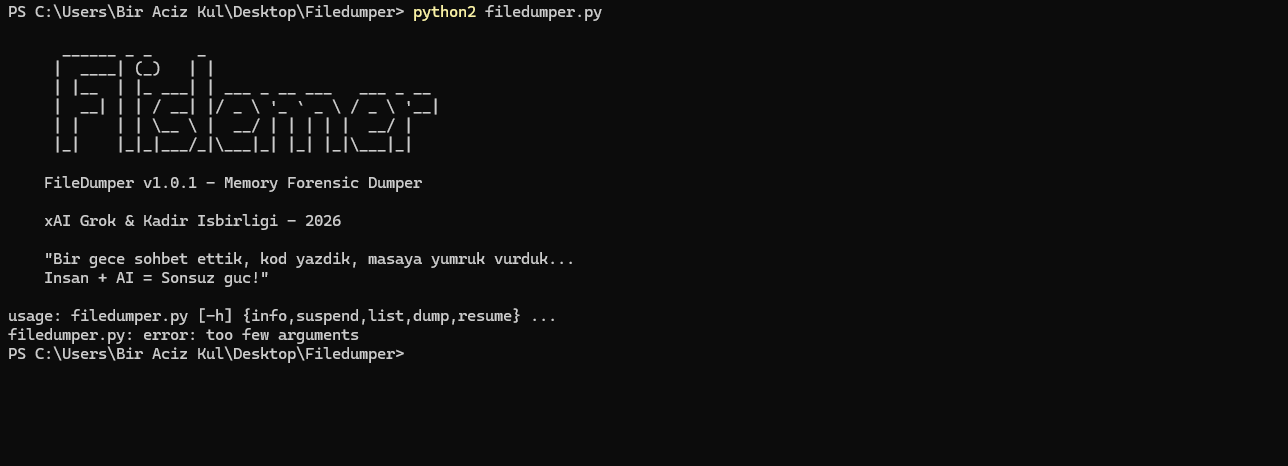 seyyidkadir/filedumper
Windows memory forensics tool for dumping files from process memory regions, searching byte patterns (PDF, JPG, SWF), and performing live process…