
memhunter
 marcosd4h/memhunter
Live hunting of code injection techniques
defensive-toolsincident-responsemalware-analysis+1
marcosd4h/memhunterLive hunting of code injection techniques
 patrowl/patrowlmanager
PatrOwl - Open Source, Smart and Scalable Security Operations Orchestration Platform
 botherder/kraken
Cross-platform Yara scanner written in Go
 airbus-cert/cve-2024-4040
Scanner for CVE-2024-4040
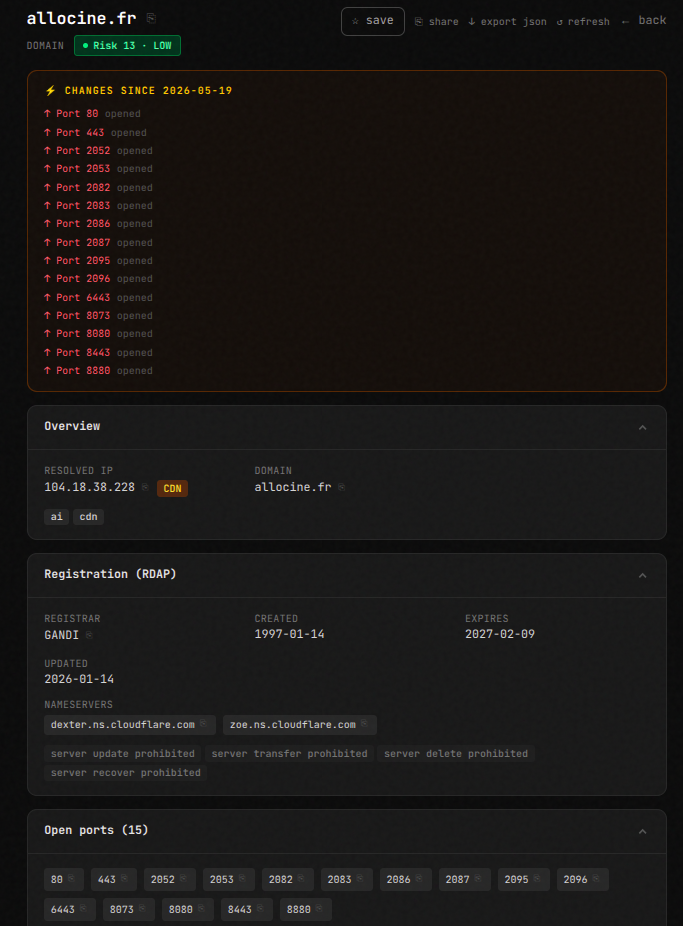 teycir/seekyou
OSINT intelligence on any IP, domain, or ASN
 captaingeech42/ransomwatch
Ransomware leak site monitoring
 stripe/log4j-remediation-tools
Tools for remediating the recent log4j2 RCE vulnerability (CVE-2021-44228)
 manishrawat21/analysis
Hands-on analysis of common APT attack techniques, focused on how they show up in logs and how defenders can realistically detect them.
 google/timesketch
Collaborative forensic timeline analysis platform for ingesting, searching, and annotating event logs to support incident response and DFIR…
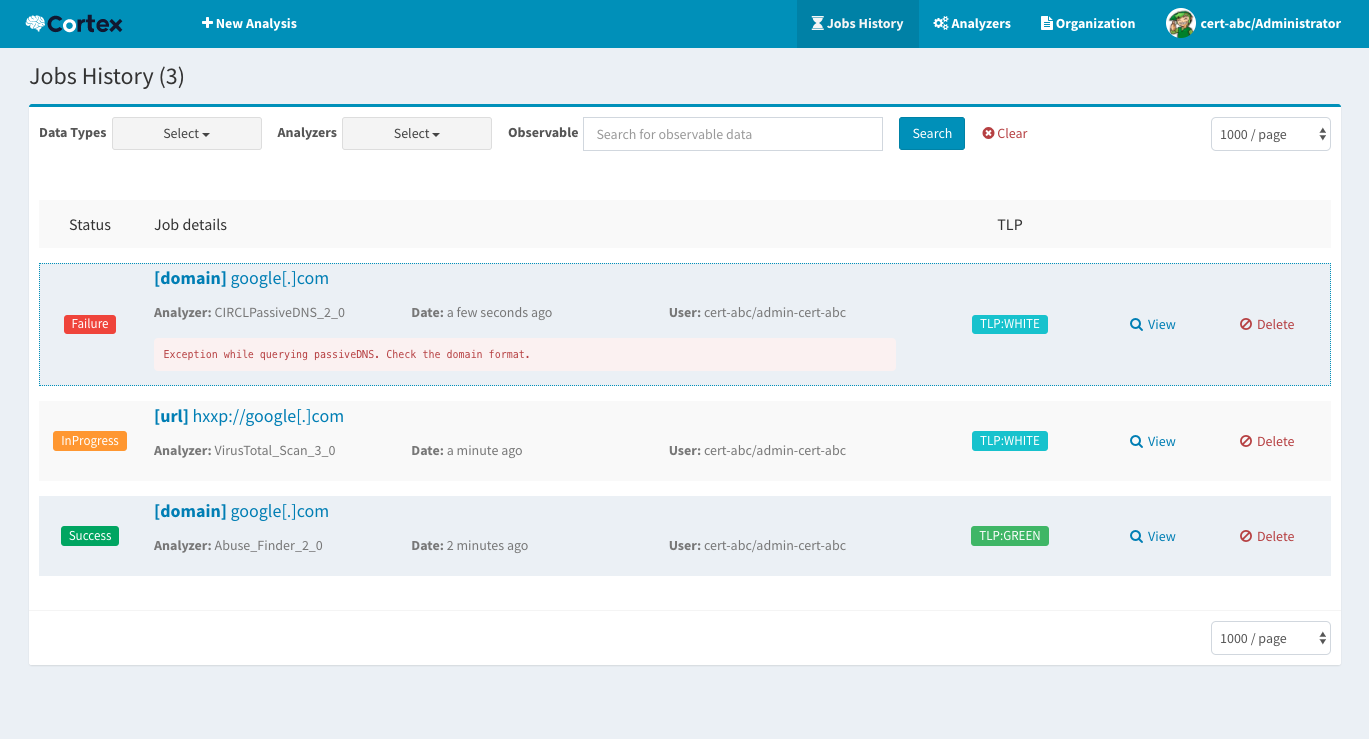 thehive-project/cortex
Cortex: a Powerful Observable Analysis and Active Response Engine
 knight0x07/bibi-windows-wiper-analysis
Technical Analysis of Bibi-Windows Wiper Targeting Israeli Organizations
 meirwah/awesome-incident-response
Curated index of incident response and DFIR tools, including memory and disk forensics, evidence collection, log analysis, playbooks, and educational…
 winsiderss/systeminformer
Real-time Windows system monitor with advanced process, network, and disk analysis, stack trace debugging, malware detection, and service management.…
 mvt-project/mvt
Forensic collection and analysis toolkit for Android and iOS devices to identify potential compromise by known spyware using public and private…
 mandiant/capa
Rule-based static and dynamic analysis tool that identifies capabilities in PE, ELF, .NET, and shellcode files, mapping them to MITRE ATT&CK…
 volatilityfoundation/volatility3
Advanced framework for extracting digital artifacts from volatile memory (RAM) samples, enabling deep forensic analysis of system runtime state…
 0x4d31/awesome-threat-detection
Curated list of threat detection and hunting resources: detection rules, SIEM and log analysis tools, endpoint/network monitoring, datasets,…
 yamato-security/hayabusa
Multi-threaded Windows event log forensics timeline generator and threat hunting tool with full Sigma rule support, producing CSV/JSON timelines for…