
Ransomware-Tool-Matrix
 bushidouk/ransomware-tool-matrix
A resource containing all the tools each ransomware gangs uses
curated-resourcesdefensive-toolsincident-response+3
1.5k
bushidouk/ransomware-tool-matrixA resource containing all the tools each ransomware gangs uses
 opensourcemalware/polinrider
Technical dossier on the DPRK-linked PolinRider supply-chain attack, documenting obfuscated JS payload injection, git history manipulation, C2…
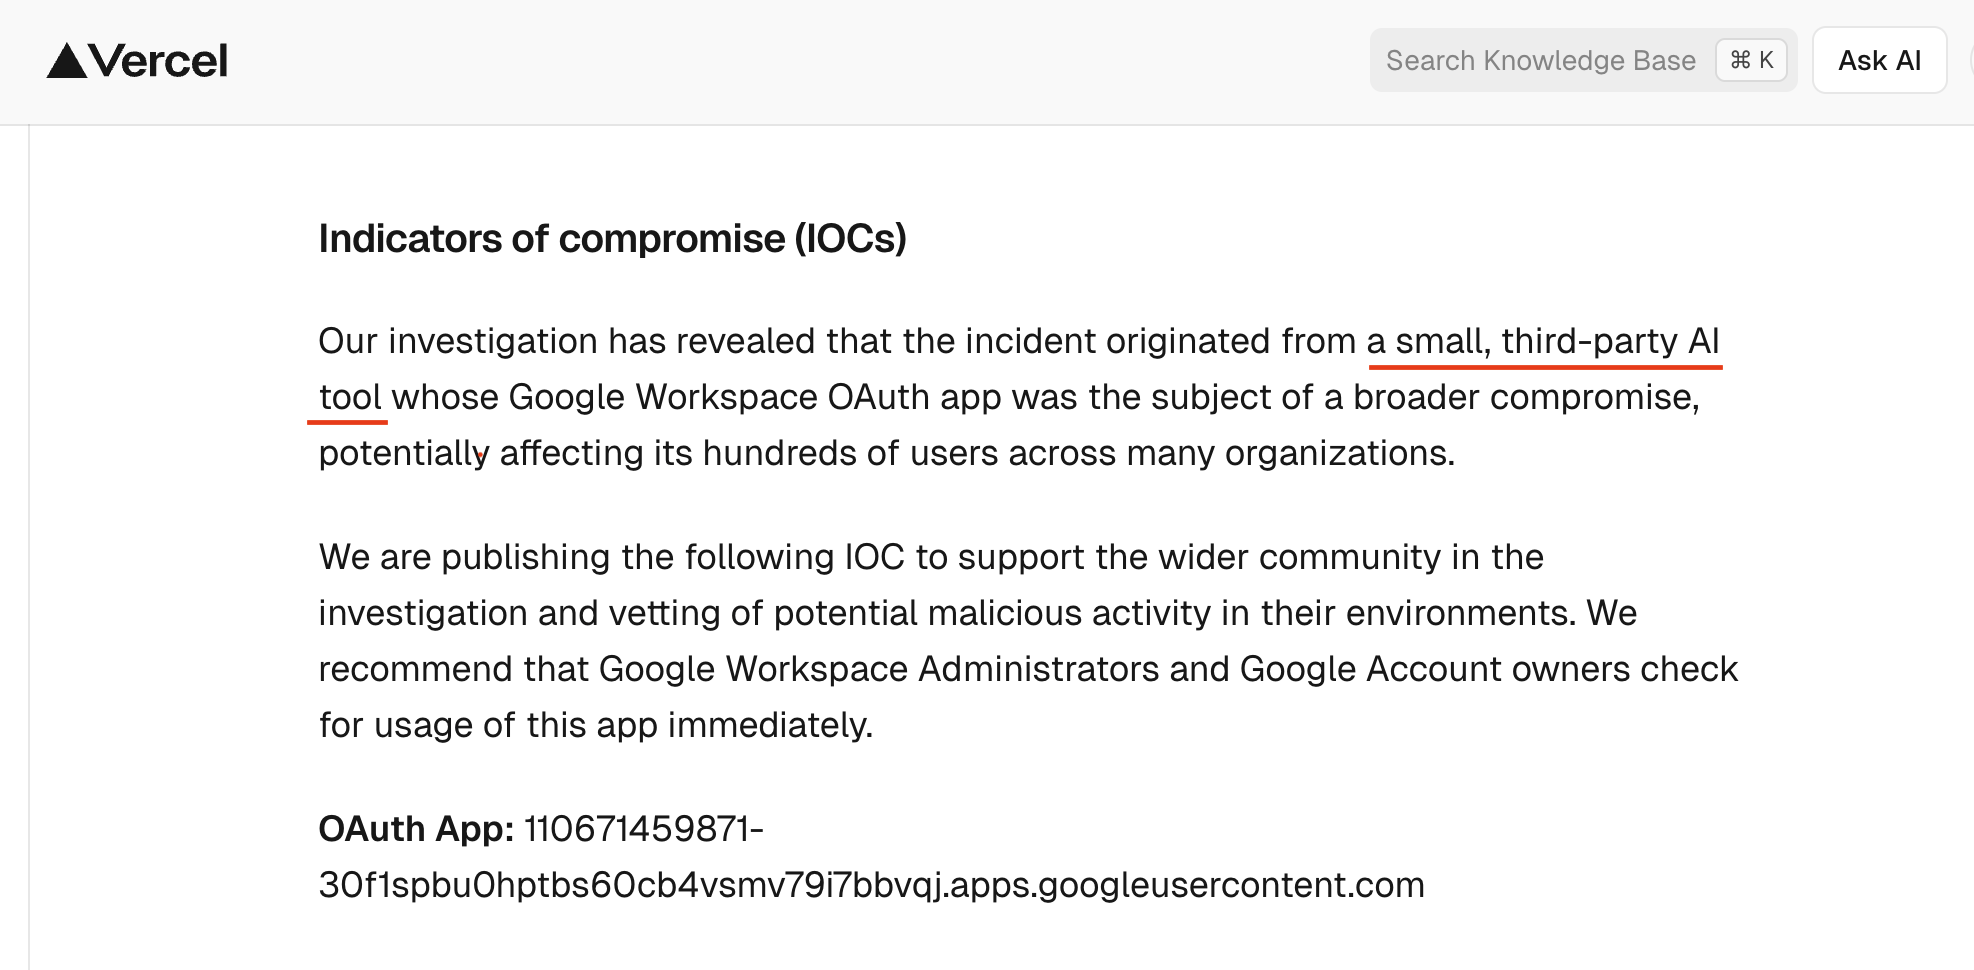 opensourcemalware/vercel-april2026-incident-response
This is an incident response playbook we created for the Vercel April 2026 compromise
 playtikaoss/leaktopus
Automated secret and leak detection scanner for GitHub and paste sites, with heuristic filtering, IOL enrichment via Shhgit/TruffleHog, and ELK-based…
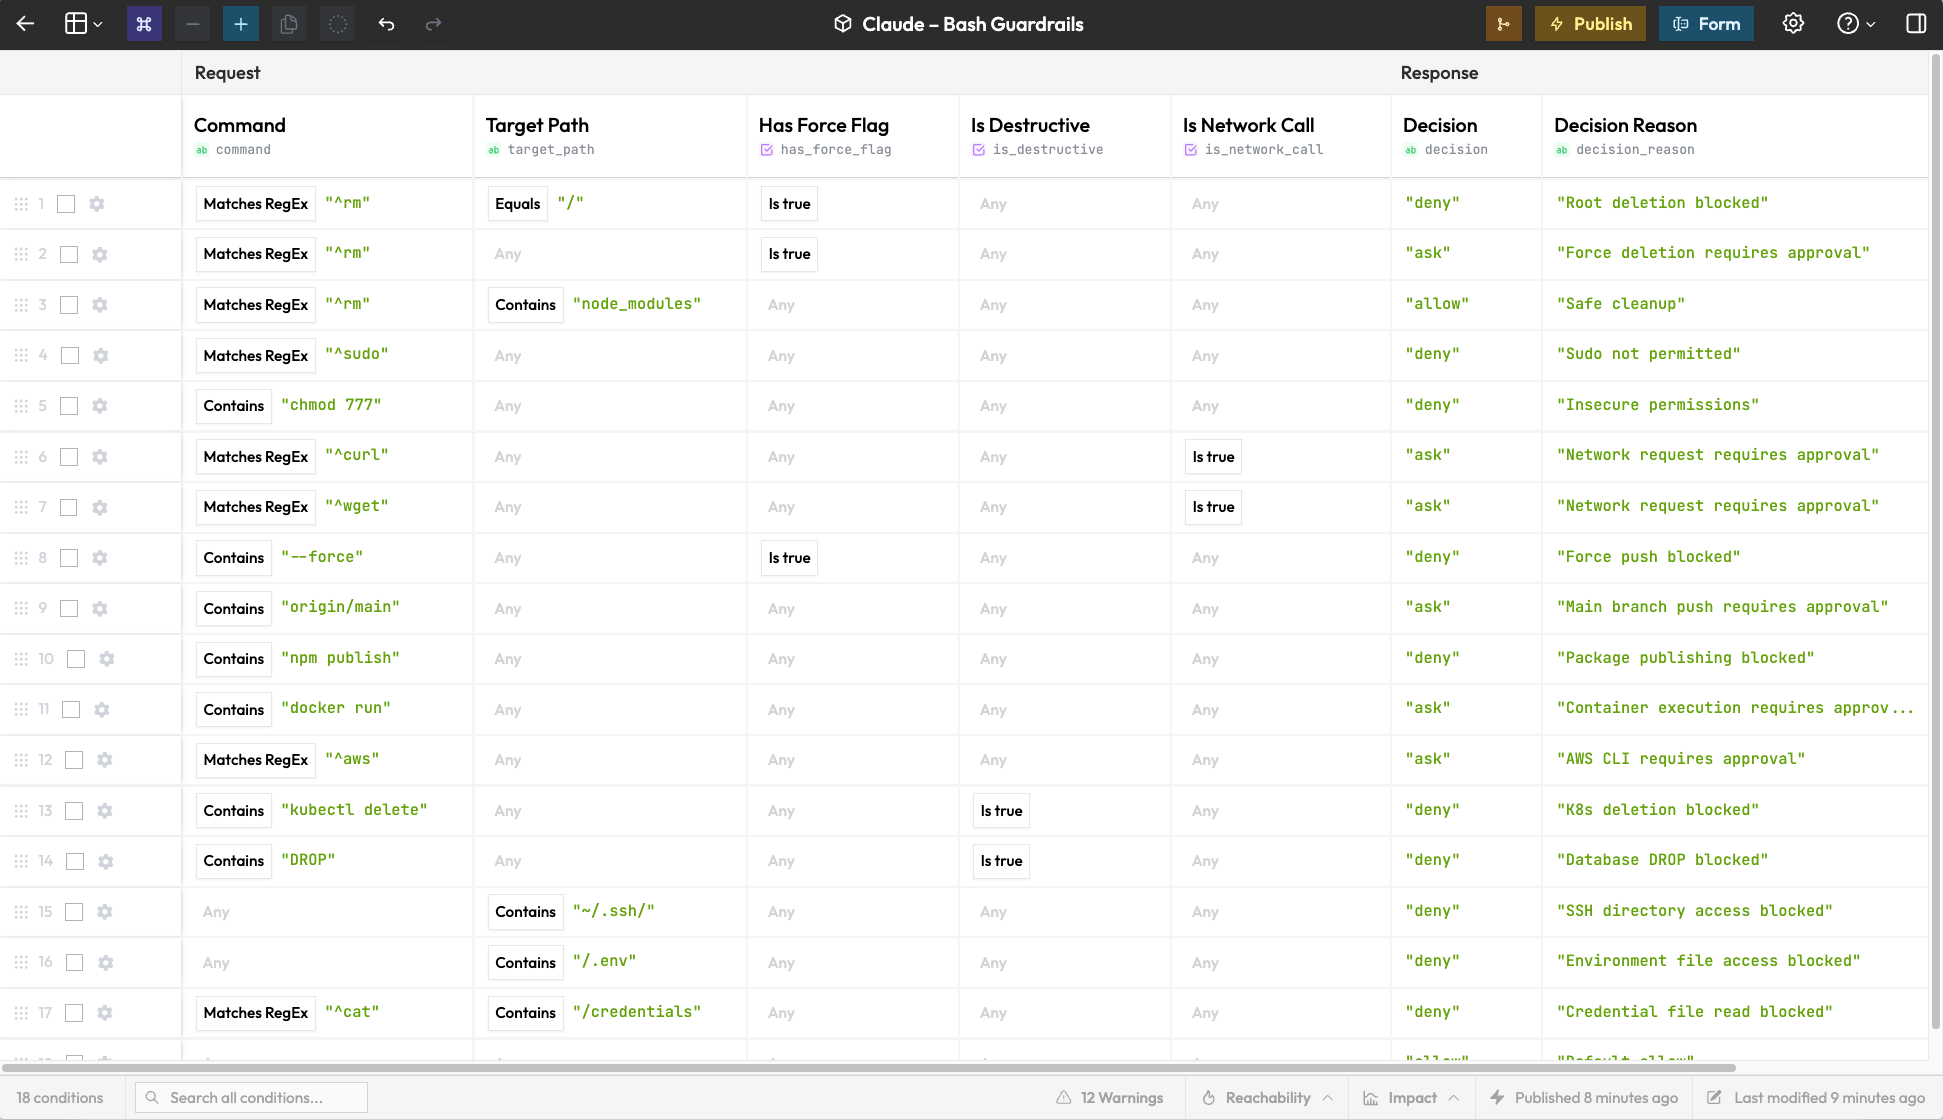 rulebricks/claude-code-guardrails
Real-time guardrails for Claude Code tool calls.
 dfir-dd/dfir-toolkit
CLI tools for forensic investigation of Windows artifacts
 enablesecurity/vulnerability-disclosure-policy
How Enable Security handles security vulnerabilities
 0xsyr0/log4shell
This repository contains all gathered resources we used during our Incident Reponse on CVE-2021-44228 and CVE-2021-45046 aka Log4Shell.
 deividasterechovas/soc335-cve-2024-49138-exploitation-detected
Documented incident response case for CVE-2024-49138 exploitation, featuring log analysis, hash validation, C2 detection, and containment procedures…
 neo23x0/raccine
A Simple Ransomware Vaccine
 letsdefend/awesome-soc-analyst
Useful resources for SOC Analyst and SOC Analyst candidates.
 sifalcon/detection
Curated collection of detection rules and IOCs extracted from DFIR engagements and malware analyses to support threat hunting, incident response, and…
 nccgroup/threat-intelligence-alerts
Welcome to the NCC Group Threat Intelligence Alert repo, here you will find the alerts which we have raised to our customers regarding intelligence…
 threathunters-io/qlog
ETW-based Windows process creation logger that enriches events with file hashes, signatures, and parent process details, outputting to Windows…
 ma1am/cve-2022-26134-exploit-detection
This repository contains Yara rule and the method that a security investigator may want to use for CVE-2022-26134 threat hunting on their Linux…
 inquest/yara-rules
Collection of YARA rules for hunting malware, malicious Office documents, and exploit artifacts, with references to samples and research write-ups.
 honeynet/log4shell-data
Data we are receiving from our honeypots about CVE-2021-44228