

fleet
 fleetdm/fleet
Open-source platform to secure and manage endpoints via MDM, patch management, software deployment, and osquery-powered visibility with compliance…
cloud-securityconfiguration-auditingdefensive-tools+4
6.9k
fleetdm/fleetOpen-source platform to secure and manage endpoints via MDM, patch management, software deployment, and osquery-powered visibility with compliance…
 anthropic-experimental/sandbox-runtime
A lightweight sandboxing tool for enforcing filesystem and network restrictions on arbitrary processes at the OS level, without requiring a container.
 intuitem/ciso-assistant-community
GRC platform for risk management, compliance, and audit with 200+ frameworks, automatic control mapping, vulnerability management, and incident…
 yamato-security/wela
Audits Windows event log settings against best-practice guidelines and Sigma-rule detectability, with automated configuration for DFIR readiness.
 netalertx/netalertx
Centralized network visibility and continuous asset discovery. Monitor devices, detect change, and stay aware across distributed networks.
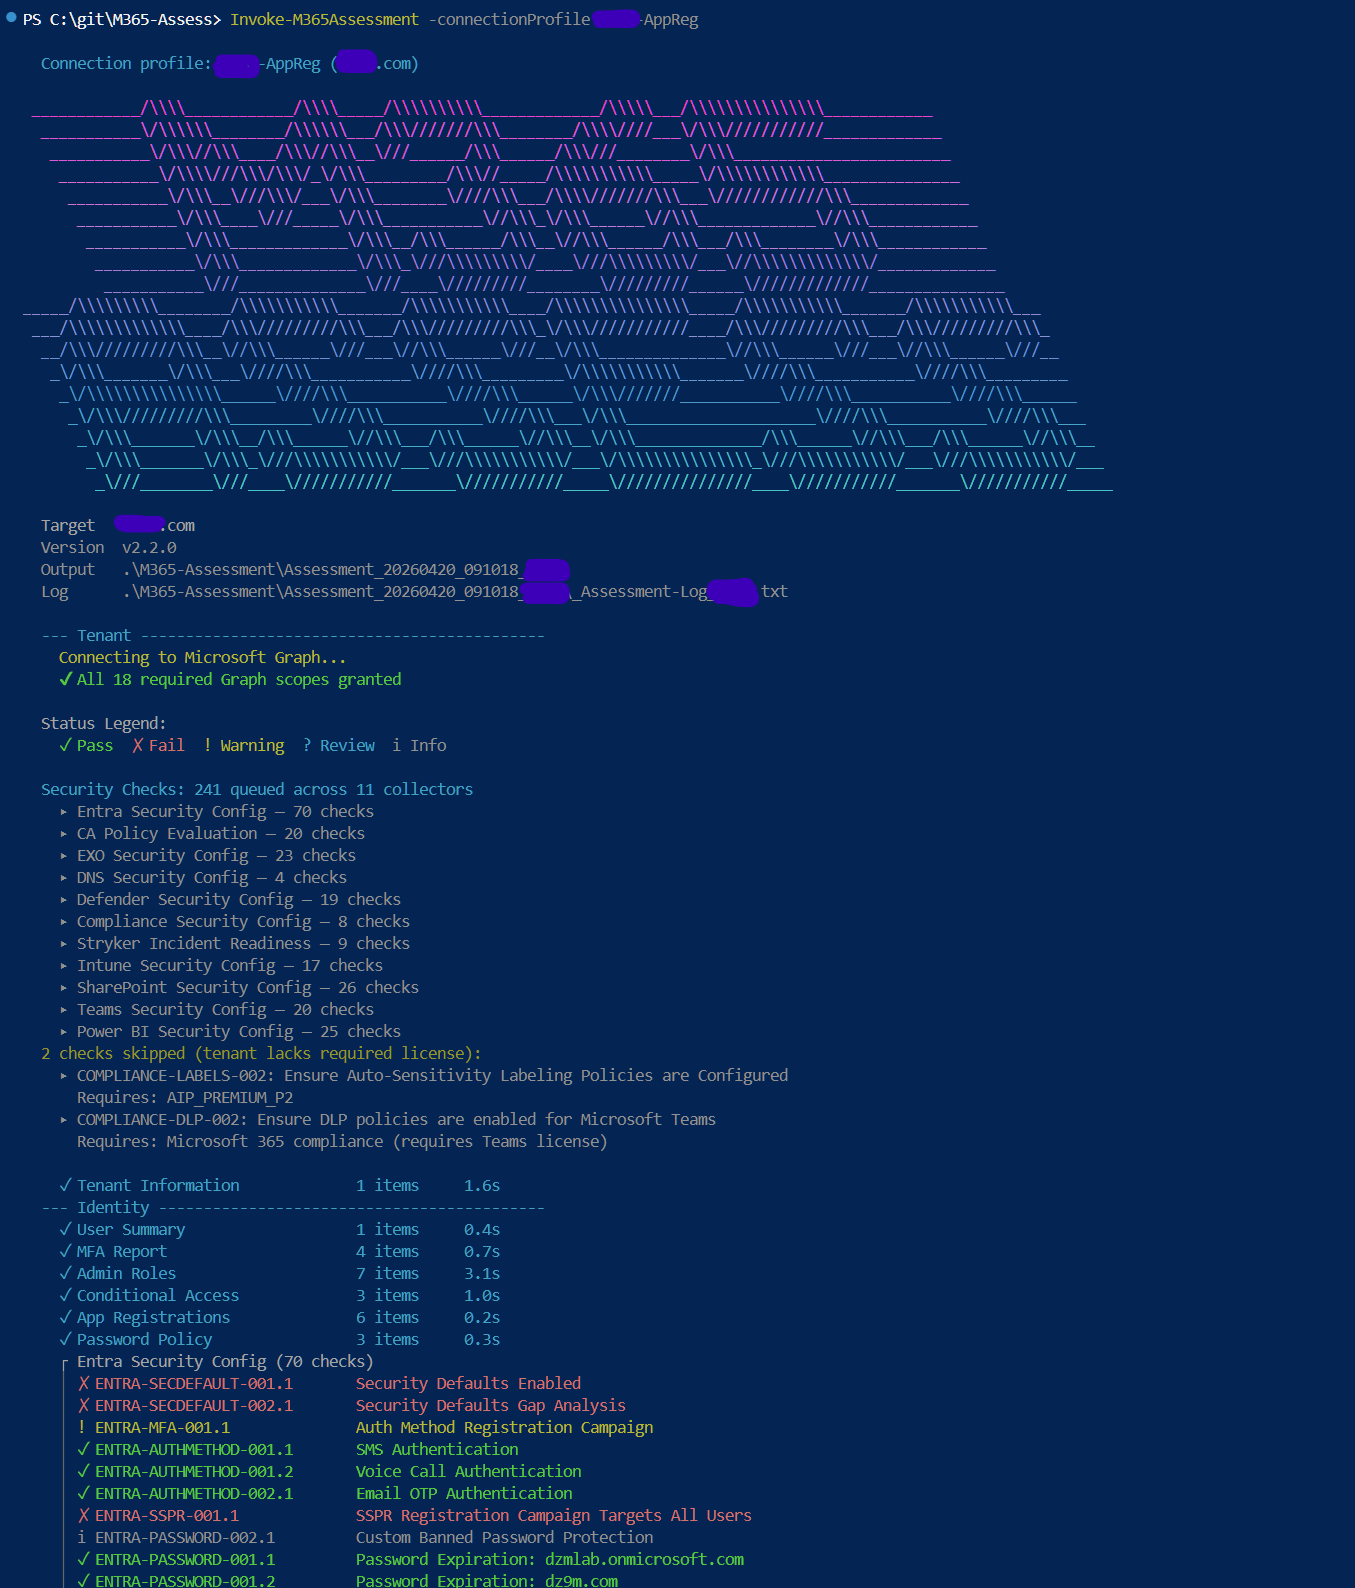 galvnyz/m365-assess
290+ Automated checks across 14 compliance frameworks, interactive HTML report, no data leaves your machine.
 ndaal_open_source/ndaal_public_auditd
Best-practice Linux Auditd rule set with 14,956 MITRE ATT&CK-mapped rules, Ansible deployment role, and lint/test tooling for security monitoring and…
 itskill-jp/wordpress-upgrade-check
Read-only check of every WordPress core version on a server. Flags CVE-2026-87902 (fixed in 7.1.2 and backports), auto-updates turned off, and…
 svtagan/wp-cve-2026-87902
Read-only PHP diagnostic script that checks WordPress version, core checksums, extra PHP files, and known plugin paths for CVE-2026-87902 exposure…
 eveo7/aa-discord-audit
Reconciliation audit for Alliance Auth's Discord integration: finds guild members holding AA-managed roles that Auth never granted and strips or…
 asmitdesai/ubuntils
Python CLI/TUI for forensic triage of Ubuntu systems — detects and remediates persistence mechanisms with artifact collection, timeline correlation,…
 furkankayapinar/cve-2026-94127
Read-only defensive detector for CVE-2026-94127 in F5 BIG-IP APM. Fingerprints hosts, checks versions via iControl REST, and verifies OAuth…
 abhishek2512mishra/claude-code-security-audit
Security scanner auditing Claude Code environments for CVE-2026-21852 pre-trust execution, hook hijacking, and eBPF lockdown.
 jithinkrishnanrs/stylesmuggler-ioc-toolkit
StyleSmuggler (CVE-2026-75650) IOC toolkit for Magento Open Source and Adobe Commerce. Detect compromised stores, Rust implants, PHP web shells,…
 sreckoskocilic/envocabulary
Trace every shell environment variable to its exact file and line origin. Audit shell configs for dead entries, duplicates, and orphaned files across…
 whereisxuezugi/cplhf
Modular Bash toolkit that hardens Debian/Ubuntu systems for CyberPatriot competitions, automating account, firewall, SSH, PAM, and service hardening…
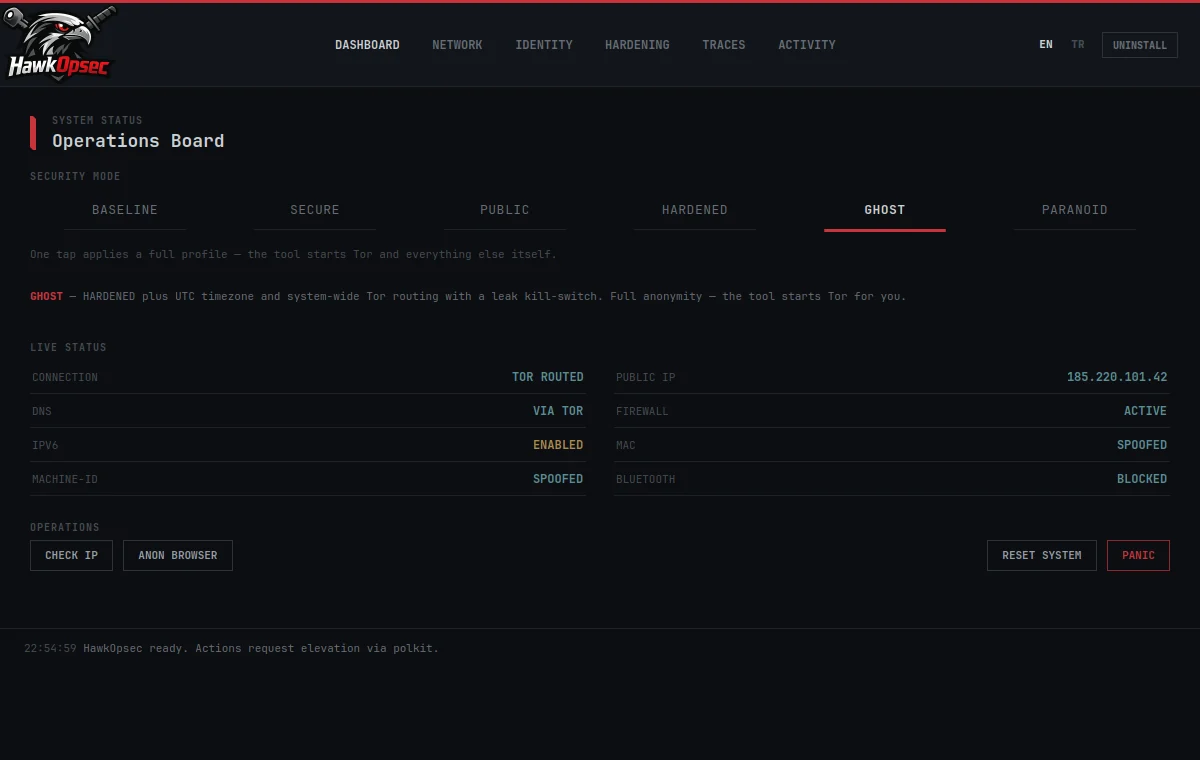 emrekybs/hawkopsec
One-tap Linux OPSEC hardening & anonymity toolkit
 juliosuas/copyfail-guard
Fast, auditable Linux mitigation for CVE-2026-31431 Copy Fail: algif_aead block, verification, and AF_ALG seccomp hardening.