
loki
 grafana/loki
Horizontally scalable, multi-tenant log aggregation system that indexes labels instead of full text, integrates with Grafana, and is optimized for…
general-purpose-utilitiesincident-responselog-analysis+1
29.0k
grafana/lokiHorizontally scalable, multi-tenant log aggregation system that indexes labels instead of full text, integrates with Grafana, and is optimized for…
 abrignoni/aleapp
Android Logs Events And Protobuf Parser
 tenzir/tenzir
Collect, parse, normalize, aggregate, store, query, and route security telemetry data at scale using pipeline-based dataflows for threat detection…
 graylog2/graylog2-server
Centralized log management platform for collecting, indexing, and analyzing streaming logs, with alerting and event correlation for security…
 wazuh/wazuh
Open-source XDR and SIEM platform for threat detection, log analysis, file integrity monitoring, vulnerability assessment, and compliance management…
 clausing/scripts
Collection of Python and Perl scripts for digital forensics, incident response, and network analysis, including hash signature tooling and packet…
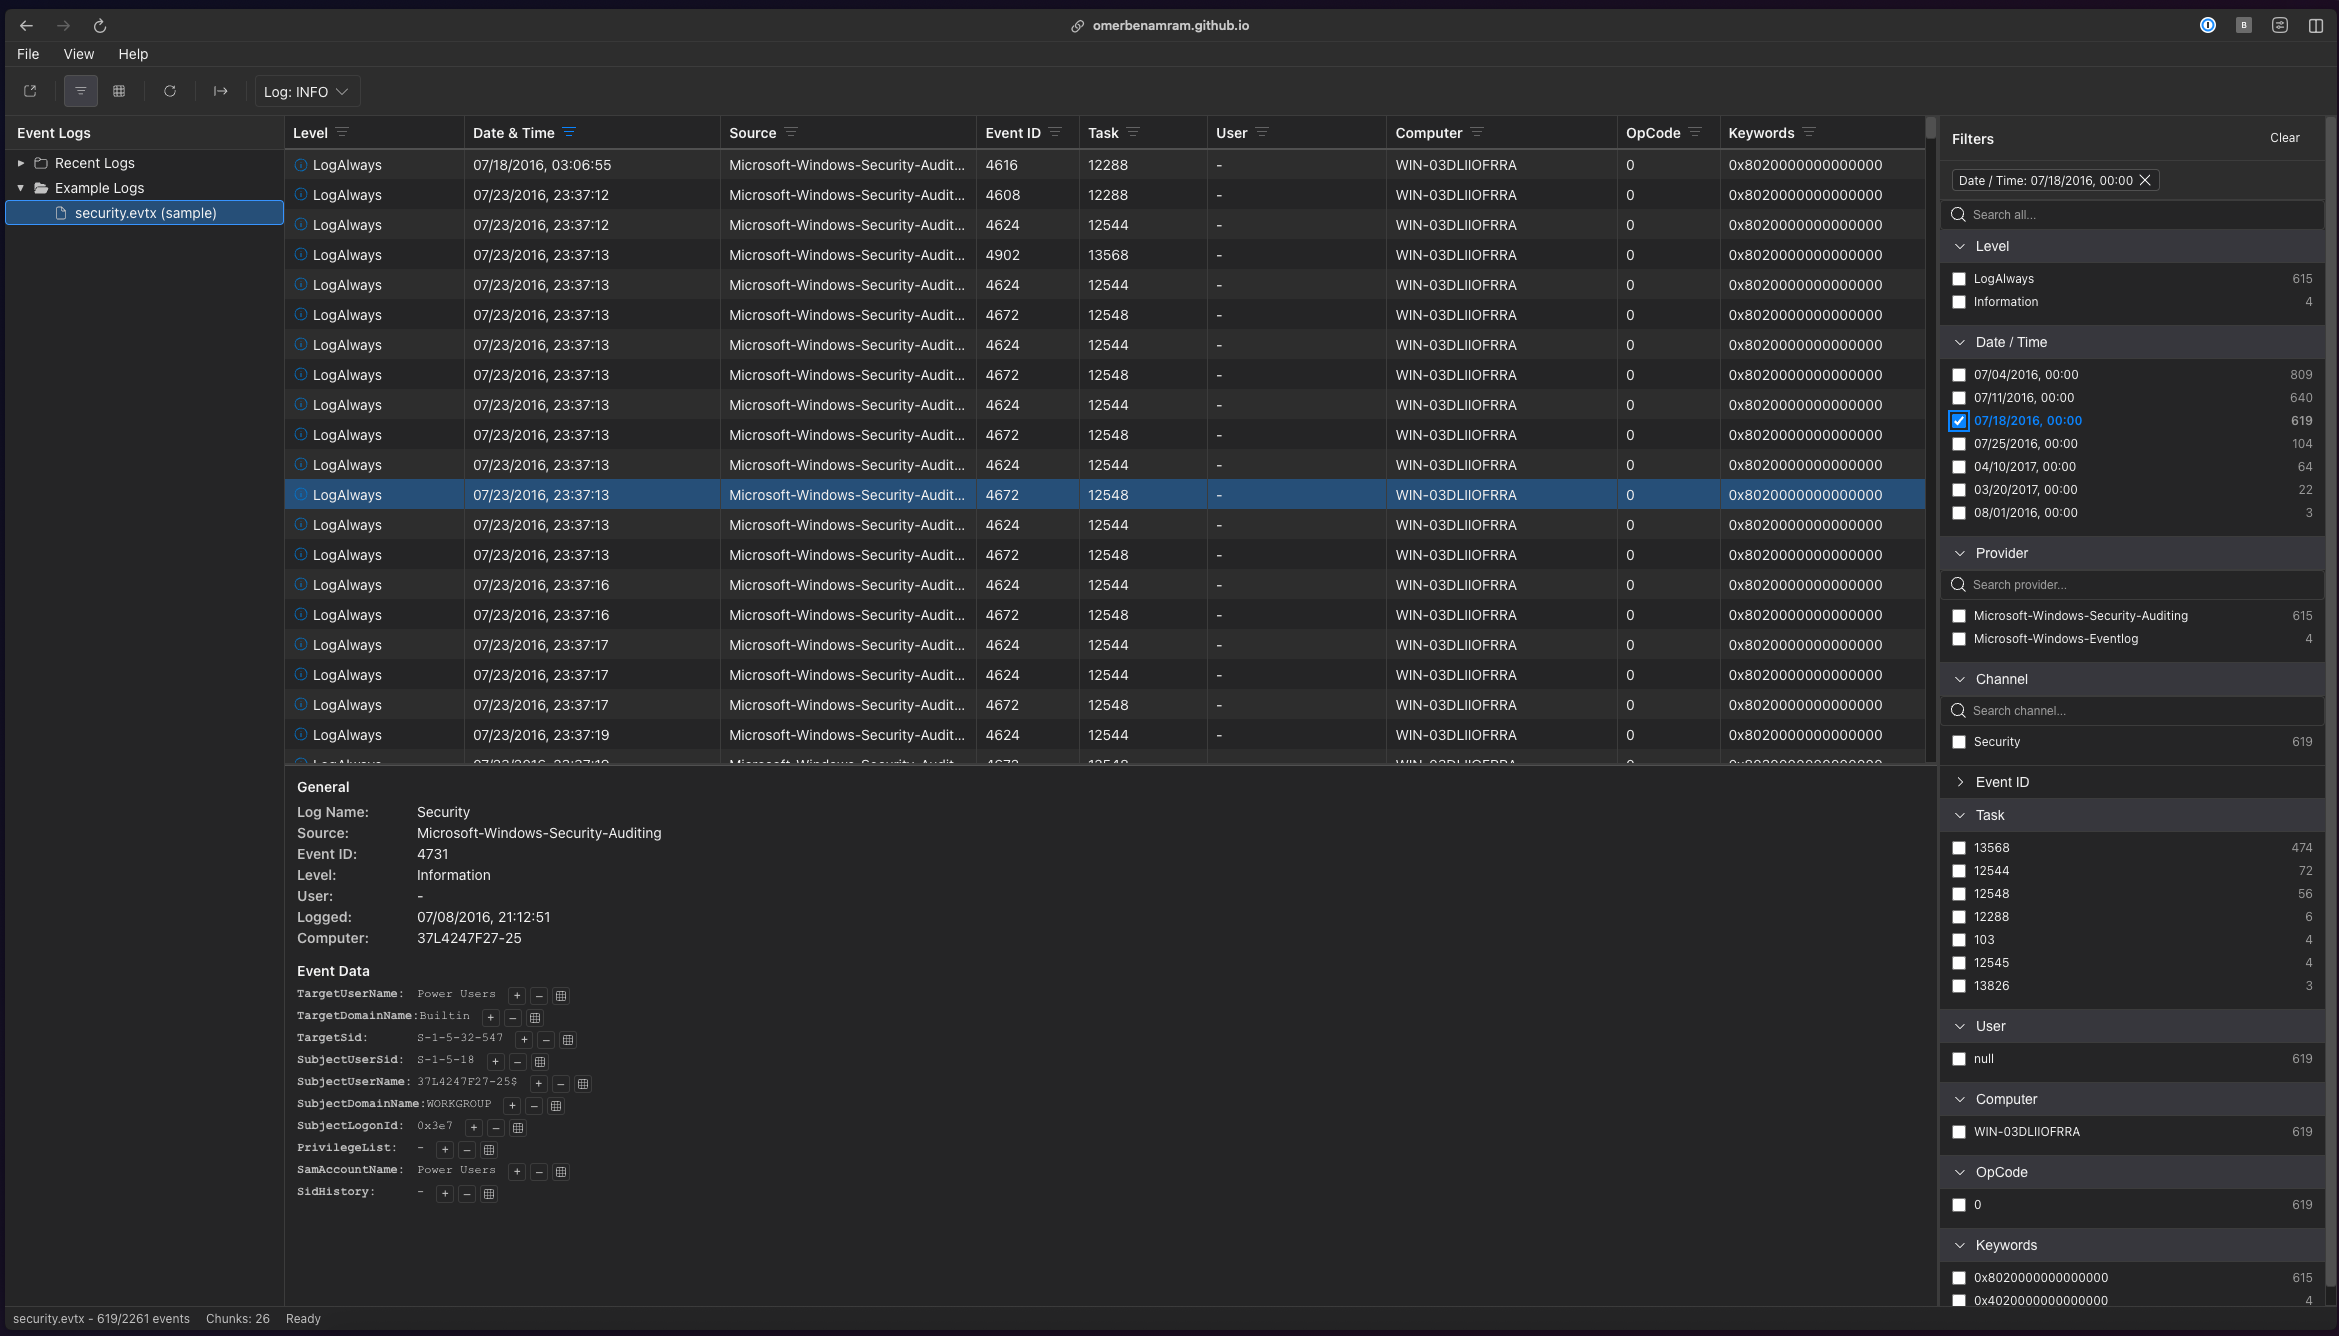 omerbenamram/evtx
A Fast (and safe) parser for the Windows XML Event Log (EVTX) format
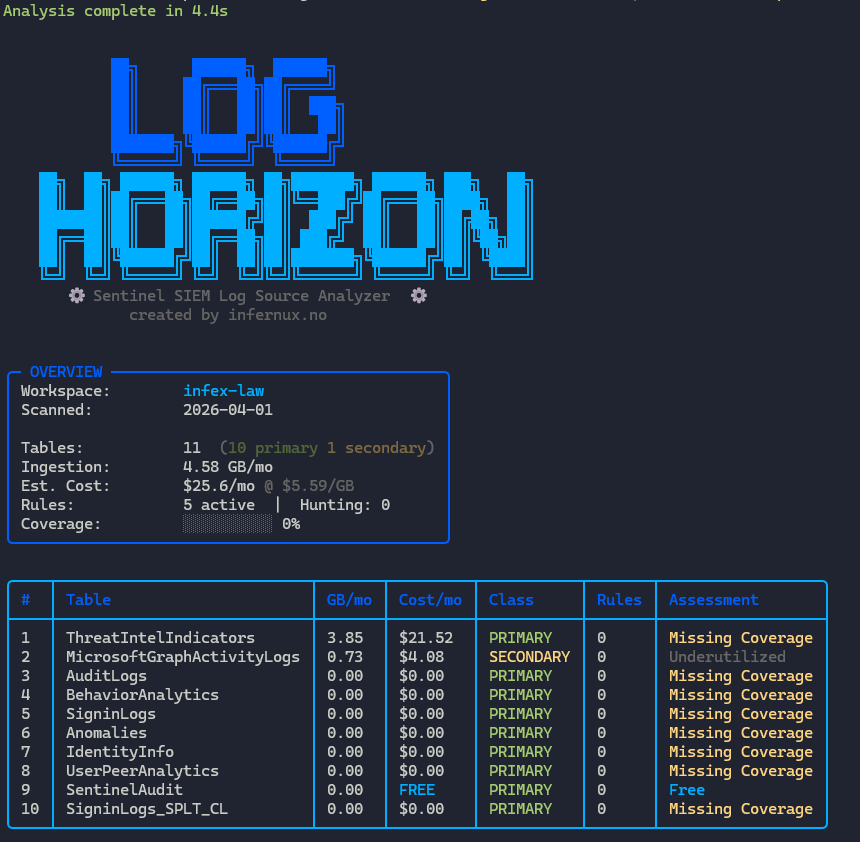 lnfernux/log-horizon
Microsoft Sentinel SIEM Log Source Analyzer
 cowrie/cowrie
Cowrie SSH/Telnet Honeypot https://docs.cowrie.org/

 yamato-security/hayabusa
Multi-threaded Windows event log forensics timeline generator and threat hunting tool with full Sigma rule support, producing CSV/JSON timelines for…
 wagga40/zircolite
A standalone SIGMA-based detection tool for EVTX, Auditd and Sysmon for Linux logs
 yamato-security/wela
Audits Windows event log settings against best-practice guidelines and Sigma-rule detectability, with automated configuration for DFIR readiness.
 corelight/ecs-logstash-mappings
Mapping Corelight or Zeek data to Elastic Common Schema logs
 jay123anta/laravel-threat-detection
Passive Laravel middleware that detects and logs SQL injection, XSS, RCE, bot scanners, and 175+ attack patterns. Features a built-in dashboard,…
 mgreen27/detectraptor
A repository to share publicly available Velociraptor detection content
 mandiant/macos-unifiedlogs
A cross platform parser for Apple UnifiedLogs!
 microsoft/msticpy
Microsoft Threat Intelligence Security Tools