
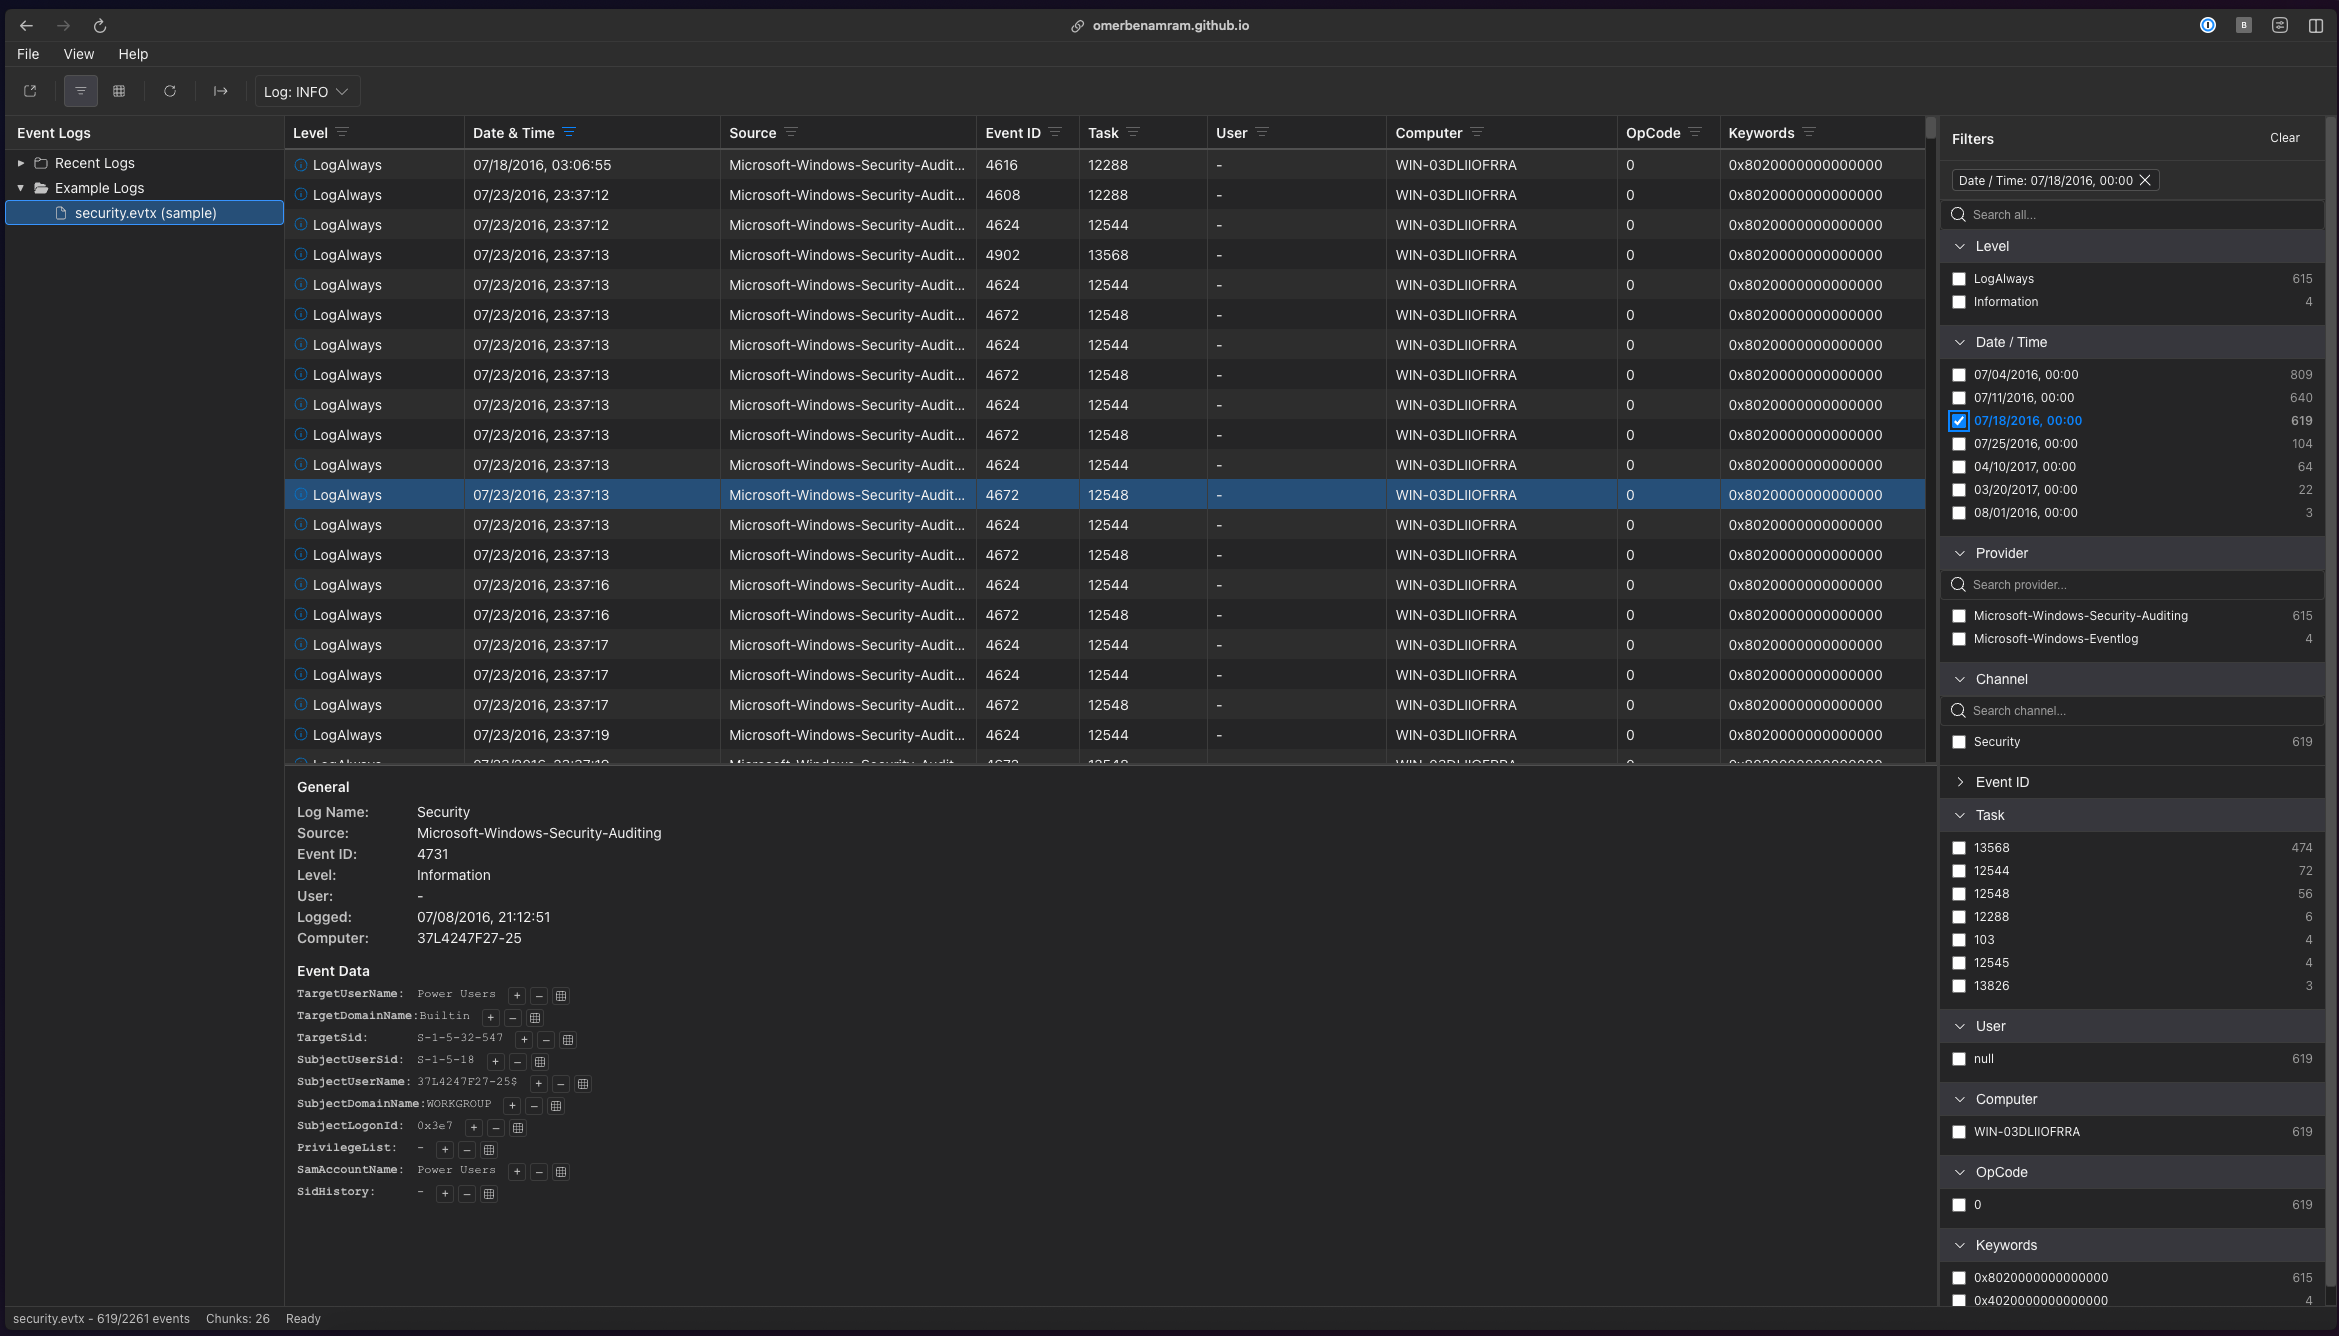
evtx
 omerbenamram/evtx
A Fast (and safe) parser for the Windows XML Event Log (EVTX) format
digital-forensicsforensicsincident-response+1
omerbenamram/evtxA Fast (and safe) parser for the Windows XML Event Log (EVTX) format
 kubeshark/kubeshark
eBPF-powered network observability for Kubernetes. Indexes L4/L7 traffic with full K8s context, decrypts TLS without keys. Queryable by AI agents via…
 rabbitstack/fibratus
Security sensor for realtime threat detection and protection
 backbay-labs/hush
Portable security rules for the action boundary of AI agents
 digital-dev/log4j-cve-2021-44228-remediation
This powershell script is intended to be used by anyone looking to remediate the Log4j Vulnerability within their environment. It can target multiple…
 somhm-solutions/shell-shock
*CVE-2014-6271* Unix Arbitrary Code Execution Exploit commonly know as Shell Shock. Examples, Docs, Incident Response and Vulnerability/Risk…