
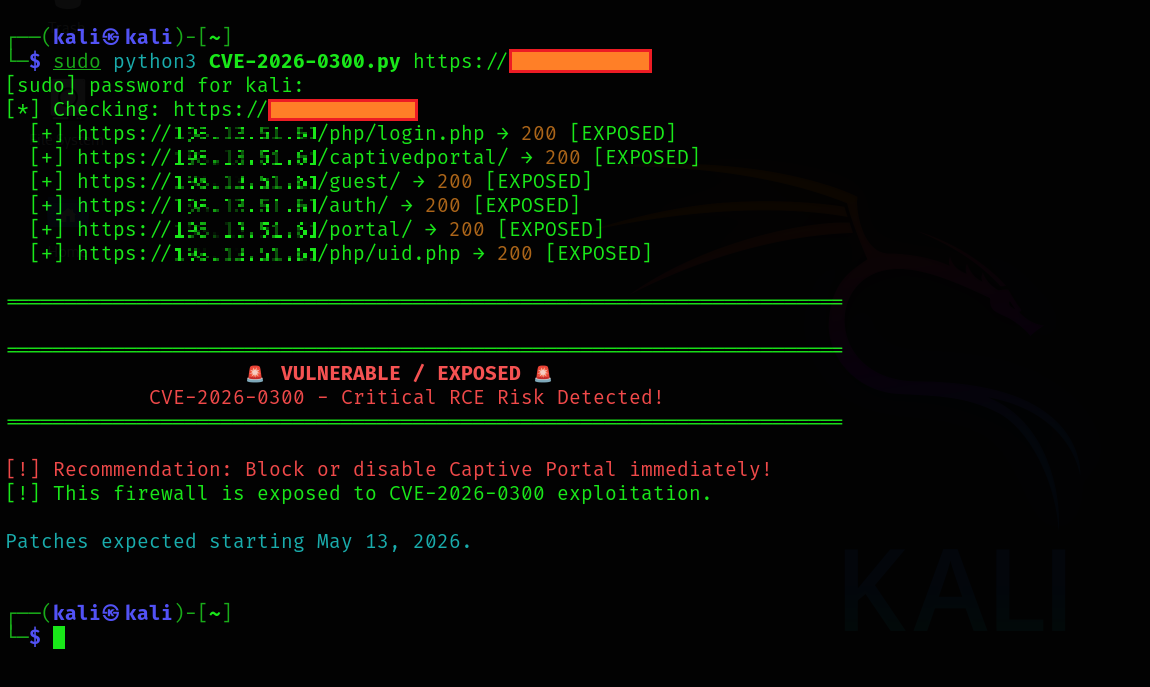
CVE-2026-0300
 0xredash/cve-2026-0300
Advisory and technical analysis of CVE-2026-0300, a critical unauthenticated buffer overflow RCE in Palo Alto PAN-OS User-ID portals, with affected…
exploitationincident-responsenetwork-security+3
1
0xredash/cve-2026-0300Advisory and technical analysis of CVE-2026-0300, a critical unauthenticated buffer overflow RCE in Palo Alto PAN-OS User-ID portals, with affected…
 brentmartinmiller/php2shell-check
Read-only triage script for WordPress sites after PHP2Shell (CVE-2026-109618, CVE-2026-109619). Checks for signs of compromise and writes a report…
 g4bri-3l3/idwolf
Read-only Active Directory & Microsoft Entra ID hygiene auditor in pure PowerShell. Collect once, analyze offline: deterministic findings, attack…
 mafifrizi/tanuki
Tactical Identity Operator for Linux & Hybrid Active Directory
 matijamiki/ranwhat
Flight recorder and secret scanner for AI coding agents. Reads what Claude Code, Codex, Gemini CLI and 17 more ran, and flags risky actions and…
 florentineprinzessinzusachsen/badbox-h713-projector
Analysis and cleanup guide for BadBox malware on Allwinner H713 Android projectors: ADB access, infection proof, firmware backup, dropper removal,…
 emrekybs/socmintelligence
A modular OSINT & SOCMINT framework for social media intelligence, investigation, and public data analysis.
 bert-janp/entratrace
Defensive research tool that documents observable API endpoints and user agents of offensive tooling targeting Microsoft Entra ID, supporting…
 basitsajidsoc/soc-investigation-cve-2024-49138
Investigation and Incident Response report for LetsDefend Alert SOC335 (CVE-2024-49138 Exploitation)
 fireeye/pywintrace
Python ctypes wrapper for Event Tracing for Windows (ETW) enabling session control, event capture, and custom callbacks for security monitoring and…
 mrk336/inside-cve-2026-20805-how-a-windows-dwm-flaw-exposed-sensitive-data
CVE‑2026‑20805: A Windows Desktop Window Manager flaw causing local information disclosure. Requires low privileges, no user interaction. Rated CVSS…
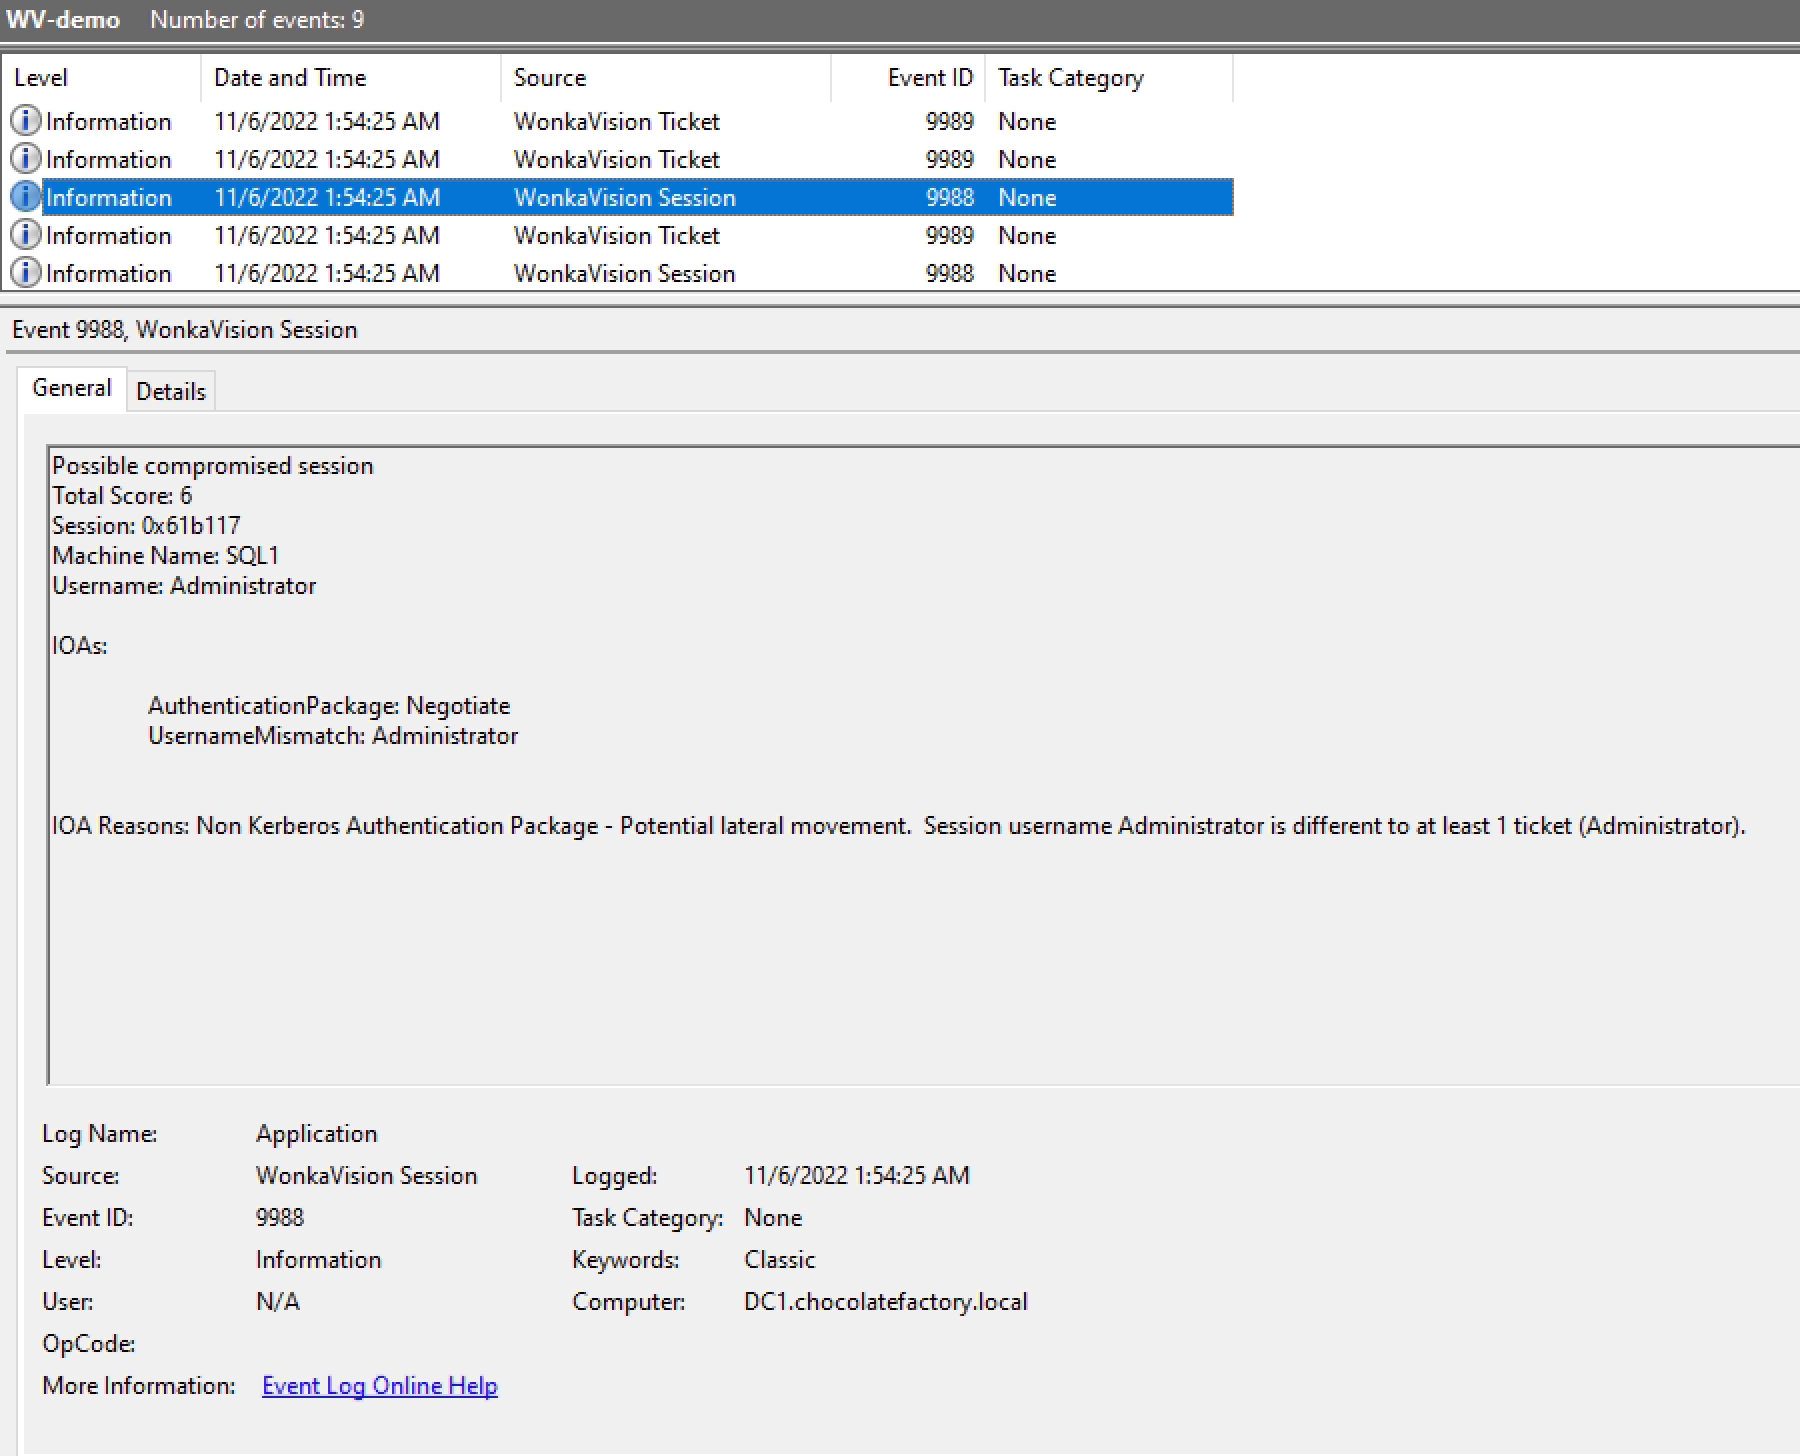 0xe7/wonkavision
Detects forged Kerberos tickets by dumping session and ticket data, scoring anomalies, and generating Windows event-log indicators for SIEM-based…
 michael-kanda/wp2shell-ioc-scanner
Detects shadow-administrator accounts in WordPress via configurable indicators and heuristics, then removes selected accounts through guarded, logged…
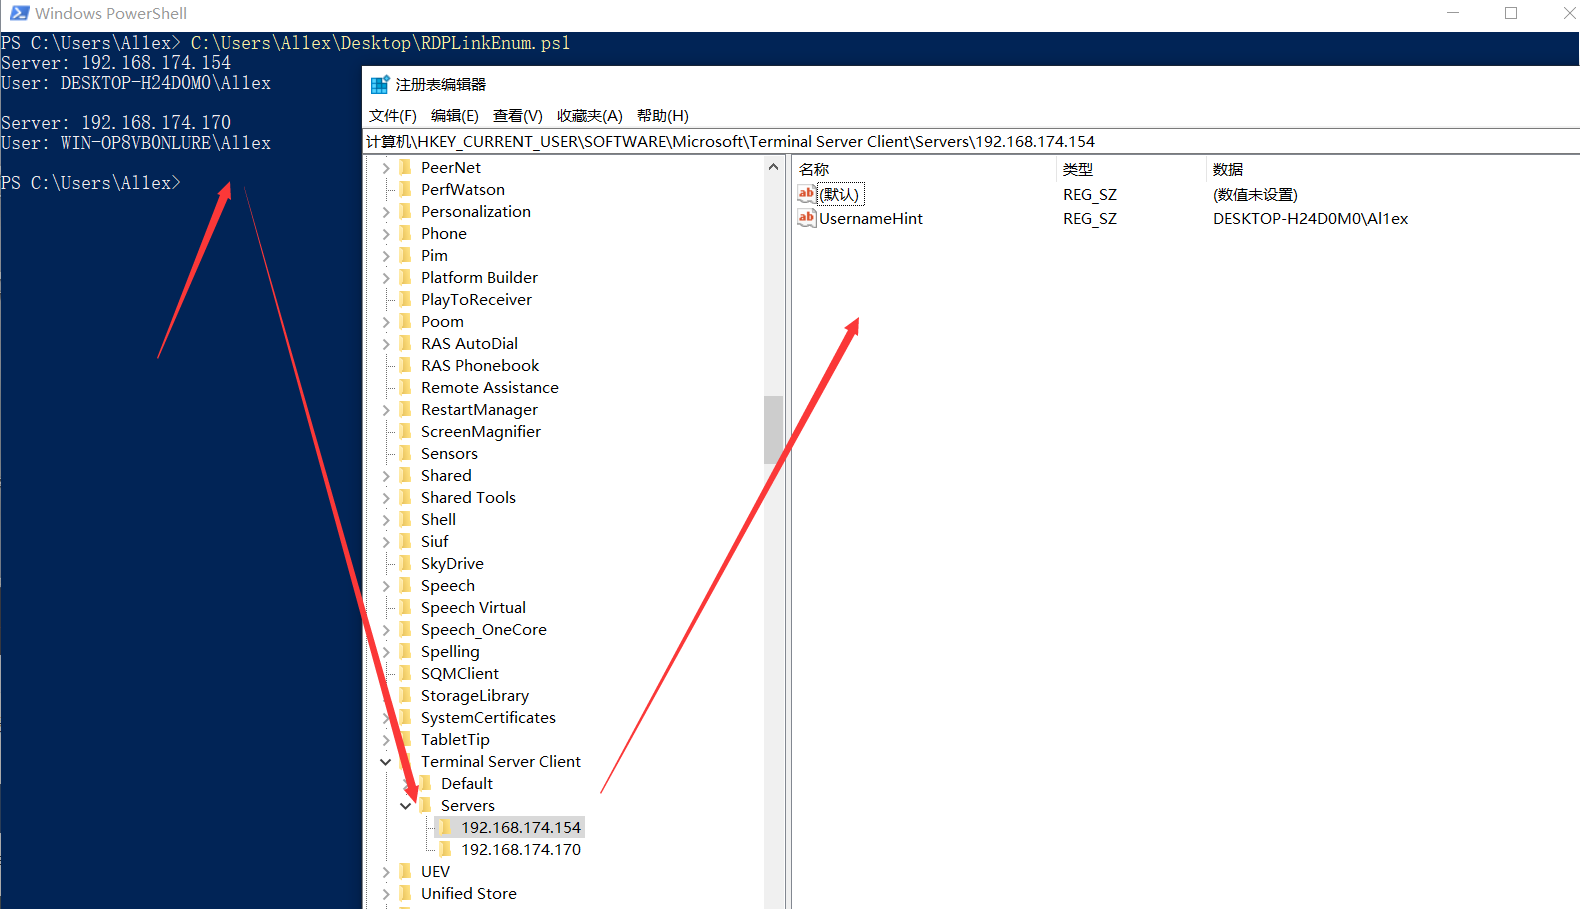
 mthcht/awesome-lists
Curated repository of threat intelligence feeds, IoC lists, YARA rules, and DFIR tool references for SOC/CERT/CTI detection and incident response.
 aburgh/disk-arbitrator
A Mac OS X forensic utility which manages file system mounting in support of forensic procedures.
 notitssixtyn3in/cve-2025-4162030
Security advisory detailing a critical authentication vulnerability (CVE-2025-4162030) in Copilot, involving user ID switching that could lead to…
 notitssixtyn3in/cve-2025-4162027
Security advisory detailing a critical authentication vulnerability in Copilot where user IDs are switched, enabling unauthorized account access and…