
detecttrace
 g0dse11/detecttrace
Open-source detection engineering tool that traces security detections end to end and identifies the first failing stage.
defensive-toolsdevsecopsincident-response+5
1
g0dse11/detecttraceOpen-source detection engineering tool that traces security detections end to end and identifies the first failing stage.
 joertx07/printnightmare-detection-lab
Splunk SIEM lab simulating and detecting CVE-2021-34527 (PrintNightmare) exploitation using Sysmon, Windows Event logs, and custom SPL detection…
 corelight/zeek-long-connections
Zeek package for tracking long connections to report them before they have completed.
 sarjanpatel22/siem-threat-detection-lab
Blue-team SIEM lab: Wazuh 4.7.5 detecting 7 simulated attacks (SSH brute force, Slowloris DoS / CVE-2007-6750, web attacks) with real-time MITRE…
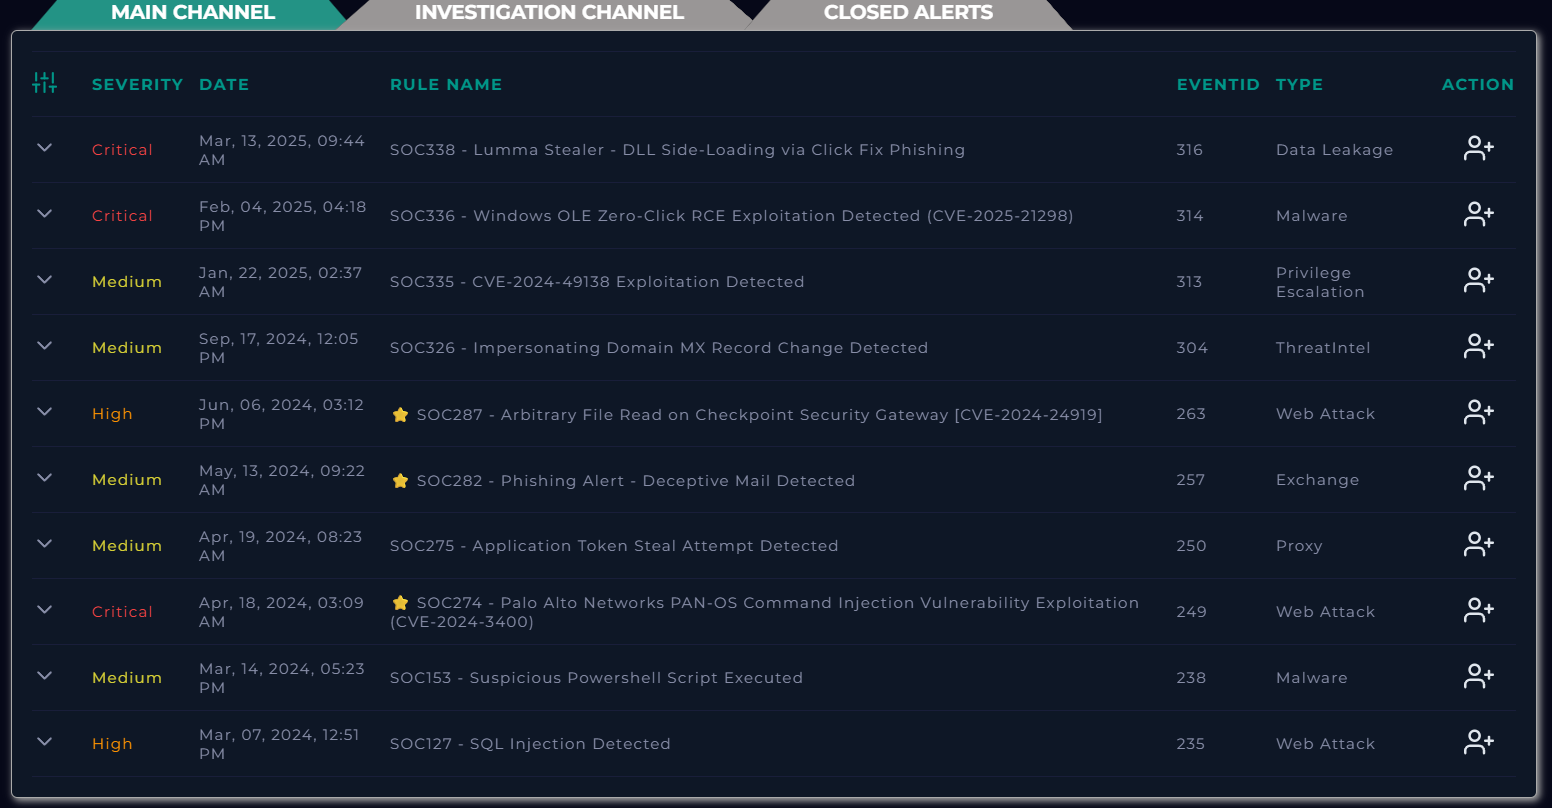 tarunbharathe/zero-click-rce-incident-response-cve-2025-21298
Technical investigation and host containment of a Critical-severity Zero-Click RCE exploit (CVE-2025-21298) using EDR telemetry and static malware…
 dawnsmithcyber/azure-vulnerability-remediation-project
End-to-end vulnerability management lifecycle on Azure Windows Server 2025. Features OS patching and network-level compensating controls (NSG) to…
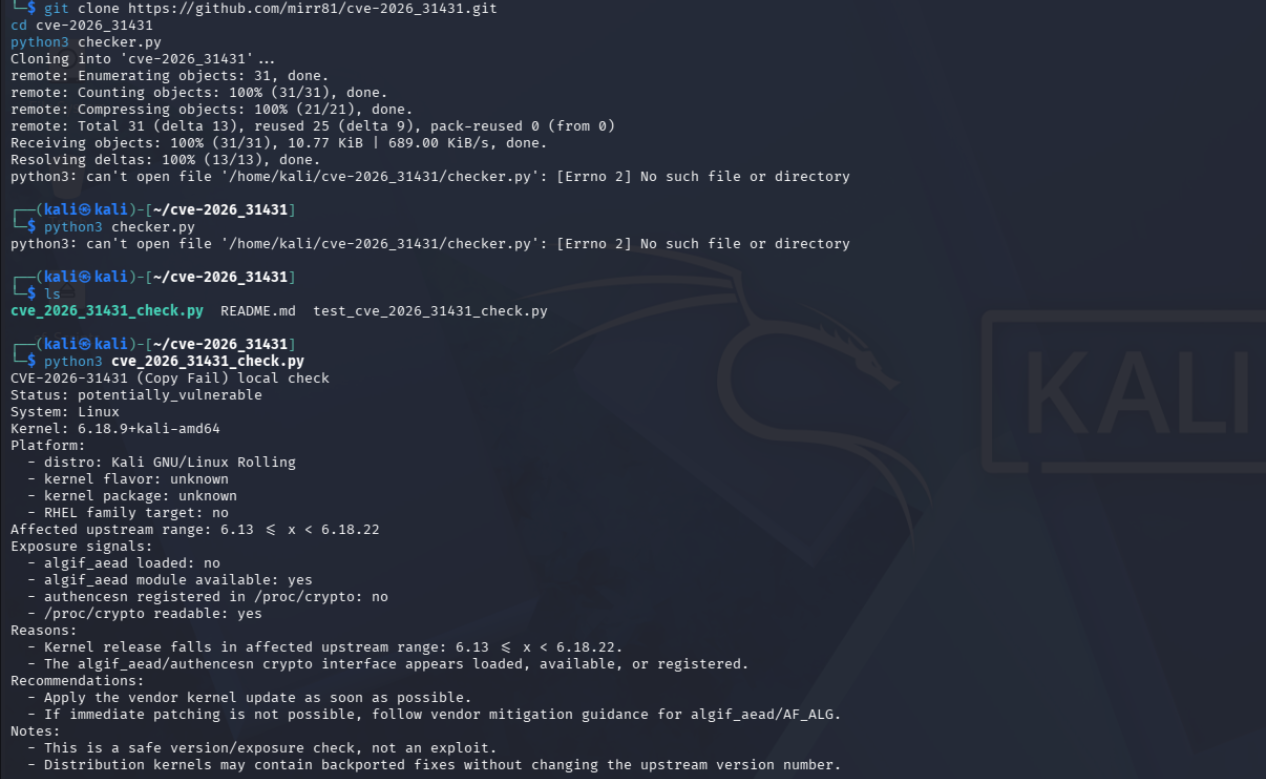 kuniyal08/copy-fail-cve-2026-31431-lab
Reproduced the fileless LPE CVE‑2026‑31431 (“Copy Fail”) on Kali Linux, then built auditd, Sigma & YARA detections to catch this stealthy kernel…
 v3ng4mxv1p3r/mobile-drop-device-soc-detection
End-to-end simulation of detecting a root-less Android Drop Device (Casper) using Wazuh SIEM to capture Layer 7 attacks like Shellshock…
 lawndoc/mediator
An extensible, end-to-end encrypted reverse shell that works across networks without port forwarding.