
opencanary
 thinkst/opencanary
Low-resource honeypot that emulates common network services to detect post-breach attacker activity, with extensible protocol modules and…
defensive-toolsincident-responseintrusion-detection+3
thinkst/opencanaryLow-resource honeypot that emulates common network services to detect post-breach attacker activity, with extensible protocol modules and…
 la3ar0v/tuxresponse
Automated Linux incident response script with live triage, memory acquisition (LiME), disk imaging, YARA scanning, and HTML report generation.
 jtsylve/lime
Kernel module for volatile memory acquisition from Linux and Android devices, producing forensically sound captures to disk or over the network.
 sonitbahl/sshintel
Self-contained SSH honeypot for capturing attacker interactions and turning them into structured security intelligence.

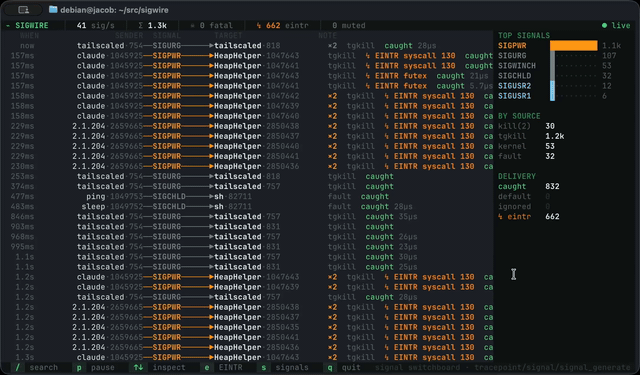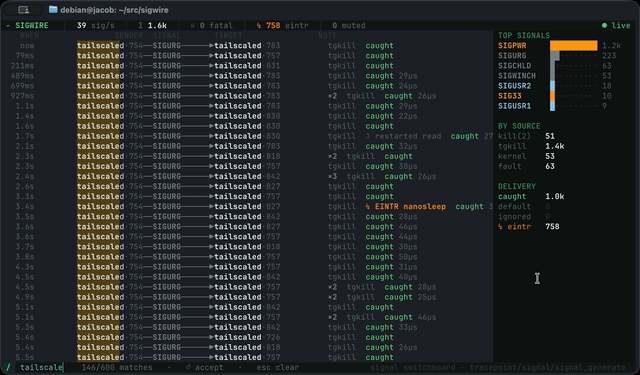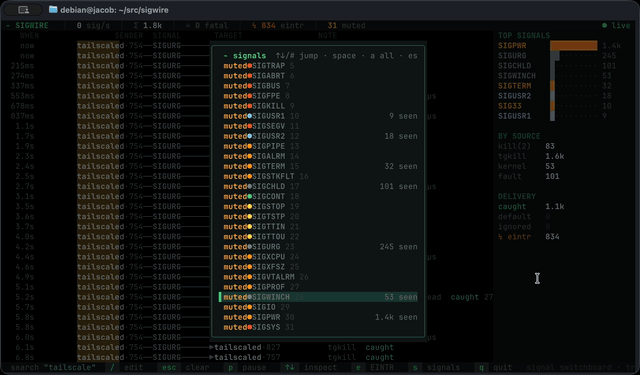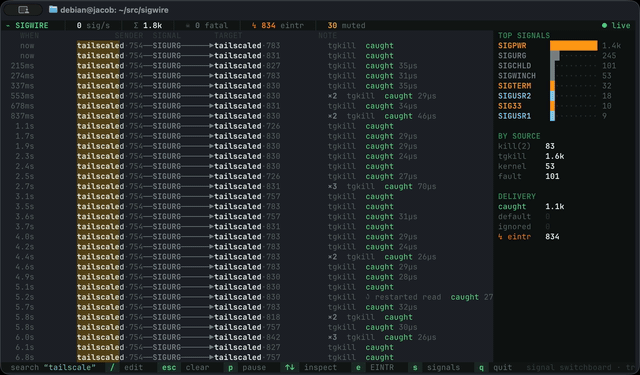 yeet-src/sigwire
Live kernel signal observability tool using eBPF tracepoints to stream every signal raised on a Linux host, showing sender, target, disposition,…
 tclahr/uac
Portable, dependency-free incident response tool that automates forensic artifact collection from Unix-like systems, including memory acquisition,…
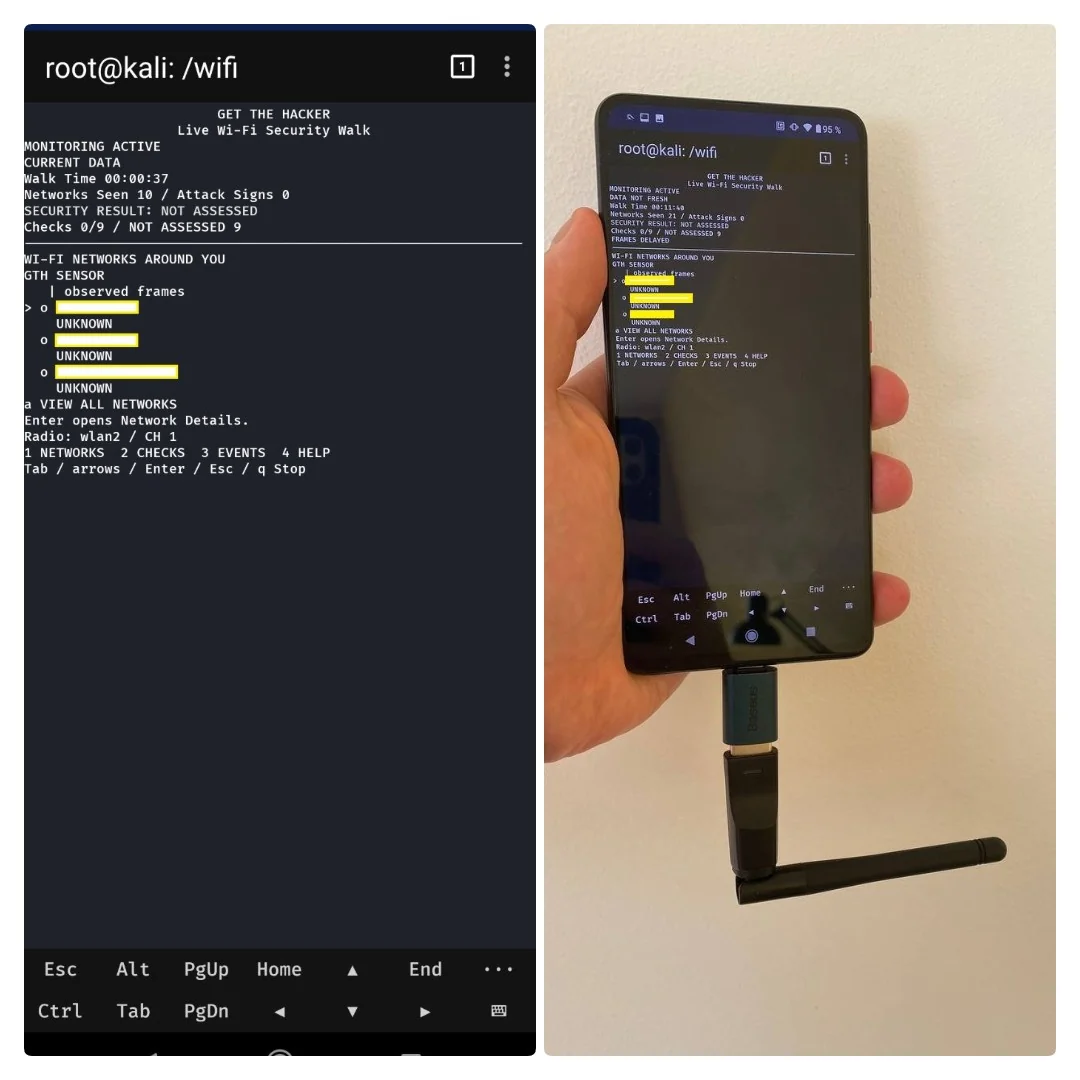 buybitart/get-the-hacker
Hunt WiFi threats silently. Catch the hackers.
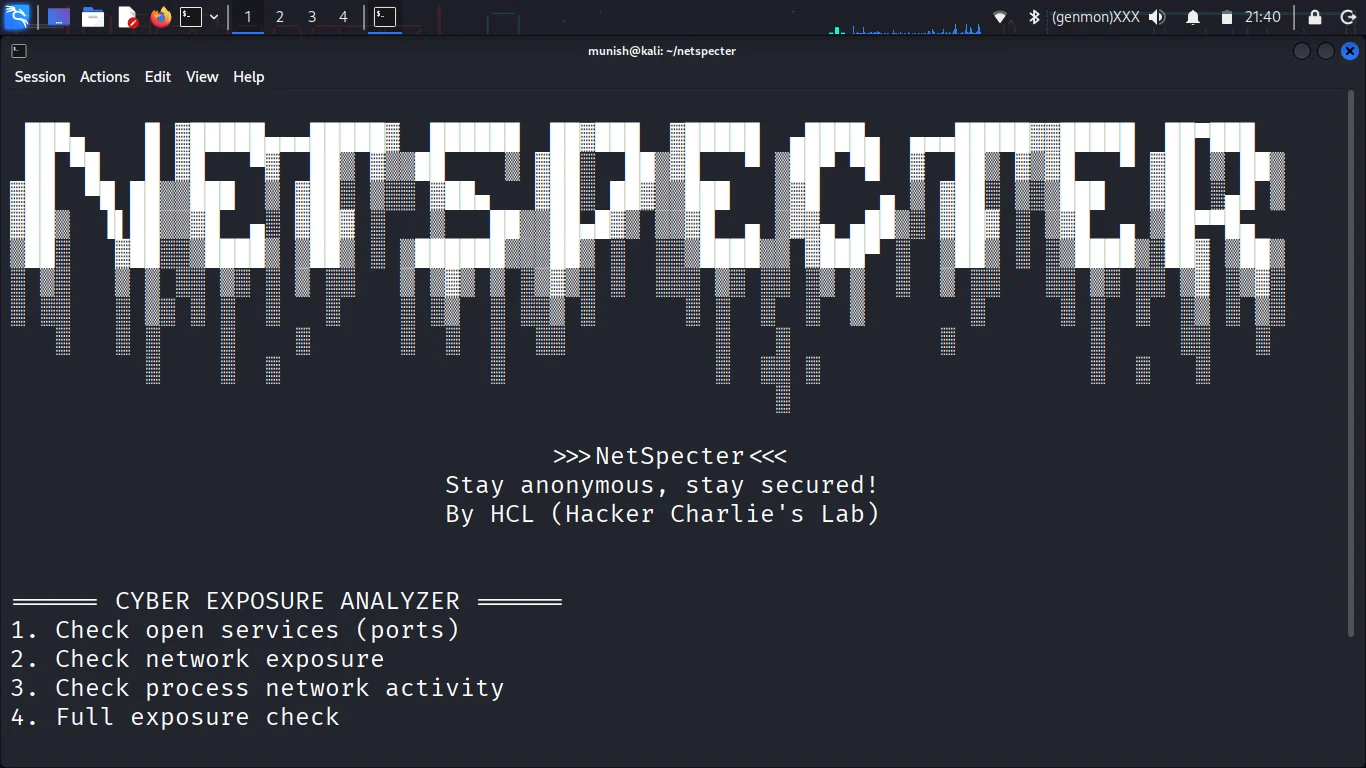 mrhackercharlie/netspecter
Real-time system monitoring tool for detecting process activity and network exposure!
 wmal/linux-kodachi
Hardened Debian-based privacy OS with pre-integrated anonymity stack (Tor, VPN, DNSCrypt), anti-forensic tooling, SOC security center, and standalone…
 daddycocoaman/dumpscan
Finding secrets in kernel and user memory
 olafhartong/sysmon-modular
A repository of sysmon configuration modules
 mrbuglf/xz-utils_cve-2024-3094
XZ-Utils工具库恶意后门植入漏洞(CVE-2024-3094)
 wagga40/logstotal
Self-hosted multi-engine Sigma detection for event logs
 maxime288/fragnesia-cve-2026-46300
Educational repository detailing CVE-2026-46300 (Fragnesia), a Linux kernel local privilege escalation vulnerability. Provides technical analysis,…
 rfxn/linux-malware-detect
Multi-engine Linux malware scanner with five detection stages (MD5, HEX pattern, YARA, ClamAV, statistical), real-time inotify monitoring,…
 opensourcemalware/polinrider
Technical dossier on the DPRK-linked PolinRider supply-chain attack, documenting obfuscated JS payload injection, git history manipulation, C2…