
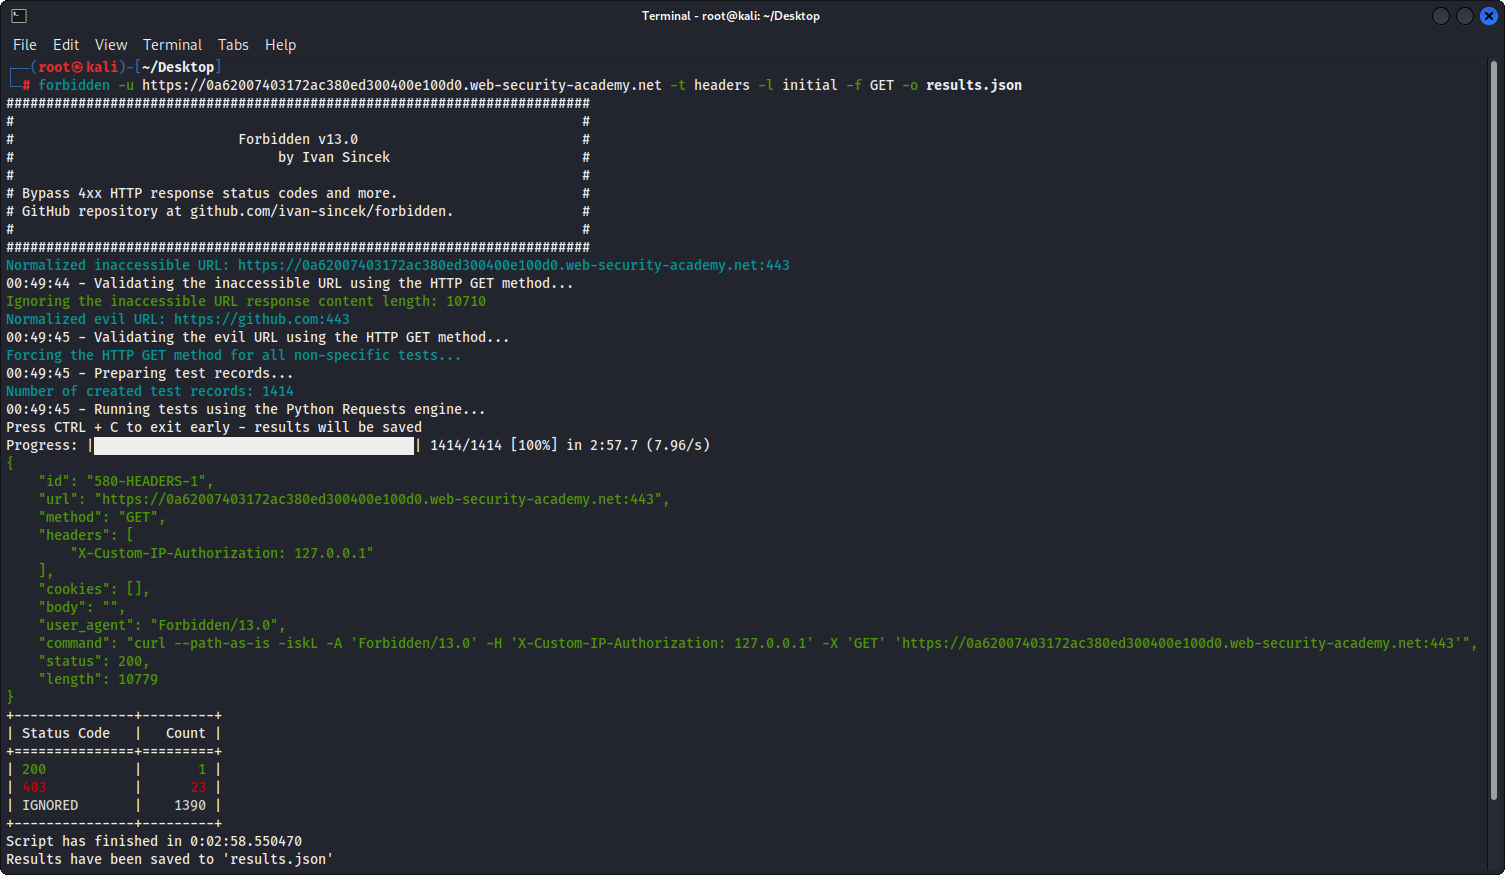
forbidden
 ivan-sincek/forbidden
Bypass 4xx HTTP response status codes and more. The tool is based on Python Requests, PycURL, and HTTP Client.
fuzzingids-ips-evasioninformation-gathering+5
257
ivan-sincek/forbiddenBypass 4xx HTTP response status codes and more. The tool is based on Python Requests, PycURL, and HTTP Client.
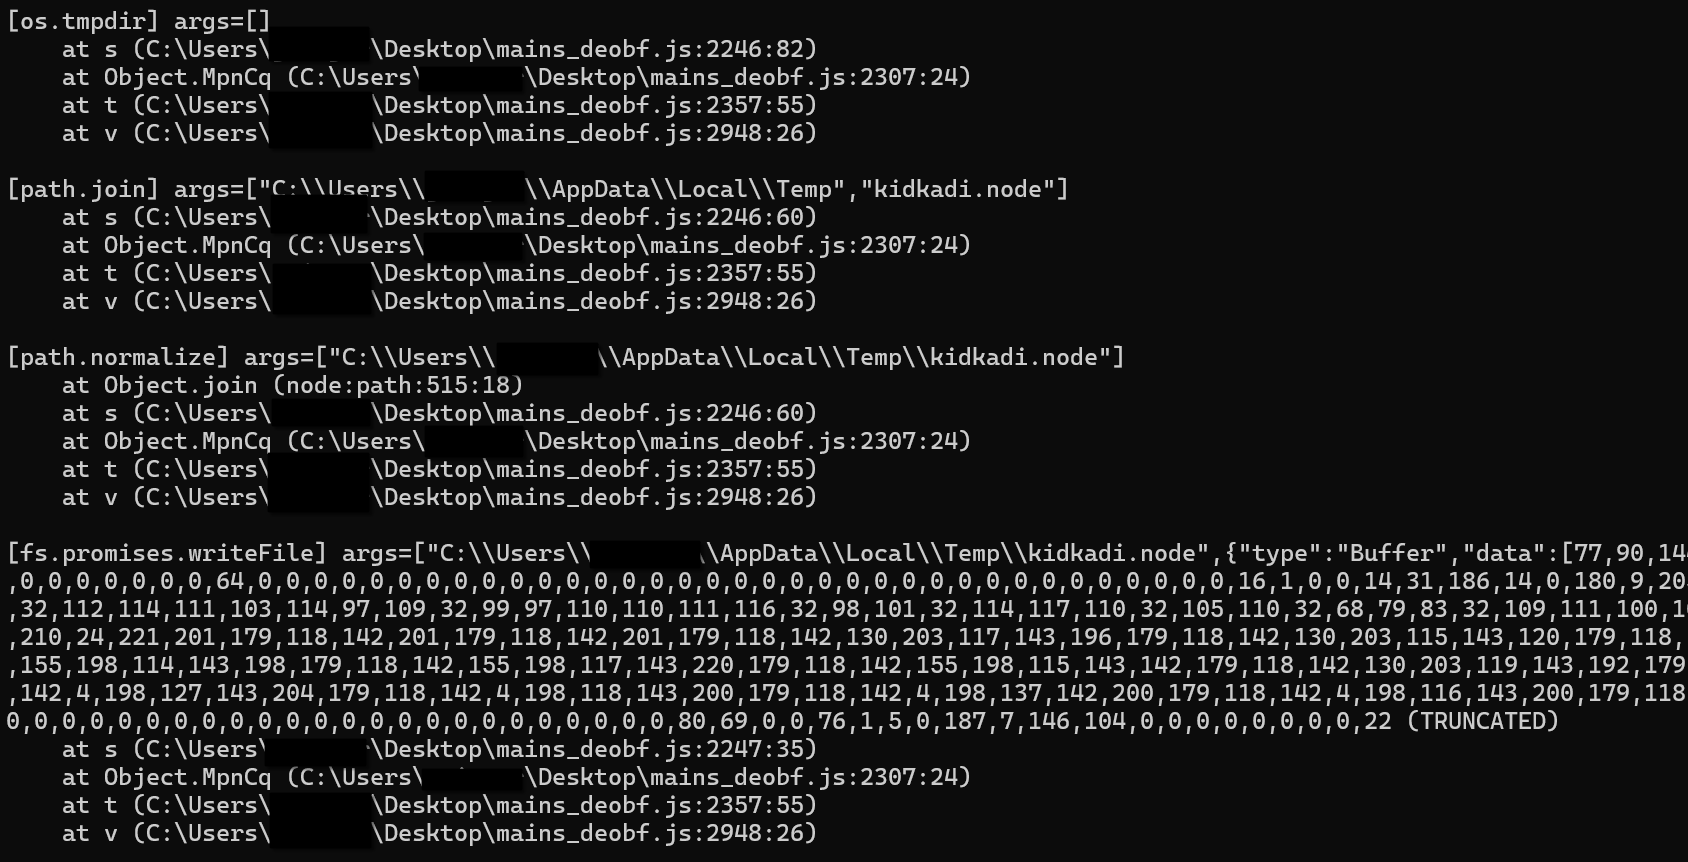 checkpointsw/nodejs-tracer
Runtime tracer for Node.js malware analysis that hooks core modules, logs calls, spoofs anti-analysis checks, and captures file writes and HTTP…
 rofl0r/proxychains-ng
proxychains ng (new generation) - a preloader which hooks calls to sockets in dynamically linked programs and redirects it through one or more…
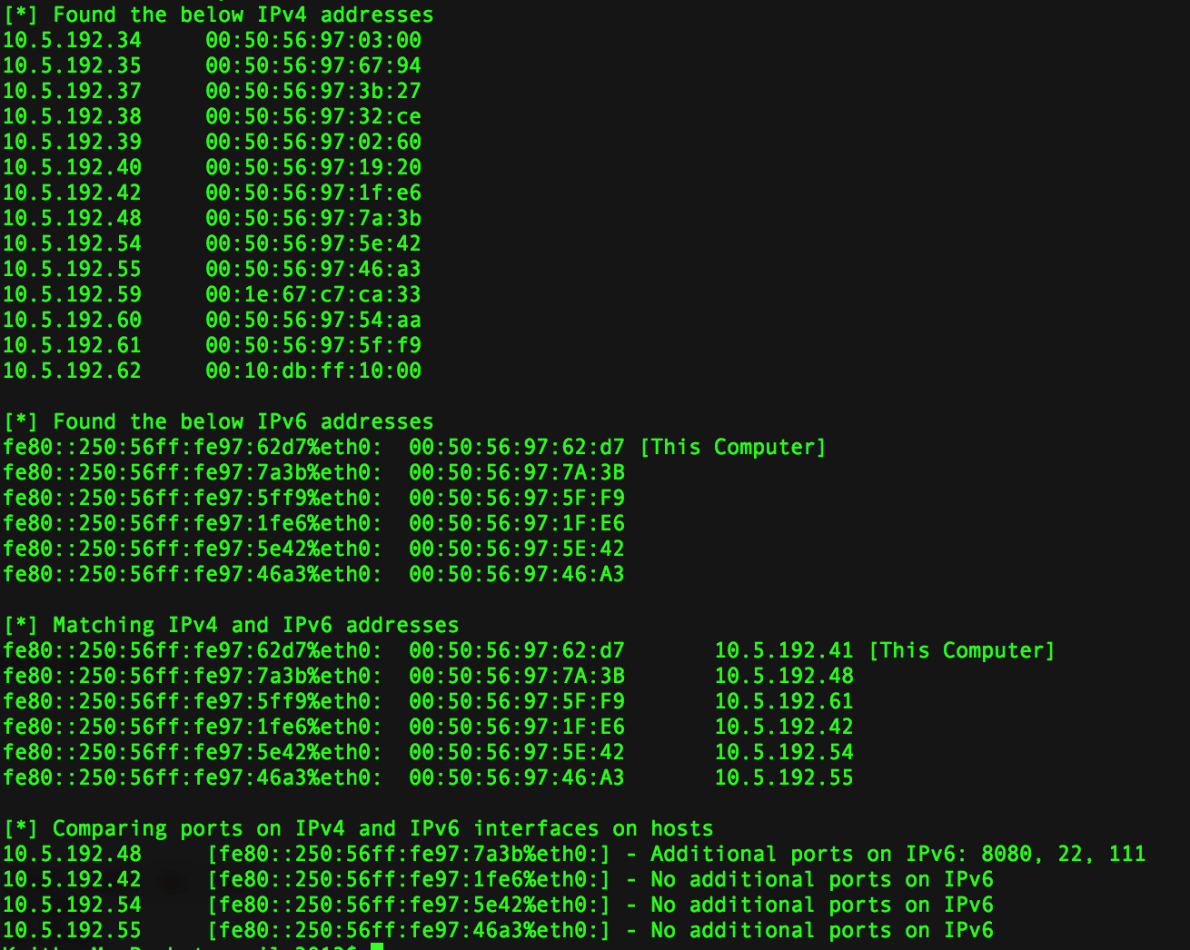 milo2012/ipv4bypass
Using IPv6 to Bypass Security
 saadahla/anti-sandbox
C++ tool for detecting AnyRun sandbox environments, enabling malware to evade dynamic analysis and automated sandboxing systems.
 matro7sh/bypassav
This map lists the essential techniques to bypass anti-virus and EDR
 toperaproject/topera
IPv6 analysis tool: the other side
 d7ead/cve-2025-61156
Insecure access control in ThreatFire System Monitor's TfSysMon.sys driver allows unprivileged process termination with kernel privileges, enabling…
 es3n1n/no-defender
A slightly more fun way to disable windows defender + firewall. (through the WSC api)
 mgeeky/stracciatella
OpSec-safe Powershell runspace from within C# (aka SharpPick) with AMSI, Constrained Language Mode and Script Block Logging disabled at startup
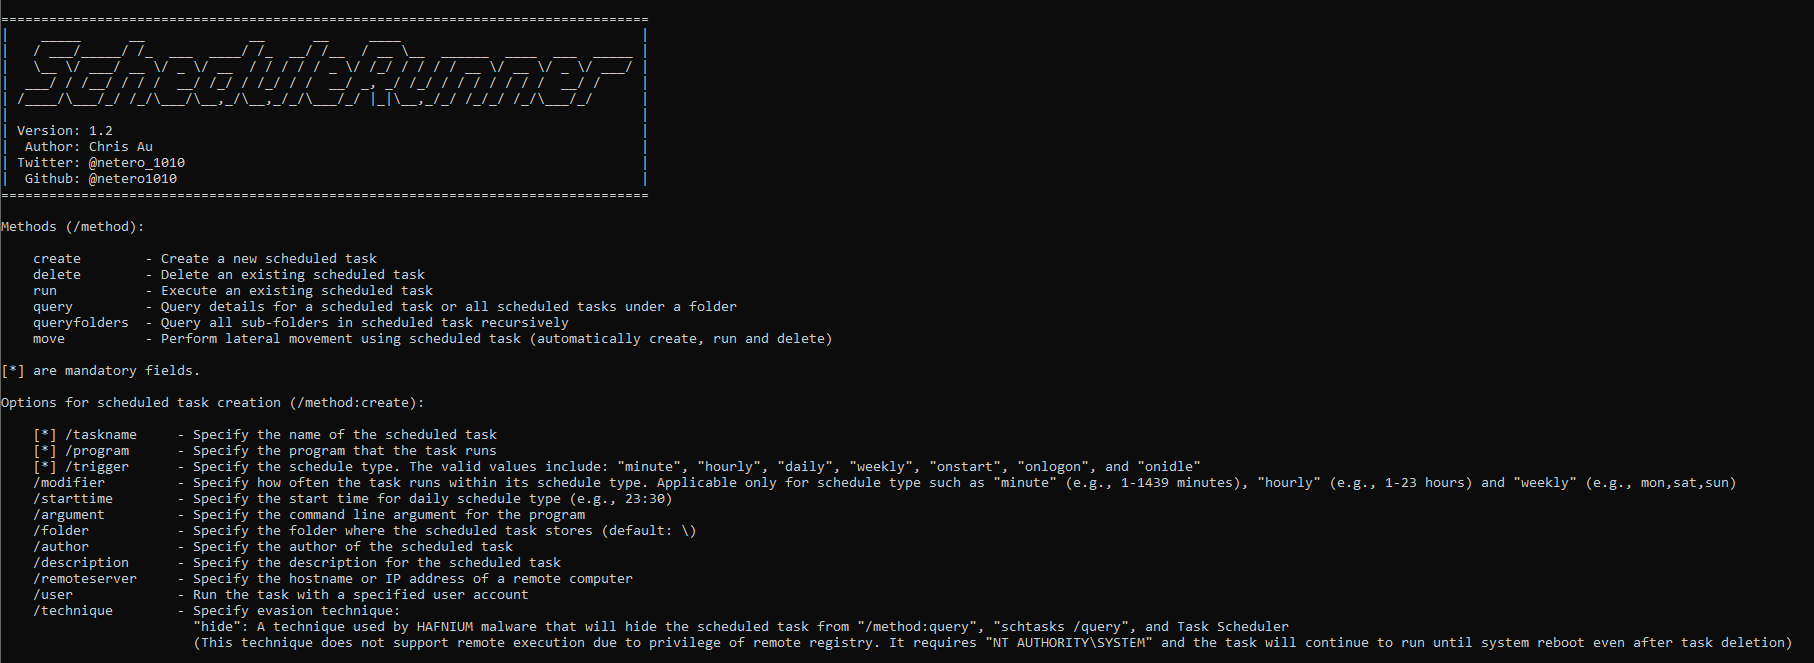 netero1010/schedulerunner
A C# tool with more flexibility to customize scheduled task for both persistence and lateral movement in red team operation
 pingport80/cve-2019-17240
This is the exploit of CVE-2019-17240.
 xaff-xaff/kernel-process-hollowing
Windows x64 kernel mode rootkit process hollowing POC.
 0xflux/vectored-exception-handling-squared
Vectored Exception Handling Squared
 h3xduck/umbra
A LKM rootkit targeting 4.x and 5.x kernel versions which opens a backdoor that can spawn a reverse shell to a remote host, launch malware and more.
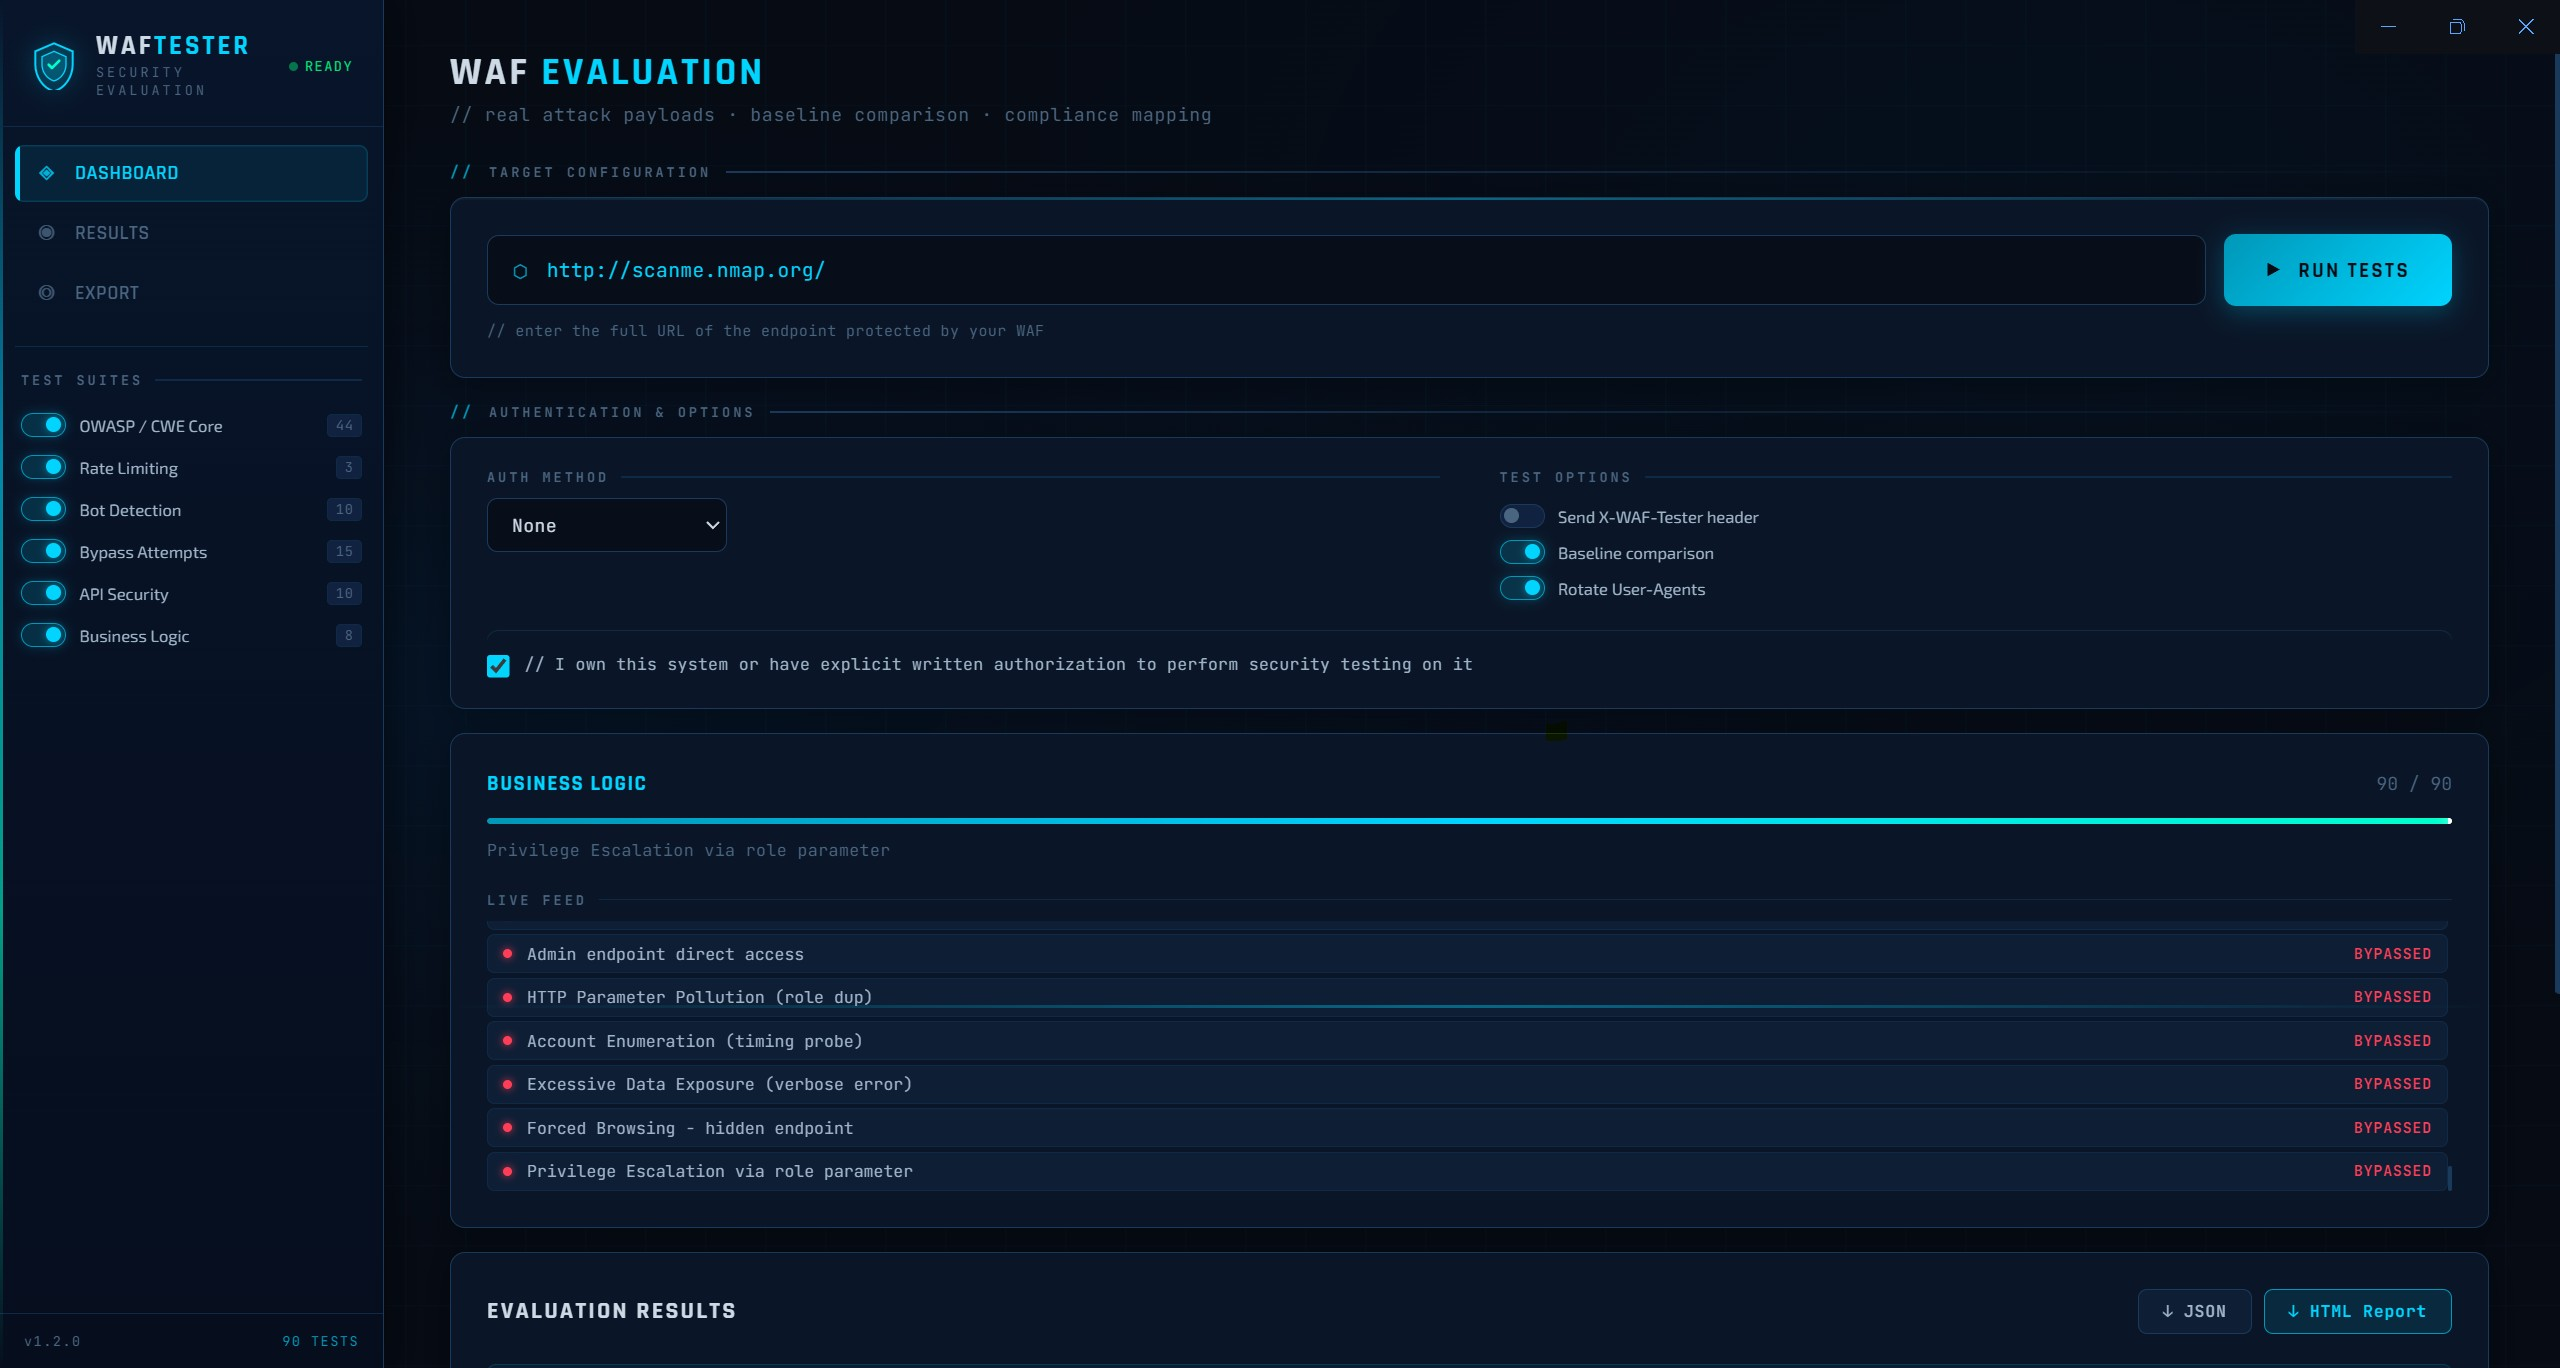 kpomin57/waf-tester
A program for testing WAF functionality
 sf0rzin/cve-2025-61155
CVE-2025-61155 — arbitrary process termination in GameDriverX64.sys (Tower of Fantasy anti-cheat). Original IDA Pro teardown, PoC, YARA, IOCs,…