
nodriver
 ultrafunkamsterdam/nodriver
Successor of Undetected-Chromedriver. Providing a blazing fast framework for web automation, webscraping, bots and any other creative ideas which are…
anti-botcaptcha-bypasscrawler+8
4.8k
ultrafunkamsterdam/nodriverSuccessor of Undetected-Chromedriver. Providing a blazing fast framework for web automation, webscraping, bots and any other creative ideas which are…
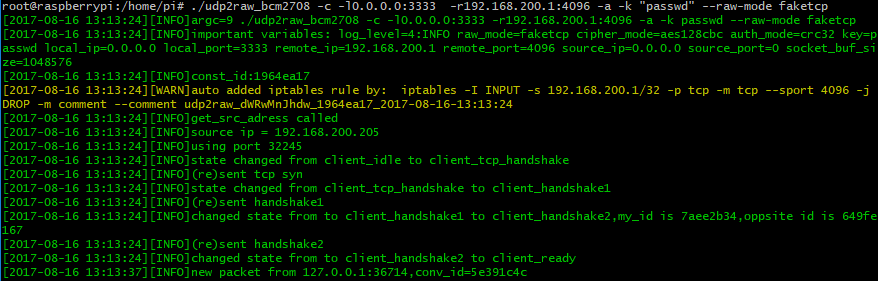 wangyu-/udp2raw
A Tunnel which Turns UDP Traffic into Encrypted UDP/FakeTCP/ICMP Traffic by using Raw Socket,helps you Bypass UDP FireWalls(or Unstable UDP…
 trustedsec/unicorn
Unicorn is a simple tool for using a PowerShell downgrade attack and inject shellcode straight into memory. Based on Matthew Graeber's powershell…
 cifertech/esp32-div
ESP32DIV is a multi-purpose wireless offensive and defensive toolkit powered by an ESP32
 dovecoteescapee/byedpiandroid
Android VPN-based local proxy that bypasses Deep Packet Inspection (DPI) and censorship by redirecting all traffic through a SOCKS5 tunnel without…
 cbeuw/cloak
A censorship circumvention tool to evade detection by authoritarian state adversaries
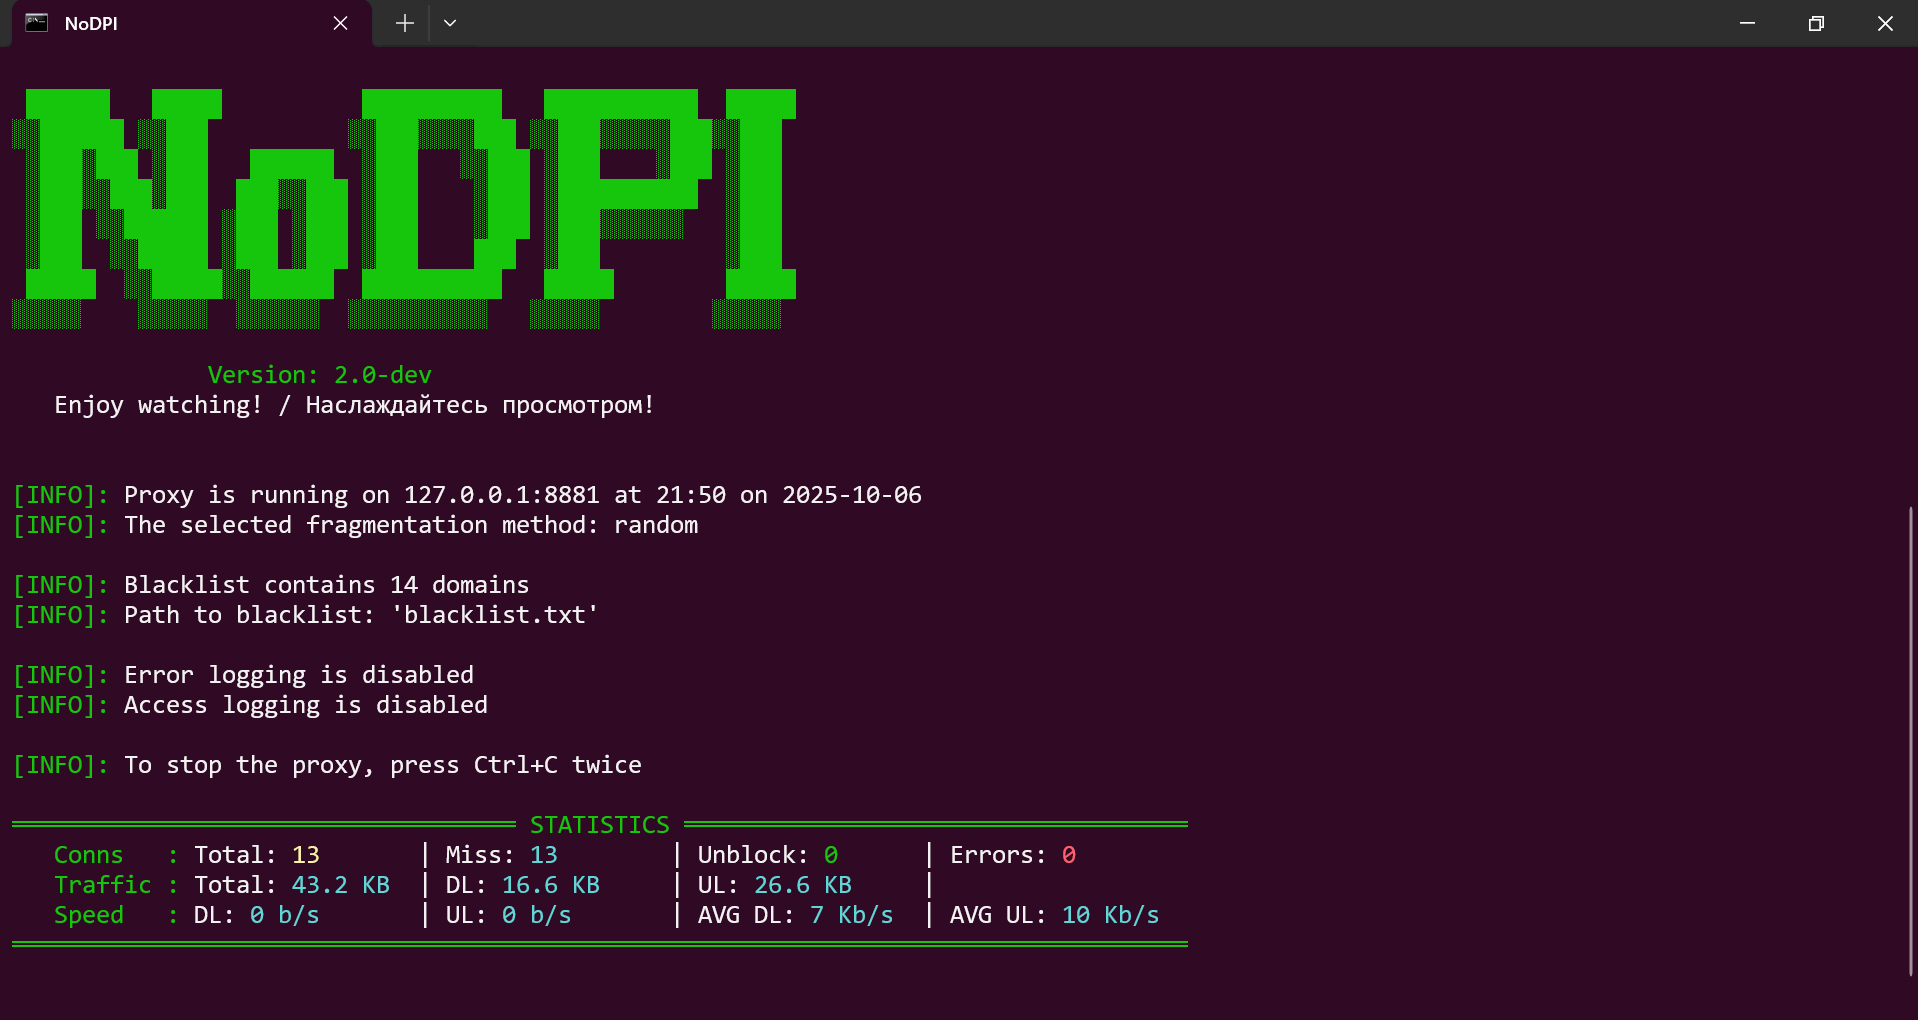 gvcoder09/nodpi
Local proxy that bypasses Deep Packet Inspection by fragmenting TLS ClientHello packets, enabling access to blocked websites without requiring…
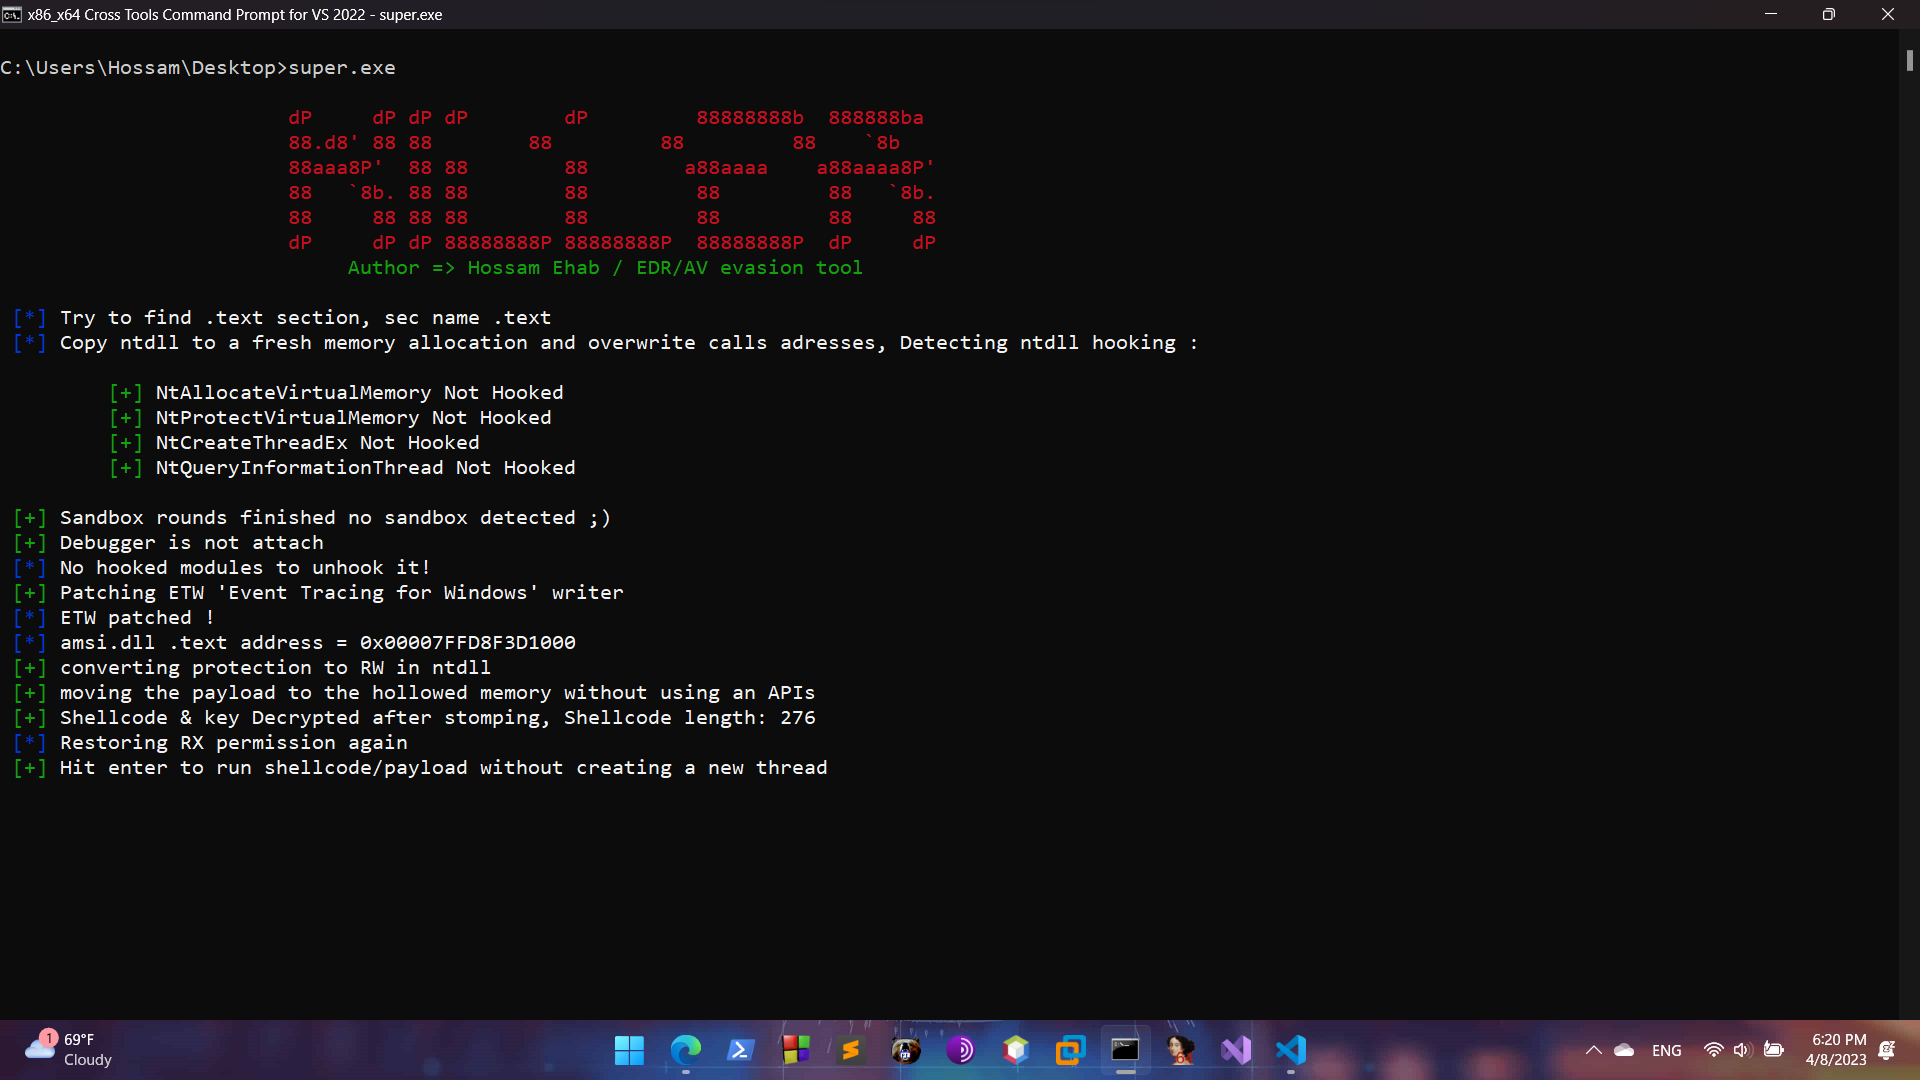 0xhossam/killer
Killer is a super simple tool designed to bypass AV/EDR security tools using various evasive techniques and used by Patchwork group.
 med0x2e/executeassembly
Load/Inject .NET assemblies by; reusing the host (spawnto) process loaded CLR AppDomainManager, Stomping Loader/.NET assembly PE DOS headers,…
 vxcrypt0r/voidgate
A technique that can be used to bypass AV/EDR memory scanners. This can be used to hide well-known and detected shellcodes (such as msfvenom) by…
 malwaretech/edr-preloader
An EDR bypass that prevents EDRs from hooking or loading DLLs into our process by hijacking the AppVerifier layer
 alirezaparsi/copg
Advanced per-app device / CPU / GPU spoofer for rooted Android — device profiles, per-app CPU models, prop & Android-ID spoofing, all driven by a…
 waelmas/frameless-bitb
A new approach to Browser In The Browser (BITB) without the use of iframes, allowing the bypass of traditional framebusters implemented by login…
 syworks/wireless-ids
Ability to detect suspicious activity such as (WEP/WPA/WPS) attack by sniffing the air for wireless packets.
 matheuzsecurity/ringreaper
Linux post-exploitation agent that uses io_uring to stealthily bypass EDR detection by avoiding traditional syscalls.
 d4rksystem/vboxcloak
A PowerShell script that attempts to help malware analysts hide their Windows VirtualBox Windows VM's from malware that may be trying to evade…
 infobyte/spoilerwall
Spoilerwall introduces a brand new concept in the field of network hardening. Avoid being scanned by spoiling movies on all your ports!
 xm0kht4r/av-edr-killer
AV/EDR processes termination by exploiting a vulnerable driver (BYOVD)