
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
12 results
legion preview
Archived

legion

GitHubabacus-group-rto/legion

Legion is an open source, easy-to-use, super-extensible and semi-automated network penetration testing tool that aids in discovery, reconnaissance…

container-securityexploitationids-ips-evasion+8
1.1k
1 year ago
matrix-rs preview
Archived

matrix-rs

GitHubmemn0ps/matrix-rs

Rusty Hypervisor - Windows Kernel Blue Pill Type-2 Hypervisor in Rust (Codename: Matrix)
dynamic-code-analysiseducationids-ips-evasion+3
3594 months ago
boopkit preview

boopkit

GitHubkrisnova/boopkit

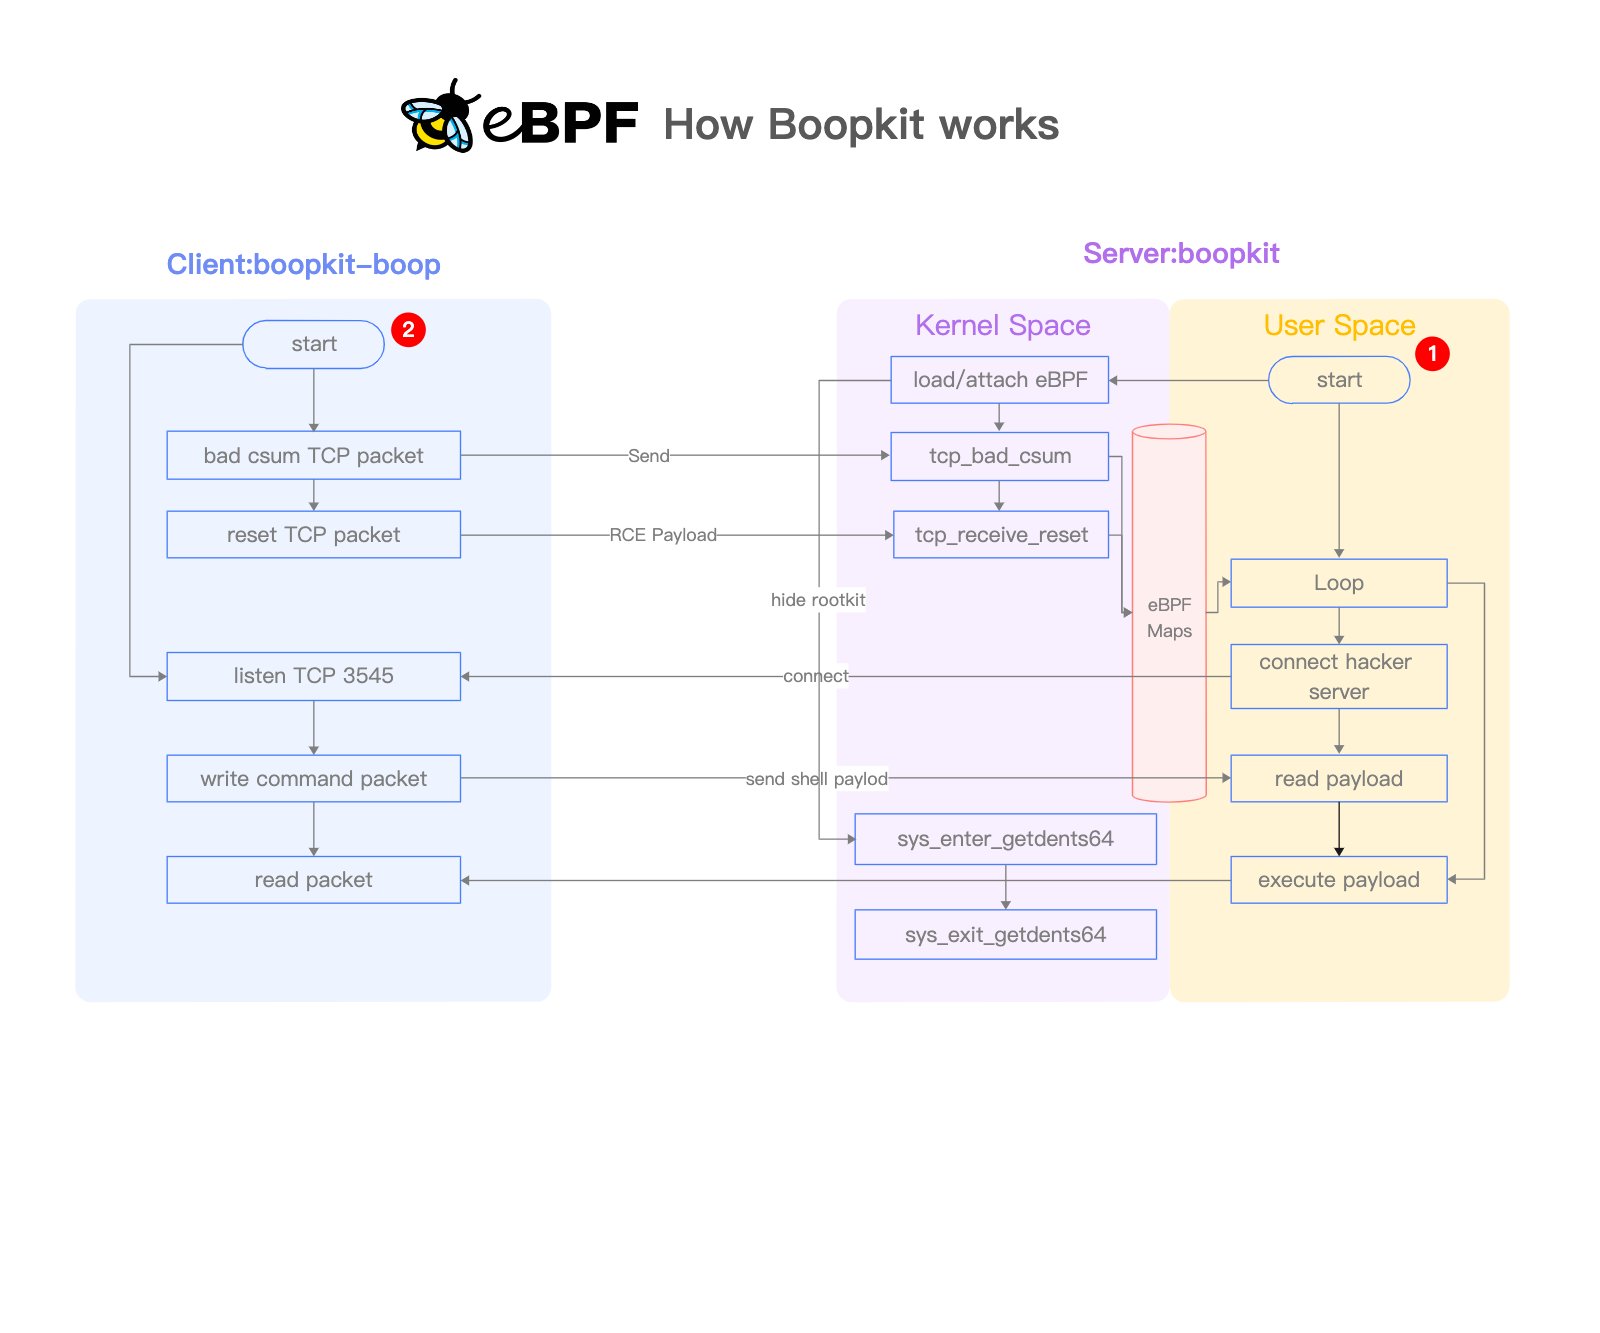
Linux eBPF backdoor over TCP. Spawn reverse shells, RCE, on prior privileged access. Less Honkin, More Tonkin.
command-and-controlexploitationids-ips-evasion+6
1.7k3 years ago
UnhookingPatch preview

UnhookingPatch

GitHubsaadahla/unhookingpatch

Bypass EDR Hooks by patching NT API stub, and resolving SSNs and syscall instructions at runtime

adversarial-attackids-ips-evasionpayload-development+2
3053 years ago
rust_syscalls preview

rust_syscalls

GitHubjanoglezcampos/rust_syscalls

Single stub direct and indirect syscalling with runtime SSN resolving for windows.
ids-ips-evasionpayload-developmentpost-exploitation+1
2383 years ago
tetragon-dirtyfrag preview

tetragon-dirtyfrag

GitHubarmircetaj/tetragon-dirtyfrag

Blocking the DirtyFrag Linux LPE chain (CVE-2026-43284 / CVE-2026-43500) at runtime with a Cilium Tetragon TracingPolicy
binary-exploitationdefensive-toolseducation+5
12 months ago
DInvoke_rs preview

DInvoke_rs

GitHubkudaes/dinvoke_rs

Dynamically invoke arbitrary unmanaged code

binary-analysisids-ips-evasionpayload-development+3
3662 months ago
obex preview

obex

GitHubdis0rder0x00/obex

Obex – Blocking unwanted DLLs in user mode

adversarial-attackids-ips-evasionpost-exploitation+1
2801 year ago
Squre preview

Squre

GitHublilify-jp/squre

🛡️ Open-source binary protection toolkit for Windows PE. Nanomite, VM protection, anti-debug, and more.

anti-botbinary-analysiscode-analysis+7
637 months ago
crypter preview

crypter

GitHubpushpenderindia/crypter

Python-based crypter that encrypts source code with AES-256 and Base64, evades VM detection via registry, process, and MAC checks, and executes…
encryption-decryption-toolsids-ips-evasionmalware-analysis
3504 years ago
Nodejs-Tracer preview

Nodejs-Tracer

GitHubcheckpointsw/nodejs-tracer

Runtime tracer for Node.js malware analysis that hooks core modules, logs calls, spoofs anti-analysis checks, and captures file writes and HTTP…
anti-botdynamic-analysis-sandboxingids-ips-evasion+3
818 months ago
Soviet preview

Soviet

GitHubmephistolist/soviet

A Runtime Crypter in C for Linux ELF binaries.

anti-botbinary-analysisencryption-decryption-tools+6
357 months ago