
Forbidden-Buster
 sn1r/forbidden-buster
A tool designed to automate various techniques in order to bypass HTTP 401 and 403 response codes and gain access to unauthorized areas in the…
fuzzingids-ips-evasionpenetration-testing+2
254
sn1r/forbidden-busterA tool designed to automate various techniques in order to bypass HTTP 401 and 403 response codes and gain access to unauthorized areas in the…
 stvemillertime/absolutely-positively-not-hacking-back-with-pcap
Streaming Unexpected Network Byte Sequences with High Probability of Blue Screening or Otherwise Crashing Attacker Command-and-Control Nodes
 maldev-academy/christmas
PoC demonstrating a multi process injection chain aimed at remotely executing shellcode
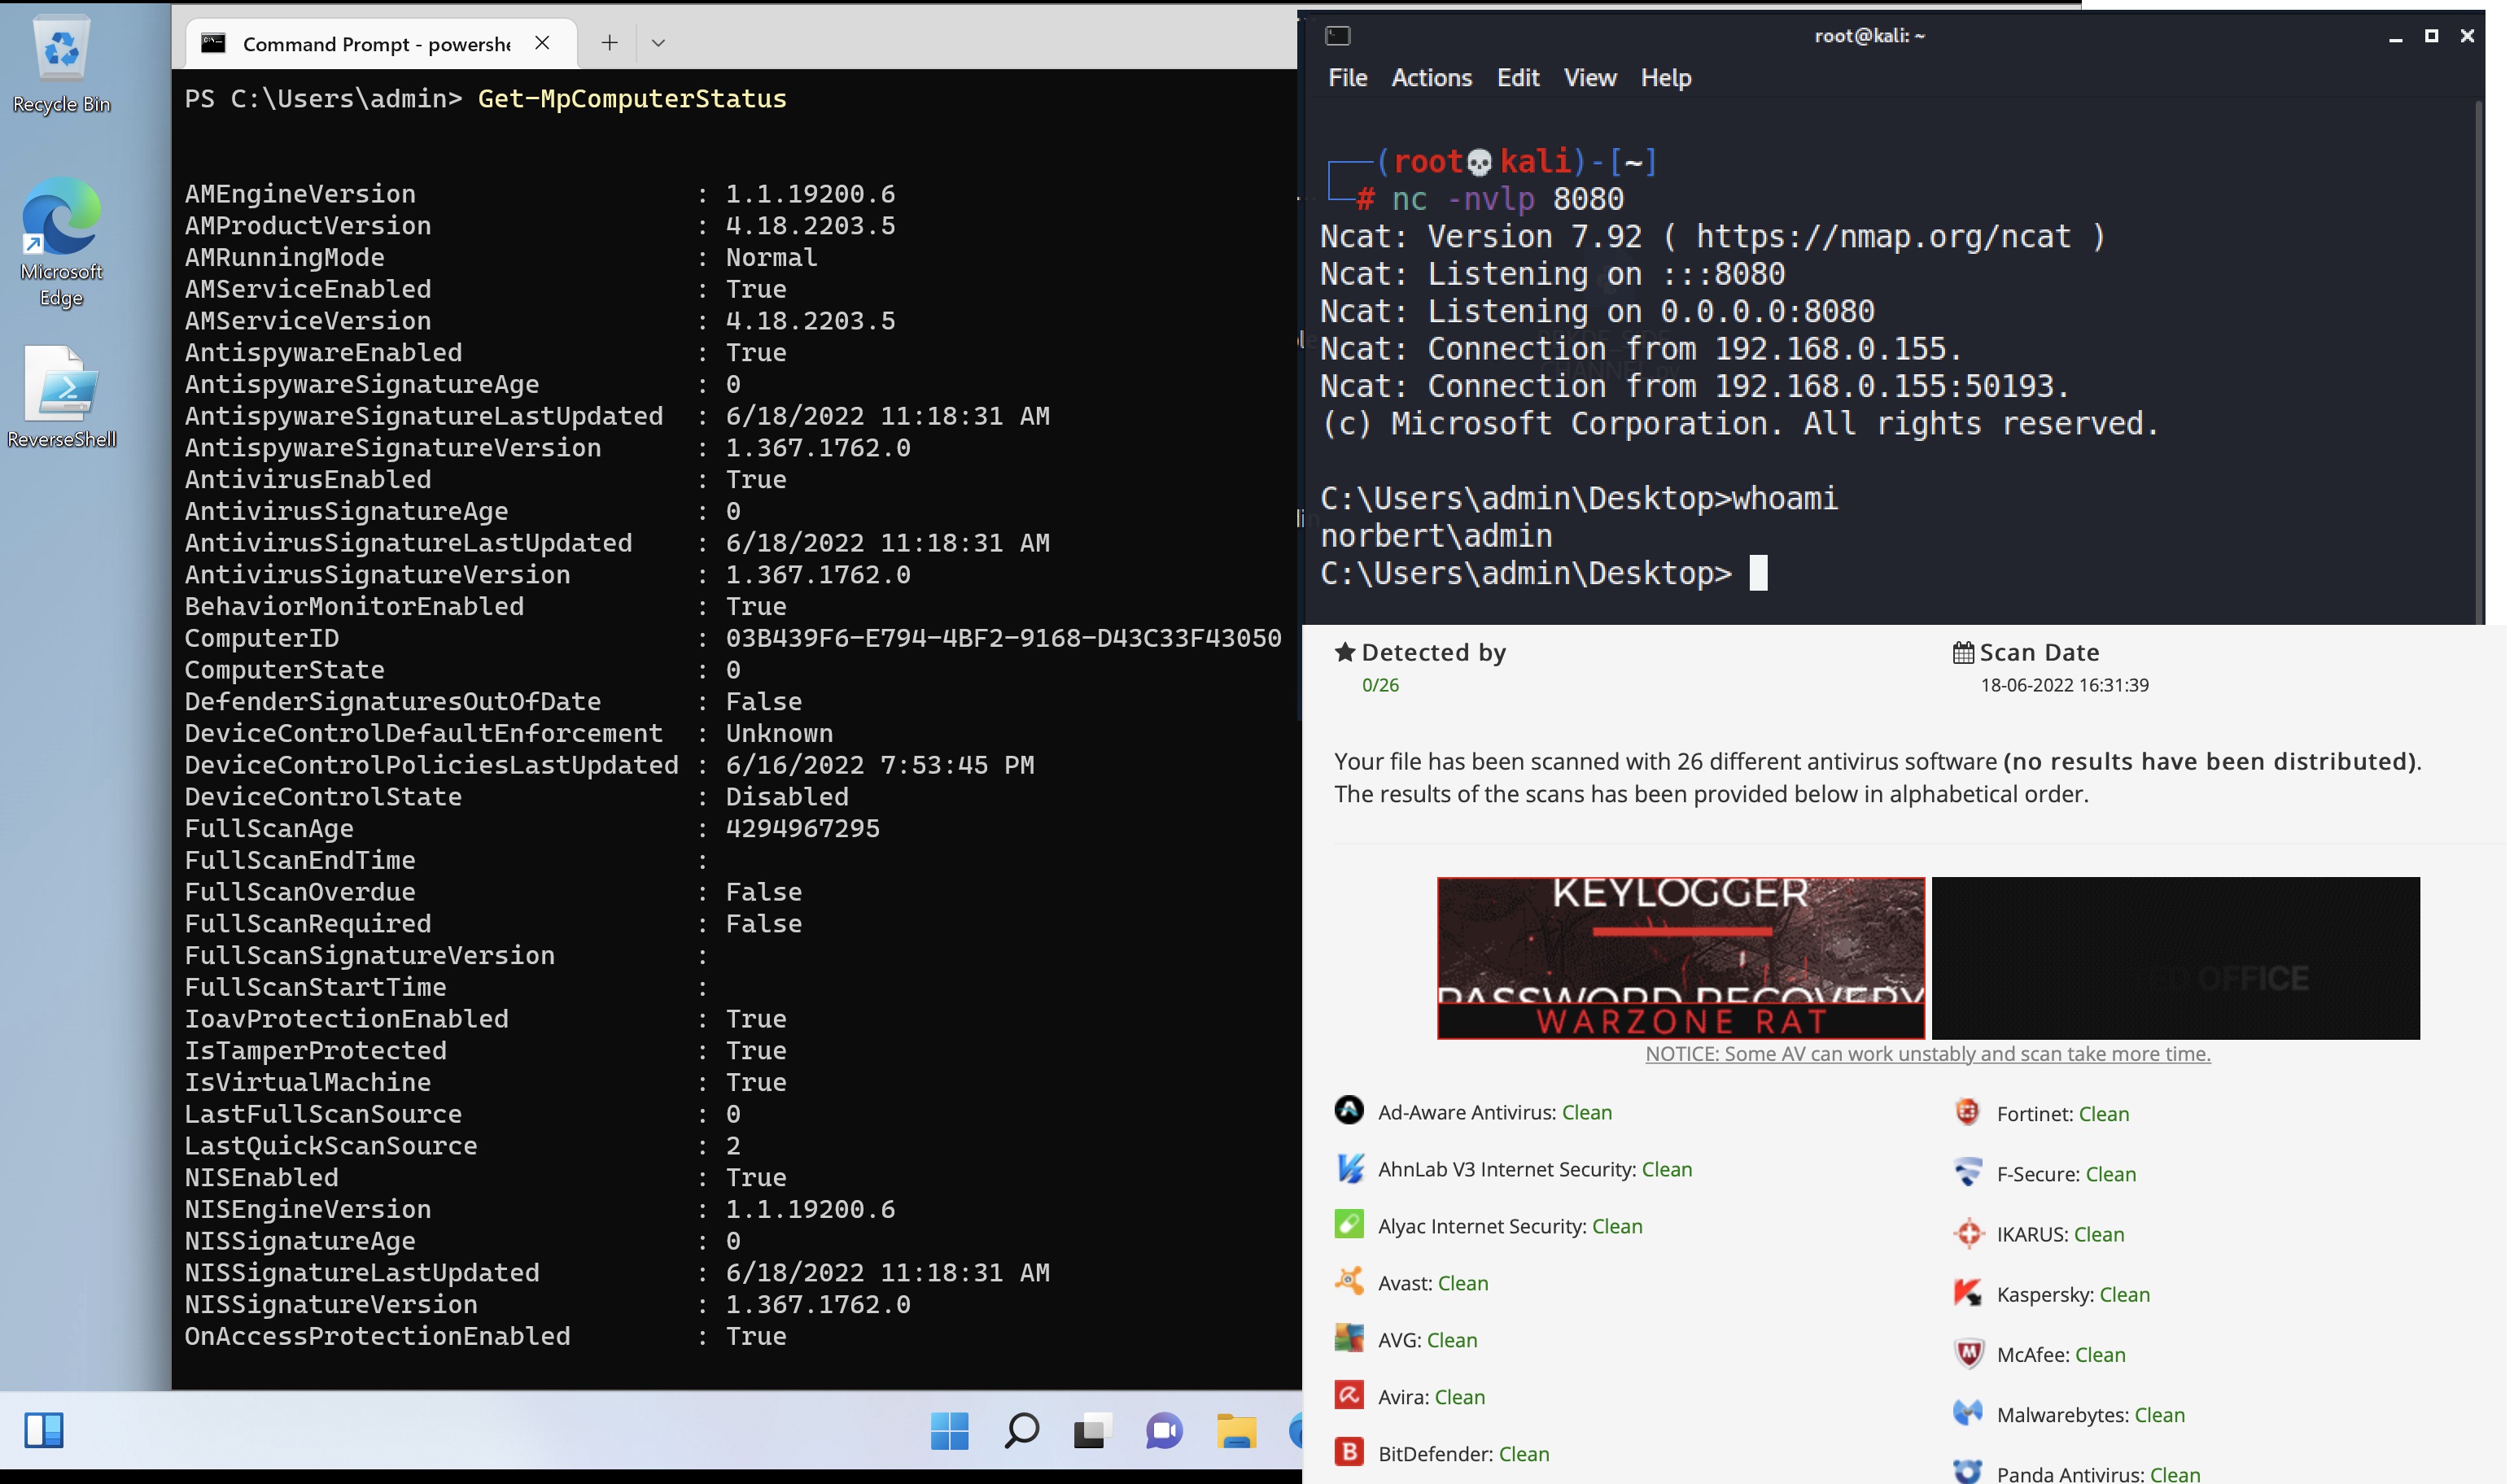 tihanyin/pssw100avb
A list of useful Powershell scripts with 100% AV bypass (At the time of publication).
 b3rt1ng/koi
Multi-session reverse shell handler with PTY upgrade, post-exploitation modules, Layer 3 tunneling, payload obfuscation for EDR evasion, session…
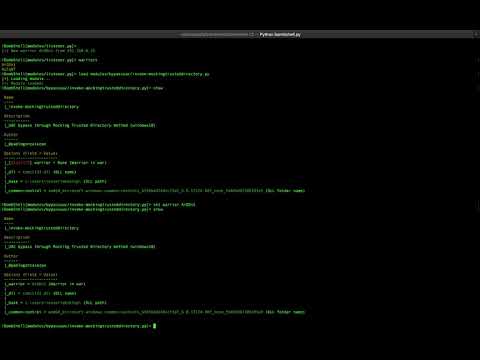 telefonica/ibombshell
Tool to deploy a post-exploitation prompt at any time
 trustedsec/unicorn
Unicorn is a simple tool for using a PowerShell downgrade attack and inject shellcode straight into memory. Based on Matthew Graeber's powershell…
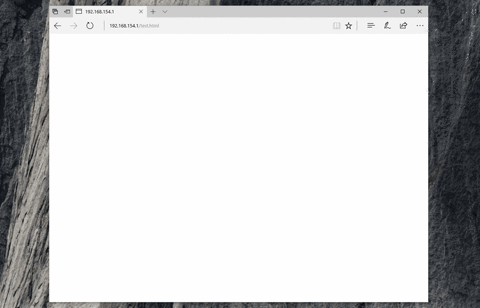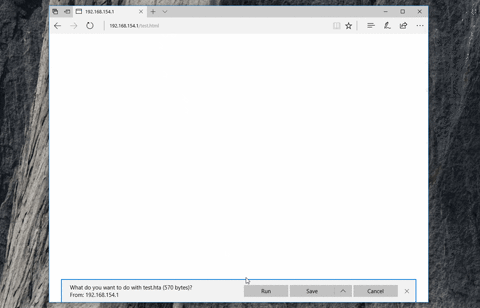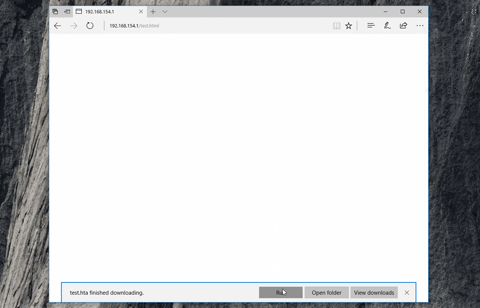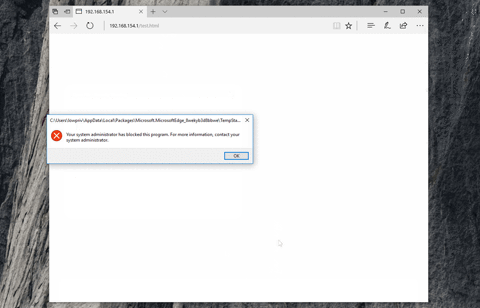 nccgroup/demiguise
HTA encryption tool for RedTeams
 beetlechunks/redsails
RedSails is a Python based post-exploitation project aimed at bypassing host based security monitoring and logging. DerbyCon 2017 Talk:…
 toperaproject/topera
IPv6 analysis tool: the other side
 ianxtianxt/tor-ip-changer
Simple shell script to automatically request new Tor identity at configurable intervals for IP rotation.
 d35ha/callobfuscator
Obfuscate specific windows apis with different apis
 appneta/tcpreplay
Edit and replay captured network traffic at arbitrary speeds — a suite of pcap tools for *NIX and Windows.
 nccgroup/phantap
Phantom Tap (PhanTap) - an ‘invisible’ network tap aimed at red teams
 d4rksystem/vboxcloak
A PowerShell script that attempts to help malware analysts hide their Windows VirtualBox Windows VM's from malware that may be trying to evade…
 mgeeky/stracciatella
OpSec-safe Powershell runspace from within C# (aka SharpPick) with AMSI, Constrained Language Mode and Script Block Logging disabled at startup
 saadahla/d1rkldr
Shellcode Loader with Indirect Dynamic syscall Implementation , shellcode in MAC format, API resolving from PEB, Syscall calll and syscall…
 saadahla/unhookingpatch
Bypass EDR Hooks by patching NT API stub, and resolving SSNs and syscall instructions at runtime