

Archived
Lime-RAT
 nyan-x-cat/lime-rat
LimeRAT | Simple, yet powerful remote administration tool for Windows (RAT)
command-and-controlcryptographydata-exfiltration+7
1.1k
 chaelsoo/nimcrypt
Nim-based encryption tool for obfuscating shellcode and payloads for evading Windows Defender.
 droe/sslsplit
Transparent man-in-the-middle proxy that terminates SSL/TLS connections, forges certificates on-the-fly, and logs decrypted traffic for network…
 emptymonkey/revsh
A reverse shell with terminal support, data tunneling, and advanced pivoting capabilities.
 kvesel/zipbrk
Zip file format fuzzer and multi-tool.
 saadahla/shellcode-hide
This repo contains : simple shellcode Loader , Encoders (base64 - custom - UUID - IPv4 - MAC), Encryptors (AES), Fileless Loader (Winhttp, socket)
 cbeuw/cloak
A censorship circumvention tool to evade detection by authoritarian state adversaries
 taherio/redi
Automated script for setting up CobaltStrike redirectors (nginx reverse proxy, letsencrypt)
 chaelsoo/hollow
A shellcode loader generator with support for multiple injection techniques, built for red team engagements.
 susmdt/effective-waffle
yet another sleep encryption thing. also used the default github repo name for this one.
 mephistolist/soviet
A Runtime Crypter in C for Linux ELF binaries.
 x3r0day/fud-c2-framework
A fileless reverse shell and C2 framework leveraging direct syscalls, proxy tunneling, and ChaCha20 encryption for AV evasion.
 hackplayers/salsa-tools
Salsa Tools - ShellReverse TCP/UDP/ICMP/DNS/SSL/BINDTCP/Shellcode/SILENTTRINITY and AV bypass, AMSI patched
 gellin/bantam
A PHP backdoor management and generation tool/C2 featuring end to end encrypted payload streaming designed to bypass WAF, IDS, SIEM systems.
 iamsopotatoe-coder/tinyload
Open source Windows x64 PE packer and crypter. Compresses and encrypts executables with a custom virtual machine into a self extracting stub.
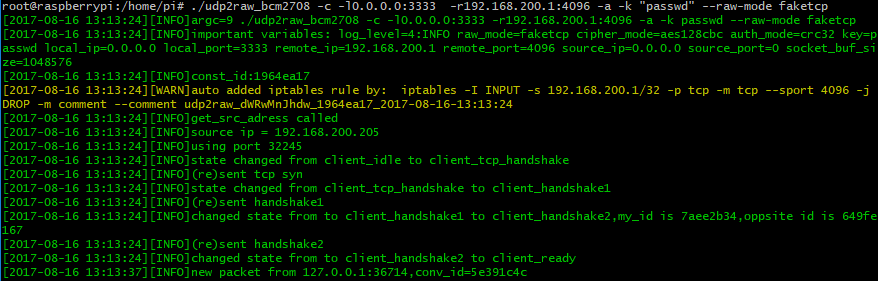 wangyu-/udp2raw
A Tunnel which Turns UDP Traffic into Encrypted UDP/FakeTCP/ICMP Traffic by using Raw Socket,helps you Bypass UDP FireWalls(or Unstable UDP…
 x011/smtp-tunnel-proxy
A high-speed covert tunnel that disguises TCP traffic as SMTP email communication to bypass Deep Packet Inspection (DPI) firewalls.
 egebalci/amber
Reflective PE packer.