pipelock
 luckypipewrench/pipelock
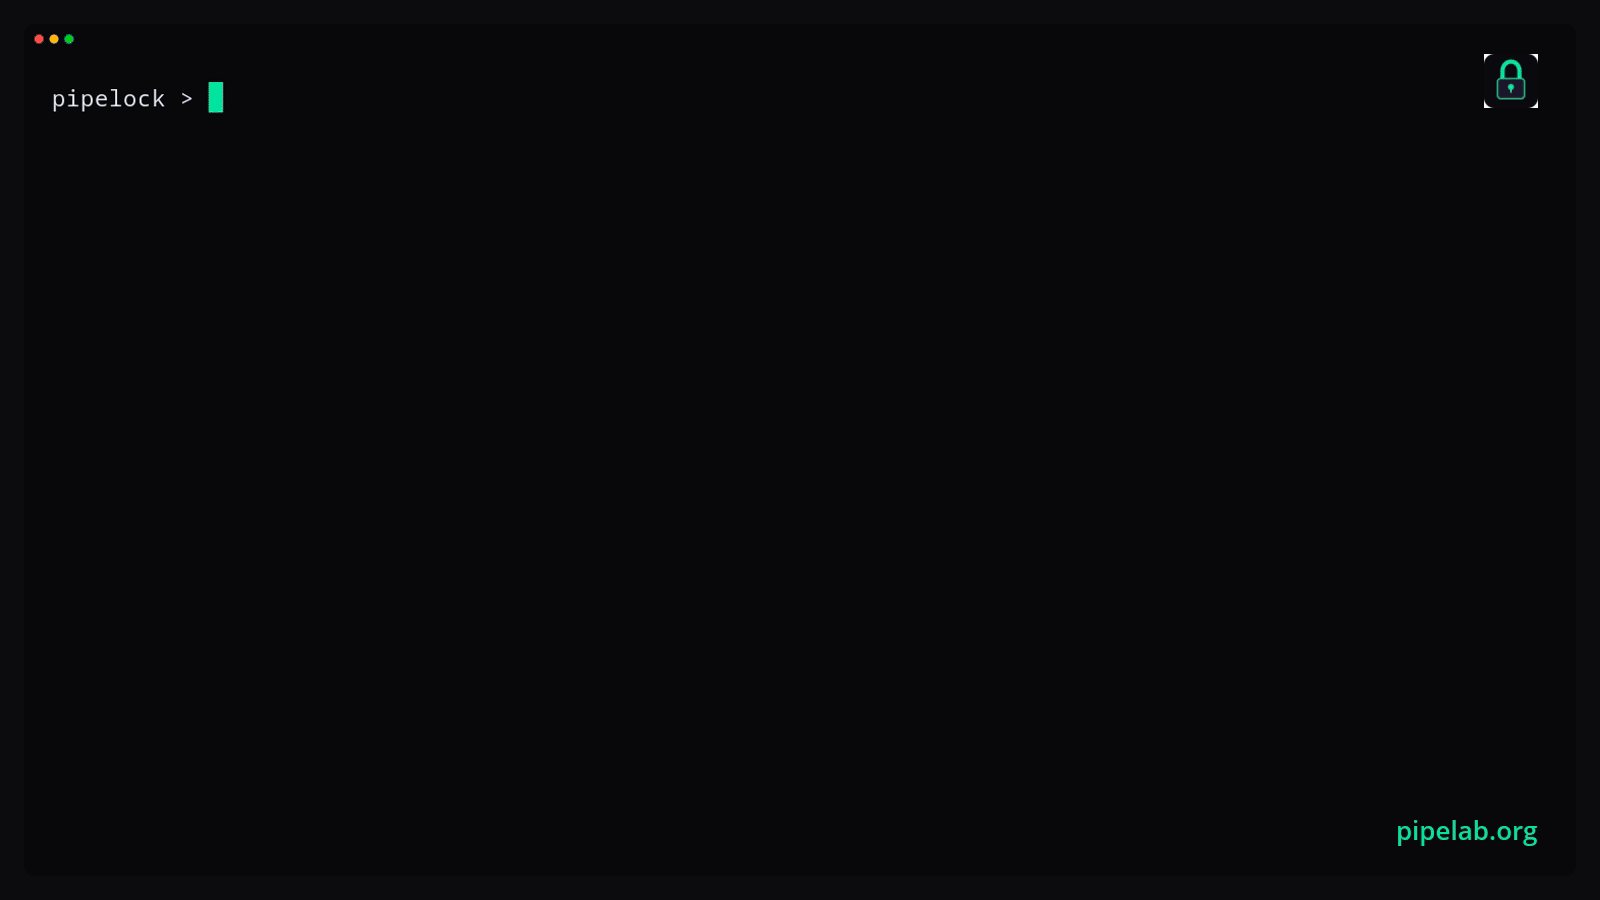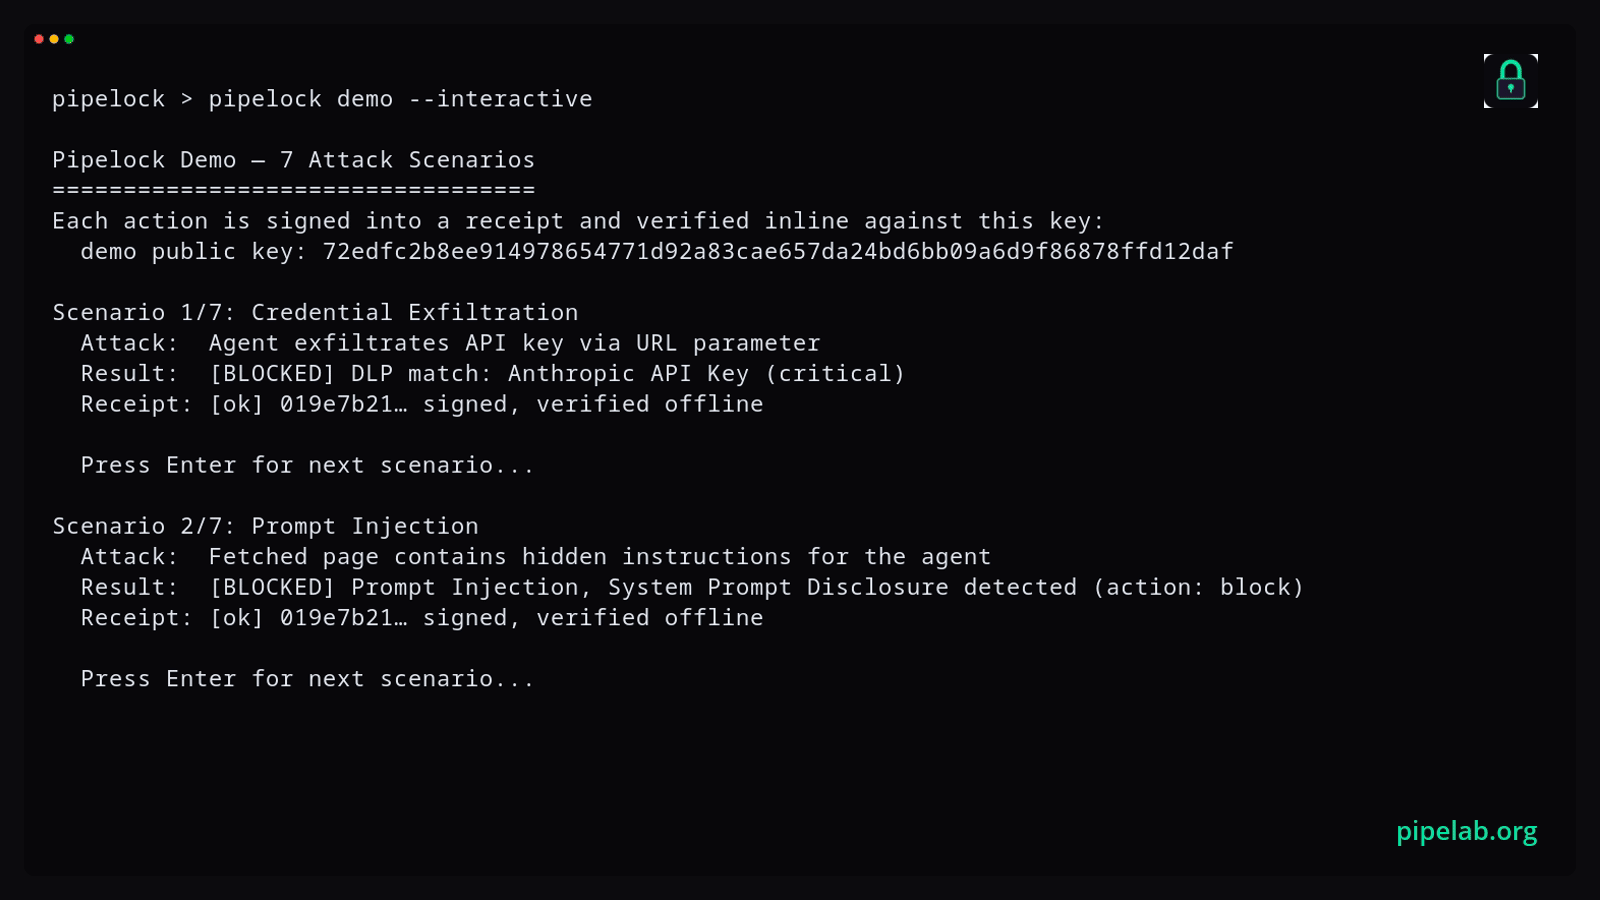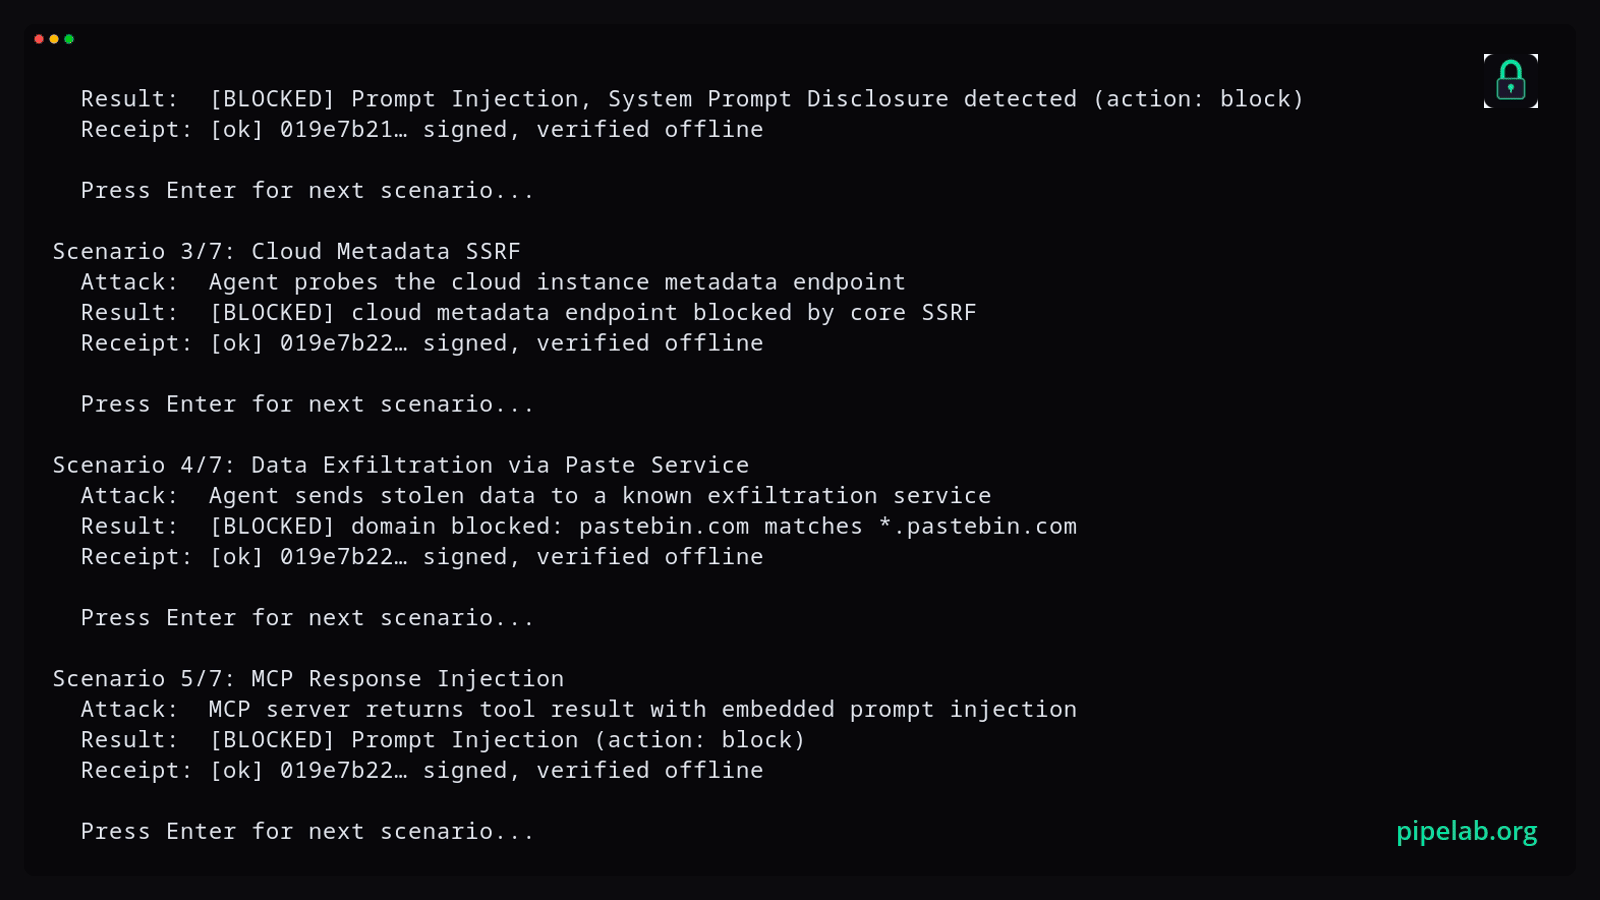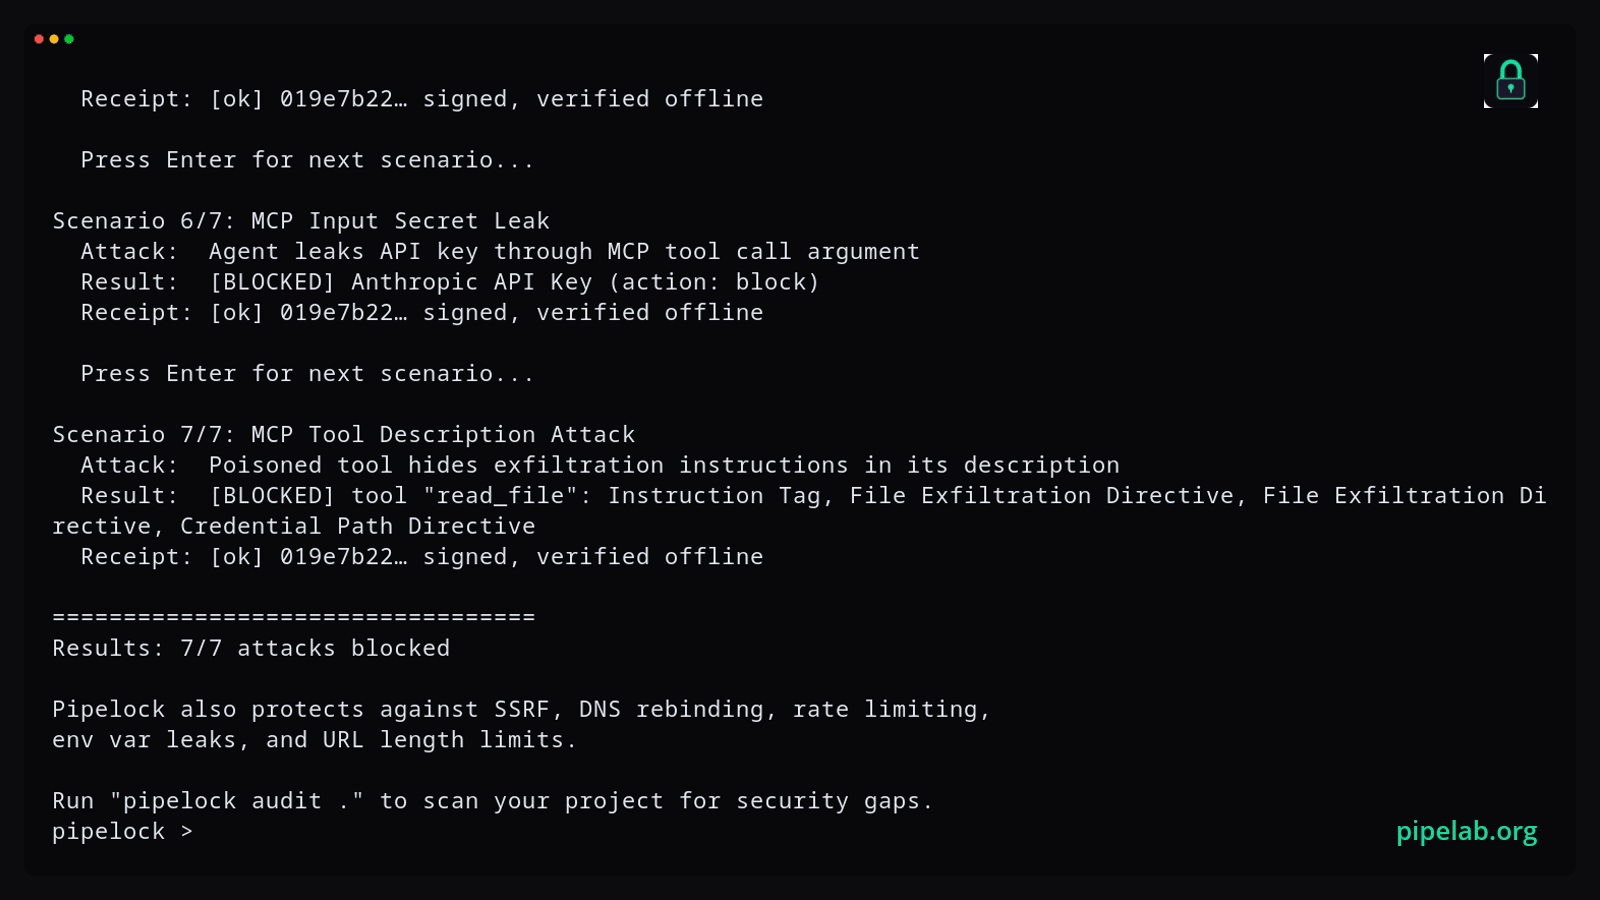
Open-source AI agent firewall that scans HTTP, MCP, A2A, and WebSocket traffic for exfiltration, SSRF, and prompt injection, emitting verifiable…
ai-securityapi-securitycloud-security+8
911
luckypipewrench/pipelockOpen-source AI agent firewall that scans HTTP, MCP, A2A, and WebSocket traffic for exfiltration, SSRF, and prompt injection, emitting verifiable…
 bishopfox/sliver
Adversary Emulation Framework
 eshlomo1/cloudsec
Master the art of cloud exploitation. A specialized resource for offensive security researchers and red teamers focused on weaponizing…

 bc-security/empire
Empire is a post-exploitation and adversary emulation framework that is used to aid Red Teams and Penetration Testers.
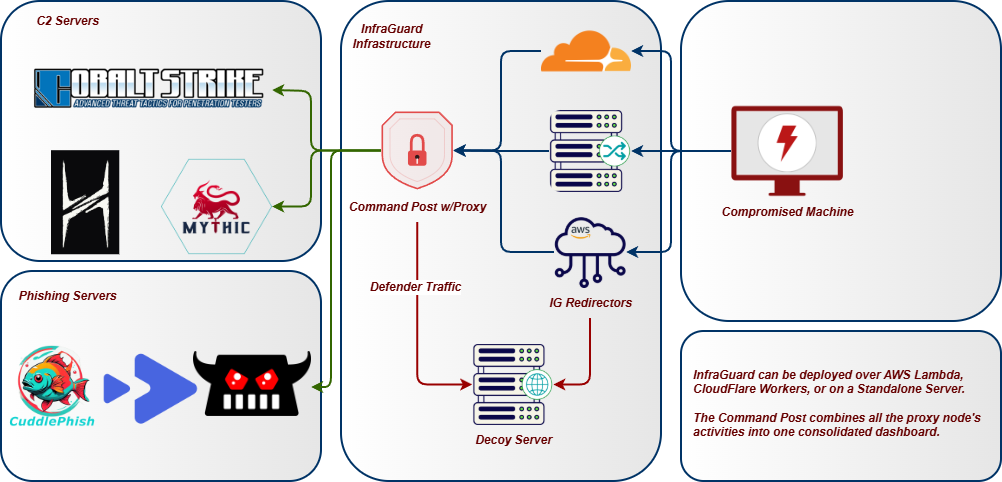 whispergate/infraguard
InfraGuard is a Command & Control Redirection Proxy and Manager which protects your Red Team Infrastructure against threat attribution
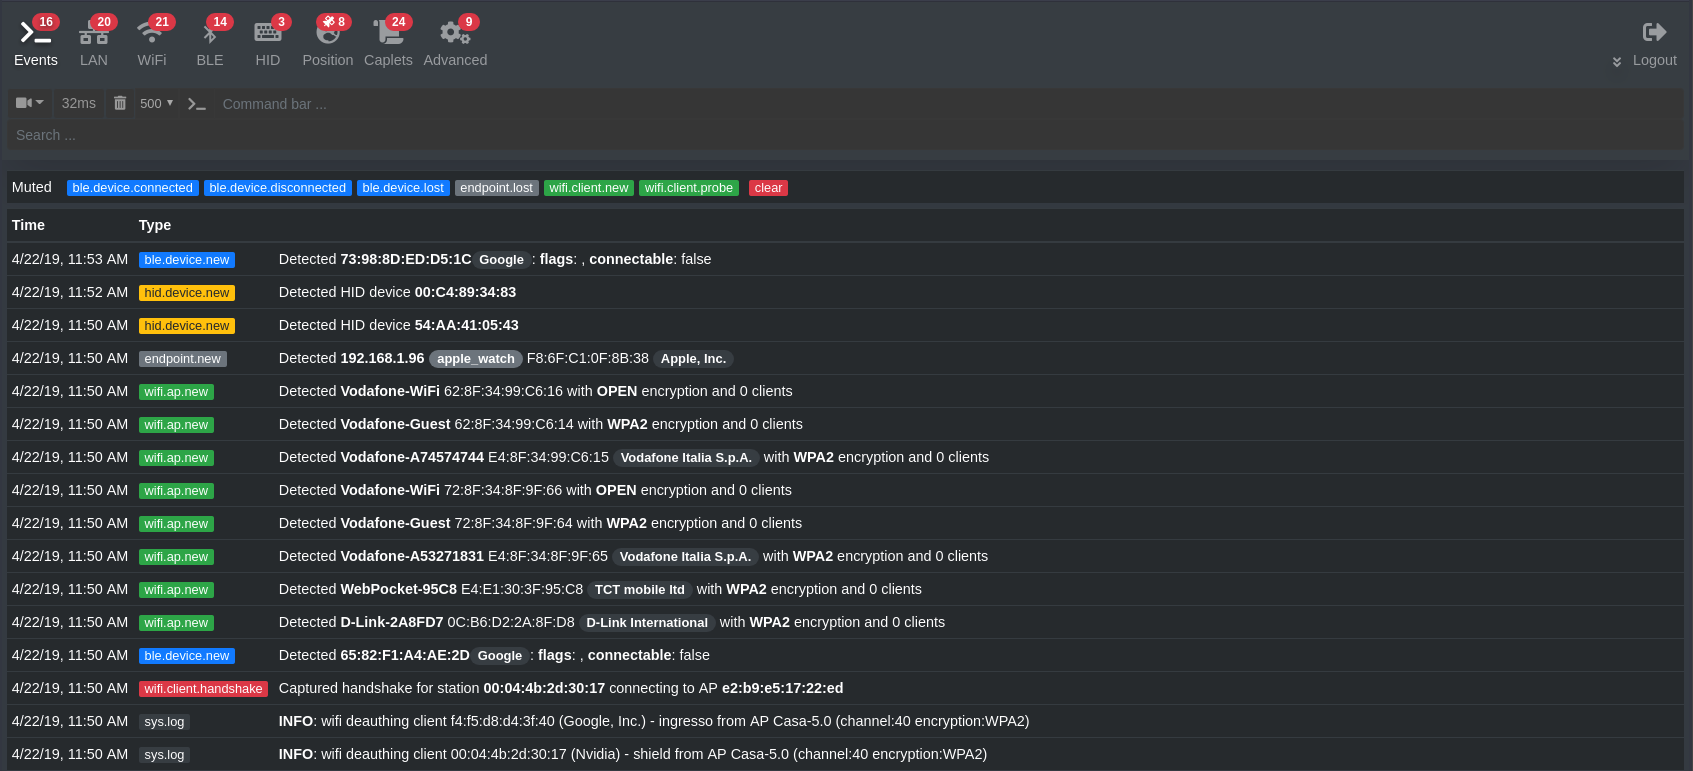 bettercap/bettercap
The Swiss Army knife for 802.11, BLE, HID, CAN-bus, IPv4 and IPv6 networks reconnaissance and MITM attacks.
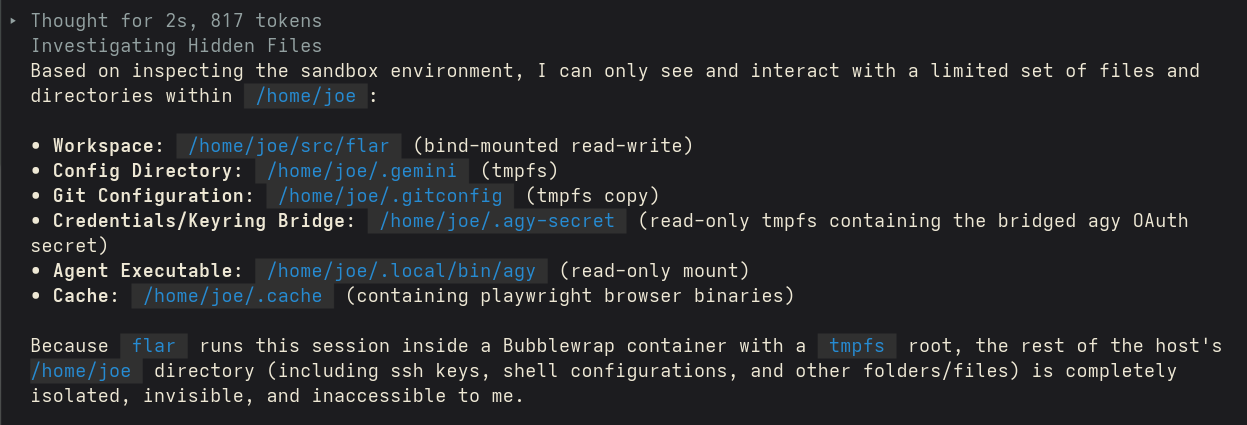 swelljoe/flar
Lightweight CLI tool that runs AI coding agents inside isolated Bubblewrap sandboxes with strict filesystem, network, and credential isolation to…
 garagehq/nightcrawler
Local AI powered red teamer on a phone
 0xdea/blindsight
Red teaming tool to dump LSASS memory, bypassing basic countermeasures.
 d00movenok/bounceback
↕️🤫 Stealth redirector for your red team operation security
 chaelsoo/hollow
A shellcode loader generator with support for multiple injection techniques, built for red team engagements.
 c0oki3s/veilgate
Asymmetric defense against adversarial AI agents. VeilGate evaluates each incoming request, redirects suspected agents into a per-IP-consistent…
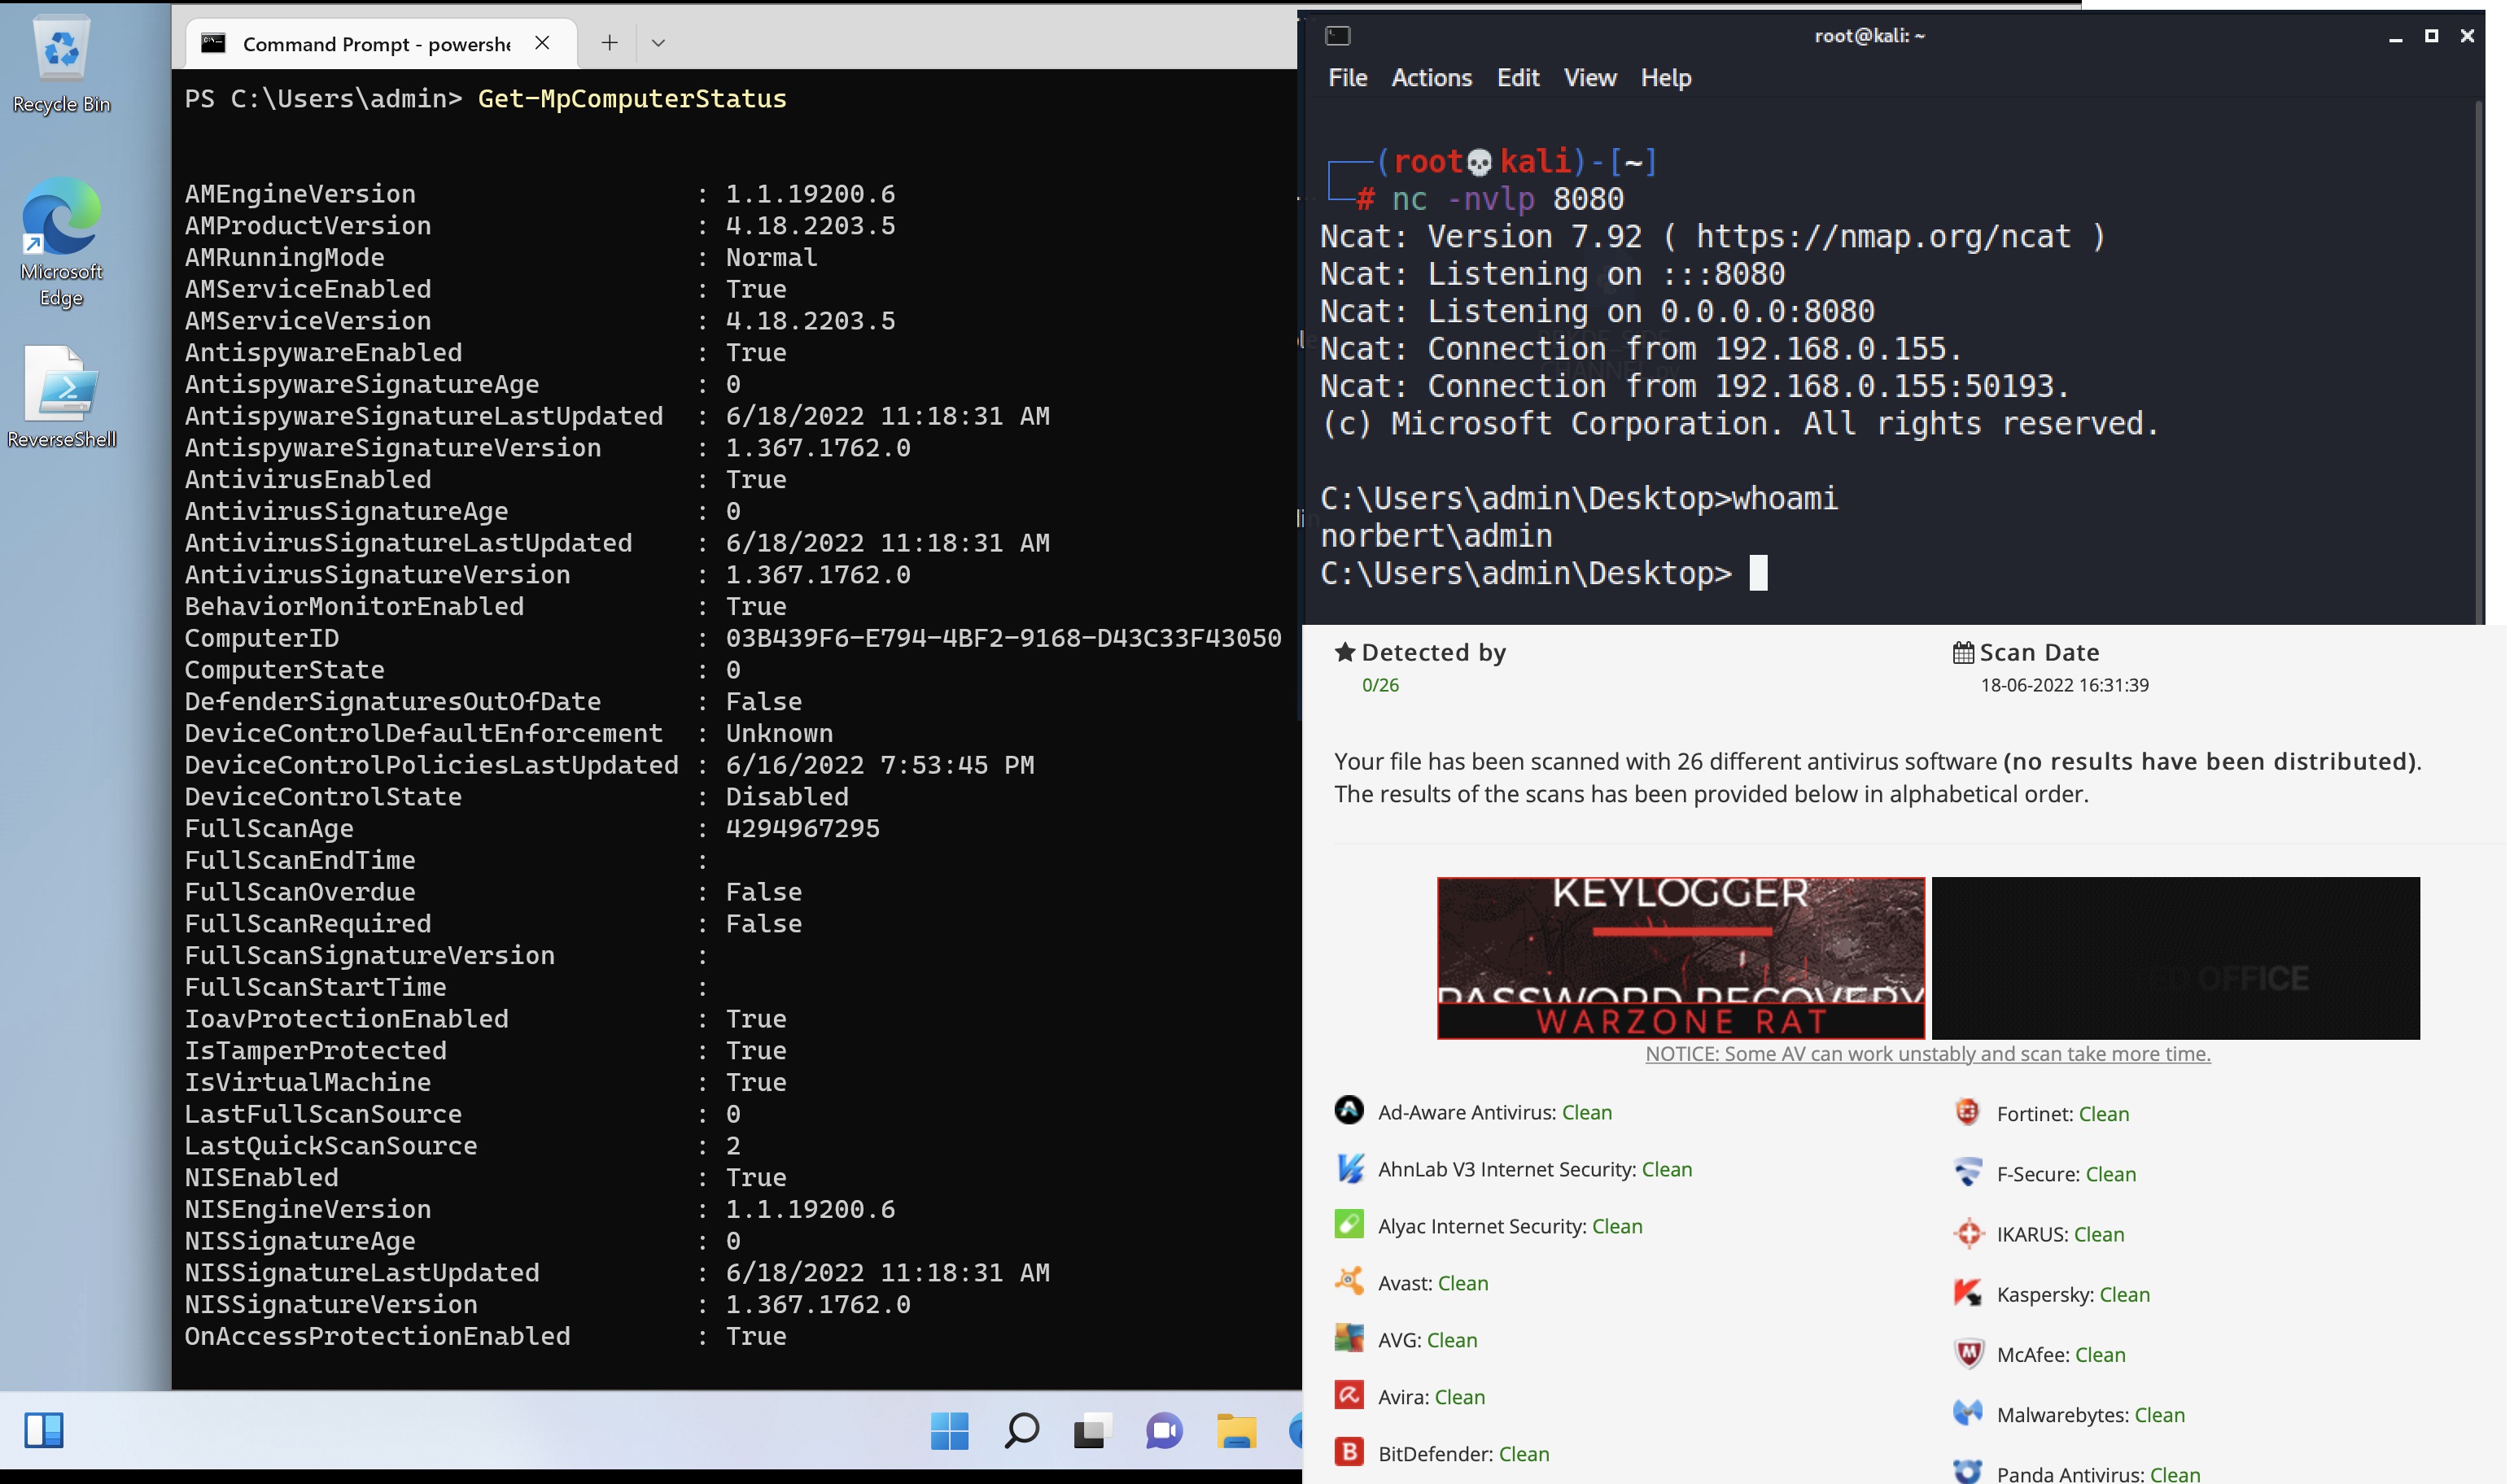 tihanyin/pssw100avb
A list of useful Powershell scripts with 100% AV bypass (At the time of publication).
 twosevenonet/edr-redir
Redirects EDR working folders using a Bind Filter (bindflt.sys) to bypass endpoint detection, corrupt EDR services, or replace with…
 undeadsec/socialfish
Modern dynamic phishing toolkit for authorized red team exercises. Clones login pages, captures credentials, cookies, and 2FA codes with a live…
 mr-un1k0d3r/edrs
Red team tool for EDR evasion: dynamically resolves syscall IDs, patches ntdll stubs, unhooks IAT hooks, and lists hooked APIs from major EDR vendors.