Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
41 results
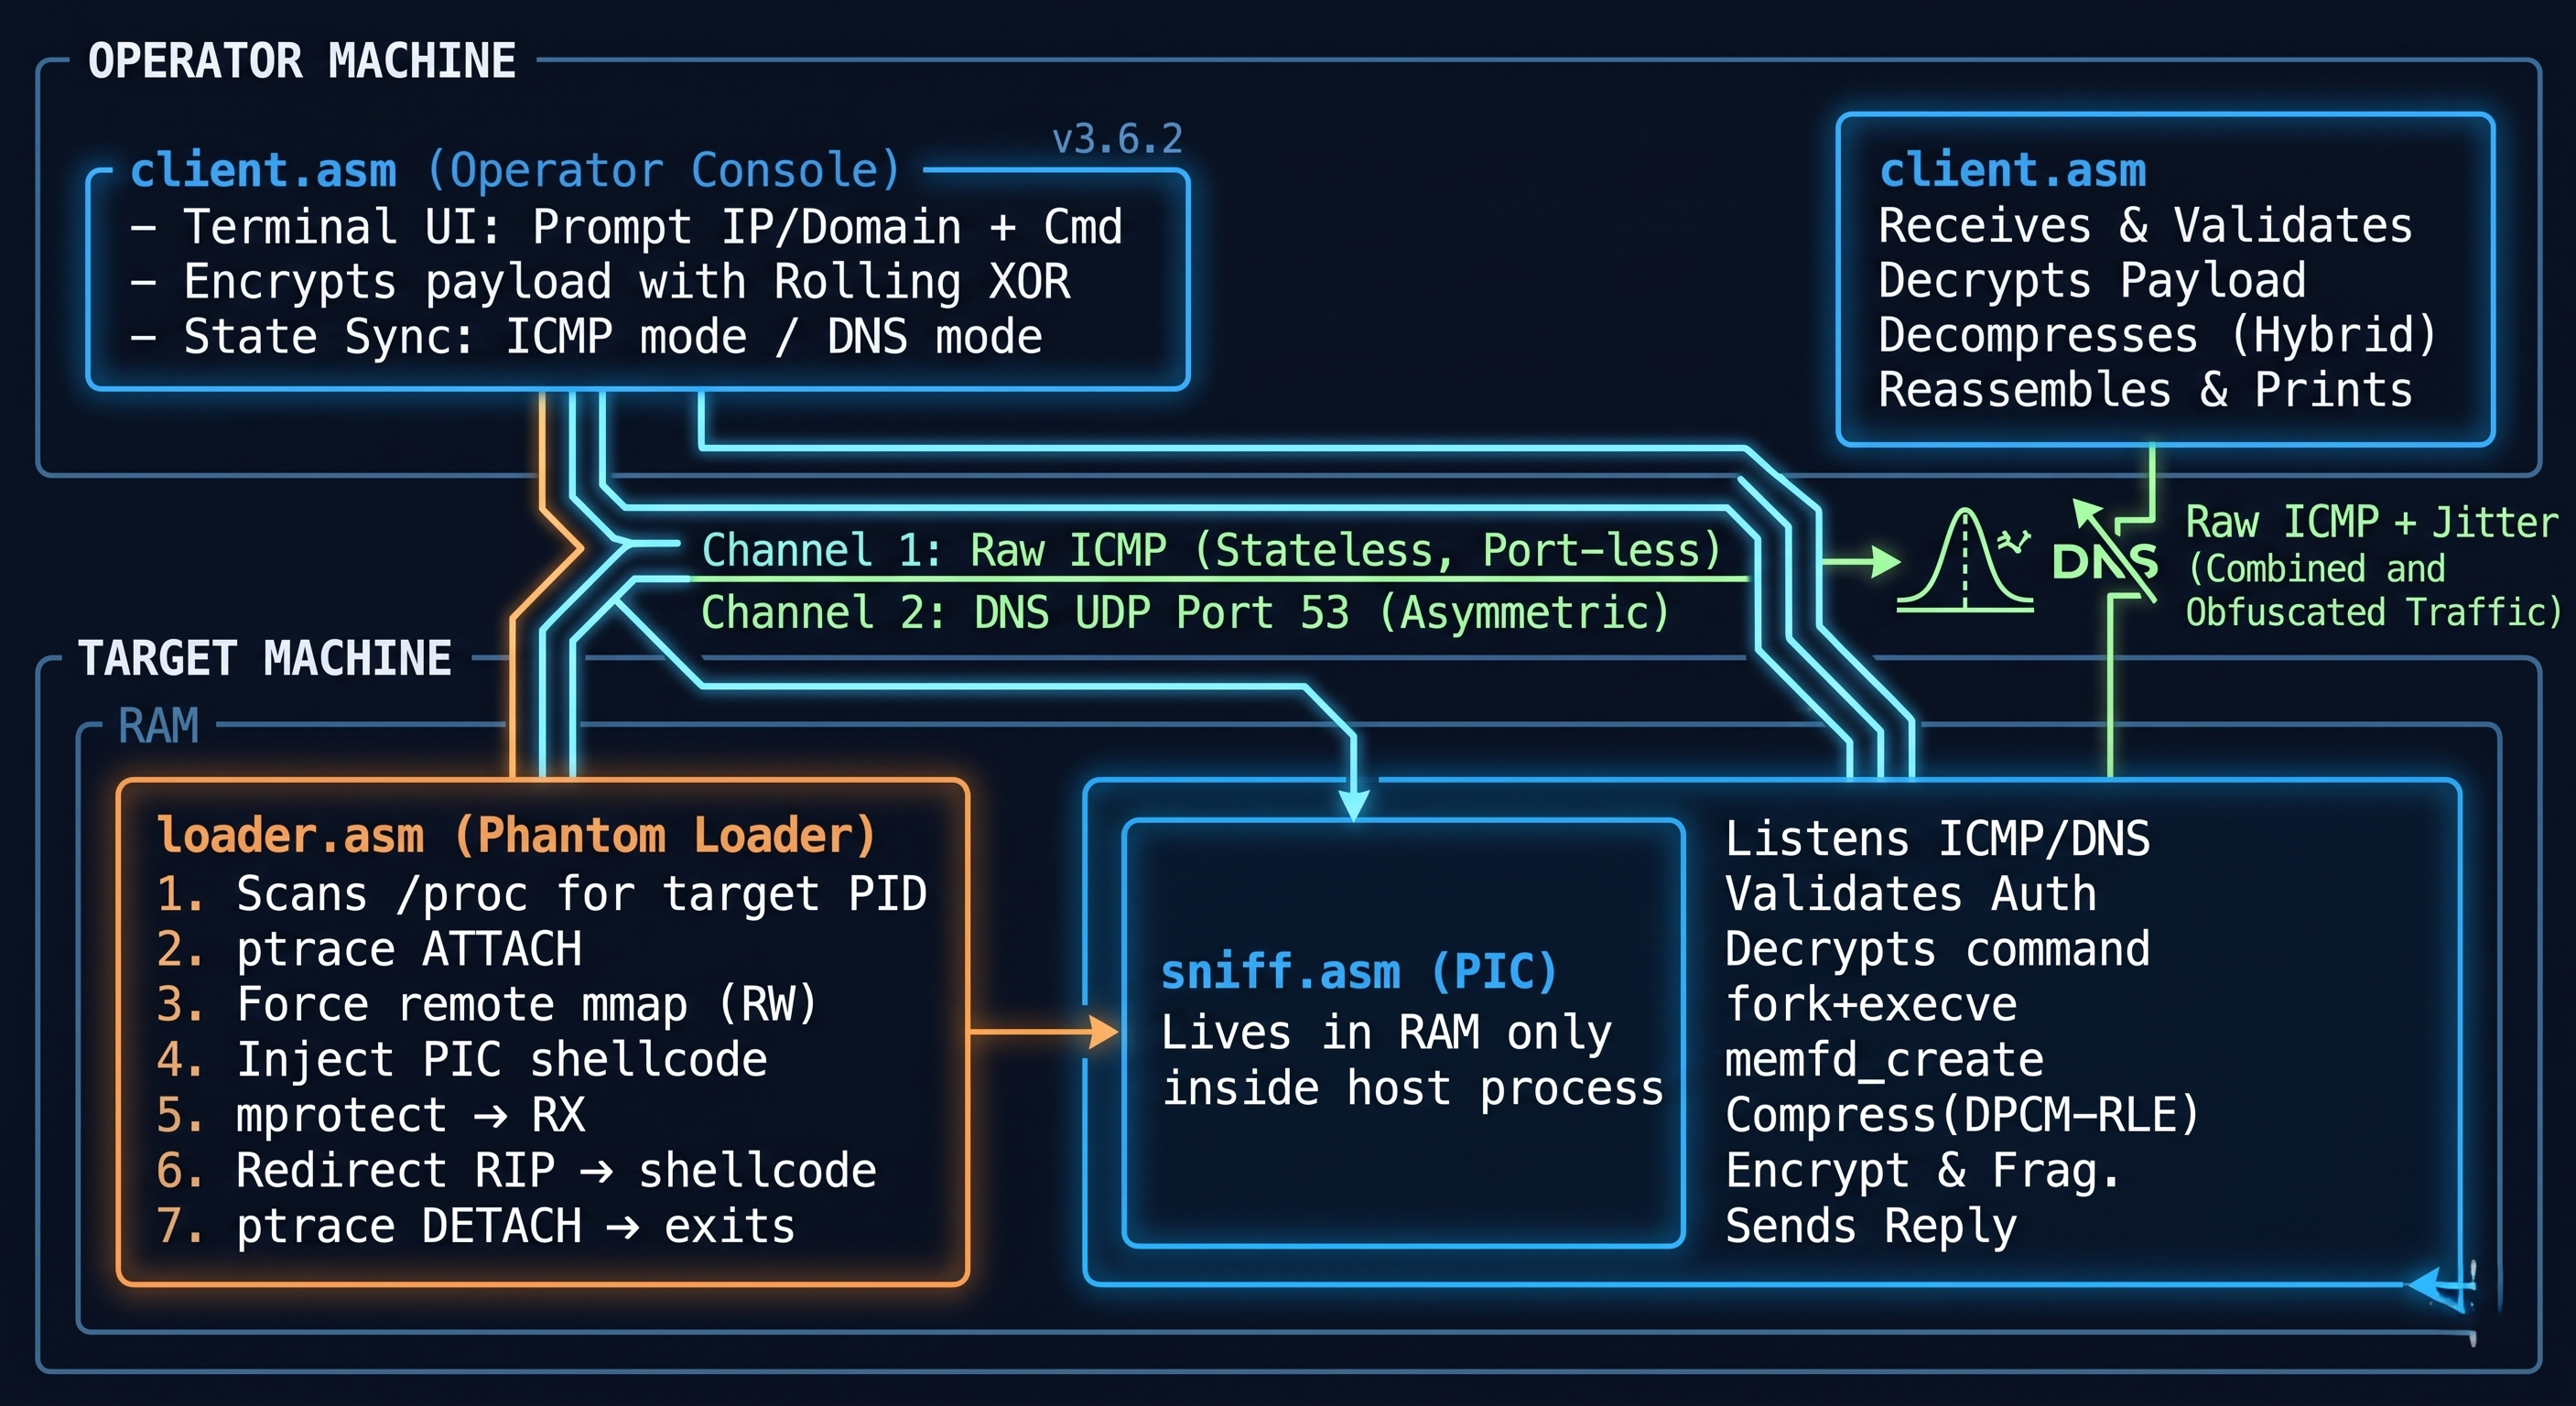
ICMP-Ghost-A-Fileless-x64-Assembly-C2-Agent preview

ICMP-Ghost-A-Fileless-x64-Assembly-C2-Agent

GitHubjm00nj/icmp-ghost-a-fileless-x64-assembly-c2-agent

Fileless x64 Assembly C2 framework with dual-channel ICMP/DNS protocol pivoting, direct syscall execution, and ptrace-based process injection for…

command-and-controlexploit-frameworksids-ips-evasion+5
95
5 days ago
Terminator_Killer preview

Terminator_Killer

GitHubhika-sec/terminator_killer

Kernel-mode process killer exploiting CVE-2026-0828 (BYOVD) to terminate protected processes via a vulnerable signed driver, bypassing PPL and…

exploitationids-ips-evasionpenetration-testing+3
11 month ago
memdumper preview

memdumper

GitHubcenobyte-vincit/memdumper

Abuses macOS debugger entitlements and DYLD_INSERT_LIBRARIES to dump or search a running process's memory while shifting EDR attribution to a signed…

digital-forensicsids-ips-evasioninformation-gathering+4
11 month ago
macos_app_structure preview

macos_app_structure

GitHubyo-yo-yo-jbo/macos_app_structure

Educational deep dive into macOS app bundles, plist files, and launchd process behavior, with offensive security notes on packaging payloads as .app…

educationids-ips-evasionpayload-development+2
472 months ago
CVE-2025-61155 preview

CVE-2025-61155

GitHubsf0rzin/cve-2025-61155

CVE-2025-61155 — arbitrary process termination in GameDriverX64.sys (Tower of Fantasy anti-cheat). Original IDA Pro teardown, PoC, YARA, IOCs,…

binary-analysiseducationexploitation+7
33 months ago
Darkcloak preview

Darkcloak

GitHub0x574r/darkcloak

Linux process identity cloaking tool that spoofs comm, argv, cmdline, environ, exe path, and VMAs via an 11-phase prctl pipeline to impersonate…

binary-analysisfingerprint-spoofingids-ips-evasion+6
123 months ago
EDR-Freeze preview

EDR-Freeze

GitHubtwosevenonet/edr-freeze

EDR-Freeze is a tool that puts a process of EDR, AntiMalware into a coma state.

exploitationids-ips-evasionpost-exploitation+1
8734 months ago
userland-exec preview

userland-exec

GitHubhardenedlinux/userland-exec

Userland exec PoC to be used as attack vector technique

binary-analysisexploitationids-ips-evasion+2
1465 months ago
WinDefenderKiller preview

WinDefenderKiller

GitHubs12cybersecurity/windefenderkiller

Windows Defender Killer | Registry-Based Disablement + BYOVD Process Termination (C++)

adversarial-attackexploitationids-ips-evasion+3
5606 months ago
AMSI.fail preview

AMSI.fail

GitHubflangvik/amsi.fail

C# Azure Function with an HTTP trigger that generates obfuscated PowerShell snippets that break or disable AMSI for the current process.

defensive-toolsexploitationids-ips-evasion+2
4687 months ago
TangledWinExec preview

TangledWinExec

GitHubdaem0nc0re/tangledwinexec

PoCs and tools for investigation of Windows process execution techniques

adversarial-attackdebuggersids-ips-evasion+6
9588 months ago
DarkWidow preview

DarkWidow

GitHubreveng007/darkwidow

Indirect Dynamic Syscall, SSN + Syscall address sorting via Modified TartarusGate approach + Remote Process Injection via APC Early Bird + Spawns a…

binary-analysiseducationexploitation+6
8098 months ago
SilentButDeadly preview

SilentButDeadly

GitHubloosehose/silentbutdeadly

SilentButDeadly is a network communication blocker specifically designed to neutralize EDR/AV software by preventing their cloud connectivity using…

command-and-controldefensive-toolsexploitation+7
45211 months ago
CVE-2025-61156 preview

CVE-2025-61156

GitHubd7ead/cve-2025-61156

Insecure access control in ThreatFire System Monitor's TfSysMon.sys driver allows unprivileged process termination with kernel privileges, enabling…

exploitationids-ips-evasionprivilege-escalation+2
811 months ago
obex preview

obex

GitHubdis0rder0x00/obex

Obex – Blocking unwanted DLLs in user mode

adversarial-attackids-ips-evasionpost-exploitation+1
2781 year ago
ProcessInjection preview

ProcessInjection

GitHub3xpl01tc0d3r/processinjection

This program is designed to demonstrate various process injection techniques

binary-exploitationeducationencryption-decryption-tools+5
1.3k1 year ago
nowafpls preview

nowafpls

GitHubassetnote/nowafpls

Burp Plugin to Bypass WAFs through the insertion of Junk Data

ids-ips-evasionpenetration-testingred-teaming+3
1.5k1 year ago
fake-sandbox preview

fake-sandbox

GitHubnuclearphoenixx/fake-sandbox

👁‍🗨 This script will simulate fake processes of analysis sandbox/VM software that some malware will try to avoid.

anti-botdefensive-toolsids-ips-evasion+1
1411 year ago
Previous123Next