
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
222 results
convoC2 preview

convoC2

GitHubcxnturi0n/convoc2

C2 infrastructure over Microsoft Teams.

command-and-controldata-exfiltrationids-ips-evasion+6
7591 year ago
CuiRi preview

CuiRi

GitHubnydubh3/cuiri

一款红队专用免杀木马生成器,基于shellcode生成绕过所有杀软的木马。
command-and-controlexploitationids-ips-evasion+7
9225 years ago
HackTheWorld preview

HackTheWorld

GitHubstormshadow07/hacktheworld

An Python Script For Generating Payloads that Bypasses All Antivirus so far .

exploitationids-ips-evasionmalware-analysis+5
1.0k2 years ago
spoofed preview

spoofed

GitHubamibhai/spoofed

A professional-grade, fully async Python network spoofing suite for authorized security auditing. Features full IPv4/IPv6 interception, 802.11…

dns-analysisids-ips-evasionnetwork-security+6
12 months ago
lockjaw preview

lockjaw

GitHubg13net/lockjaw

Modular Windows C2 framework with a Rust teamserver, Zig implant, indirect syscalls, AMSI bypass, reflective/PoolParty injection, in-memory BOF…

command-and-controldns-analysisexploit-frameworks+9
3429 days ago
Koi preview

Koi

GitHubb3rt1ng/koi

Multi-session reverse shell handler with PTY upgrade, post-exploitation modules, Layer 3 tunneling, payload obfuscation for EDR evasion, session…
command-and-controlids-ips-evasionlateral-movement+9
371 day ago
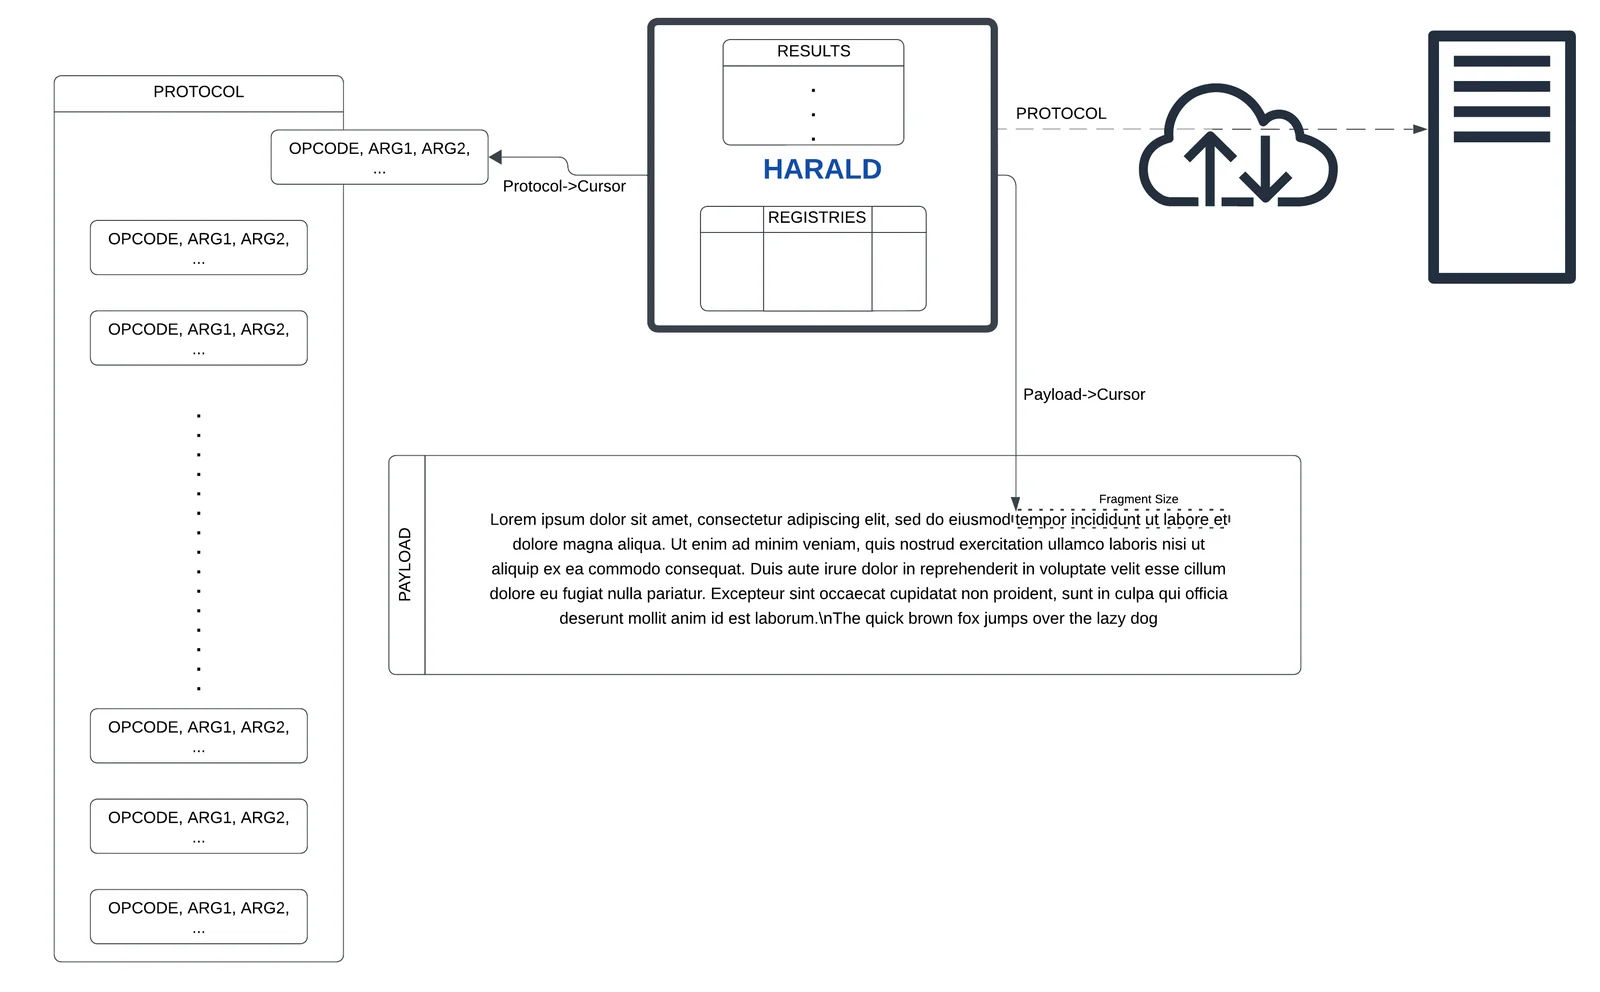
Harald preview

Harald

GitHubgmh5225/harald

An in-memory minimal CPU for agnostic on-the-fly protocols creation
command-and-controlexploitationids-ips-evasion+6
1 year ago
F31 preview

F31

GitHubgmh5225/f31

Tool for hiding Kali Linux on the network
anti-botdefensive-toolsfingerprint-spoofing+6
32 years ago
tfo-connect-bypass preview

tfo-connect-bypass

GitHub4n4s4zi/tfo-connect-bypass

Using TCP Fast Open to bypass syscall-based networking rules (CVE-2026-63828/CVE-2026-72243 PoC)

exploitationids-ips-evasionnetwork-security+3
11 month ago
Empire preview

Empire

GitHubbc-security/empire

Empire is a post-exploitation and adversary emulation framework that is used to aid Red Teams and Penetration Testers.
adversarial-attackcommand-and-controldata-exfiltration+16
5.3k1 month ago
Lastenzug preview

Lastenzug

GitHubcodewhitesec/lastenzug

Socks4a proxy leveraging PIC, Websockets and static obfuscation on assembly level
command-and-controlids-ips-evasionpayload-development+3
2354 years ago
WTSRM preview

WTSRM

GitHubrad9800/wtsrm

WTSRM

adversarial-attackeducationids-ips-evasion+2
2124 years ago
MalwareApiLibrary preview

MalwareApiLibrary

GitHubmalwareapilib/malwareapilibrary

collection of apis used in malware development
ids-ips-evasionpayload-developmentred-teaming
2314 years ago
AtomicSyscall preview

AtomicSyscall

GitHubdaem0nc0re/atomicsyscall

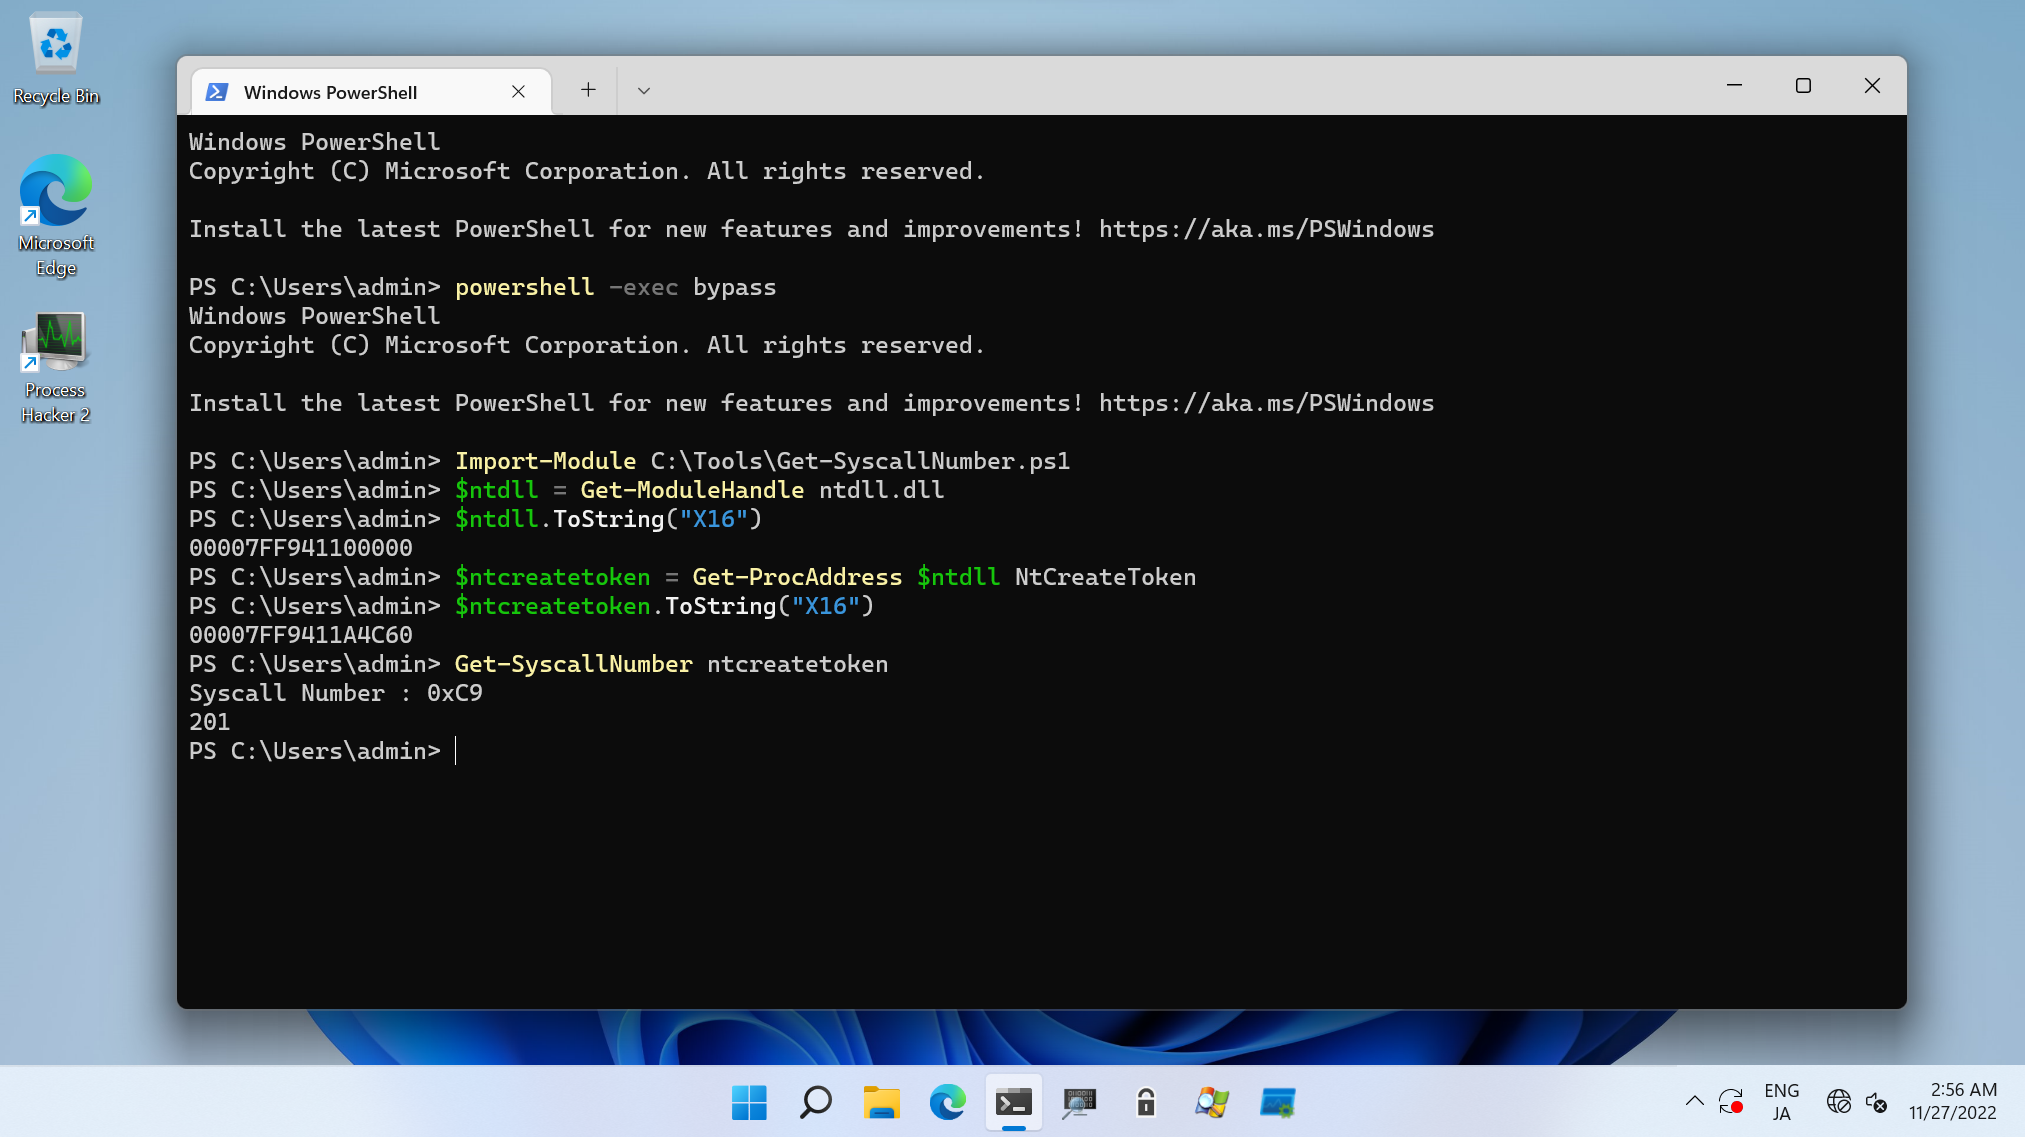
Tools and PoCs for Windows syscall investigation.
adversarial-attackbinary-analysiseducation+3
36411 months ago
Payload-Download-Cradles preview

Payload-Download-Cradles

GitHubvirtualalllocex/payload-download-cradles

This are different types of download cradles which should be an inspiration to play and create new download cradles to bypass AV/EPP/EDR in context…
curated-resourcesids-ips-evasionpayload-development+3
2584 years ago
Unwinder preview

Unwinder

GitHubkudaes/unwinder

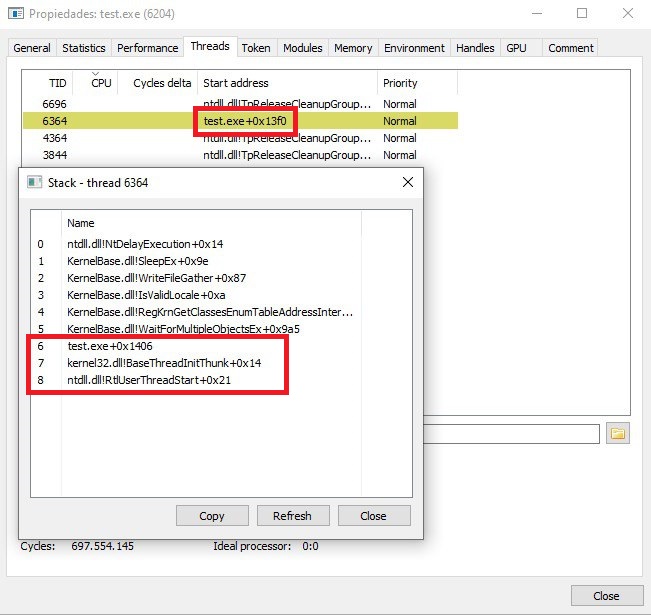
Call stack spoofing for Rust
adversarial-attackids-ips-evasionpayload-development+2
3871 year ago
WTSRM2 preview

WTSRM2

GitHubrad9800/wtsrm2

Header-only C++17 library for evasive Windows development: compile-time API hashing, DLL unhooking, hardware breakpoint clearing, VEH removal, and…
ids-ips-evasionpayload-developmentred-teaming
1633 years ago
Win32_Offensive_Cheatsheet preview

Win32_Offensive_Cheatsheet

GitHubmatthieu-hackwitharts/win32_offensive_cheatsheet

Win32 and Kernel abusing techniques for pentesters

binary-analysiscurated-resourceseducation+8
9833 years ago
Previous12…13Next