
Skip to content
KitploitKITPLOIT
ToolsBlog
Submit
ToolsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
293 results
evillimiter preview

evillimiter

GitHubdavidsonrafaelk/evillimiter

Tool that monitors, analyzes and limits the bandwidth of devices on the local network without administrative access
ids-ips-evasioninformation-gatheringnetwork-mapping+4
8
10 days ago
tfo-connect-bypass preview

tfo-connect-bypass

GitHub4n4s4zi/tfo-connect-bypass

Using TCP Fast Open to bypass syscall-based networking rules (CVE-2026-63828/CVE-2026-72243 PoC)
exploitationids-ips-evasionnetwork-security+3
7 days ago
-CTT-NSP-Convergent-Time-Theory---Network-Stack-Projection-CVE-2026-24858- preview

-CTT-NSP-Convergent-Time-Theory---Network-Stack-Projection-CVE-2026-24858-

GitHubsimoesctt/-ctt-nsp-convergent-time-theory---network-stack-projection-cve-2026-24858-

A Proof-of-Concept demonstrating the application of 3D Navier-Stokes CTT formulations to packet flow optimization and defensive bypass.
educationexploitationids-ips-evasion+1
7 months ago
memdumper preview

memdumper

GitHubcenobyte-vincit/memdumper

Abuses macOS debugger entitlements and DYLD_INSERT_LIBRARIES to dump or search a running process's memory while shifting EDR attribution to a signed…
digital-forensicsids-ips-evasioninformation-gathering+4
128 days ago
ShieldBreak preview

ShieldBreak

GitHub1neptune/shieldbreak

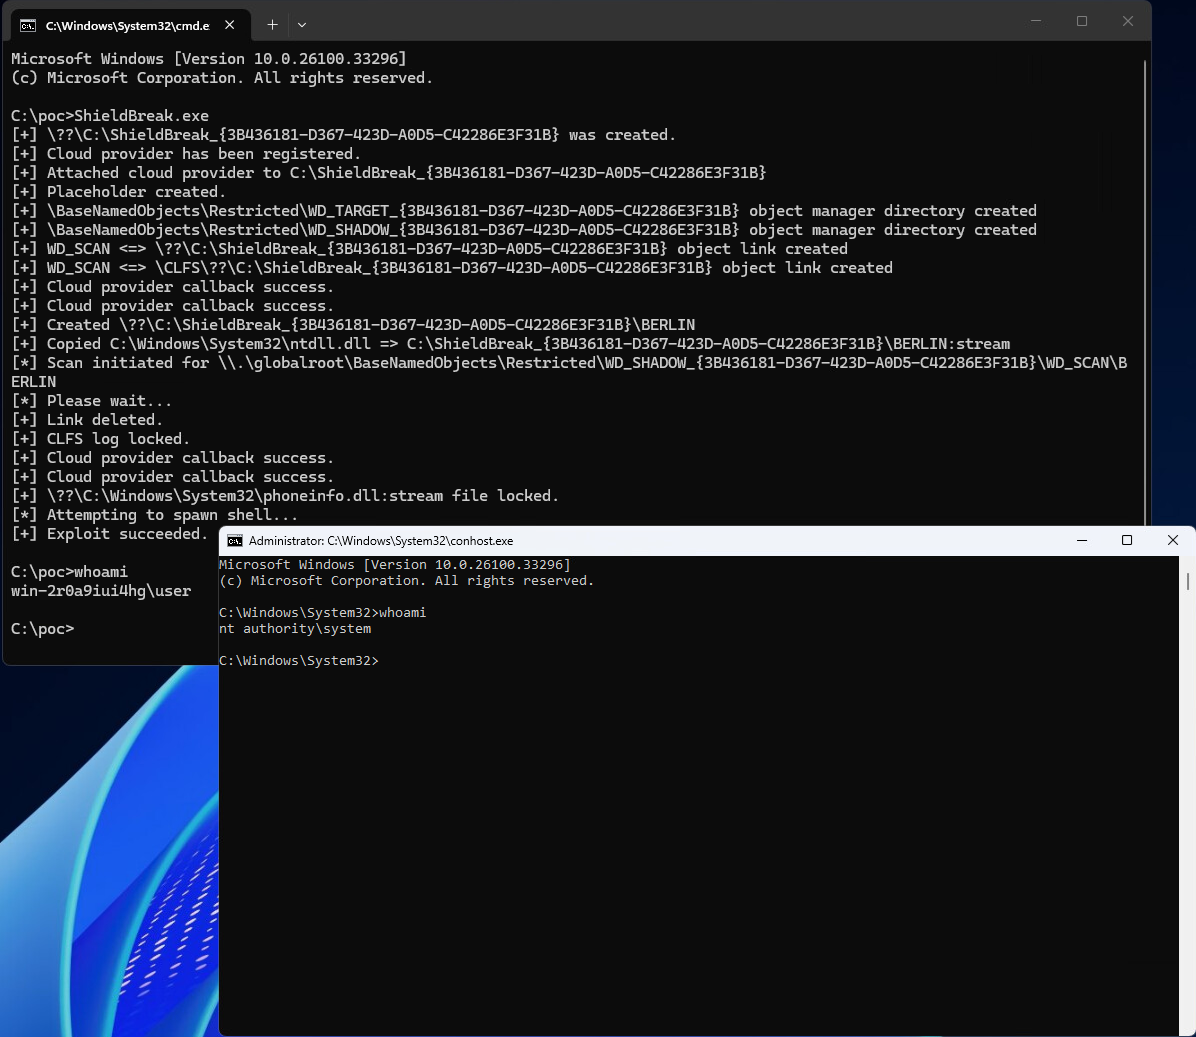
Windows Defender 0day proof-of-concept demonstrating a patch bypass for CVE-2026-69414, targeting Windows 11 25H2 and Server 2025 to evade endpoint…

exploitationids-ips-evasionred-teaming+1
128 days ago
CVE-2025-7771 preview

CVE-2025-7771

GitHubenessakircolak/cve-2025-7771

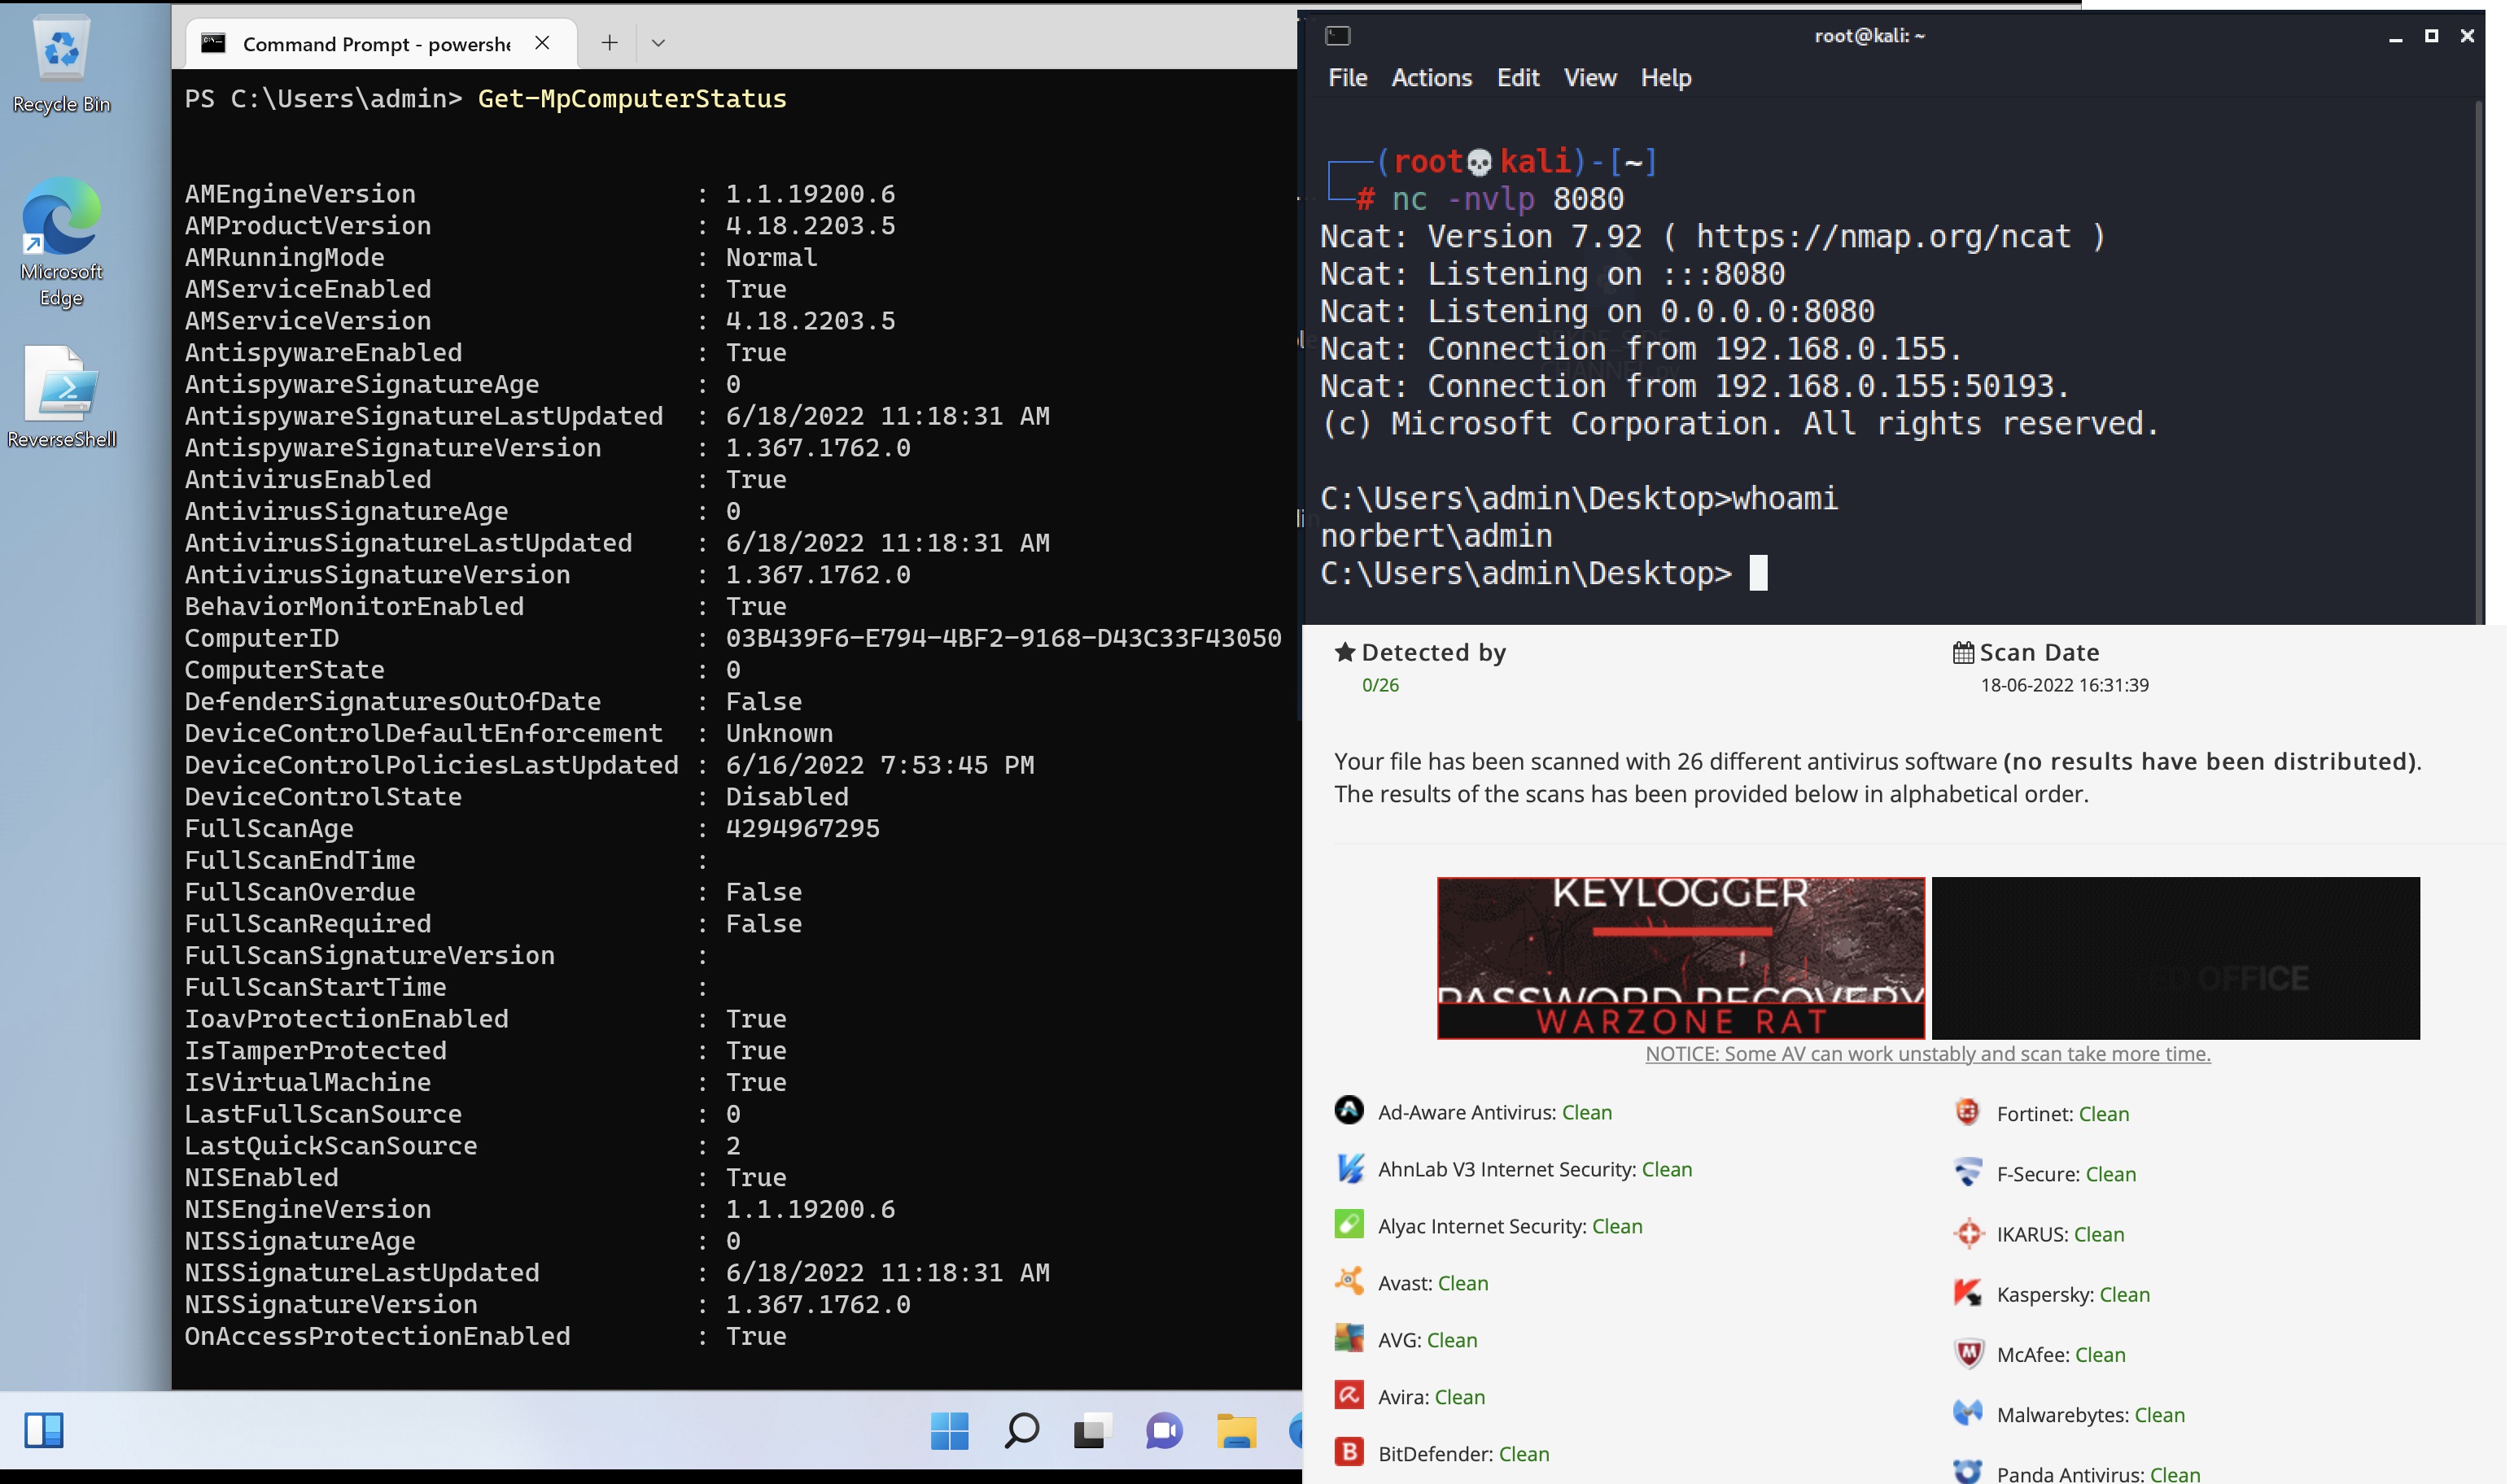
ThrottleStop.sys Arbitrary Physical Memory R/W
exploitationids-ips-evasionpenetration-testing+3
191 month ago
PSSW100AVB preview

PSSW100AVB

GitHubtihanyin/pssw100avb

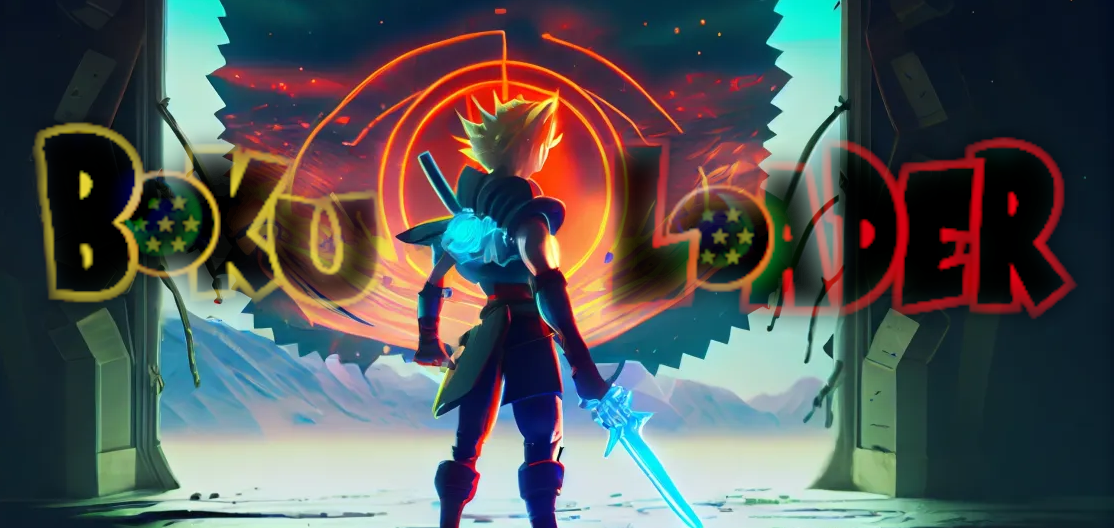
A list of useful Powershell scripts with 100% AV bypass (At the time of publication).
ai-securitycommand-and-controlids-ips-evasion+5
1.4k3 months ago
BokuLoader preview

BokuLoader

GitHubxforcered/bokuloader

A proof-of-concept Cobalt Strike Reflective Loader which aims to recreate, integrate, and enhance Cobalt Strike's evasion features!

adversarial-attackcommand-and-controlids-ips-evasion+4
3352 years ago
WTSRM preview

WTSRM

GitHubrad9800/wtsrm

WTSRM

adversarial-attackeducationids-ips-evasion+2
2144 years ago
TamperingSyscalls preview

TamperingSyscalls

GitHubrad9800/tamperingsyscalls

C++ library that retrieves and spoofs Windows syscall arguments using hardware breakpoints and exception handlers to subvert EDR telemetry.

ids-ips-evasionpayload-developmentpost-exploitation+1
5084 years ago
breakcyserver preview

breakcyserver

GitHubwaawaa/breakcyserver

Red-team EDR evasion utility that terminates security services by abusing Process Explorer driver functionality to bypass PPL and ObRegisterCallbacks.
exploitationids-ips-evasionpost-exploitation+2
524 years ago
Beginners-Guide-to-Obfuscation preview

Beginners-Guide-to-Obfuscation

GitHubbc-security/beginners-guide-to-obfuscation

Hands-on red-team obfuscation workshop teaching AMSI bypass, ETW evasion, and payload obfuscation with PowerShell, Visual Basic, and C# to evade…
educationids-ips-evasionlabs-practice+3
1.1k2 years ago
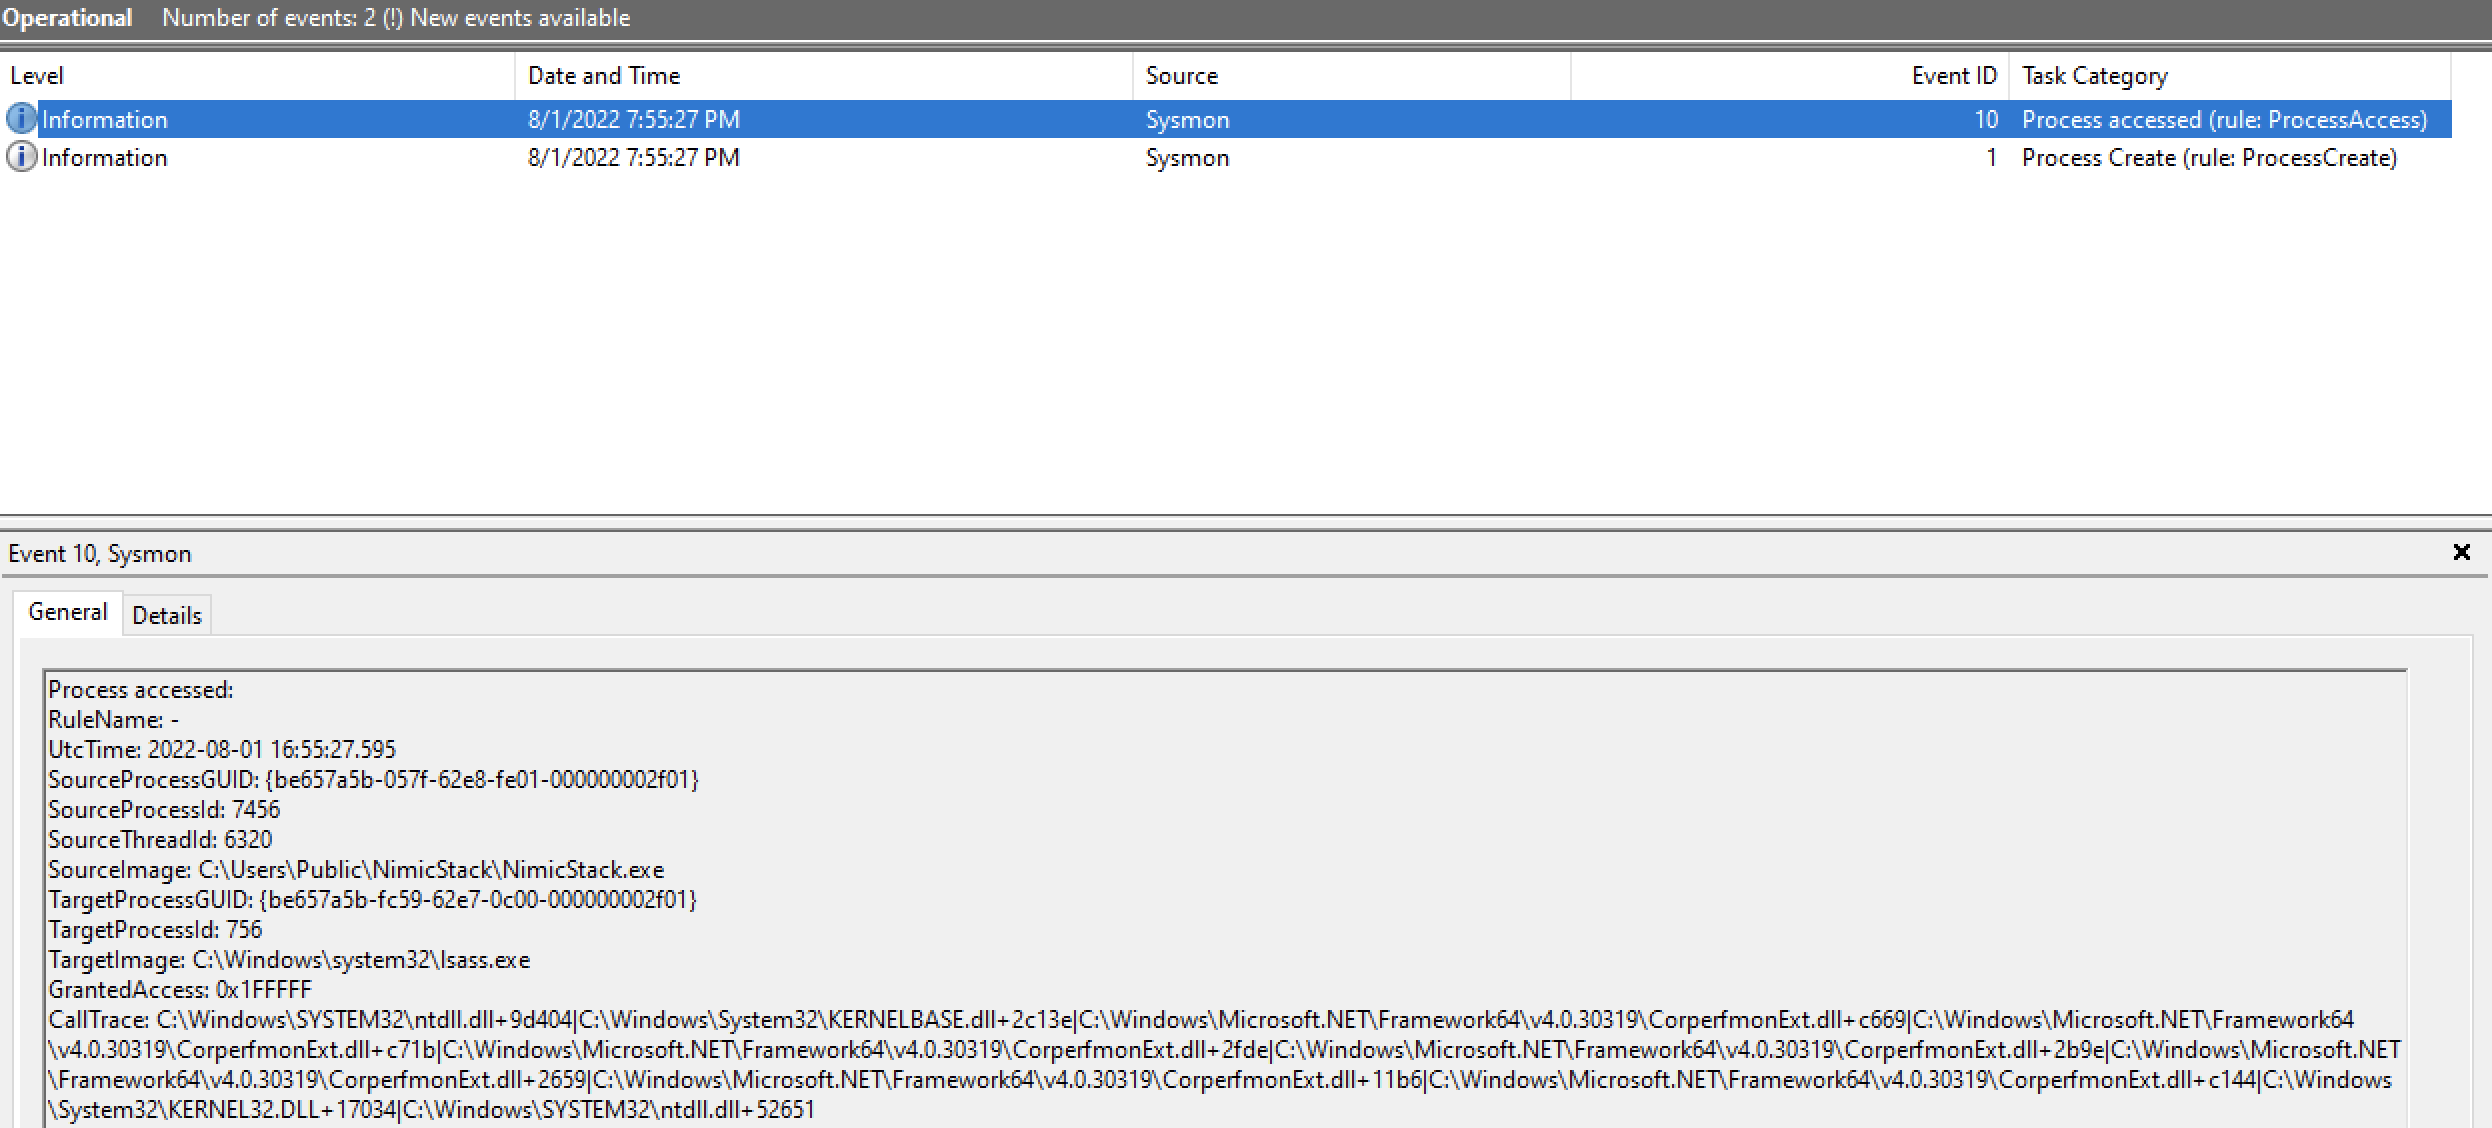
NimicStack preview

NimicStack

GitHubfrkngksl/nimicstack

NimicStack is the pure Nim implementation of Call Stack Spoofing technique to mimic legitimate programs
adversarial-attackids-ips-evasionpost-exploitation+1
955 months ago
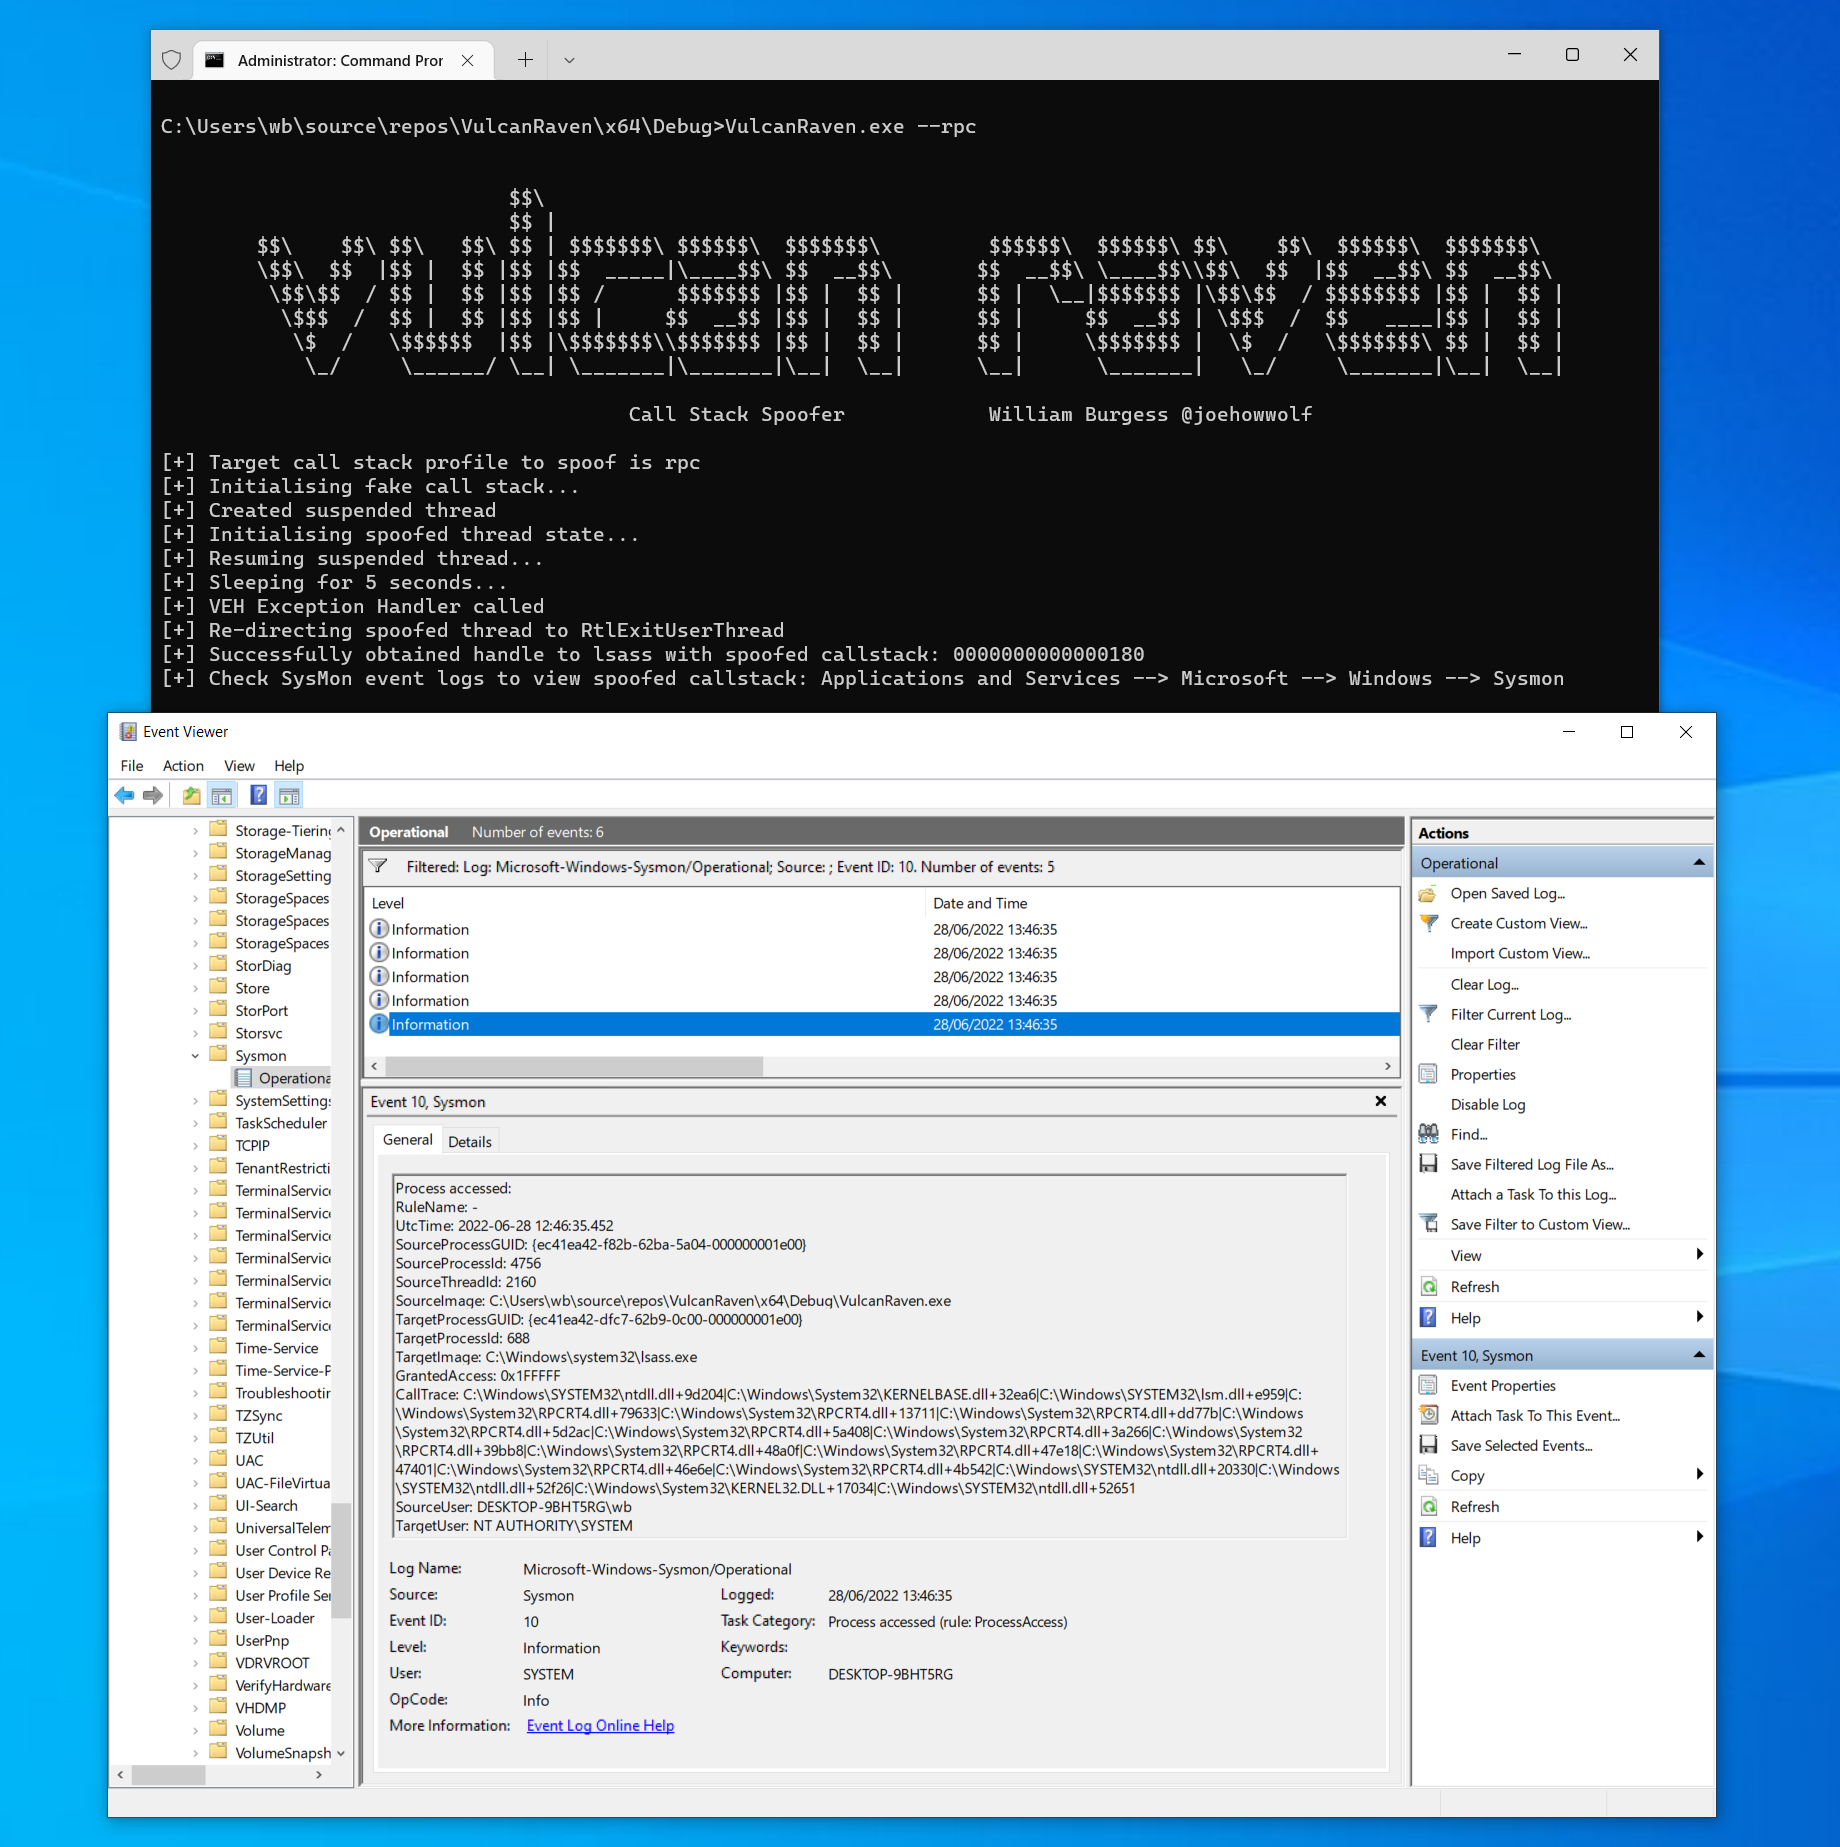
CallStackSpoofer preview

CallStackSpoofer

GitHubwithsecurelabs/callstackspoofer

A PoC implementation for spoofing arbitrary call stacks when making sys calls (e.g. grabbing a handle via NtOpenProcess)

adversarial-attackids-ips-evasionpost-exploitation+1
5991 year ago
SharpWhispers preview

SharpWhispers

GitHubsecforce/sharpwhispers

C# porting of SysWhispers2. It uses SharpASM to find the code caves for executing the system call stub.
ids-ips-evasionpayload-developmentpost-exploitation+2
1123 years ago
Cronos preview

Cronos

GitHubidov31/cronos

PoC for a sleep obfuscation technique leveraging waitable timers to evade memory scanners.
cryptographyids-ips-evasionpayload-development+2
6282 years ago
Awesome-CobaltStrike preview

Awesome-CobaltStrike

GitHubzer0yu/awesome-cobaltstrike

List of Awesome CobaltStrike Resources
command-and-controlcurated-resourceseducation+7
4.4k2 years ago
AtomicSyscall preview

AtomicSyscall

GitHubdaem0nc0re/atomicsyscall

Tools and PoCs for Windows syscall investigation.

adversarial-attackbinary-analysiseducation+3
3659 months ago
Previous12…17Next