
Codecepticon
 sadreck/codecepticon
.NET/PowerShell/VBA Offensive Security Obfuscator
code-analysisdefensive-toolsids-ips-evasion+5
sadreck/codecepticon.NET/PowerShell/VBA Offensive Security Obfuscator
 k4n3co/lab-rats-v1.6
Lab-RATS is a powerful and lightweight Android Remote Administration Tool full of features that enables remote monitoring, management and interaction…
 cylancevulnresearch/reflectivedllrefresher
Reflective DLL that scans process memory and unhooks loaded libraries to evade security software, with UPX, TLS injector, and Meterpreter integration.
 cxnturi0n/convoc2
C2 infrastructure over Microsoft Teams.
 damonmohammadbagher/ebook-bypassingavsbycsharp
eBook "Bypassing AVS by C#.NET Programming" (Free Chapters only)
 nydubh3/cuiri
一款红队专用免杀木马生成器,基于shellcode生成绕过所有杀软的木马。
 stormshadow07/hacktheworld
An Python Script For Generating Payloads that Bypasses All Antivirus so far .
 amibhai/spoofed
A professional-grade, fully async Python network spoofing suite for authorized security auditing. Features full IPv4/IPv6 interception, 802.11…
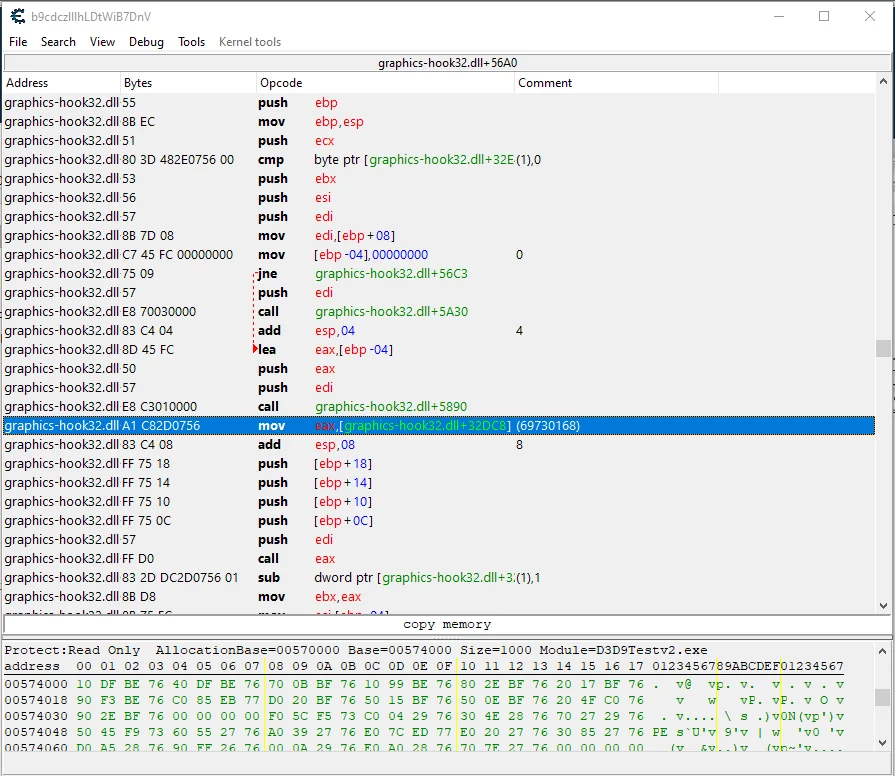 gmh5225/obs-graphics-hook32-hook
Demonstrates hooking OBS graphics-hook32.dll's D3D9 Present pointer to achieve stream-proof rendering that evades anti-cheat game capture detection.
 gmh5225/offensivedriver
Windows kernel driver prototype that toggles process protection, adjusts process privileges, patches DSE policy, and manipulates AV/EDR kernel…
 gmh5225/no-access-protection-x86
It encrypts the text section and set the protection to NO_ACCESS.
 silentisvox/syscallrevenant
Clean Indirect Syscalls with Syscall Tampering.
 kamalx06/tornadoc2
Pull-based C2 framework with ten native transports, concurrent multi-profile handlers, ECDSA-signed tasking, and a multi-operator team server with…
 twosevenonet/injectsetconsole
Proof of Concept for Process Code Injection Without Using WriteProcessMemory
 sk4r4b/ntdll-reconstruction
A technique that mixes NTDLL unhooking and hellsgate gate varients
 linnemanlabs/glimmer
Adversary emulation and C2 framework for security research
 abraxas/veneficus
Super elite end-to-end implant 0day. Full kill-chain. Exploit, escalate, pivot, poison, persistence.
 g13net/lockjaw
Modular Windows C2 framework with a Rust teamserver, Zig implant, indirect syscalls, AMSI bypass, reflective/PoolParty injection, in-memory BOF…