
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
64 results
reportly preview

reportly

GitHubsap8899/reportly

AzureAD/EntraID user activity reporter for blue teams. Input a suspicious user and time frame to receive a detailed report of user info, actions, and…
cloud-securityidentity-access-managementincident-response+2
96
3 years ago
CVE-2026-59358 preview

CVE-2026-59358

GitHubabraxas/cve-2026-59358

Proof-of-concept lab and exploit client for CVE-2026-59358, demonstrating Cloud Foundry UAA reuse of a user PKCE token as client_credentials Bearer…

authenticationexploitationidentity-access-management+4
2 days ago
IDWolf preview

IDWolf

GitHubg4bri-3l3/idwolf

Read-only Active Directory & Microsoft Entra ID hygiene auditor in pure PowerShell. Collect once, analyze offline: deterministic findings, attack…
cloud-securityconfiguration-auditingdefensive-tools+6
224 days ago
AADInternals preview

AADInternals

GitHubgerenios/aadinternals

PowerShell module for administering and auditing Azure AD and Office 365, enabling token manipulation, user enumeration, and security assessments of…
authenticationcloud-securityidentity-access-management+2
1.7k1 year ago
nebulousAD preview
Archived

nebulousAD

GitHubnuid/nebulousad

NebulousAD automated credential auditing tool.
api-securityauthenticationidentity-access-management+3
1526 years ago
aws-key-disabler preview

aws-key-disabler

GitHubte-papa/aws-key-disabler

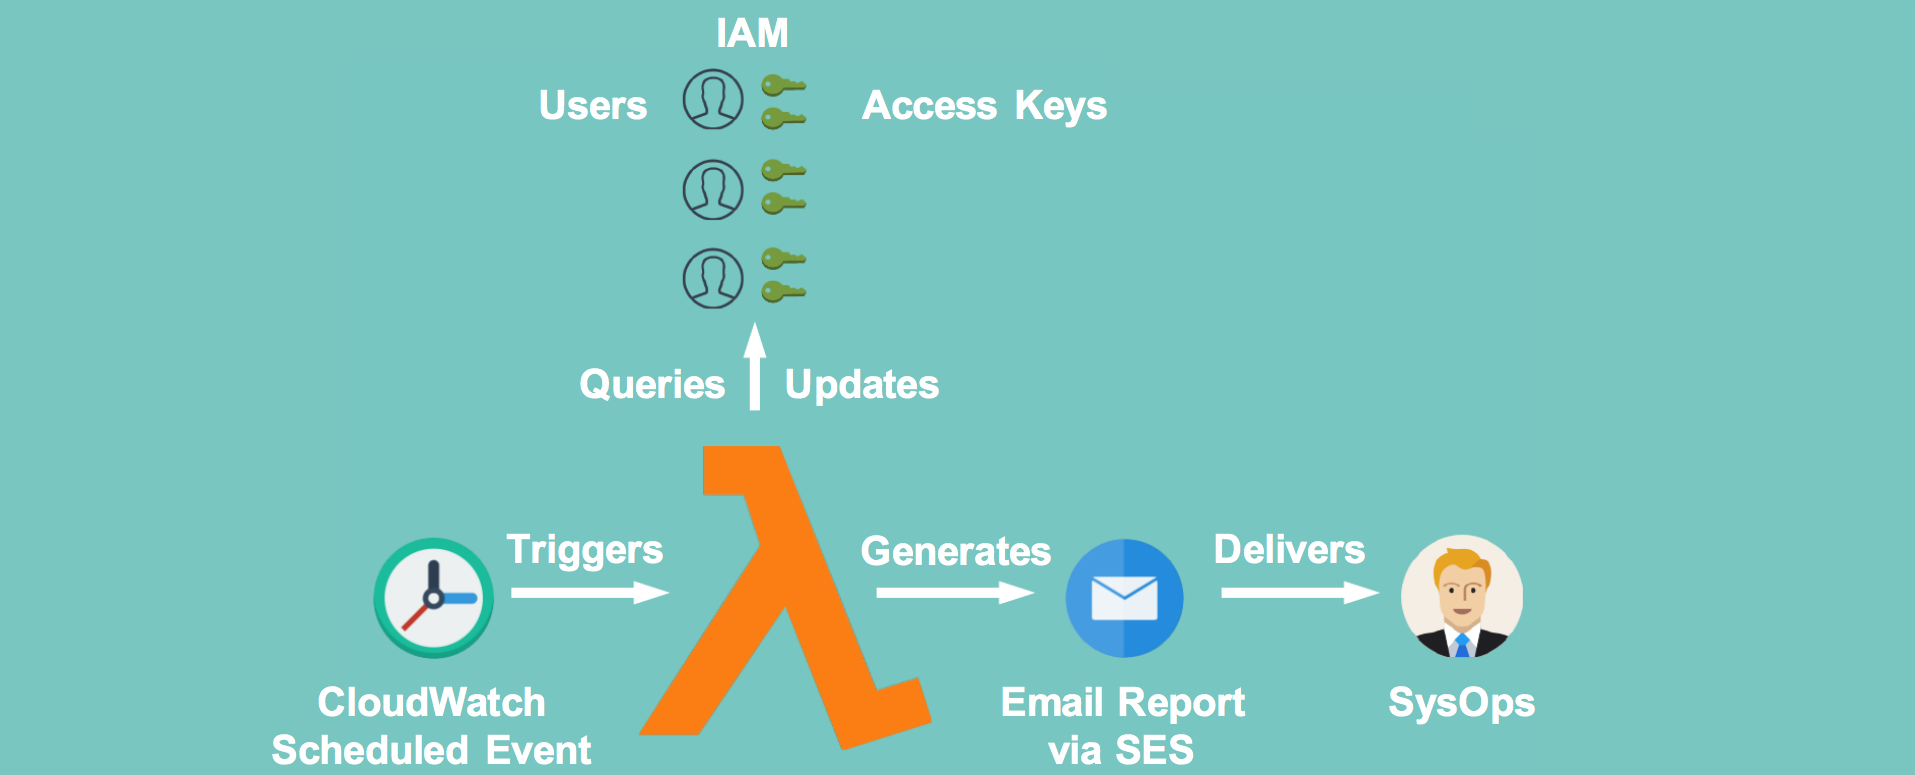
A small lambda script that will disable access keys older than a given amount of days.
cloud-securityconfiguration-auditingidentity-access-management
1545 years ago
ldapsdk preview

ldapsdk

GitHubpingidentity/ldapsdk

UnboundID LDAP SDK for Java

api-securityauthentication-authorizationdatabase-security+3
3763 days ago
BloodHound preview

BloodHound

GitHubspecterops/bloodhound

Six Degrees of Domain Admin
defensive-toolsidentity-access-managementinformation-gathering+4
3.5k19h 52m ago
ACLight preview

ACLight

GitHubcyberark/aclight

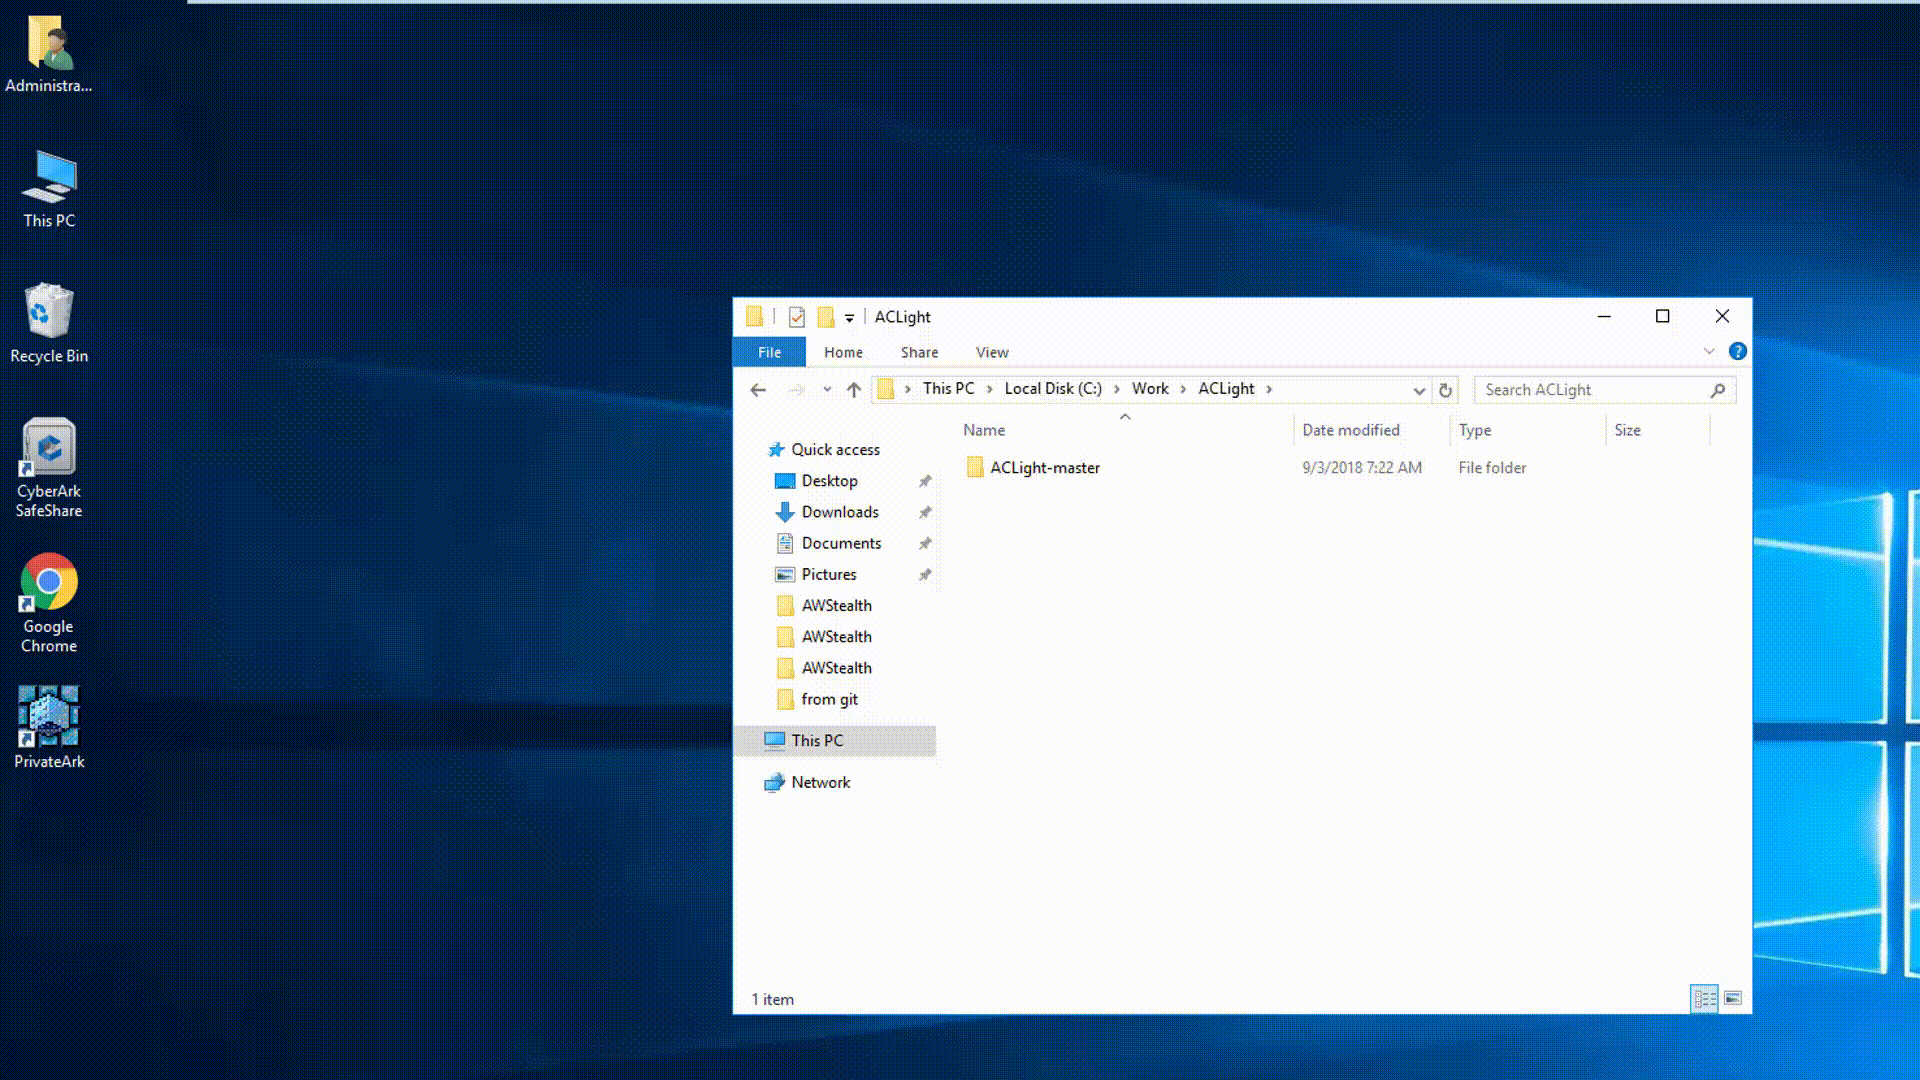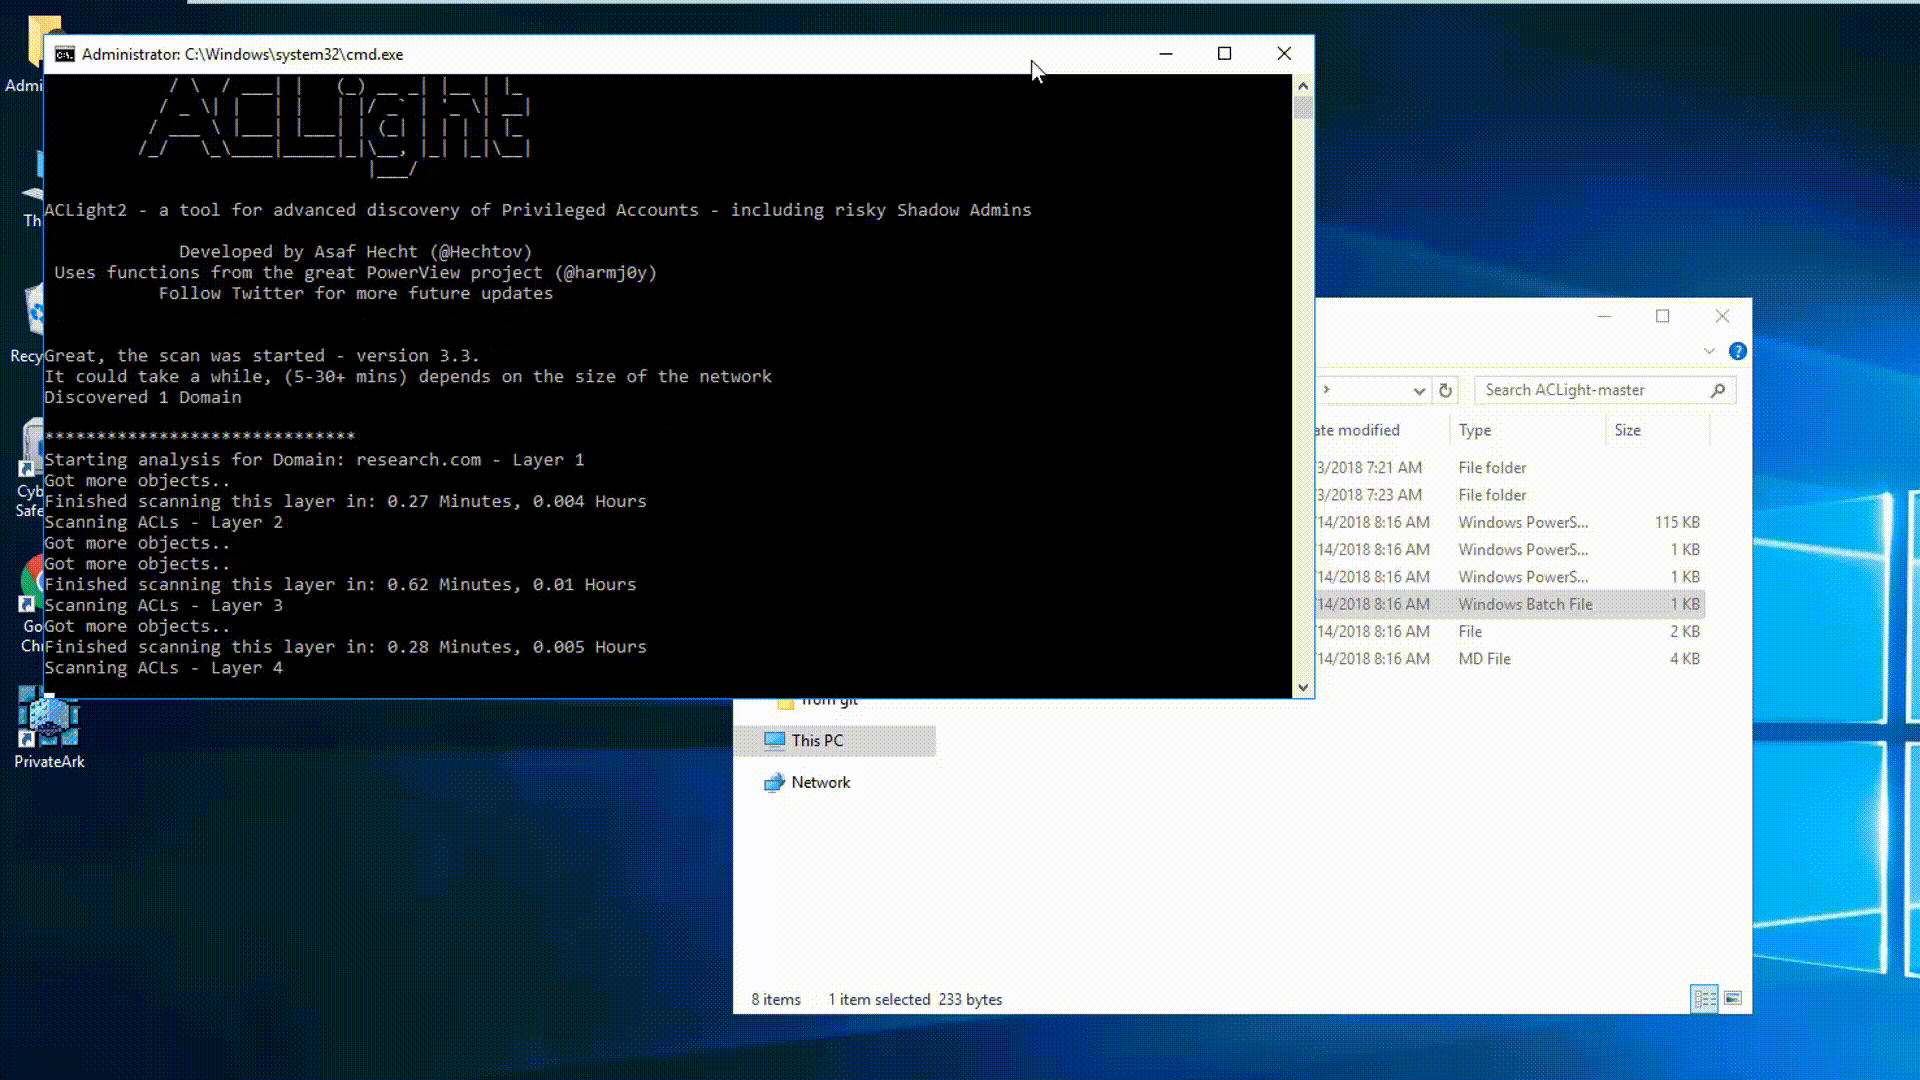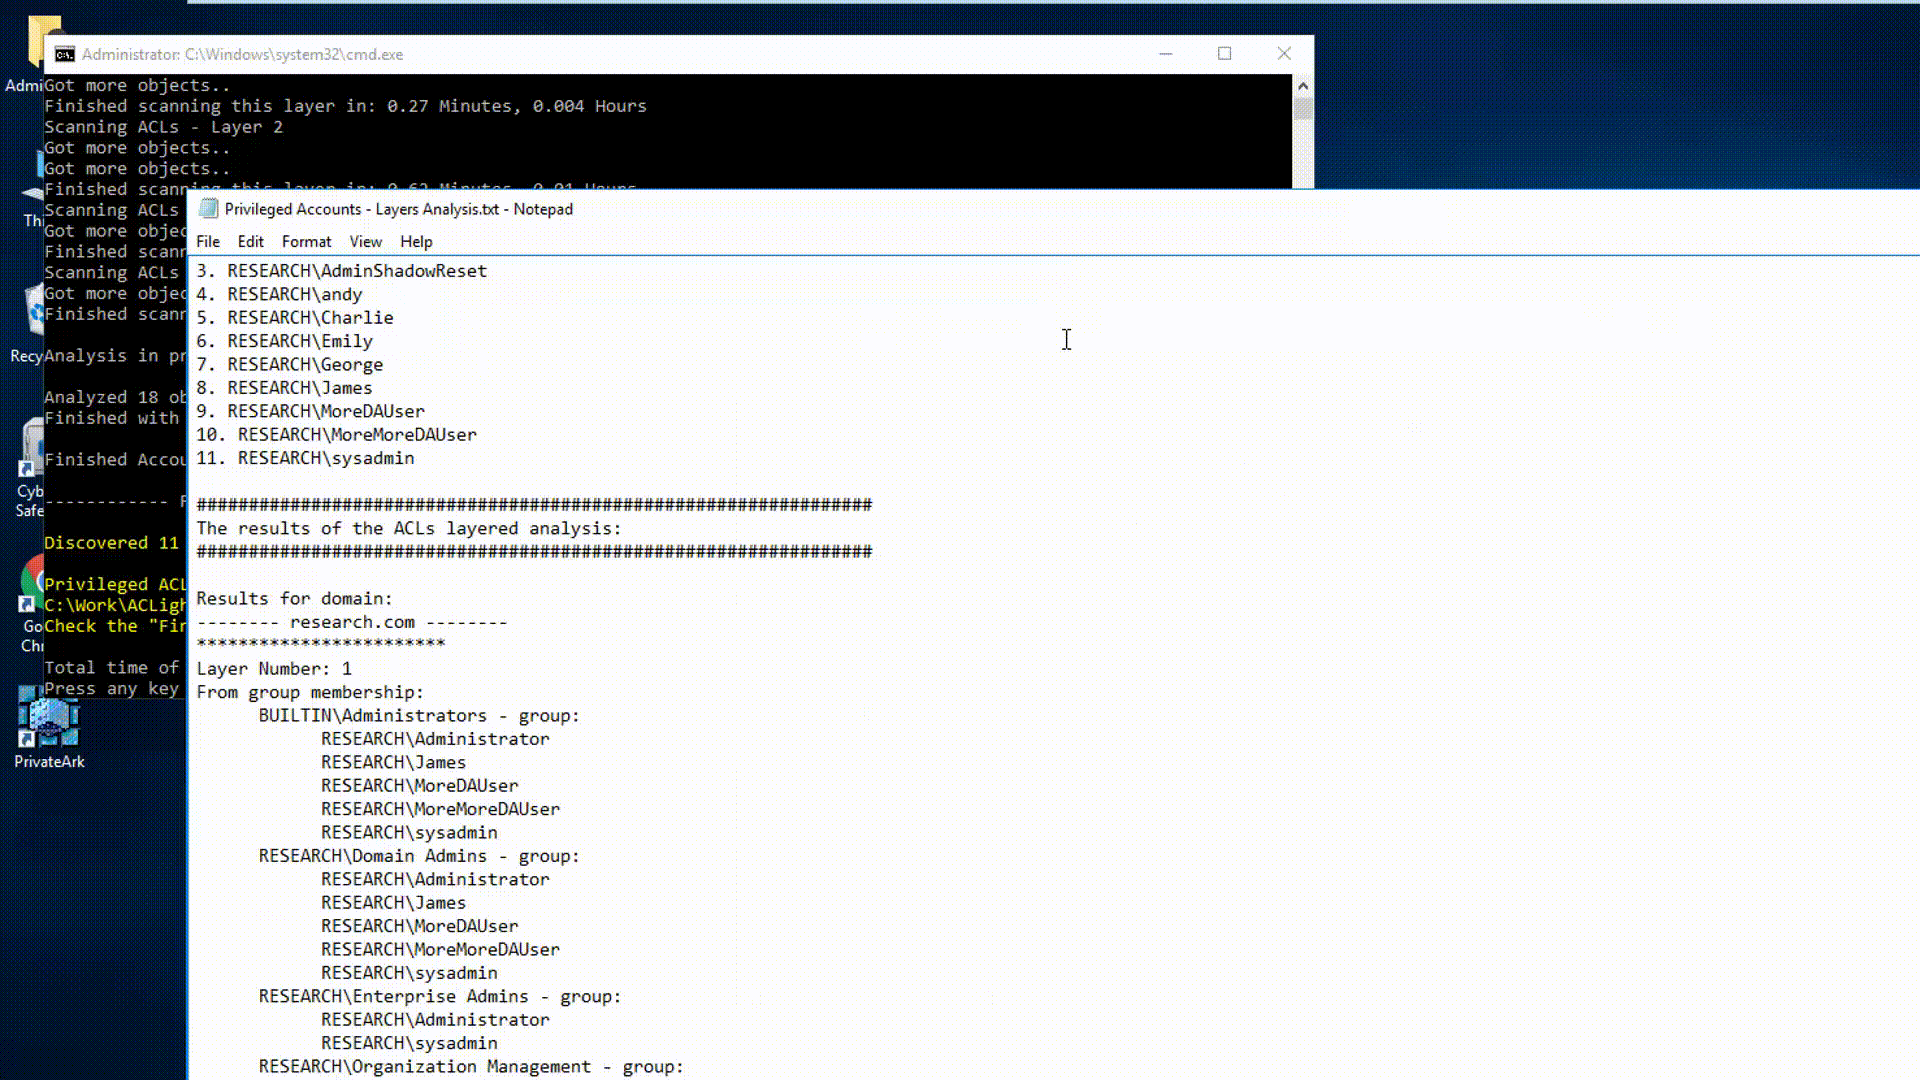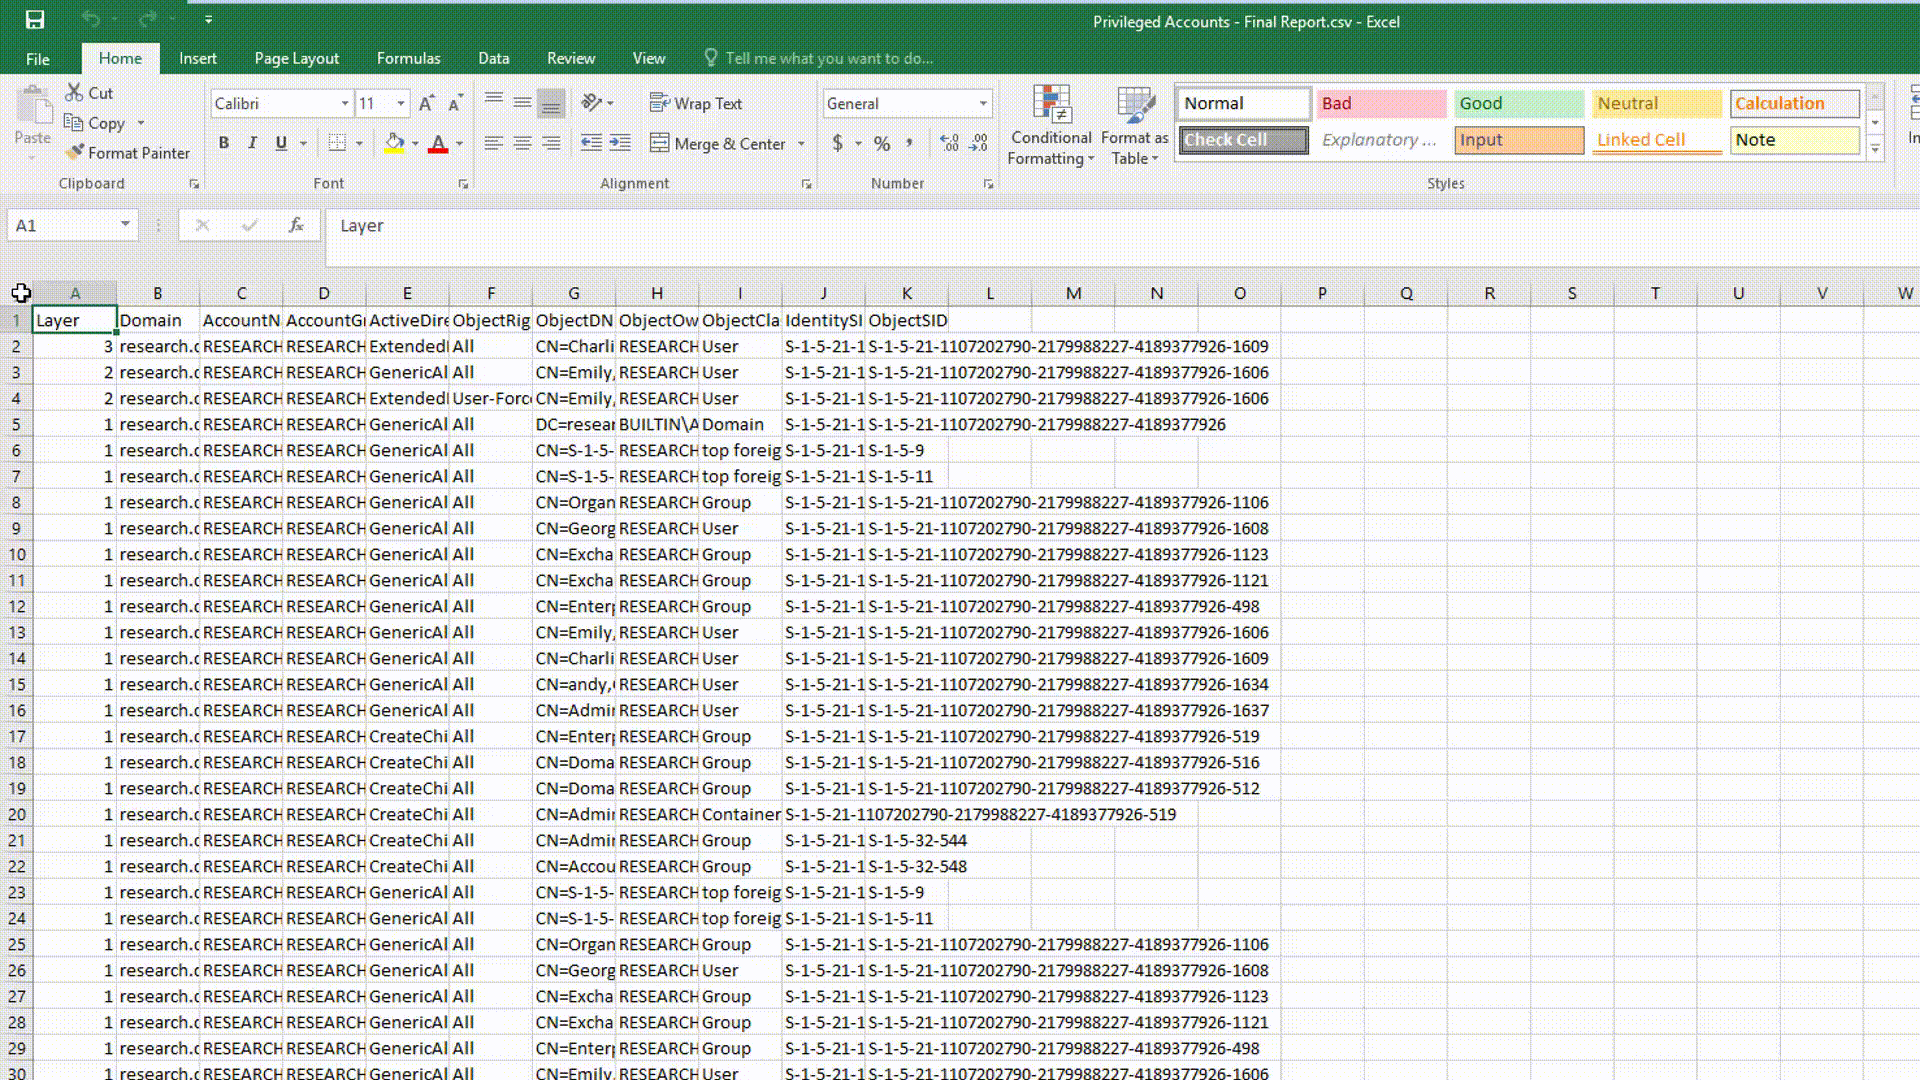
A script for advanced discovery of Privileged Accounts - includes Shadow Admins
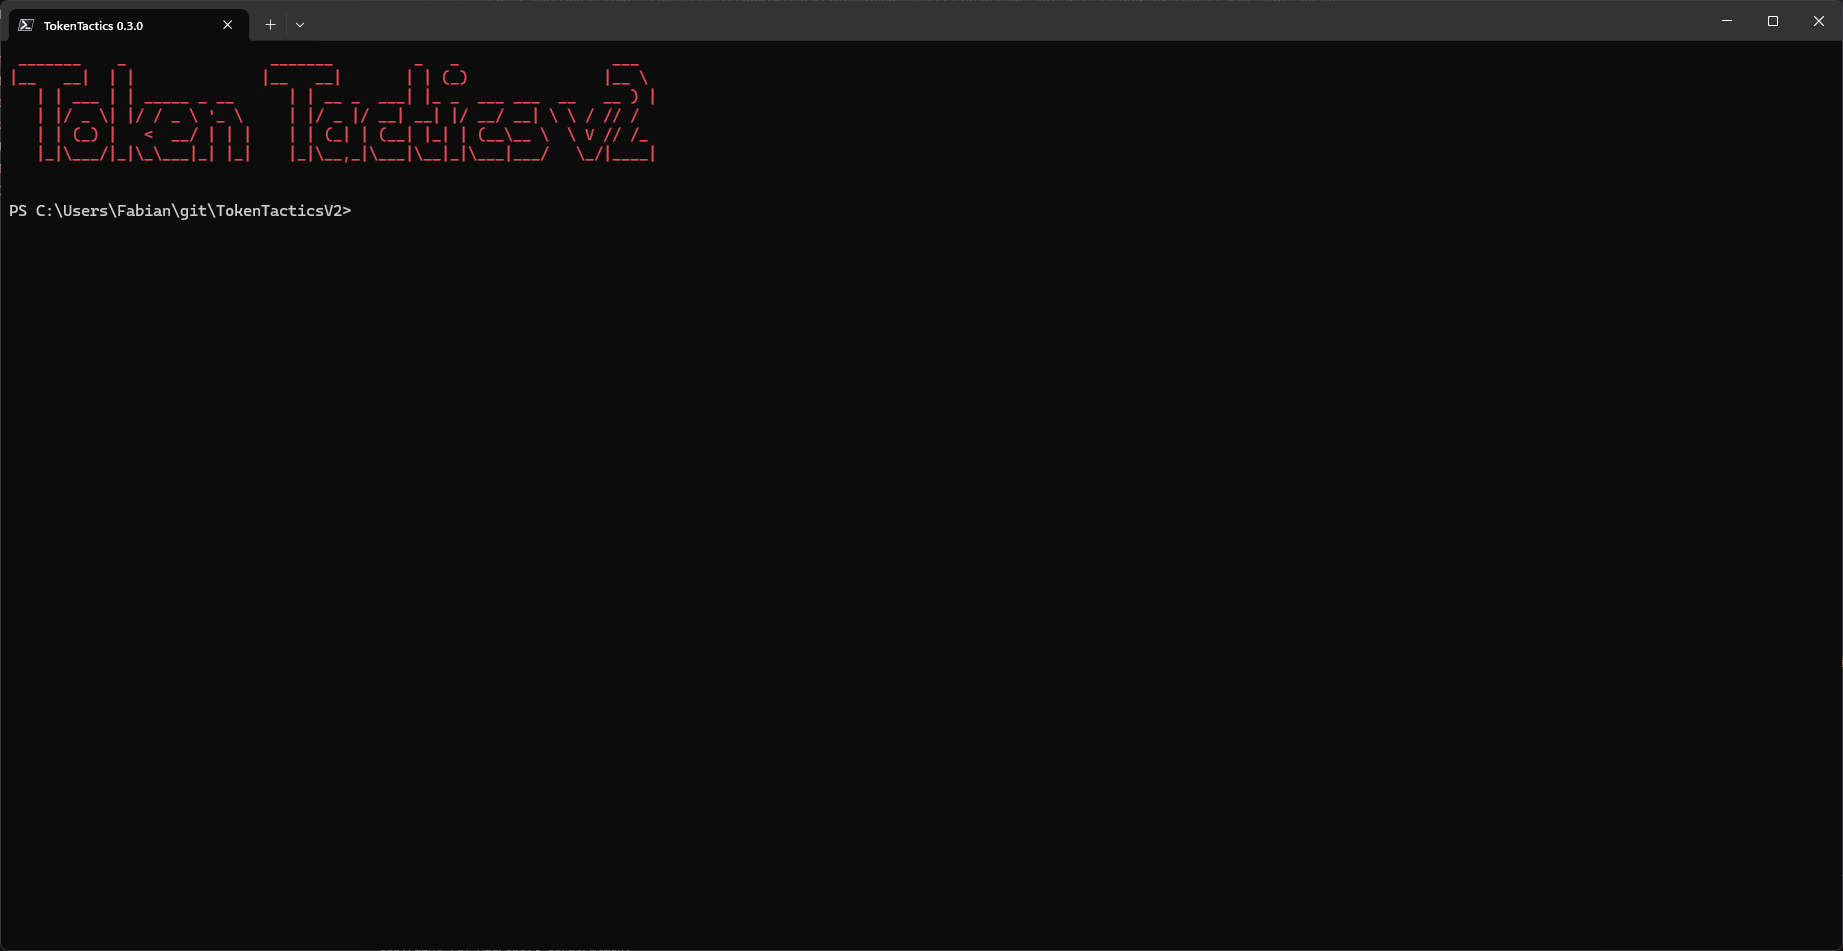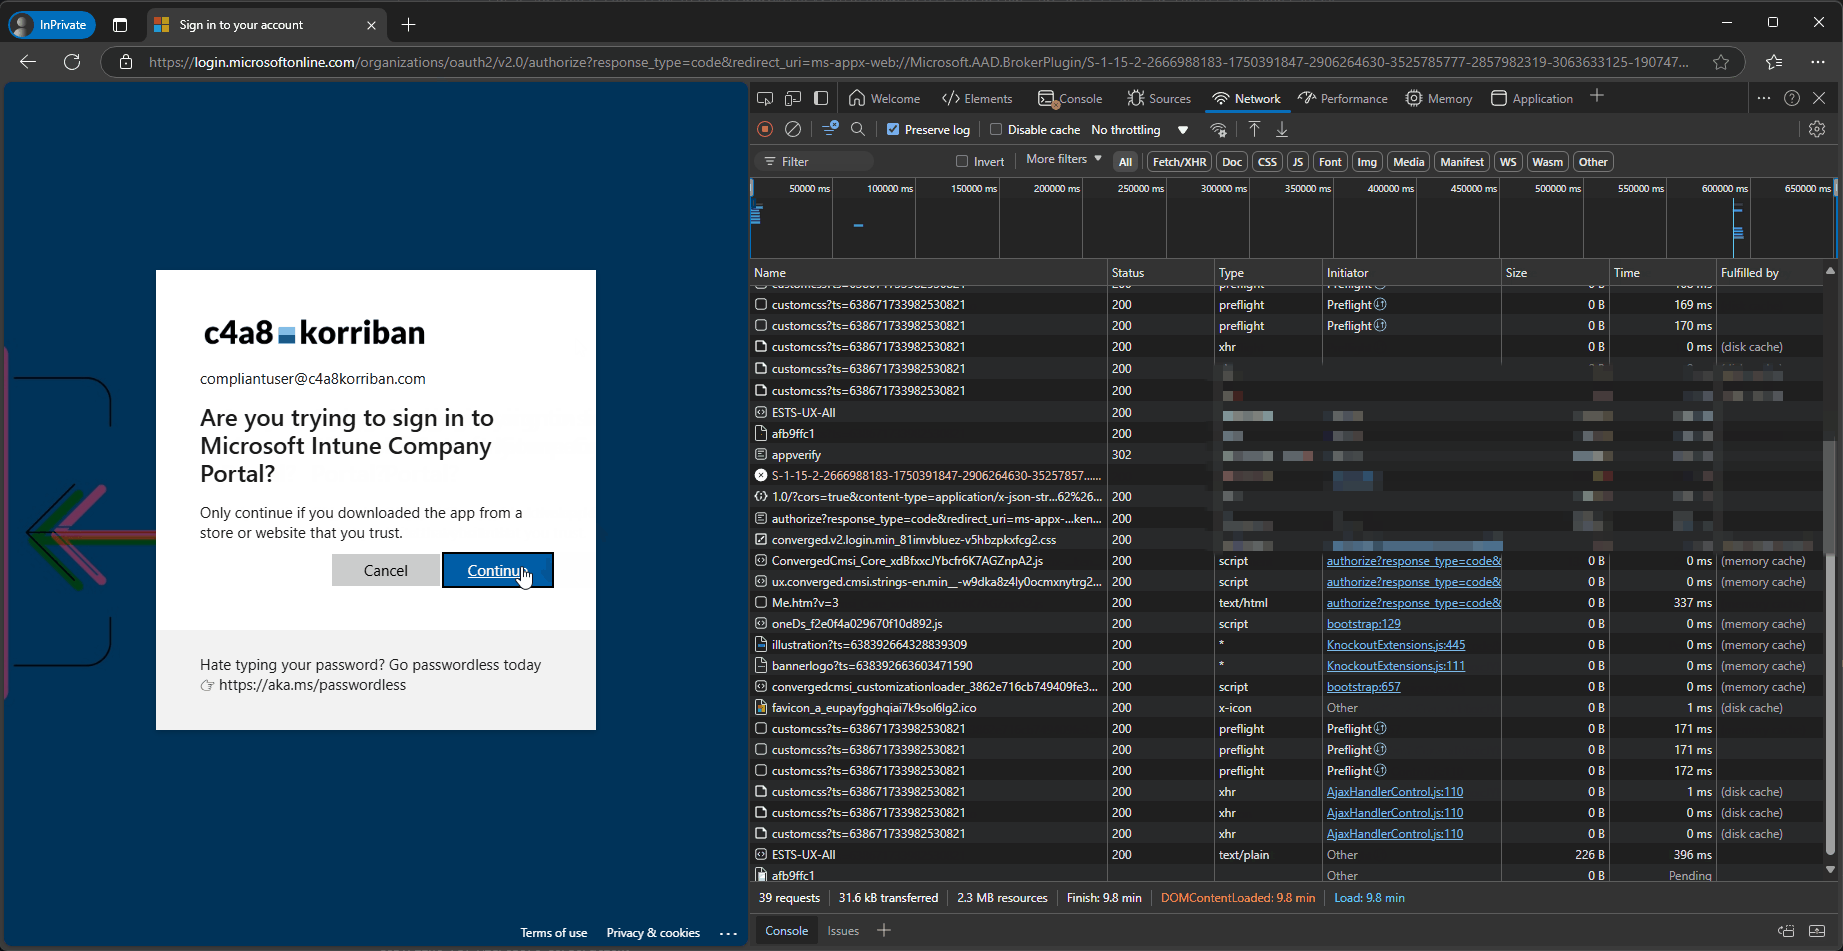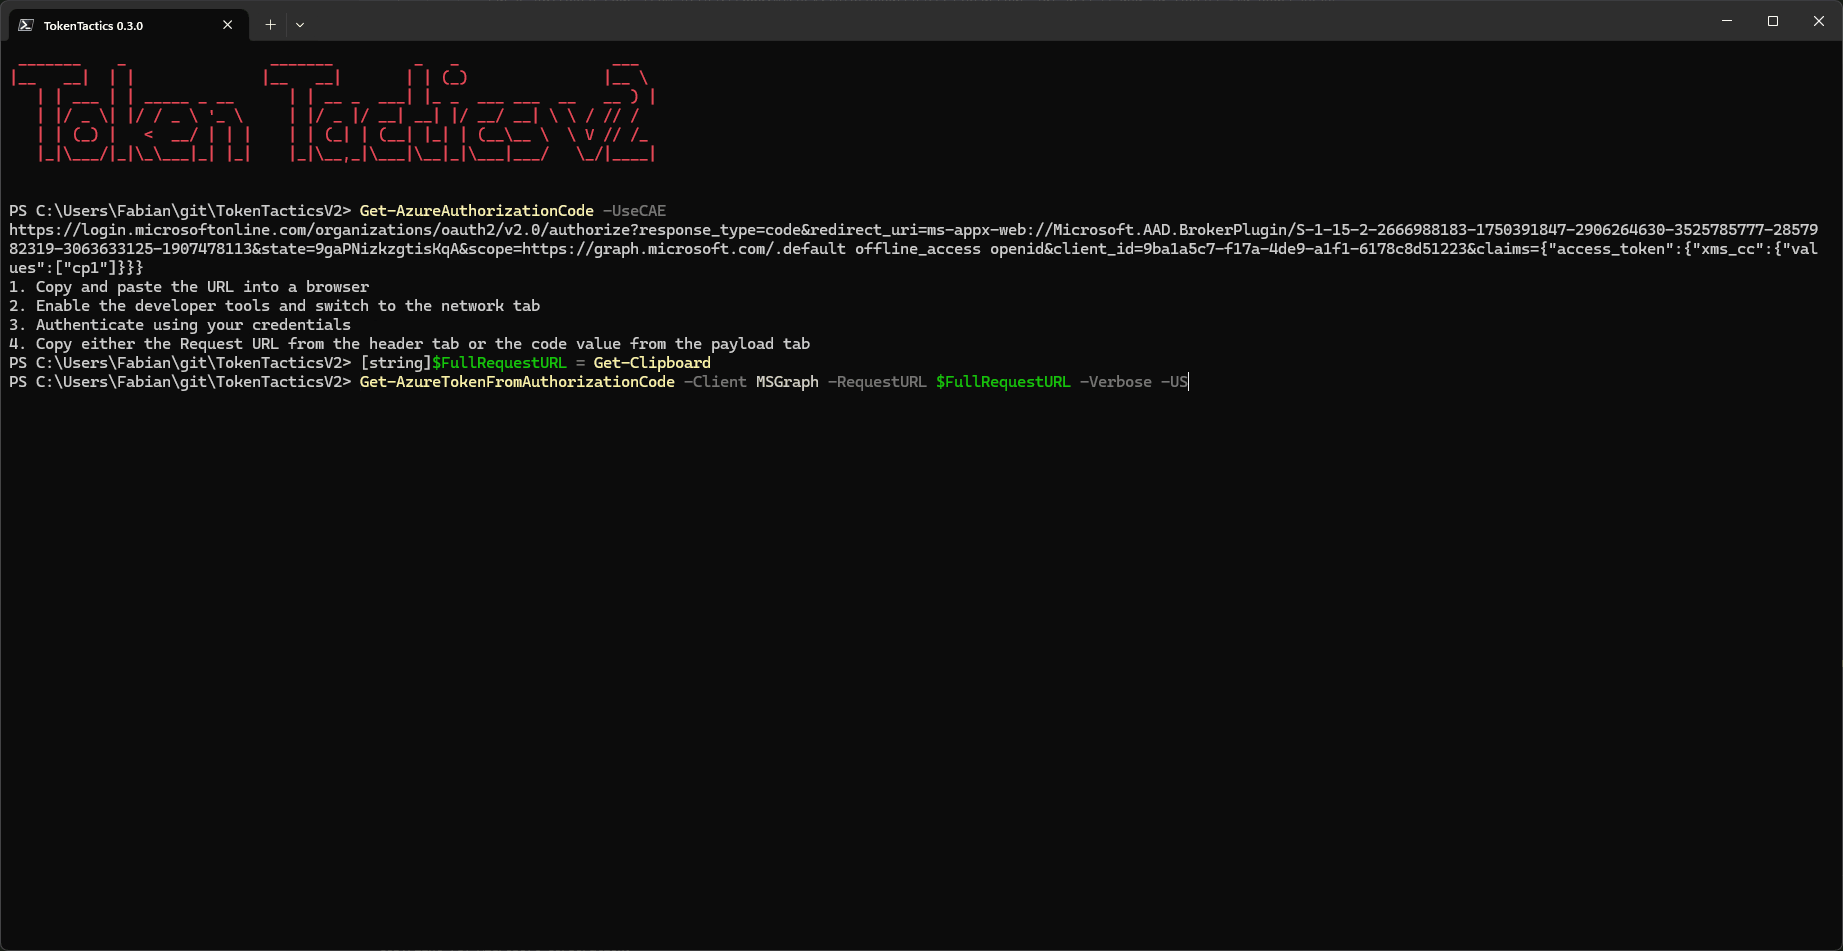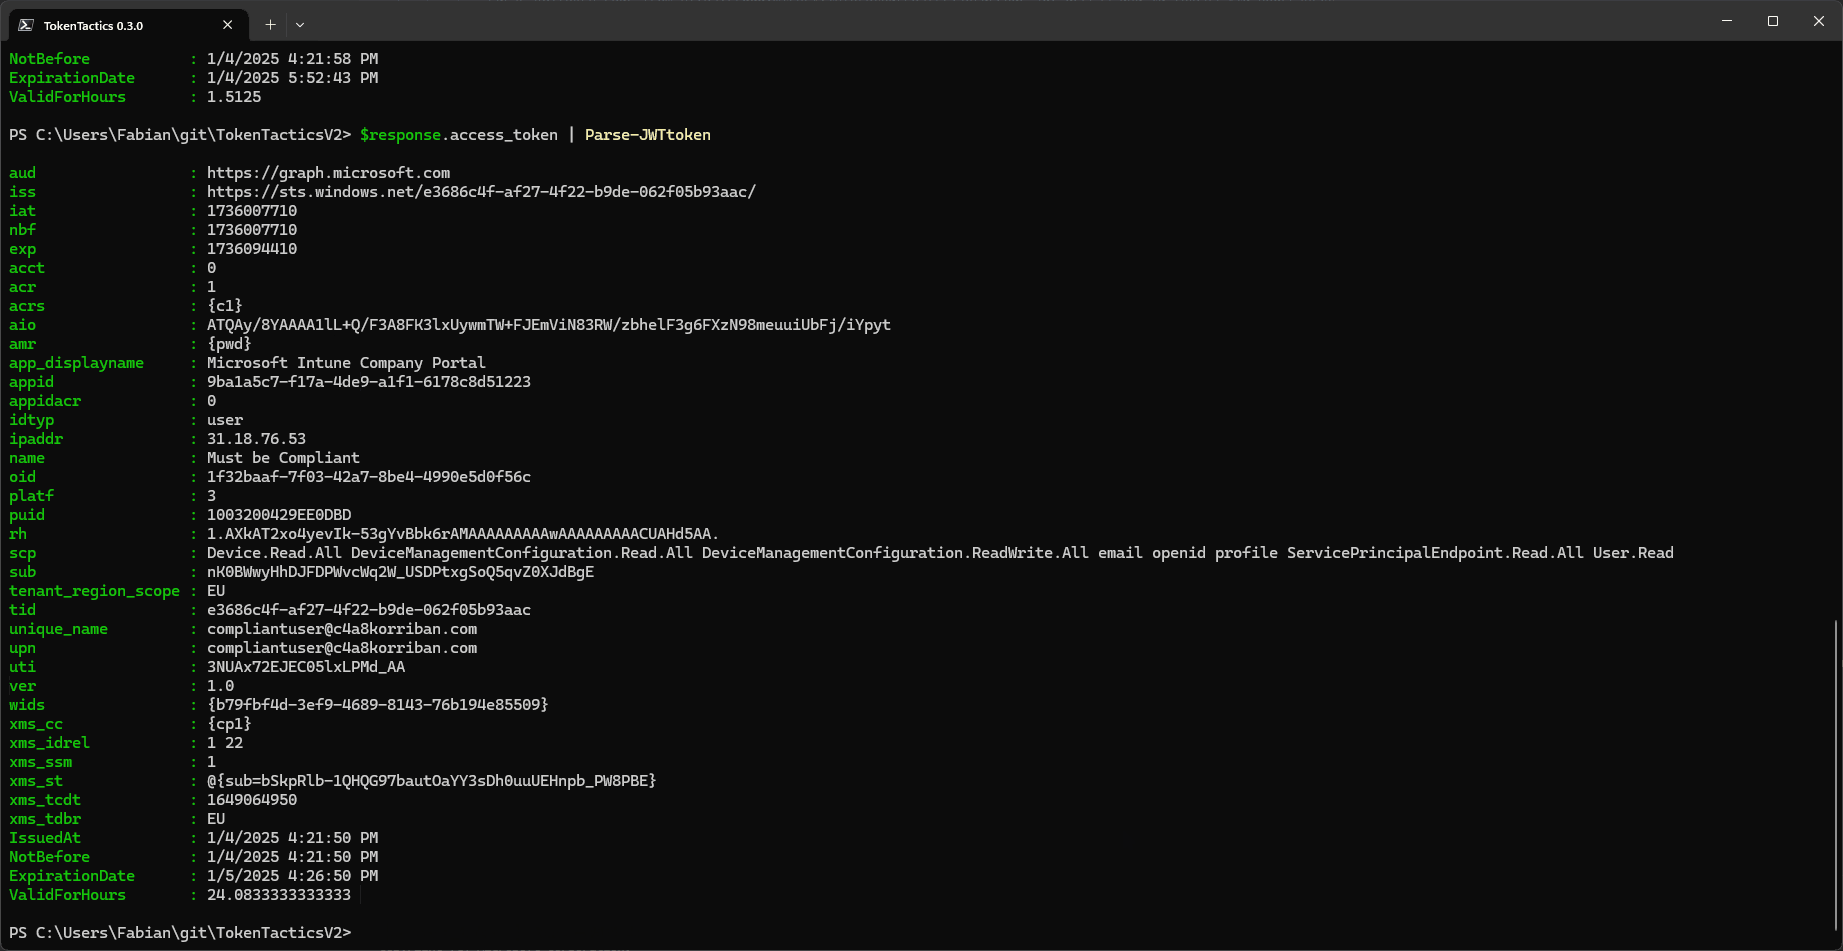
identity-access-managementprivilege-escalation
8287 years ago
TokenTacticsV2 preview

TokenTacticsV2

GitHubf-bader/tokentacticsv2

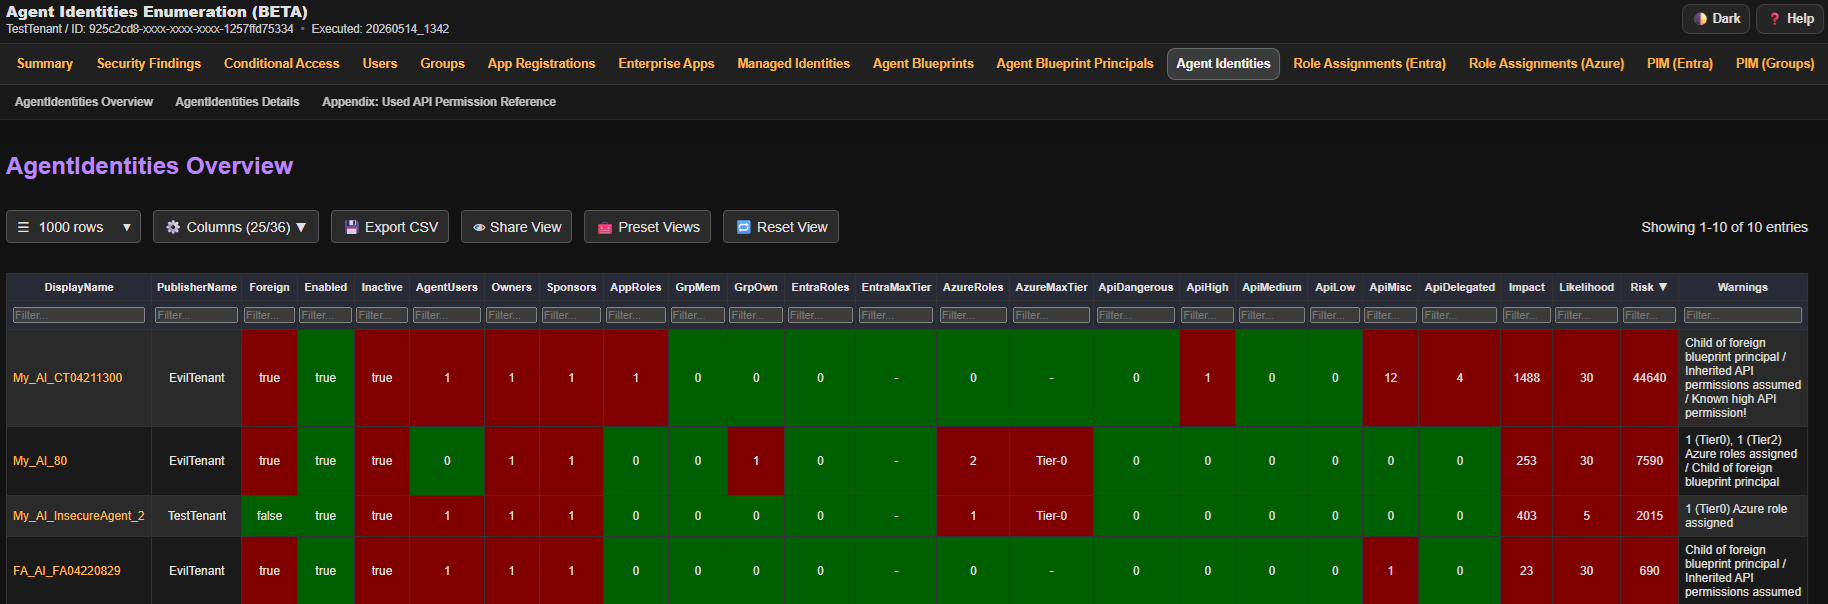
A fork of the great TokenTactics with support for CAE and token endpoint v2
authenticationcloud-securityidentity-access-management+3
4711 month ago
EntraFalcon preview

EntraFalcon

GitHubcompasssecurity/entrafalcon

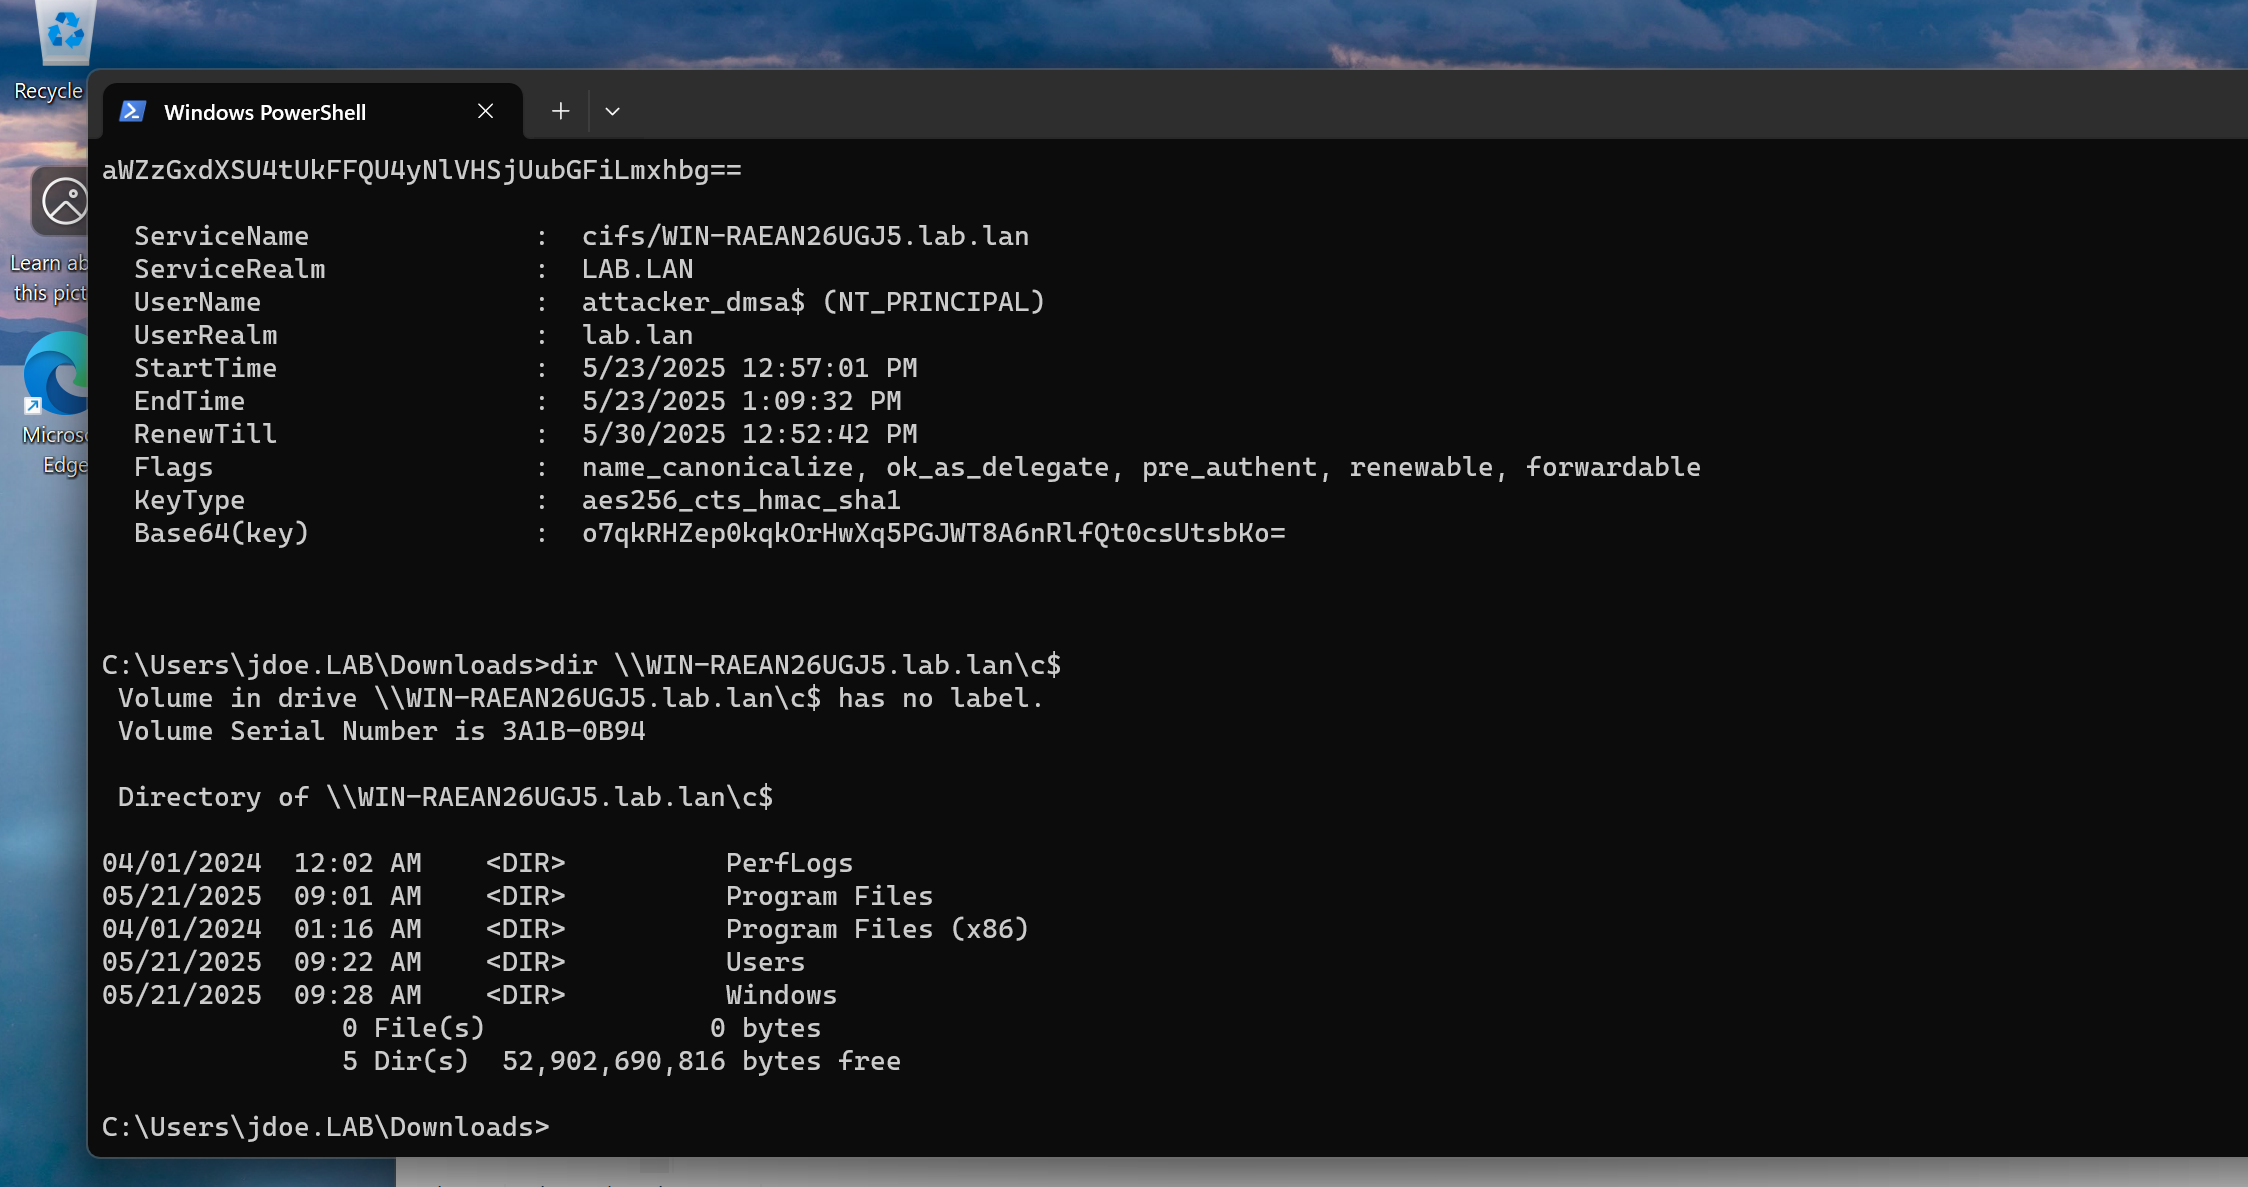
A lightweight PowerShell tool for assessing the security posture of Microsoft Entra ID environments. It helps identify privileged objects, risky…
cloud-securityidentity-access-managementinformation-gathering+3
5241 month ago
SharpSuccessor preview

SharpSuccessor

GitHublogangoins/sharpsuccessor

SharpSuccessor is a .NET Proof of Concept (POC) for fully weaponizing Yuval Gordon’s (@YuG0rd) BadSuccessor attack from Akamai.
authenticationexploitationidentity-access-management+4
4331 year ago
CredSpy preview

CredSpy

GitHubredbyte1337/credspy

Entra ID user enumeration and auth method discovery via the public GetCredentialType API
authenticationcloud-securityidentity-access-management+5
1781 month ago
EvilMist preview

EvilMist

GitHublogisek/evilmist

EvilMist is a collection of scripts and utilities designed to support cloud penetration testing & red teaming. The toolkit helps identify…
authenticationcloud-securityidentity-access-management+7
1708 months ago
Mandiant-Azure-AD-Investigator preview
Archived

Mandiant-Azure-AD-Investigator

GitHubmandiant/mandiant-azure-ad-investigator

Read-only PowerShell module for detecting UNC2452 and other threat actor artifacts in Azure AD, auditing federated domains, service principals,…
cloud-securitydigital-forensicsidentity-access-management+4
6473 years ago
SkyArk preview

SkyArk

GitHubcyberark/skyark

SkyArk helps to discover, assess and secure the most privileged entities in Azure and AWS
cloud-securityidentity-access-managementinformation-gathering+3
9141 year ago
adexplorersnapshot-rs preview

adexplorersnapshot-rs

GitHubt94j0/adexplorersnapshot-rs

Converts Active Directory Explorer snapshot (.dat) files into BloodHound CE JSON archives for graph-based AD attack-path analysis and reconnaissance.
identity-access-managementinformation-gatheringpenetration-testing+1
966 months ago
openwisp-controller preview

openwisp-controller

GitHubopenwisp/openwisp-controller

Network and WiFi controller: provisioning, configuration management and updates, (pull via openwisp-config or push via SSH), x509 PKI management and…

identity-access-managementiot-securitynetwork-access-control+3
7922 days ago
Previous1234Next