
oauthseeker
 praetorian-inc/oauthseeker
A malicious OAuth application that can be leveraged for both internal and external phishing attacks targeting Microsoft Azure and Office365 users.
authenticationcloud-securityidentity-access-management+6
180
praetorian-inc/oauthseekerA malicious OAuth application that can be leveraged for both internal and external phishing attacks targeting Microsoft Azure and Office365 users.
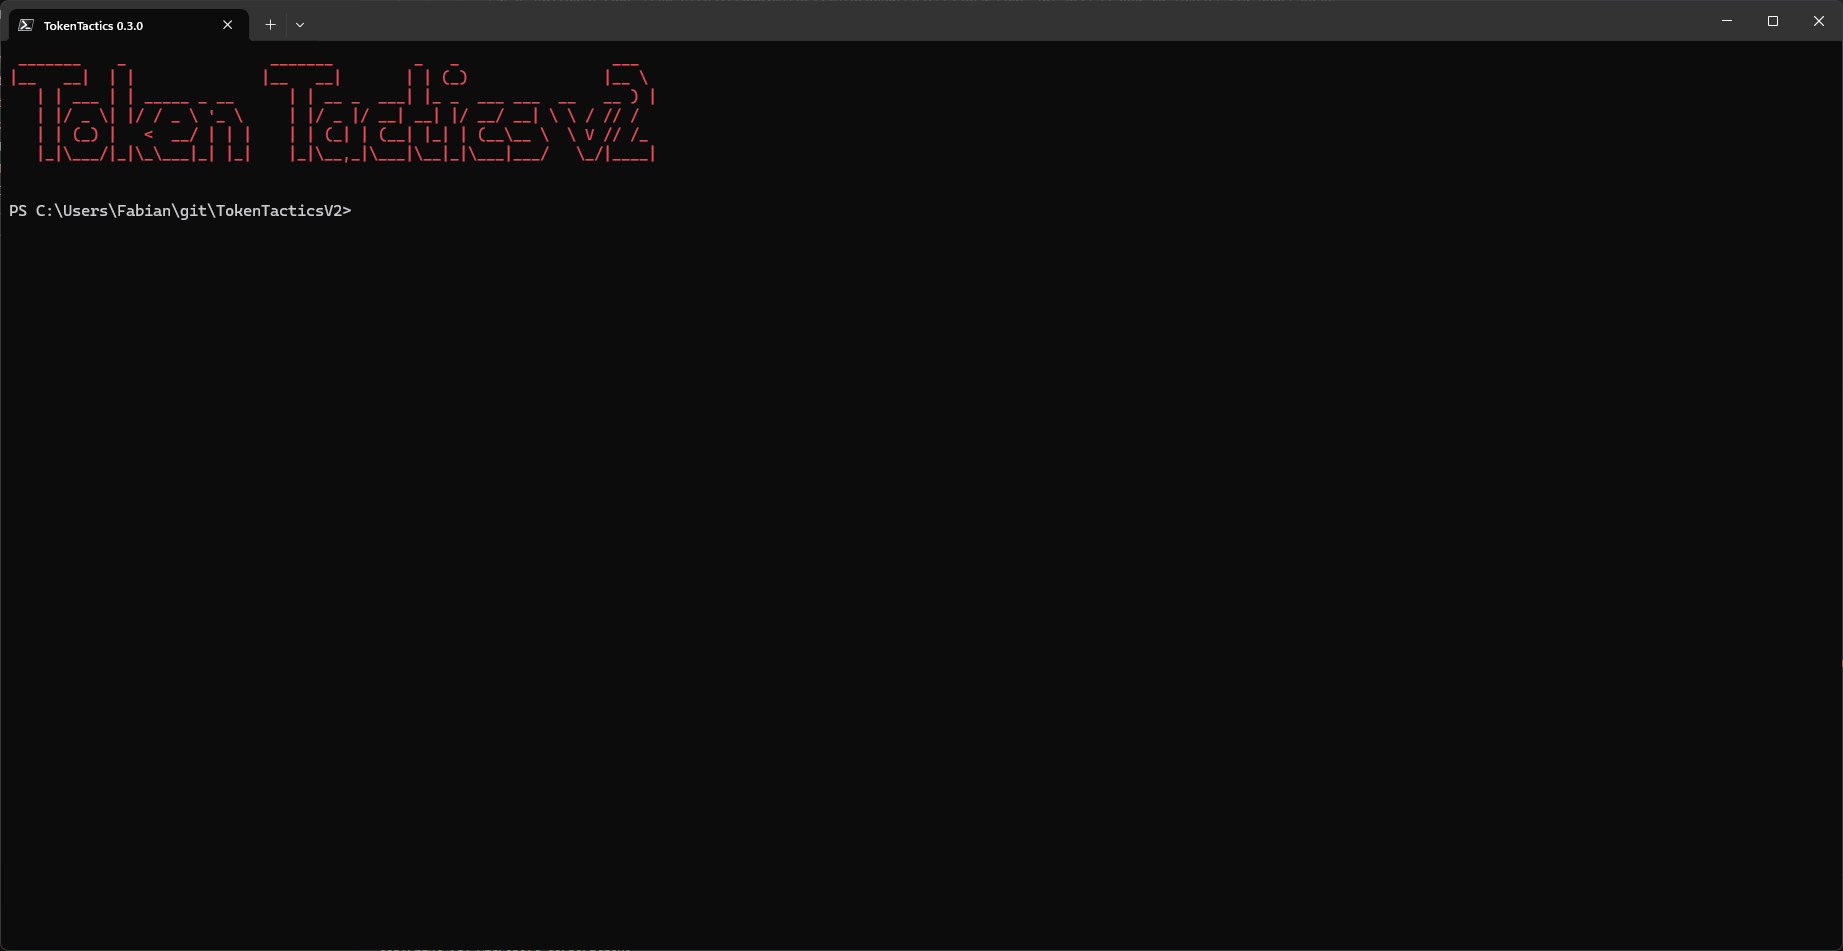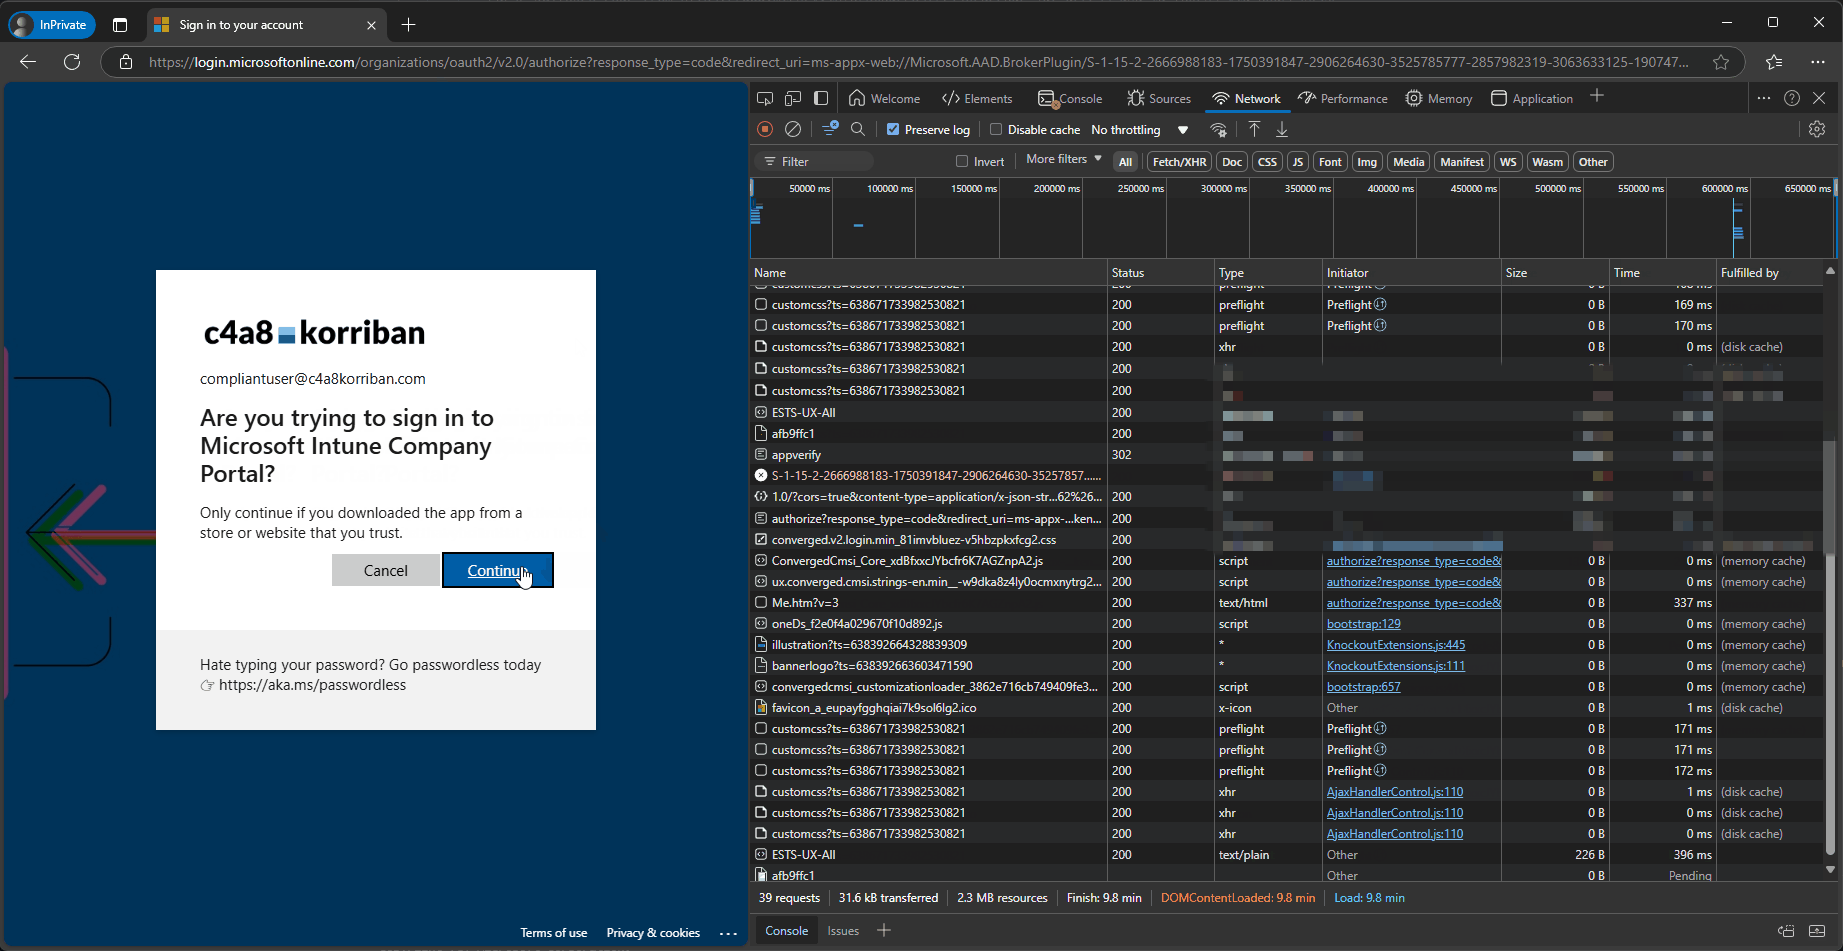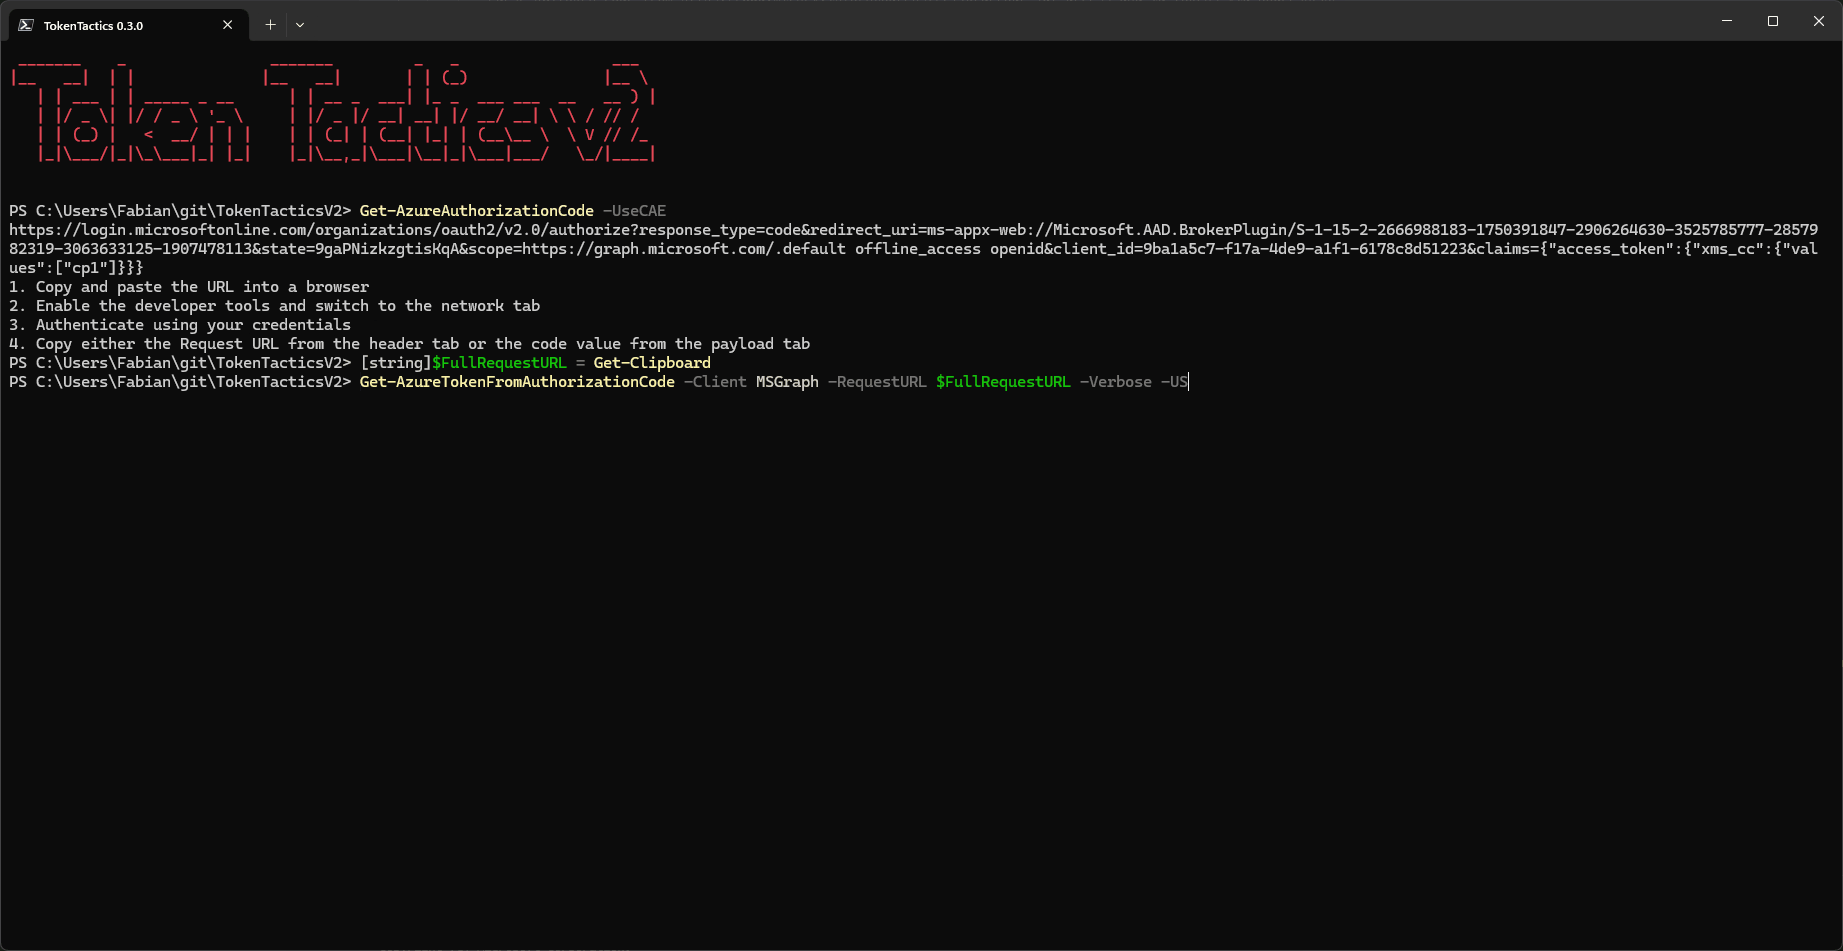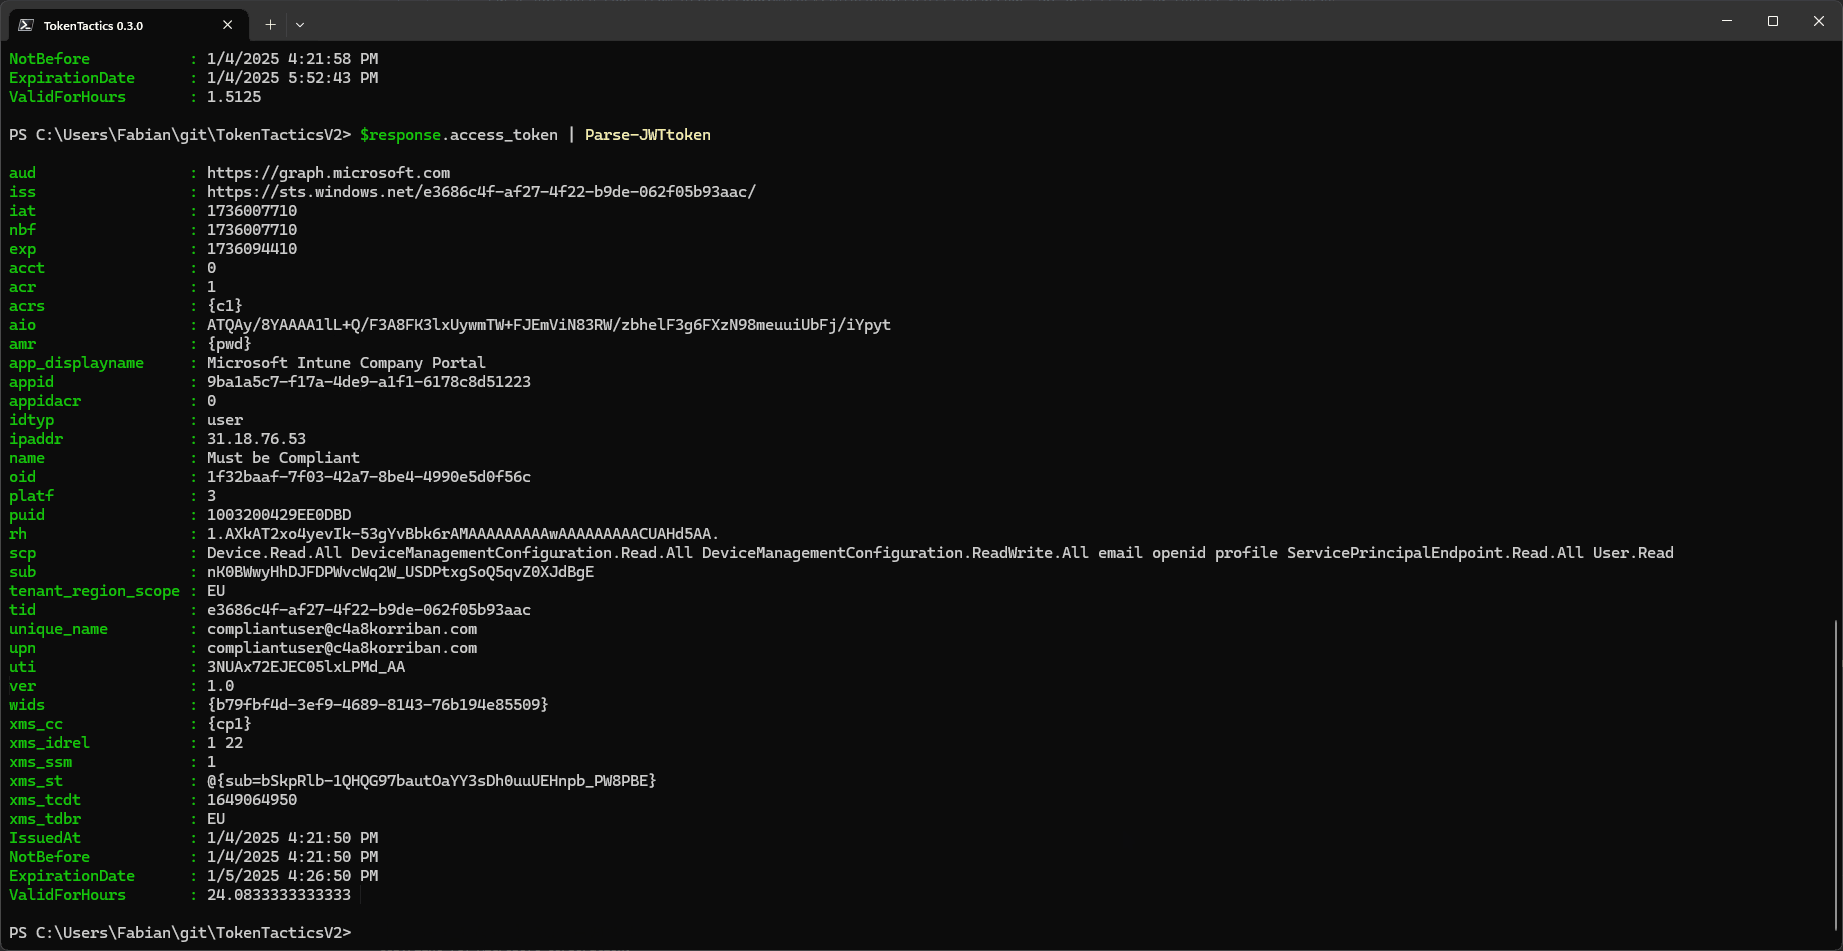 f-bader/tokentacticsv2
A fork of the great TokenTactics with support for CAE and token endpoint v2
 randomaccess3/awesome-bec
Repository of attack and defensive information for Business Email Compromise investigations
 vectra-ai-research/maad-af
MAAD Attack Framework - An attack tool for simple, fast & effective security testing of M365 & Entra ID (Azure AD).
 temp43487580/entrapassthecert
tool for requesting Entra ID's P2P certificate and authenticating to a remote Entra joinned devices with it
 vhscom/private-landing
🔐 Learn authentication by building it right. An extensible, standards-compliant reference implementation for Cloudflare Workers with Hono, Turso,…
 katrielmoses/mailaccess
Free email OSINT tool, 2500+ platforms, identity clustering, breach detection. No API keys required. pip install mailaccess
 redbyte1337/credspy
Entra ID user enumeration and auth method discovery via the public GetCredentialType API
 jenderal92/shadow-vault
Shadow Vault – Add shadow users with SHA-512 hash, auto aging match, multiple write fallbacks.
 cloud-architekt/azuread-attack-defense
This publication is a collection of various common attack scenarios on Microsoft Entra ID (formerly known as Azure Active Directory) and how they can…
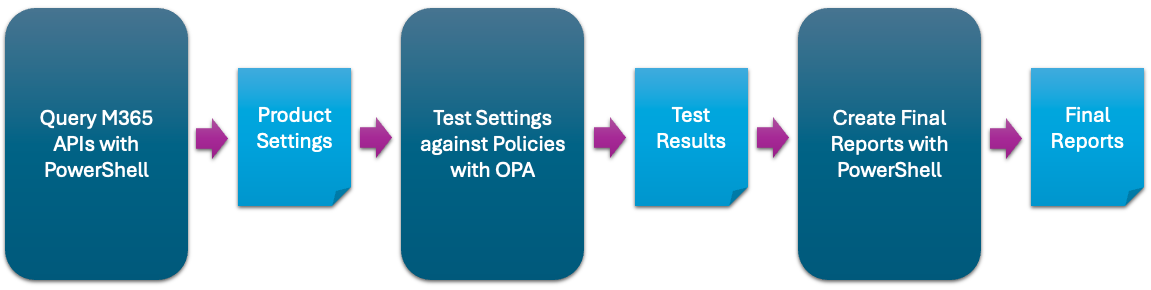 cisagov/scubagear
Automation to assess the state of your M365 tenant against CISA's baselines
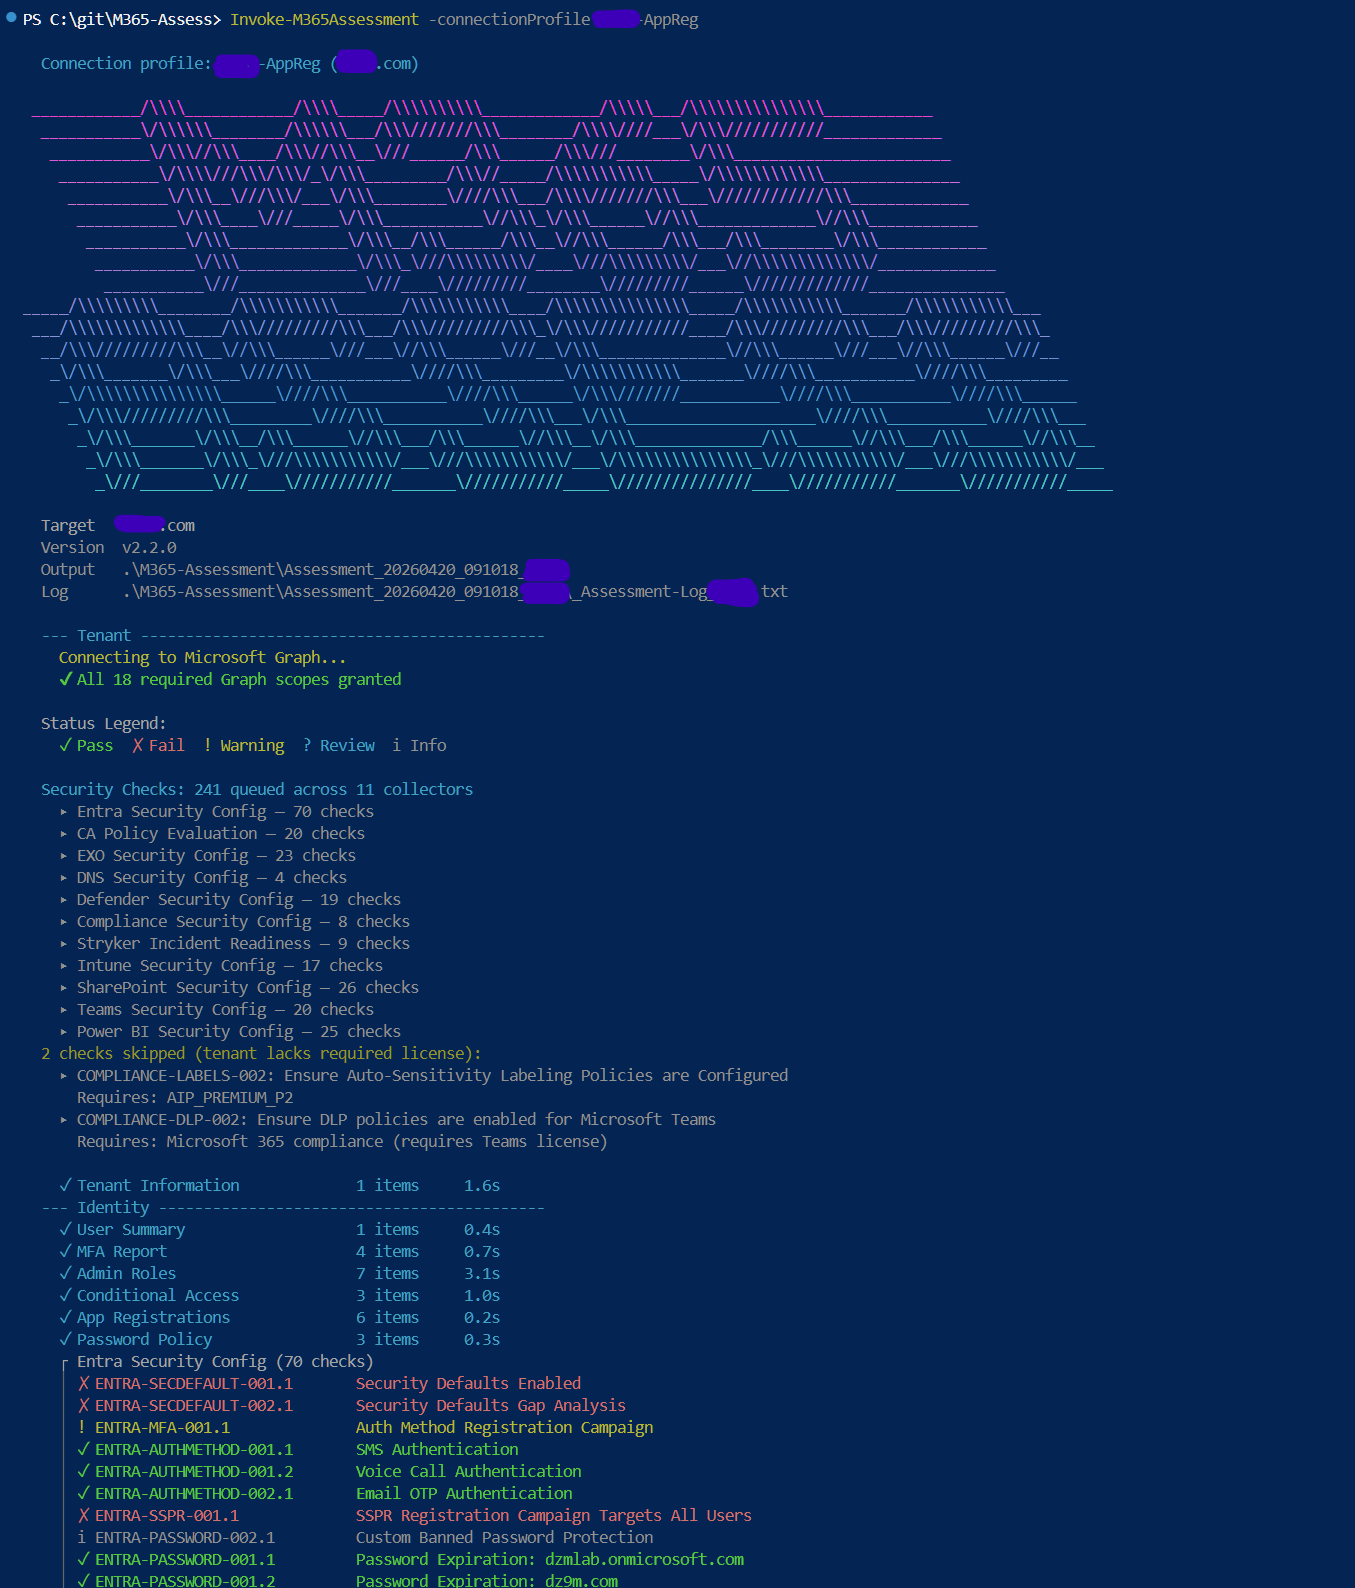 galvnyz/m365-assess
290+ Automated checks across 14 compliance frameworks, interactive HTML report, no data leaves your machine.